Claimed undisclosed PIN exfiltration vulnerability
a_ferron-2085731252657696911
- Author
- @a_ferron
- Organisation
- independent
- Evidence role
- social statement
- Posted
- 7 Aug 2026, 14:14 UTC
- Capture status
- capture held
Antoine Ferron says he found a PIN-exfiltration vulnerability in a Coldcard product two years ago, waited for a fix, and will now publish because the update never arrived. Held as a dated, specific claim about an undisclosed prior vulnerability. The existence and details of the vulnerability are the poster's own and are not verified here.
This post is registered as evidence and has a locally held capture. The original remains the canonical publication. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
The conversation
Captured . 2 continuation posts, 7 replies held, 2 muted as low signal. Posts are in the archive's own order, oldest first, not the order X ranks them in.
-
capture taken
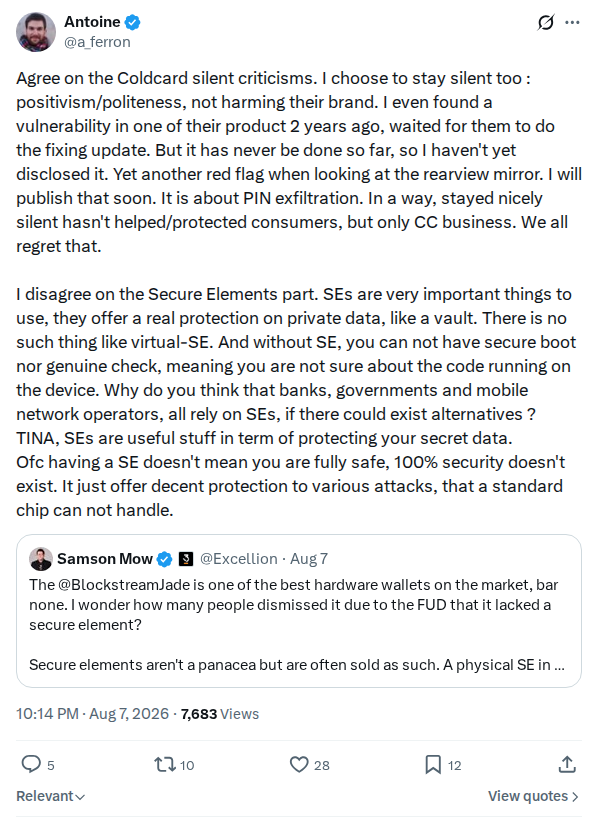
Agree on the Coldcard silent criticisms. I choose to stay silent too : positivism/politeness, not harming their brand. I even found a vulnerability in one of their product 2 years ago, waited for them to do the fixing update. But it has never be done so far, so I haven't yet disclosed it. Yet another red flag when looking at the rearview mirror. I will publish that soon. It is about PIN exfiltration. In a way, stayed nicely silent hasn't helped/protected consumers, but only CC business. We all regret that. I disagree on the Secure Elements part. SEs are very important things to use, they offer a real protection on private data, like a vault. There is no such thing like virtual-SE. And without SE, you can not have secure boot nor genuine check, meaning you are not sure about the code running on the device. Why do you think that banks, governments and mobile network operators, all rely on SEs, if there could exist alternatives ? TINA, SEs are useful stuff in term of protecting your secret data. Ofc having a SE doesn't mean you are fully safe, 100% security doesn't exist. It just offer decent protection to various attacks, that a standard chip can not handle.
-
capture taken
The wallet I like the most today is the @Keycard_ Shell. An airgap device, with integrated smartcard SE reader that protects the seed. Plus you can easily change account/seed by just changing the smartcard inserted.
-
capture taken
A last word about the exfil protection. I see it as a complex mathematical toy that helps only to avoid very specific issues, which are rarely used by malicious actors. It adds more complexity than real security. As the author of this security mechanism wrote : "that still wouldn't stop a malicious wallet from stealing from you because it can basically just do whatever it wants." And without a SE, you have no guarantee what your hw wallet is doing.
Replies held in this capture (7)
Low-signal replies are collapsed to one line, never removed. A reply is collapsed only on mechanical grounds: fewer than 40 characters, no text, mentions only, no letters or digits, a bare link, or text identical to another reply in the same capture. What a reply argues is never a reason. Each one says which rule collapsed it, and its screenshot is one click away.
-
capture taken
There's a Trading Path Most People Don't Know Exists
show the capture
capture taken
-
capture taken
What is pIN exfiltration?
show the capture
capture taken
-
capture taken
Wait for the publication of the issue. I will release the details soon. Basically it is possible to recover the user PIN from the in-flight encrypted data, in a Coinkite hardware product product.
show the capture
capture taken
-
capture taken
The opposite of this.
show the capture
capture taken
-
capture taken
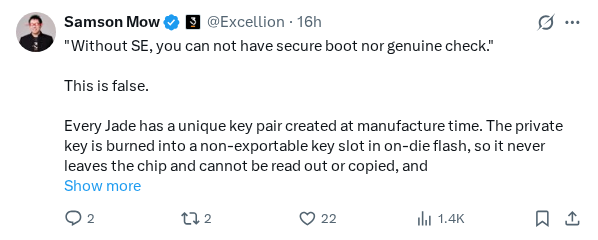
"Without SE, you can not have secure boot nor genuine check." This is false. Every Jade has a unique key pair created at manufacture time. The private key is burned into a non-exportable key slot in on-die flash, so it never leaves the chip and cannot be read out or copied, and Blockstream signs a certificate over the corresponding public key. To check a device is genuine, you send it a random challenge. Jade signs that challenge with its private key and sends back three things: the public key, the signature over your challenge, and Blockstream's certificate for that public key. Your wallet software already knows the Blockstream manufacturer public key, so it can run two checks. First it verifies the certificate, which proves that this particular public key belongs to a device Blockstream actually made. Then it verifies the signature over the challenge, which proves the device in front of you really holds the matching private key rather than just replaying someone else's public key and certificate. Both checks matter. The certificate alone proves nothing about who you are talking to, since certificates and public keys are public data and anyone could copy them. The signature alone proves nothing about provenance, since anyone can generate a key pair and sign things. Together they show that the device you are connected to right now holds a private key that Blockstream certified at manufacture. And because the challenge is fresh and random each time, an old captured response cannot be replayed to fake it.
show the capture
capture taken
-
capture taken
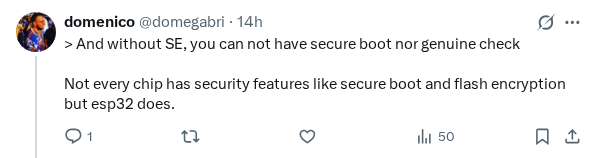
> And without SE, you can not have secure boot nor genuine check Not every chip has security features like secure boot and flash encryption but esp32 does.
show the capture
capture taken
-
capture taken
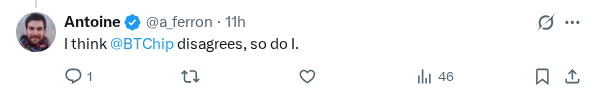
I think @BTChip disagrees, so do I.
show the capture
capture taken
The remaining 0 replies
This capture reached the end of the conversation as X served it: it stopped because nothing further loaded, not because a limit was hit. X decides what a reader is shown, so that is not the same as a guarantee of every reply.
Held captures
-
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 0 lines
Extracted text as captured
thread: 2085731252657696911
url: https://x.com/a_ferron/status/2085731252657696911
author: a_ferron

post: 2085731252657696911
role: focal
author: a_ferron
name: Antoine
created: 2026-08-07T14:14:16Z
media: 0
body:
Agree on the Coldcard silent criticisms. I choose to stay silent too : positivism/politeness, not harming their brand. I even found a vulnerability in one of their product 2 years ago, waited for them to do the fixing update. But it has never be done so far, so I haven't yet disclosed it. Yet another red flag when looking at the rearview mirror. I will publish that soon. It is about PIN exfiltration. In a way, stayed nicely silent hasn't helped/protected consumers, but only CC business. We all regret that.

I disagree on the Secure Elements part. SEs are very important things to use, they offer a real protection on private data, like a vault. There is no such thing like virtual-SE. And without SE, you can not have secure boot nor genuine check, meaning you are not sure about the code running on the device. Why do you think that banks, governments and mobile network operators, all rely on SEs, if there could exist alternatives ? TINA, SEs are useful stuff in term of protecting your secret data.
Ofc having a SE doesn't mean you are fully safe, 100% security doesn't exist. It just offer decent protection to various attacks, that a standard chip can not handle.

post: 2085731255274942910
role: self-thread
author: a_ferron
name: Antoine
created: 2026-08-07T14:14:16Z
media: 0
body:
The wallet I like the most today is the
@Keycard_
 Shell. An airgap device, with integrated smartcard SE reader that protects the seed. Plus you can easily change account/seed by just changing the smartcard inserted.

post: 2085734605315854700
role: self-thread
author: a_ferron
name: Antoine
created: 2026-08-07T14:27:35Z
media: 0
body:
A last word about the exfil protection. I see it as a complex mathematical toy that helps only to avoid very specific issues, which are rarely used by malicious actors. It adds more complexity than real security. As the author of this security mechanism wrote : "that still wouldn't stop a malicious wallet from stealing from you because it can basically just do whatever it wants." And without a SE, you have no guarantee what your hw wallet is doing.

post: 2085835023240888816
role: reply
author: Enkitek
name: EnkiTek
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
2 presentation-noise differences. Sidebar, ticker and other page chrome churn that our review classified as not being changes to what the source says.
- +9 -20 A single promotional reply record was swapped for another; capped remained false, posts_observed and replies_observed stayed at 10 and 7, and scroll rounds fell from 8 to 7, indicating ranking churn.
- +20 -0 A single promotional domain-sale reply was added; capped remained false, posts_observed rose from 9 to 10, and scroll rounds rose from 4 to 8, indicating ranking recovery rather than new content.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.