Chronological reconstruction of the incident discovery
ishi0k-incident-reconstruction
- Author
- @ishi0k
- Organisation
- independent
- Evidence role
- social statement
- Posted
- 5 Aug 2026, 01:13 UTC
- Capture status
- capture held
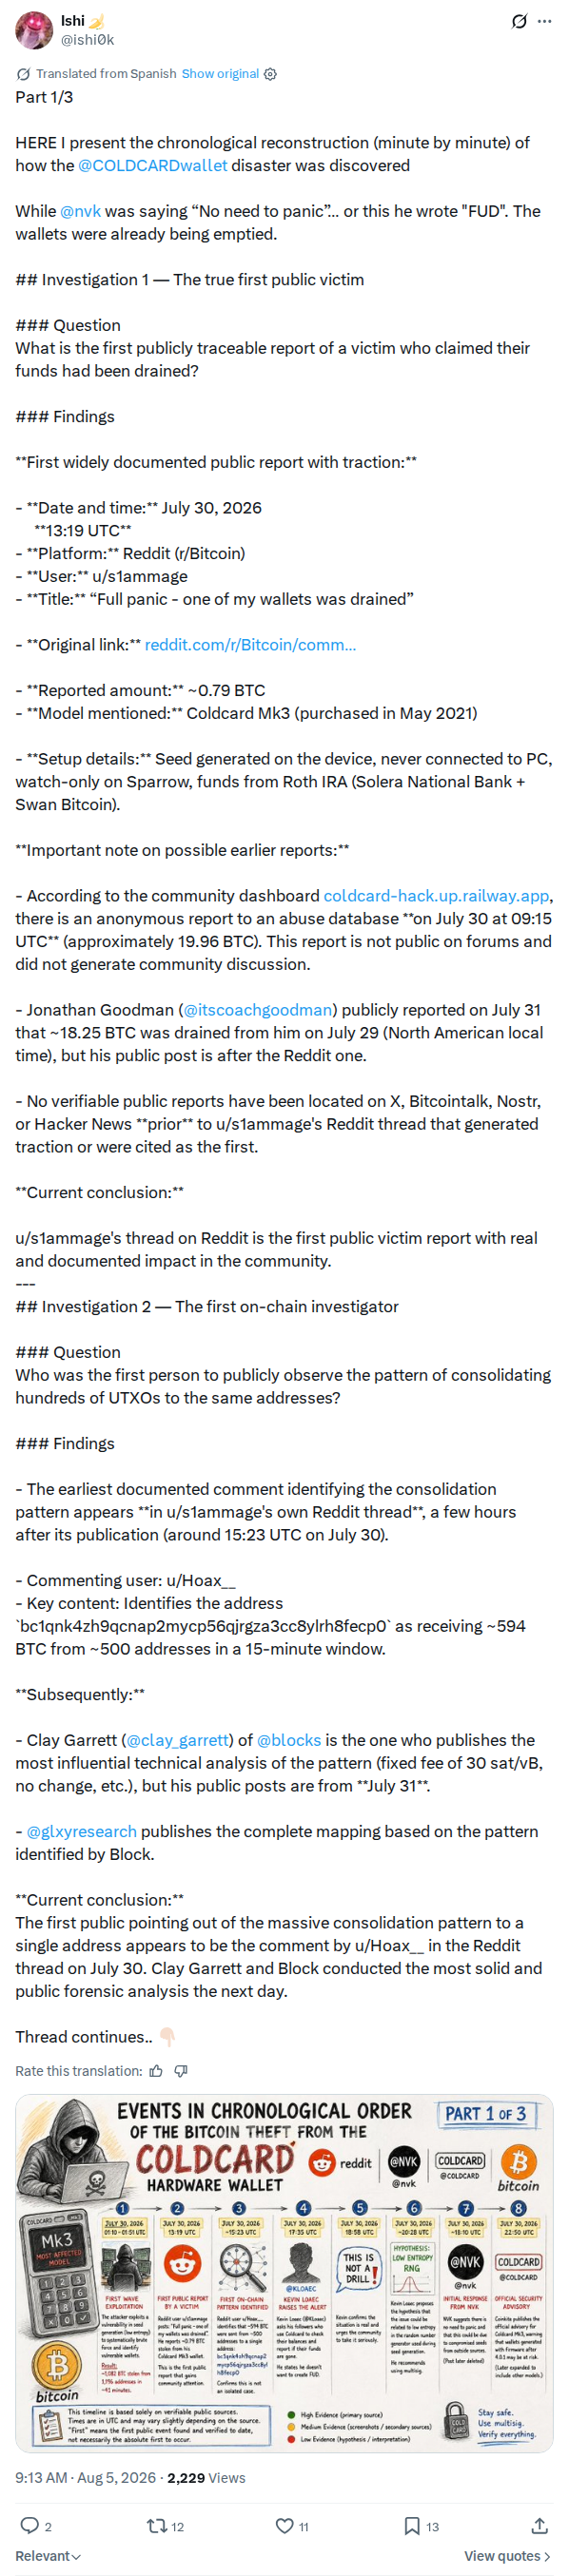
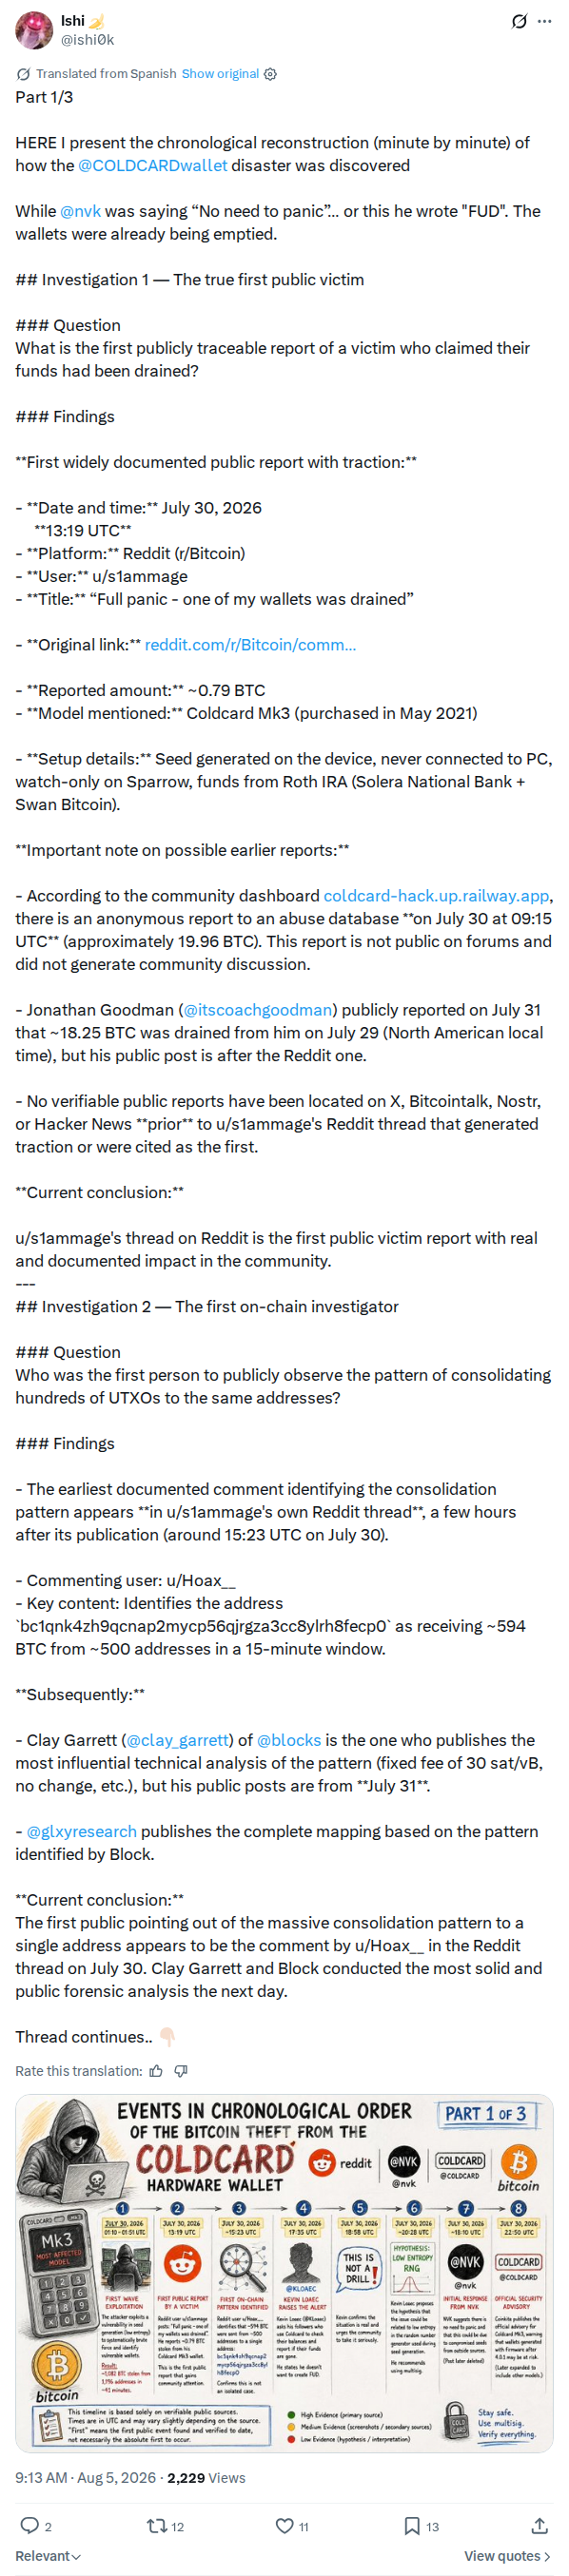
Ishi publishes a three-part thread reconstructing the discovery of the COLDCARD disaster, identifying the first widely documented public victim report and the first on-chain observation of the consolidation pattern. Held as a dated reported reconstruction of the incident timeline. The claims about timing and identity are the poster's own and are not independently verified here.
This post is registered as evidence and has a locally held capture. The original remains the canonical publication. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
The conversation
Captured . 1 continuation posts, 3 replies held. Posts are in the archive's own order, oldest first, not the order X ranks them in.
-
capture taken
Part 1/3 HERE I present the chronological reconstruction (minute by minute) of how the @COLDCARDwallet disaster was discovered While @nvk was saying “No need to panic”… or this he wrote "FUD". The wallets were already being emptied. ## Investigation 1 — The true first public victim ### Question What is the first publicly traceable report of a victim who claimed their funds had been drained? ### Findings **First widely documented public report with traction:** - **Date and time:** July 30, 2026 **13:19 UTC** - **Platform:** Reddit (r/Bitcoin) - **User:** u/s1ammage - **Title:** “Full panic - one of my wallets was drained” - **Original link:** https:// reddit.com/r/Bitcoin/comm ents/1vatgl4/full_panic_one_of_my_wallets_was_drained/ … - **Reported amount:** ~0.79 BTC - **Model mentioned:** Coldcard Mk3 (purchased in May 2021) - **Setup details:** Seed generated on the device, never connected to PC, watch-only on Sparrow, funds from Roth IRA (Solera National Bank + Swan Bitcoin). **Important note on possible earlier reports:** - According to the community dashboard http:// coldcard-hack.up.railway.app, there is an anonymous report to an abuse database **on July 30 at 09:15 UTC** (approximately 19.96 BTC). This report is not public on forums and did not generate community discussion. - Jonathan Goodman ( @itscoachgoodman ) publicly reported on July 31 that ~18.25 BTC was drained from him on July 29 (North American local time), but his public post is after the Reddit one. - No verifiable public reports have been located on X, Bitcointalk, Nostr, or Hacker News **prior** to u/s1ammage's Reddit thread that generated traction or were cited as the first. **Current conclusion:** u/s1ammage's thread on Reddit is the first public victim report with real and documented impact in the community. --- ## Investigation 2 — The first on-chain investigator ### Question Who was the first person to publicly observe the pattern of consolidating hundreds of UTXOs to the same addresses? ### Findings - The earliest documented comment identifying the consolidation pattern appears **in u/s1ammage's own Reddit thread**, a few hours after its publication (around 15:23 UTC on July 30). - Commenting user: u/Hoax__ - Key content: Identifies the address `bc1qnk4zh9qcnap2mycp56qjrgza3cc8ylrh8fecp0` as receiving ~594 BTC from ~500 addresses in a 15-minute window. **Subsequently:** - Clay Garrett ( @clay_garrett ) of @blocks is the one who publishes the most influential technical analysis of the pattern (fixed fee of 30 sat/vB, no change, etc.), but his public posts are from **July 31**. - @glxyresearch publishes the complete mapping based on the pattern identified by Block. **Current conclusion:** The first public pointing out of the massive consolidation pattern to a single address appears to be the comment by u/Hoax__ in the Reddit thread on July 30. Clay Garrett and Block conducted the most solid and public forensic analysis the next day. Thread continues..
-
capture taken
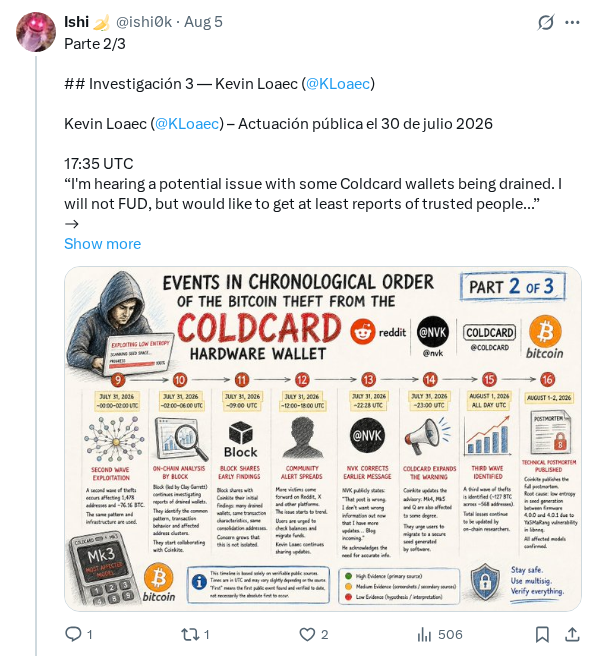
Parte 2/3 ## Investigación 3 — Kevin Loaec ( @KLoaec ) Kevin Loaec ( @KLoaec ) – Actuación pública el 30 de julio 2026 17:35 UTC “I'm hearing a potential issue with some Coldcard wallets being drained. I will not FUD, but would like to get at least reports of trusted people...” → Primer mensaje público. Pide verificaciones. 18:58 UTC “Alright I'm convinced THIS IS NOT A DRILL.” → Pasa de duda a certeza. \~20:01 UTC Thread: Single-sig only por ahora. No sabemos si es seed o otro bug. Passphrase o dice rolls pueden no salvar. USE MULTISIG. → Empieza a dar recomendaciones. \~20:28 UTC “My current hypothesis for the @COLDCARDwallet theft.” Propone Low entropy RNG (biblioteca o secure element). Hipótesis de que el atacante usó IA y solo escaneó rutas BIP84. → Primera hipótesis pública fuerte de bajo entropy / RNG por parte de un investigador relevante. ### Posteriores Continúa actualizando, advierte sobre Mk3, habla de entropía, recomienda multisig y Liana. Kevin fue de los primeros en llevar el tema de “posible FUD de Reddit” a “esto es real y puede ser un problema de entropy”. --- ## Investigación 4 — NVK ( @nvk ) NVK ( @nvk ) – Primeras 24 horas (30 de julio 2026) \~18:10 UTC Post público: “No need to panic. Someone loaded a compromised seed onto a Coldcard and/or their seed leaked. This is part of a broader attack involving 500 private keys...” → ELIMINADO posteriormente \~21:47 UTC Post: “We've done a lot of investigation about the COLDCARD reports, blog post incoming!” → Investigando \~22:28 UTC Respuesta: “That post is wrong. I don’t want wrong information out now... Blog incoming.” → Reconoce error del post anterior 22:50 UTC Cuenta oficial @COLDCARDwallet Publica el primer Security Advisory (Mk3) → Reconocimiento oficial del riesgo **Cambio de postura documentado:** Pasó de atribuir el problema a “seeds comprometidas / filtradas de fuera” (post eliminado) a reconocer un problema en el firmware de Coldcard (advisory + disculpa posterior del 31 de julio). --- ## Investigación 5 — ¿Cuándo fue avisado Coinkite? ### Evidencia pública disponible - No existe evidencia pública de emails, tickets de GitHub, mensajes de Telegram/Discord o contactos privados filtrados que indiquen la hora exacta en que Coinkite fue notificado por primera vez. - @blocks (Clay Garrett y equipo) investigó reportes de wallets no-Bitkey siendo drenadas el 30 de julio y colaboró con @Coinkite - El advisory oficial se publica a las **22:50 UTC del 30 de julio**. - @nvk habla de “investigación” desde la tarde del 30. **Conclusión actual:** La evidencia pública muestra que @Coinkite estaba al tanto y investigando al menos desde la tarde del 30 de julio. No hay prueba pública del “primer aviso interno” exacto. --- ## Investigación 6 — Preparación del atacante ### Solo evidencia respaldada - @blocks identificó que el operador usó una cuenta de pago en un proveedor de servicios blockchain para consultar direcciones durante los sweeps. - El patrón (fee fija, sin change, consolidación rápida, enfoque en direcciones >0.15 BTC y dormidas) indica automatización y lista pre-preparada. - Galaxy y Block describen la operación como altamente automatizada y preparada. - No se han publicado scripts del atacante ni evidencia pública de cuándo empezó el cómputo de las seeds candidatas. - Coinkite sugirió que pudo usarse IA para encontrar el bug en el código open-source. **No hay evidencia pública sólida** que permita afirmar con precisión cuántos días/semanas/meses llevaba preparando el ataque antes del 30 de julio. El hilo continua
Replies held in this capture (3)
Low-signal replies are collapsed to one line, never removed. A reply is collapsed only on mechanical grounds: fewer than 40 characters, no text, mentions only, no letters or digits, a bare link, or text identical to another reply in the same capture. What a reply argues is never a reason. Each one says which rule collapsed it, and its screenshot is one click away.
-
capture taken
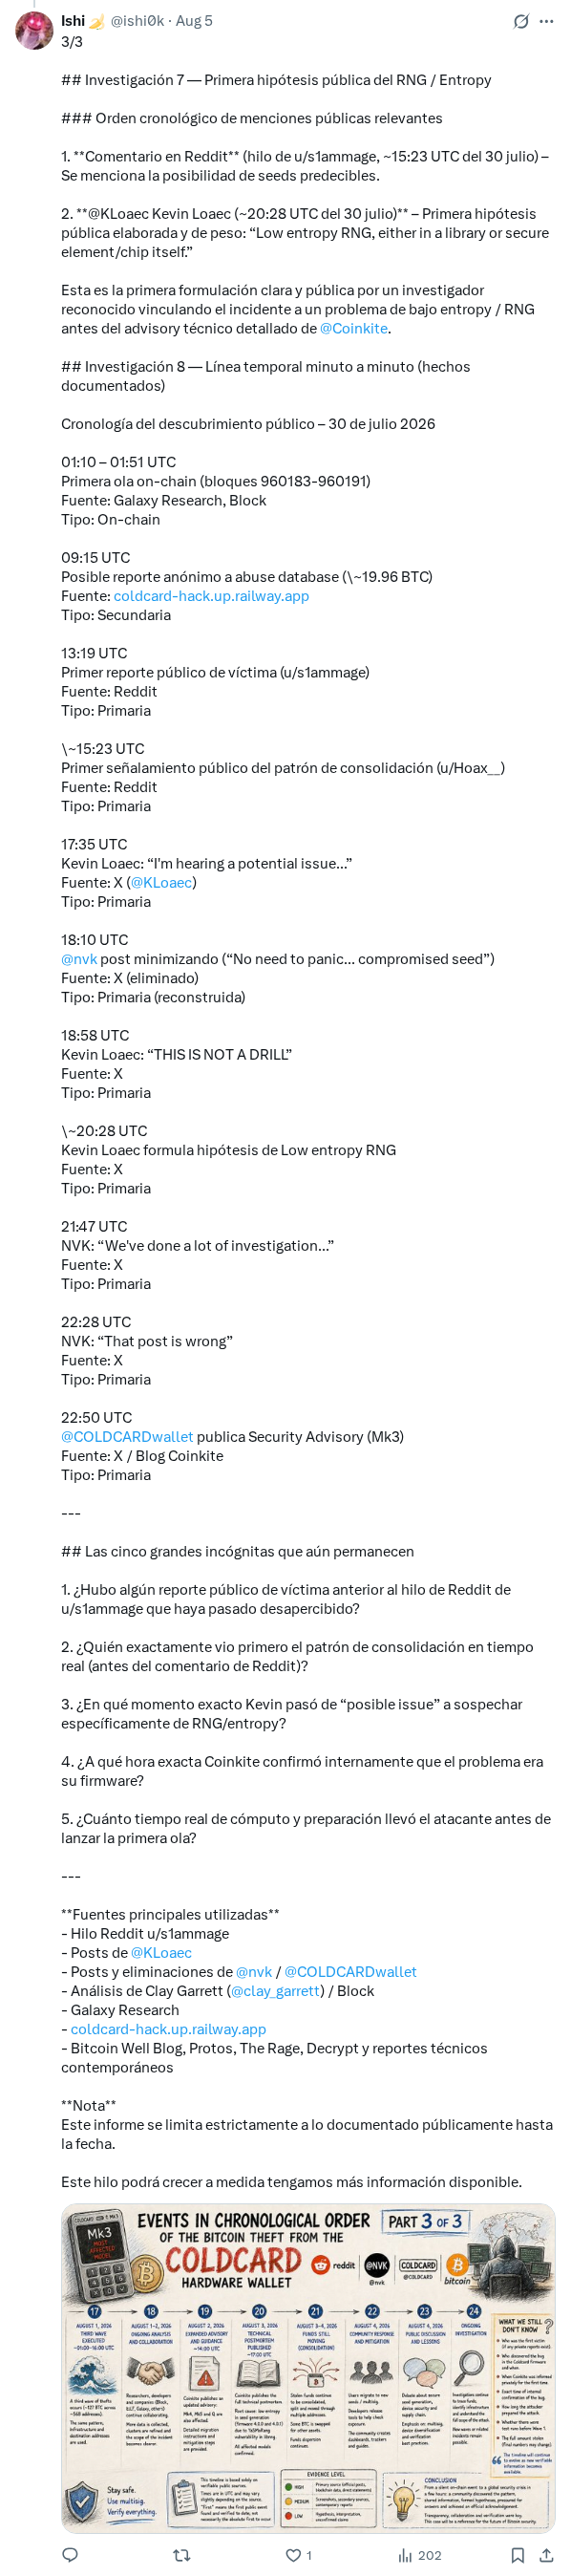
3/3 ## Investigación 7 — Primera hipótesis pública del RNG / Entropy ### Orden cronológico de menciones públicas relevantes 1. **Comentario en Reddit** (hilo de u/s1ammage, ~15:23 UTC del 30 julio) – Se menciona la posibilidad de seeds predecibles. 2. **@KLoaec Kevin Loaec (~20:28 UTC del 30 julio)** – Primera hipótesis pública elaborada y de peso: “Low entropy RNG, either in a library or secure element/chip itself.” Esta es la primera formulación clara y pública por un investigador reconocido vinculando el incidente a un problema de bajo entropy / RNG antes del advisory técnico detallado de @Coinkite . ## Investigación 8 — Línea temporal minuto a minuto (hechos documentados) Cronología del descubrimiento público – 30 de julio 2026 01:10 – 01:51 UTC Primera ola on-chain (bloques 960183-960191) Fuente: Galaxy Research, Block Tipo: On-chain 09:15 UTC Posible reporte anónimo a abuse database (\~19.96 BTC) Fuente: http:// coldcard-hack.up.railway.app Tipo: Secundaria 13:19 UTC Primer reporte público de víctima (u/s1ammage) Fuente: Reddit Tipo: Primaria \~15:23 UTC Primer señalamiento público del patrón de consolidación (u/Hoax__) Fuente: Reddit Tipo: Primaria 17:35 UTC Kevin Loaec: “I'm hearing a potential issue...” Fuente: X ( @KLoaec ) Tipo: Primaria 18:10 UTC @nvk post minimizando (“No need to panic... compromised seed”) Fuente: X (eliminado) Tipo: Primaria (reconstruida) 18:58 UTC Kevin Loaec: “THIS IS NOT A DRILL” Fuente: X Tipo: Primaria \~20:28 UTC Kevin Loaec formula hipótesis de Low entropy RNG Fuente: X Tipo: Primaria 21:47 UTC NVK: “We've done a lot of investigation...” Fuente: X Tipo: Primaria 22:28 UTC NVK: “That post is wrong” Fuente: X Tipo: Primaria 22:50 UTC @COLDCARDwallet publica Security Advisory (Mk3) Fuente: X / Blog Coinkite Tipo: Primaria --- ## Las cinco grandes incógnitas que aún permanecen 1. ¿Hubo algún reporte público de víctima anterior al hilo de Reddit de u/s1ammage que haya pasado desapercibido? 2. ¿Quién exactamente vio primero el patrón de consolidación en tiempo real (antes del comentario de Reddit)? 3. ¿En qué momento exacto Kevin pasó de “posible issue” a sospechar específicamente de RNG/entropy? 4. ¿A qué hora exacta Coinkite confirmó internamente que el problema era su firmware? 5. ¿Cuánto tiempo real de cómputo y preparación llevó el atacante antes de lanzar la primera ola? --- **Fuentes principales utilizadas** - Hilo Reddit u/s1ammage - Posts de @KLoaec - Posts y eliminaciones de @nvk / @COLDCARDwallet - Análisis de Clay Garrett ( @clay_garrett ) / Block - Galaxy Research - http:// coldcard-hack.up.railway.app - Bitcoin Well Blog, Protos, The Rage, Decrypt y reportes técnicos contemporáneos **Nota** Este informe se limita estrictamente a lo documentado públicamente hasta la fecha. Este hilo podrá crecer a medida tengamos más información disponible.
show the capture
capture taken
-
capture taken
missing the "part 0": swap of the seed generation library! from the trezor GPL to a proprietary - source viewable license.
show the capture
capture taken
-
capture taken
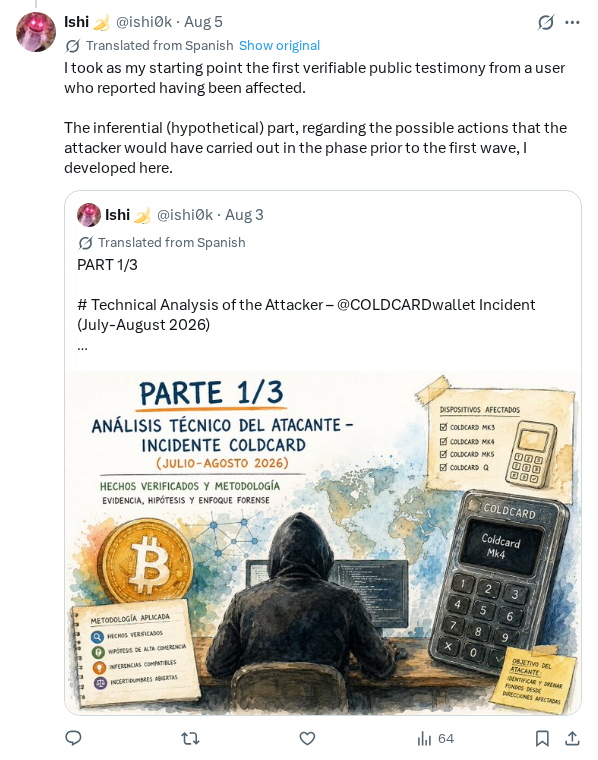
I took as my starting point the first verifiable public testimony from a user who reported having been affected. The inferential (hypothetical) part, regarding the possible actions that the attacker would have carried out in the phase prior to the first wave, I developed here.
show the capture
capture taken
The remaining 0 replies
This capture reached the end of the conversation as X served it: it stopped because nothing further loaded, not because a limit was hit. X decides what a reader is shown, so that is not the same as a guarantee of every reply.
Held captures
-
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 0 lines
Extracted text as captured
thread: 2084809954922258718
url: https://x.com/ishi0k/status/2084809954922258718
author: ishi0k

post: 2084809954922258718
role: focal
author: ishi0k
name: Ishi
created: 2026-08-05T01:13:21Z
media: 1
body:
Part 1/3

HERE I present the chronological reconstruction (minute by minute) of how the
@COLDCARDwallet
 disaster was discovered

While
@nvk
 was saying “No need to panic”… or this he wrote "FUD". The wallets were already being emptied.

## Investigation 1 — The true first public victim

### Question
What is the first publicly traceable report of a victim who claimed their funds had been drained?

### Findings

**First widely documented public report with traction:**

- **Date and time:** July 30, 2026
     **13:19 UTC**
- **Platform:** Reddit (r/Bitcoin)
- **User:** u/s1ammage
- **Title:** “Full panic - one of my wallets was drained”

- **Original link:**
https://
reddit.com/r/Bitcoin/comm
ents/1vatgl4/full_panic_one_of_my_wallets_was_drained/
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
0 presentation-noise differences. Sidebar, ticker and other page chrome churn that our review classified as not being changes to what the source says.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.