Claim that drains were reported as early as 2022
stackernews-drains-since-2022
- Organisation
- Stacker News
- Evidence role
- Reporting
- Published
- 2026-08-02
- Source changes
- 0
- Detected differences
- 3
- Unreviewed
- 0
- Copies held
- 4
A Stacker News thread collecting screenshots said to show COLDCARD owners reporting unexplained drains from 2022 onward, and asking what a vendor could have done about a defect of this kind without signalling it to attackers. The underlying claim is unverified here: the screenshots are reproduced from elsewhere, the thread links an X thread as its source, and this project has not established the provenance or dates of the original reports. Registered because a claim of much earlier losses would change the incident's scope if it held up, and because the discussion itself is part of the response record.
Captured through the site's public GraphQL API since 4 Aug 2026: the browser route began crashing the capture tab sitewide, and the API answers POST from this host while the rendered page is challenge-gated. The query fixes the captured surface to the item's title, text and two levels of comments, each with author and absolute timestamp.
Every check is recorded, including checks that found no text change. A detected edit is therefore bounded between two checks. The publisher's exact save time is not observable from this record. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
Held captures
-
The capture route moved from browser-rendered page text to the stacker.news GraphQL API: post and comment text are unchanged, but captures no longer carry sats counters or relative age labels, and timestamps are now absolute. The browser route had begun crashing the capture tab on stacker.news pages.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 125 lines
-pull down to refresh - -ColdCard users have allegedly been reporting drains since 2022 -2426 sats \ 21 comments \ @justin_shocknet - 12h bitcoin -5000 sats - -https://m.stacker.news/150556 - -https://m.stacker.news/150557 - -https://m.stacker.news/150559 - -Thread: https://x.com/Zenul_Abidin/status/2083756420843839872?s=20 - -Raises an interesting question, if they did know, and wanted to patch it... how could they release a patch that didn't automatically highlight the issue for attack? As soon as you tell users to upgrade and regen, or anyone capable sees the code diff, it'd be open season on all prior keys. - -write -compose - - - - -speak now and forever hold your keys -reply 10 sats -related posts -1985 sats -LIT -NEW -TOP -1 sat \ 9 replies \ @tomlaies - 12h -Raises an interesting question, if they did know, and wanted to patch it - -What I find particularly interesting here is who did these drains <relative-time>? - -Did an attacker know of this vulnerability and only slowly exploited it? -Or did Coldcard users create new wallets and found somebody elses wallet? -reply -254 sats \ 8 replies \ @justin_shocknet - OP 11h -420 sats -103 sats \ 2 replies \ @optimism 12h -how could they release a patch that didn't automatically highlight the issue for attack? - -Same way Core does it. Hide it in a refactor. - -reply -126 sats \ 1 reply \ @justin_shocknet - OP 12h -420 sats -1 sat \ 0 replies \ @nitter - 12h - -https://twiiit.com/Zenul_Abidin/status/2083756420843839872 - -reply -18 sats \ 4 replies \ @Undisciplined - 12h - -I was talking to @optimism about someone potentially trying to replicate the attack for the purpose of safeguarding vulnerable funds and trying to return them later. - -It’s a bad idea for a bunch of reasons, in the current context, but maybe ColdCard would have had to do something like that. - -reply -70 sats \ 3 replies \ @justin_shocknet - OP 12h -420 sats -1 sat \ 1 reply \ @Scoresby - 12h - -I've been looking through a number of these this morning. I'm not sure that it's very convincing that the firmware was the problem -- it is also possible users screwed up. - -https://www.reddit.com/r/coldcard/comments/17epqk8/040_bitcoin_taken_instantly_from_my_coldcard/ - -reply -103 sats \ 0 replies \ @justin_shocknet - OP 12h -420 sats +{ + "data": { + "item": { + "comments": { + "comments": [ + { + "createdAt": "2026-08-02T14:29:54.148Z", + "text": "> Raises an interesting question, if they did know, and wanted to patch it\n\nWhat I find particularly interesting here is who did these drains 3 years ago?\n\n* Did an attacker know of this vulnerability and only slowly exploited it?\n* Or did Coldcard users create new wallets and found somebody elses wallet?", + "user": { + "name": "tomlaies" + } + }, + { + "createdAt": "2026-08-02T14:26:09.392Z", + "text": "> how could they release a patch that didn't automatically highlight the issue for attack?\n\nSame way Core does it. Hide it in a refactor.", + "user": { + "name": "optimism" + } + }, + { + "createdAt": "2026-08-02T14:15:00.482Z", + "text": "https://twiiit.com/Zenul_Abidin/status/2083756420843839872", + "user": { + "name": "nitter" + } + }, + { + "createdAt": "2026-08-02T14:19:28.335Z", + "text": "I was talking to @optimism about someone potentially trying to replicate the attack for the purpose of safeguarding vulnerable funds and trying to return them later.\n\nIt’s a bad idea for a bunch of reasons, in the current context, but maybe ColdCard would have had to do something like that.", + "user": { + "name": "Undisciplined" + } + }, + { + "createdAt": "2026-08-02T14:25:40.385Z", + "text": "I've been looking through a number of these this morning. I'm not sure that it's very convincing that the firmware was the problem -- it is also possible users screwed up.\n\n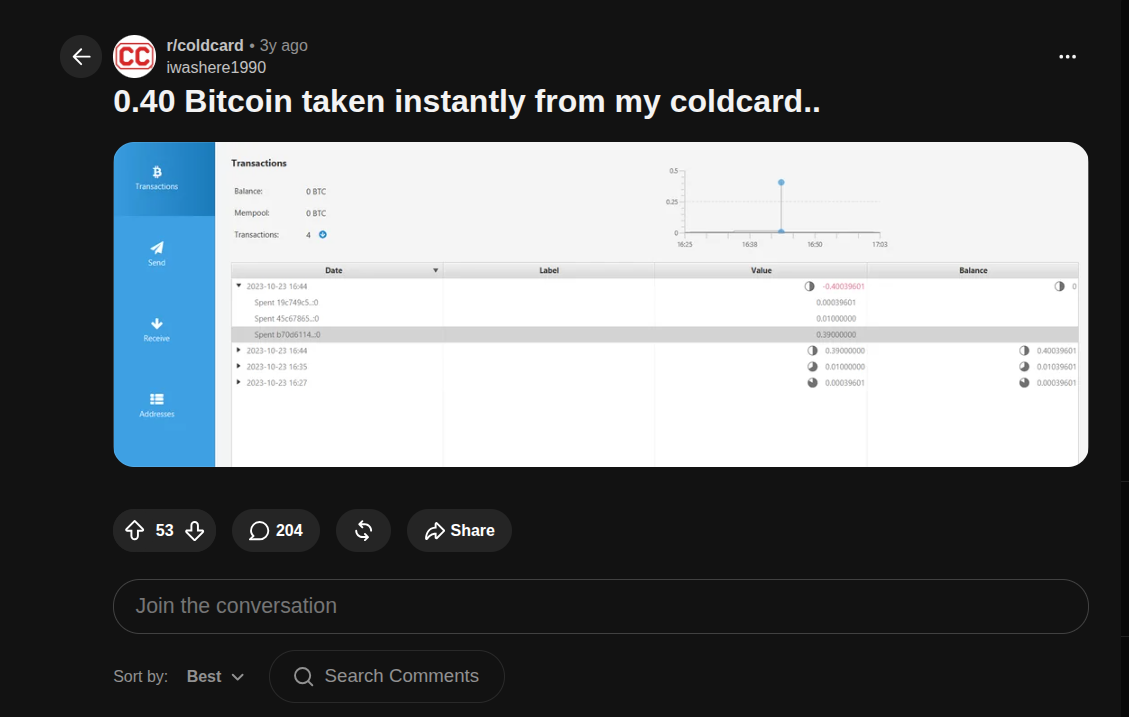\n\nhttps://www.reddit.com/r/coldcard/comments/17epqk8/040_bitcoin_taken_instantly_from_my_coldcard/", + "user": { + "name": "Scoresby" + } + } + ] + }, + "createdAt": "2026-08-02T14:14:38.703Z", + "text": "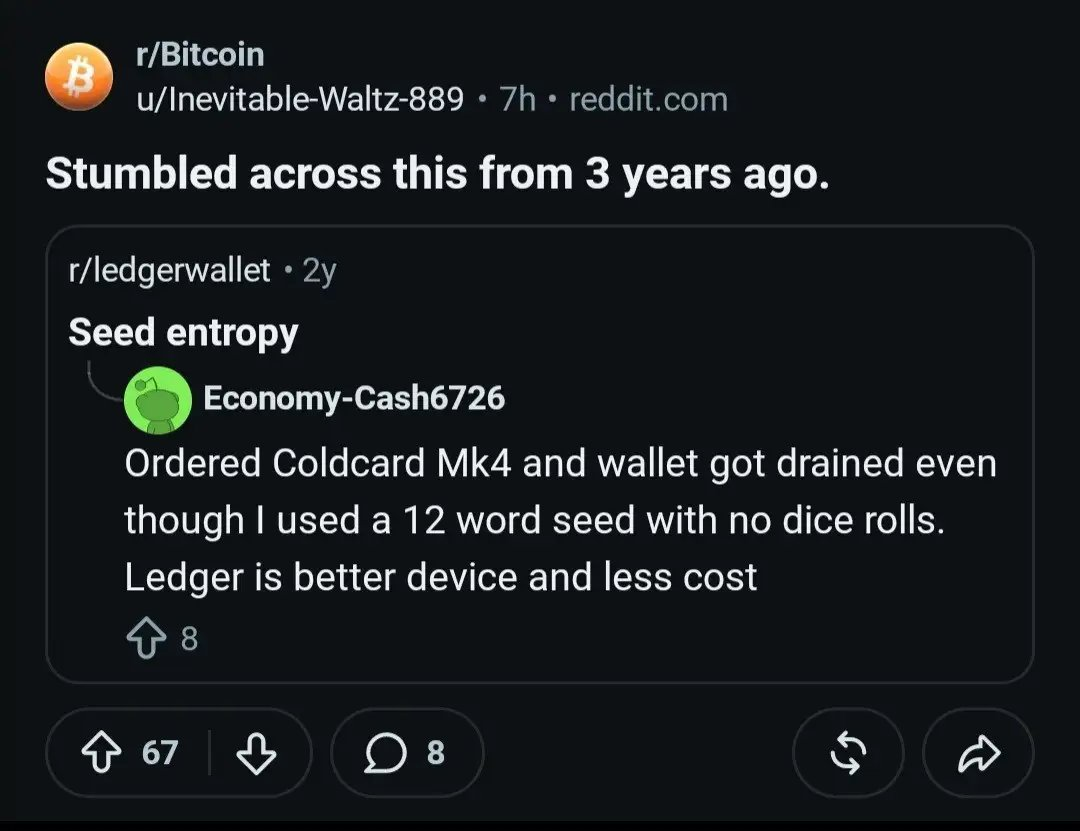\n\n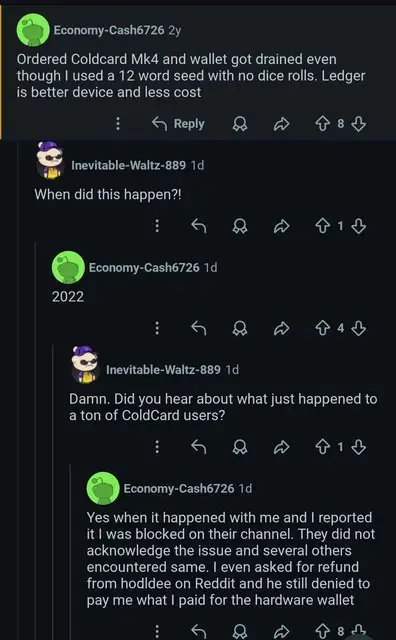\n\n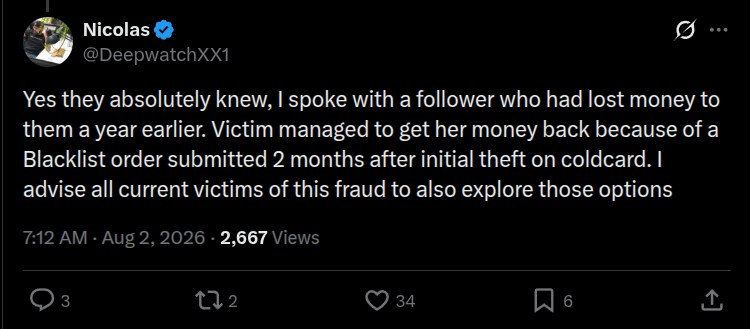\n\nThread: [https://x.com/Zenul\\_Abidin/status/2083756420843839872?s=20](https://x.com/Zenul_Abidin/status/2083756420843839872?s=20)\n\n\nRaises an interesting question, if they did know, and wanted to patch it... how could they release a patch that didn't automatically highlight the issue for attack? As soon as you tell users to upgrade and regen, or anyone capable sees the code diff, it'd be open season on all prior keys.", + "title": "ColdCard users have allegedly been reporting drains since 2022", + "user": { + "name": "justin_shocknet" + } + } + } +}Extracted text as captured
{ "data": { "item": { "comments": { "comments": [ { "createdAt": "2026-08-02T14:29:54.148Z", "text": "> Raises an interesting question, if they did know, and wanted to patch it\n\nWhat I find particularly interesting here is who did these drains 3 years ago?\n\n* Did an attacker know of this vulnerability and only slowly exploited it?\n* Or did Coldcard users create new wallets and found somebody elses wallet?", "user": { "name": "tomlaies" } }, { "createdAt": "2026-08-02T14:26:09.392Z", "text": "> how could they release a patch that didn't automatically highlight the issue for attack?\n\nSame way Core does it. Hide it in a refactor.", "user": { "name": "optimism" } }, { "createdAt": "2026-08-02T14:15:00.482Z", "text": "https://twiiit.com/Zenul_Abidin/status/2083756420843839872", "user": { "name": "nitter" } }, { "createdAt": "2026-08-02T14:19:28.335Z", "text": "I was talking to @optimism about someone potentially trying to replicate the attack for the purpose of safeguarding vulnerable funds and trying to return them later.\n\nIt’s a bad idea for a bunch of reasons, in the current context, but maybe ColdCard would have had to do something like that.", "user": { "name": "Undisciplined" } }, { "createdAt": "2026-08-02T14:25:40.385Z", "text": "I've been looking through a number of these this morning. I'm not sure that it's very convincing that the firmware was the problem -- it is also possible users screwed up.\n\n\n\nhttps://www.reddit.com/r/coldcard/comments/17epqk8/040_bitcoin_taken_instantly_from_my_coldcard/", "user": { "name": "Scoresby" } }Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 0 lines
Extracted text as captured
pull down to refresh

ColdCard users have allegedly been reporting drains since 2022
2297 sats \ 21 comments \ @justin_shocknet
 1h bitcoin -5000 sats

https://m.stacker.news/150556

https://m.stacker.news/150557

https://m.stacker.news/150559

Thread: https://x.com/Zenul_Abidin/status/2083756420843839872?s=20

Raises an interesting question, if they did know, and wanted to patch it... how could they release a patch that didn't automatically highlight the issue for attack? As soon as you tell users to upgrade and regen, or anyone capable sees the code diff, it'd be open season on all prior keys.

write
compose


speak now and forever hold your keys
reply 10 sats
related posts
1681 sats
LIT
NEW
TOP
1 sat \ 9 replies \ @tomlaies
 1h
Raises an interesting question, if they did know, and wanted to patch it

What I find particularly interesting here is who did these drains <relative-time>?

Did an attacker know of this vulnerability and only slowly exploited it?
Or did Coldcard users create new wallets and found somebody elses wallet?
reply
11 sats \ 8 replies \ @justin_shocknet
 OP 1h -420 sats
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
2 presentation-noise differences. Sidebar, ticker and other page chrome churn that our review classified as not being changes to what the source says.
- +11 -11 Only live counters and relative times changed: the post sats total moved from 2398 to 2426 and age labels advanced from 5h to 12h. Comment text was unchanged.
- +13 -13 Only live counters and relative times changed: sats totals moved on the post and comments (2297 to 2398 on the post, 11 to 254 on one comment) and age labels advanced from 1h to 5h. Comment text was unchanged.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.