GLM-5.2 was able to easily find the ColdCard vulnerability
stackernews-glm-ai-finds-vuln
- Organisation
- Stacker News
- Evidence role
- Community discussion
- Published
- 2026-08-03
- Source changes
- 0
- Detected differences
- 0
- Unreviewed
- 0
- Copies held
- 1
gmd reporting that GLM-5.2 found the vulnerability easily, following a similar demonstration with Claude Code linked via Reddit. Part of the record of AI tools independently locating the defect, which bears on how findable the bug was. The demonstrations are the reporters'. Captured through the site's public GraphQL API: the rendered pages crash the capture tab, and the API answers POST from this host. The query fixes the captured surface to the item's title, text and two levels of comments, each with author and absolute timestamp.
Every check is recorded, including checks that found no text change. A detected edit is therefore bounded between two checks. The publisher's exact save time is not observable from this record. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
Held captures
-
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 0 lines
Extracted text as captured
{ "data": { "item": { "comments": { "comments": [ { "createdAt": "2026-08-03T10:02:58.118Z", "text": "> Incredible that after months of hearing about Mythos vulnerability exploits they never bothered to do a simple AI security audit on their code\n\nThey did a `simple` one. It said \"all clear\". Defending is harder than attacking.", "user": { "name": "optimism" } }, { "createdAt": "2026-08-03T05:59:10.094Z", "text": "was there a websearch in the toolcalls?", "user": { "name": "kilianbuhn" } }, { "createdAt": "2026-08-03T02:19:05.982Z", "text": "https://x.com/SteveSimple/status/2083971557861269828", "user": { "name": "Bell_curve" } } ] }, "createdAt": "2026-08-03T00:56:10.196Z", "text": "Apologies for linking to /r/bitcoin lol\n\nSomeone first showed that Claude Code easily found the exploit after 8 minutes of thinking.\n[https://www.reddit.com/r/Bitcoin/comments/1vddeuy/are\\_you\\_kidding\\_me\\_claude\\_code\\_found\\_the/](https://www.reddit.com/r/Bitcoin/comments/1vddeuy/are_you_kidding_me_claude_code_found_the/)\n\n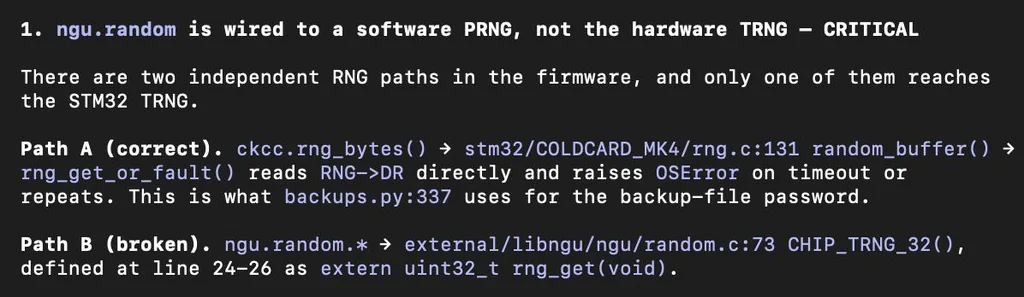\n\nAfter some discussion of whether Claude might have found the exploit from the recent news they tested this on GLM 5.2, trained June 16th, without internet access with a similar result\n[https://www.reddit.com/r/Bitcoin/comments/1vdes1l/update\\_to\\_my\\_last\\_post\\_glm52\\_trained\\_june\\_16th\\_no/](https://www.reddit.com/r/Bitcoin/comments/1vdes1l/update_to_my_last_post_glm52_trained_june_16th_no/)\n\n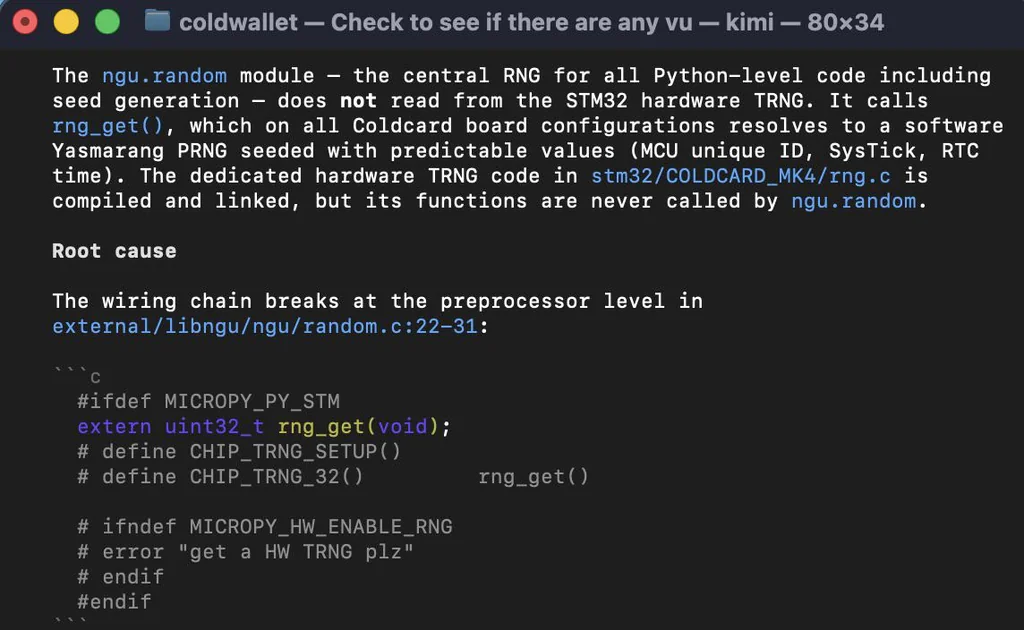\n\nIncredible that after months of hearing about Mythos vulnerability exploits they never bothered to do a simple AI security audit on their code\n\n🤦♂️🤦♂️🤦♂️", "title": "GLM-5.2 was able to easily find the ColdCard vulnerability", "user": { "name": "gmd" } } } }Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
0 presentation-noise differences. Sidebar, ticker and other page chrome churn that our review classified as not being changes to what the source says.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.