Allegation that CoinKite CTO wrote vulnerable dependency pseudonymously
oomahq-2085717166884618584
Latest reviewed change
source content difference between and
Four replies (from kiawtzin, Brandoniann1, Brandonwords and xolandar) were removed even though the capture deepened from 23 to 24 scroll rounds, while two older replies (MichaelDunwort1 and theretailbull) re-entered due to the deeper scroll.
 And after I was done I thought a non-vaguepost version of this information was needed.

-post: 2085755157296427477
-role: reply
-author: kiawtzin
-name: Kiawtzin - BIP110
-created: 2026-08-07T15:49:15Z
First lines only. The complete diff is in the timeline below.
- Author
- @oomahq
- Organisation
- independent
- Evidence role
- social statement
- Posted
- 7 Aug 2026, 13:18 UTC
- Capture status
- capture held
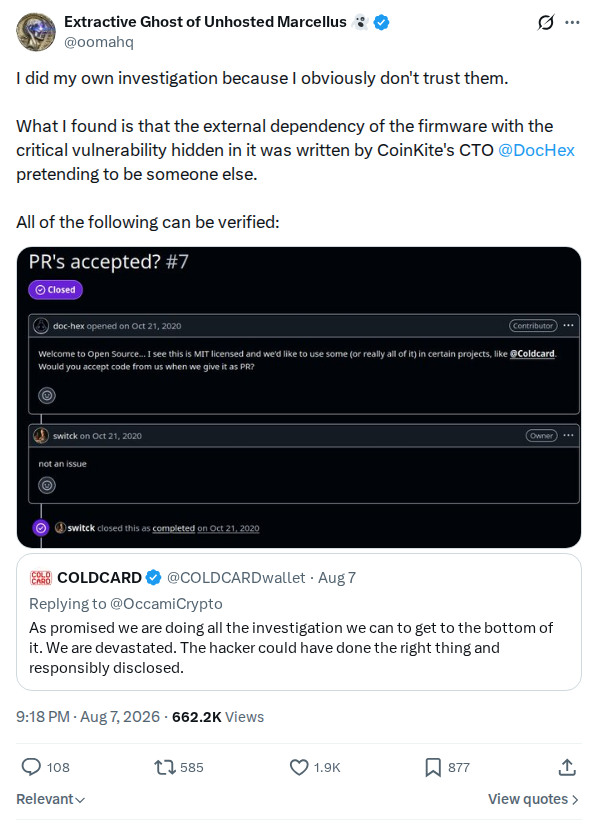
oomahq alleges that the external firmware dependency containing the critical vulnerability was written by CoinKite CTO Peter Gray under the @DocHex nym, and that the claim is verifiable. Held as a dated, specific attribution allegation made during the incident-response period, alongside the related oomahq-nvk-switck-knowledge-claim. The allegation and the cited evidence are the poster's own reading and are not independently verified here.
This post is registered as evidence and has a locally held capture. The original remains the canonical publication. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
The conversation
Captured . 6 continuation posts, 123 replies held, 49 muted as low signal. Posts are in the archive's own order, oldest first, not the order X ranks them in.
-
capture taken
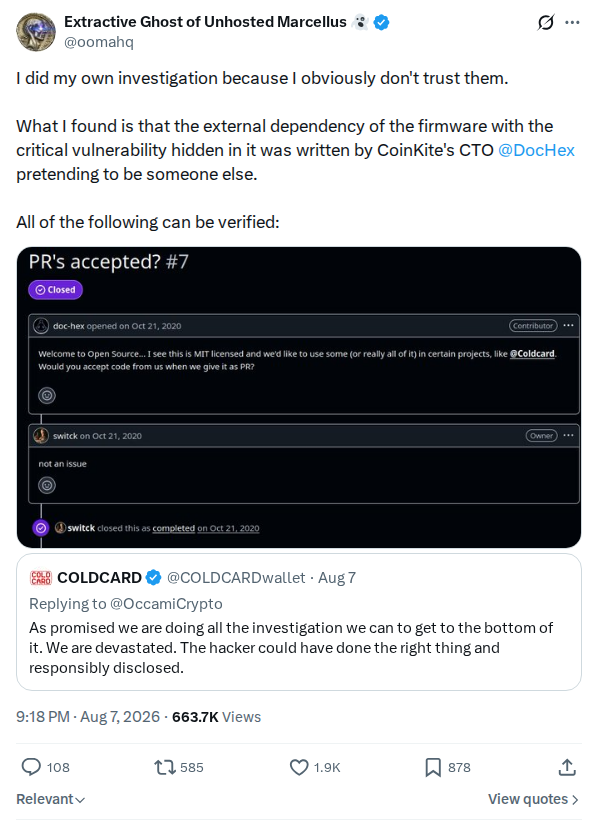
I did my own investigation because I obviously don't trust them. What I found is that the external dependency of the firmware with the critical vulnerability hidden in it was written by CoinKite's CTO @DocHex pretending to be someone else. All of the following can be verified:
-
capture taken
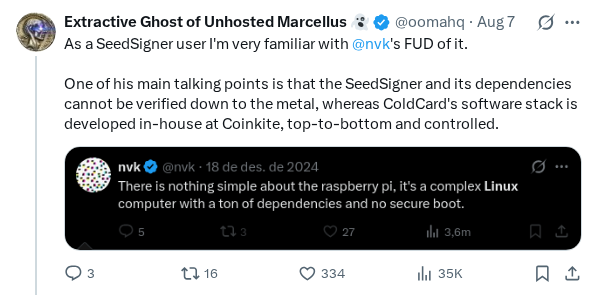
As a SeedSigner user I'm very familiar with @nvk 's FUD of it. One of his main talking points is that the SeedSigner and its dependencies cannot be verified down to the metal, whereas ColdCard's software stack is developed in-house at Coinkite, top-to-bottom and controlled.
-
capture taken
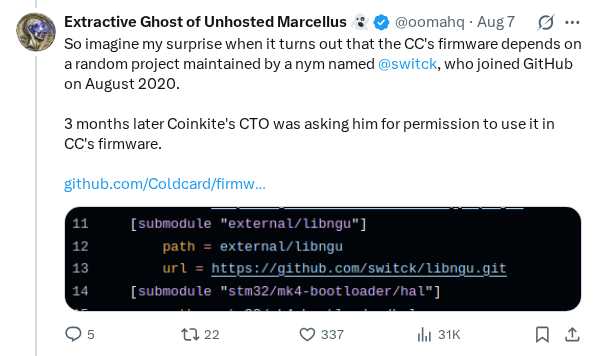
So imagine my surprise when it turns out that the CC's firmware depends on a random project maintained by a nym named @switck , who joined GitHub on August 2020. 3 months later Coinkite's CTO was asking him for permission to use it in CC's firmware. https:// github.com/Coldcard/firmw are/blob/dd2be687e1ed76fcca3aa0eef54d132936e81ee9/.gitmodules …
-
capture taken
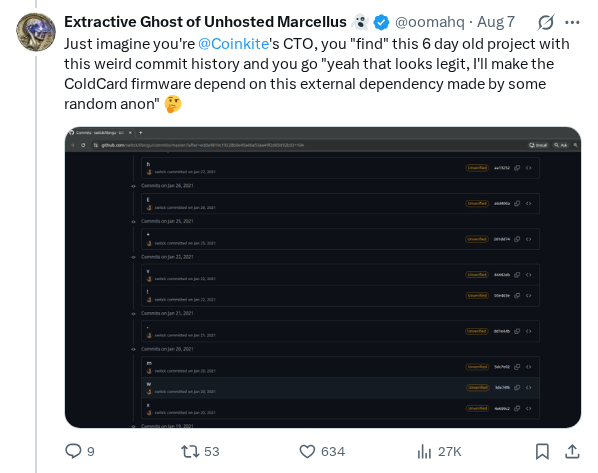
Just imagine you're @Coinkite 's CTO, you "find" this 6 day old project with this weird commit history and you go "yeah that looks legit, I'll make the ColdCard firmware depend on this external dependency made by some random anon"
-
capture taken
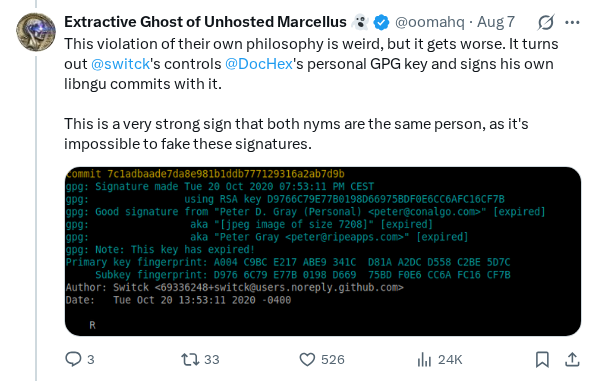
This violation of their own philosophy is weird, but it gets worse. It turns out @switck 's controls @DocHex 's personal GPG key and signs his own libngu commits with it. This is a very strong sign that both nyms are the same person, as it's impossible to fake these signatures.
-
capture taken
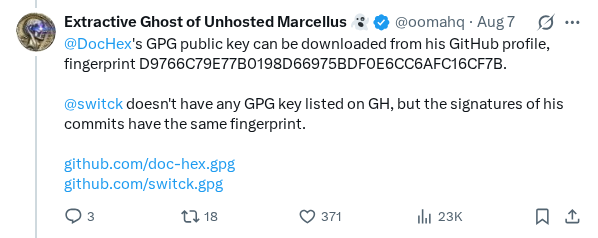
@DocHex 's GPG public key can be downloaded from his GitHub profile, fingerprint D9766C79E77B0198D66975BDF0E6CC6AFC16CF7B. @switck doesn't have any GPG key listed on GH, but the signatures of his commits have the same fingerprint. https:// github.com/doc-hex.gpg https:// github.com/switck.gpg
-
capture taken
So this article that was making the rounds a couple days ago completely misses the point. It's @Coinkite 's CTO who made this error, not a junior C developer. It was the senior CTO pretending to be a junior while he talked to himself in issues and PRs.
Replies held in this capture (123)
Low-signal replies are collapsed to one line, never removed. A reply is collapsed only on mechanical grounds: fewer than 40 characters, no text, mentions only, no letters or digits, a bare link, or text identical to another reply in the same capture. What a reply argues is never a reason. Each one says which rule collapsed it, and its screenshot is one click away.
-
capture taken
In Swift, you can use if expressions as assignments — a neat way to clean up your code. I’m planning more short Swift tips like this — would you like to see them?
show the capture
capture taken
-
capture taken
Is this real or AI? Even a year ago that wasn't what made you stop the scroll...but now it is. That's why we built Resemble AI Deepfake Detector for Chrome, available here (for free) > https:// chromewebstore.google.com/detail/resembl e-ai-deepfake-dete/ligejojghpehckjpfldljdcckgcbngle?twclid=23ghtw1si4e301qeqxj4fnel8s … Deepfakes are everywhere, but so are we.
show the capture
capture taken
-
capture taken
It's simple: Ship your app between Aug 1 - Sept 30. Compete for $1M+ in prizes. Win eternal fame and glory. (We can't promise the last one, but it's a likely outcome if you win) GET SHIPPING!
show the capture
capture taken
-
capture taken
Our loved ones don't always reach out for help when they're overwhelmed, worried they'll be a burden or ashamed of appearing weak. Everyone deserves help in difficult times, so we built: http:// secondaid.com /?twclid=298ds2wzzsbeddyyka2wz4slyb It's already helped 80,000+ people. Try it. Save it. Share it.
show the capture
capture taken
-
capture taken
Slanted design drains water fast - no more puddles, just dry, clean counters every time! Buy it here: https:// snuvnest.com/mat ?twclid=2e0eb57djtnobnwjl79ktpcy5e
show the capture
capture taken
-
capture taken
EWA — the app trusted by 60 MILLION learners worldwide! Learn English through your favorite movies & TV shows, 10,000+ books with audio, and fun games. Just 5 minutes a day — and you'll actually feel the progress!
show the capture
capture taken
-
capture taken
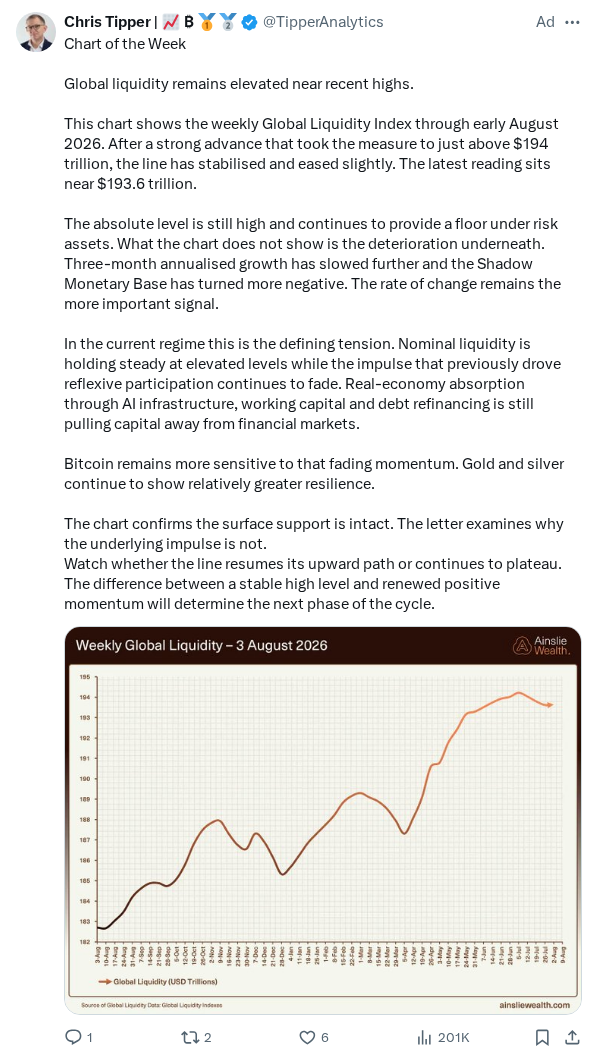
Chart of the Week Global liquidity remains elevated near recent highs. This chart shows the weekly Global Liquidity Index through early August 2026. After a strong advance that took the measure to just above $194 trillion, the line has stabilised and eased slightly. The latest reading sits near $193.6 trillion. The absolute level is still high and continues to provide a floor under risk assets. What the chart does not show is the deterioration underneath. Three-month annualised growth has slowed further and the Shadow Monetary Base has turned more negative. The rate of change remains the more important signal. In the current regime this is the defining tension. Nominal liquidity is holding steady at elevated levels while the impulse that previously drove reflexive participation continues to fade. Real-economy absorption through AI infrastructure, working capital and debt refinancing is still pulling capital away from financial markets. Bitcoin remains more sensitive to that fading momentum. Gold and silver continue to show relatively greater resilience. The chart confirms the surface support is intact. The letter examines why the underlying impulse is not. Watch whether the line resumes its upward path or continues to plateau. The difference between a stable high level and renewed positive momentum will determine the next phase of the cycle.
show the capture
capture taken
-
capture taken
Another detail that caught my eye was Peter Gray's personal email, [email protected] There's nothing much on that site, which according to the Internet Archive has been online since 2001. But it used to host an Easter Egg in it: @DocHex old resume. https:// conalgo.com
show the capture
capture taken
-
capture taken
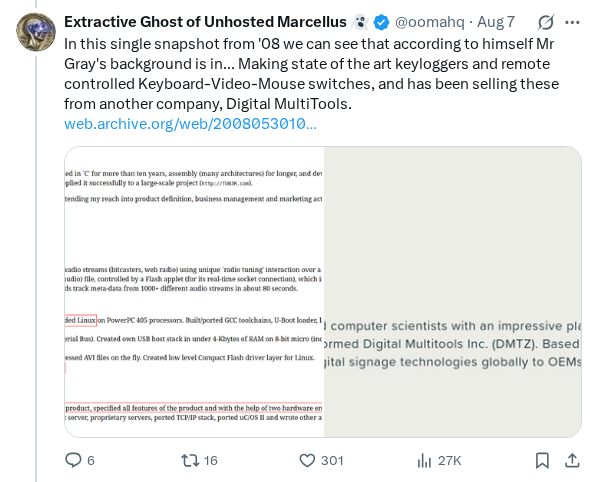
In this single snapshot from '08 we can see that according to himself Mr Gray's background is in... Making state of the art keyloggers and remote controlled Keyboard-Video-Mouse switches, and has been selling these from another company, Digital MultiTools. https:// web.archive.org/web/2008053010 5629/http://www.conalgo.com/resume/resume.html …
show the capture
capture taken
-
capture taken
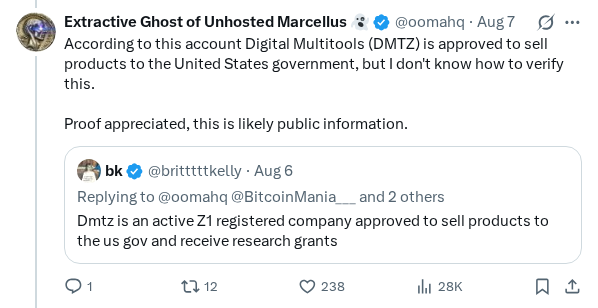
According to this account Digital Multitools (DMTZ) is approved to sell products to the United States government, but I don't know how to verify this. Proof appreciated, this is likely public information.
show the capture
capture taken
-
capture taken
In conclusion @Coinkite 's CTO wrote the vulnerable code himself trying to pass as someone else. He also has a background in making USB keyloggers, spooky KVM switches and most likely deals with the USG from another company. I'm sorry if all this is painful to take all at once.
show the capture
capture taken
-
capture taken
Spread the word and be very skeptical about anyone who downplays or suppresses this information. It was very easy to find. Spooks in Bitcoin are real, the ColdCard debacle confirms it. Thank you for reading and stay safe out there.
show the capture
capture taken
The remaining 111 replies
-
@oomahq glad your own research corroborates what has already been discovered first by someone else. Always verify.
show the capture
capture taken
-
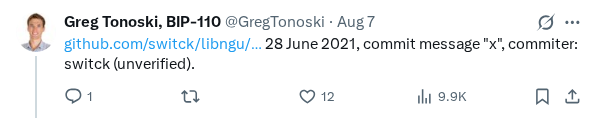
https:// github.com/switck/libngu/ blame/0371d6372eb7c1165f9c0410f6d6537e09882402/ngu/random.c#L30 … 28 June 2021, commit message "x", commiter: switck (unverified).
show the capture
capture taken
-
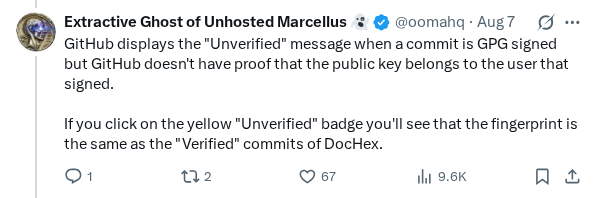
GitHub displays the "Unverified" message when a commit is GPG signed but GitHub doesn't have proof that the public key belongs to the user that signed. If you click on the yellow "Unverified" badge you'll see that the fingerprint is the same as the "Verified" commits of DocHex.
show the capture
capture taken
-
Yup, this tweet is part of what made me start digging. And after I was done I thought a non-vaguepost version of this information was needed.
show the capture
capture taken
-
Sick
show the capture
capture taken
-
Rip new startups focusing on hardware wallet and @Trezor and companies working and already established will take the whole cake
show the capture
capture taken
-
show the capture
capture taken
-
show the capture
capture taken
-
@grok is this true?
show the capture
capture taken
-
gut undefeated
show the capture
capture taken
-
excellent work
show the capture
capture taken
-
Nvk gloating about this in a sly roundabout way.."One gray beard"
show the capture
capture taken
-
X account not found in 3…2…
show the capture
capture taken
-
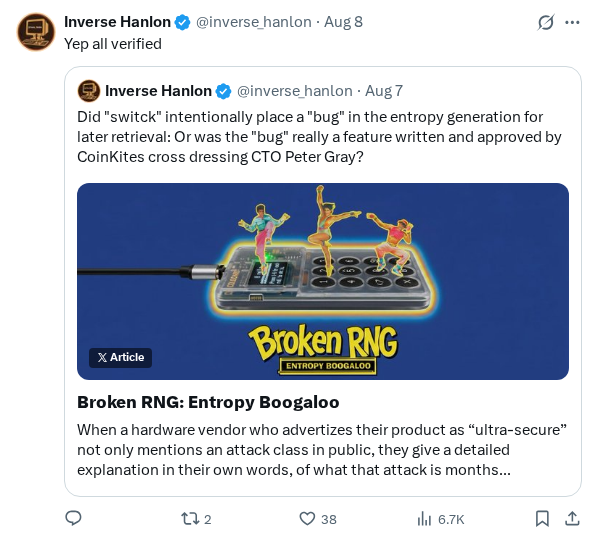
Yep all verified
show the capture
capture taken
-
Next it'll be confirmed dude is Mossad.
show the capture
capture taken
-
I’m beginning to think that the deep state actually wants you to lose trust in self custody which is the one thing which makes one truly sovereign. And this is want to they want to kill. AI/quantum/coldcard hack… any threat or scandal to scare you out of self custody bitcoin.
show the capture
capture taken
-
Apart from the fact that this vulnerability was exploited, I find it alarming that so few people have familiarised themselves with the open source code and that everything relied on trust me bro.
show the capture
capture taken
-
show the capture
capture taken
-
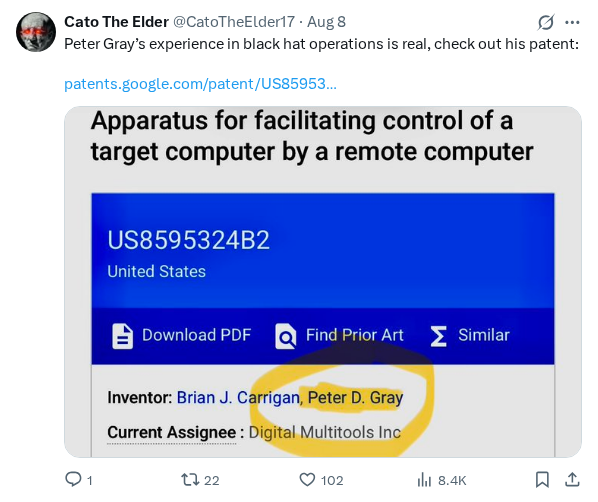
Peter Gray’s experience in black hat operations is real, check out his patent: https:// patents.google.com/patent/US85953 24B2/en …
show the capture
capture taken
-
show the capture
capture taken
-
These two rats likely run to a particular desert country soon
show the capture
capture taken
-
Looking like many useful idiots among podcasters
show the capture
capture taken
-
@ozsats256 99/1 now
show the capture
capture taken
-
People thought “Canadian company, must be safe”. Turns out it was likely a State sponsored attack, and preplanned before BIP110, scooping coins onto exchanges. Now a Chinese company like Keystone is and was always, the safer choice.
show the capture
capture taken
-
What’s the next move? Reach out to @DocHex ? Go straight to authorities?
show the capture
capture taken
-
Humiliation ritual.
show the capture
capture taken
-
@threadreaderapp unroll
show the capture
capture taken
-
That whole SLT are pieces of shit. Scum of the earth. Deserve to go to prison.
show the capture
capture taken
-
Smoking gun
show the capture
capture taken
-
@noD7R
show the capture
capture taken
-
show the capture
capture taken
-
Thank you for your service.
show the capture
capture taken
-
Do these guys live chill after this kind of stuff ? I mean, considering a lot of bitcoin holders are pretty bad guys, I would never wanna live my life having to watch my back 24/7.
show the capture
capture taken
-
Whenever I see something marketed heavily, I get paranoid. Coldcard was that for me and stayed away from it.
show the capture
capture taken
-
show the capture
capture taken
-
You're the best
show the capture
capture taken
-
I seriously considered getting one. But I move slow
show the capture
capture taken
-
@R38TAO
show the capture
capture taken
-
omg
show the capture
capture taken
-
Thanks but intuitively this was obvious from the start
show the capture
capture taken
-
He thought he was being slick.
show the capture
capture taken
-
Look when switck stopped posting on X.
show the capture
capture taken
-
This is so so so so so bad.
show the capture
capture taken
-
Excellent forensics
show the capture
capture taken
-
Expedite the man to the French!
show the capture
capture taken
-
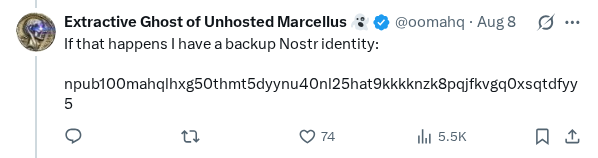
If that happens I have a backup Nostr identity: npub100mahqlhxg50thmt5dyynu40nl25hat9kkkknzk8pqjfkvgq0xsqtdfyy5
show the capture
capture taken
-
Jesus.
show the capture
capture taken
-
Ooph! This is going to be damning during the forthcoming lawsuits!
show the capture
capture taken
-
Interesting his name is Gray. Which is a mix of white and black.
show the capture
capture taken
-
We need the #osint community to dig and see if there is a #CIA connection.
show the capture
capture taken
-
Yo @grok what here is true?
show the capture
capture taken
-
Can we trust anything these days?
show the capture
capture taken
-
@DocHex needs to answer to this.
show the capture
capture taken
-
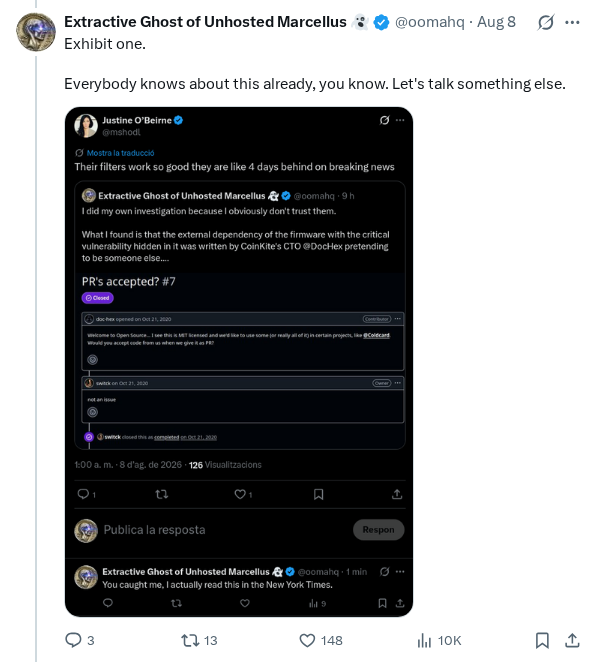
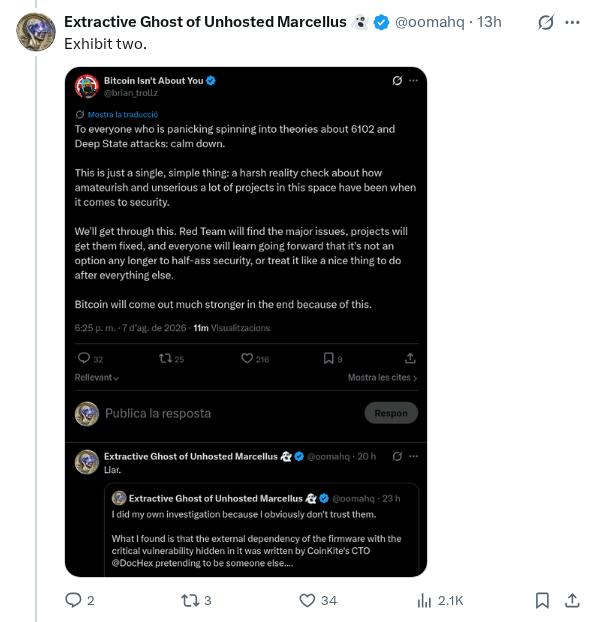
Exhibit one. Everybody knows about this already, you know. Let's talk something else.
show the capture
capture taken
-
He will be running to Tel Aviv
show the capture
capture taken
-
Has anyone seen this guy in the last week?
show the capture
capture taken
-
This has Israel written all over it.
show the capture
capture taken
-
Tldr:
show the capture
capture taken
-
This @dochex @switck guy is literally the evil counterpart to @halfin and satoshi.
show the capture
capture taken
-
show the capture
capture taken
-
I'd be happy if did it irresponsibly or responsibly.
show the capture
capture taken
-
@twitt_tr some nerd stuff you probably find interesting
show the capture
capture taken
-
Is there any chance, the bug was there. Then he impersonated himself, now he introduces a clear place where the bug is traceable and as part of a white hat rescue, recovers all the wallets? In this way, the rescue is within the same company but operated in the shadow.
show the capture
capture taken
-
THIS HACK WAS PROMISED TO THEM 3000 YEARS AGO.
show the capture
capture taken
-
show the capture
capture taken
-
Is Jon Stewart the only honest one in their group? He has empathy. Nobody else does.
show the capture
capture taken
-
That peter gray replying to himself is the biggest clue
show the capture
capture taken
-
Cryptographic signatures are undeniable. So… unless there’s another explanation, this is starting to smell like an insider job. Interesting.
show the capture
capture taken
-
@Mmagnet7 Inside job just as I said
show the capture
capture taken
-
looks so incredibly shady, the chance of a dev accidentally setting 0 instead of 1 and also having a insanely insufficient fallback option is too much of a coincidence
show the capture
capture taken
-
That is absolutely insane . Thanks for sharing this research.
show the capture
capture taken
-
wait till you find out @DocHex is an @nvk alt account
show the capture
capture taken
-
@jackmallers
show the capture
capture taken
-
The obvious question: Has anyone ever seen Peter Gray and NVK in the same room?
show the capture
capture taken
-
Waiting for them to disprove it...still waiting...still waiting...
show the capture
capture taken
-
I doubt this because once the cat was out of the bag on July 30-31th anyone in the world with half a clue could start sweeping UTXOs. It's next to impossible that they've all been swept by the same entity. It's also impossible to clearly identify all the sweeping txs if the thieves are careful.
show the capture
capture taken
-
@hodlonaut
show the capture
capture taken
-
wow what an investigation - I am still trying to understand it all but its already very interesting and I assumed this to be an inside job from the moment I tried to reproduce the bug and understand it better and must say, it seemed weird to me that someone randomly found and exploited it.
show the capture
capture taken
-
pretty damn damning
show the capture
capture taken
-
Wow this is incredible work. Free Samourai, make room for the real criminals
show the capture
capture taken
-
Viste @PabloSabbatella
show the capture
capture taken
-
This is what I was thinking man. It was an odd class of “bug” on the only thing the software was supposed to do. I was 50-50 but now I’m 70-30
show the capture
capture taken
-
I lost $17,000 on their platform and did my own firmeware analysis of the code and its bypass structures. I realised they had nothing to offer in terms of security and after filing my AP order. My crypto was frozen on 2 websites, literally at a point of sale. My independent investigators at that time also linked the identities to 2 ip addresses, located near their own facility
show the capture
capture taken
-
@galgitron called it
show the capture
capture taken
-
Thank you for your work here man
show the capture
capture taken
-
Also worth noting that CoinKite is from Canada and with X’s new country feature you can see that @switck is also from Canada
show the capture
capture taken
-
I tested it using Yasmarang PRNG, used different seeds and timestamps, believe me, it's real if someone knows the PRNG used.. It has atypical state of 32-bit which is easily exhausted.
show the capture
capture taken
-
And now this brings us to another query, is there any other wallet that uses PRNG like LCG, Xorshift32, SFC32, PCG32 etc. All this can be exploited in hours.
show the capture
capture taken
-
So did you actually mine some drained wallets?
show the capture
capture taken
-
My pleasure.
show the capture
capture taken
-
legendary work sir
show the capture
capture taken
-
Thank you, Pav.
show the capture
capture taken
-
Thanks for the writeup. You should probably read this if you haven’t https:// cryptome.org/2012/07/gent-f orum-spies.htm …
show the capture
capture taken
-
@bitdov é muita teoria da conspiração? Será?
show the capture
capture taken
-
I wonder how many wallets dochex has swiped over the years with his exploit. Maybe that’s why that gaslit anyone who discovered their coldcard stack mysteriously swiped.
show the capture
capture taken
-
You guys are so fucking smart. How do you even begin to start a process like this
show the capture
capture taken
-
Exhibit two.
show the capture
capture taken
-
^ @mshodl maybe you clown can explain why Shitnobi was spreading this nonsense if everything in my thread was already known to him 5 days ago, by your own account.
show the capture
capture taken
-
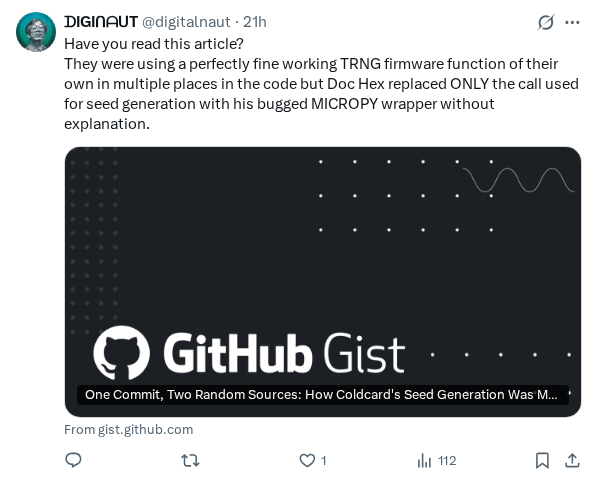
Have you read this article? They were using a perfectly fine working TRNG firmware function of their own in multiple places in the code but Doc Hex replaced ONLY the call used for seed generation with his bugged MICROPY wrapper without explanation.
show the capture
capture taken
-
Don’t do your own research. The vulnerability wasnt in the external dependency
show the capture
capture taken
-
Will they be arrested for this??
show the capture
capture taken
-
@berm_blazer .
show the capture
capture taken
-
Is @FBI or @DOJFraudDiv looking into this? (unless fedbois were involved somehow.. of course)
show the capture
capture taken
-
@grok vies mi zhrnúť tento thread?
show the capture
capture taken
-
Forgive my ignorance, I do see how this is suspect, but if the wallets where the swept funds are being watched like a hawk, how do the perps spend it? Or do they not care about that, the intention was to try and disrupt/discredit Bitcoin in general?
show the capture
capture taken
-
Someone tell the @FBI
show the capture
capture taken
-
Wow... words fail me.
show the capture
capture taken
-
Hey
show the capture
capture taken
-
Stop juggling multiple systems. Your entire truck and civil business... One login...now with live GPS tracking
show the capture
capture taken
-
Get Pro Workspace, early access, & featured work. Lottie Squad is now open worldwide. For designers, developers & motion lovers. Application link in the comments If you got into Squad, what would you build first?
show the capture
capture taken
-
I just launched AfterShot — a shared event camera for weddings, parties, birthdays, and trips. Invite guests by link or QR code and collect everyone’s photos and videos in one private album.
show the capture
capture taken
This capture reached the end of the conversation as X served it: it stopped because nothing further loaded, not because a limit was hit. X decides what a reader is shown, so that is not the same as a guarantee of every reply.
Held captures
-
Four replies (from kiawtzin, Brandoniann1, Brandonwords and xolandar) were removed even though the capture deepened from 23 to 24 scroll rounds, while two older replies (MichaelDunwort1 and theretailbull) re-entered due to the deeper scroll.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 55 lines
 And after I was done I thought a non-vaguepost version of this information was needed.

-post: 2085755157296427477
-role: reply
-author: kiawtzin
-name: Kiawtzin - BIP110
-created: 2026-08-07T15:49:15Z
-media: 0
-body:
-Sick
-
 post: 2085778395825054109
 role: reply
 author: PrivacyisBetter
 body:
 Looking like many useful idiots among podcasters

+post: 2085798708059459964
+role: reply
+author: MichaelDunwort1
+name: Michael Dunworth
+created: 2026-08-07T18:42:18Z
+media: 0
+body:
+@ozsats256
+ 99/1 now
+
 post: 2085799334025842914
 role: reply
 author: jstamby
 body:
 You're the best

-post: 2085819407373054120
-role: reply
-author: Brandoniann1
-name: Braindoniann
-created: 2026-08-07T20:04:34Z
-media: 0
-body:
-I seriously considered getting one. But I move slow
-
 post: 2085820979641819200
 role: reply
 author: vera_rostova
 body:
 He thought he was being slick.

+post: 2085832812280561894
+role: reply
+author: theretailbull
+name: Tim Lamb
+created: 2026-08-07T20:57:50Z
+media: 0
+body:
+Look when switck stopped posting on X.
+
 post: 2085835412090577304
 role: reply
 author: GRIDsquad
 media: 0
 body:
 Has anyone seen this guy in the last week?
-
-post: 2085883885091741732
-role: reply
-author: Brandonwords
-name: Bangkok Carnivore
-created: 2026-08-08T00:20:46Z
-media: 0
-body:
-This has Israel written all over it.
-
-post: 2085884563675349020
-role: reply
-author: xolandar
-name: Xolandar
-created: 2026-08-08T00:23:28Z
-media: 1
-body:
-Tldr:

 post: 2085886339959185560
 role: reply
Extracted text as captured
thread: 2085717166884618584
url: https://x.com/oomahq/status/2085717166884618584
author: oomahq

post: 2085717166884618584
role: focal
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:18:17Z
media: 1
body:
I did my own investigation because I obviously don't trust them.

What I found is that the external dependency of the firmware with the critical vulnerability hidden in it was written by CoinKite's CTO
@DocHex
 pretending to be someone else.

All of the following can be verified:

post: 2085717418123383008
role: self-thread
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:19:17Z
media: 1
body:
As a SeedSigner user I'm very familiar with
@nvk
's FUD of it.

One of his main talking points is that the SeedSigner and its dependencies cannot be verified down to the metal, whereas ColdCard's software stack is developed in-house at Coinkite, top-to-bottom and controlled.

post: 2085717576449995123
role: self-thread
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:19:55Z
media: 1
body:
So imagine my surprise when it turns out that the CC's firmware depends on a random project maintained by a nym named
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
Two reply authors changed their display names: GregTonoski added 'Blake2b' to 'Greg Tonoski, BIP-110', and Delcin changed '#BIP110' to '#Observer'.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 32 lines
 post: 2085727326130598068
 role: reply
 author: GregTonoski
-name: Greg Tonoski, BIP-110
+name: Greg Tonoski, BIP-110, Blake2b
 created: 2026-08-07T13:58:40Z
 media: 0
 body:
 body:
 Looking like many useful idiots among podcasters

-post: 2085798708059459964
-role: reply
-author: MichaelDunwort1
-name: Michael Dunworth
-created: 2026-08-07T18:42:18Z
-media: 0
-body:
-@ozsats256
- 99/1 now
-
 post: 2085799334025842914
 role: reply
 author: jstamby
 body:
 He thought he was being slick.

-post: 2085832812280561894
-role: reply
-author: theretailbull
-name: Tim Lamb
-created: 2026-08-07T20:57:50Z
-media: 0
-body:
-Look when switck stopped posting on X.
-
 post: 2085835412090577304
 role: reply
 author: GRIDsquad
 Exhibit one.

 Everybody knows about this already, you know. Let's talk something else.
-
-post: 2085873969941606436
-role: reply
-author: BeachMaster893
-name: Congo_Dandy
-created: 2026-08-07T23:41:22Z
-media: 0
-body:
-He will be running to Tel Aviv

 post: 2085881105132233214
 role: reply
 post: 2086114171708682395
 role: reply
 author: DelcinMaria
-name: Delcin #BIP110
+name: Delcin #Observer
 created: 2026-08-08T15:35:51Z
 media: 0
 body:
Extracted text as captured
thread: 2085717166884618584
url: https://x.com/oomahq/status/2085717166884618584
author: oomahq

post: 2085717166884618584
role: focal
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:18:17Z
media: 1
body:
I did my own investigation because I obviously don't trust them.

What I found is that the external dependency of the firmware with the critical vulnerability hidden in it was written by CoinKite's CTO
@DocHex
 pretending to be someone else.

All of the following can be verified:

post: 2085717418123383008
role: self-thread
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:19:17Z
media: 1
body:
As a SeedSigner user I'm very familiar with
@nvk
's FUD of it.

One of his main talking points is that the SeedSigner and its dependencies cannot be verified down to the metal, whereas ColdCard's software stack is developed in-house at Coinkite, top-to-bottom and controlled.

post: 2085717576449995123
role: self-thread
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:19:55Z
media: 1
body:
So imagine my surprise when it turns out that the CC's firmware depends on a random project maintained by a nym named
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
The thread lost one reply and gained five additional replies, plus one display-name change.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 56 lines
 post: 2085781515502235977
 role: reply
 author: djsenior13
-name: David - Satoshi Services
+name: David
 created: 2026-08-07T17:33:59Z
 media: 0
 body:


-post: 2085803131741348283
-role: reply
-author: GigmaSigachad
-name: Windows Explorer
-created: 2026-08-07T18:59:53Z
-media: 0
-body:
-Man there’s jews deserve prison
-
 post: 2085805005802541288
 role: reply
 author: GotAll21
 body:
 omg

+post: 2085824906327986203
+role: reply
+author: EGrey3717
+name: Edever Grey
+created: 2026-08-07T20:26:25Z
+media: 0
+body:
+Thanks but intuitively this was obvious from the start
+
 post: 2085827728415064074
 role: reply
 author: DutyToRebel
 media: 0
 body:
 Has anyone seen this guy in the last week?
+
+post: 2085883885091741732
+role: reply
+author: Brandonwords
+name: Bangkok Carnivore
+created: 2026-08-08T00:20:46Z
+media: 0
+body:
+This has Israel written all over it.

 post: 2085884563675349020
 role: reply
 body:


+post: 2085961700810064378
+role: reply
+author: Annathehumanist
+name: pricesearch.net
+created: 2026-08-08T05:29:59Z
+media: 0
+body:
+Is Jon Stewart the only honest one in their group? He has empathy. Nobody else does.
+
 post: 2085965012347359464
 role: reply
 author: guitarstar87
 @nvk
  alt account

+post: 2086005374360989950
+role: reply
+author: 9FigureSats
+name: DatSupraKid
+created: 2026-08-08T08:23:32Z
+media: 0
+body:
+@jackmallers
+
 post: 2086007718104473737
 role: reply
 author: MichaelRoerade
 media: 0
 body:
 Wow... words fail me.
+
+post: 2086909727619895583
+role: reply
+author: SavannahSmhi
+name: Savannah Smith
+created: 2026-08-10T20:17:06Z
+media: 0
+body:
+Hey
Extracted text as captured
thread: 2085717166884618584
url: https://x.com/oomahq/status/2085717166884618584
author: oomahq

post: 2085717166884618584
role: focal
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:18:17Z
media: 1
body:
I did my own investigation because I obviously don't trust them.

What I found is that the external dependency of the firmware with the critical vulnerability hidden in it was written by CoinKite's CTO
@DocHex
 pretending to be someone else.

All of the following can be verified:

post: 2085717418123383008
role: self-thread
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:19:17Z
media: 1
body:
As a SeedSigner user I'm very familiar with
@nvk
's FUD of it.

One of his main talking points is that the SeedSigner and its dependencies cannot be verified down to the metal, whereas ColdCard's software stack is developed in-house at Coinkite, top-to-bottom and controlled.

post: 2085717576449995123
role: self-thread
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:19:55Z
media: 1
body:
So imagine my surprise when it turns out that the CC's firmware depends on a random project maintained by a nym named
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
A new reply by LibertyTrek was added and two users' display names lost their BIP110 suffixes, while two older replies are missing in a capture that stopped one scroll round earlier.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 31 lines
 post: 2085827728415064074
 role: reply
 author: DutyToRebel
-name: Duty to Re₿el #BIP110
+name: Duty to Re₿el
 created: 2026-08-07T20:37:37Z
 media: 0
 body:
 media: 0
 body:
 Has anyone seen this guy in the last week?
-
-post: 2085883885091741732
-role: reply
-author: Brandonwords
-name: Bangkok Carnivore - BIP110
-created: 2026-08-08T00:20:46Z
-media: 0
-body:
-This has Israel written all over it.

 post: 2085884563675349020
 role: reply
 @nvk
  alt account

-post: 2086005374360989950
-role: reply
-author: 9FigureSats
-name: DatSupraKid
-created: 2026-08-08T08:23:32Z
-media: 0
-body:
-@jackmallers
-
 post: 2086007718104473737
 role: reply
 author: MichaelRoerade
 post: 2086027079649231275
 role: reply
 author: roger__9000
-name: ROGER 9000  + ₿IP-110
+name: ROGER 9000
 created: 2026-08-08T09:49:46Z
 media: 0
 body:
 body:
 Someone tell the
 @FBI
+
+post: 2086440709175787948
+role: reply
+author: LibertyTrek
+name: LibertyTrek
+created: 2026-08-09T13:13:23Z
+media: 0
+body:
+Wow... words fail me.
Extracted text as captured
thread: 2085717166884618584
url: https://x.com/oomahq/status/2085717166884618584
author: oomahq

post: 2085717166884618584
role: focal
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:18:17Z
media: 1
body:
I did my own investigation because I obviously don't trust them.

What I found is that the external dependency of the firmware with the critical vulnerability hidden in it was written by CoinKite's CTO
@DocHex
 pretending to be someone else.

All of the following can be verified:

post: 2085717418123383008
role: self-thread
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:19:17Z
media: 1
body:
As a SeedSigner user I'm very familiar with
@nvk
's FUD of it.

One of his main talking points is that the SeedSigner and its dependencies cannot be verified down to the metal, whereas ColdCard's software stack is developed in-house at Coinkite, top-to-bottom and controlled.

post: 2085717576449995123
role: self-thread
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:19:55Z
media: 1
body:
So imagine my surprise when it turns out that the CC's firmware depends on a random project maintained by a nym named
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 0 lines
Extracted text as captured
thread: 2085717166884618584
url: https://x.com/oomahq/status/2085717166884618584
author: oomahq

post: 2085717166884618584
role: focal
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:18:17Z
media: 1
body:
I did my own investigation because I obviously don't trust them.

What I found is that the external dependency of the firmware with the critical vulnerability hidden in it was written by CoinKite's CTO
@DocHex
 pretending to be someone else.

All of the following can be verified:

post: 2085717418123383008
role: self-thread
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:19:17Z
media: 1
body:
As a SeedSigner user I'm very familiar with
@nvk
's FUD of it.

One of his main talking points is that the SeedSigner and its dependencies cannot be verified down to the metal, whereas ColdCard's software stack is developed in-house at Coinkite, top-to-bottom and controlled.

post: 2085717576449995123
role: self-thread
author: oomahq
name: Extractive Ghost of Unhosted Marcellus
created: 2026-08-07T13:19:55Z
media: 1
body:
So imagine my surprise when it turns out that the CC's firmware depends on a random project maintained by a nym named
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
6 presentation-noise differences. Sidebar, ticker and other page chrome churn that our review classified as not being changes to what the source says.
- +128 -107 Multiple promotional reply records were swapped and a few short replies left the capture, but capped remained false and scroll rounds fell from 21 to 19 while posts_observed fell from 131 to 130, indicating ranking/selection churn rather than new content.
- +129 -0 The capture recovered several promotional reply records that the previous pass missed; capped remained false, posts_observed rose from 120 to 131, and scroll rounds fell from 27 to 21, indicating ranking/selection churn rather than new content.
- +27 -0 Three older reply records re-entered the capture after the later poll scrolled deeper (27 rounds and 113 replies observed) than the earlier one (23 rounds and 110 replies); capped was false both times, so the difference is ranking recovery rather than new posts.
- +18 -0 Old replies by Brandoniann1 and xolandar that had dropped out of the preceding capture reappeared while scroll rounds fell from 24 to 23, showing ranking churn rather than new posts.
- +107 -0 The deeper capture (17 scroll rounds vs 14) recovered older replies and a few newer August 9 replies; the depth records show ranking recovery, not pure new content.
- +209 -34 The later capture scrolled one round deeper and observed 99 replies versus 80; all added and removed replies predate the previous capture, so the difference is ranking and depth recovery rather than new content.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.