Latest reviewed change
source content difference between and
Asanoha's display name changed to include 'Timechain Art Magazine', and the reply by IphigenAleksy to that account is no longer present in a same-depth capture (37 scroll rounds).
 post: 2083353279573155874
 role: reply
 author: asanoha_gold
-name: Asanoha
+name: Asanoha | Timechain Art Magazine
 created: 2026-08-01T00:45:03Z
 media: 0
 body:
First lines only. The complete diff is in the timeline below.
- Author
- @clay_garrett
- Organisation
- Block
- Evidence role
- social statement
- Posted
- 31 Jul 2026, 17:42 UTC
- Capture status
- capture held
Block's report that the operator used a paid blockchain-services account; the complete thread says the provider's logs matched the workflow and that Block saw no evidence of knowing participation.
This post is registered as evidence and has a locally held capture. The original remains the canonical publication. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
The conversation
Captured . 2 continuation posts, 166 replies held, 75 muted as low signal. Posts are in the archive's own order, oldest first, not the order X ranks them in.
-
capture taken
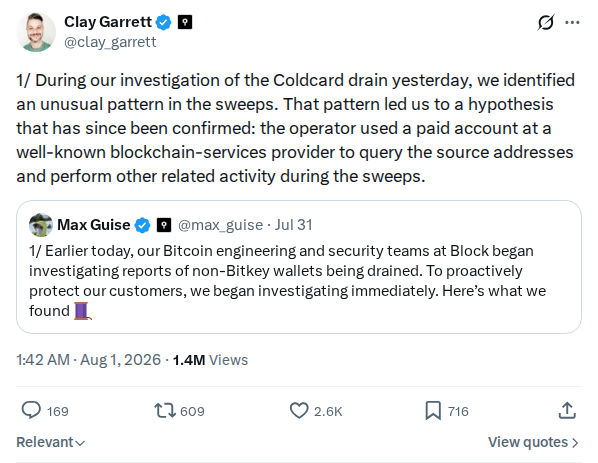
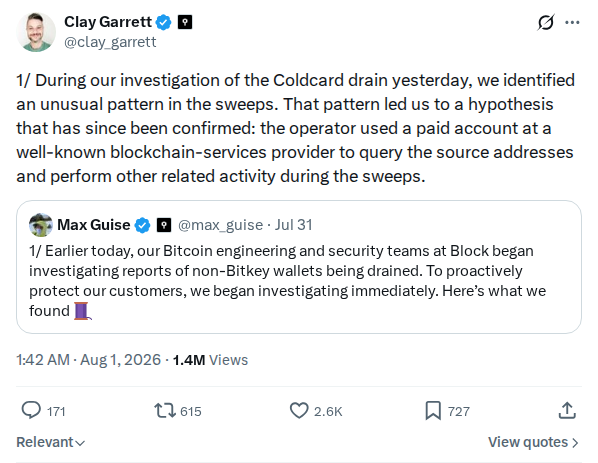
1/ During our investigation of the Coldcard drain yesterday, we identified an unusual pattern in the sweeps. That pattern led us to a hypothesis that has since been confirmed: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps.
-
capture taken
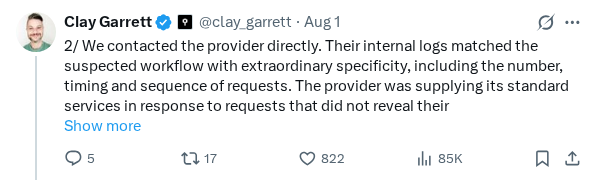
2/ We contacted the provider directly. Their internal logs matched the suspected workflow with extraordinary specificity, including the number, timing and sequence of requests. The provider was supplying its standard services in response to requests that did not reveal their broader purpose. We have seen no evidence that the provider knowingly participated in or facilitated the suspected theft.
-
capture taken
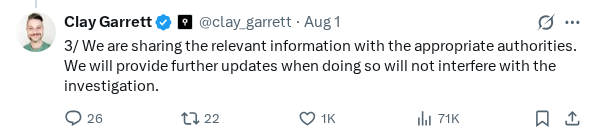
3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.
Replies held in this capture (166)
Low-signal replies are collapsed to one line, never removed. A reply is collapsed only on mechanical grounds: fewer than 40 characters, no text, mentions only, no letters or digits, a bare link, or text identical to another reply in the same capture. What a reply argues is never a reason. Each one says which rule collapsed it, and its screenshot is one click away.
-
capture taken
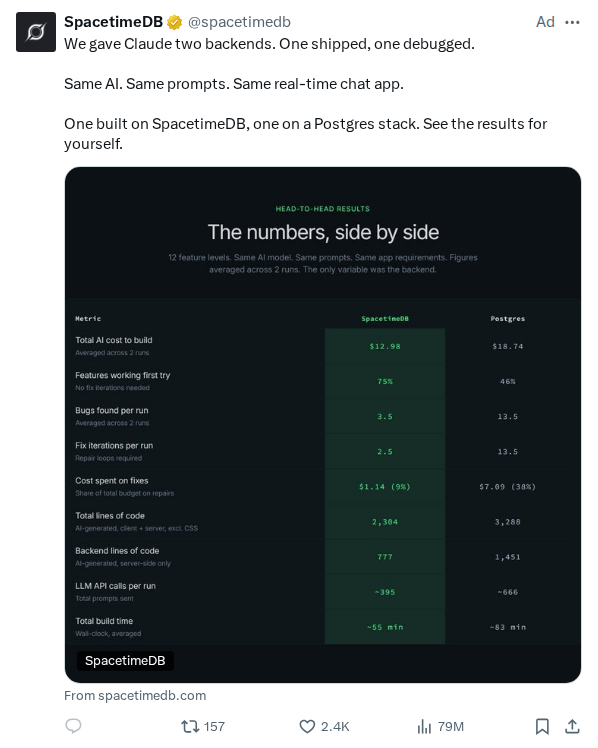
We gave Claude two backends. One shipped, one debugged. Same AI. Same prompts. Same real-time chat app. One built on SpacetimeDB, one on a Postgres stack. See the results for yourself.
show the capture
capture taken
-
capture taken
Hardware wallet. Bitcoin reward included. Get 20% OFF any Tangem Wallet and receive $10 in BTC after activation. A limited-time offer for those who take crypto security seriously.
show the capture
capture taken
-
capture taken
Opportunities don't wait. Neither should you. Access markets outside standard hours, including 24/7 crypto trading.
show the capture
capture taken
-
capture taken
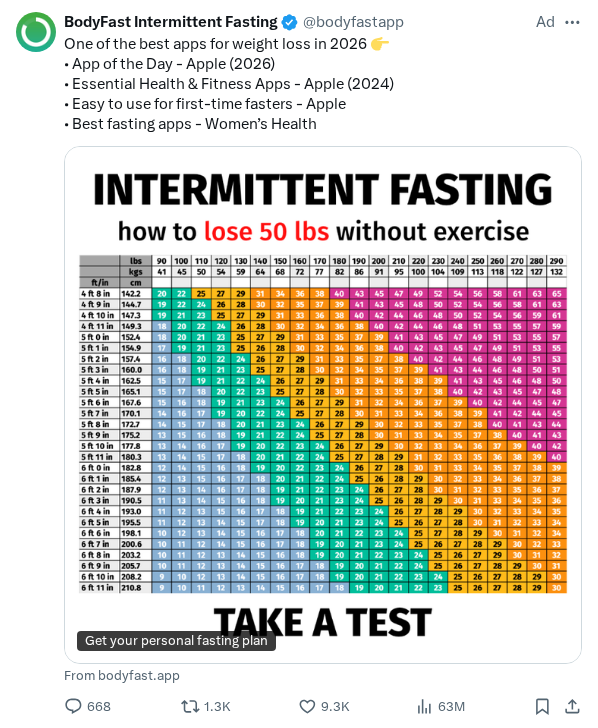
One of the best apps for weight loss in 2026 • App of the Day - Apple (2026) • Essential Health & Fitness Apps - Apple (2024) • Easy to use for first-time fasters - Apple • Best fasting apps - Women’s Health
show the capture
capture taken
-
capture taken
Get sophisticated.
show the capture
capture taken
-
capture taken
Loop through every piece of product feedback
show the capture
capture taken
-
capture taken
Full Claude Course Master Claude to automate repetitive tasks, build apps without coding, create real portfolio projects, and become more valuable at work.
show the capture
capture taken
-
capture taken
Get fast, reliable home internet for seamless streaming, working from home, gaming, and more across multiple devices. Residential service starting at A$75/mo. Order online in minutes.
show the capture
capture taken
-
capture taken
Y'all are about to find him aren't you. And then he's going to say "Oops my LLM just autonomously did all that."
show the capture
capture taken
-
capture taken
interesting. what pattern in the sweeps lead to hypothesis of certain provider?
show the capture
capture taken
-
capture taken
Wow
show the capture
capture taken
-
capture taken
Interesting. Without naming the provider, can you at least clarify whether you're referring to an enterprise blockchain analytics platform or a blockchain data/API service?
show the capture
capture taken
The remaining 154 replies
-
We didn’t even ran his full node to query the utxo set. This just shows how novice the attacker is
show the capture
capture taken
-
go get em, champ.
show the capture
capture taken
-
Worth pairing with the chain state: none of it has moved. The consolidation address is at 4 transactions and 56,202,005,440 sats received with zero spent. A paid account trail on one side and a fully tagged, unmoved pile on the other is a bad place to be sitting.
show the capture
capture taken
-
Awesome work Clay
show the capture
capture taken
-
@grok - please explain what the service provider gave up that assisted in this attack. Is it related to KYC at an exchange?
show the capture
capture taken
-
So the hacker wasn’t even a very good one.., and still stole MILLIONS?!!
show the capture
capture taken
-
Way to go! Go get em! The chances are slim but it would be such a great ending to find and return every stack and hold this/these loser(s) accountable.
show the capture
capture taken
-
Amazing work. If this ends up with people's funds being returned, you'll never again need to buy your own beer at a conference. You'll probably also have the offer of free BJs for life from nvk, but personally I'd just take the beer.
show the capture
capture taken
-
http:// Mempool.space?
show the capture
capture taken
-
wowee
show the capture
capture taken
-
Vibe coder confirmed
show the capture
capture taken
-
great find. hope this helps identify the bad actor
show the capture
capture taken
-
Maybe that means it could be a white hat, who has been quiet so far. Doesn't explain the sloppiness. Or they just used Tor/VPN, and not much will be found.
show the capture
capture taken
-
@grok so who is the service provider then?
show the capture
capture taken
-
wow! awesome work! thanks for keeping us updated on your findings. did the provider have any activity logs for that user that could track whether they were monitoring other addresses and help prevent future sweeps?
show the capture
capture taken
-
Well this should be traceable
show the capture
capture taken
-
Somebody is about to be FUCKED.
show the capture
capture taken
-
Wow. well done
show the capture
capture taken
-
How did the operator pay for the services?
show the capture
capture taken
-
Great work!
show the capture
capture taken
-
Doing Satoshi's work.
show the capture
capture taken
-
Nice work guys.
show the capture
capture taken
-
great work. keep us updated on findings.
show the capture
capture taken
-
let it be a credit card payment
show the capture
capture taken
-
Any guess on provider??
show the capture
capture taken
-
Amazing work you guys Thank for leading on this Hoping all funds get returned and affected wallets moved in time
show the capture
capture taken
-
Wow. Great job.
show the capture
capture taken
-
@BtcChicoFatal
show the capture
capture taken
-
damn, you guys are good
show the capture
capture taken
-
show the capture
capture taken
-
Legends! I hope the attacker is arrested quickly and the bitcoins are recovered.
show the capture
capture taken
-
Bravo
show the capture
capture taken
-
It was Coinbase I TOLD YOU
show the capture
capture taken
-
great work but let the hacker keep it, this isnt theft, it is gamesmenship, welcome to bitcoin
show the capture
capture taken
-
What's the chances this is a ramp up to some play by the new, self appointed 'Bitcoin Security Consortium'...
show the capture
capture taken
-
show the capture
capture taken
-
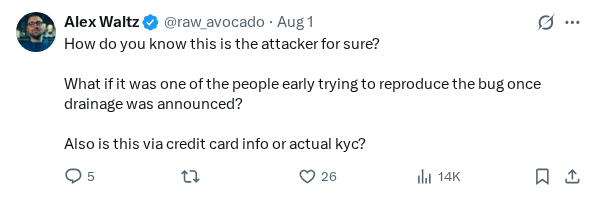
How do you know this is the attacker for sure? What if it was one of the people early trying to reproduce the bug once drainage was announced? Also is this via credit card info or actual kyc?
show the capture
capture taken
-
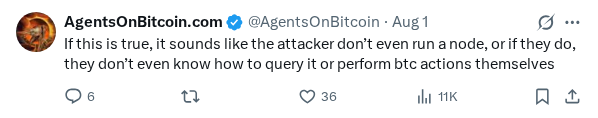
If this is true, it sounds like the attacker don’t even run a node, or if they do, they don’t even know how to query it or perform btc actions themselves
show the capture
capture taken
-
know your customers!
show the capture
capture taken
-
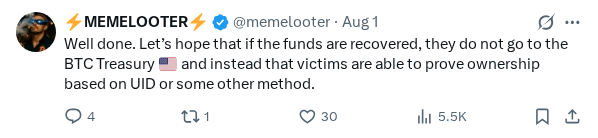
Well done. Let’s hope that if the funds are recovered, they do not go to the BTC Treasury and instead that victims are able to prove ownership based on UID or some other method.
show the capture
capture taken
-
blockchair
show the capture
capture taken
-
Clay, please check your DMs
show the capture
capture taken
-
Maybe hot wallets are the safe bet?
show the capture
capture taken
-
@BTCsessions
show the capture
capture taken
-
show the capture
capture taken
-
Impressive
show the capture
capture taken
-
Ty for your service Bitcoin history will remember you
show the capture
capture taken
-
What was the pattern?
show the capture
capture taken
-
please keep us updated
show the capture
capture taken
-
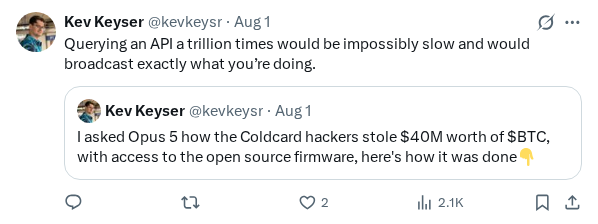
Querying an API a trillion times would be impossibly slow and would broadcast exactly what you’re doing.
show the capture
capture taken
-
Thanks for doing the hard work for the whole community!
show the capture
capture taken
-
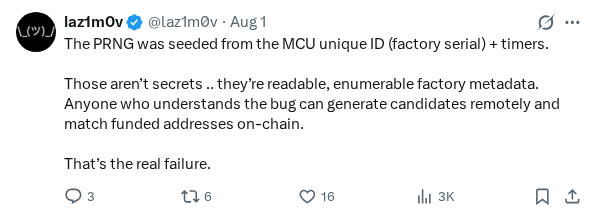
The PRNG was seeded from the MCU unique ID (factory serial) + timers. Those aren’t secrets .. they’re readable, enumerable factory metadata. Anyone who understands the bug can generate candidates remotely and match funded addresses on-chain. That’s the real failure.
show the capture
capture taken
-
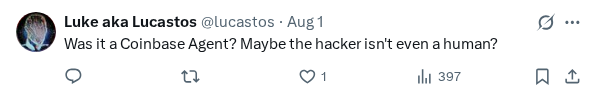
Was it a Coinbase Agent? Maybe the hacker isn't even a human?
show the capture
capture taken
-
show the capture
capture taken
-
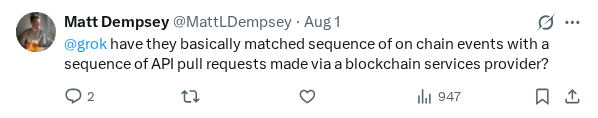
@grok have they basically matched sequence of on chain events with a sequence of API pull requests made via a blockchain services provider?
show the capture
capture taken
-
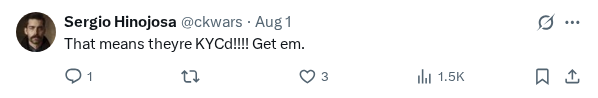
That means theyre KYCd!!!! Get em.
show the capture
capture taken
-
show the capture
capture taken
-
Awesome! Well done.
show the capture
capture taken
-
Lord’s work right there, sir
show the capture
capture taken
-
Wow. Doing God’s work
show the capture
capture taken
-
Nice job Clay and team!
show the capture
capture taken
-
The @Bitkey team did an incredible job investigating the incident. Hope this helps regain the trust of many Bitcoiners who unfairly criticized the product over the years.
show the capture
capture taken
-
So what does this mean? Can folks potentially get their coin back?
show the capture
capture taken
-
> operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps curious how did you get this signal?
show the capture
capture taken
-
show the capture
capture taken
-
We have a section here dedicated to hardware wallets as well as software wallets; try checking them out they might help you make your choice.
show the capture
capture taken
-
I hope this results in the eventual return of funds. I'm sorry to whoever was impacted by this.
show the capture
capture taken
-
bruh couldnt just download the utxo set himself
show the capture
capture taken
-
@ProfEduStream @mariusoffchain
show the capture
capture taken
-
This is the moment
show the capture
capture taken
-
That's a pretty basic operational mistake for someone running a drain. Using a paid account at a chain analytics provider basically hands the investigator a timestamped receipt with your email on it.
show the capture
capture taken
-
@grok explain like I’m 5
show the capture
capture taken
-
So, it’s a 16 year old with a Fable account doing this. Figures!
show the capture
capture taken
-
Good shit thank you
show the capture
capture taken
-
It’s obvious an ai did this
show the capture
capture taken
-
What blockchain services provider is it?
show the capture
capture taken
-
show the capture
capture taken
-
Bravo on all things comms and analysis today
show the capture
capture taken
-
Block coming out looking very good today
show the capture
capture taken
-
show the capture
capture taken
-
Let's not mince words. This is a bloody nose for self-custody. Normies won't. The vast majority of people will remain normies and they see this as a self-custody fail. Self-custody lost today. ETFs are the winners today. Sad.
show the capture
capture taken
-
Plz lord get these ppl their funds back
show the capture
capture taken
-
If your asset requires a trusted third party, then your asset is vulnerable to that third party
show the capture
capture taken
-
@ojedabtc
show the capture
capture taken
-
how do they even know which addresses to target? cold card leave some kind of footprint?
show the capture
capture taken
-
show the capture
capture taken
-
After 23 years, the human and financial cost of Iraq deserves serious public discussion.\nThe country owes that much to service members and Iraqi civilians alike.
show the capture
capture taken
-
Calling a flood '1000-year' repeatedly across different states in the same season should raise more questions about the label than about the storm. Either the statistics need updating or the climate baseline they're built on already has.
show the capture
capture taken
-
Keep up the good work
show the capture
capture taken
-
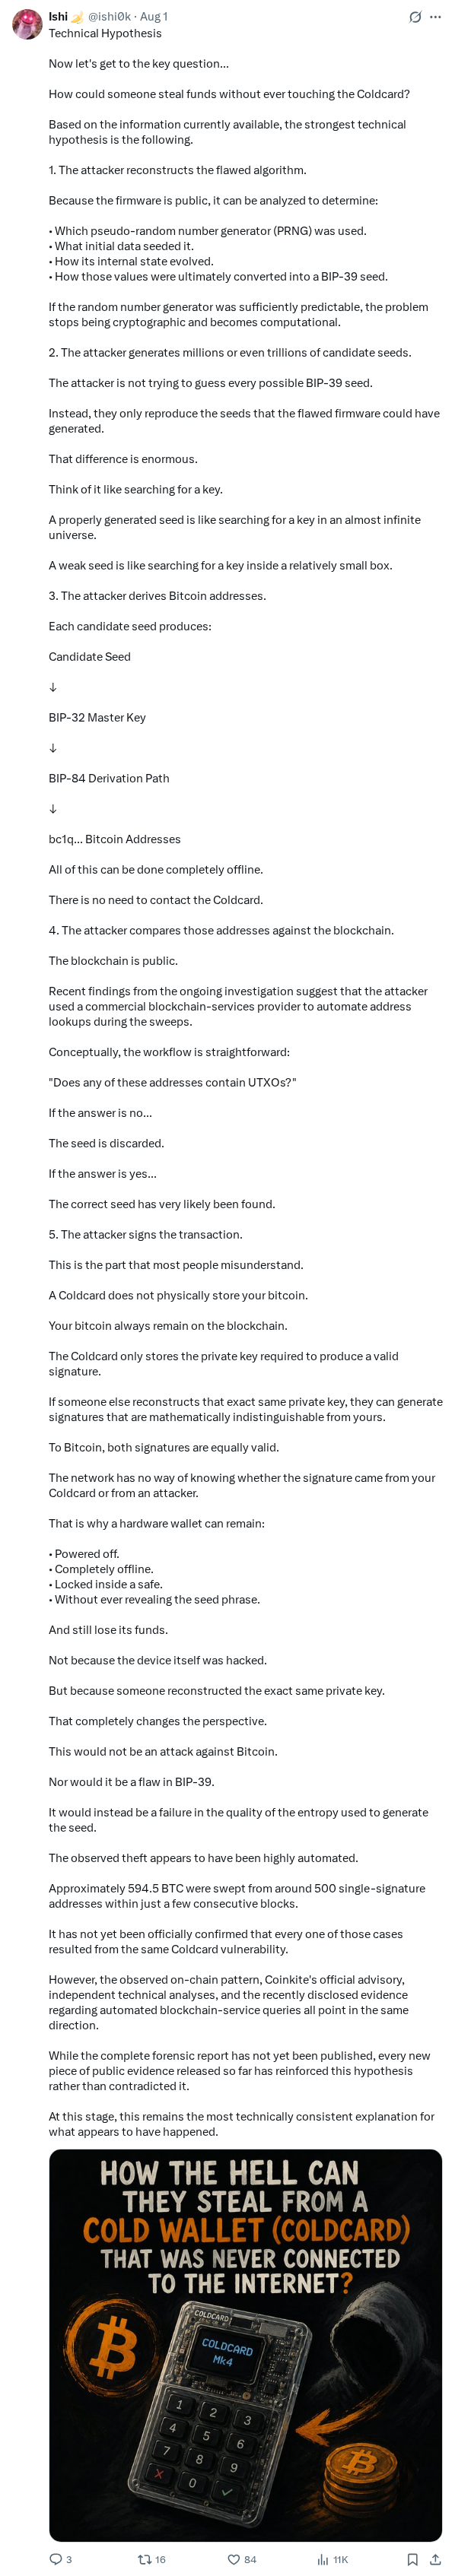
Technical Hypothesis Now let's get to the key question... How could someone steal funds without ever touching the Coldcard? Based on the information currently available, the strongest technical hypothesis is the following. 1. The attacker reconstructs the flawed algorithm. Because the firmware is public, it can be analyzed to determine: • Which pseudo-random number generator (PRNG) was used. • What initial data seeded it. • How its internal state evolved. • How those values were ultimately converted into a BIP-39 seed. If the random number generator was sufficiently predictable, the problem stops being cryptographic and becomes computational. 2. The attacker generates millions or even trillions of candidate seeds. The attacker is not trying to guess every possible BIP-39 seed. Instead, they only reproduce the seeds that the flawed firmware could have generated. That difference is enormous. Think of it like searching for a key. A properly generated seed is like searching for a key in an almost infinite universe. A weak seed is like searching for a key inside a relatively small box. 3. The attacker derives Bitcoin addresses. Each candidate seed produces: Candidate Seed ↓ BIP-32 Master Key ↓ BIP-84 Derivation Path ↓ bc1q... Bitcoin Addresses All of this can be done completely offline. There is no need to contact the Coldcard. 4. The attacker compares those addresses against the blockchain. The blockchain is public. Recent findings from the ongoing investigation suggest that the attacker used a commercial blockchain-services provider to automate address lookups during the sweeps. Conceptually, the workflow is straightforward: "Does any of these addresses contain UTXOs?" If the answer is no... The seed is discarded. If the answer is yes... The correct seed has very likely been found. 5. The attacker signs the transaction. This is the part that most people misunderstand. A Coldcard does not physically store your bitcoin. Your bitcoin always remain on the blockchain. The Coldcard only stores the private key required to produce a valid signature. If someone else reconstructs that exact same private key, they can generate signatures that are mathematically indistinguishable from yours. To Bitcoin, both signatures are equally valid. The network has no way of knowing whether the signature came from your Coldcard or from an attacker. That is why a hardware wallet can remain: • Powered off. • Completely offline. • Locked inside a safe. • Without ever revealing the seed phrase. And still lose its funds. Not because the device itself was hacked. But because someone reconstructed the exact same private key. That completely changes the perspective. This would not be an attack against Bitcoin. Nor would it be a flaw in BIP-39. It would instead be a failure in the quality of the entropy used to generate the seed. The observed theft appears to have been highly automated. Approximately 594.5 BTC were swept from around 500 single-signature addresses within just a few consecutive blocks. It has not yet been officially confirmed that every one of those cases resulted from the same Coldcard vulnerability. However, the observed on-chain pattern, Coinkite's official advisory, independent technical analyses, and the recently disclosed evidence regarding automated blockchain-service queries all point in the same direction. While the complete forensic report has not yet been published, every new piece of public evidence released so far has reinforced this hypothesis rather than contradicted it. At this stage, this remains the most technically consistent explanation for what appears to have happened.
show the capture
capture taken
-
"a paid account at a well-known blockchain-services provider" requires KYC?
show the capture
capture taken
-
well-known blockchain-services provider means absolutely nothing Clay.
show the capture
capture taken
-
Followed
show the capture
capture taken
-
Dang great work. Can only hope
show the capture
capture taken
-
Thanks for your efforts. Glad that I am a Bitkey user that had transferred everything out of the Coldcard ecosystem for both myself and my family. My thoughts go out to those that were not so lucky. Thanks to the team!
show the capture
capture taken
-
"I swear my open claw went rouge."
show the capture
capture taken
-
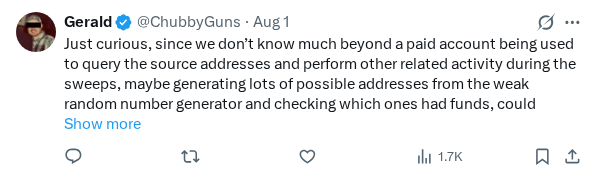
Just curious, since we don’t know much beyond a paid account being used to query the source addresses and perform other related activity during the sweeps, maybe generating lots of possible addresses from the weak random number generator and checking which ones had funds, could the “blockchain service provider”in question possibly be Arkham that helped identify and sweep those addresses?
show the capture
capture taken
-
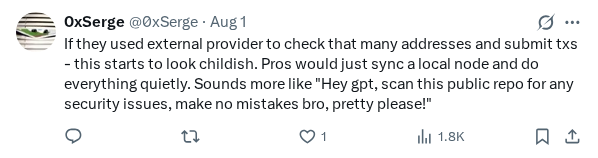
If they used external provider to check that many addresses and submit txs - this starts to look childish. Pros would just sync a local node and do everything quietly. Sounds more like "Hey gpt, scan this public repo for any security issues, make no mistakes bro, pretty please!"
show the capture
capture taken
-
Awesome work Clay
show the capture
capture taken
-
good work!
show the capture
capture taken
-
Good work
show the capture
capture taken
-
From here uncle Sam owns your btc
show the capture
capture taken
-
show the capture
capture taken
-
show the capture
capture taken
-
Basically the attacker used a local node to check whether generated keys were on chain but were too lazy to write a script to scan the balance(or takes too long for them) of every matched address, so they used a blockchain scanner api to get the balance, with a paid account.
show the capture
capture taken
-
With the fiber connections we have, he could download the blockchain in just a few hours and from there run the queries. So that the LLM helped him find errors but not to hide his tracks.
show the capture
capture taken
-
The company is being credited for transparency here, but the breaches themselves happened months before anyone outside Anthropic knew about them. Disclosure after the fact is better than silence, but it's not the same as actually preventing the breach in the first place.
show the capture
capture taken
-
Hey, I'm working on finding more possible addresses from attackers. I think Waves 1-4 are from the same attacker https:// coldcard-hack.up.railway.app You guys might already be aware but I figured I'd forward my findings which built upon @Blocks . There is some other verified attackers with different, harder to track patterns.
show the capture
capture taken
-
Interested to see the full play by play.
show the capture
capture taken
-
Lol
show the capture
capture taken
-
Did you get a name and contact details?
show the capture
capture taken
-
Nice job
show the capture
capture taken
-
Odds are pretty good that it would be a kyc exchange right? If they were smart it would be fake id but if they were smart they wouldn’t be doing this through a fucking public provider
show the capture
capture taken
-
Amazing work! Thank you!
show the capture
capture taken
-
Bitkey is available in 95 countries, but not in some of the places where people need it most. Ukraine comes to mind immediately. War, banking disruptions, displacement, damaged infrastructure, and the constant need for financial sovereignty would seem like the perfect use case for Bitcoin self-custody. Apparently, not for Bitkey.
show the capture
capture taken
-
Should be available for shipment to Ukraine next week.
show the capture
capture taken
-
@grok Is this how the attacker knew how to hone in the addresses to brute force? What I don't get yet is, if those low entropy addresses were sitting on the chain for that long, why weren't they attacked earlier? Low entropy brain wallets get emptied instantly.
show the capture
capture taken
-
Nice one brother, sounds promising
show the capture
capture taken
-
What does it mean if the hackers are found and stolen bitcoin is recovered?
show the capture
capture taken
-
the attacker stole coins with a key generation flaw, then left a paper trail through a KYC'd data provider decentralized theft centralized mistake
show the capture
capture taken
-
Agreed
show the capture
capture taken
-
show the capture
capture taken
-
A 4.3% single-year tuition jump might sound modest until you remember it's stacked on top of years of steady increases that have already outpaced typical household income growth. Compounding annual hikes add up fast, even when each individual year's percentage increase looks manageable on its own.
show the capture
capture taken
-
Often the first people they investigate are insiders. Did anyone quick recently or get fired etc. Then everyone still at the company. It seems like the thief’s will have a hard time successfully converting to fiat or another crypto? Is it possible this is a friendly doing this to force the industry to evolve and get more secure? How would anyone on the outside know the RNG was weak? They guessed? Seems unlikely?
show the capture
capture taken
-
Disarmament deals fail when nobody trusts enforcement.\nInternational monitoring may be just as important as the agreement itself.
show the capture
capture taken
-
Assuming white hat hacker: What if this was done mid attack to try and figure out which hardware wallet is the one producing all the collisions? What are the chances? Nah can’t be. Cold card wouldn’t allow themselves to get caught. Idk
show the capture
capture taken
-
Cheering for you all to catch this scumbag!
show the capture
capture taken
-
I smell CIA
show the capture
capture taken
-
@grok who is it ?
show the capture
capture taken
-
Looks to me like the attackers used AI to automate this entire process: from finding the weaknesses in entropy generation to sweep publically know btc addresses. Now who could that be? Yep, US gov proxies using the latest models. With their Israeli enforcers.
show the capture
capture taken
-
On the internet you can easily find scripts that keep generating and checking thousands of wallets per second, even before this discovery. This is the nature of the blockchain: anyone can generate a random wallet and it belongs to that person. Does everyone who does this have to be arrested? That doesn’t make any sense at all.
show the capture
capture taken
-
Good work!
show the capture
capture taken
-
Based af.
show the capture
capture taken
-
show the capture
capture taken
-
Why on earth would this be announced? Doesn't this risk tipping off the attacker(s)?
show the capture
capture taken
-
the attacker looking up adresses through a registered account indicates that this is not a sophisticated actor. there is a high likelyhood that we will find out who is responsible. my guess is that its someone close to @Coinkite @nvk
show the capture
capture taken
-
Good work!
show the capture
capture taken
-
@threadreaderapp unroll please
show the capture
capture taken
-
Plot twist. Fable did it itself, building up funds to create an ai army
show the capture
capture taken
-
show the capture
capture taken
-
Competence doesn't usually extend to a wide variety of fields. The areas where this hacker is less competant will be their undoing. Asymmetric search.
show the capture
capture taken
-
Great work. So if this wasn’t intentional, they should know where the “stolen” coins went and be able to give them back- right??
show the capture
capture taken
-
For something is so basic and an upmost important you guys screwed up… providing a random seed phrase generator that is not random
show the capture
capture taken
-
Nice work
show the capture
capture taken
-
what kind of provider
show the capture
capture taken
-
@grok quais as últimas notícias?
show the capture
capture taken
-
GET THEM
show the capture
capture taken
-
Great effort. But don't think this is a good idea to share this publicly before the suspect is caught. Although a bit late, it's still a good idea to take this down @max_guise
show the capture
capture taken
-
Redemption Code:GS70YTASTJ Genshin Impact Version 7.0 "Everwinter Without Mercy" will be released on August 12.
show the capture
capture taken
-
Running ClickHouse in production? check out @NeverBlinkAI for query analytics, live insights, optimizations recommendations and everything you need to keep it optimized and reliable.
show the capture
capture taken
-
Ready to test your brain?
show the capture
capture taken
-
Back-to-school shopping? Do it through the PeanutButterJelly Marketplace; real brands across style, tech & travel. Commissions support student scholarships and hunger relief.
show the capture
capture taken
-
Level up your on-the-go gaming with an immersive, wide display made for entertaining on the all-new Galaxy Z Fold8 Ultra. Available now to purchase.
show the capture
capture taken
-
So whats happening to Cyber here @thsottiaux ? @OpenAI @OpenAIDevs Is Cyber as a solo no longer a thing? All gotta go through TAC? What happens to account if was previously approved?
show the capture
capture taken
This capture reached the end of the conversation as X served it: it stopped because nothing further loaded, not because a limit was hit. X decides what a reader is shown, so that is not the same as a guarantee of every reply.
Held captures
-
Asanoha's display name changed to include 'Timechain Art Magazine', and the reply by IphigenAleksy to that account is no longer present in a same-depth capture (37 scroll rounds).
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 12 lines
 post: 2083353279573155874
 role: reply
 author: asanoha_gold
-name: Asanoha
+name: Asanoha | Timechain Art Magazine
 created: 2026-08-01T00:45:03Z
 media: 0
 body:
 body:
 Should be available for shipment to Ukraine next week.

-post: 2083462272291340458
-role: reply
-author: IphigenAleksy
-name: Aleksy
-created: 2026-08-01T07:58:09Z
-media: 0
-body:
-@grok
- Is this how the attacker knew how to hone in the addresses to  brute force? What I don't get yet is, if those low entropy addresses were sitting on the chain for that long, why weren't they attacked earlier? Low entropy brain wallets get emptied instantly.
-
 post: 2083470017132187992
 role: reply
 author: observerofdecay
Extracted text as captured
thread: 2083247006139503065
url: https://x.com/clay_garrett/status/2083247006139503065
author: clay_garrett

post: 2083247006139503065
role: focal
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:45Z
media: 0
body:
1/ During our investigation of the Coldcard drain yesterday, we identified an unusual pattern in the sweeps. That pattern led us to a hypothesis that has since been confirmed: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps.

post: 2083247007808774228
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
2/ We contacted the provider directly. Their internal logs matched the suspected workflow with extraordinary specificity, including the number, timing and sequence of requests. The provider was supplying its standard services in response to requests that did not reveal their broader purpose. We have seen no evidence that the provider knowingly participated in or facilitated the suspected theft.

post: 2083247009125822647
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.

post: 2083247959056007408
role: reply
author: AJ__1337
name: AJ
created: 2026-07-31T17:46:32Z
media: 0
body:
Y'all are about to find him aren't you. And then he's going to say "Oops my LLM just autonomously did all that."
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
One reply author's display name changed from 'Plebtitioner RN' to 'Reformed Practitioner RN'; the thread depth and reply count were unchanged.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 2 lines
 post: 2083530023320142052
 role: reply
 author: RNHairman
-name: Plebtitioner RN
+name: Reformed Practitioner RN
 created: 2026-08-01T12:27:22Z
 media: 0
 body:
Extracted text as captured
thread: 2083247006139503065
url: https://x.com/clay_garrett/status/2083247006139503065
author: clay_garrett

post: 2083247006139503065
role: focal
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:45Z
media: 0
body:
1/ During our investigation of the Coldcard drain yesterday, we identified an unusual pattern in the sweeps. That pattern led us to a hypothesis that has since been confirmed: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps.

post: 2083247007808774228
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
2/ We contacted the provider directly. Their internal logs matched the suspected workflow with extraordinary specificity, including the number, timing and sequence of requests. The provider was supplying its standard services in response to requests that did not reveal their broader purpose. We have seen no evidence that the provider knowingly participated in or facilitated the suspected theft.

post: 2083247009125822647
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.

post: 2083247959056007408
role: reply
author: AJ__1337
name: AJ
created: 2026-07-31T17:46:32Z
media: 0
body:
Y'all are about to find him aren't you. And then he's going to say "Oops my LLM just autonomously did all that."
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
The reply thread changed composition: AJ__1337's reply appeared while five replies (joaodealmeida_, CobraBitcoin, herogamer21btc, mattcrv and asanoha_gold) were no longer observed, in a capture that reached 30 scroll rounds versus the previous capture's 25, both capped: false.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 56 lines
 body:
 3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.

+post: 2083247959056007408
+role: reply
+author: AJ__1337
+name: AJ
+created: 2026-07-31T17:46:32Z
+media: 0
+body:
+Y'all are about to find him aren't you. And then he's going to say "Oops my LLM just autonomously did all that."
+
 post: 2083248035916550633
 role: reply
 author: BitcoinCoderBob
 body:
 Interesting. Without naming the provider, can you at least clarify whether you're referring to an enterprise blockchain analytics platform or a blockchain data/API service?

-post: 2083250908486381850
-role: reply
-author: joaodealmeida_
-name: João Almeida — ₿/acc
-created: 2026-07-31T17:58:16Z
-media: 0
-body:
-We didn’t even ran his full node to query the utxo set. This just shows how novice the attacker is
-
 post: 2083252962898440487
 role: reply
 author: beeforbacon1
 media: 0
 body:

-
-post: 2083265372732420348
-role: reply
-author: CobraBitcoin
-name: Cøbra
-created: 2026-07-31T18:55:44Z
-media: 0
-body:
-Legends! I hope the attacker is arrested quickly and the bitcoins are recovered.

 post: 2083265621123580082
 role: reply
 body:
 Impressive

-post: 2083270812270797005
-role: reply
-author: herogamer21btc
-name: HeroGamer
-created: 2026-07-31T19:17:21Z
-media: 0
-body:
-Ty for your service  Bitcoin history will remember you
-
 post: 2083271845277827430
 role: reply
 author: KayBeSee
 body:
 Nice job Clay and team!

-post: 2083280019938283645
-role: reply
-author: mattcrv
-name: Matt Carvalho
-created: 2026-07-31T19:53:56Z
-media: 0
-body:
-The
-@Bitkey
- team did an incredible job investigating the incident. Hope this helps regain the trust of many Bitcoiners who unfairly criticized the product over the years.
-
 post: 2083281839439933850
 role: reply
 author: melkelly84
 body:
 well-known blockchain-services provider means absolutely nothing Clay.

-post: 2083353279573155874
-role: reply
-author: asanoha_gold
-name: Asanoha
-created: 2026-08-01T00:45:03Z
-media: 0
-body:
-Followed
-
 post: 2083364236055756940
 role: reply
 author: billiamBTC
Extracted text as captured
thread: 2083247006139503065
url: https://x.com/clay_garrett/status/2083247006139503065
author: clay_garrett

post: 2083247006139503065
role: focal
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:45Z
media: 0
body:
1/ During our investigation of the Coldcard drain yesterday, we identified an unusual pattern in the sweeps. That pattern led us to a hypothesis that has since been confirmed: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps.

post: 2083247007808774228
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
2/ We contacted the provider directly. Their internal logs matched the suspected workflow with extraordinary specificity, including the number, timing and sequence of requests. The provider was supplying its standard services in response to requests that did not reveal their broader purpose. We have seen no evidence that the provider knowingly participated in or facilitated the suspected theft.

post: 2083247009125822647
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.

post: 2083247959056007408
role: reply
author: AJ__1337
name: AJ
created: 2026-07-31T17:46:32Z
media: 0
body:
Y'all are about to find him aren't you. And then he's going to say "Oops my LLM just autonomously did all that."
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
The thread gained six additional reply records and two participants changed their display names.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 69 lines
 body:
 3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.

-post: 2083247959056007408
-role: reply
-author: AJ__1337
-name: AJ
-created: 2026-07-31T17:46:32Z
-media: 0
-body:
-Y'all are about to find him aren't you. And then he's going to say "Oops my LLM just autonomously did all that."
-
 post: 2083248035916550633
 role: reply
 author: BitcoinCoderBob
 post: 2083249035864154259
 role: reply
 author: humble21m
-name: ∞/21M (BIP448)
+name: ∞/21M | BIP448
 created: 2026-07-31T17:50:49Z
 media: 0
 body:
 Wow
+
+post: 2083250076638494866
+role: reply
+author: mercalerta
+name: mercalerta
+created: 2026-07-31T17:54:57Z
+media: 0
+body:
+Interesting. Without naming the provider, can you at least clarify whether you're referring to an enterprise blockchain analytics platform or a blockchain data/API service?
+
+post: 2083250908486381850
+role: reply
+author: joaodealmeida_
+name: João Almeida — ₿/acc
+created: 2026-07-31T17:58:16Z
+media: 0
+body:
+We didn’t even ran his full node to query the utxo set. This just shows how novice the attacker is

 post: 2083252962898440487
 role: reply
 media: 0
 body:

+
+post: 2083265372732420348
+role: reply
+author: CobraBitcoin
+name: Cøbra
+created: 2026-07-31T18:55:44Z
+media: 0
+body:
+Legends! I hope the attacker is arrested quickly and the bitcoins are recovered.

 post: 2083265621123580082
 role: reply
 body:
 Impressive

+post: 2083270812270797005
+role: reply
+author: herogamer21btc
+name: HeroGamer
+created: 2026-07-31T19:17:21Z
+media: 0
+body:
+Ty for your service  Bitcoin history will remember you
+
 post: 2083271845277827430
 role: reply
 author: KayBeSee
 body:
 Nice job Clay and team!

+post: 2083280019938283645
+role: reply
+author: mattcrv
+name: Matt Carvalho
+created: 2026-07-31T19:53:56Z
+media: 0
+body:
+The
+@Bitkey
+ team did an incredible job investigating the incident. Hope this helps regain the trust of many Bitcoiners who unfairly criticized the product over the years.
+
 post: 2083281839439933850
 role: reply
 author: melkelly84
 body:
 well-known blockchain-services provider means absolutely nothing Clay.

+post: 2083353279573155874
+role: reply
+author: asanoha_gold
+name: Asanoha
+created: 2026-08-01T00:45:03Z
+media: 0
+body:
+Followed
+
 post: 2083364236055756940
 role: reply
 author: billiamBTC
 post: 2083475534424719517
 role: reply
 author: StaunchOrange
-name: Staunchy
+name: Staunchy BIP110 GFY
 created: 2026-08-01T08:50:51Z
 media: 0
 body:
Extracted text as captured
thread: 2083247006139503065
url: https://x.com/clay_garrett/status/2083247006139503065
author: clay_garrett

post: 2083247006139503065
role: focal
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:45Z
media: 0
body:
1/ During our investigation of the Coldcard drain yesterday, we identified an unusual pattern in the sweeps. That pattern led us to a hypothesis that has since been confirmed: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps.

post: 2083247007808774228
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
2/ We contacted the provider directly. Their internal logs matched the suspected workflow with extraordinary specificity, including the number, timing and sequence of requests. The provider was supplying its standard services in response to requests that did not reveal their broader purpose. We have seen no evidence that the provider knowingly participated in or facilitated the suspected theft.

post: 2083247009125822647
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.

post: 2083248035916550633
role: reply
author: BitcoinCoderBob
name: Bob
created: 2026-07-31T17:46:51Z
media: 0
body:
interesting. what pattern in the sweeps lead to hypothesis of certain provider?
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
At the same observed depth (135 replies, 29 scroll rounds), two older replies vanished, one user's display name dropped the 'BIP-110' suffix, and two newer replies appeared.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 38 lines
 body:
 great work. keep us updated on findings.

-post: 2083262290854388055
-role: reply
-author: MctoshiW
-name: McToshi Whoppamoto
-created: 2026-07-31T18:43:29Z
-media: 0
-body:
-Any guess on provider??
-
 post: 2083262795207041083
 role: reply
 author: darrenahunter
 body:


-post: 2083276133613584491
-role: reply
-author: ggggggg13131313
-name: Nero
-created: 2026-07-31T19:38:30Z
-media: 0
-body:
-Awesome! Well done.
-
 post: 2083277255191429287
 role: reply
 author: leafdelpino
 post: 2083281839439933850
 role: reply
 author: melkelly84
-name: Melissa Kelly - BIP-110
+name: Melissa Kelly
 created: 2026-07-31T20:01:10Z
 media: 0
 body:
 body:
 Lol

+post: 2083427608629326307
+role: reply
+author: Zenul_Abidin
+name: Ali Sherief
+created: 2026-08-01T05:40:24Z
+media: 0
+body:
+Did you get a name and contact details?
+
 post: 2083435429756563708
 role: reply
 author: mannan25195
 body:
 For something is so basic and an upmost important you guys screwed up… providing a random seed phrase generator that is not random

+post: 2083805166940127666
+role: reply
+author: mmni99inc
+name: Adam Charles Maxwell
+created: 2026-08-02T06:40:41Z
+media: 0
+body:
+Nice work
+
 post: 2083823213042192384
 role: reply
 author: OurielOhayon
Extracted text as captured
thread: 2083247006139503065
url: https://x.com/clay_garrett/status/2083247006139503065
author: clay_garrett

post: 2083247006139503065
role: focal
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:45Z
media: 0
body:
1/ During our investigation of the Coldcard drain yesterday, we identified an unusual pattern in the sweeps. That pattern led us to a hypothesis that has since been confirmed: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps.

post: 2083247007808774228
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
2/ We contacted the provider directly. Their internal logs matched the suspected workflow with extraordinary specificity, including the number, timing and sequence of requests. The provider was supplying its standard services in response to requests that did not reveal their broader purpose. We have seen no evidence that the provider knowingly participated in or facilitated the suspected theft.

post: 2083247009125822647
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.

post: 2083247959056007408
role: reply
author: AJ__1337
name: AJ
created: 2026-07-31T17:46:32Z
media: 0
body:
Y'all are about to find him aren't you. And then he's going to say "Oops my LLM just autonomously did all that."
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
Multiple replies left the thread, including those from r0ckstardev, MctoshiW, CobraBitcoin, ggggggg13131313, mattcrv, bitchimlying, IphigenAleksy and RNHairman, and one display name changed. The capture reached a greater scroll depth (29 vs 27) with nine fewer observed posts (138 vs 147), so the removals are not under-collection.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 86 lines
 body:
 great work. keep us updated on findings.

-post: 2083261908908495216
-role: reply
-author: r0ckstardev
-name: Uncle Rockstar Developer
-created: 2026-07-31T18:41:58Z
-media: 0
-body:
-let it be a credit card payment
-
-post: 2083262290854388055
-role: reply
-author: MctoshiW
-name: McToshi Whoppamoto
-created: 2026-07-31T18:43:29Z
-media: 0
-body:
-Any guess on provider??
-
 post: 2083262795207041083
 role: reply
 author: darrenahunter
 media: 0
 body:

-
-post: 2083265372732420348
-role: reply
-author: CobraBitcoin
-name: Cøbra
-created: 2026-07-31T18:55:44Z
-media: 0
-body:
-Legends! I hope the attacker is arrested quickly and the bitcoins are recovered.

 post: 2083265621123580082
 role: reply
 body:


-post: 2083276133613584491
-role: reply
-author: ggggggg13131313
-name: Nero
-created: 2026-07-31T19:38:30Z
-media: 0
-body:
-Awesome! Well done.
-
 post: 2083277255191429287
 role: reply
 author: leafdelpino
 media: 0
 body:
 Nice job Clay and team!
-
-post: 2083280019938283645
-role: reply
-author: mattcrv
-name: Matt Carvalho
-created: 2026-07-31T19:53:56Z
-media: 0
-body:
-The
-@Bitkey
- team did an incredible job investigating the incident. Hope this helps regain the trust of many Bitcoiners who unfairly criticized the product over the years.

 post: 2083281839439933850
 role: reply
 body:
 @ojedabtc

-post: 2083330414869905443
-role: reply
-author: bitchimlying
-name: -.-- --- ..- / .- .-. . / -... --- .-. . -..
-created: 2026-07-31T23:14:11Z
-media: 0
-body:
-how do they even know which addresses to target? cold card leave some kind of footprint?
-
 post: 2083331018170233053
 role: reply
 author: loblawbob2
 body:
 Should be available for shipment to Ukraine next week.

-post: 2083462272291340458
-role: reply
-author: IphigenAleksy
-name: Aleksy
-created: 2026-08-01T07:58:09Z
-media: 0
-body:
-@grok
- Is this how the attacker knew how to hone in the addresses to  brute force? What I don't get yet is, if those low entropy addresses were sitting on the chain for that long, why weren't they attacked earlier? Low entropy brain wallets get emptied instantly.
-
 post: 2083470017132187992
 role: reply
 author: observerofdecay
 body:
 Cheering for you all to catch this scumbag!

-post: 2083530023320142052
-role: reply
-author: RNHairman
-name: Plebtitioner RN
-created: 2026-08-01T12:27:22Z
-media: 0
-body:
-I smell CIA
-
 post: 2083531203974402095
 role: reply
 author: bokiko
 post: 2083748472466055411
 role: reply
 author: Krypto_Knight33
-name: Knight_of_Krypto
+name: Round_Peg_in_a_Square_World
 created: 2026-08-02T02:55:24Z
 media: 0
 body:
 @grok
  quais as últimas notícias?

-post: 2084038620806328398
-role: reply
-author: FiatisF00lsgold
-name: April Snow
-created: 2026-08-02T22:08:21Z
-media: 0
-body:
-GET THEM
-
 post: 2084403700957872525
 role: reply
 author: pseudoramdom
Extracted text as captured
thread: 2083247006139503065
url: https://x.com/clay_garrett/status/2083247006139503065
author: clay_garrett

post: 2083247006139503065
role: focal
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:45Z
media: 0
body:
1/ During our investigation of the Coldcard drain yesterday, we identified an unusual pattern in the sweeps. That pattern led us to a hypothesis that has since been confirmed: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps.

post: 2083247007808774228
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
2/ We contacted the provider directly. Their internal logs matched the suspected workflow with extraordinary specificity, including the number, timing and sequence of requests. The provider was supplying its standard services in response to requests that did not reveal their broader purpose. We have seen no evidence that the provider knowingly participated in or facilitated the suspected theft.

post: 2083247009125822647
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.

post: 2083247959056007408
role: reply
author: AJ__1337
name: AJ
created: 2026-07-31T17:46:32Z
media: 0
body:
Y'all are about to find him aren't you. And then he's going to say "Oops my LLM just autonomously did all that."
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
Six new replies to Block's attribution thread, from JuicyMagiK, teapotbytes, dev_on_cycle, IphigenAleksy, RNHairman and FiatisF00lsgold. Additions only, with no reply leaving the capture, which is the first poll pair to show the thread lane behaving as designed.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 55 lines
 body:
 It’s obvious an ai did this

+post: 2083306980123312279
+role: reply
+author: JuicyMagiK
+name: Juicy MagiK
+created: 2026-07-31T21:41:04Z
+media: 0
+body:
+What blockchain services provider is it?
+
 post: 2083307262001782874
 role: reply
 author: B1teco1n
 body:
 "a paid account at a well-known blockchain-services provider" requires KYC?

+post: 2083344102905585884
+role: reply
+author: teapotbytes
+name: YSeparator
+created: 2026-08-01T00:08:35Z
+media: 0
+body:
+well-known blockchain-services provider means absolutely nothing Clay.
+
 post: 2083353279573155874
 role: reply
 author: asanoha_gold
 body:
 Basically the attacker used a local node to check whether generated keys were on chain but were too lazy to write a script to scan the balance(or takes too long for them) of every matched address, so they used a blockchain scanner api to get the balance, with a paid account.

+post: 2083407182209470636
+role: reply
+author: dev_on_cycle
+name: dev_on_cycle
+created: 2026-08-01T04:19:14Z
+media: 0
+body:
+With the fiber connections we have, he could download the blockchain in just a few hours and from there run the queries. So that the LLM helped him find errors but not to hide his tracks.
+
 post: 2083418174742278241
 role: reply
 author: midnightmusicth
 body:
 Should be available for shipment to Ukraine next week.

+post: 2083462272291340458
+role: reply
+author: IphigenAleksy
+name: Aleksy
+created: 2026-08-01T07:58:09Z
+media: 0
+body:
+@grok
+ Is this how the attacker knew how to hone in the addresses to  brute force? What I don't get yet is, if those low entropy addresses were sitting on the chain for that long, why weren't they attacked earlier? Low entropy brain wallets get emptied instantly.
+
 post: 2083470017132187992
 role: reply
 author: observerofdecay
 body:
 Cheering for you all to catch this scumbag!

+post: 2083530023320142052
+role: reply
+author: RNHairman
+name: Plebtitioner RN
+created: 2026-08-01T12:27:22Z
+media: 0
+body:
+I smell CIA
+
 post: 2083531203974402095
 role: reply
 author: bokiko
 @grok
  quais as últimas notícias?

+post: 2084038620806328398
+role: reply
+author: FiatisF00lsgold
+name: April Snow
+created: 2026-08-02T22:08:21Z
+media: 0
+body:
+GET THEM
+
 post: 2084403700957872525
 role: reply
 author: pseudoramdom
Extracted text as captured
thread: 2083247006139503065
url: https://x.com/clay_garrett/status/2083247006139503065
author: clay_garrett

post: 2083247006139503065
role: focal
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:45Z
media: 0
body:
1/ During our investigation of the Coldcard drain yesterday, we identified an unusual pattern in the sweeps. That pattern led us to a hypothesis that has since been confirmed: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps.

post: 2083247007808774228
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
2/ We contacted the provider directly. Their internal logs matched the suspected workflow with extraordinary specificity, including the number, timing and sequence of requests. The provider was supplying its standard services in response to requests that did not reveal their broader purpose. We have seen no evidence that the provider knowingly participated in or facilitated the suspected theft.

post: 2083247009125822647
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.

post: 2083247959056007408
role: reply
author: AJ__1337
name: AJ
created: 2026-07-31T17:46:32Z
media: 0
body:
Y'all are about to find him aren't you. And then he's going to say "Oops my LLM just autonomously did all that."
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
Recovery from the under-collected capture above, so the restored text is this project's missing collection rather than new material from the source: 140 replies held once dryness stopped being read as convergence.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 886 lines
 body:
 interesting. what pattern in the sweeps lead to hypothesis of certain provider?

+post: 2083249035864154259
+role: reply
+author: humble21m
+name: HODL ∞/21M
+created: 2026-07-31T17:50:49Z
+media: 0
+body:
+Wow
+
+post: 2083250908486381850
+role: reply
+author: joaodealmeida_
+name: João Almeida — ₿/acc
+created: 2026-07-31T17:58:16Z
+media: 0
+body:
+We didn’t even ran his full node to query the utxo set. This just shows how novice the attacker is
+
 post: 2083252962898440487
 role: reply
 author: beeforbacon1
 http://
 Mempool.space?

+post: 2083258584465363430
+role: reply
+author: OttawaGestapo
+name: Ottawa Gestapo
+created: 2026-07-31T18:28:46Z
+media: 0
+body:
+wowee
+
 post: 2083258751205961906
 role: reply
 author: r0bertclarkson
 body:
 great find. hope this helps identify the bad actor

+post: 2083259151006740487
+role: reply
+author: Tonteldoos416
+name: Tonteldoos
+created: 2026-07-31T18:31:01Z
+media: 0
+body:
+Someone's AI agent gone rogue?
+
 post: 2083259435187573201
 role: reply
 author: TomZarebczan

 Or they just used Tor/VPN, and not much will be found.

+post: 2083259769469763999
+role: reply
+author: hellaxbt
+name: hella
+created: 2026-07-31T18:33:28Z
+media: 0
+body:
+@grok
+ so who is the service provider then?
+
 post: 2083259909555015698
 role: reply
 author: ivygalindo
 body:
 Well this should be traceable

+post: 2083260213126115802
+role: reply
+author: ec1ipse_sol
+name: Ec1ipse.sol
+created: 2026-07-31T18:35:14Z
+media: 0
+body:
+Somebody is about to be FUCKED.
+
 post: 2083260923452498256
 role: reply
 author: zherbert
 body:
 Doing Satoshi's work.

+post: 2083261398805540945
+role: reply
+author: AnalysisFeral
+name: Feral Analysis
+created: 2026-07-31T18:39:57Z
+media: 0
+body:
+Nice work guys.
+
+post: 2083261781372182778
+role: reply
+author: Zimo0o0
+name: Z
+created: 2026-07-31T18:41:28Z
+media: 0
+body:
+great work. keep us updated on findings.
+
+post: 2083261908908495216
+role: reply
+author: r0ckstardev
+name: Uncle Rockstar Developer
+created: 2026-07-31T18:41:58Z
+media: 0
+body:
+let it be a credit card payment
+
+post: 2083262290854388055
+role: reply
+author: MctoshiW
+name: McToshi Whoppamoto
+created: 2026-07-31T18:43:29Z
+media: 0
+body:
+Any guess on provider??
+
+post: 2083262795207041083
+role: reply
+author: darrenahunter
+name: darren
+created: 2026-07-31T18:45:30Z
+media: 0
+body:
+Amazing work you guys
+Thank for leading on this
+Hoping all funds get returned and affected wallets moved in time
+
 post: 2083264300601282892
 role: reply
 author: SatsScholar
 body:
 Wow. Great job.

+post: 2083264434038771794
+role: reply
+author: volpeLP
+name: drumr_
+created: 2026-07-31T18:52:00Z
+media: 0
+body:
+@BtcChicoFatal
+
+post: 2083265270605303994
+role: reply
+author: Nih_Noh
+name: Nih Noh
+created: 2026-07-31T18:55:20Z
+media: 0
+body:
+damn, you guys are good
+
+post: 2083265281749598276
+role: reply
+author: potapac1
+name: Potapac
+created: 2026-07-31T18:55:23Z
+media: 0
+body:
+
+
+post: 2083265372732420348
+role: reply
+author: CobraBitcoin
+name: Cøbra
+created: 2026-07-31T18:55:44Z
+media: 0
+body:
+Legends! I hope the attacker is arrested quickly and the bitcoins are recovered.
+
+post: 2083265621123580082
+role: reply
+author: craftlawyer
+name: Craft Lawyer
+created: 2026-07-31T18:56:43Z
+media: 0
+body:
+Bravo
+
 post: 2083265755987034170
 role: reply
 author: TomGotTwitteer
 body:
 It was Coinbase I TOLD YOU

+post: 2083265910857748719
+role: reply
+author: CryptoTits69
+name: CryptoTits69
+created: 2026-07-31T18:57:53Z
+media: 0
+body:
+great work but let the hacker keep it, this isnt theft, it is gamesmenship, welcome to bitcoin
+
+post: 2083266046077624681
+role: reply
+author: BetruetoitUK
+name: SemiSol
+created: 2026-07-31T18:58:25Z
+media: 0
+body:
+What's the chances this is a ramp up to some play by the new, self appointed 'Bitcoin Security Consortium'...
+
+post: 2083266982527598858
+role: reply
+author: Everythingascam
+name: Captain B
+created: 2026-07-31T19:02:08Z
+media: 0
+body:
+
+
 post: 2083267313948561508
 role: reply
 author: raw_avocado
 body:
 If this is true, it sounds like the attacker don’t even run a node, or if they do, they don’t even know how to query it or perform btc actions themselves

+post: 2083268095418802502
+role: reply
+author: JumpmanJLow
+name: JLow
+created: 2026-07-31T19:06:33Z
+media: 0
+body:
+know your customers!
+
 post: 2083268273421086892
 role: reply
 author: memelooter
 body:
 Well done. Let’s hope that if the funds are recovered, they do not go to the BTC Treasury  and instead that victims are able to prove ownership based on UID or some other method.

+post: 2083268305423622476
+role: reply
+author: Kaxaax12
+name: 13371337
+created: 2026-07-31T19:07:23Z
+media: 0
+body:
+blockchair
+
+post: 2083268840515850318
+role: reply
+author: OwenKemeys
+name: Owen Kemeys
+created: 2026-07-31T19:09:31Z
+media: 0
+body:
+Clay, please check your DMs
+
+post: 2083269133723164893
+role: reply
+author: joeokeefejr
+name: Joe O’Keefe Jr.
+created: 2026-07-31T19:10:41Z
+media: 0
+body:
+Maybe hot  wallets are the safe bet?
+
+post: 2083269275293487327
+role: reply
+author: Dannyseabird
+name: Danny
+created: 2026-07-31T19:11:15Z
+media: 0
+body:
+@BTCsessions
+
+post: 2083270522796753387
+role: reply
+author: BuddhaPerchance
+name: StackchainBuddha 580kGang
+created: 2026-07-31T19:16:12Z
+media: 1
+body:
+
+
+post: 2083270549640237540
+role: reply
+author: lawlesslogic
+name: Andrew
+created: 2026-07-31T19:16:18Z
+media: 0
+body:
+Impressive
+
+post: 2083270812270797005
+role: reply
+author: herogamer21btc
+name: HeroGamer
+created: 2026-07-31T19:17:21Z
+media: 0
+body:
+Ty for your service  Bitcoin history will remember you
+
 post: 2083271845277827430
 role: reply
 author: KayBeSee
 media: 0
 body:
 please keep us updated
+
+post: 2083272155039732034
+role: reply
+author: kevkeysr
+name: Kev Keyser
+created: 2026-07-31T19:22:41Z
+media: 0
+body:
+Querying an API a trillion times would be impossibly slow and would broadcast exactly what you’re doing.
+
+post: 2083272239643025774
+role: reply
+author: AGtheAlchemist
+name: AG the Alchemist
+created: 2026-07-31T19:23:01Z
+media: 0
+body:
+Thanks for doing the hard work for the whole community!
+
+post: 2083272637577298173
+role: reply
+author: laz1m0v
+name: laz1m0v
+created: 2026-07-31T19:24:36Z
+media: 0
+body:
+The PRNG was seeded from the MCU unique ID (factory serial) + timers.
+
+Those aren’t secrets .. they’re readable, enumerable factory metadata. Anyone who understands the bug can generate candidates remotely and match funded addresses on-chain.
+
+That’s the real failure.
+
+post: 2083273516346982467
+role: reply
+author: lucastos
+name: Luke aka Lucastos
+created: 2026-07-31T19:28:06Z
+media: 0
+body:
+Was it a Coinbase Agent? Maybe the hacker isn't even a human?
+
+post: 2083274675631566928
+role: reply
+author: MattLDempsey
+name: Matt Dempsey
+created: 2026-07-31T19:32:42Z
+media: 0
+body:
+@grok
+ have they basically matched sequence of on chain events with a sequence of API pull requests made via a blockchain services provider?
+
+post: 2083274865143136399
+role: reply
+author: ckwars
+name: Sergio Hinojosa
+created: 2026-07-31T19:33:27Z
+media: 0
+body:
+That means theyre KYCd!!!! Get em.

 post: 2083276050759389665
 role: reply
 body:


+post: 2083276133613584491
+role: reply
+author: ggggggg13131313
+name: Nero
+created: 2026-07-31T19:38:30Z
+media: 0
+body:
+Awesome! Well done.
+
+post: 2083277255191429287
+role: reply
+author: leafdelpino
+name: Leaf del Pino
+created: 2026-07-31T19:42:57Z
+media: 0
+body:
+Lord’s work right there, sir
+
 post: 2083277803491873151
 role: reply
 author: BTC_broo
 body:
 Nice job Clay and team!

+post: 2083280019938283645
+role: reply
+author: mattcrv
+name: Matt Carvalho
+created: 2026-07-31T19:53:56Z
+media: 0
+body:
+The
+@Bitkey
+ team did an incredible job investigating the incident. Hope this helps regain the trust of many Bitcoiners who unfairly criticized the product over the years.
+
+post: 2083281839439933850
+role: reply
+author: melkelly84
+name: Melissa Kelly - BIP-110
+created: 2026-07-31T20:01:10Z
+media: 0
+body:
+So what does this mean?  Can folks potentially get their coin back?
+
+post: 2083282061398249853
+role: reply
+author: rnair_
+name: ⊃ ∪ ⊃ ⊂
+created: 2026-07-31T20:02:03Z
+media: 0
+body:
+> operator used a paid account at a  well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps
+
+curious how did you get this signal?
+
+post: 2083282614786642215
+role: reply
+author: VanquishTrader
+name: VanquishTrader
+created: 2026-07-31T20:04:15Z
+media: 1
+body:
+
+
 post: 2083288539224314301
 role: reply
 author: GeorgeInPants
 body:
 bruh couldnt just download the utxo set himself

+post: 2083292206924808281
+role: reply
+author: FredPocketIQ
+name: Fred | PocketIQ | Free AI Trading
+created: 2026-07-31T20:42:22Z
+media: 0
+body:
+ This is the moment
+
+post: 2083296499342221328
+role: reply
+author: founder_sohan
+name: Founder Sohan — XReply
+created: 2026-07-31T20:59:25Z
+media: 0
+body:
+That's a pretty basic operational mistake for someone running a drain. Using a paid account at a chain analytics provider basically hands the investigator a timestamped receipt with your email on it.
+
+post: 2083299973488112045
+role: reply
+author: UbbaDubbz
+name: .
+created: 2026-07-31T21:13:14Z
+media: 0
+body:
+@grok
+ explain like I’m 5
+
 post: 2083301611581898910
 role: reply
 author: LindenJohan
 body:
 Good shit thank you

+post: 2083303886392107043
+role: reply
+author: erniebumwhistle
+name: dave ahoy
+created: 2026-07-31T21:28:47Z
+media: 0
+body:
+It’s obvious an ai did this
+
+post: 2083307262001782874
+role: reply
+author: B1teco1n
+name: 21Million
+created: 2026-07-31T21:42:11Z
+media: 0
+body:
+
+
 post: 2083311398101418361
 role: reply
 author: ryanlanman1
 body:
 Bravo on all things comms and analysis today

+post: 2083313995742663164
+role: reply
+author: Danielbutunique
+name: Daniel Castello
+created: 2026-07-31T22:08:57Z
+media: 0
+body:
+Block coming out looking very good today
+
+post: 2083316690616553853
+role: reply
+author: satsdisco
+name: Grafton @ LunarRails.io
+created: 2026-07-31T22:19:39Z
+media: 1
+body:
+
+
+post: 2083319565363363884
+role: reply
+author: ZARkiwi
+name: ZARkiwi
+created: 2026-07-31T22:31:05Z
+media: 0
+body:
+Let's not mince words. This is a bloody nose for self-custody. Normies won't. The vast majority of people will remain normies and they see this as a self-custody fail.
+Self-custody lost today.
+ETFs are the winners today. Sad.
+
 post: 2083321253243346989
 role: reply
 author: BitcoinBro86
 media: 0
 body:
 Plz lord get these ppl their funds back
+
+post: 2083323190420652228
+role: reply
+author: The_Richard_J
+name: Richard L. Johnson
+created: 2026-07-31T22:45:29Z
+media: 0
+body:
+If your asset requires a trusted third party, then your asset is vulnerable to that third party
+
+post: 2083329816921575615
+role: reply
+author: LeaoHard
+name: Leonardo
+created: 2026-07-31T23:11:49Z
+media: 0
+body:
+@ojedabtc
+
+post: 2083330414869905443
+role: reply
+author: bitchimlying
+name: -.-- --- ..- / .- .-. . / -... --- .-. . -..
+created: 2026-07-31T23:14:11Z
+media: 0
+body:
+how do they even know which addresses to target? cold card leave some kind of footprint?
+
+post: 2083331018170233053
+role: reply
+author: loblawbob2
+name: ₿ob Loblaw
+created: 2026-07-31T23:16:35Z
+media: 0
+body:
+
+
+post: 2083332779023245572
+role: reply
+author: changemindlike
+name: 나비
+created: 2026-07-31T23:23:35Z
+media: 0
+body:
+After 23 years, the human and financial cost of Iraq deserves serious public discussion.\nThe country owes that much to service members and Iraqi civilians alike.
+
+post: 2083333308923216273
+role: reply
+author: midnightmusicth
+name: JooHyunRyu
+created: 2026-07-31T23:25:41Z
+media: 0
+body:
+Calling a flood '1000-year' repeatedly across different states in the same season should raise more questions about the label than about the storm.
+Either the statistics need updating or the climate baseline they're built on already has.
+
+post: 2083335868304269358
+role: reply
+author: Augustusmint9
+name: Augustus
+created: 2026-07-31T23:35:52Z
+media: 0
+body:
+Keep up the good work

 post: 2083341014379438592
 role: reply

 At this stage, this remains the most technically consistent explanation for what appears to have happened.

+post: 2083341082868510853
+role: reply
+author: maskjiro
+name: MaskJiro
+created: 2026-07-31T23:56:35Z
+media: 0
+body:
+"a paid account at a well-known blockchain-services provider" requires KYC?
+
+post: 2083353279573155874
+role: reply
+author: asanoha_gold
+name: Asanoha
+created: 2026-08-01T00:45:03Z
+media: 0
+body:
+Followed
+
+post: 2083364236055756940
+role: reply
+author: billiamBTC
+name: Billiam
+created: 2026-08-01T01:28:35Z
+media: 0
+body:
+Dang great work. Can only hope
+
+post: 2083367834676077003
+role: reply
+author: GlennCB
+name: Glenn Charles
+created: 2026-08-01T01:42:53Z
+media: 0
+body:
+Thanks for your efforts. Glad that I am a Bitkey user that had transferred everything out of the Coldcard ecosystem for both myself and my family.  My thoughts go out to those that were not so lucky.  Thanks to the team!
+
+post: 2083372239777677333
+role: reply
+author: athewmay
+name: Ŧhe ₿iŧcoin Faŧ Caŧ
+created: 2026-08-01T02:00:23Z
+media: 0
+body:
+"I swear my open claw went rouge."
+
+post: 2083379267736351216
+role: reply
+author: ChubbyGuns
+name: Gerald
+created: 2026-08-01T02:28:19Z
+media: 0
+body:
+Just curious, since we don’t know much beyond a paid account being used to query the source addresses and perform other related activity during the sweeps, maybe generating lots of possible addresses from the weak random number generator and checking which ones had funds, could the “blockchain service provider”in question possibly be Arkham that helped identify and sweep those addresses?
+
+post: 2083381390129954926
+role: reply
+author: 0xSerge
+name: 0xSerge
+created: 2026-08-01T02:36:45Z
+media: 0
+body:
+If they used external provider to check that many addresses and submit txs - this starts to look childish. Pros would just sync a local node and do everything quietly. Sounds more like "Hey gpt, scan this public repo for any security issues, make no mistakes bro, pretty please!"
+
 post: 2083387270057378131
 role: reply
 author: TheCoinDad
 body:
 Good work

+post: 2083389529797308755
+role: reply
+author: flaccyboi
+name: FLAKITO
+created: 2026-08-01T03:09:06Z
+media: 0
+body:
+From here uncle Sam owns your btc
+
+post: 2083391201202536516
+role: reply
+author: baitmogged
+name: Non Sense
+created: 2026-08-01T03:15:44Z
+media: 1
+body:
+
+
+post: 2083391386926321830
+role: reply
+author: GarrettMcManus
+name: GM
+created: 2026-08-01T03:16:28Z
+media: 1
+body:
+
+
+post: 2083404467253490059
+role: reply
+author: 0xAnthraX
+name: Anthr@X
+created: 2026-08-01T04:08:27Z
+media: 0
+body:
+Basically the attacker used a local node to check whether generated keys were on chain but were too lazy to write a script to scan the balance(or takes too long for them) of every matched address, so they used a blockchain scanner api to get the balance, with a paid account.
+
+post: 2083418174742278241
+role: reply
+author: midnightmusicth
+name: JooHyunRyu
+created: 2026-08-01T05:02:55Z
+media: 0
+body:
+The company is being credited for transparency here, but the breaches themselves happened months before anyone outside Anthropic knew about them.
+Disclosure after the fact is better than silence, but it's not the same as actually preventing the breach in the first place.
+
 post: 2083420933243433347
 role: reply
 author: KevinKelbie
 .

 There is some other verified attackers with different, harder to track patterns.
+
+post: 2083422588278018277
+role: reply
+author: GingerSherpa
+name: Chester
+created: 2026-08-01T05:20:27Z
+media: 0
+body:
+Interested to see the full play by play.

 post: 2083426864064758237
 role: reply
 body:
 Lol

+post: 2083427608629326307
+role: reply
+author: Zenul_Abidin
+name: Ali Sherief
+created: 2026-08-01T05:40:24Z
+media: 0
+body:
+Did you get a name and contact details?
+
+post: 2083435429756563708
+role: reply
+author: mannan25195
+name: MD Mannan
+created: 2026-08-01T06:11:29Z
+media: 0
+body:
+Nice job
+
+post: 2083437568163479820
+role: reply
+author: yang620
+name: seth
+created: 2026-08-01T06:19:59Z
+media: 0
+body:
+Odds are pretty good that it would be a kyc exchange right? If they were smart it would be fake id but if they were smart they wouldn’t be doing this through a fucking public provider
+
 post: 2083451540312850589
 role: reply
 author: gunzaj12
 body:
 Should be available for shipment to Ukraine next week.

+post: 2083470017132187992
+role: reply
+author: observerofdecay
+name: Observer of Decay
+created: 2026-08-01T08:28:55Z
+media: 0
+body:
+Nice one brother, sounds promising
+
 post: 2083478560774537574
 role: reply
 author: bee_swarm
 body:
 the attacker stole coins with a key generation flaw, then left a paper trail through a KYC'd data provider decentralized theft centralized mistake

+post: 2083483557197160758
+role: reply
+author: imanpyudha
+name: TTD
+created: 2026-08-01T09:22:43Z
+media: 0
+body:
+Agreed
+
+post: 2083506315138371752
+role: reply
+author: midnightmusicth
+name: JooHyunRyu
+created: 2026-08-01T10:53:09Z
+media: 0
+body:
+A 4.3% single-year tuition jump might sound modest until you remember it's stacked on top of years of steady increases that have already outpaced typical household income growth.
+Compounding annual hikes add up fast, even when each individual year's percentage increase looks manageable on its own.
+
+post: 2083507932952428745
+role: reply
+author: TheOrdAmerican
+name: TheOrdinaryAmerican
+created: 2026-08-01T10:59:35Z
+media: 0
+body:
+Often the first people they investigate are insiders.   Did anyone quick recently or get fired etc.  Then everyone still at the company.
+It seems like the thief’s will have a hard time successfully converting to fiat or another crypto?
+Is it possible this is a friendly doing this to force the industry to evolve and get more secure?
+How would anyone on the outside know the RNG was weak?   They guessed?   Seems unlikely?
+
+post: 2083517586613178390
+role: reply
+author: changemindlike
+name: 나비
+created: 2026-08-01T11:37:57Z
+media: 0
+body:
+Disarmament deals fail when nobody trusts enforcement.\nInternational monitoring may be just as important as the agreement itself.
+
+post: 2083517855614525472
+role: reply
+author: LeoDelamoJr
+name: Leonel Delamo Jr
+created: 2026-08-01T11:39:01Z
+media: 0
+body:
+Assuming white hat hacker: What if this was done mid attack to try and figure out which hardware wallet is the one producing all the collisions?  What are the chances?
+Nah can’t be. Cold card wouldn’t allow themselves to get caught. Idk
+
+post: 2083518746086248582
+role: reply
+author: iSchmiegle
+name: Chad Wick
+created: 2026-08-01T11:42:33Z
+media: 0
+body:
+Cheering for you all to catch this scumbag!
+
+post: 2083531203974402095
+role: reply
+author: bokiko
+name: Bokiko
+created: 2026-08-01T12:32:03Z
+media: 0
+body:
+@grok
+ who is it ?
+
+post: 2083570141724618958
+role: reply
+author: fortunekr75
+name: fortunekr [LTC]
+created: 2026-08-01T15:06:47Z
+media: 0
+body:
+Looks to me like the attackers used AI to automate this entire process: from finding the weaknesses in entropy generation to sweep publically know btc addresses. Now who could that be? Yep, US gov proxies using the latest models. With their Israeli enforcers.
+
+post: 2083573920616050749
+role: reply
+author: itxtoledo
+name: Toledo ➔ hotgate.com.br
+created: 2026-08-01T15:21:48Z
+media: 0
+body:
+On the internet you can easily find scripts that keep generating and checking thousands of wallets per second, even before this discovery. This is the nature of the blockchain: anyone can generate a random wallet and it belongs to that person. Does everyone who does this have to be arrested? That doesn’t make any sense at all.
+
+post: 2083576487718842759
+role: reply
+author: AdamAmrich
+name: Am Rich
+created: 2026-08-01T15:32:00Z
+media: 0
+body:
+Good work!
+
+post: 2083584649067184403
+role: reply
+author: wealthpotion
+name: Brandon Bedford
+created: 2026-08-01T16:04:26Z
+media: 0
+body:
+Based af.
+
+post: 2083593878284681219
+role: reply
+author: ai_asul
+name: asul
+created: 2026-08-01T16:41:06Z
+media: 1
+body:
+
+
+post: 2083600405624135700
+role: reply
+author: entreprenuri
+name: Uri
+created: 2026-08-01T17:07:02Z
+media: 0
+body:
+Why on earth would this be announced? Doesn't this risk tipping off the attacker(s)?
+
+post: 2083615881305661828
+role: reply
+author: ob_hodl
+name: bitcoin pirate  I  I ∞/21M
+created: 2026-08-01T18:08:32Z
+media: 0
+body:
+the attacker looking up adresses through a registered account indicates that this is not a sophisticated actor. there is a high likelyhood that we will find out who is responsible. my guess is that its someone close to
+@Coinkite
+
+@nvk
+
+post: 2083625394809307510
+role: reply
+author: lucio_stf
+name: Lucio
+created: 2026-08-01T18:46:20Z
+media: 0
+body:
+Good work!
+
+post: 2083629621522620836
+role: reply
+author: rachelkillsbam
+name: Rachelkillsbam
+created: 2026-08-01T19:03:08Z
+media: 0
+body:
+@threadreaderapp
+ unroll please
+
+post: 2083669692200464527
+role: reply
+author: chrimack
+name: Chris Mack
+created: 2026-08-01T21:42:21Z
+media: 0
+body:
+Plot twist.  Fable did it itself,  building up funds to create an ai army
+
+post: 2083686630372642897
+role: reply
+author: guillefernandes
+name: Guillermo
+created: 2026-08-01T22:49:40Z
+media: 0
+body:
+
+
+post: 2083709525878816954
+role: reply
+author: UncleBo05435478
+name: Papa Stack
+created: 2026-08-02T00:20:39Z
+media: 0
+body:
+Competence doesn't usually extend to a wide variety of fields. The areas where this hacker is less competant will be their undoing. Asymmetric search.
+
+post: 2083748472466055411
+role: reply
+author: Krypto_Knight33
+name: Knight_of_Krypto
+created: 2026-08-02T02:55:24Z
+media: 0
+body:
+Great work.
+So if this wasn’t intentional, they should know where the “stolen” coins went and be able to give them back- right??
+
+post: 2083761234047021388
+role: reply
+author: su02008402
+name: Su-N
+created: 2026-08-02T03:46:07Z
+media: 1
+body:
+For something is so basic and an upmost important you guys screwed up… providing a random seed phrase generator that is not random
+
+post: 2083805166940127666
+role: reply
+author: mmni99inc
+name: Adam Charles Maxwell
+created: 2026-08-02T06:40:41Z
+media: 0
+body:
+Nice work
+
 post: 2083823213042192384
 role: reply
 author: OurielOhayon
 media: 0
 body:
 what kind of provider
+
+post: 2083861006388760632
+role: reply
+author: fabiojr15
+name: Fábio Alves
+created: 2026-08-02T10:22:34Z
+media: 0
+body:
+@grok
+ quais as últimas notícias?
+
+post: 2084403700957872525
+role: reply
+author: pseudoramdom
+name: Ram
+created: 2026-08-03T22:19:03Z
+media: 0
+body:
+Great effort. But don't think this is a good idea to share this publicly before the suspect is caught.
+Although a bit late, it's still a good idea to take this down
+@max_guise
Extracted text as captured
thread: 2083247006139503065
url: https://x.com/clay_garrett/status/2083247006139503065
author: clay_garrett

post: 2083247006139503065
role: focal
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:45Z
media: 0
body:
1/ During our investigation of the Coldcard drain yesterday, we identified an unusual pattern in the sweeps. That pattern led us to a hypothesis that has since been confirmed: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps.

post: 2083247007808774228
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
2/ We contacted the provider directly. Their internal logs matched the suspected workflow with extraordinary specificity, including the number, timing and sequence of requests. The provider was supplying its standard services in response to requests that did not reveal their broader purpose. We have seen no evidence that the provider knowingly participated in or facilitated the suspected theft.

post: 2083247009125822647
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.

post: 2083247959056007408
role: reply
author: AJ__1337
name: AJ
created: 2026-07-31T17:46:32Z
media: 0
body:
Y'all are about to find him aren't you. And then he's going to say "Oops my LLM just autonomously did all that."
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 0 lines
Extracted text as captured
thread: 2083247006139503065
url: https://x.com/clay_garrett/status/2083247006139503065
author: clay_garrett

post: 2083247006139503065
role: focal
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:45Z
media: 0
body:
1/ During our investigation of the Coldcard drain yesterday, we identified an unusual pattern in the sweeps. That pattern led us to a hypothesis that has since been confirmed: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and perform other related activity during the sweeps.

post: 2083247007808774228
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
2/ We contacted the provider directly. Their internal logs matched the suspected workflow with extraordinary specificity, including the number, timing and sequence of requests. The provider was supplying its standard services in response to requests that did not reveal their broader purpose. We have seen no evidence that the provider knowingly participated in or facilitated the suspected theft.

post: 2083247009125822647
role: self-thread
author: clay_garrett
name: Clay Garrett
created: 2026-07-31T17:42:46Z
media: 0
body:
3/ We are sharing the relevant information with the appropriate authorities. We will provide further updates when doing so will not interfere with the investigation.

post: 2083247959056007408
role: reply
author: AJ__1337
name: AJ
created: 2026-07-31T17:46:32Z
media: 0
body:
Y'all are about to find him aren't you. And then he's going to say "Oops my LLM just autonomously did all that."
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
16 presentation-noise differences. Sidebar, ticker and other page chrome churn that our review classified as not being changes to what the source says.
- +111 -139 Multiple visible replies were replaced by different promotional or off-topic ads, but capped remained false and the later capture reached a higher scroll round while observing fewer posts, indicating ranking/selection churn rather than new content.
- +186 -0 The capture picked up additional reply records, mostly promotional or off-topic ads, that the previous pass missed; capped remained false and posts_observed rose from 155 to 171 while scroll rounds fell, so this is ranking/recovery rather than new thread content.
- +39 -0 Four older replies from July 31 and August 1 re-entered the ranked view while the later capture observed more posts (155 versus 151) at fewer scroll rounds (27 versus 37), so the change is ranking recovery rather than new content.
- +9 -0 Owen Kemeys' July 31 reply re-entered the capture after the later poll scrolled deeper (37 rounds and 149 replies observed versus 31 rounds and 148 replies), so the change is ranking recovery rather than a new post.
- +47 -0 Old replies by joaodealmeida_, CobraBitcoin, herogamer21btc, mattcrv and asanoha_gold re-entered the thread when the capture deepened from 30 to 31 scroll rounds and replies observed rose from 143 to 148, so this is ranking recovery rather than new content.
- +65 -1 The deeper capture (30 scroll rounds vs 29) recovered older replies and one updated display name; the depth records show ranking recovery, not new content.
- +18 -18 Two older replies re-entered the capture and two others dropped out while the depth record showed the same reply count and scroll depth, so this is ranking churn.
- +157 -9 The capture expanded from 128 to 144 observed replies at the same scroll depth (capped false, posts expanded from 8 to 10), so the added and dropped July 31-August 2 replies are ranking or expansion churn rather than reliable deletions or new posts.
- +27 -27 X reply ranking again, and this pair is self-correcting evidence for reading the previous one as ranking rather than deletion: leafdelpino's reply, which left the capture at 20260807T205522Z, is back. Three replies enter and three leave, posts observed unchanged at 131 over 27 scroll rounds against 24, capped false and no gap declared. All six are dated 31 July or 1 August, and the text of the three that left is preserved in this diff.
- +9 -27 X reply ranking again: one reply enters the capture (0xkuncoro, posted 31 July, pairing the paid-account trail with the unmoved consolidation balance) and three leave, all of them posted on 31 July. Posts observed fell from 133 to 131 over fewer scroll rounds, 28 to 24, with capped false and no gap declared in either state. The dropped replies' text is preserved in this diff. Under-collection and deletion are not distinguishable from the text alone, and nothing here indicates deletion.
- +0 -112 X reply-load variance: thirteen replies present in the prior capture are absent here, all with unchanged bodies and timestamps. Same varying-reply-subset pattern documented for this thread on 6 and 7 August; nothing demonstrably deleted.
- +111 -0 X reply-load variance: twelve replies reappear that the previous capture (20260806T164447Z) had missed, all with unchanged bodies and timestamps. Same varying-reply-subset pattern as the preceding diff.
- +0 -147 X reply-load variance: fourteen replies present in the prior capture are absent here, and the next capture (20260807T081349Z) shows most of them again. The browser capture sees a different reply subset per load; nothing was demonstrably deleted.
- +9 -826 Under-collection, not deletion and not ranking: the capture went quiet for four rounds while X's loader lagged mid-page and read that as the end of the conversation, holding 45 of 146 replies while declaring no gap. Its depth record shows capped false with 45 replies observed against 140 the poll before. capture.py now refuses a capture collecting under 75 percent of the previous one, and convergence requires the viewport to have reached the bottom of loaded content.
- +31 -38 X reply ranking changed again, replacing earlier replies with a different subset and reporting that the reply cap was reached.
- +113 -99 X returned a different ranked subset of replies, adding and omitting older reply records while the focal attribution post remained unchanged.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.