Swan's code-review pipeline published as a template
skwp-2085475419386519875
- Author
- @skwp
- Organisation
- independent
- Evidence role
- social statement
- Posted
- 6 Aug 2026, 21:17 UTC
- Capture status
- capture held
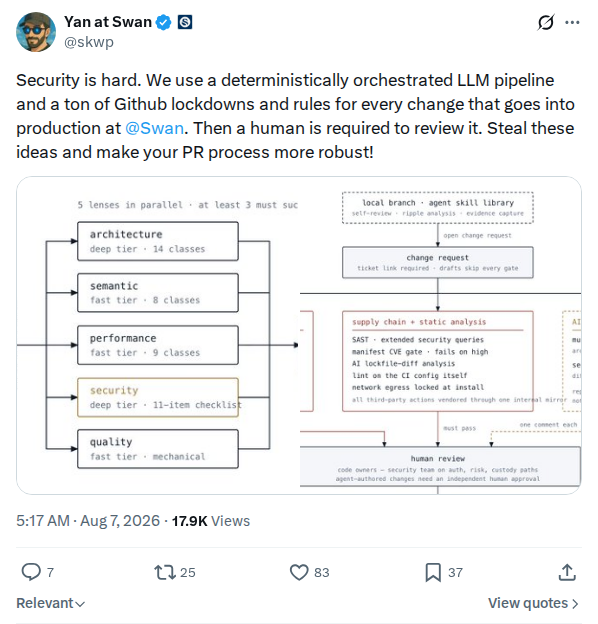
Yan Pritzker describes the process Swan uses for every change that reaches production, a deterministically orchestrated LLM pipeline plus GitHub lockdowns and rules, with a human review required afterwards, and invites other teams to copy it. The attached diagram sets out the detail: five review lenses run in parallel with at least three required to succeed, covering architecture, semantic, performance, security and quality; a change-request gate requiring a ticket link; supply-chain and static analysis with extended security queries, a manifest CVE gate failing on high, third-party actions vendored through an internal mirror and network egress locked at install; and a final human review in which code owners and the security team sign off and agent-authored changes need independent human approval. Held because the incident turned AI code review into a live argument, and this is a concrete published process rather than a position on it, usable as a document by anyone assessing that argument. Pritzker is at Swan and the post promotes Swan's own engineering practice. Nothing here establishes that the pipeline works as described or that it would have caught this defect.
This post is registered as evidence and has a locally held capture. The original remains the canonical publication. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
Held captures
0 presentation-noise differences. Sidebar, ticker and other page chrome churn that our review classified as not being changes to what the source says.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.