BTCPay Server active exploitation warning
pavlenex-2085756609741930534
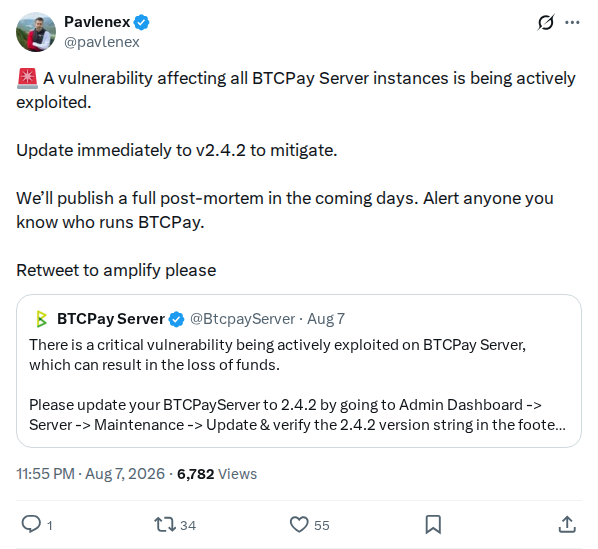
- Author
- @pavlenex
- Organisation
- independent
- Evidence role
- social statement
- Posted
- 7 Aug 2026, 15:55 UTC
- Capture status
- capture held
Pavlenex warns that a vulnerability affecting all BTCPay Server instances is being actively exploited, urges immediate update to v2.4.2, and says a full post-mortem will follow. Held as a dated incident-response alert from a BTCPay Server maintainer, alongside the organisational btcpayserver statement posted the same hour. The claims are the poster's own and are not verified here.
This post is registered as evidence and has a locally held capture. The original remains the canonical publication. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
Held captures
0 presentation-noise differences. Sidebar, ticker and other page chrome churn that our review classified as not being changes to what the source says.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.