User reports their coldcard wallet being drained on Reddit
stackernews-first-drain-report
Latest reviewed change
source content difference between and
The thread added Murch's updated situation summary, including expanded device, entropy and passphrase assertions, alongside later community replies.
       "comments": {
         "comments": [
           {
+            "createdAt": "2026-08-05T21:35:21.769Z",
+            "text": "###### Summary of Situation as of this Time\n\n**ACTION RECOMMENDATION: PLEASE CAREFULLY MOVE FUNDS STORED ON COLDCARD WALLETS CREATED FROM DEVICE-GENERATED ENTROPY TO UNAFFECTED WALLETS *ASAP*.**\n\nAny funds on a **COLDCARD Mk3 using a firmware from version 4.0.1 (March 2021) to 4.1.9 (latest version until July 30th)**, where the entropy was only generated by the device, **should be considered compromised**. COLDCARD Mk4, Mk5, and Q are affected by the same issue to a lesser degree. Wallets generated by those devices are at risk of theft. Wallets created with externally generated entropy with at least 50 dice throws should not be exposed. Wallets that pair the device entropy with a passphrase are only as secure as the passphrase.  If you used a weak passphrase (less than 25 random characters or fewer than seven BIP39 words) and did not provide external entropy (at least fifty dice throws), your funds are at risk.\n\nCoinkite has released firmware updates for COLDCARD Mk3, Mk4, Mk5, and Q. Wallets generated with the new firmware should be secure. **Updating to the new firmware does *not make affected wallets secure*. Only new wallets generated with the new firmware are unaffected.** Coinkite put out a [security advisory](https://blog.coinkite.com/coldcard-mk3-seed-generation-warning/). The security advisory has been updated to include more devices, more details about the issue, and migration advice.\n\nBlock security researchers reports that the COLDCARD Mk2 is affected the same way as the Mk3.\n\nAnyone with access to a frontier AI model is capable of reproducing the attack. Especially if you have funds on a COLDCARD single-sig wallet created with wallet-generated entropy, please carefully **move your funds to an unaffected wallet ASAP**. Single-sig wallets with a weak passphrase, or multisig wallets that can be spent by a quorum of COLDCARD wallets or composed only of COLDCARD wallets created with device-generated entropy should be considered **at risk** and funds should also be moved.",
+            "user": {
+              "name": "Murch"
+            }
First lines only. The complete diff is in the timeline below.
- Organisation
- Stacker News
- Evidence role
- Community discussion
- Published
- 2026-07-30
- Source changes
- 4
- Detected differences
- 6
- Unreviewed
- 0
- Copies held
- 7
The earliest incident thread identified on Stacker News: Murch relaying the first Reddit drain report while the recipient address was still collecting, the evening before Coinkite's disclosure. The drain claims quoted are the Reddit posters', unverified here; the thread's value is that it fixes when the incident first surfaced publicly and how the community read it in real time. Captured through the site's public GraphQL API: the rendered pages crash the capture tab, and the API answers POST from this host. The query fixes the captured surface to the item's title, text and two levels of comments, each with author and absolute timestamp.
Every check is recorded, including checks that found no text change. A detected edit is therefore bounded between two checks. The publisher's exact save time is not observable from this record. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
Held captures
-
The thread added Murch's updated situation summary, including expanded device, entropy and passphrase assertions, alongside later community replies.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 154 lines
"comments": { "comments": [ { + "createdAt": "2026-08-05T21:35:21.769Z", + "text": "###### Summary of Situation as of this Time\n\n**ACTION RECOMMENDATION: PLEASE CAREFULLY MOVE FUNDS STORED ON COLDCARD WALLETS CREATED FROM DEVICE-GENERATED ENTROPY TO UNAFFECTED WALLETS *ASAP*.**\n\nAny funds on a **COLDCARD Mk3 using a firmware from version 4.0.1 (March 2021) to 4.1.9 (latest version until July 30th)**, where the entropy was only generated by the device, **should be considered compromised**. COLDCARD Mk4, Mk5, and Q are affected by the same issue to a lesser degree. Wallets generated by those devices are at risk of theft. Wallets created with externally generated entropy with at least 50 dice throws should not be exposed. Wallets that pair the device entropy with a passphrase are only as secure as the passphrase. If you used a weak passphrase (less than 25 random characters or fewer than seven BIP39 words) and did not provide external entropy (at least fifty dice throws), your funds are at risk.\n\nCoinkite has released firmware updates for COLDCARD Mk3, Mk4, Mk5, and Q. Wallets generated with the new firmware should be secure. **Updating to the new firmware does *not make affected wallets secure*. Only new wallets generated with the new firmware are unaffected.** Coinkite put out a [security advisory](https://blog.coinkite.com/coldcard-mk3-seed-generation-warning/). The security advisory has been updated to include more devices, more details about the issue, and migration advice.\n\nBlock security researchers reports that the COLDCARD Mk2 is affected the same way as the Mk3.\n\nAnyone with access to a frontier AI model is capable of reproducing the attack. Especially if you have funds on a COLDCARD single-sig wallet created with wallet-generated entropy, please carefully **move your funds to an unaffected wallet ASAP**. Single-sig wallets with a weak passphrase, or multisig wallets that can be spent by a quorum of COLDCARD wallets or composed only of COLDCARD wallets created with device-generated entropy should be considered **at risk** and funds should also be moved.", + "user": { + "name": "Murch" + } + }, + { + "createdAt": "2026-07-30T21:32:10.114Z", + "text": "update with complete timeline/story from reddit OP: https://www.reddit.com/r/Bitcoin/comments/1vb6teq/wallet_drained_timeline/", + "user": { + "name": "k00b" + } + }, + { + "createdAt": "2026-08-05T00:01:12.036Z", + "text": "1m zap for @Murch - This timely post certainly saved funds during an emergency. Thank you.", + "user": { + "name": "Kruw" + } + }, + { + "createdAt": "2026-07-30T18:47:43.894Z", + "text": "This is super weird. He says he only deposited to the wallet and never withdrew. If that's true, looks like he leaked his seed phrase. Doesn't seem like a Coldcard issue. Let's hold off for more info.", + "user": { + "name": "0xbitcoiner" + } + }, + { + "createdAt": "2026-07-31T00:12:37.929Z", + "text": "Block says they can confirm a second batch of transactions from before the batch that most people were made aware of:\n\nhttps://x.com/clay_garrett/status/2082980439367487724\n\nI think this is the same batch narceilo spotted:\n \nhttps://stacker.news/items/1536238/r/Scoresby?commentId=1536347", + "user": { + "name": "Scoresby" + } + }, + { + "createdAt": "2026-08-05T00:25:07.022Z", + "text": "Eeeh, _one million CCs stacked_?!", + "user": { + "name": "denlillaapan" + } + }, + { + "createdAt": "2026-07-30T20:38:10.917Z", + "text": "Kevin Loaec preliminary [conclusion](https://x.com/KLoaec/status/2082926304995762209):\n\n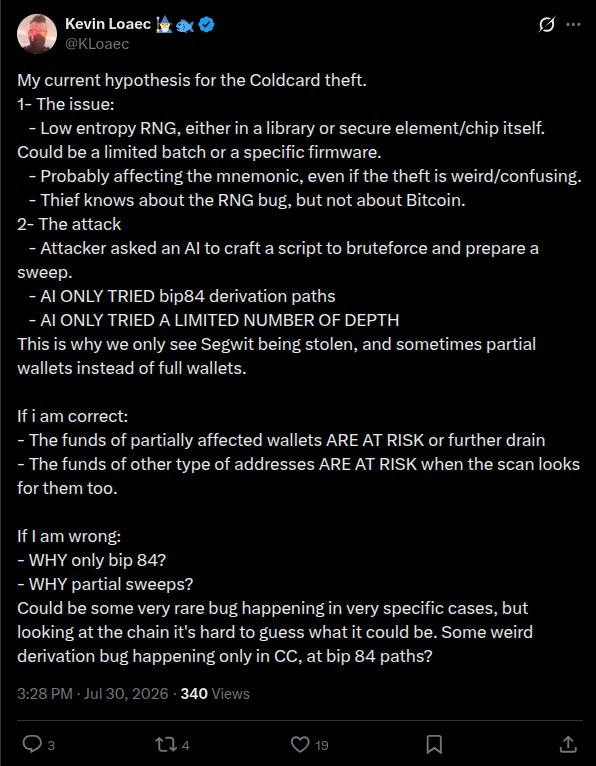\n\nLoaec is the founder of Wizardsardine and knows his way around bitcoin wallet stuff.", + "user": { + "name": "Scoresby" + } + }, + { + "createdAt": "2026-07-31T00:08:32.130Z", + "text": "###### Summary of Situation as of this Time\n\nAny funds on a **Coldcard Mk3 using a firmware version 4.0.1 (March 2021) or later, up to the *current* version**, where the entropy was generated by the Coldcard and it was not paired with a strong password, are at risk.\n\nCoinkite has put out a [security advisory](https://blog.coinkite.com/coldcard-mk3-seed-generation-warning/).\n\nIt looks like anyone with access to a regular LLM subscription is capable of reproducing the attack now. If this describes your wallet setup, please **move your funds to an unaffected wallet ASAP**. Please move deliberately enough to move your funds safely, people make mistakes when they rush.\n\nMk2 may also be at risk, unclear.", + "user": { + "name": "Murch" + } + }, + { + "createdAt": "2026-08-05T23:04:46.927Z", + "text": "I feel too bad anytime I hear of this.", + "user": { + "name": "Jacksoncarpenter" + } + }, + { + "createdAt": "2026-07-31T18:54:14.562Z", + "text": "anyone get any info on opendimes if they were affected at all?\nused them over the years to gift sats for weddings/graduations\n\nhavent seen much talk about them at all", + "user": { + "name": "falsefaucet" + } + }, + { + "createdAt": "2026-08-01T00:30:58.841Z", + "text": "Cannot trust other products from CoinKite either\n\nhttps://primal.net/e/nevent1qqs272yqcpr3awzapmhszf88yne3e8lh007y0ut2edtgjffpwxhgpcqdpnngp\n\nhttps://primal.net/e/nevent1qqsg9tzxn33k3agkg6qxclh0etqysh89u4cv6yjlz6y7ua9fsdlrt3gfvqtkw\n\n\n\n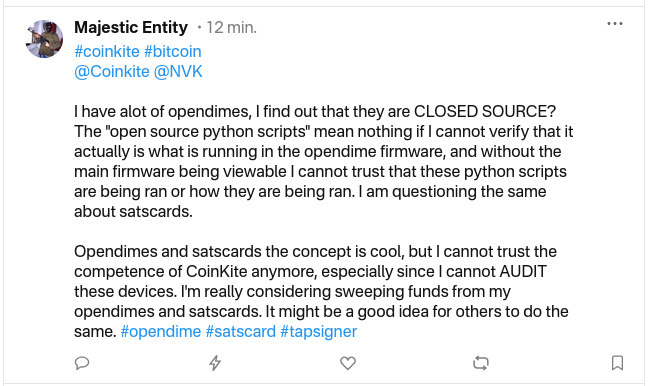\n\n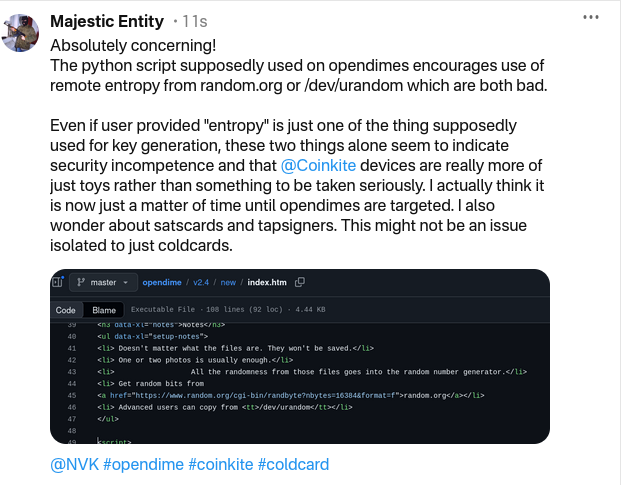", + "user": { + "name": "satonymous" + } + }, + { + "createdAt": "2026-07-30T23:17:38.208Z", + "text": "Superbly fast and comprehensible coverage on the situation. Thank you SN community", + "user": { + "name": "didiplaywell" + } + }, + { "createdAt": "2026-07-31T14:36:54.095Z", "text": "###### Summary of Situation as of this Time\n\n**ACTION RECOMMENDATION: PLEASE CAREFULLY MOVE FUNDS STORED ON COLDCARD WALLETS CREATED FROM DEVICE-GENERATED ENTROPY TO UNAFFECTED WALLETS *ASAP*.**\n\nAny funds on a **COLDCARD Mk3 using a firmware from version 4.0.1 (March 2021) to 4.1.9 (latest version as of yesterday)**, where the entropy was only generated by the device, **should be considered compromised**. COLDCARD Mk4, Mk5, and Q are affected by the same issue to a lesser degree. Wallets generated by those devices are at risk of theft. Wallets that pair the device entropy with a strong passphrase or wallets created with externally generated entropy with at least 50 dice throws should not be exposed. If you used a weak passphrase and did not input external entropy (at least fifty dice throws), your funds are at risk.\n\nCoinkite has released firmware updates for COLDCARD Mk3, Mk4, Mk5, and Q. Wallets generated with the new firmware should be secure. **Updating to the new firmware does *not make affected wallets secure*. Only new wallets generated with the new firmware are unaffected.** Coinkite put out a [security advisory](https://blog.coinkite.com/coldcard-mk3-seed-generation-warning/). The security advisory has been updated to include more devices, more details about the issue, and migration advice.\n\nBlock security researchers reports that the COLDCARD Mk2 is affected the same way as the Mk3.\n\nAnyone with access to a frontier AI model is capable of reproducing the attack. Especially if you have funds on a COLDCARD single-sig wallet created with wallet-generated entropy, please carefully **move your funds to an unaffected wallet ASAP**. Single-sig wallets with a weak passphrase, or multisig wallets that can be spent by a quorum of COLDCARD wallets or composed only of COLDCARD wallets created with device-generated entropy should be considered **at risk** and funds should also be moved.", "user": { "name": "Murch" - } - }, - { - "createdAt": "2026-07-30T21:32:10.114Z", - "text": "update with complete timeline/story from reddit OP: https://www.reddit.com/r/Bitcoin/comments/1vb6teq/wallet_drained_timeline/", - "user": { - "name": "k00b" - } - }, - { - "createdAt": "2026-08-05T00:01:12.036Z", - "text": "1m zap for @Murch - This timely post certainly saved funds during an emergency. Thank you.", - "user": { - "name": "Kruw" - } - }, - { - "createdAt": "2026-07-30T18:47:43.894Z", - "text": "This is super weird. He says he only deposited to the wallet and never withdrew. If that's true, looks like he leaked his seed phrase. Doesn't seem like a Coldcard issue. Let's hold off for more info.", - "user": { - "name": "0xbitcoiner" - } - }, - { - "createdAt": "2026-07-31T00:12:37.929Z", - "text": "Block says they can confirm a second batch of transactions from before the batch that most people were made aware of:\n\nhttps://x.com/clay_garrett/status/2082980439367487724\n\nI think this is the same batch narceilo spotted:\n \nhttps://stacker.news/items/1536238/r/Scoresby?commentId=1536347", - "user": { - "name": "Scoresby" - } - }, - { - "createdAt": "2026-08-05T00:25:07.022Z", - "text": "Eeeh, _one million CCs stacked_?!", - "user": { - "name": "denlillaapan" - } - }, - { - "createdAt": "2026-07-30T20:38:10.917Z", - "text": "Kevin Loaec preliminary [conclusion](https://x.com/KLoaec/status/2082926304995762209):\n\n\n\nLoaec is the founder of Wizardsardine and knows his way around bitcoin wallet stuff.", - "user": { - "name": "Scoresby" - } - }, - { - "createdAt": "2026-07-31T00:08:32.130Z", - "text": "###### Summary of Situation as of this Time\n\nAny funds on a **Coldcard Mk3 using a firmware version 4.0.1 (March 2021) or later, up to the *current* version**, where the entropy was generated by the Coldcard and it was not paired with a strong password, are at risk.\n\nCoinkite has put out a [security advisory](https://blog.coinkite.com/coldcard-mk3-seed-generation-warning/).\n\nIt looks like anyone with access to a regular LLM subscription is capable of reproducing the attack now. If this describes your wallet setup, please **move your funds to an unaffected wallet ASAP**. Please move deliberately enough to move your funds safely, people make mistakes when they rush.\n\nMk2 may also be at risk, unclear.", - "user": { - "name": "Murch" - } - }, - { - "createdAt": "2026-07-31T18:54:14.562Z", - "text": "anyone get any info on opendimes if they were affected at all?\nused them over the years to gift sats for weddings/graduations\n\nhavent seen much talk about them at all", - "user": { - "name": "falsefaucet" - } - }, - { - "createdAt": "2026-08-01T00:30:58.841Z", - "text": "Cannot trust other products from CoinKite either\n\nhttps://primal.net/e/nevent1qqs272yqcpr3awzapmhszf88yne3e8lh007y0ut2edtgjffpwxhgpcqdpnngp\n\nhttps://primal.net/e/nevent1qqsg9tzxn33k3agkg6qxclh0etqysh89u4cv6yjlz6y7ua9fsdlrt3gfvqtkw\n\n\n\n\n\n", - "user": { - "name": "satonymous" - } - }, - { - "createdAt": "2026-07-30T23:17:38.208Z", - "text": "Superbly fast and comprehensible coverage on the situation. Thank you SN community", - "user": { - "name": "didiplaywell" } }, {Extracted text as captured
{
  "data": {
    "item": {
      "comments": {
        "comments": [
          {
            "createdAt": "2026-08-05T21:35:21.769Z",
            "text": "###### Summary of Situation as of this Time\n\n**ACTION RECOMMENDATION: PLEASE CAREFULLY MOVE FUNDS STORED ON COLDCARD WALLETS CREATED FROM DEVICE-GENERATED ENTROPY TO UNAFFECTED WALLETS *ASAP*.**\n\nAny funds on a **COLDCARD Mk3 using a firmware from version 4.0.1 (March 2021) to 4.1.9 (latest version until July 30th)**, where the entropy was only generated by the device, **should be considered compromised**. COLDCARD Mk4, Mk5, and Q are affected by the same issue to a lesser degree. Wallets generated by those devices are at risk of theft. Wallets created with externally generated entropy with at least 50 dice throws should not be exposed. Wallets that pair the device entropy with a passphrase are only as secure as the passphrase.  If you used a weak passphrase (less than 25 random characters or fewer than seven BIP39 words) and did not provide external entropy (at least fifty dice throws), your funds are at risk.\n\nCoinkite has released firmware updates for COLDCARD Mk3, Mk4, Mk5, and Q. Wallets generated with the new firmware should be secure. **Updating to the new firmware does *not make affected wallets secure*. Only new wallets generated with the new firmware are unaffected.** Coinkite put out a [security advisory](https://blog.coinkite.com/coldcard-mk3-seed-generation-warning/). The security advisory has been updated to include more devices, more details about the issue, and migration advice.\n\nBlock security researchers reports that the COLDCARD Mk2 is affected the same way as the Mk3.\n\nAnyone with access to a frontier AI model is capable of reproducing the attack. Especially if you have funds on a COLDCARD single-sig wallet created with wallet-generated entropy, please carefully **move your funds to an unaffected wallet ASAP**. Single-sig wallets with a weak passphrase, or multisig wallets that can be spent by a quorum of COLDCARD wallets or composed only of COLDCARD wallets created with device-generated entropy should be considered **at risk** and funds should also be moved.",
            "user": {
              "name": "Murch"
            }
          },
          {
            "createdAt": "2026-07-30T21:32:10.114Z",
            "text": "update with complete timeline/story from reddit OP: https://www.reddit.com/r/Bitcoin/comments/1vb6teq/wallet_drained_timeline/",
            "user": {
              "name": "k00b"
            }
          },
          {
            "createdAt": "2026-08-05T00:01:12.036Z",
            "text": "1m zap for @Murch  - This timely post certainly saved funds during an emergency. Thank you.",
            "user": {
              "name": "Kruw"
            }
          },
          {
            "createdAt": "2026-07-30T18:47:43.894Z",
            "text": "This is super weird. He says he only deposited to the wallet and never withdrew. If that's true, looks like he leaked his seed phrase. Doesn't seem like a Coldcard issue. Let's hold off for more info.",
            "user": {
              "name": "0xbitcoiner"
            }
          },
          {
            "createdAt": "2026-07-31T00:12:37.929Z",
            "text": "Block says they can confirm a second batch of transactions from before the batch that most people were made aware of:\n\nhttps://x.com/clay_garrett/status/2082980439367487724\n\nI think this is the same batch narceilo spotted:\n \nhttps://stacker.news/items/1536238/r/Scoresby?commentId=1536347",
            "user": {
              "name": "Scoresby"
            }
          },
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
The thread gained a comment offering to connect someone with a purported drainer developer to review the tool and improve the wallet's defences.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 7 lines
"text": "", "user": { "name": "npub1zapsats" + } + }, + { + "createdAt": "2026-08-05T13:11:10.781Z", + "text": "I know a person who builds drainers if you guys want I can urge him to sell that drainer to someone who can review the drainer and update the coldcard wallet to prevent such drains... I have that person in contact", + "user": { + "name": "QuietHorizon" } }, {Extracted text as captured
{ "data": { "item": { "comments": { "comments": [ { "createdAt": "2026-07-31T14:36:54.095Z", "text": "###### Summary of Situation as of this Time\n\n**ACTION RECOMMENDATION: PLEASE CAREFULLY MOVE FUNDS STORED ON COLDCARD WALLETS CREATED FROM DEVICE-GENERATED ENTROPY TO UNAFFECTED WALLETS *ASAP*.**\n\nAny funds on a **COLDCARD Mk3 using a firmware from version 4.0.1 (March 2021) to 4.1.9 (latest version as of yesterday)**, where the entropy was only generated by the device, **should be considered compromised**. COLDCARD Mk4, Mk5, and Q are affected by the same issue to a lesser degree. Wallets generated by those devices are at risk of theft. Wallets that pair the device entropy with a strong passphrase or wallets created with externally generated entropy with at least 50 dice throws should not be exposed. If you used a weak passphrase and did not input external entropy (at least fifty dice throws), your funds are at risk.\n\nCoinkite has released firmware updates for COLDCARD Mk3, Mk4, Mk5, and Q. Wallets generated with the new firmware should be secure. **Updating to the new firmware does *not make affected wallets secure*. Only new wallets generated with the new firmware are unaffected.** Coinkite put out a [security advisory](https://blog.coinkite.com/coldcard-mk3-seed-generation-warning/). The security advisory has been updated to include more devices, more details about the issue, and migration advice.\n\nBlock security researchers reports that the COLDCARD Mk2 is affected the same way as the Mk3.\n\nAnyone with access to a frontier AI model is capable of reproducing the attack. Especially if you have funds on a COLDCARD single-sig wallet created with wallet-generated entropy, please carefully **move your funds to an unaffected wallet ASAP**. Single-sig wallets with a weak passphrase, or multisig wallets that can be spent by a quorum of COLDCARD wallets or composed only of COLDCARD wallets created with device-generated entropy should be considered **at risk** and funds should also be moved.", "user": { "name": "Murch" } }, { "createdAt": "2026-08-05T00:01:12.036Z", "text": "1m zap for @Murch - This timely post certainly saved funds during an emergency. Thank you.", "user": { "name": "Kruw" } }, { "createdAt": "2026-08-05T00:25:07.022Z", "text": "Eeeh, _one million CCs stacked_?!", "user": { "name": "denlillaapan" } }, { "createdAt": "2026-07-30T20:38:10.917Z", "text": "Kevin Loaec preliminary [conclusion](https://x.com/KLoaec/status/2082926304995762209):\n\n\n\nLoaec is the founder of Wizardsardine and knows his way around bitcoin wallet stuff.", "user": { "name": "Scoresby" } }, { "createdAt": "2026-07-31T18:54:14.562Z", "text": "anyone get any info on opendimes if they were affected at all?\nused them over the years to gift sats for weddings/graduations\n\nhavent seen much talk about them at all", "user": { "name": "falsefaucet" } },Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
The Stacker News thread gained a new participant reply.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 7 lines
             "text": "1m zap for @Murch  - This timely post certainly saved funds during an emergency. Thank you.",
             "user": {
               "name": "Kruw"
+            }
+          },
+          {
+            "createdAt": "2026-08-05T00:25:07.022Z",
+            "text": "Eeeh, _one million CCs stacked_?!",
+            "user": {
+              "name": "denlillaapan"
             }
           },
           {
Extracted text as captured
{ "data": { "item": { "comments": { "comments": [ { "createdAt": "2026-07-31T14:36:54.095Z", "text": "###### Summary of Situation as of this Time\n\n**ACTION RECOMMENDATION: PLEASE CAREFULLY MOVE FUNDS STORED ON COLDCARD WALLETS CREATED FROM DEVICE-GENERATED ENTROPY TO UNAFFECTED WALLETS *ASAP*.**\n\nAny funds on a **COLDCARD Mk3 using a firmware from version 4.0.1 (March 2021) to 4.1.9 (latest version as of yesterday)**, where the entropy was only generated by the device, **should be considered compromised**. COLDCARD Mk4, Mk5, and Q are affected by the same issue to a lesser degree. Wallets generated by those devices are at risk of theft. Wallets that pair the device entropy with a strong passphrase or wallets created with externally generated entropy with at least 50 dice throws should not be exposed. If you used a weak passphrase and did not input external entropy (at least fifty dice throws), your funds are at risk.\n\nCoinkite has released firmware updates for COLDCARD Mk3, Mk4, Mk5, and Q. Wallets generated with the new firmware should be secure. **Updating to the new firmware does *not make affected wallets secure*. Only new wallets generated with the new firmware are unaffected.** Coinkite put out a [security advisory](https://blog.coinkite.com/coldcard-mk3-seed-generation-warning/). The security advisory has been updated to include more devices, more details about the issue, and migration advice.\n\nBlock security researchers reports that the COLDCARD Mk2 is affected the same way as the Mk3.\n\nAnyone with access to a frontier AI model is capable of reproducing the attack. Especially if you have funds on a COLDCARD single-sig wallet created with wallet-generated entropy, please carefully **move your funds to an unaffected wallet ASAP**. Single-sig wallets with a weak passphrase, or multisig wallets that can be spent by a quorum of COLDCARD wallets or composed only of COLDCARD wallets created with device-generated entropy should be considered **at risk** and funds should also be moved.", "user": { "name": "Murch" } }, { "createdAt": "2026-08-05T00:01:12.036Z", "text": "1m zap for @Murch - This timely post certainly saved funds during an emergency. Thank you.", "user": { "name": "Kruw" } }, { "createdAt": "2026-08-05T00:25:07.022Z", "text": "Eeeh, _one million CCs stacked_?!", "user": { "name": "denlillaapan" } }, { "createdAt": "2026-07-30T20:38:10.917Z", "text": "Kevin Loaec preliminary [conclusion](https://x.com/KLoaec/status/2082926304995762209):\n\n\n\nLoaec is the founder of Wizardsardine and knows his way around bitcoin wallet stuff.", "user": { "name": "Scoresby" } }, { "createdAt": "2026-07-31T18:54:14.562Z", "text": "anyone get any info on opendimes if they were affected at all?\nused them over the years to gift sats for weddings/graduations\n\nhavent seen much talk about them at all", "user": { "name": "falsefaucet" } },Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
The Stacker News thread gained a reply thanking Murch for the timely emergency post.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 7 lines
             "text": "###### Summary of Situation as of this Time\n\n**ACTION RECOMMENDATION: PLEASE CAREFULLY MOVE FUNDS STORED ON COLDCARD WALLETS CREATED FROM DEVICE-GENERATED ENTROPY TO UNAFFECTED WALLETS *ASAP*.**\n\nAny funds on a **COLDCARD Mk3 using a firmware from version 4.0.1 (March 2021) to 4.1.9 (latest version as of yesterday)**, where the entropy was only generated by the device, **should be considered compromised**. COLDCARD Mk4, Mk5, and Q are affected by the same issue to a lesser degree. Wallets generated by those devices are at risk of theft. Wallets that pair the device entropy with a strong passphrase or wallets created with externally generated entropy with at least 50 dice throws should not be exposed. If you used a weak passphrase and did not input external entropy (at least fifty dice throws), your funds are at risk.\n\nCoinkite has released firmware updates for COLDCARD Mk3, Mk4, Mk5, and Q. Wallets generated with the new firmware should be secure. **Updating to the new firmware does *not make affected wallets secure*. Only new wallets generated with the new firmware are unaffected.** Coinkite put out a [security advisory](https://blog.coinkite.com/coldcard-mk3-seed-generation-warning/). The security advisory has been updated to include more devices, more details about the issue, and migration advice.\n\nBlock security researchers reports that the COLDCARD Mk2 is affected the same way as the Mk3.\n\nAnyone with access to a frontier AI model is capable of reproducing the attack. Especially if you have funds on a COLDCARD single-sig wallet created with wallet-generated entropy, please carefully **move your funds to an unaffected wallet ASAP**. Single-sig wallets with a weak passphrase, or multisig wallets that can be spent by a quorum of COLDCARD wallets or composed only of COLDCARD wallets created with device-generated entropy should be considered **at risk** and funds should also be moved.",
             "user": {
               "name": "Murch"
+            }
+          },
+          {
+            "createdAt": "2026-08-05T00:01:12.036Z",
+            "text": "1m zap for @Murch  - This timely post certainly saved funds during an emergency. Thank you.",
+            "user": {
+              "name": "Kruw"
             }
           },
           {
Extracted text as captured
{ "data": { "item": { "comments": { "comments": [ { "createdAt": "2026-07-31T14:36:54.095Z", "text": "###### Summary of Situation as of this Time\n\n**ACTION RECOMMENDATION: PLEASE CAREFULLY MOVE FUNDS STORED ON COLDCARD WALLETS CREATED FROM DEVICE-GENERATED ENTROPY TO UNAFFECTED WALLETS *ASAP*.**\n\nAny funds on a **COLDCARD Mk3 using a firmware from version 4.0.1 (March 2021) to 4.1.9 (latest version as of yesterday)**, where the entropy was only generated by the device, **should be considered compromised**. COLDCARD Mk4, Mk5, and Q are affected by the same issue to a lesser degree. Wallets generated by those devices are at risk of theft. Wallets that pair the device entropy with a strong passphrase or wallets created with externally generated entropy with at least 50 dice throws should not be exposed. If you used a weak passphrase and did not input external entropy (at least fifty dice throws), your funds are at risk.\n\nCoinkite has released firmware updates for COLDCARD Mk3, Mk4, Mk5, and Q. Wallets generated with the new firmware should be secure. **Updating to the new firmware does *not make affected wallets secure*. Only new wallets generated with the new firmware are unaffected.** Coinkite put out a [security advisory](https://blog.coinkite.com/coldcard-mk3-seed-generation-warning/). The security advisory has been updated to include more devices, more details about the issue, and migration advice.\n\nBlock security researchers reports that the COLDCARD Mk2 is affected the same way as the Mk3.\n\nAnyone with access to a frontier AI model is capable of reproducing the attack. Especially if you have funds on a COLDCARD single-sig wallet created with wallet-generated entropy, please carefully **move your funds to an unaffected wallet ASAP**. Single-sig wallets with a weak passphrase, or multisig wallets that can be spent by a quorum of COLDCARD wallets or composed only of COLDCARD wallets created with device-generated entropy should be considered **at risk** and funds should also be moved.", "user": { "name": "Murch" } }, { "createdAt": "2026-08-05T00:01:12.036Z", "text": "1m zap for @Murch - This timely post certainly saved funds during an emergency. Thank you.", "user": { "name": "Kruw" } }, { "createdAt": "2026-07-30T20:38:10.917Z", "text": "Kevin Loaec preliminary [conclusion](https://x.com/KLoaec/status/2082926304995762209):\n\n\n\nLoaec is the founder of Wizardsardine and knows his way around bitcoin wallet stuff.", "user": { "name": "Scoresby" } }, { "createdAt": "2026-07-31T18:54:14.562Z", "text": "anyone get any info on opendimes if they were affected at all?\nused them over the years to gift sats for weddings/graduations\n\nhavent seen much talk about them at all", "user": { "name": "falsefaucet" } }, { "createdAt": "2026-08-01T00:30:58.841Z", "text": "Cannot trust other products from CoinKite either\n\nhttps://primal.net/e/nevent1qqs272yqcpr3awzapmhszf88yne3e8lh007y0ut2edtgjffpwxhgpcqdpnngp\n\nhttps://primal.net/e/nevent1qqsg9tzxn33k3agkg6qxclh0etqysh89u4cv6yjlz6y7ua9fsdlrt3gfvqtkw\n\n\n\n\n\n", "user": { "name": "satonymous" } },Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 0 lines
Extracted text as captured
{ "data": { "item": { "comments": { "comments": [ { "createdAt": "2026-07-31T14:36:54.095Z", "text": "###### Summary of Situation as of this Time\n\n**ACTION RECOMMENDATION: PLEASE CAREFULLY MOVE FUNDS STORED ON COLDCARD WALLETS CREATED FROM DEVICE-GENERATED ENTROPY TO UNAFFECTED WALLETS *ASAP*.**\n\nAny funds on a **COLDCARD Mk3 using a firmware from version 4.0.1 (March 2021) to 4.1.9 (latest version as of yesterday)**, where the entropy was only generated by the device, **should be considered compromised**. COLDCARD Mk4, Mk5, and Q are affected by the same issue to a lesser degree. Wallets generated by those devices are at risk of theft. Wallets that pair the device entropy with a strong passphrase or wallets created with externally generated entropy with at least 50 dice throws should not be exposed. If you used a weak passphrase and did not input external entropy (at least fifty dice throws), your funds are at risk.\n\nCoinkite has released firmware updates for COLDCARD Mk3, Mk4, Mk5, and Q. Wallets generated with the new firmware should be secure. **Updating to the new firmware does *not make affected wallets secure*. Only new wallets generated with the new firmware are unaffected.** Coinkite put out a [security advisory](https://blog.coinkite.com/coldcard-mk3-seed-generation-warning/). The security advisory has been updated to include more devices, more details about the issue, and migration advice.\n\nBlock security researchers reports that the COLDCARD Mk2 is affected the same way as the Mk3.\n\nAnyone with access to a frontier AI model is capable of reproducing the attack. Especially if you have funds on a COLDCARD single-sig wallet created with wallet-generated entropy, please carefully **move your funds to an unaffected wallet ASAP**. Single-sig wallets with a weak passphrase, or multisig wallets that can be spent by a quorum of COLDCARD wallets or composed only of COLDCARD wallets created with device-generated entropy should be considered **at risk** and funds should also be moved.", "user": { "name": "Murch" } }, { "createdAt": "2026-07-30T20:38:10.917Z", "text": "Kevin Loaec preliminary [conclusion](https://x.com/KLoaec/status/2082926304995762209):\n\n\n\nLoaec is the founder of Wizardsardine and knows his way around bitcoin wallet stuff.", "user": { "name": "Scoresby" } }, { "createdAt": "2026-07-31T18:54:14.562Z", "text": "anyone get any info on opendimes if they were affected at all?\nused them over the years to gift sats for weddings/graduations\n\nhavent seen much talk about them at all", "user": { "name": "falsefaucet" } }, { "createdAt": "2026-08-01T00:30:58.841Z", "text": "Cannot trust other products from CoinKite either\n\nhttps://primal.net/e/nevent1qqs272yqcpr3awzapmhszf88yne3e8lh007y0ut2edtgjffpwxhgpcqdpnngp\n\nhttps://primal.net/e/nevent1qqsg9tzxn33k3agkg6qxclh0etqysh89u4cv6yjlz6y7ua9fsdlrt3gfvqtkw\n\n\n\n\n\n", "user": { "name": "satonymous" } }, { "createdAt": "2026-07-30T23:17:38.208Z", "text": "Superbly fast and comprehensible coverage on the situation. Thank you SN community", "user": { "name": "didiplaywell" } },Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
2 presentation-noise differences. Sidebar, ticker and other page chrome churn that our review classified as not being changes to what the source says.
- +60 -60 Comment ordering churn only: the same set of comments (Murch, Scoresby, satonymous, didiplaywell, 028559d218 and others) appears in a different order with no new or changed text.
- +28 -28 The GraphQL response reordered already captured comments, including the existing advisory summary and timeline links. No comment text changed.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.