Galaxy Research identifies third wave of Coldcard hacks, attacks ongoing
stackernews-galaxy-third-wave
- Organisation
- Stacker News
- Evidence role
- Community discussion
- Published
- 2026-08-01
- Source changes
- 0
- Detected differences
- 0
- Unreviewed
- 0
- Copies held
- 1
Scoresby relaying Galaxy Research's identification of a third wave of drains, 207.7294 BTC, taking the estimated observed total to 1,367.05 BTC. The numbers are Galaxy's reported figures; Galaxy's own publications are registered separately. Captured through the site's public GraphQL API: the rendered pages crash the capture tab, and the API answers POST from this host. The query fixes the captured surface to the item's title, text and two levels of comments, each with author and absolute timestamp.
Every check is recorded, including checks that found no text change. A detected edit is therefore bounded between two checks. The publisher's exact save time is not observable from this record. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
Held captures
-
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 0 lines
Extracted text as captured
{ "data": { "item": { "comments": { "comments": [ { "createdAt": "2026-08-01T20:11:04.482Z", "text": "See, the same damn thing would happen if you buried your money in a treasure chest out in the wilderness. \"*I'll come back for it in 20 years.*\"Many people in history have been wrecked this way because shit happens.\n\nYou can't just drop your money into cold storage and tune the entire world out. Believe me I get that temptation, but holy shit, you need to maintain enough social ties with the network for someone to text you to say, \"*Hey there's a problem!*\"\n\nThis is really unfortunate at this point. Each successive wave is pissing me off more because where the hell are these guys and why haven't they secured their property yet? I know they surely have some reason, but damn 🤦♂️😩", "user": { "name": "Aeneas" } }, { "createdAt": "2026-08-02T05:32:42.060Z", "text": "I'm no expert, but this confirms there's more than one attacker. I'd say it's a team, since with the sheer number of wallets affected, it would be very difficult for one person to do it!\n\nJust to be clear, I'm not an expert like you guys!", "user": { "name": "mkmloom" } }, { "createdAt": "2026-08-01T19:50:00.538Z", "text": "https://twiiit.com/glxyresearch/status/2083623500183421043", "user": { "name": "nitter" } }, { "createdAt": "2026-08-02T02:16:46.090Z", "text": "*deleted by author*", "user": { "name": "crenshaw" } } ] }, "createdAt": "2026-08-01T19:49:32.331Z", "text": "> 🚨 A 3rd wave in what we suspect are hacks of Coldcard-generated addresses has been identified in which 207.7294 BTC has been drained.\n>\n> Our estimated observed size of the Coldcard hack is now 1,367.05 BTC (\\~$88.6m) across 4,585 addresses.\n\n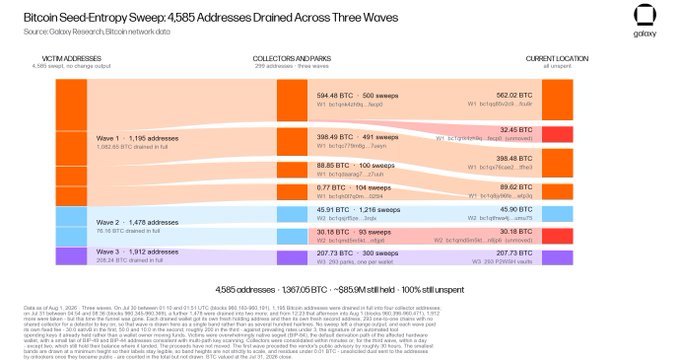\n\n> Before this thread continues, we must disclaim that this data is derived solely from analyzing Bitcoin block data and the unspent-output set. We have not utilized compute to test whether the addresses we have identified as possible victims were indeed generated with low entropy. Some initial addresses were received from victim reports on X and used to build the initial onchain topographies. This analysis represents our best effort on short notice and should not be considered to be complete or definitive, and is for informational purposes only. Nothing in these threads should be considered investment advice or a recommendation whether or how to own or store BTC.\n>\n> Waves 1 and 2 followed similar patterns: the same funnel topology into a handful of shared collectors, the same P2WPKH destinations, the same mix of derivation paths, 27 hours apart. Treating them as one operator is reasonable, but it rests on resemblance, not on proof, and they already differ in two respects — the fee constant, and whether the sweeps signal replace-by-fee.\n>\n> Even if we can assume Waves 1 and 2 are the same attacker, Wave 3 should not be assumed to be the same operator. It differs from both earlier waves on every behavioural axis we can measure: it abandons the shared collector for one destination per victim, it holds in P2WSH rather than P2WPKH, it batches an average of 6.37 victims into each sweep where wave 1 took exactly one, and it scans only the default derivation path.\n>\n> It may be the same actor with rebuilt tooling — the anti-clustering design is exactly the evolution one would predict after waves 1 and 2 were enumerated — or it may be a second actor working the same vulnerable key space independently, which the published disclosures make entirely feasible. The chain does not distinguish these, nor can we.\n>\n> While we are confident Wave 1 is one operator, Wave 2 is one operator, and Wave 3 is one operator, outside of the pattern similarity between Waves 1 and 2 describe in the prior post above, we cannot definitively link any of the waves together.\n\n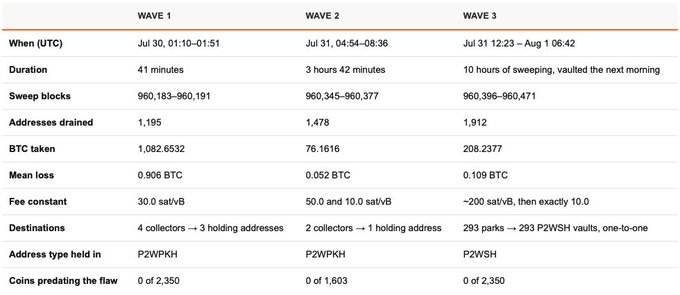\n\n> Addresses drained per block across all 3 waves. Within each wave, intervening blocks contain no identifiable hacker sweep activity, suggesting that the sweep transactions were broadcast in batches rather than streamed. Bars below are one slot per block and not to scale in time.\n\n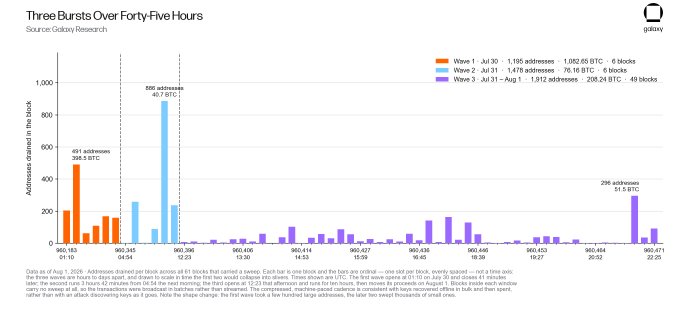\n\n> Total under attacker control: 1,366.3865 BTC (\\~$88.6m). All endpoint attacker addresses remain fully unspent onchain.\n\n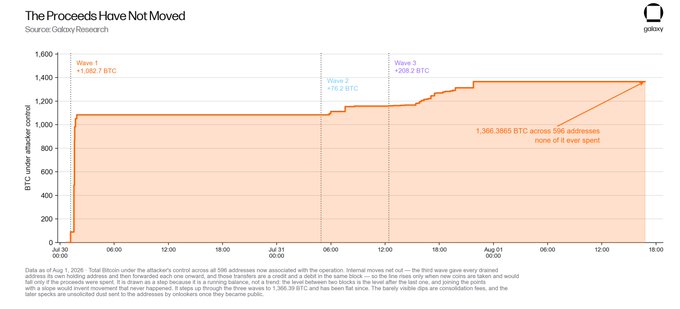\n\n> The loss profile is dominated by sub-1 BTC addresses in count, but by larger addresses in value. This appears to be the shape of individual self-custody, not institutional holdings.\n\n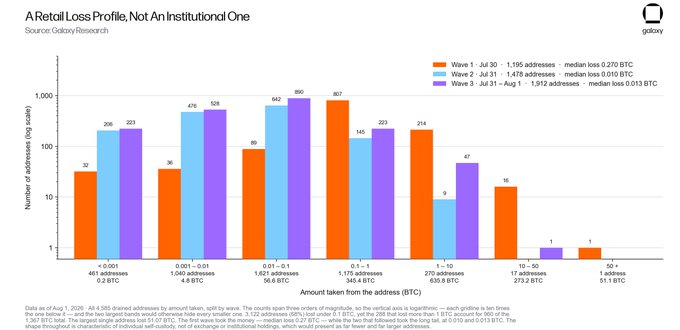\n\n> The vulnerable Coldcard firmware shipped on March 17, 2021 around block 674,951. Not one of the coins we have identified in Waves 1-3 taken was created before that block.\n\n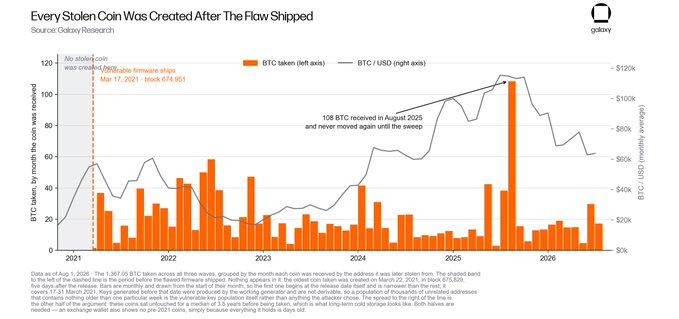\n\n> The same population counted by address rather by value. Each drained address placed in the month it last received anything, which is the last time it moved before being drained.\n\n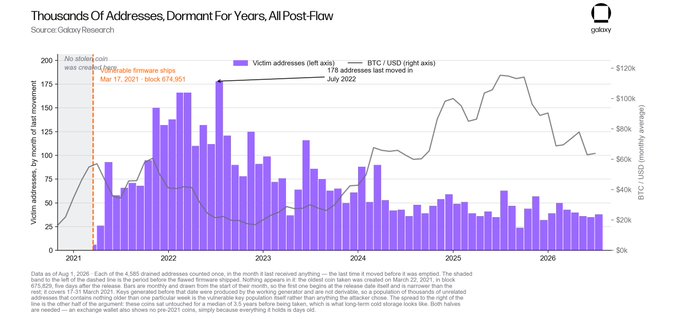\n\n> We are actively monitoring these 7 addresses from Waves 1 and 2, which collectively hold 1,158.8148 BTC:\n> \n> bc1qq85v2c926eg6pgxhwp6q7lf6cnsz80qs3fcu9r\n> bc1qx76cae2706qd5q576feh7xq8rfcsjpf2htfhe3\n> bc1q8jy96fe5lf8vfugydnte3cguk92gpev7kwtp3q\n> bc1qtfrwa4j6rmj9rsgspv6a0yjumkg39js2numu75\n> bc1qnk4zh9qcnap2mycp56qjrgza3cc8ylrh8fecp0\n> bc1qmd5m5ktv7m5ffujxv4248fxv36myvdx79n8jp6\n> bc1qsjrf5ze5tmulz7y2x4pc7qaex2a35sanp3rqlx\n> \n> We are also monitoring 293 P2WSH vaults that received funds in Wave 3. Because these are are P2WSH and unspent, their scripts are hidden. The first spend from any of them will reveal its script, and a cosigner key reused across two vaults could help us definitively connect them.\n\n> f you become aware of other suspected attacker addresses or victim addresses, reply here or DM [@intangiblecoins](https://x.com/intangiblecoins) and we will do our best to add them to our investigation.", "title": "Galaxy Research identifies third wave of Coldcard hacks, attacks ongoing", "user": { "name": "Scoresby"Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
0 presentation-noise differences. Sidebar, ticker and other page chrome churn that our review classified as not being changes to what the source says.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.