Illustrated incident explainer thread
bitcoindevs-explainer-thread
Latest reviewed change
source content difference between and
The reply from men13542 saying 'Info here' was removed; both captures reached 11 scroll rounds with capped: false.
 @grok
  is ledger and Trezor safe in this context?

-post: 2084309796178800954
-role: reply
-author: men13542
-name: men13542
-created: 2026-08-03T16:05:54Z
First lines only. The complete diff is in the timeline below.
- Author
- @Bitcoin_Devs
- Organisation
- independent
- Evidence role
- reporting
- Posted
- 2 Aug 2026, 13:45 UTC
- Capture status
- capture held
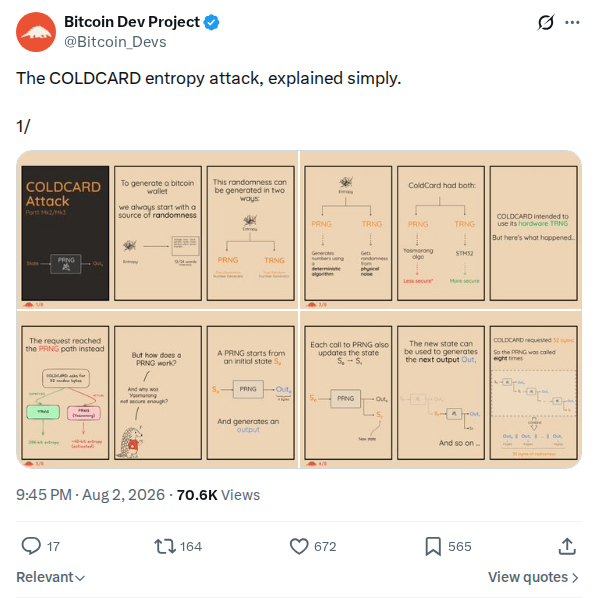
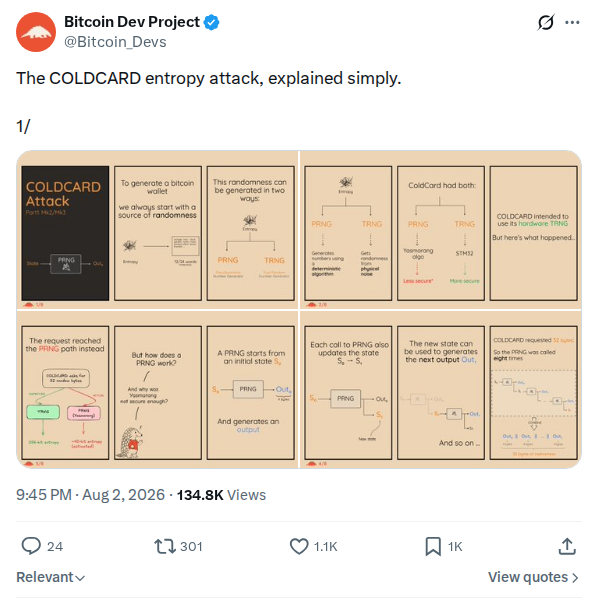
An illustrated thread explaining the entropy attack simply; held as a record of how the incident was being explained to a general audience. Only the first post was held until 7 Aug 2026, when the conversation was added to the curated thread tier.
This post is registered as evidence and has a locally held capture. The original remains the canonical publication. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
The conversation
Captured . 2 continuation posts, 27 replies held, 6 muted as low signal. Posts are in the archive's own order, oldest first, not the order X ranks them in.
-
capture taken
The COLDCARD entropy attack, explained simply. 1/
-
capture taken
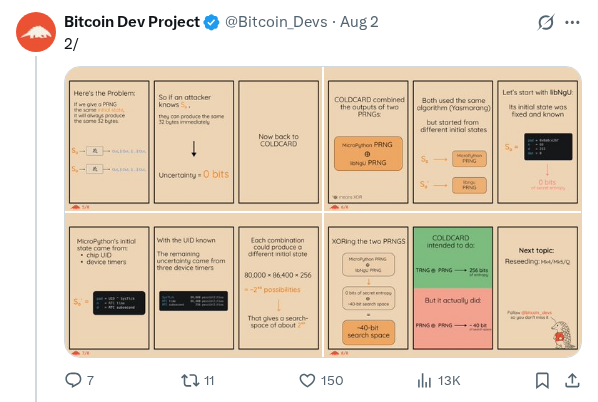
2/
-
capture taken
Follow @Bitcoin_Devs for next post on part 2 on Mk4/Mk5/Q
Replies held in this capture (27)
Low-signal replies are collapsed to one line, never removed. A reply is collapsed only on mechanical grounds: fewer than 40 characters, no text, mentions only, no letters or digits, a bare link, or text identical to another reply in the same capture. What a reply argues is never a reason. Each one says which rule collapsed it, and its screenshot is one click away.
-
capture taken
Watch tax tasks disappear. Submit to ATO faster with LodgeiT. Company tax lodgements from $60. Try for free.
show the capture
capture taken
-
capture taken
please do a set explaining the difference between CSRNG's, PRNG's and TRNG's, most PRNG's start with a seed, since every algorithm is deterministic, you cant change the output and since you cant start from "0", you need an input or seed, hence entering the same seed = same output
show the capture
capture taken
-
capture taken
noted a PRNG vs CSPRNG set is on the list for this week
show the capture
capture taken
-
capture taken
I hate being a double digit IQ Hick. This might aswell be cuniform lmao. Why can't this stuff be simple, i just wanna store my £££ without the fear of it being nabbed lmfao.
show the capture
capture taken
-
capture taken
@AndreSeverini
show the capture
capture taken
-
capture taken
Why did you flip TRNG and PRNG in slide 3? Confusing!
show the capture
capture taken
-
capture taken
its too simple for me
show the capture
capture taken
-
capture taken
ai slop
show the capture
capture taken
-
capture taken
Great post. Thanks.
show the capture
capture taken
-
capture taken
Basically it’s supposed to use hardware to generate and and if that’s not there use software A dev turned off the hardware look side of things due to an error compiling so it therefore just used the weak software side to generate. This bug was known to them it seems for over 4yrs look at Reddit posts right now, someone flagged they got emptied in 2021
show the capture
capture taken
-
capture taken
Why did those cold cards default to not true random?
show the capture
capture taken
-
capture taken
Very cool DYOR tool. Thanks for sharing.
show the capture
capture taken
The remaining 15 replies
-
this is great! How does anyone know what an individual chip UID is for the micropython PRNG?
show the capture
capture taken
-
With the new software, is it safe to create a new address using dice? Or did this affect other things in Coldcard Q?
show the capture
capture taken
-
Crypto will never be mainstream when this is considered ”simply explained”
show the capture
capture taken
-
This all goes to demonstrate that even if Bitcoin were cryptographically perfect or unbreakable, the layers on top required for most laypeople to use it never will be.
show the capture
capture taken
-
Rodolfo had one job.
show the capture
capture taken
-
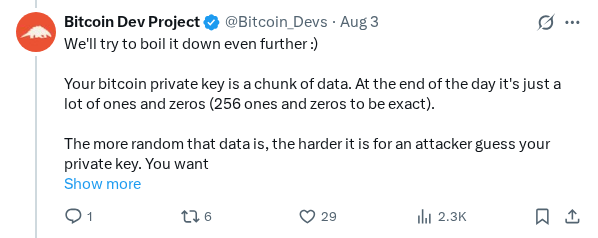
We'll try to boil it down even further :) Your bitcoin private key is a chunk of data. At the end of the day it's just a lot of ones and zeros (256 ones and zeros to be exact). The more random that data is, the harder it is for an attacker guess your private key. You want your private key to be as random as possible. Humans are very bad at being random, we are always making patterns. Machines are pretty bad at it too. You can't write a mathematical algorithm to make random outputs. The best way to get random data is to take it from something physical. That can be voltage fluctuations in a device's underlying hardware, rolling dice, or even photos of lava lamps! Coldcard thought it was using true random numbers from a physical source like the underlying hardware, but it wasn't. There was a bug in the code that caused it to use numbers that were only kind of random (psuedo random) ones generated by a mathematical algorithm. This meant that instead of there being 2^256 possible values for your private key, there were only 2^40 possible values. It's far easier for an attacker to guess your private key from 2^40 possible values, and on specialized GPUs that you can rent, it only takes 20-45 minutes. That's less than $1 of compute. This bug went unnoticed for over 5 years and it has opened up many conversations on the importance of open-source software and peer review, the consequences of influencer culture (some people were storing bitcoin with Coldcards without really knowing how to use them), and how engineers can use AI (or sometimes can't because of closed models) to vet their code for vulnerabilities before attackers find them. It's wild out there right now, be safe! Multi-signature using devices from multiple different vendors seems to continue to be the gold standard, but if that is too advanced, there is a whole spectrum of other options. At this point, anything is better than keeping funds on a Coldcard MK2/MK3 and to a lesser extent, the more recent models which also have the same vulnerability but not as bad.
show the capture
capture taken
-
entropy attacks on hardware wallets are the kind of vulnerability you can't fix with a firmware update
show the capture
capture taken
-
This is why you need to fail loudly
show the capture
capture taken
-
That breakdown makes the whole entropy concept much easier to visualize.
show the capture
capture taken
-
@grok is ledger and Trezor safe in this context?
show the capture
capture taken
-
Entropy attacks on Coldcard boil down to bad RNG. If the hardware can't generate true randomness, your keys aren't as private as you think.
show the capture
capture taken
-
The Yasmarang PRNG in the MicroPython code? There’s certainly a case to be made for that
show the capture
capture taken
-
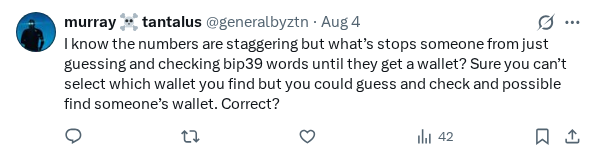
I know the numbers are staggering but what’s stops someone from just guessing and checking bip39 words until they get a wallet? Sure you can’t select which wallet you find but you could guess and check and possible find someone’s wallet. Correct?
show the capture
capture taken
-
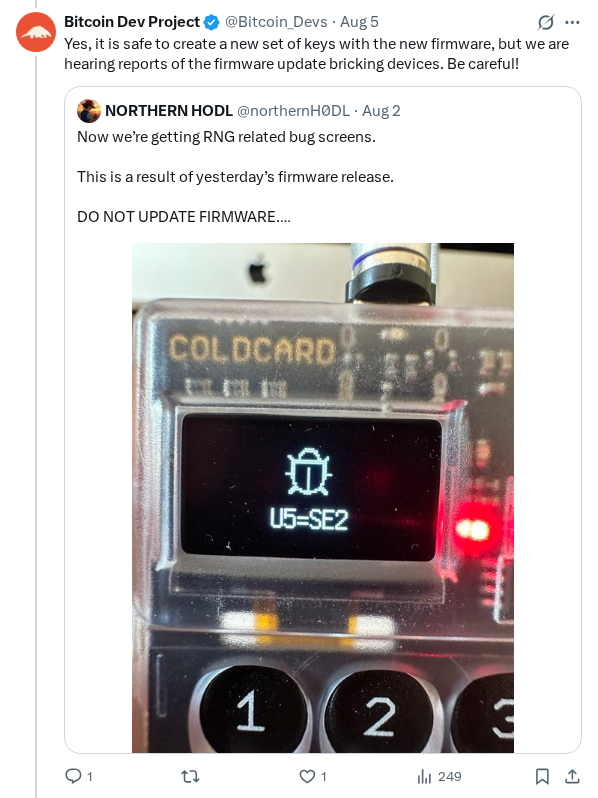
Yes, it is safe to create a new set of keys with the new firmware, but we are hearing reports of the firmware update bricking devices. Be careful!
show the capture
capture taken
-
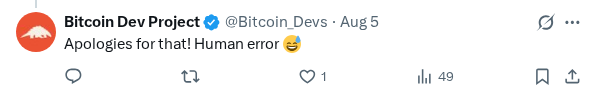
Apologies for that! Human error
show the capture
capture taken
This capture reached the end of the conversation as X served it: it stopped because nothing further loaded, not because a limit was hit. X decides what a reader is shown, so that is not the same as a guarantee of every reply.
Held captures
-
The reply from men13542 saying 'Info here' was removed; both captures reached 11 scroll rounds with capped: false.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 9 lines
 @grok
  is ledger and Trezor safe in this context?

-post: 2084309796178800954
-role: reply
-author: men13542
-name: men13542
-created: 2026-08-03T16:05:54Z
-media: 0
-body:
-Info here
-
 post: 2084327779223617641
 role: reply
 author: AstraXLabs
Extracted text as captured
thread: 2083912081255153897
url: https://x.com/Bitcoin_Devs/status/2083912081255153897
author: Bitcoin_Devs

post: 2083912081255153897
role: focal
author: Bitcoin_Devs
name: Bitcoin Dev Project
created: 2026-08-02T13:45:32Z
media: 4
body:
The COLDCARD entropy attack, explained simply.

1/

post: 2083912086086935035
role: self-thread
author: Bitcoin_Devs
name: Bitcoin Dev Project
created: 2026-08-02T13:45:33Z
media: 4
body:
2/

post: 2083913545532793048
role: self-thread
author: Bitcoin_Devs
name: Bitcoin Dev Project
created: 2026-08-02T13:51:21Z
media: 0
body:
Follow
@Bitcoin_Devs
 for next post on part 2 on Mk4/Mk5/Q

post: 2083949593260073000
role: reply
author: OikosBack
name: Oiko
created: 2026-08-02T16:14:35Z
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
Two replies appear for the first time and none leaves: meirelindo asking on 2 August whether it is safe to create a new address with dice under the new software, and the Bitcoin Dev Project account answering on 5 August that it is but that devices are being reported bricked by the firmware update. Both predate the previous capture, posts observed rose from 28 to 30, and no gap was declared in either state, so this is collection recovering replies an earlier scroll missed rather than the conversation growing.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 20 lines
 body:
 this is great!  How does anyone know what an individual chip UID is for the micropython PRNG?

+post: 2084036698325815570
+role: reply
+author: meirelindo
+name: @meirelindo
+created: 2026-08-02T22:00:43Z
+media: 0
+body:
+With the new software, is it safe to create a new address using dice?
+
+Or did this affect other things in Coldcard Q?
+
 post: 2084041637852787155
 role: reply
 author: joinduelcom
 body:
 I know the numbers are staggering but what’s stops someone from just guessing and checking bip39 words until they get a wallet? Sure you can’t select which wallet you find but you could guess and check and possible find someone’s wallet. Correct?

+post: 2084849733705560486
+role: reply
+author: Bitcoin_Devs
+name: Bitcoin Dev Project
+created: 2026-08-05T03:51:25Z
+media: 1
+body:
+Yes, it is safe to create a new set of keys with the new firmware, but we are hearing reports of the firmware update bricking devices. Be careful!
+
 post: 2084850669001847071
 role: reply
 author: Bitcoin_Devs
Extracted text as captured
thread: 2083912081255153897
url: https://x.com/Bitcoin_Devs/status/2083912081255153897
author: Bitcoin_Devs

post: 2083912081255153897
role: focal
author: Bitcoin_Devs
name: Bitcoin Dev Project
created: 2026-08-02T13:45:32Z
media: 4
body:
The COLDCARD entropy attack, explained simply.

1/

post: 2083912086086935035
role: self-thread
author: Bitcoin_Devs
name: Bitcoin Dev Project
created: 2026-08-02T13:45:33Z
media: 4
body:
2/

post: 2083913545532793048
role: self-thread
author: Bitcoin_Devs
name: Bitcoin Dev Project
created: 2026-08-02T13:51:21Z
media: 0
body:
Follow
@Bitcoin_Devs
 for next post on part 2 on Mk4/Mk5/Q

post: 2083949593260073000
role: reply
author: OikosBack
name: Oiko
created: 2026-08-02T16:14:35Z
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 0 lines
Extracted text as captured
thread: 2083912081255153897
url: https://x.com/Bitcoin_Devs/status/2083912081255153897
author: Bitcoin_Devs

post: 2083912081255153897
role: focal
author: Bitcoin_Devs
name: Bitcoin Dev Project
created: 2026-08-02T13:45:32Z
media: 4
body:
The COLDCARD entropy attack, explained simply.

1/

post: 2083912086086935035
role: self-thread
author: Bitcoin_Devs
name: Bitcoin Dev Project
created: 2026-08-02T13:45:33Z
media: 4
body:
2/

post: 2083913545532793048
role: self-thread
author: Bitcoin_Devs
name: Bitcoin Dev Project
created: 2026-08-02T13:51:21Z
media: 0
body:
Follow
@Bitcoin_Devs
 for next post on part 2 on Mk4/Mk5/Q

post: 2083949593260073000
role: reply
author: OikosBack
name: Oiko
created: 2026-08-02T16:14:35Z
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
5 presentation-noise differences. Sidebar, ticker and other page chrome churn that our review classified as not being changes to what the source says.
- +9 -9 A single promotional reply record was swapped for another; capped remained false, posts_observed and replies_observed stayed the same at 30 and 27, and scroll rounds stayed at 8, indicating ranking churn.
- +9 -0 A single promotional reply record was added; capped remained false, posts_observed rose from 29 to 30, and scroll rounds fell from 11 to 8, indicating ranking recovery rather than new content.
- +20 -0 Two older replies re-entered the ranked view (a dice-safety question and a firmware-update bricking warning); both captures reached 29 posts/26 replies at 11 scroll rounds, so this is ranking recovery.
- +0 -20 Two replies were absent from the shallower capture (10 scroll rounds and 24 replies observed versus 11 scroll rounds and 26 replies, capped false), so the change is under-collection rather than deletion.
- +0 -20 X reply-load variance: two earlier replies (meirelindo asking whether dice-generated keys are safe on the new firmware, and the Bitcoin_Devs answer cautioning about reports of bricked devices) drop out of the capture with unchanged bodies and timestamps. The browser capture sees a different reply subset per load.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.