7 August update: $111M confirmed, 1,719 BTC, 25+ patterns
glxyresearch-2085748513015488758
Latest reviewed change
source content difference between and
A new reply from jordanschochet links the Galaxy report's Aug 6 date to a Kalshi self-certification change and alleges a separate Kalshi hack; an unrelated ad reply also re-entered the capture.
 media: 0
 body:
 multiple actors is a bigger finding than the total. does the footprint clustering separate distinct actors, or just distinct sweep sessions?
+
+post: 2087106875112522093
+role: reply
+author: ryoran_ads
+name: 百花繚乱 剣姫クロニクル_デベロッパー
First lines only. The complete diff is in the timeline below.
- Author
- @glxyresearch
- Organisation
- Galaxy Research
- Evidence role
- on-chain-analysis
- Posted
- 7 Aug 2026, 23:59 UTC
- Capture status
- capture held
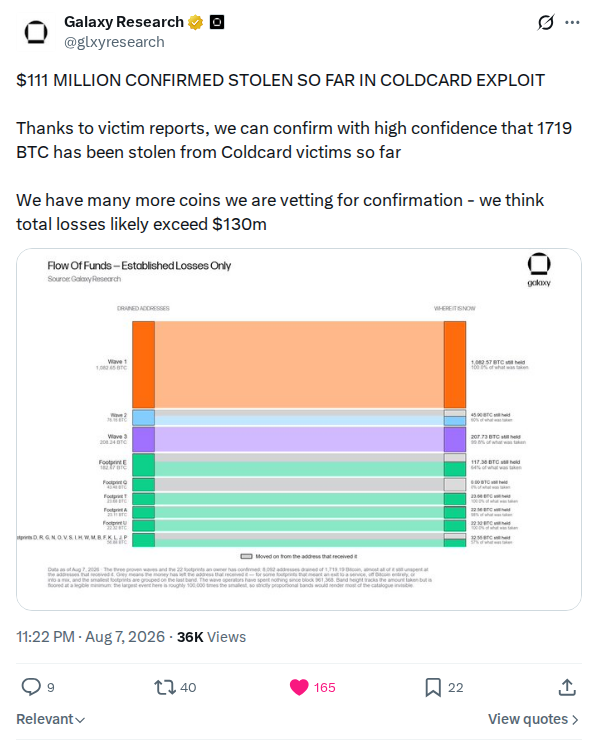
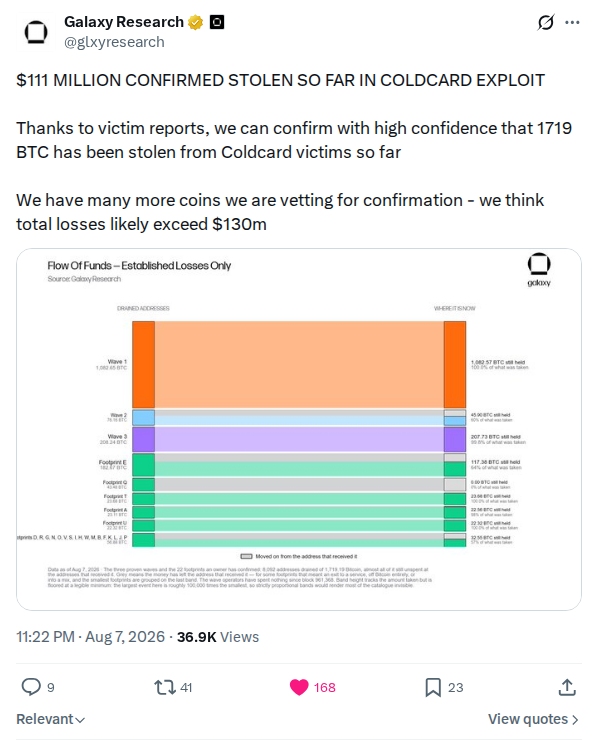
Galaxy Research 7 August 2026 update: $111 million confirmed stolen so far, 1,719 BTC with high confidence, 25+ separate attack patterns, 250+ victim reports to @intangiblecoins, no stolen coin created before the 17 March 2021 affected-firmware release. This supersedes the 1,596 BTC / ~7,300 address figure in glxy-losses-exceed-100m and is the basis for the state-changed flags on the 8 August 2026 claim sweep.
This post is registered as evidence and has a locally held capture. The original remains the canonical publication. Last checked .
This post is held twice: here, with this project's own note on why it matters, and again as part of the conversation captured at , which is polled for changes. Both copies are the same post; neither is a separate event.
Snapshot and diff bodies for this chain monitor are held in the local evidence archive but withheld from the public site because they can contain the addresses of people who published nothing themselves. Capture times and reviewed change summaries remain available below.
The conversation
Captured . 5 continuation posts, 9 replies held, 3 muted as low signal. Posts are in the archive's own order, oldest first, not the order X ranks them in.
-
capture taken
$111 MILLION CONFIRMED STOLEN SO FAR IN COLDCARD EXPLOIT Thanks to victim reports, we can confirm with high confidence that 1719 BTC has been stolen from Coldcard victims so far We have many more coins we are vetting for confirmation - we think total losses likely exceed $130m
-
capture taken
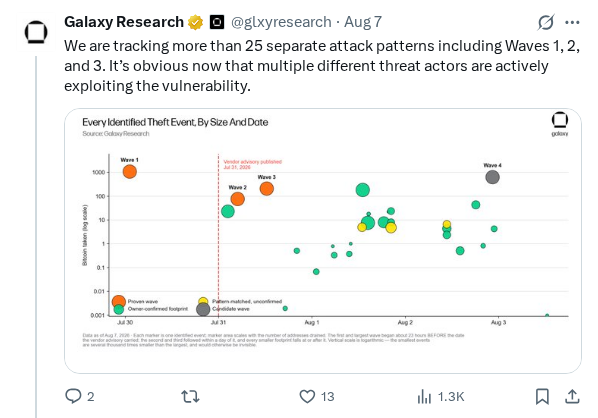
We are tracking more than 25 separate attack patterns including Waves 1, 2, and 3. It’s obvious now that multiple different threat actors are actively exploiting the vulnerability.
-
capture taken
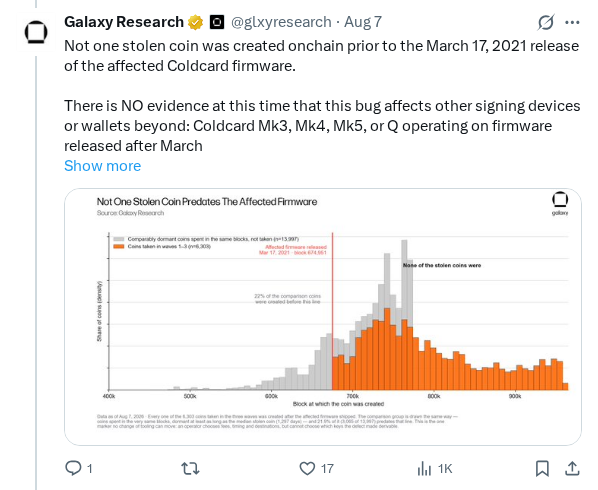
Not one stolen coin was created onchain prior to the March 17, 2021 release of the affected Coldcard firmware. There is NO evidence at this time that this bug affects other signing devices or wallets beyond: Coldcard Mk3, Mk4, Mk5, or Q operating on firmware released after March 17, 2021
-
capture taken
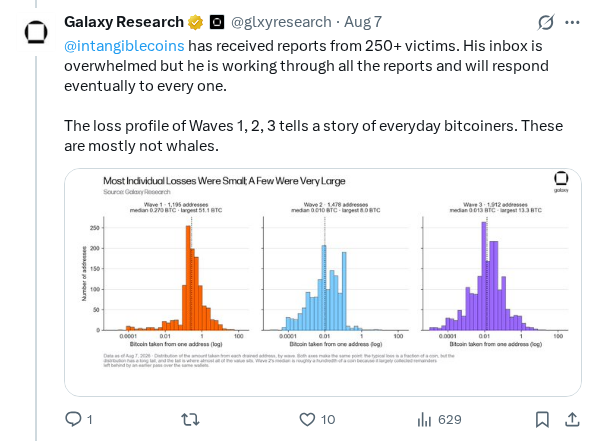
@intangiblecoins has received reports from 250+ victims. His inbox is overwhelmed but he is working through all the reports and will respond eventually to every one. The loss profile of Waves 1, 2, 3 tells a story of everyday bitcoiners. These are mostly not whales.
-
capture taken
We only promote victims and attackers into the confirmed set if we have high confidence (usually established by multiple confirmations from victim reports). The chart below shows how our outstanding candidates for promotion would take the total loss to 2300+ BTC if we ultimately promote them.
-
capture taken
Please continue sending victim reports to @intangiblecoins via DM. Alex’s robots can get started the quickest if you share correct list of bitcoin addresses that were drained in the first message. There are many victims and reports to sort through but he will ultimately respond to everyone.
Replies held in this capture (9)
Low-signal replies are collapsed to one line, never removed. A reply is collapsed only on mechanical grounds: fewer than 40 characters, no text, mentions only, no letters or digits, a bare link, or text identical to another reply in the same capture. What a reply argues is never a reason. Each one says which rule collapsed it, and its screenshot is one click away.
-
capture taken
another day another exploit
show the capture
capture taken
-
capture taken
This is getting out of control
show the capture
capture taken
-
capture taken
Thank you for your work and keeping and eye on this. I lost my life savings of 6.8 Bitcoin due to this absurd negligence. I hope a class action lawsuit eventually surfaces.
show the capture
capture taken
-
capture taken
devastating to say the least
show the capture
capture taken
-
capture taken
How you only have 23k followers, your work is amazing :D
show the capture
capture taken
-
capture taken
one more spin has never once been one more spin
show the capture
capture taken
-
capture taken
multiple actors is a bigger finding than the total. does the footprint clustering separate distinct actors, or just distinct sweep sessions?
show the capture
capture taken
-
capture taken
Longer Than Ever. 30 seconds Per Video Output Seedance 2.5 Video Model Is Officially Available on Framia. Imagine how many dreams you can make in one generation? AI-Powered by Converge AI
show the capture
capture taken
-
capture taken
@glxyresearch this is highly speculative..but I have been posting about what appears to be a BAD hack hitting Kalshi (see my profile). The Aug 6 date in your report caught my attention- happens to be the date Kalshi self certified a bizarre change re allowing advanced deposits to Kalshi before on-chain confirmation. And in prior posts I shared clear evidence of Kalshi reporting Perp data that is 100% wrong. Kalshi prime reports $50mm of net capital, which would aline with the wave 1 attack aum. https:// kalshi.com/prime "Re: Kalshi Klear LLC – Additional Method to Enable Self-Clearing Members to Receive Pre-funded Amounts of In-Transit USDC Deposits Before On-chain Confirmation of Funds" https:// kalshi.com/regulatory/not ices … pdf below https:// kalshi-public-docs.s3.amazonaws.com/regulatory/not ices/COVER%20LETTER-Additional%20Method%20to%20Deposit%20U.S.%20Dollars%208.6.26.pdf …
show the capture
capture taken
The remaining 0 replies
This capture reached the end of the conversation as X served it: it stopped because nothing further loaded, not because a limit was hit. X decides what a reader is shown, so that is not the same as a guarantee of every reply.
Held captures
-
A new reply from jordanschochet links the Galaxy report's Aug 6 date to a Kalshi self-certification change and alleges a separate Kalshi hack; an unrelated ad reply also re-entered the capture.
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 39 lines
 media: 0
 body:
 multiple actors is a bigger finding than the total. does the footprint clustering separate distinct actors, or just distinct sweep sessions?
+
+post: 2087106875112522093
+role: reply
+author: ryoran_ads
+name: 百花繚乱 剣姫クロニクル_デベロッパー
+created:
+media: 0
+body:
+No download, free to play
+
+W-What are you looking at! Fool!
+Claim $600 of Items Now
+
+post: 2088417554997903807
+role: reply
+author: jordanschochet
+name: Jordan Schochet
+created: 2026-08-15T00:08:40Z
+media: 0
+body:
+@glxyresearch
+ this is highly speculative..but I have been posting about what appears to be a BAD hack hitting Kalshi (see my profile).
+
+The Aug 6 date in your report caught my attention- happens to be the date Kalshi self certified a bizarre change re allowing advanced deposits to Kalshi before on-chain confirmation. And in prior posts I shared clear evidence of Kalshi reporting Perp data that is 100% wrong. Kalshi prime reports $50mm of net capital, which would aline with the wave 1 attack aum.
+https://
+kalshi.com/prime
+
+"Re: Kalshi Klear LLC – Additional Method to Enable Self-Clearing Members to Receive Pre-funded Amounts of In-Transit USDC Deposits Before On-chain Confirmation of Funds"
+
+https://
+kalshi.com/regulatory/not
+ices
+…
+pdf below
+
+https://
+kalshi-public-docs.s3.amazonaws.com/regulatory/not
+ices/COVER%20LETTER-Additional%20Method%20to%20Deposit%20U.S.%20Dollars%208.6.26.pdf
+…
Extracted text as captured
thread: 2085748513015488758
url: https://x.com/glxyresearch/status/2085748513015488758
author: glxyresearch

post: 2085748513015488758
role: focal
author: glxyresearch
name: Galaxy Research
created: 2026-08-07T15:22:51Z
media: 1
body:
$111 MILLION CONFIRMED STOLEN SO FAR IN COLDCARD EXPLOIT

Thanks to victim reports, we can confirm with high confidence that 1719 BTC has been stolen from Coldcard victims so far

We have many more coins we are vetting for confirmation - we think total losses likely exceed $130m

post: 2085748519625707727
role: self-thread
author: glxyresearch
name: Galaxy Research
created: 2026-08-07T15:22:53Z
media: 1
body:
We are tracking more than 25 separate attack patterns including Waves 1, 2, and 3. It’s obvious now that multiple different threat actors are actively exploiting the vulnerability.

post: 2085748526034690520
role: self-thread
author: glxyresearch
name: Galaxy Research
created: 2026-08-07T15:22:54Z
media: 1
body:
Not one stolen coin was created onchain prior to the March 17, 2021 release of the affected Coldcard firmware.

There is NO evidence at this time that this bug affects other signing devices or wallets beyond: Coldcard Mk3, Mk4, Mk5, or Q operating on firmware released after March 17, 2021

post: 2085748532208656819
role: self-thread
author: glxyresearch
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
-
Recovered from the Internet Archive rather than captured by this project. The row records that third-party provenance separately from captures made by this project.
What changed from the previous capture 0 lines
Extracted text as captured
thread: 2085748513015488758
url: https://x.com/glxyresearch/status/2085748513015488758
author: glxyresearch

post: 2085748513015488758
role: focal
author: glxyresearch
name: Galaxy Research
created: 2026-08-07T15:22:51Z
media: 1
body:
$111 MILLION CONFIRMED STOLEN SO FAR IN COLDCARD EXPLOIT

Thanks to victim reports, we can confirm with high confidence that 1719 BTC has been stolen from Coldcard victims so far

We have many more coins we are vetting for confirmation - we think total losses likely exceed $130m

post: 2085748519625707727
role: self-thread
author: glxyresearch
name: Galaxy Research
created: 2026-08-07T15:22:53Z
media: 1
body:
We are tracking more than 25 separate attack patterns including Waves 1, 2, and 3. It’s obvious now that multiple different threat actors are actively exploiting the vulnerability.

post: 2085748526034690520
role: self-thread
author: glxyresearch
name: Galaxy Research
created: 2026-08-07T15:22:54Z
media: 1
body:
Not one stolen coin was created onchain prior to the March 17, 2021 release of the affected Coldcard firmware.

There is NO evidence at this time that this bug affects other signing devices or wallets beyond: Coldcard Mk3, Mk4, Mk5, or Q operating on firmware released after March 17, 2021

post: 2085748532208656819
role: self-thread
author: glxyresearch
Excerpt only. The complete copy is held offline and backs quotations on this site. The original publication remains the canonical public source.
1 presentation-noise difference. Sidebar, ticker and other page chrome churn that our review classified as not being a change to what the source says.
- +11 -6 One promotional ad reply was swapped for another; capped remained false, posts_observed and replies_observed stayed at 15 and 9, and scroll rounds rose from 9 to 10, while the substantive reply remained present.
The excerpts and plain unified diffs above show the text this project held and how it changed. To verify a quotation, compare it against the page itself or against the Internet Archive's copies, which are independent of this project.
Complete captures are held offline rather than mirrored here, so this page shows diffs and excerpts. If a quotation is ever disputed, the full copy can be produced. Ask.
Compare the screenshot or a quotation against the original while it is available.