Public statements and actions
What organisations and individuals said they were doing after disclosure. The record keeps product guidance, operational claims, commercial positions and community actions attributed to the people who published them.
Custody providers published key-rotation and threshold-policy guidance on 31 July. Competing wallet vendors published their own scope and scam warnings. On 2 August Coinkite reported halting shipments, destroying affected stock, contacting customers and supporting migration, then acknowledged lasting damage in a Sunday update. By 6 and 7 August it was describing continuing firmware work while saying it will very likely not be around, and had published a temporary suspension of its customer-data blanking; a custody provider had begun telling customers to replace the device. Community participants also described outreach and organisational changes. Unless the underlying action is independently visible, these are records of what each publisher said, not confirmation that every described action occurred. R1
Custody providers and wallet vendors
Guidance, product-scope claims, and the interests behind them
These statements answer different questions. Unchained and Casa described changes to customer policies. Ledger and Trezor described their own implementations and said they were not affected. None is treated as a neutral comparison of custody products.
-
Rotate every COLDCARD-generated key
Unchained recommended replacing every COLDCARD-generated key with one generated on another device. It described two COLDCARD-generated keys in its 2-of-3 vault as the most severe case, while saying one affected key is normally below threshold. R2
-
Keep one manufacturer's failure below threshold
Casa presented multi-key, multi-vendor custody as a way to keep a single manufacturer's failure below a spending threshold. Nick Neuman also published a migration video using Casa. Both have a commercial interest in the service being recommended, and the result depends on the policy and origin of every key in it. R3
-
A competing vendor says its devices are not affected
Ledger attributed its not-affected claim to a true-random-number generator inside its Secure Element and said each 24-word recovery phrase receives 256 bits of entropy. This archive holds the statement but has not independently reviewed that implementation. Ledger is a competing hardware-wallet vendor. R4
-
A second competing vendor says its devices are not affected
Trezor said wallets originally generated on a Trezor are unaffected, described its own generation as drawing on several independent sources of randomness including the connected host and, on newer models, a Secure Element, and told anyone who restored a Coldcard-generated backup onto a Trezor to migrate to a newly generated wallet. This archive has not independently reviewed that implementation. Trezor is a competing hardware-wallet vendor. R5 On 6 August Trezor edited that article: where it had told affected readers to follow Coinkite's official guidance, it now points them at Trezor's own instructions. V6
-
A support page starts recommending device replacement
Casa added a security advisory to its Coldcard troubleshooting page saying that funds generated on affected firmware may be at risk and that it does recommend replacing the device as soon as the owner is able. Casa dates the advisory 1 August; this collector held the page without it on 3 August and with it on 6 August, so the record fixes only when it appeared here. Casa sells a multi-key service that Coldcard devices can be part of, and has a commercial interest in the advice it gives about them. R7 The same day Casa's chief security officer published an account of what the company did after 30 July: reviewing every place its own systems touch entropy and key generation, running its automated pentest out of cycle weighted toward this class of defect, contacting members with affected devices below their vault quorum, and offering free security consultations to non-members migrating off an affected setup. None of those internal actions is observable from this archive, and the consultation offer is an offer to prospective customers. R8
-
A free multisig workshop offered to people reconsidering their setup
Casa announced a live session on moving from one key to multiple keys across different hardware vendors, addressed to people whom the incident has prompted to reconsider how they hold bitcoin. The session promotes the company's own product area, and the workshop itself is not something this archive observed. R9
The threshold mechanics behind the provider statements live on the technical conditions page. The publishers' migration recommendations and their limits live in the migration record.
Coinkite's operational statements
Shipments, stock, customer contact, support and the Sunday update
The statements below are the vendor's own accounts of operations that are not observable from this archive. They are preserved as published and linked to the captured posts.
-
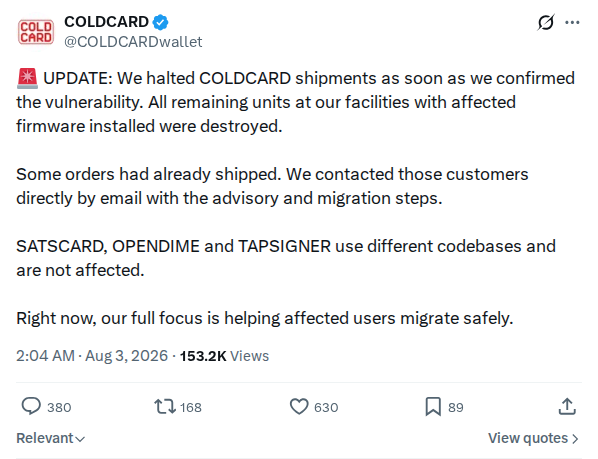
Shipments halted and remaining affected stock destroyed
Coinkite said it halted shipments once the vulnerability was confirmed, destroyed remaining units carrying affected firmware and emailed customers whose devices had shipped. The post also said SATSCARD, OPENDIME and TAPSIGNER use different codebases and are not affected. R10
 captured
-
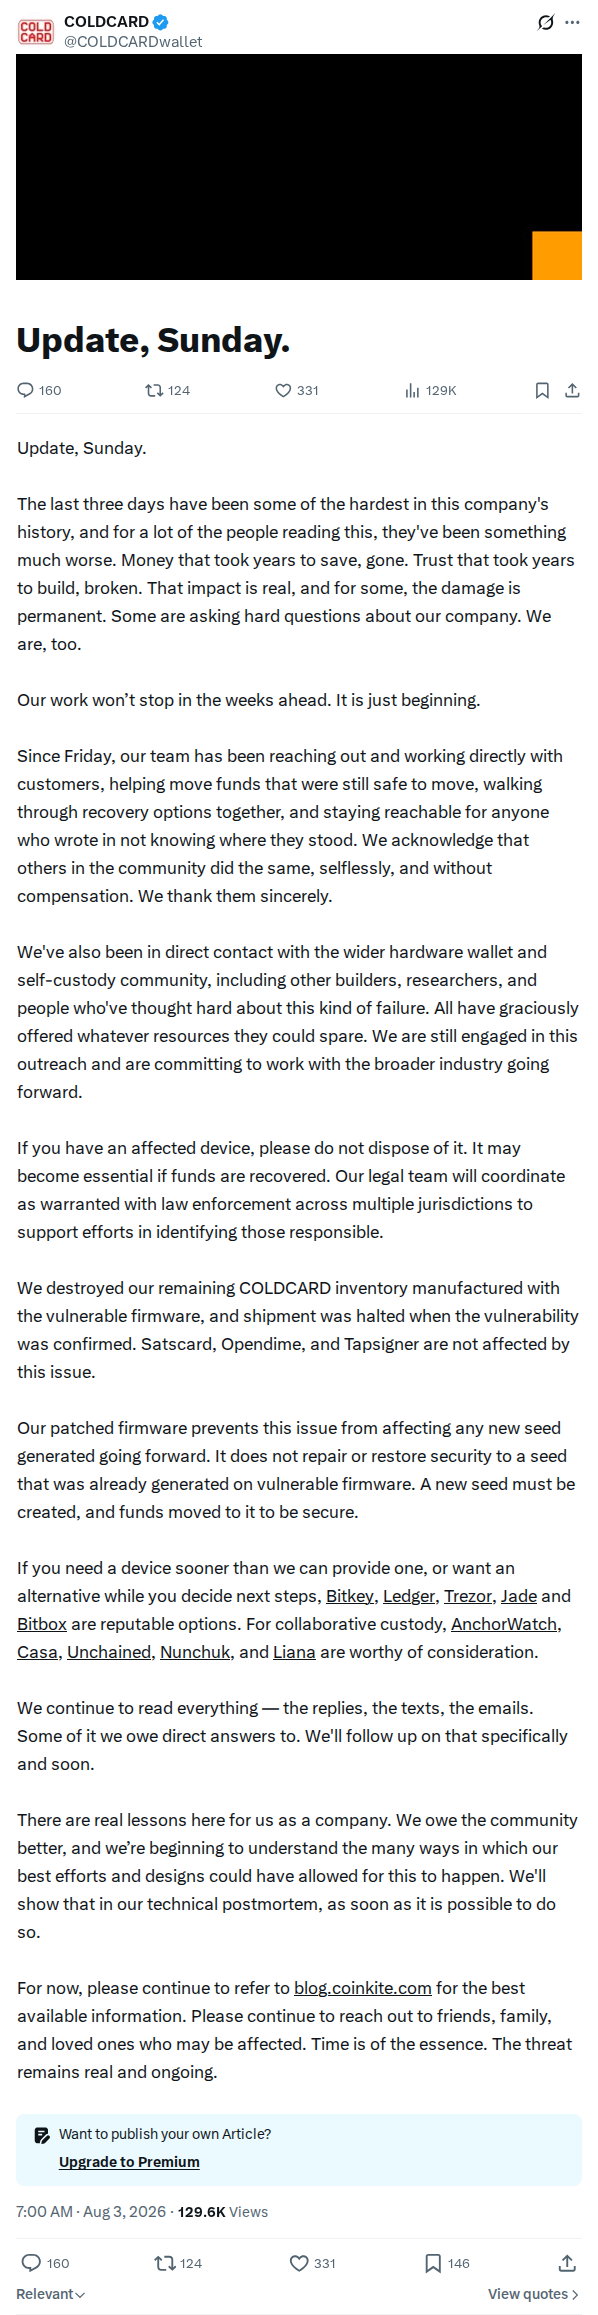
The Sunday update acknowledges lasting damage
The vendor described customer outreach and migration help, thanked community members who helped through the weekend and said the damage done is permanent, with hard questions remaining about the company. R11
 captured
-
Firmware work pointed at GitHub, and customer key migration
The vendor said its next firmware updates can be followed on GitHub and that it was focusing on the next release and on customer key migration. What that work consists of is visible in the firmware repositories the record already tracks; the description of priorities is the vendor's own. R12
-
More releases promised, alongside doubt that the company survives
Replying to a question and to two critics in three posts within seven minutes, the vendor said it had multiple pull requests under review with new versions coming, that it was doing all the investigation it can and was devastated, adding that the hacker could have disclosed responsibly, and that it was very likely not going to be around but should keep trying to give people the best firmware it can. The 2 August Sunday update had put the same subject as hard questions remaining about the company; the 7 August reply states an expectation rather than a question. R13
No held source carries Coinkite's own words on the scale of customer losses. Two held sources relay a Bloomberg report of 6 August that the vendor will publish a post-mortem once its investigation is complete and declines to estimate those losses: a Cointelegraph post of 7 August and a BitcoinTalk post of the same day that quotes the report at greater length. The Bloomberg article itself is not held here, and neither relay is a capture of anything Coinkite published. R14
The outreach and data-retention exchange
Coinkite said phone numbers and customer personal data are deleted, that many customers were therefore unreachable by email and that an earlier post could have been worded better. R15 Satochip then asked how store customers received emails if Coinkite deletes data after 90 days. The 90-day period is Satochip's premise, not an established fact, and Satochip is a competing hardware-wallet vendor. R16 Coinkite's separate June paper-spam statement gives 120 days for deletion of customer data including physical addresses. On 7 August Coinkite published an update on customer data retention that states the same period: its standard practice is to blank customer records automatically after 120 days, retaining only email addresses and country of residence, with accelerated blanking available on request after delivery. The same post says that automated blanking has been temporarily suspended because of legal obligations arising from the incident, and that a customer who does not want their data preserved may ask for the standard policy to be applied instead. V17 That account puts the period at 120 days rather than the 90 days Satochip's question assumed, and puts email addresses among the fields the blanking keeps rather than among those it removes. Both the 2 August reply and the 7 August post are the vendor's own accounts of its own systems, and no held source tests either against what was actually stored.
Wider public positions
Arguments prompted by the incident, not findings the incident can settle
NCFA Canada argued that self custody removes the custodian but not the vendor layer beneath it: the device, its firmware, seed-generation code and update path. This defect did sit in that layer. Its comparison with regulated custody is an argument about where risk is placed, not something this incident measures, and its loss figures are carried secondhand from Galaxy Research. NCFA Canada is a fintech industry association whose members include financial-technology and digital-asset businesses. R18
On 7 August Ledger published an argument by its chief technology officer that open source is valuable but is not itself a security property, quoting the line that a security model resting on the crowd saving you is a hope rather than a model. That is a position about how review works, prompted by this incident rather than settled by it, and the linked article is not held here: the record holds the post and the line it quotes. Ledger is a competing hardware-wallet vendor whose not-affected statement is recorded above. R19
Other broad positions are kept beside the evidence needed to read them: the open-source and AI discovery dispute, dice claims, and the first-spend debate. This avoids maintaining a second verdict table here.
Community and organisational actions
Outreach, support and a board departure published during the incident weekend
-
An endorsement apology and an account of migration help
Bent apologised to people who bought a COLDCARD on his recommendation and described spending the weekend helping people move funds. R20
-
A community member describes direct owner outreach
One individual described finding older posts that mentioned buying a COLDCARD and replying with an alert about the incident, while accepting the risk of account moderation. R21
-
NVK steps down from the OpenSats board
OpenSats announced the departure as immediately effective and said the board would continue with eight members. The post gave no reason. Its timing falls within the incident weekend, but the source itself does not connect the two. R22
-
Code RED: priority funding for people red teaming Bitcoin software
The same organisation announced a funding path for people auditing critical Bitcoin software after the incident, including reimbursement of past LLM token costs, and said it would prioritise those applications for the foreseeable future. The post frames the programme as support for the people who spent the days after disclosure triaging and red teaming. Whether any grant was made is not visible from this archive. V23
Evidence on this page 23 items
- R1 Reported · contested
The dated overview of provider, vendor and community statements on this page
Source Primary posts and publications preserved in the linked source records
Evidence → captured
- R2 Reported · contested
Unchained's incident guidance and its assessment of 2-of-3 vault exposure
Source Unchained's captured public guidance
Evidence → captured 1 Aug 2026
- R3 Reported · contested
Casa's multi-vendor-custody position and Neuman's migration and risk claim
Source Casa and Nick Neuman, captured primary posts; commercial interest stated above
Evidence → captured 1 Aug 2026
- R4 Reported · contested
Ledger's not-affected statement and its description of its entropy architecture
Source Ledger's captured primary post; implementation not independently assessed here
Evidence → captured 1 Aug 2026
- R5 Reported · contested
Trezor's not-affected statement, its description of its own entropy sources and its instruction to holders of restored Coldcard backups
Source Trezor's captured article; implementation not independently assessed here
Evidence → captured 6 Aug 2026
- V6 Verified · contested
The 6 August wording change from Coinkite's official guidance to Trezor's own instructions
Source Diff between the held 6 August captures of the same article
Evidence → captured
- R7 Reported · contested
Casa's advisory text and its recommendation to replace the device
Source Casa's captured support page; the advisory is absent from the 3 August capture and present in the 6 August one, and Casa's own banner date is 1 August; commercial interest stated above
Evidence → captured 6 Aug 2026
- R8 Reported · contested
Casa's account of its own post-incident review, its out-of-cycle scan, its member outreach and its consultation offer
Source Casa's captured 6 August blog post, written by its co-founder and chief security officer; the internal actions it describes are not independently visible here
Evidence → captured 7 Aug 2026
- R9 Reported · contested
Casa's announcement of the workshop and what it said the session would cover
Source Casa's captured post of 7 Aug 2026; commercial interest stated above
Evidence → captured 7 Aug 2026
- R10 Reported · contested
The vendor's shipment, stock, customer-email and product-scope statements
Source Coinkite's captured official post of 2 Aug 2026
Evidence → captured
- R11 Reported · contested
The Sunday statement's damage acknowledgement, outreach description, community thanks and forward commitment
Source Coinkite's captured official post of 2 Aug 2026
Evidence → captured
- R12 Reported · contested
Coinkite's statement of where its firmware work can be followed and what it says it is focusing on
Source COLDCARD's captured post of 6 Aug 2026
Evidence → captured 7 Aug 2026
- R13 Reported · contested
Coinkite's statements on pending firmware releases, its own investigation, responsible disclosure and the company's likely continuation
Source COLDCARD's three captured replies of 7 Aug 2026, linked in the sentence above
Evidence → captured 7 Aug 2026
- R14 Reported · contested
That two held sources relay a Bloomberg report of Coinkite declining to estimate customer losses, and that the report itself is not held
Source Cointelegraph's captured post and the captured BitcoinTalk thread; both are relays of a Bloomberg article this archive does not hold
Evidence → captured 7 Aug 2026
- R15 Reported · contested
Coinkite's statement on outreach data handling and deletion
Source Coinkite's captured official reply of 2 Aug 2026
Evidence → captured
- R16 Reported · contested
Satochip's public data-retention question and its 90-day premise
Source Satochip's captured post of 2 Aug 2026; competing interest stated above
Evidence → captured
- V17 Verified · contested
Coinkite's stated 120-day blanking period, what that blanking retains, and the temporary suspension of the automated process
Source Held capture of Coinkite's own 7 August post; it is also listed on the captured blog index, dated 6 August there before the publisher retimestamped it to 7 August
Evidence → captured 7 Aug 2026
- R18 Reported · contested
NCFA Canada's vendor-layer position and its secondhand use of Galaxy Research's loss figures
Source NCFA Canada's captured 3 August commentary; affiliation stated above
Evidence → captured 5 Aug 2026
- R19 Reported · contested
Ledger's published open-source position and the line it quotes from its CTO
Source Ledger's captured post of 7 Aug 2026; the article it links is not held here; competing interest stated above
Evidence → captured 7 Aug 2026
- R20 Reported · contested
Bent's apology and his account of helping people migrate
Source Marty Bent's captured post of 2 Aug 2026
Evidence → captured
- R21 Reported · contested
The described owner-outreach effort and its accepted moderation risk
Source Pledditor's captured post of 2 Aug 2026
Evidence → captured
- R22 Reported · contested
The OpenSats board departure and interim board size; no causal link to the incident
Source OpenSats' captured statement of 2 Aug 2026
Evidence → captured
- V23 Verified · contested
The Code RED post's stated terms, its displayed 6 August publication date and its wording as held
Source Held capture of the OpenSats blog post, announced the same day on the organisation's X account
Evidence → captured 7 Aug 2026